
 owasp/offat
Automated API security testing tool that generates tests from OpenAPI specs, fuzzes inputs, and checks for OWASP API Top 10 vulnerabilities including SQLi, BOLA, and broken access control.

OWASP OFFAT (OFFensive Api Tester) is created to automatically test API for common vulnerabilities after generating tests from openapi specification file. It provides feature to automatically fuzz inputs and use user provided inputs during tests specified via YAML config file.
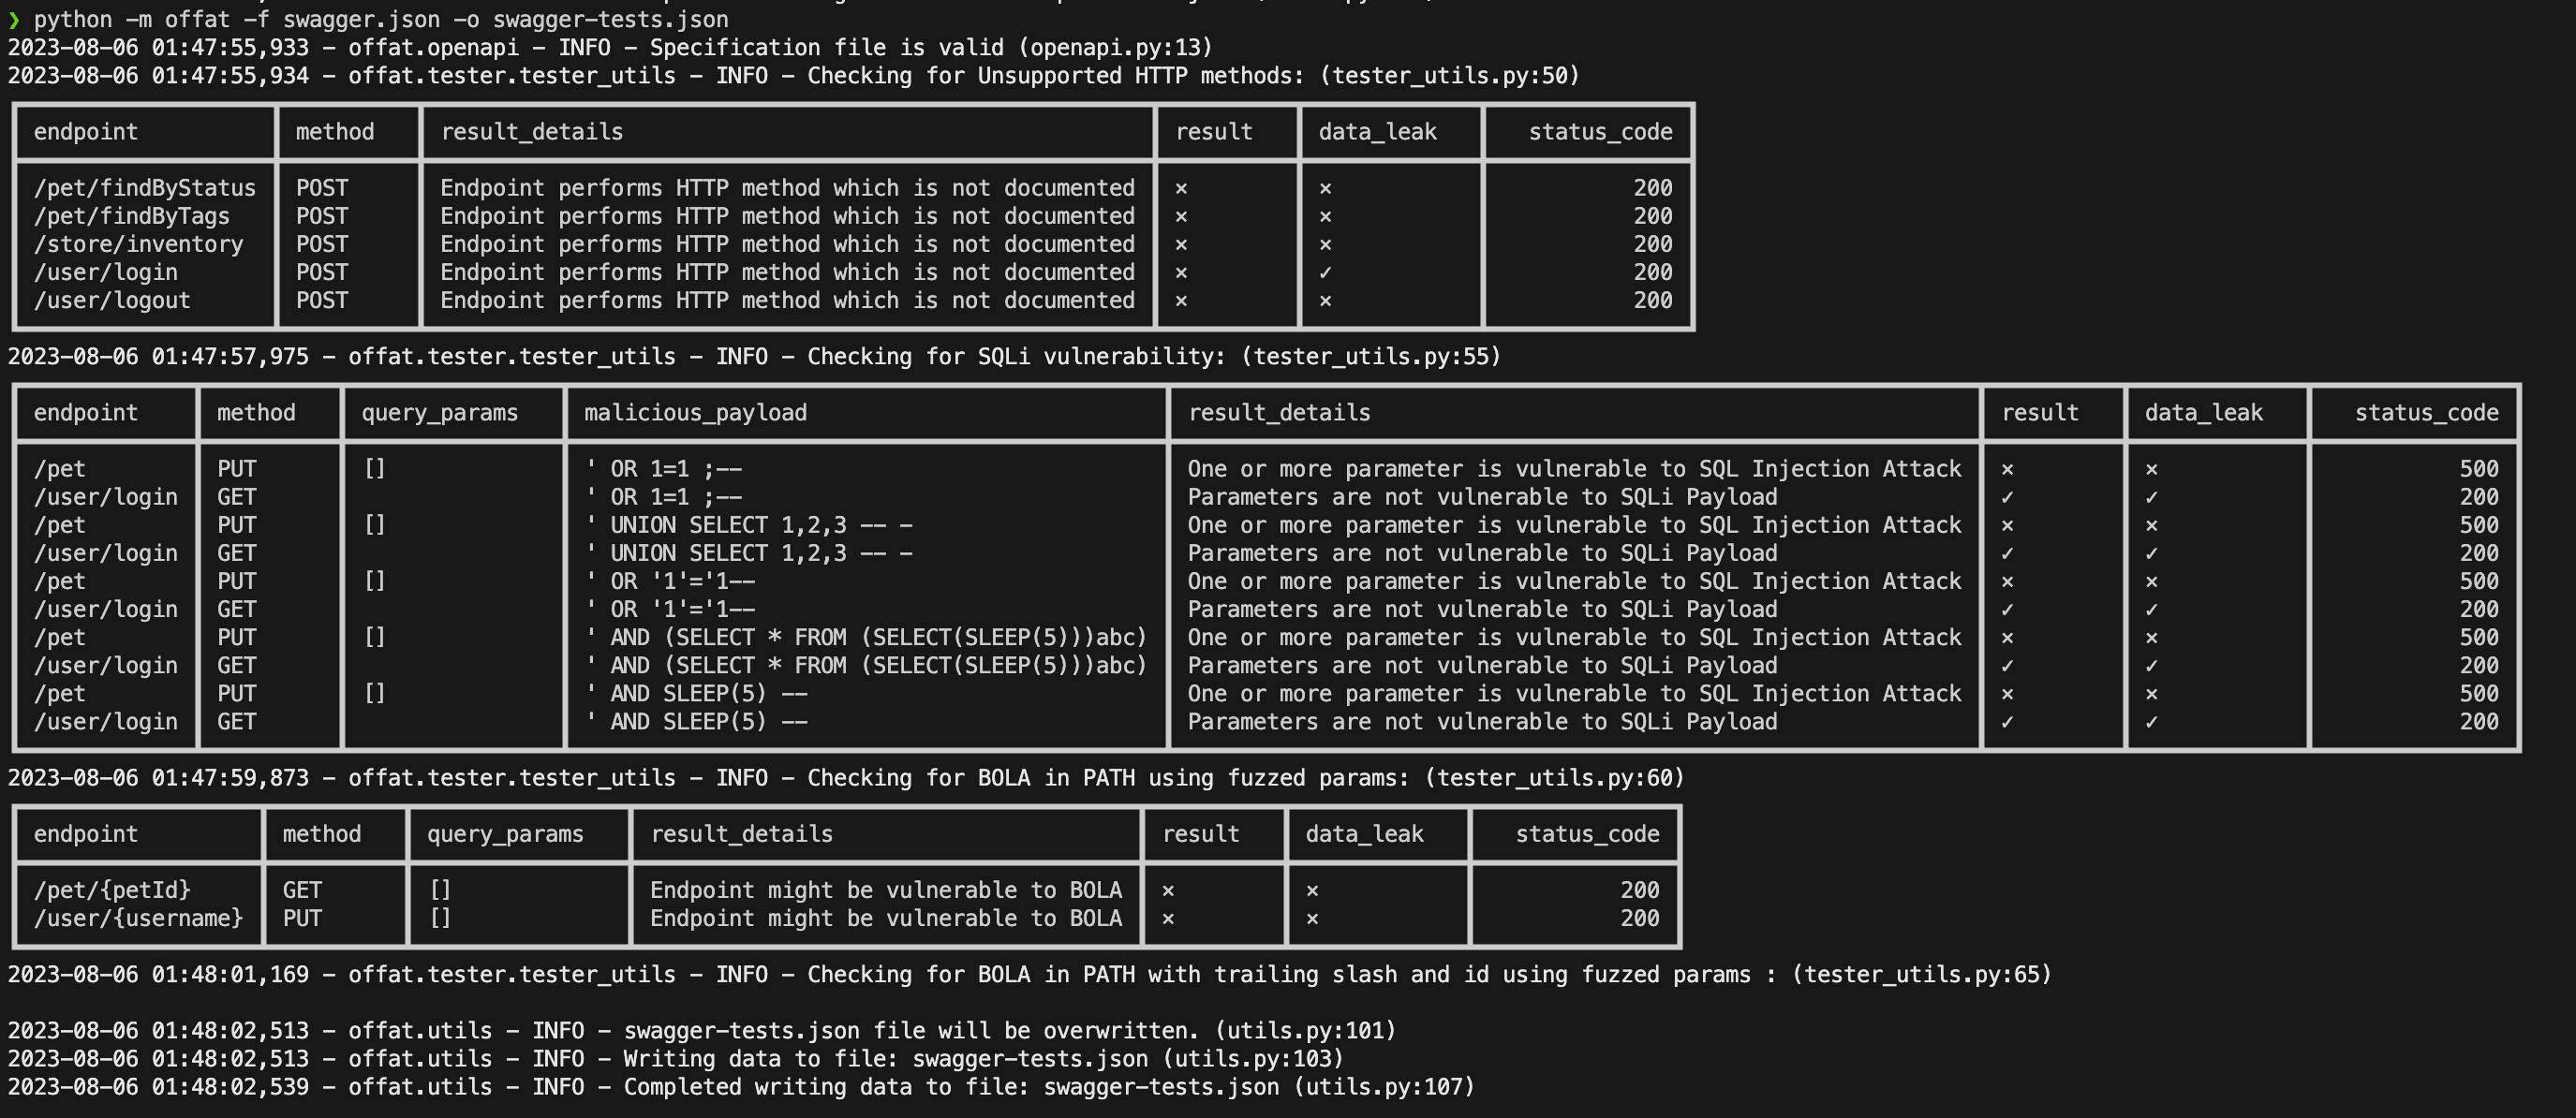

Note: The columns for 'data_leak' and 'result' in the table represent independent aspects. It's possible for there to be a data leak in the endpoint, yet the result for that endpoint may still be marked as 'Success'. This is because the 'result' column doesn't necessarily reflect the overall test result; it may indicate success even in the presence of a data leak.
python -m pip install offat
offat -f swagger_file.json
Alongside the classic offat CLI above, this repository now also hosts
OFFAT-AI, a staged, source-aware API pentest platform (white-box SAST,
gray-box reachability, and a Rust execution engine) built around a single
canonical Bundle file. It is additive and does not change the existing tool.
offat-platform run <source> --url <target> --yes