
Argus
 dozermx/argus
Multi-phase reconnaissance and attack-surface scanner that maps domains, IPs, ASNs, cloud assets, and CVEs into a knowledge graph with CVSS scoring…
api-securityfuzzinginformation-gathering+9
5
dozermx/argusMulti-phase reconnaissance and attack-surface scanner that maps domains, IPs, ASNs, cloud assets, and CVEs into a knowledge graph with CVSS scoring…
 vavkamil/awesome-bugbounty-tools
Curated directory of bug bounty tools organized by category: reconnaissance, subdomain enumeration, port scanning, content discovery, exploitation,…
 hmrumman777-beep/netaudit-iot
Research-driven UPnP vulnerability scanner focusing on libupnp 1.6.19 and CVE-2012-5958.
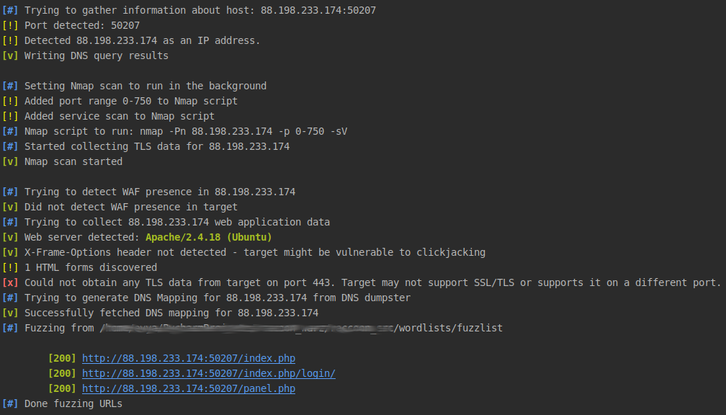 evyatarmeged/raccoon
A high performance offensive security tool for reconnaissance and vulnerability scanning
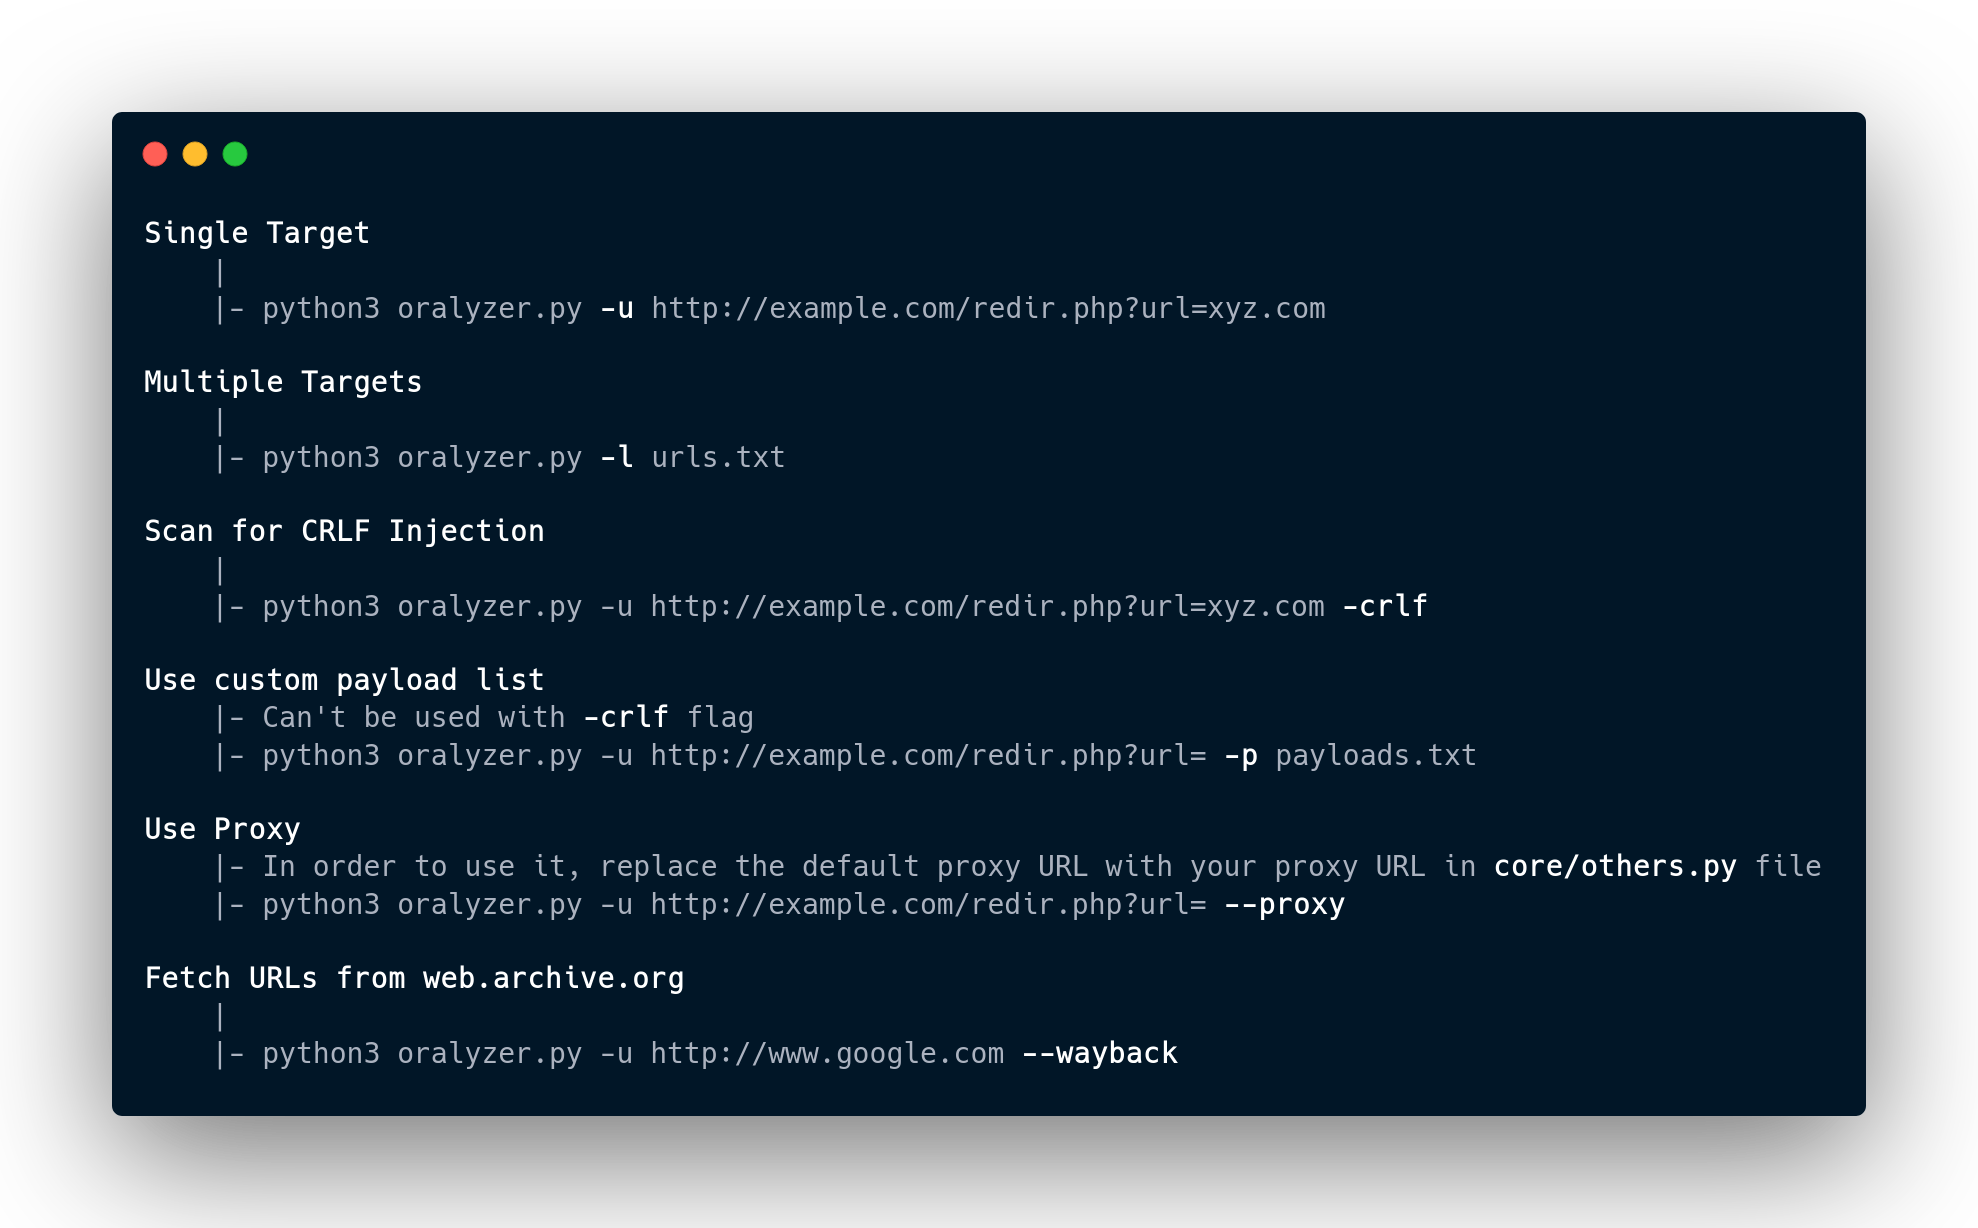 r0075h3ll/oralyzer
Python-based open redirect vulnerability scanner that fuzzes URLs to detect header, JavaScript, and meta tag-based redirects, with integrated…
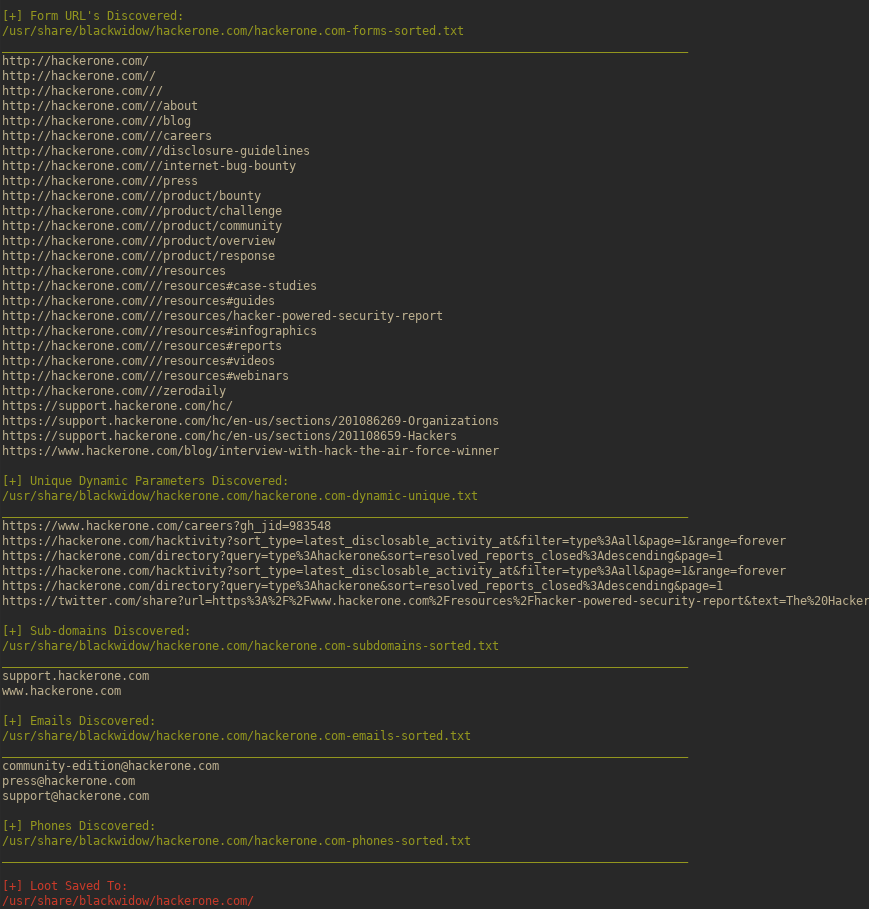 1n3/blackwidow
A Python based web application scanner to gather OSINT and fuzz for OWASP vulnerabilities on a target website.
 gokulapap/reconator
Automated reconnaissance framework with 17+ modules for subdomain enumeration, directory brute-forcing, JS/link mining, WAF fingerprinting, and…
 c0dejump/hawkscan
Security Tool for Reconnaissance and Information Gathering on a website. (python 3.x)
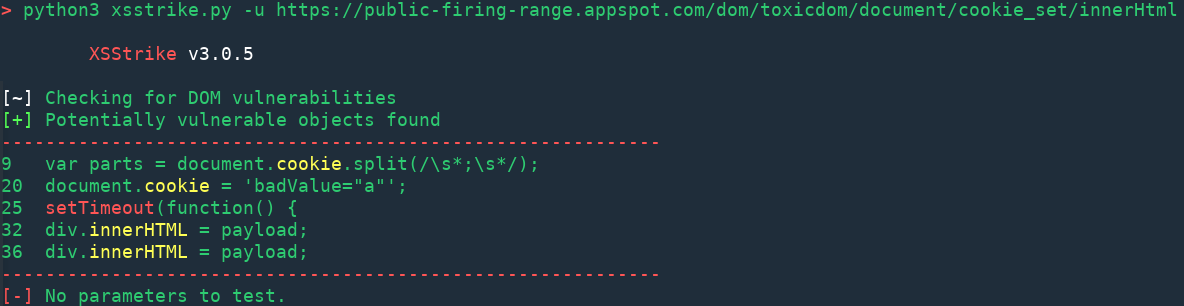
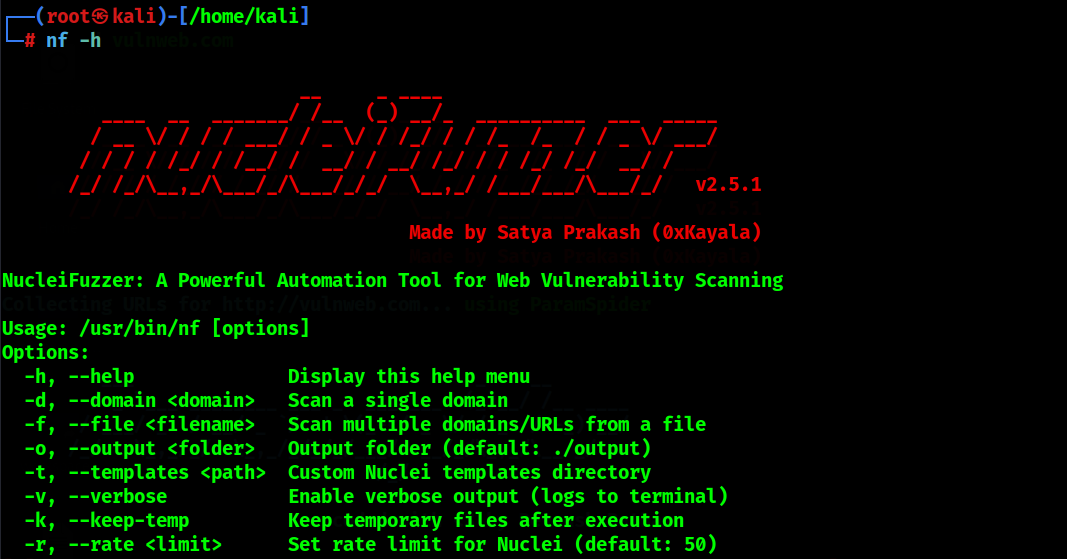 0xkayala/nucleifuzzer
Automated web vulnerability scanner combining URL discovery tools (ParamSpider, waybackurls, gauplus, hakrawler, katana) with Nuclei fuzzing…
 spinkham/skipfish
Web application security scanner created by lcamtuf for google - Unofficial Mirror
 fcavallarin/htcap
htcap is a web application scanner able to crawl single page application (SPA) recursively by intercepting ajax calls and DOM changes.
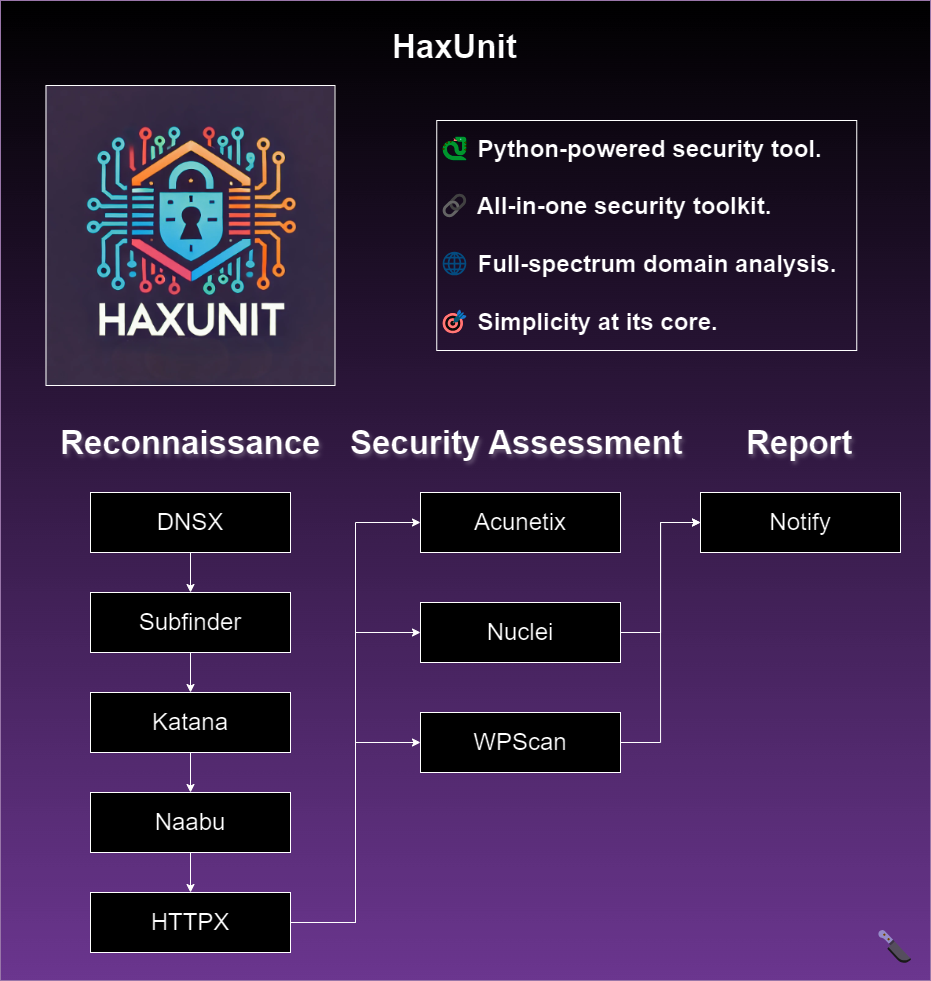 bandit-haxunit/haxunit
Automated web domain reconnaissance and security assessment tool integrating subdomain enumeration, port scanning, vulnerability scanning, and…
 th0h0/autossrf
Smart context-based SSRF vulnerability scanner.
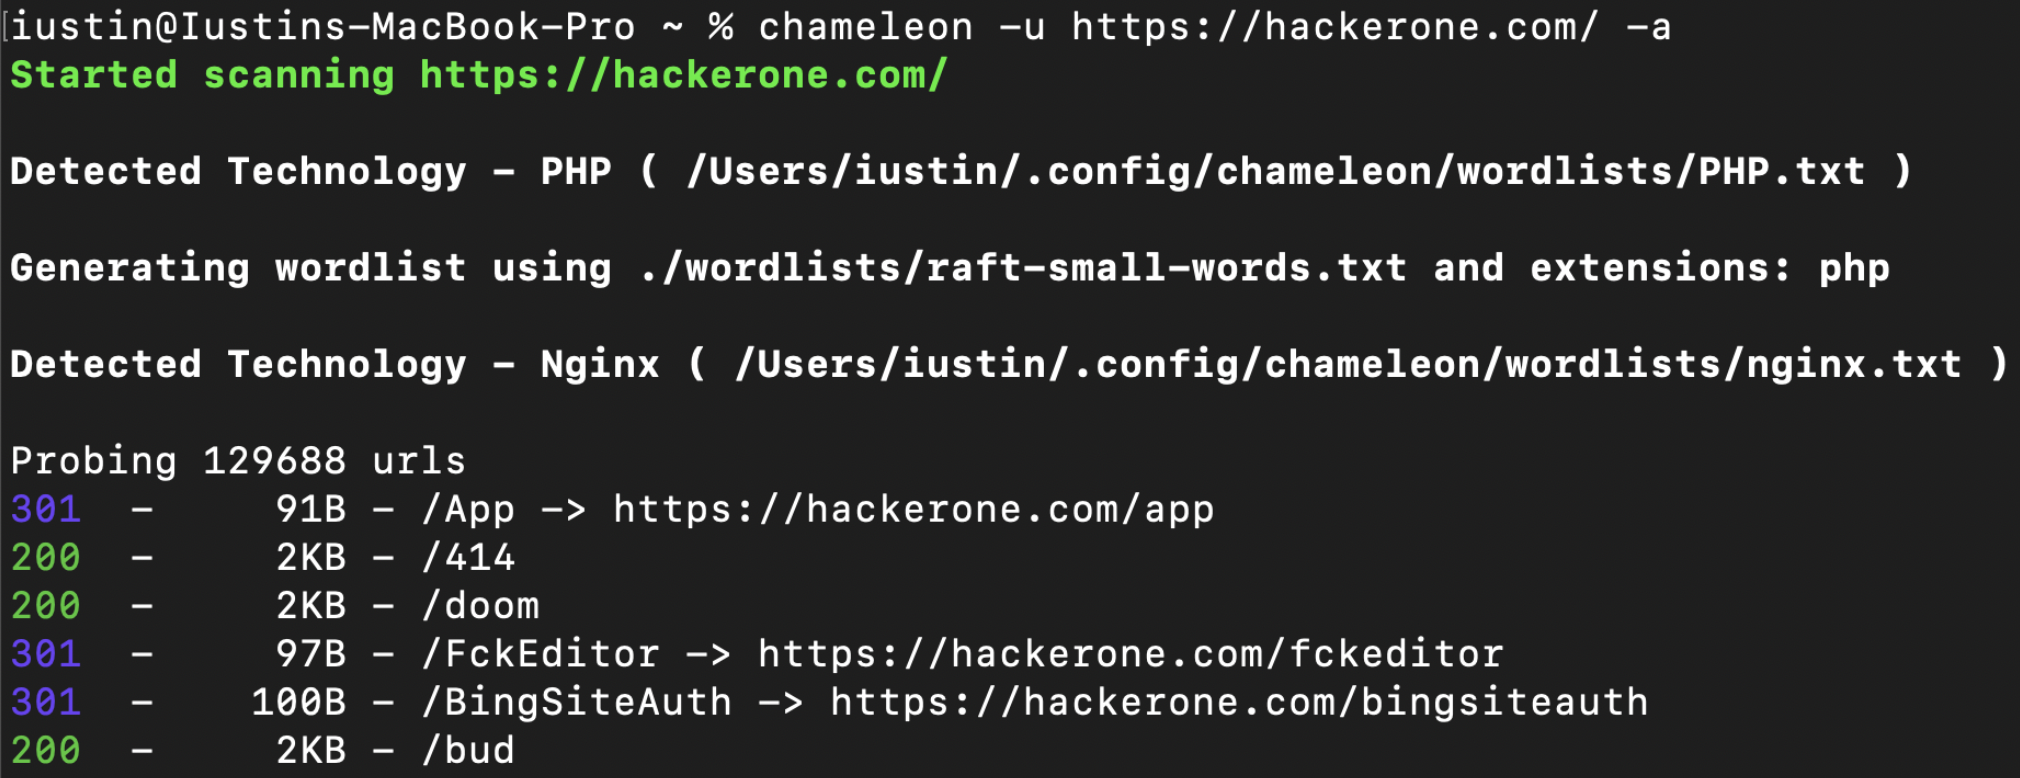 iustin24/chameleon
Technology-aware web content discovery scanner: detects Wappalyzer fingerprints, adapts wordlists/extensions, and performs fast directory bruteforce…
 s_r_e_e_r_a_j/reconhound
ReconHound is a Python-based web reconnaissance tool designed for penetration testers, bug bounty hunters, and ethical hackers. It supports directory…
 abrewer251/cve-2024-38475_sonicboom_apache_url_traversal_poc
Proof-of-concept scanner for CVE-2024-38475 (SonicBoom) Apache URL traversal. Automates TLS negotiation, directory scanning, traversal verification,…
 scheibling/py-log4shellscanner
Scanner for the Log4j vulnerability dubbed Log4Shell (CVE-2021-44228)