
cve-2023-21987-poc
 chunzhennn/cve-2023-21987-poc
Proof-of-concept exploit for Oracle VirtualBox VGA out-of-bounds read vulnerability, demonstrating address leaking from VirtualBox components on…
binary-exploitationexploitationfuzzing+3
1
chunzhennn/cve-2023-21987-pocProof-of-concept exploit for Oracle VirtualBox VGA out-of-bounds read vulnerability, demonstrating address leaking from VirtualBox components on…
 ioprojecton/dir-3040_dos
Proof-of-concept exploit for CVE-2024-27619 causing denial of service on D-Link DIR-3040/3060 routers via FTP memory exhaustion without…
 jonathansalwan/triton
Triton is a dynamic binary analysis library. Build your own program analysis tools, automate your reverse engineering, perform software verification…
 openrce/sulley
A pure-python fully automated and unattended fuzzing framework.
 microsoft/windowsprotocoltestsuites
⭐⭐ Join us at SNIA SDC for the SMB3 IO Lab (September 28 - October 1, 2026), see upcoming Interoperability Events
 openrce/paimei
A reverse engineering framework written in Python.
 quarkslab/rewind
Snapshot-based coverage-guided windows kernel fuzzer
 grp-ops/react2shell
Lightweight scanner and Nuclei templates for identifying React and Next.js deserialization RCEs (CVE-2025-55182 / CVE-2025-66478).
 darkflippers/unleashed-firmware
Custom firmware for Flipper Zero enabling Sub-GHz radio, NFC/RFID emulation, infrared, and BadUSB attack features for hardware security testing.
 brucedevices/firmware
Predatory ESP32 Firmware
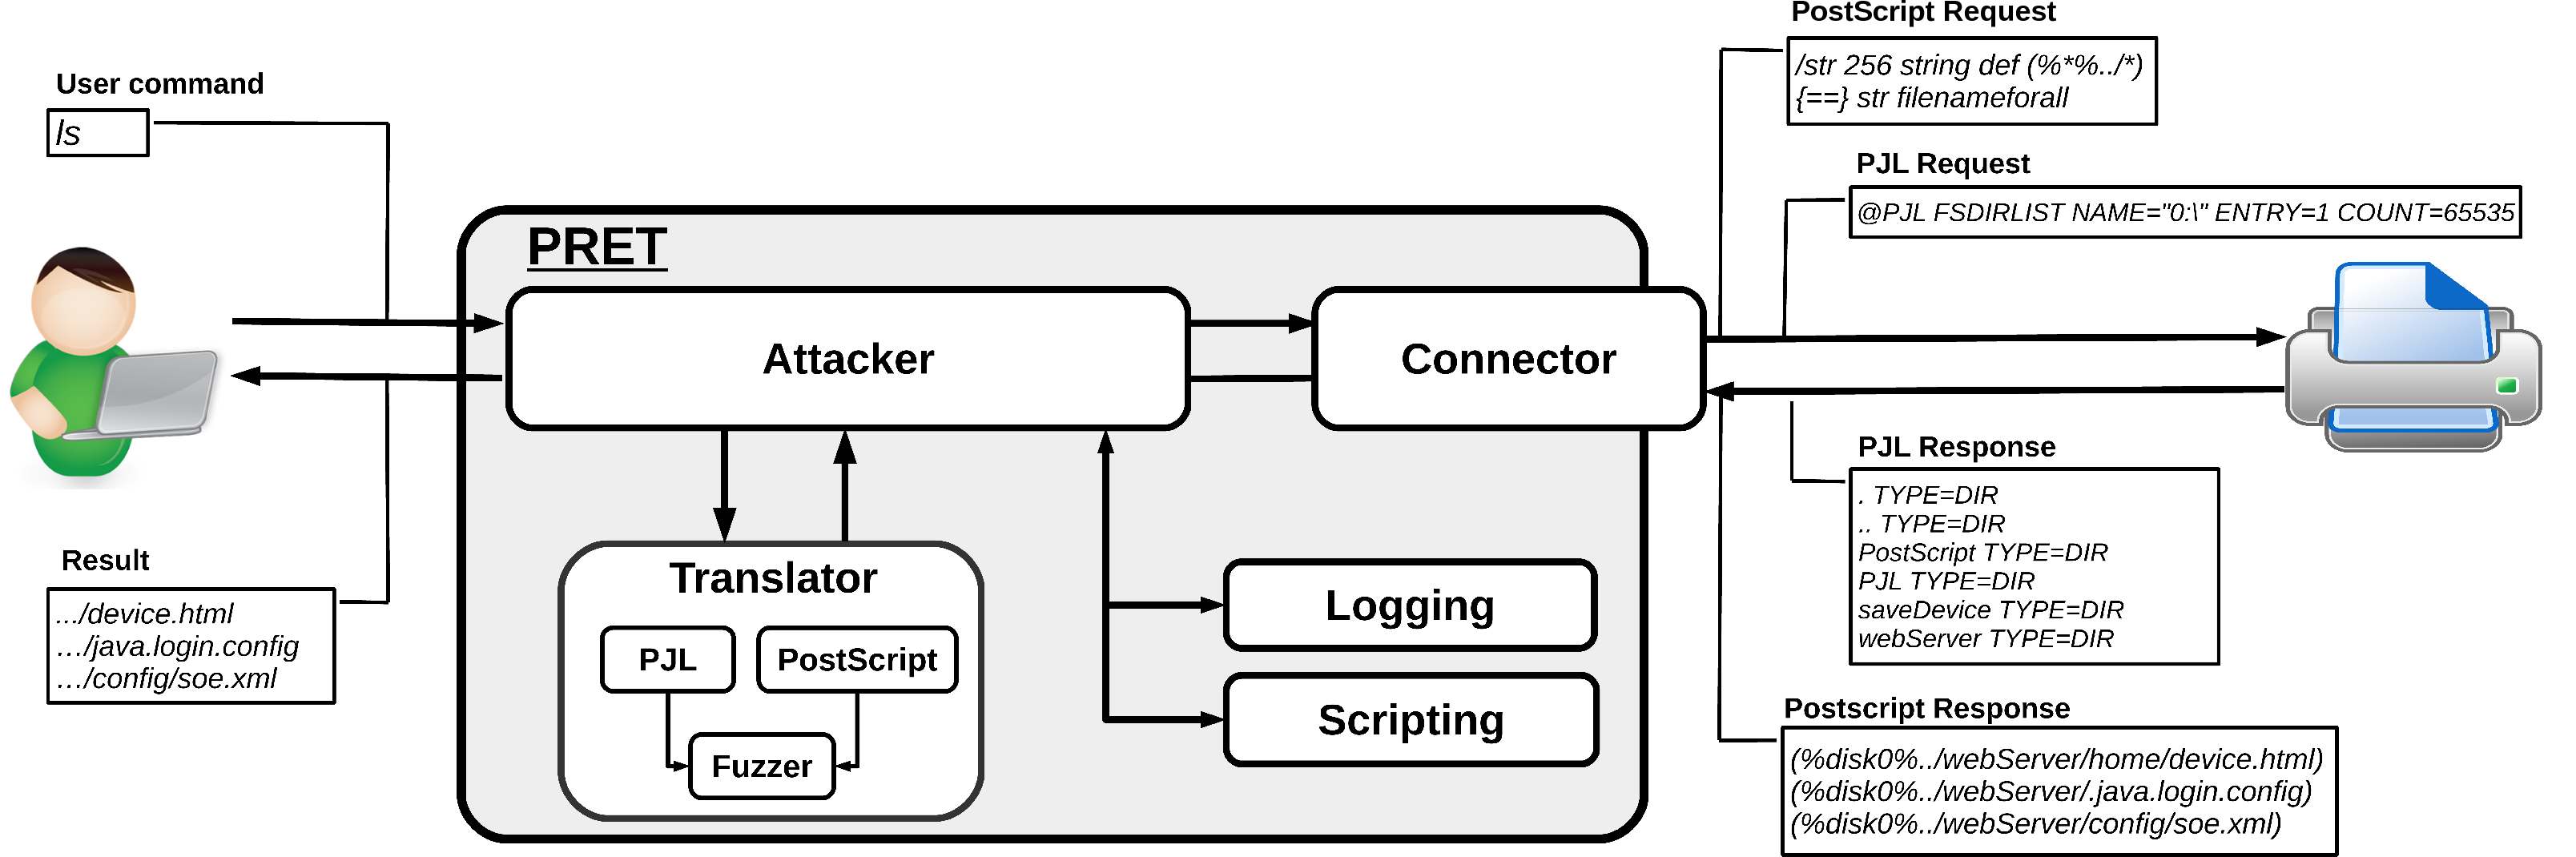 rub-nds/pret
Printer Exploitation Toolkit - The tool that made dumpster diving obsolete.
 matheus-garbelini/esp32_esp8266_attacks
Proof of Concept of ESP32/8266 Wi-Fi vulnerabilties (CVE-2019-12586, CVE-2019-12587, CVE-2019-12588)
 rfidtool/esp-rfid-tool
A tool for logging data/testing devices with a Wiegand Interface. Can be used to create a portable RFID reader or installed directly into an existing…
 tothi/pwn-hisilicon-dvr
Proof-of-concept exploit and vulnerability disclosure for HiSilicon hi3520d DVR/NVR devices. Demonstrates RCE via web interface, backdoor…
 leochen-coremind/vmpacker
ARM64 ELF Virtual Machine Protection System
 eik00d/cantoolz
CANToolz - framework for black-box CAN network analysis
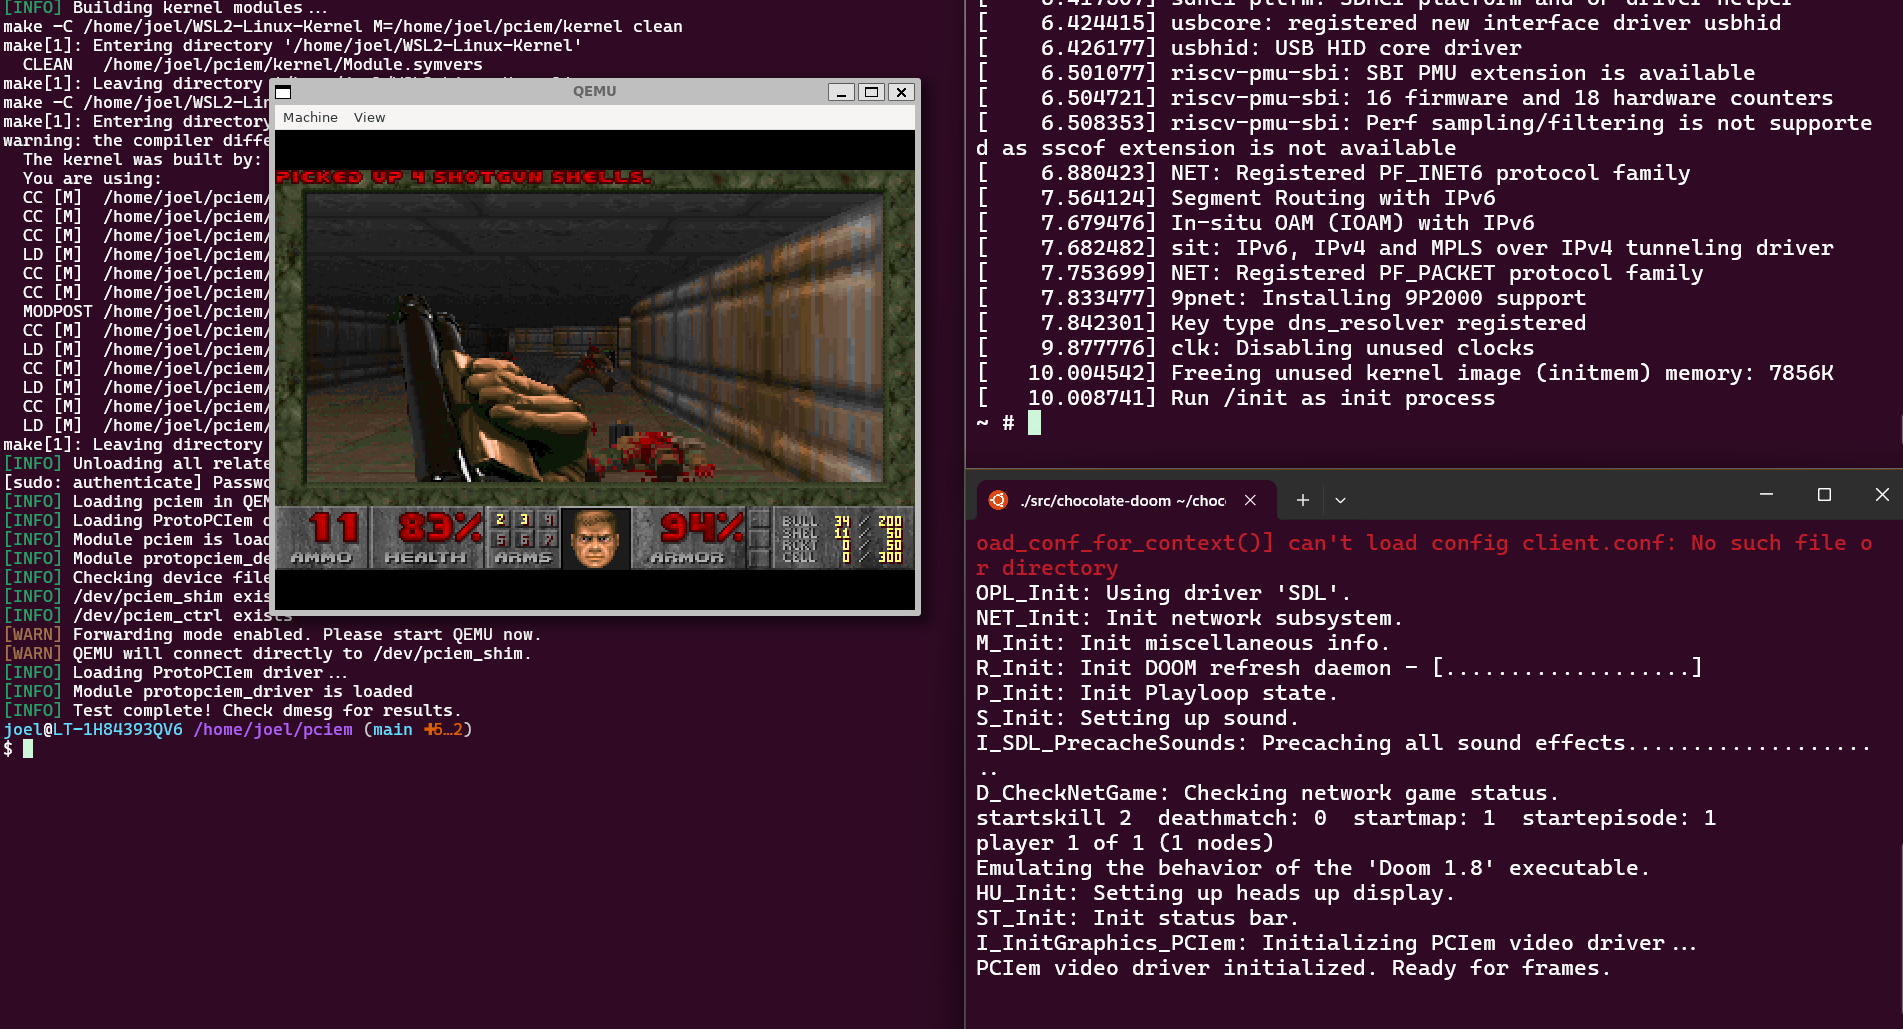 cakehonolulu/pciem
A Linux framework to enable userspace-defined "Virtual" PCIe card shims to enable in-host PCIe card driver development.
 pagalaxylab/unifuzzer
A fuzzing tool for closed-source binaries based on Unicorn and LibFuzzer