
HawkScan
 c0dejump/hawkscan
Security Tool for Reconnaissance and Information Gathering on a website. (python 3.x)
crawlerfuzzinginformation-gathering+5
463
c0dejump/hawkscanSecurity Tool for Reconnaissance and Information Gathering on a website. (python 3.x)
 ihebski/angryfuzzer
Tools for information gathering
 nokn0wthing/cve-2023-20052
CVE-2023-20052, information leak vulnerability in the DMG file parser of ClamAV
 maherazzouzi/cve-2022-36163
Proof-of-concept exploit for CVE-2022-36163, a format string vulnerability in pdftoroff hovacui 1.1.0 PDF reader, demonstrating local…
 harsh-bothra/bheem
Scope-based reconnaissance automation framework that orchestrates multiple open-source tools for subdomain enumeration, vulnerability scanning, and…
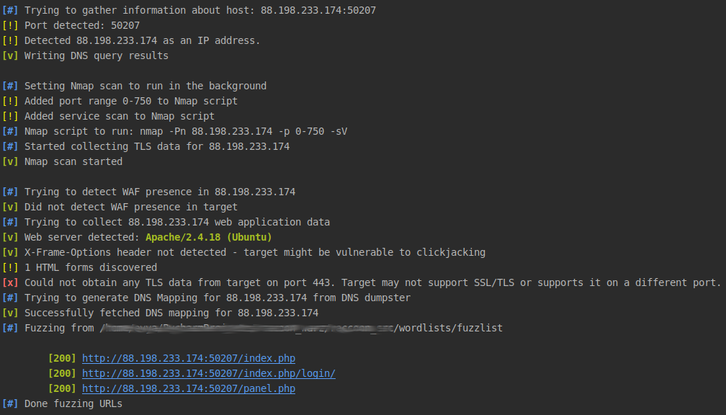 evyatarmeged/raccoon
A high performance offensive security tool for reconnaissance and vulnerability scanning
 overspace-labs/caa
BurpSuite plugin for HTTP packet analysis and fuzzing dictionary generation. Extracts parameters, paths, and files from requests, counts frequency,…
 x3omdax/penbox
PenBox - A Penetration Testing Framework - The Tool With All The Tools , The Hacker's Repo
 0xpugal/fuzz4bounty
1337 Wordlists for Bug Bounty Hunting
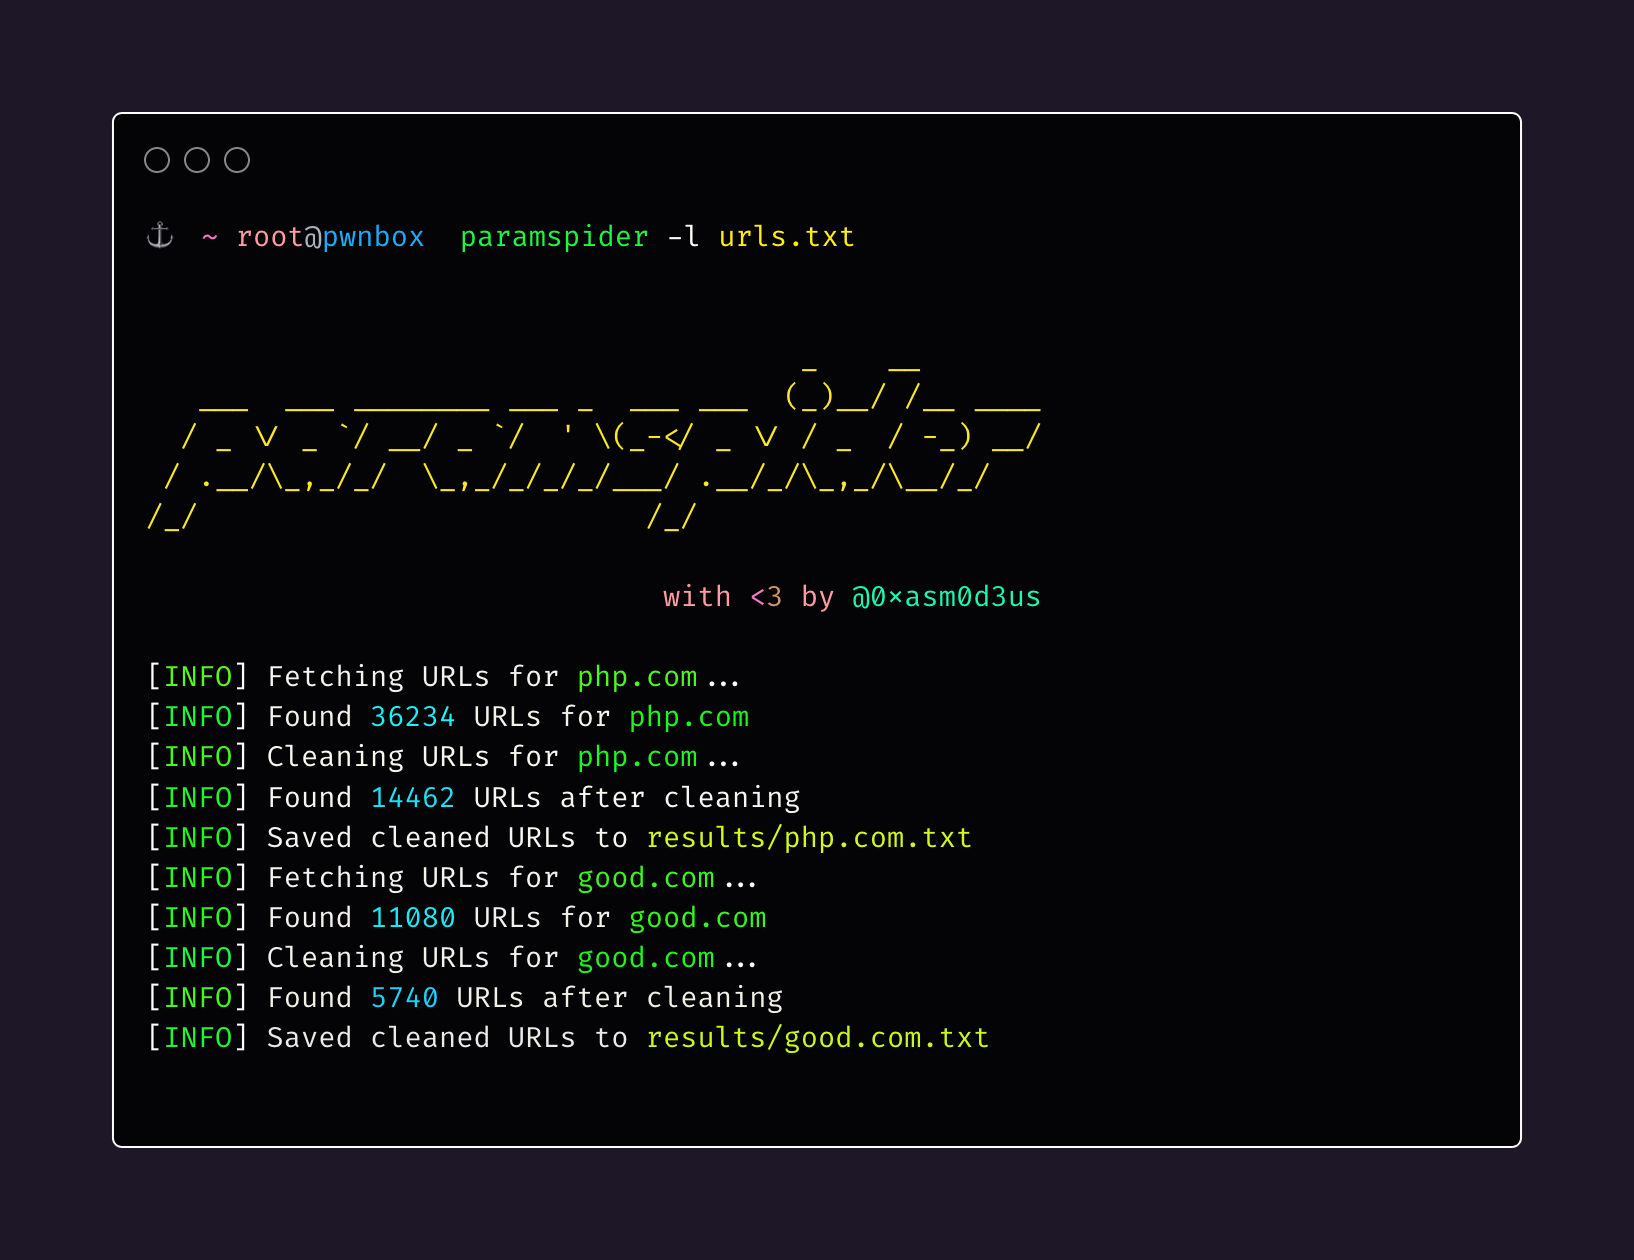 devanshbatham/paramspider
Mining URLs from dark corners of Web Archives for bug hunting/fuzzing/further probing
 six2dez/onelistforall
Curated, categorized wordlist generator for web fuzzing, directory enumeration, and subdomain discovery. Automatically syncs 36+ sources, classifies…
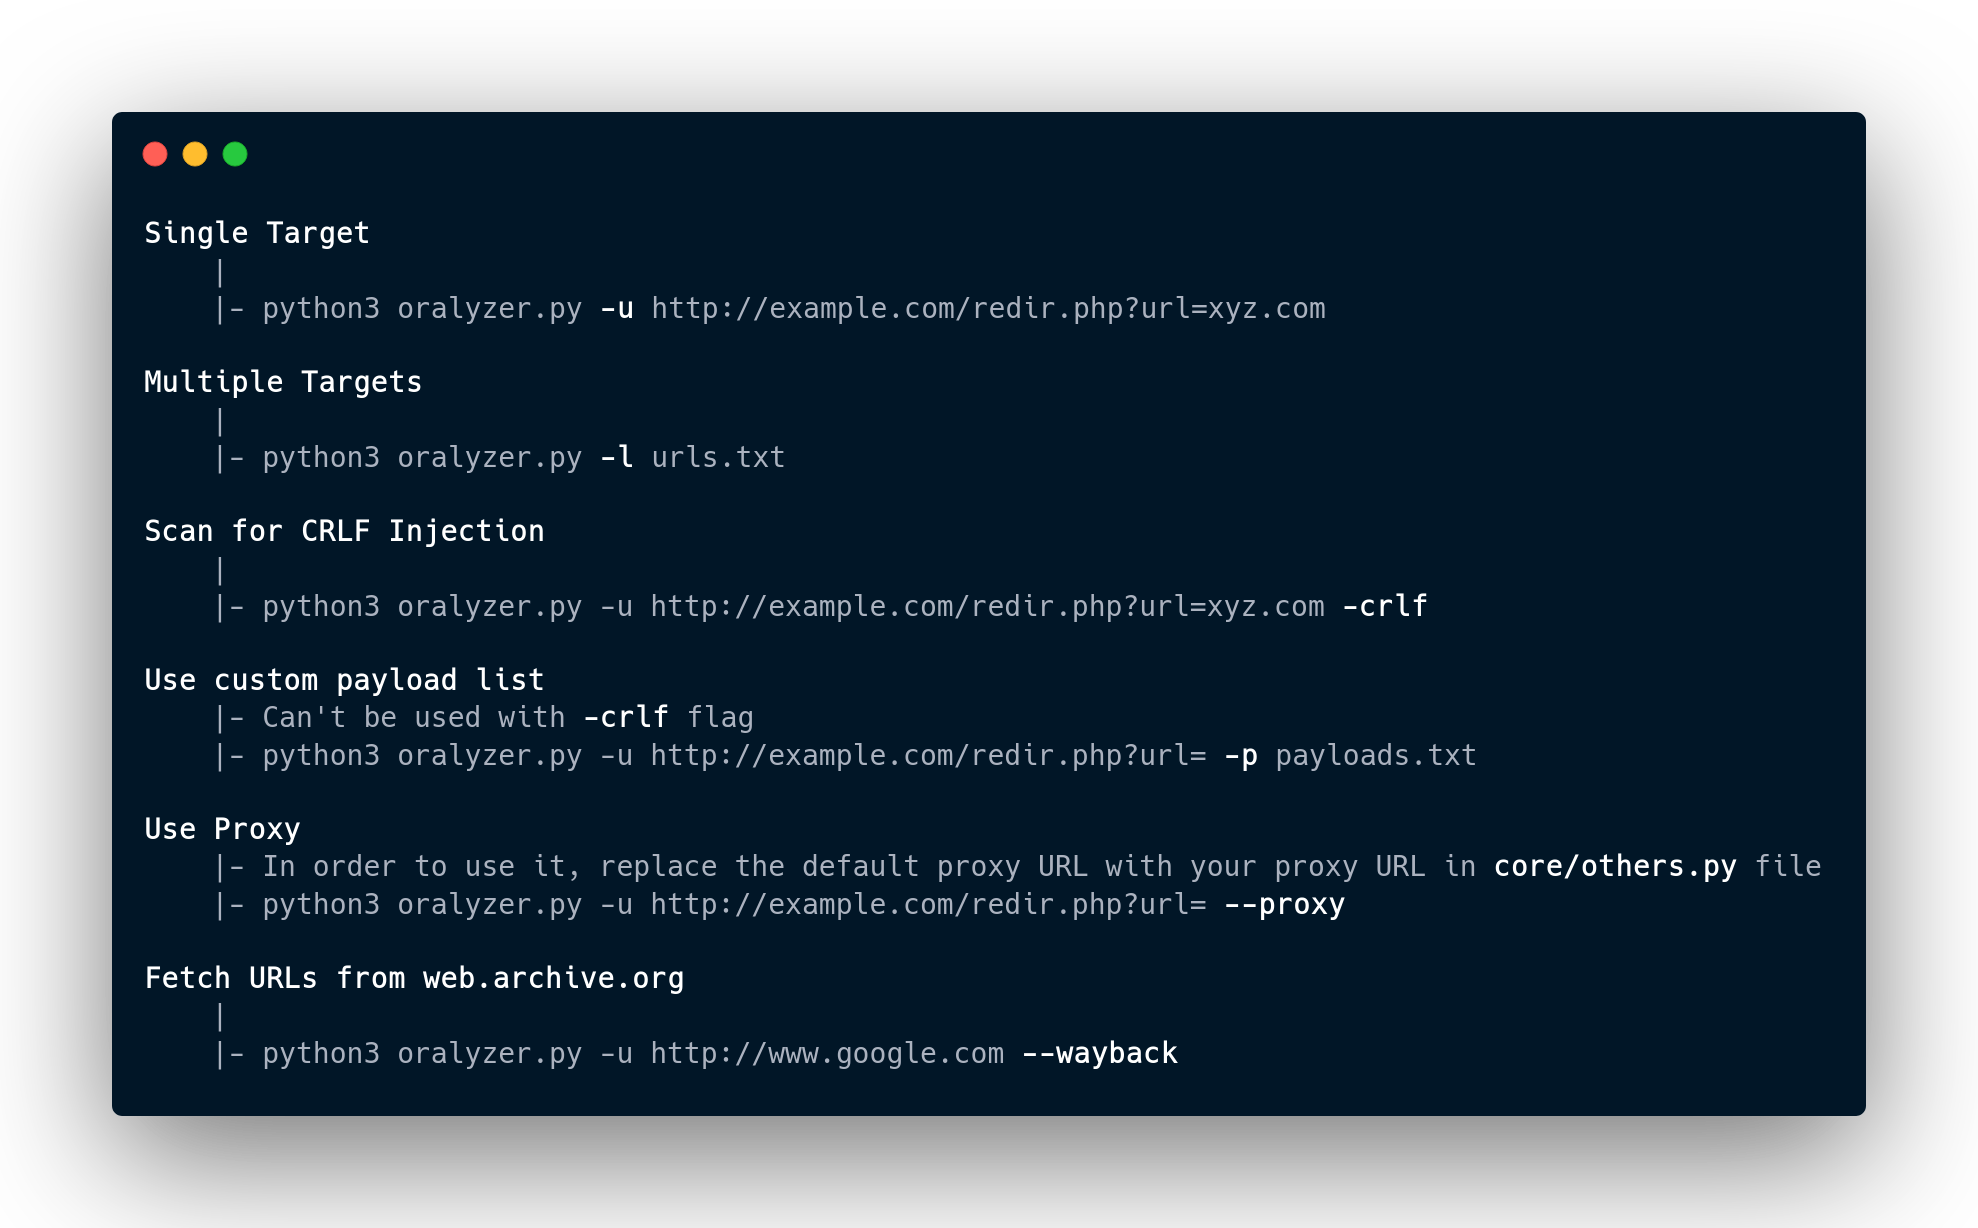 r0075h3ll/oralyzer
Python-based open redirect vulnerability scanner that fuzzes URLs to detect header, JavaScript, and meta tag-based redirects, with integrated…
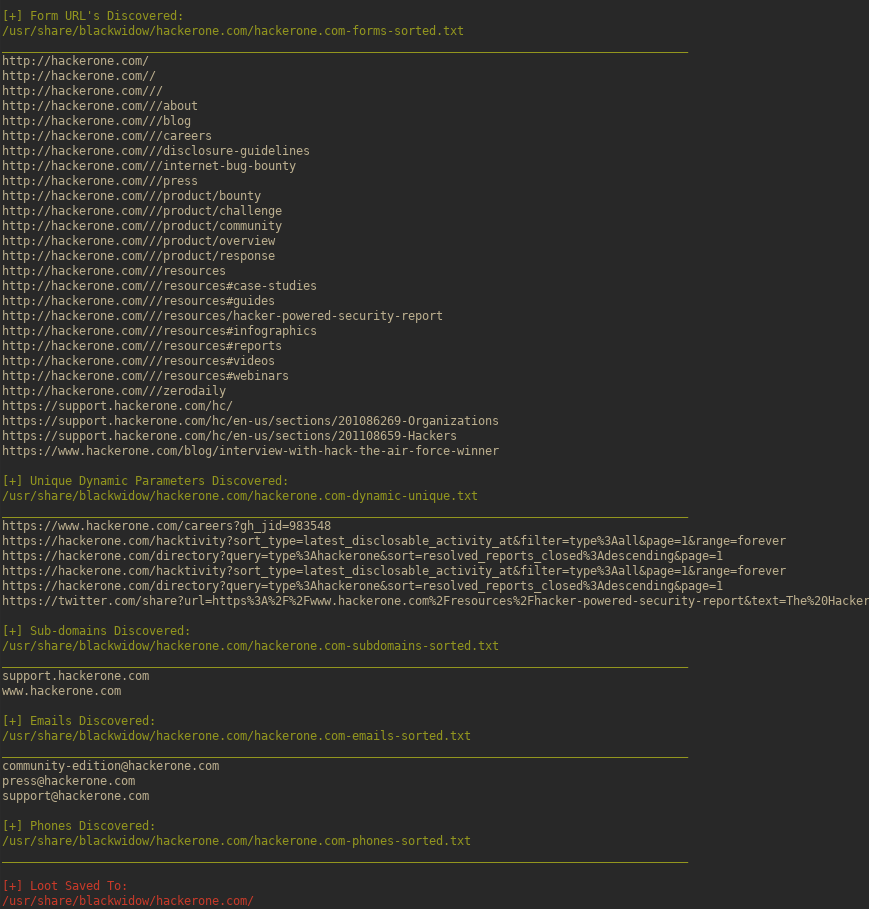 1n3/blackwidow
A Python based web application scanner to gather OSINT and fuzz for OWASP vulnerabilities on a target website.
 0xinfection/tidos-framework
The Offensive Manual Web Application Penetration Testing Framework.
 ayoubfathi/leaky-paths
A collection of special paths linked to common sensitive APIs, devops internals, frameworks conf, known misconfigurations, juicy APIs ..etc. It could…
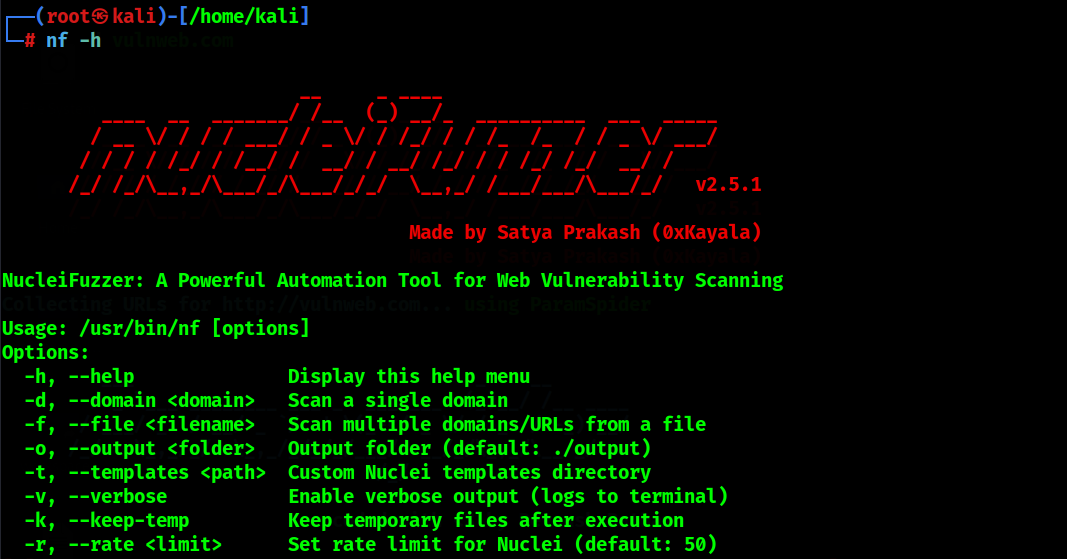 0xkayala/nucleifuzzer
Automated web vulnerability scanner combining URL discovery tools (ParamSpider, waybackurls, gauplus, hakrawler, katana) with Nuclei fuzzing…
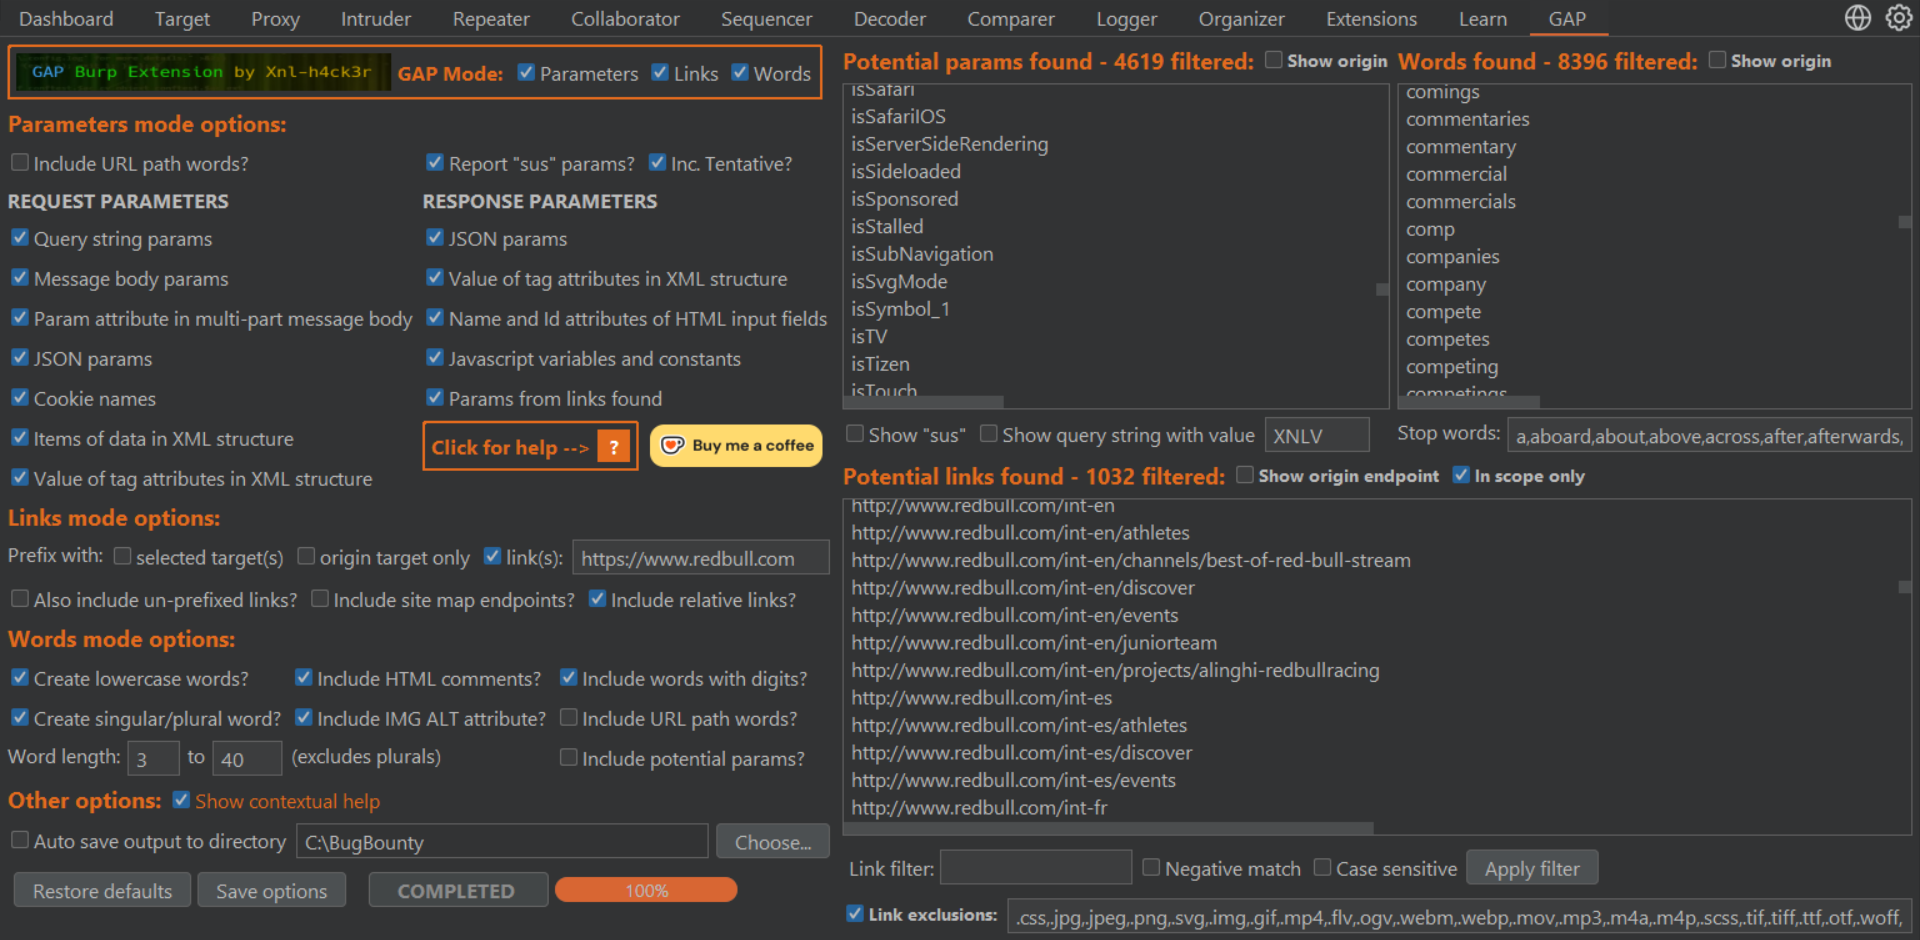 xnl-h4ck3r/gap-burp-extension
Burp Extension to find potential endpoints, parameters, and generate a custom target wordlist