CVE-2021-44228-log4jVulnScanner-metasploit

open detection and scanning tool for discovering and fuzzing for Log4J RCE CVE-2021-44228 vulnerability

open detection and scanning tool for discovering and fuzzing for Log4J RCE CVE-2021-44228 vulnerability

Proof-of-concept exploit for a buffer overflow vulnerability (CVE-2024-44596) in Netis N5VN AC1200 routers, causing a denial of service by crashing…

Proof-of-concept exploit for CVE-2024-22640, a ReDoS vulnerability in TCPDF <=6.7.4 triggered by crafted HTML color input, with demonstration code.

A fully automated, reliable, super-fast, scanning and validation toolkit for the Log4J RCE CVE-2021-44228 vulnerability.

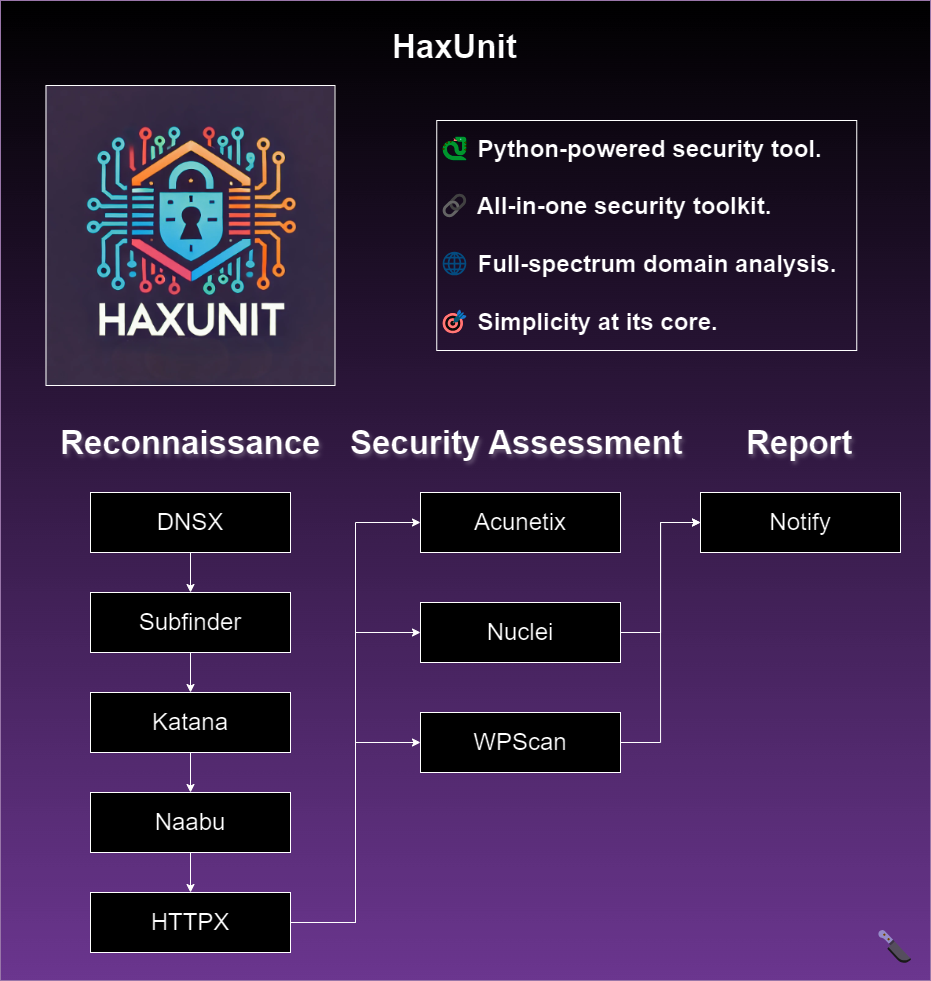
Automated web domain reconnaissance and security assessment tool integrating subdomain enumeration, port scanning, vulnerability scanning, and…

Proof-of-concept exploit for CVE-2022-36163, a format string vulnerability in pdftoroff hovacui 1.1.0 PDF reader, demonstrating local…

A Python based web application scanner to gather OSINT and fuzz for OWASP vulnerabilities on a target website.

CVE-2020-27824 exploit reproduction environment for OpenJPEG JPEG 2000 codec, enabling vulnerability analysis, fuzzing, and binary exploitation…

Proof-of-concept exploit for CVE-2024-6387, a remote code execution vulnerability in OpenSSH server, demonstrating exploitation techniques for…

AI Smart Contract Security Analysis and PoC Generation Framework

Autonomous security research framework integrating static analysis, binary analysis, fuzzing, LLM-powered vulnerability validation, exploit…

No-dongle, no-root Bluetooth security assessment tool for wireless earbuds affected by the Airoha SDK vulnerability chain (CVE-2025-20700/20701/20702)

C library for stream-oriented XML parsing with a focus on vulnerability analysis and exploitation of CVE-2022-43680, enabling fuzzing and…

Behavior-preserving fix for CVE-2025-60876 HTTP header injection in BusyBox wget, with proof-of-concept, percent-encoding patch, and upstream…

Evaluation framework for studying LLM agents that automatically generate working exploits from vulnerability reports, bypassing modern security…

This POC exploits a format validation vulnerability in the RTSP service of the Hipcam RealServer/V1.0, inducing a crash for approximately 45 seconds…

Proof-of-concept exploit for CVE-2023-1999 targeting the WebP codec library on Android 10 (r33). Demonstrates a heap buffer overflow vulnerability in…

C library for stream-oriented XML parsing, with a focus on analyzing and reproducing CVE-2024-28757 vulnerability in Expat 2.1.0.