
CVE-2023-38545
 yang-shun-yu/cve-2023-38545
Proof-of-concept exploit for CVE-2023-38545, a curl heap buffer overflow. Includes SOCKS5 proxy and HTTP server to trigger the vulnerability and…
exploitationfuzzingnetwork-security+3
yang-shun-yu/cve-2023-38545Proof-of-concept exploit for CVE-2023-38545, a curl heap buffer overflow. Includes SOCKS5 proxy and HTTP server to trigger the vulnerability and…
 hzqst/unicorn_pe
Emulates Windows PE execution using Unicorn engine for malware analysis, unpacking packed binaries, and decrypting VMProtect strings and imports.
 googleprojectzero/sockfuzzer
Coverage-guided kernel fuzzing framework that runs XNU as a userspace library and discovers vulnerabilities across BSD, Mach, virtual memory, and…
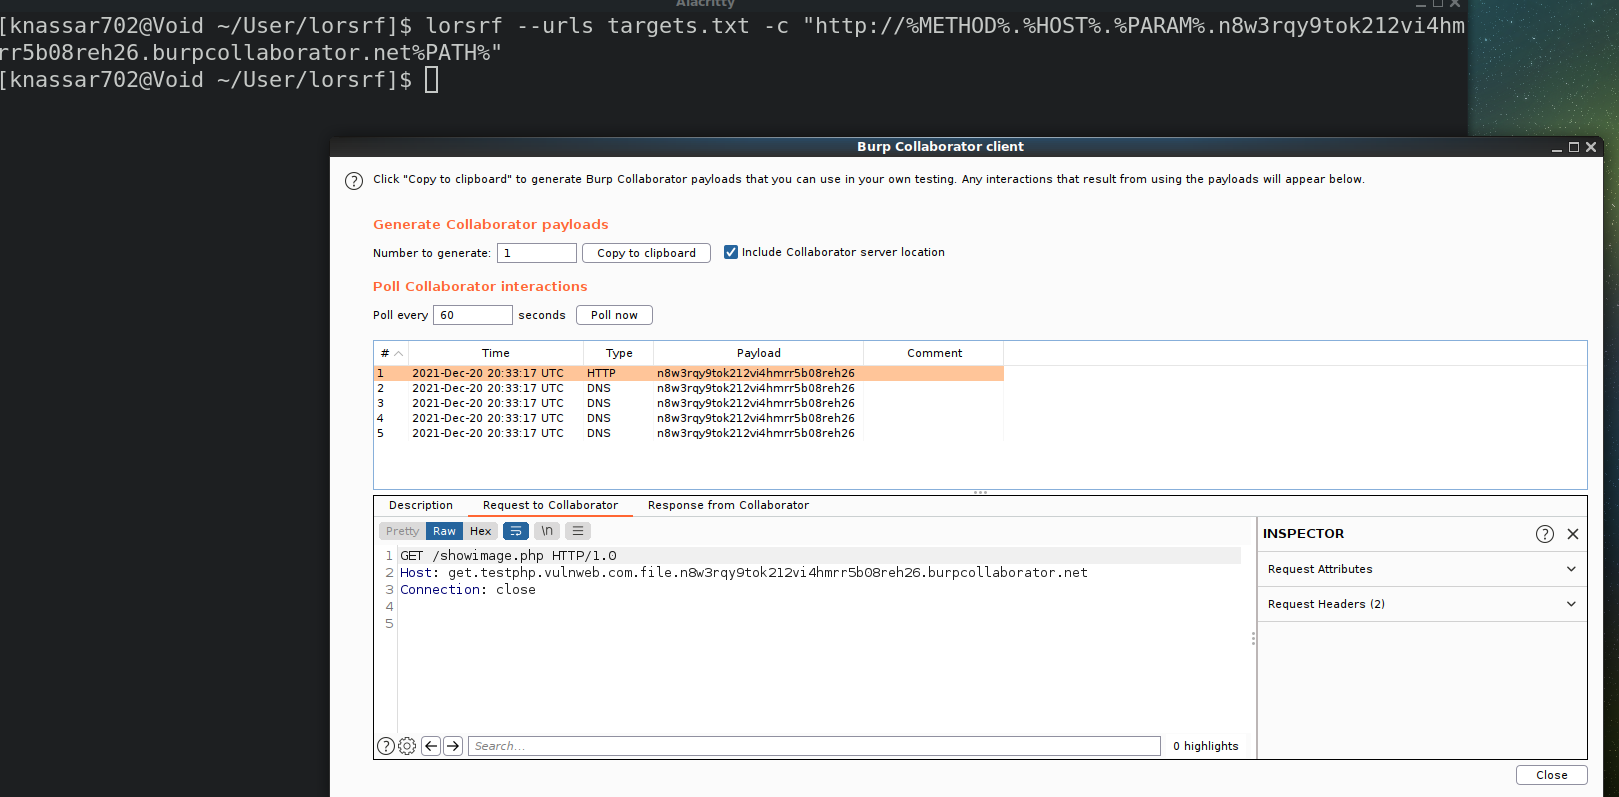 mindpatch/lorsrf
Fast CLI tool to find the parameters that can be used to find SSRF or Out-of-band resource load :artificial_satellite: :crab:
 r00tkitsmm/pishi
Pishi is a code coverage tool like kcov for macOS.
 sn1r/forbidden-buster
A tool designed to automate various techniques in order to bypass HTTP 401 and 403 response codes and gain access to unauthorized areas in the…
 microsoft/restler-fuzzer
RESTler is the first stateful REST API fuzzing tool for automatically testing cloud services through their REST APIs and finding security and…
 holo-routing/holo
Rust-based routing protocol suite implementing BGP, OSPF, IS-IS, RIP, and VRRP with YANG-modeled configuration, gNMI/gRPC automation, and built-in…
 oxagast/ansvif
A Not So Very Intelligent Fuzzer: An advanced fuzzing framework designed to find vulnerabilities in C/C++ code.
 nu11secur1ty/insect
High-performance web path discovery and directory brute-forcing tool. Discovers hidden files, directories, and endpoints using customizable…
 libnet/nemesis
A command-line network packet crafting and injection utility
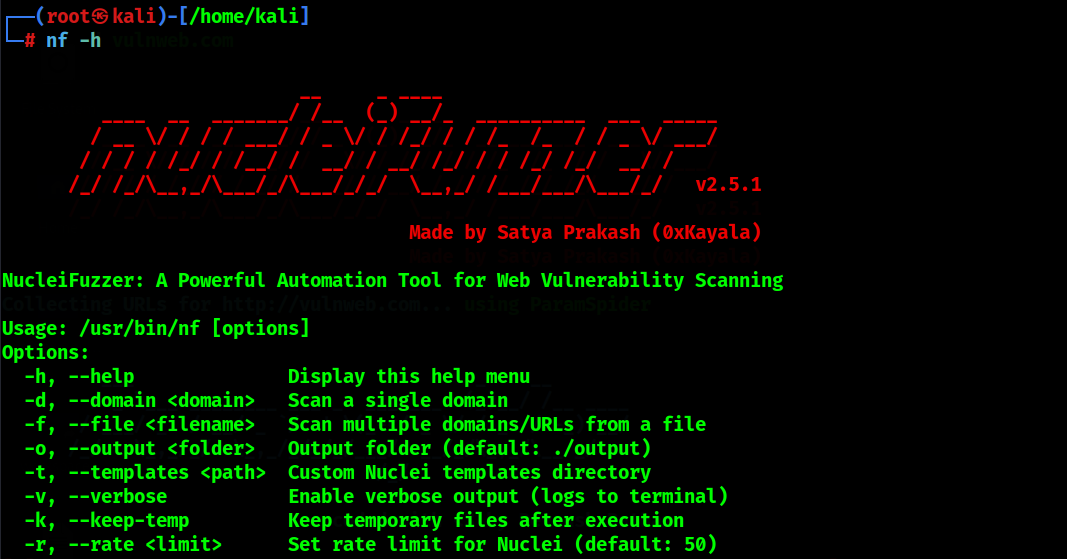 0xkayala/nucleifuzzer
Automated web vulnerability scanner combining URL discovery tools (ParamSpider, waybackurls, gauplus, hakrawler, katana) with Nuclei fuzzing…
 juanschallibaum/cve-2024-38473-nuclei-template
Nuclei template to detect Apache servers vulnerable to CVE-2024-38473
 zenzue/cve-2024-38063-poc
potential memory corruption vulnerabilities in IPv6 networks.
 vighnesh91/-logicsentry-ai
Offline SAST/DAST triage engine that parses source code and replays HAR traffic to detect business-logic flaws, BOLA, race conditions, and privilege…
 googleprojectzero/brokentype
TrueType and OpenType font fuzzing toolset