
CVE-2023-40296
 halcy0nic/cve-2023-40296
Proof of Concept for CVE-2023-40296
binary-exploitationcode-analysisexploitation+3
halcy0nic/cve-2023-40296Proof of Concept for CVE-2023-40296
 halcy0nic/cve-2022-44318
Proof of concept for CVE-2022-44318
 halcy0nic/cve-2022-34556
Proof of concept for CVE-2022-34556
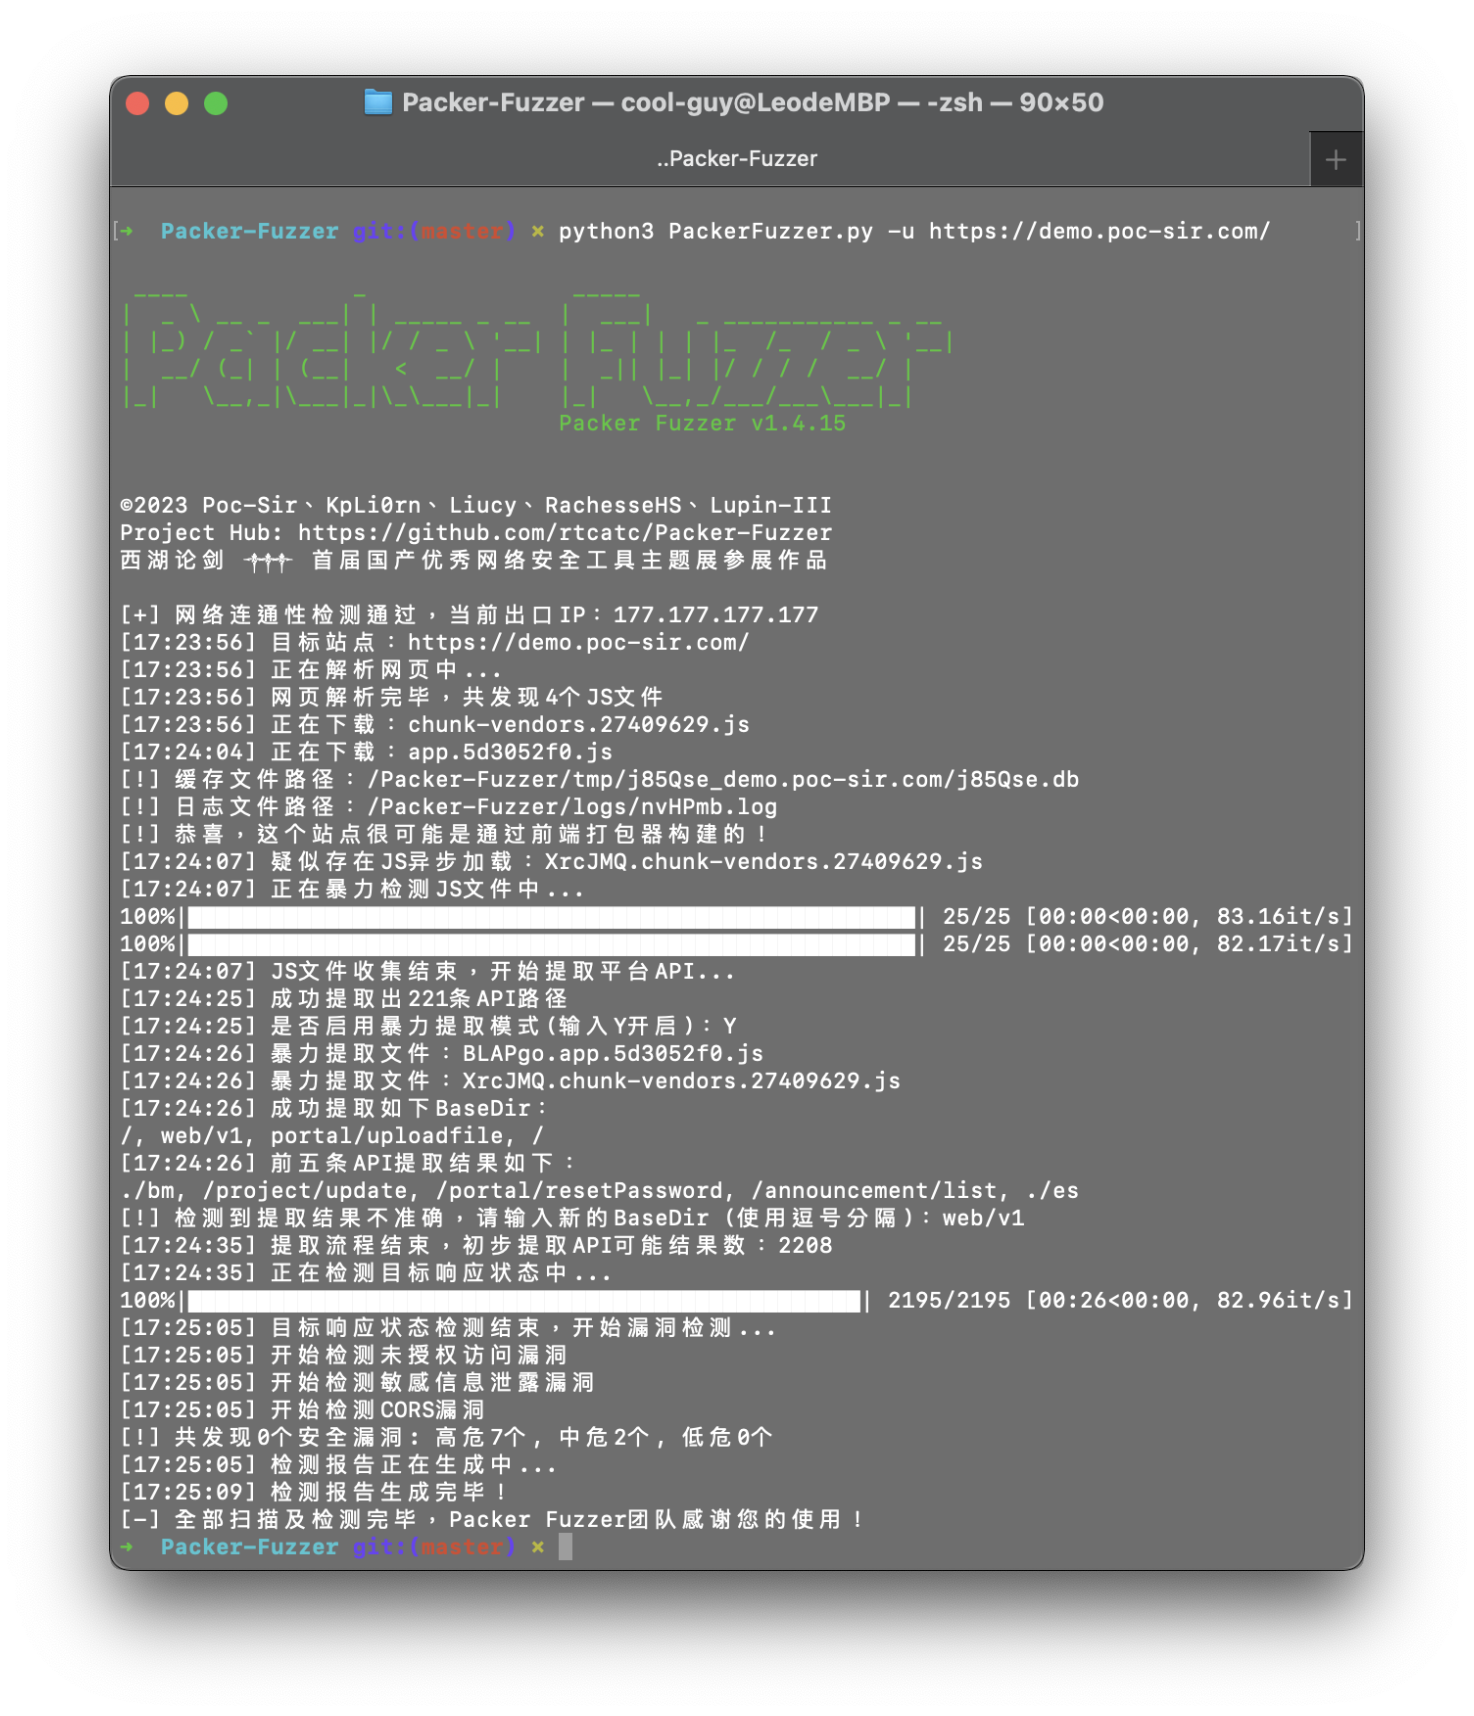 rtcatc/packer-fuzzer
Packer Fuzzer is a fast and efficient scanner for security detection of websites constructed by javascript module bundler such as Webpack.
 uni-due-syssec/efcf-framework
EF/CF - Extremely Fast smart Contract Fuzzing
 bettercap/bettercap
The Swiss Army knife for 802.11, BLE, HID, CAN-bus, IPv4 and IPv6 networks reconnaissance and MITM attacks.
 vigolium/vigolium
Vigolium - High-fidelity vulnerability scanner fusing agentic AI with native speed, modularity, and precision
 hahwul/gori
A fast, keyboard-driven HTTP intercepting proxy and hacking & pentesting toolkit for the terminal.
 akha-security/akca
Evidence-oriented DAST scanner in Go that crawls web apps and APIs, then runs adaptive SQLi, XSS, RCE, SSRF, and auth checks with replayable proof.
 sjkim1127/reversecore_mcp
A security-first MCP server that empowers AI agents to perform automated reverse engineering, malware analysis, forensics, vulnerability research,…
 r3fr4kt/popcorn-tjnull-oscp-
Popcorn HTB write-up covering advanced directory fuzzing, file upload bypass via magic numbers/extension spoofing using Burp Suite, and privilege…
 trailofbits/polytracker
An LLVM-based instrumentation tool for universal taint tracking, dataflow analysis, and tracing.
 slayerkkkk/cve-2025-46817-poc
C-based exploit for CVE-2025-46817, a Redis integer overflow vulnerability, enabling crash detection and potential RCE via Lua unpack() payload.
 hantwister/fakedellom
A fake host that can be "managed" by Dell OMSA, getting you past the login screen.
 google/path-auditor
Runtime libc function auditor that detects file access race conditions and symlink vulnerabilities by hooking filesystem syscalls via LD_PRELOAD,…
 sentinel-one/peafl64
Static Binary Instrumentation tool for Windows x64 executables
 dwisiswant0/ppfuzz
A fast tool to scan client-side prototype pollution vulnerability written in Rust. 🦀