

WebSocketTurboIntruder
 d0ge/websocketturbointruder
Burp Suite extension for fuzzing WebSocket messages with custom Python code, supporting multiple engines, HTTP middleware routing, and response…
api-security-testingfuzzingpenetration-testing+5
12
d0ge/websocketturbointruderBurp Suite extension for fuzzing WebSocket messages with custom Python code, supporting multiple engines, HTTP middleware routing, and response…
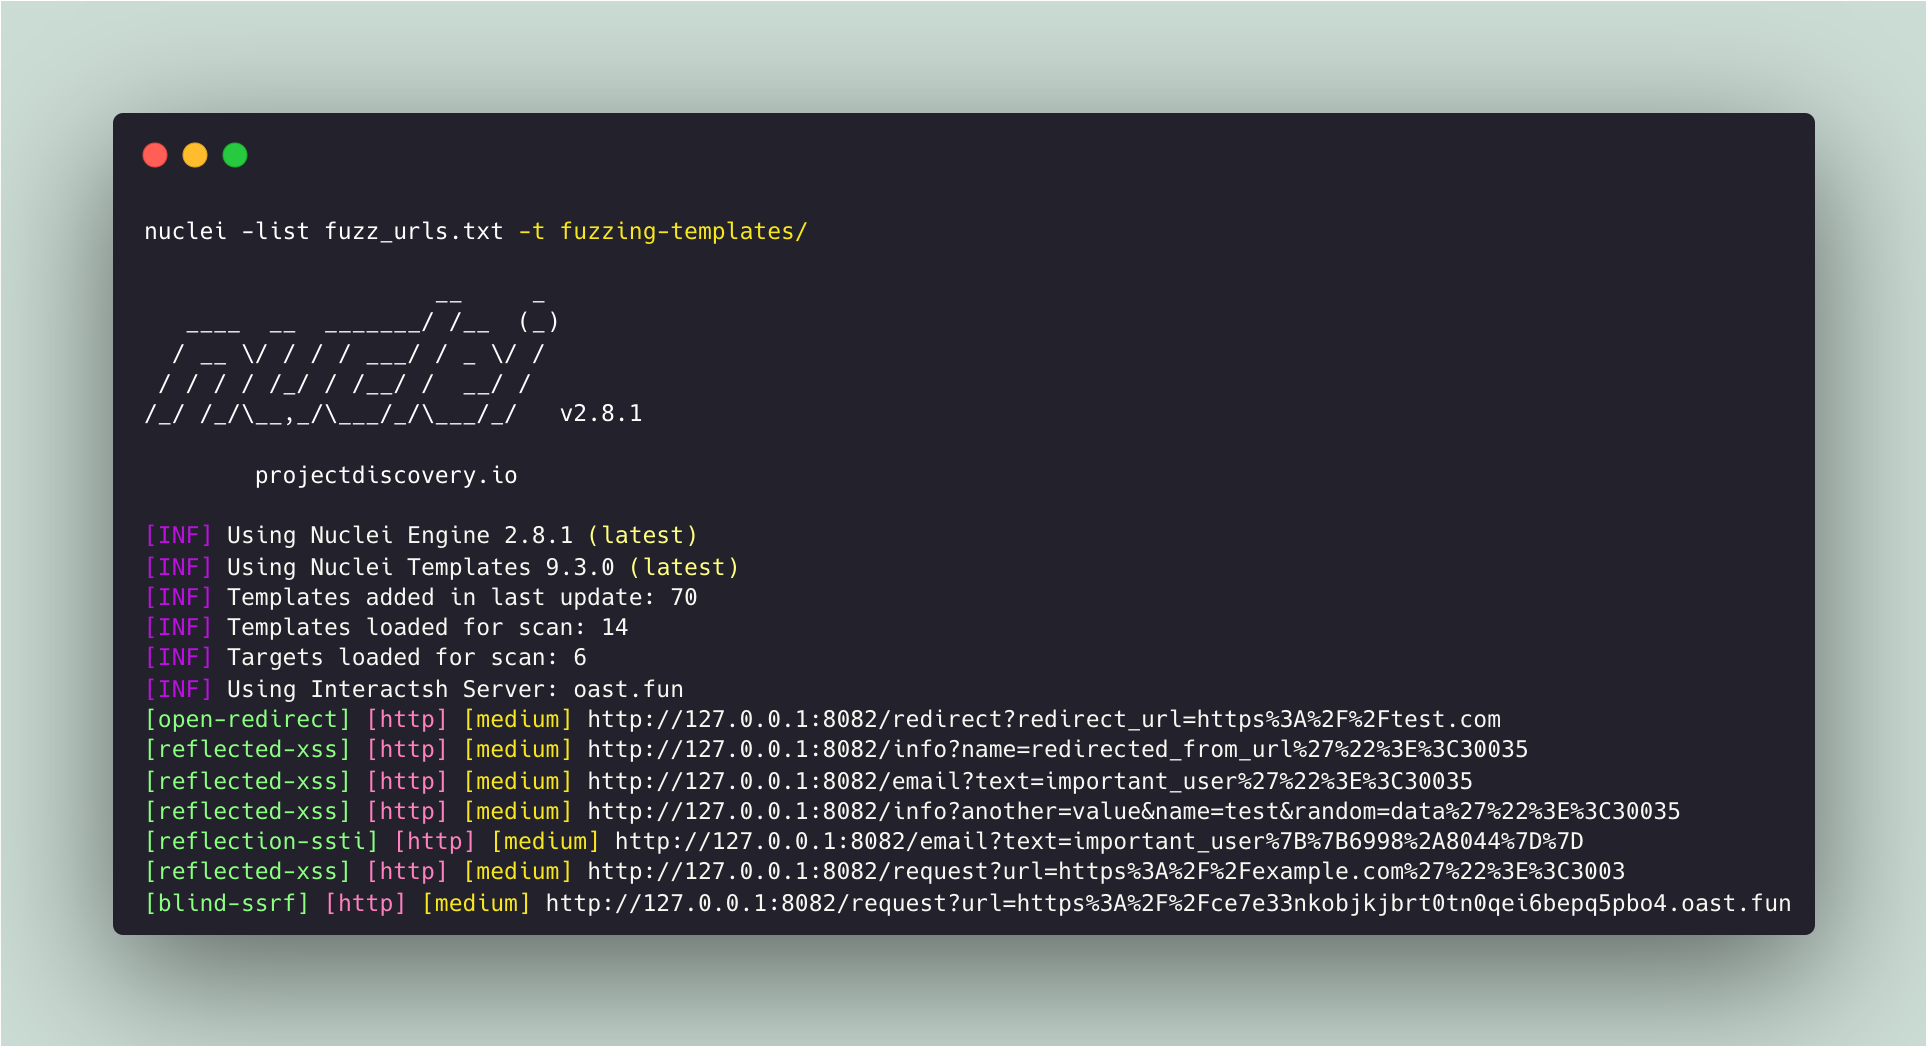 projectdiscovery/fuzzing-templates
Community curated list of nuclei templates for finding "unknown" security vulnerabilities.
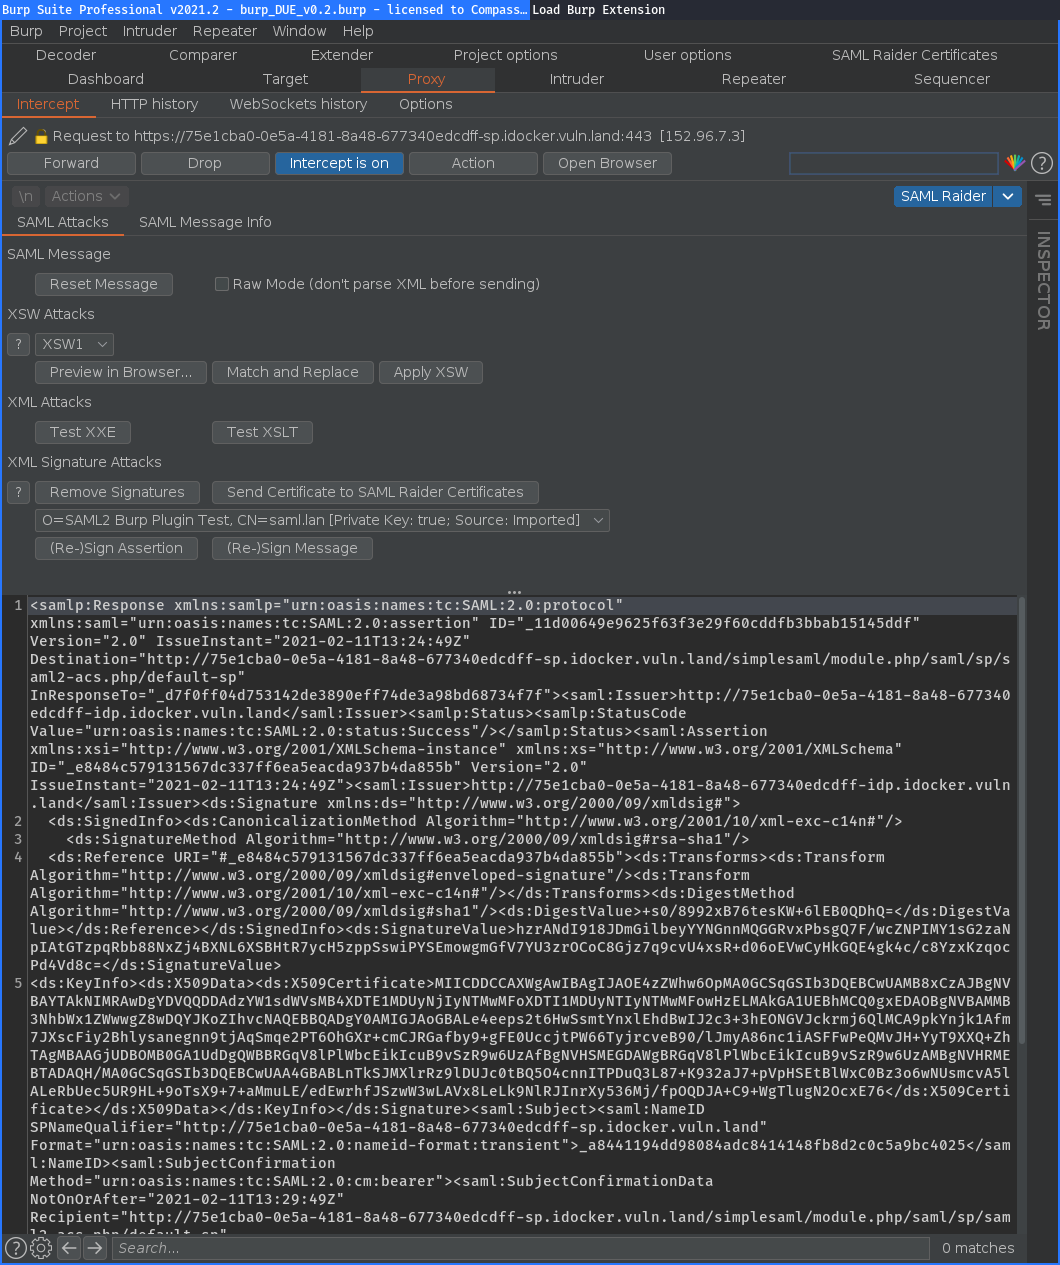 compasssecurity/samlraider
SAML2 Burp Extension
 mohammadalimehri/cve-2021-44790-lab
Dockerized Apache mod_lua lab with a Python PoC reproducing the CVE-2021-44790 multipart boundary buffer overflow for local defensive testing and…
 jaf0rk/cve-2026-3909
Proof-of-concept exploit for CVE-2026-3909, a Chromium Skia out-of-bounds vulnerability, with patches and crash analysis for reliable triggering in…
 abrewer251/cve-2024-38475_sonicboom_apache_url_traversal_poc
Proof-of-concept scanner for CVE-2024-38475 (SonicBoom) Apache URL traversal. Automates TLS negotiation, directory scanning, traversal verification,…
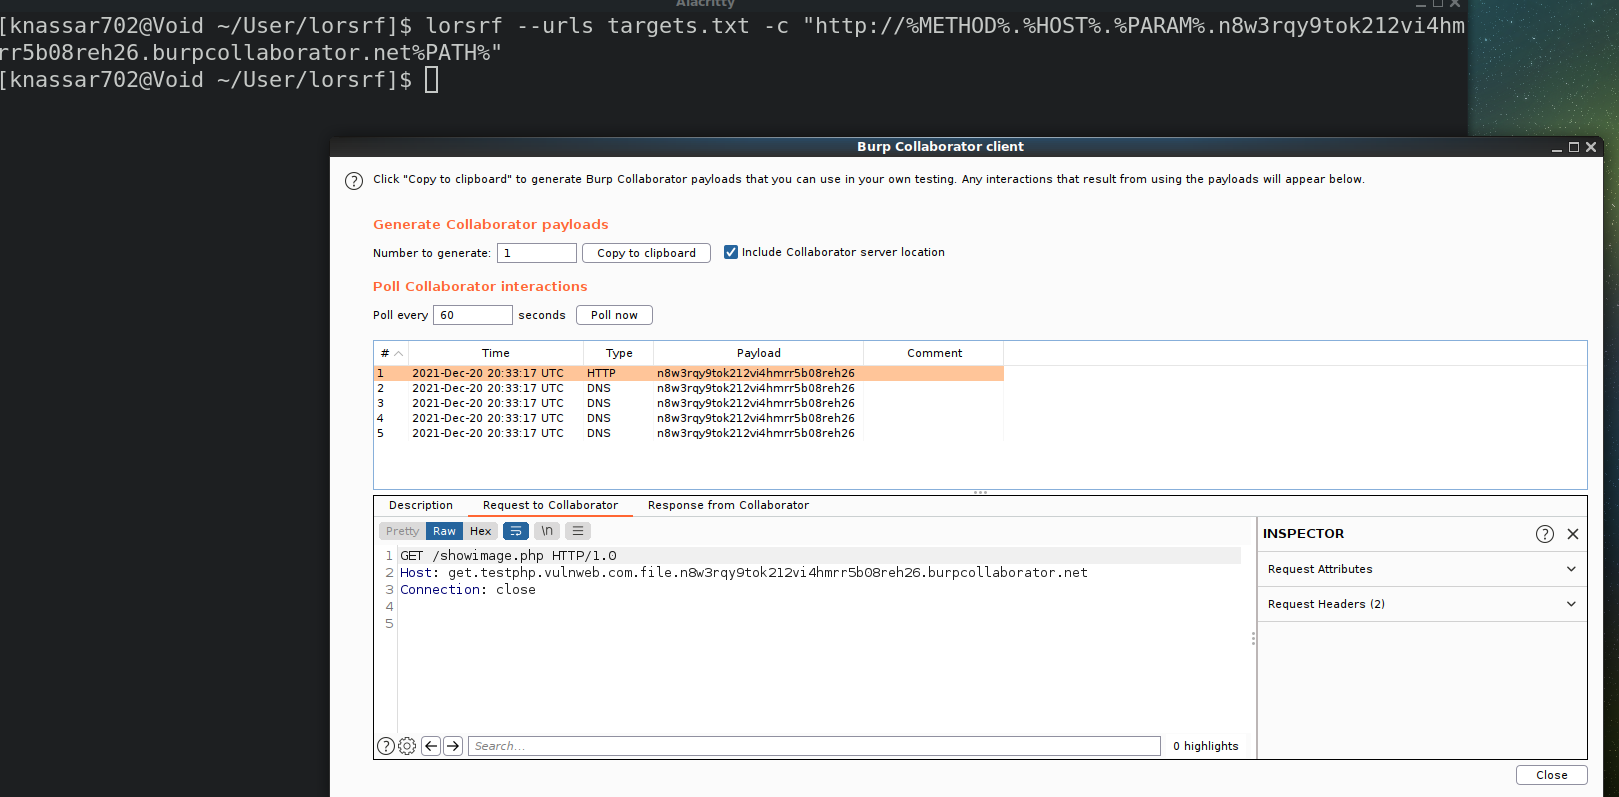 mindpatch/lorsrf
Fast CLI tool to find the parameters that can be used to find SSRF or Out-of-band resource load :artificial_satellite: :crab:
 ticarpi/jwt_tool
:snake: A toolkit for testing, tweaking and cracking JSON Web Tokens
 s0md3v/arjun
HTTP parameter discovery tool that finds valid query parameters for URL endpoints using a large dictionary, supporting GET/POST/JSON/XML requests,…
 microsoft/restler-fuzzer
RESTler is the first stateful REST API fuzzing tool for automatically testing cloud services through their REST APIs and finding security and…
 swisskyrepo/graphqlmap
Security module for php7 and php8 - Killing bugclasses and virtual-patching the rest!
 endava/cats
Automated REST API fuzzer and negative testing tool for OpenAPI endpoints. Generates, runs, and reports thousands of self-healing tests with no…
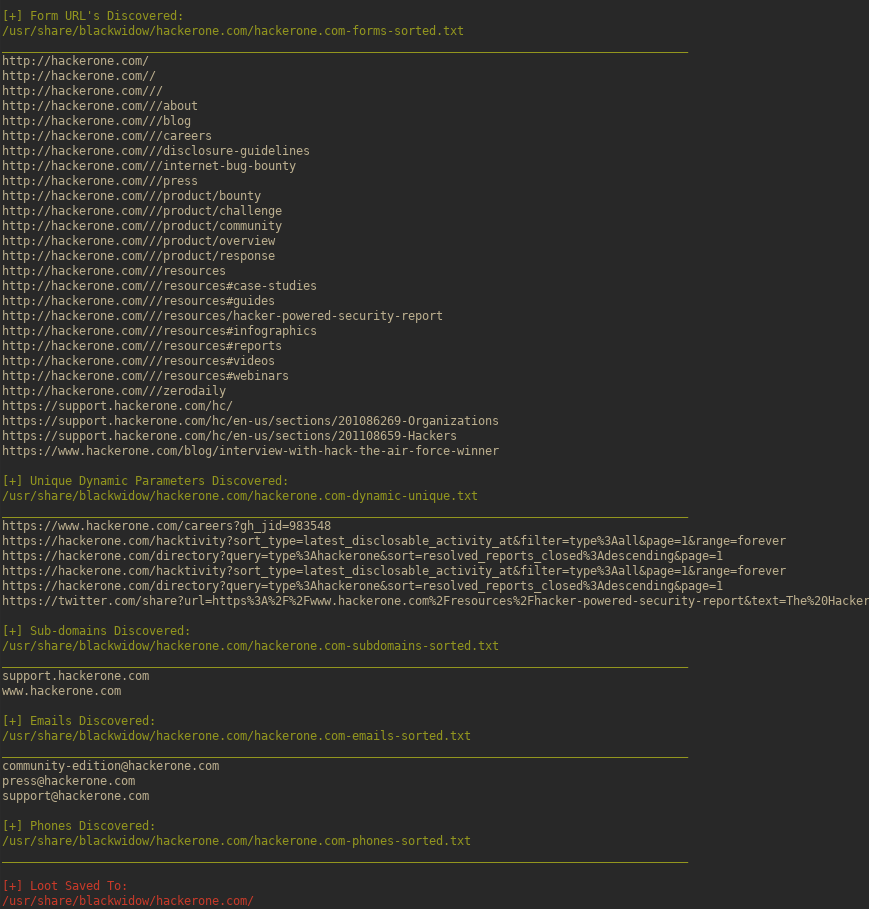 1n3/blackwidow
A Python based web application scanner to gather OSINT and fuzz for OWASP vulnerabilities on a target website.
 albinowax/activescanplusplus
Burp Suite extension that extends active and passive scanning with checks for host header attacks, XXE, expression language injection, shellshock and…
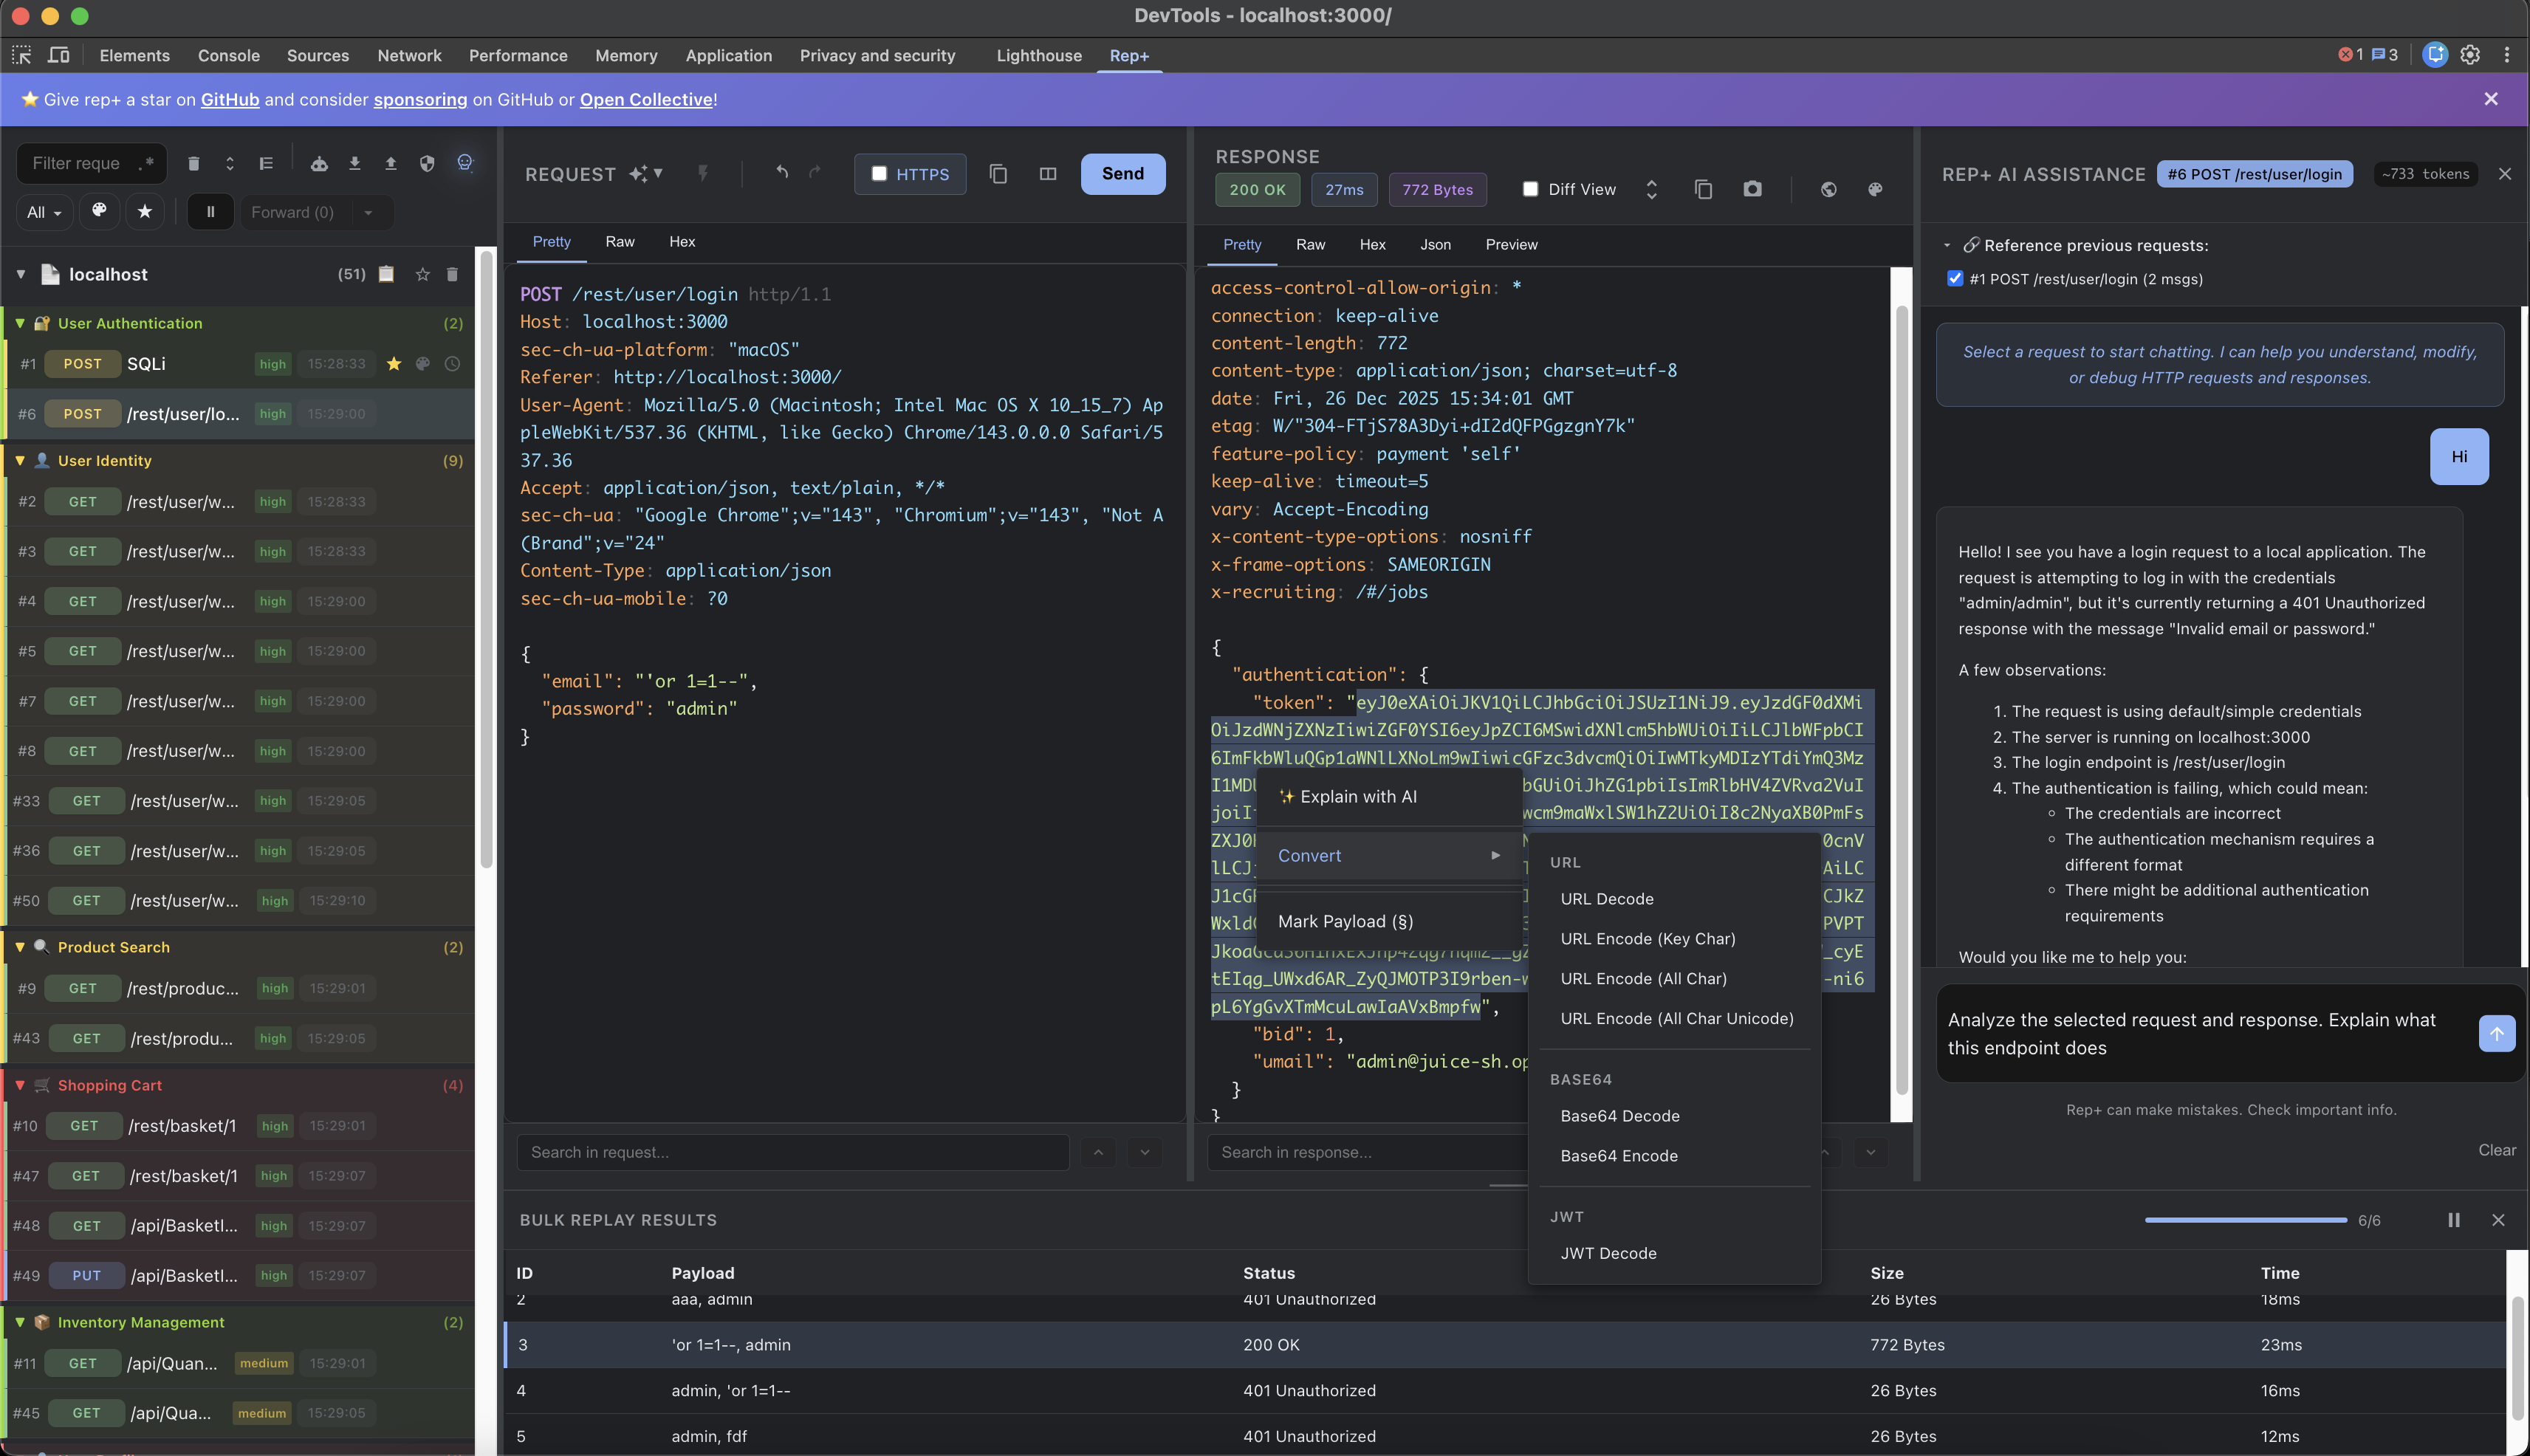 repplus/rep-chrome
rep+ — Burp-style HTTP Repeater for Chrome DevTools with built‑in AI to explain requests and suggest attacks
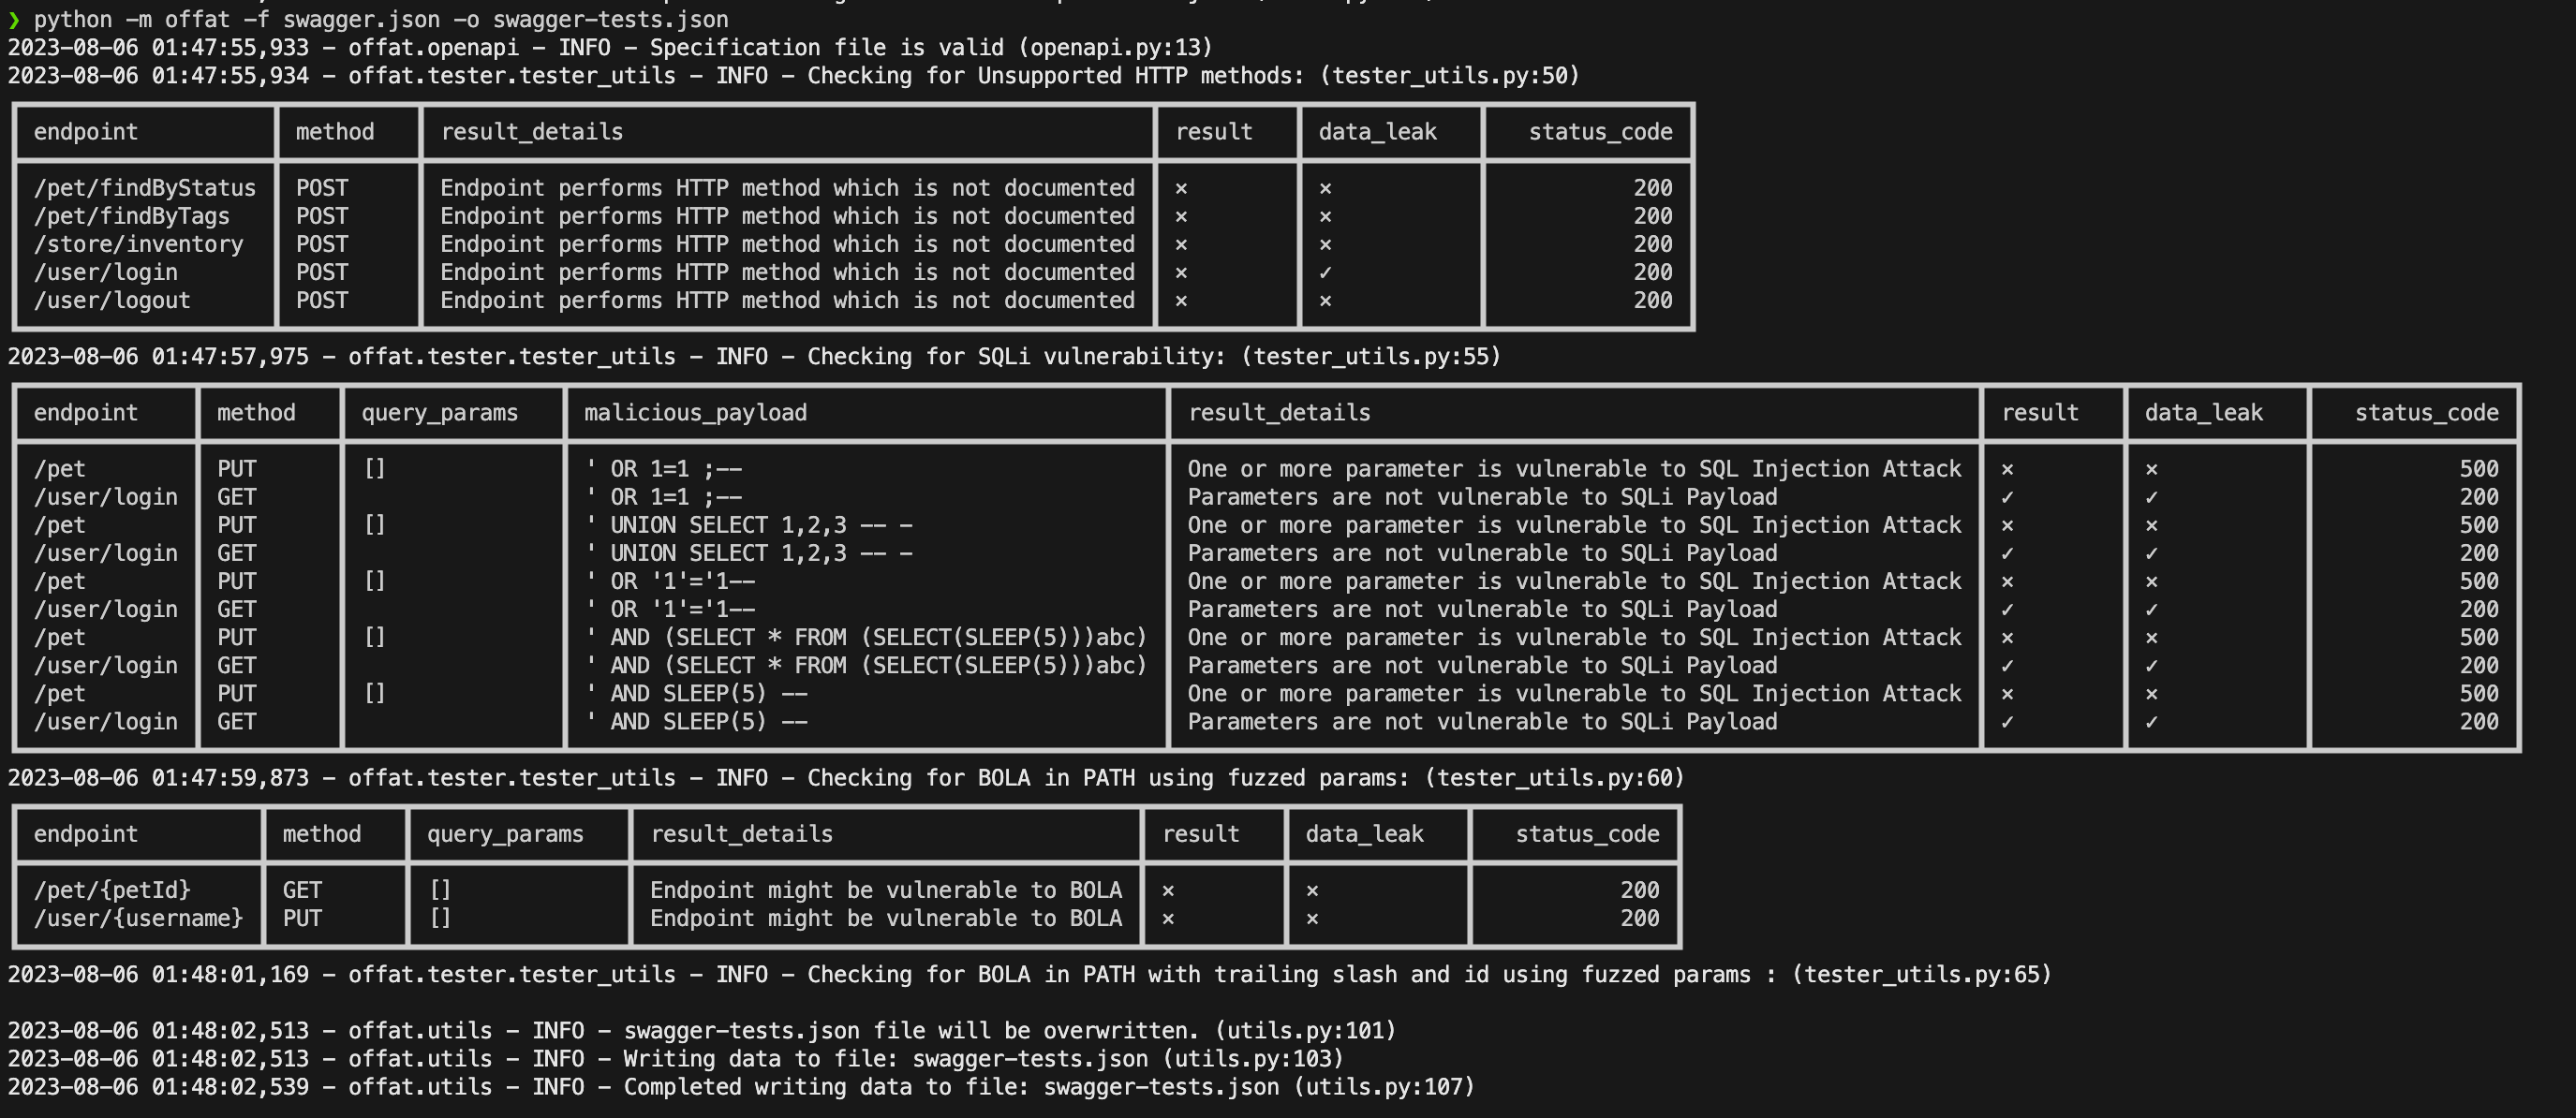 owasp/offat
Automated API security testing tool that generates tests from OpenAPI specs, fuzzes inputs, and checks for OWASP API Top 10 vulnerabilities including…
 noptrix/lulzbuster
A multithreaded, very fast and smart HTTP(S) directory and file bruteforcer written in C on top of libcurl
 tno-s3/wuppiefuzz
A coverage-guided REST API fuzzer developed on top of LibAFL