

OFFAT
 owasp/offat
Automated API security testing tool that generates tests from OpenAPI specs, fuzzes inputs, and checks for OWASP API Top 10 vulnerabilities including…
api-securityapi-security-testingfuzzing+2
6633h 23m ago
owasp/offatAutomated API security testing tool that generates tests from OpenAPI specs, fuzzes inputs, and checks for OWASP API Top 10 vulnerabilities including…
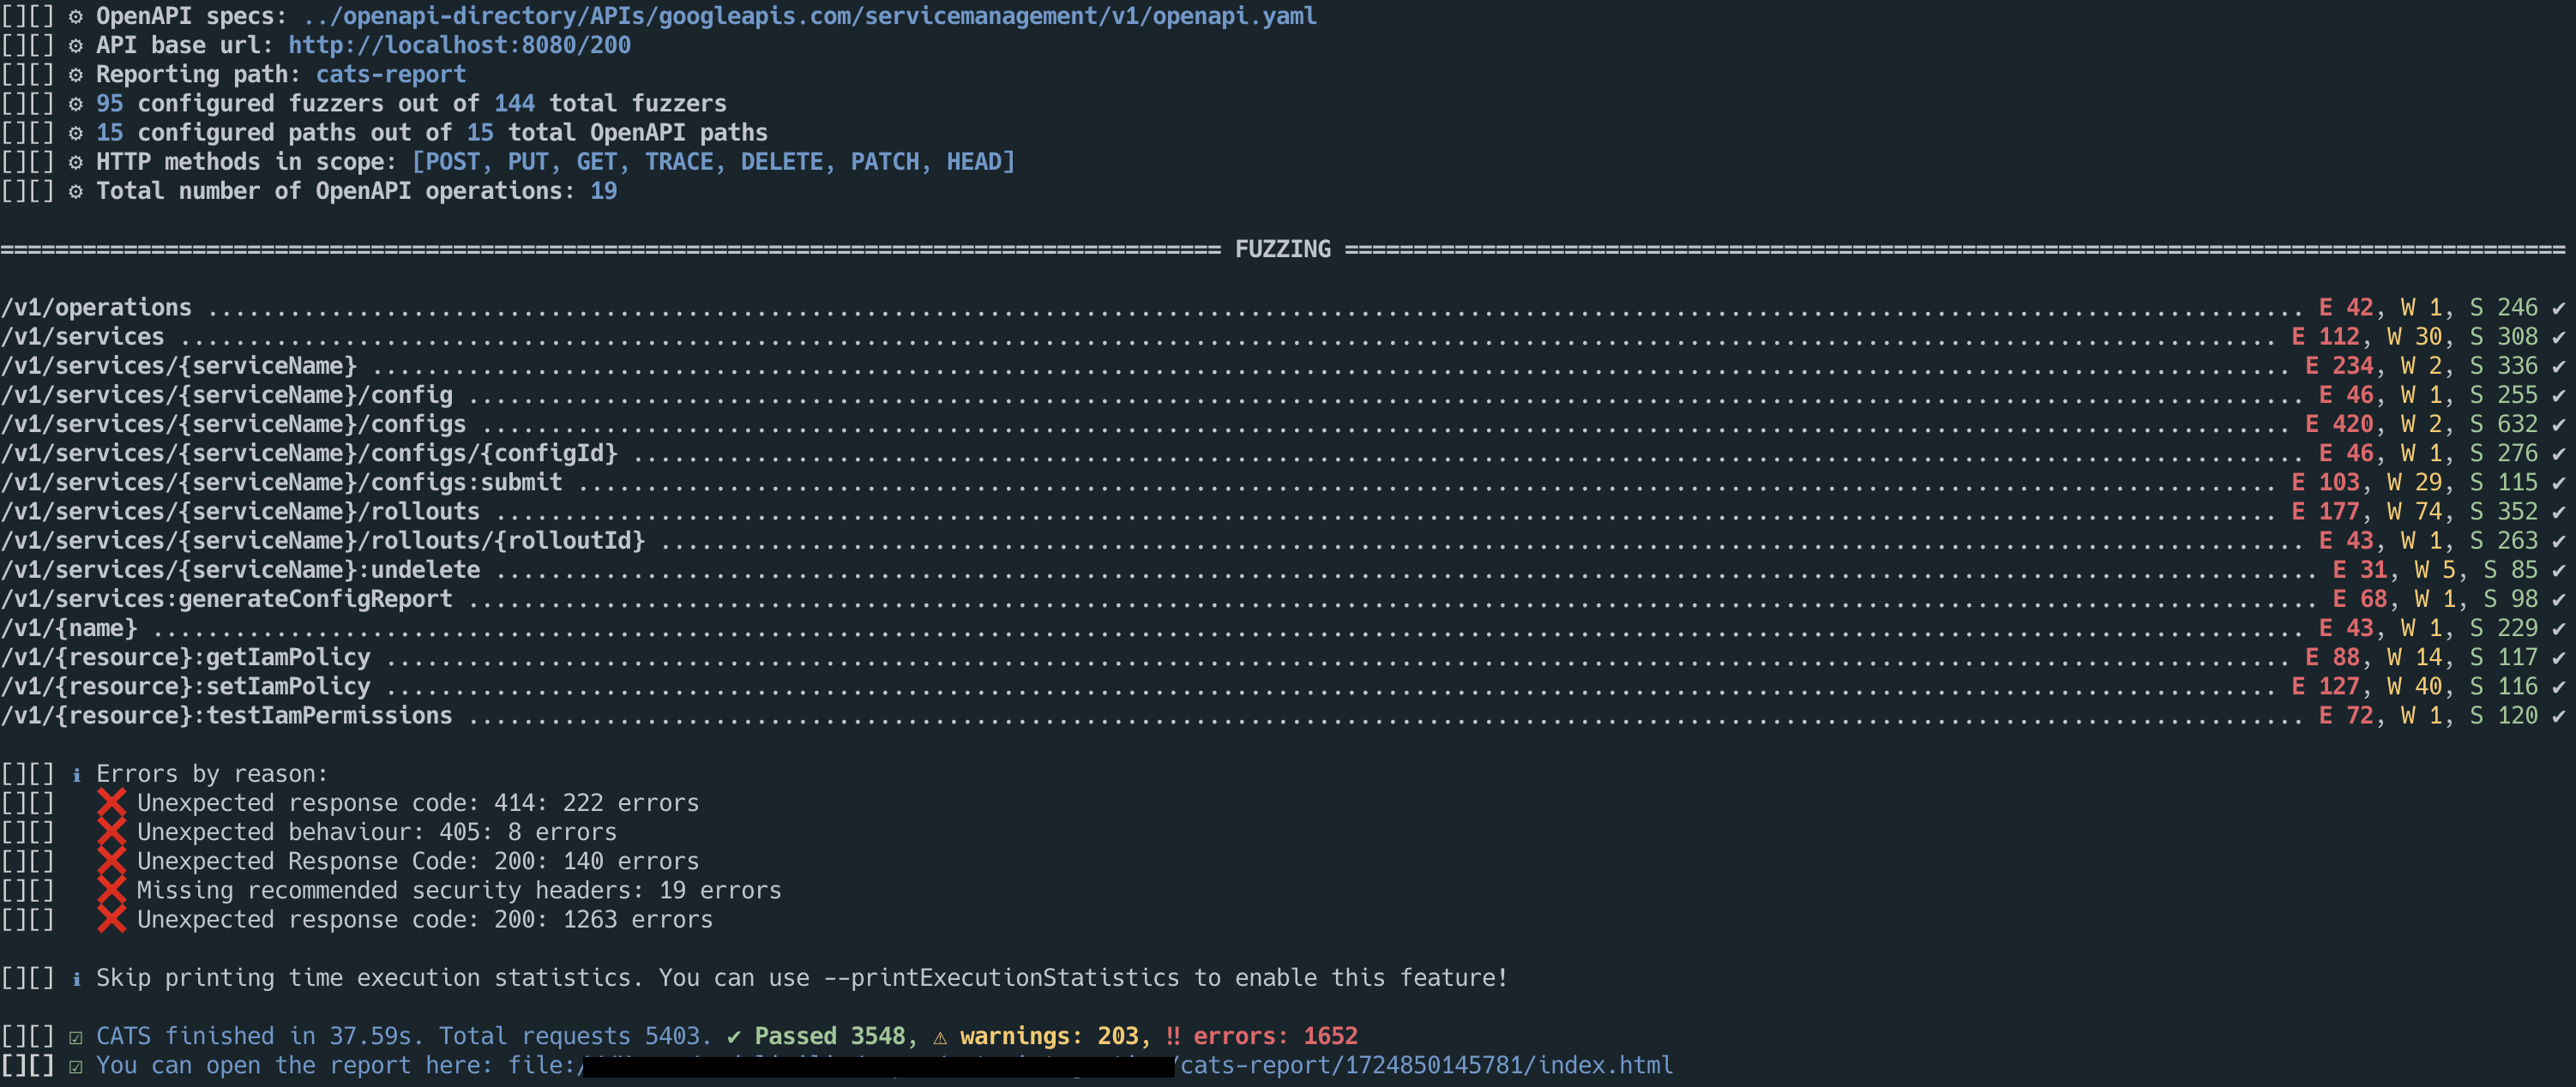 endava/cats
Automated REST API fuzzer and negative testing tool for OpenAPI endpoints. Generates, runs, and reports thousands of self-healing tests with no…
 foxcornlab/thc-bloodmiami
AI chat-box pentesting tool in C: fires language (SQLi/NoSQL/XSS/SSTI) and prompt injection payloads at chat interfaces and flags the ones that bite
 sqlancer/sqlancer
Automated testing to find logic and performance bugs in database systems
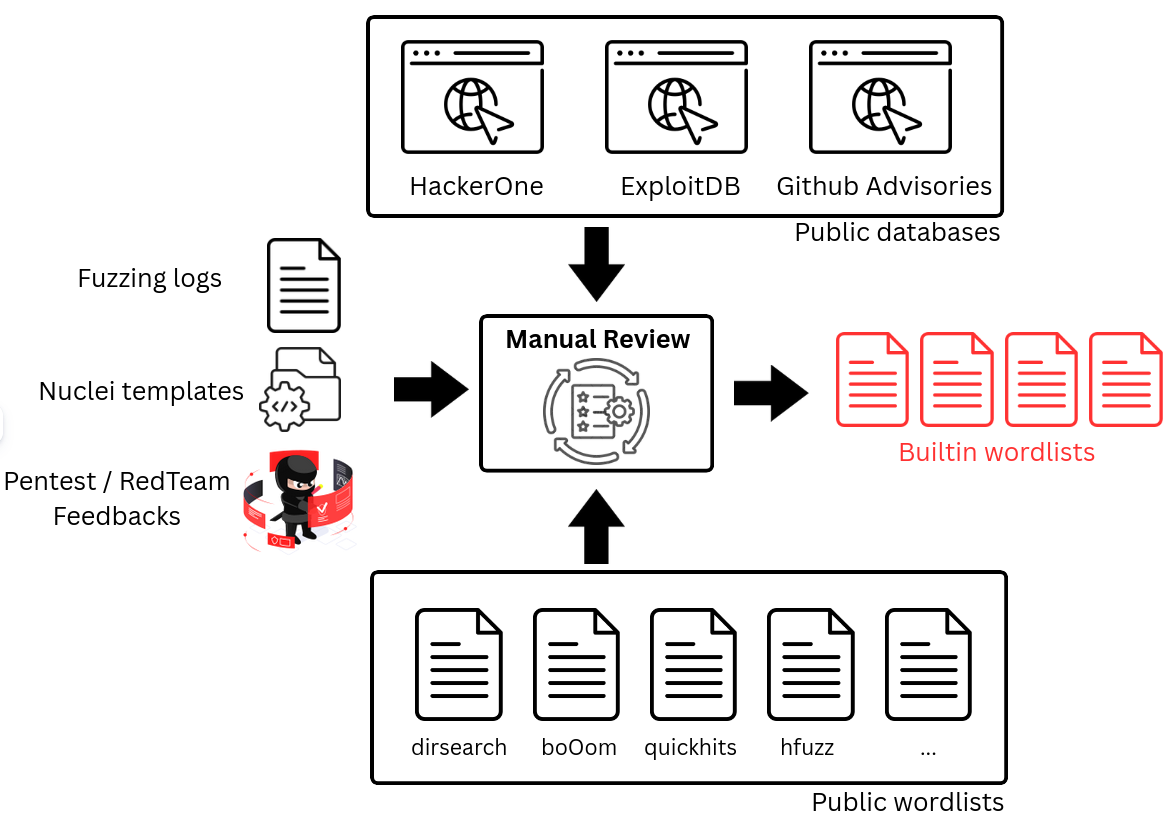 synacktiv/dicozorus
A tool to generate and maintain wordlists for Web fuzzing.
 reversenseorg/dexcalibur
[Official] Android reverse engineering tool focused on dynamic instrumentation automation leveraging Frida. It disassembles dex, analyzes it…
 meliht/mr.sip
SIP Security Assessment Framework for VoIP Pentesters. Presented at DEFCON, BlackHat & Offzone.
 tegal1337/pocketpentester
Offline-first Android offensive security toolkit with 21 modules for recon, port scanning, subdomain enumeration, SQLi/XSS/JWT exploitation, payload…
 vladko312/sstimap
Automatic SSTI detection tool with interactive interface
 r00tkitsmm/pishi
Pishi is a code coverage tool like kcov for macOS.
 teycir/burpapisecuritysuite
Burp Suite extension for API security testing with 15 attack types, 108+ payloads, intelligent fuzzing, BOLA/IDOR detection, AI integration, and…
 piratesshield/apiharvester
The one shot API attacker tool - finds the API url from the given root simulate the automated attacks
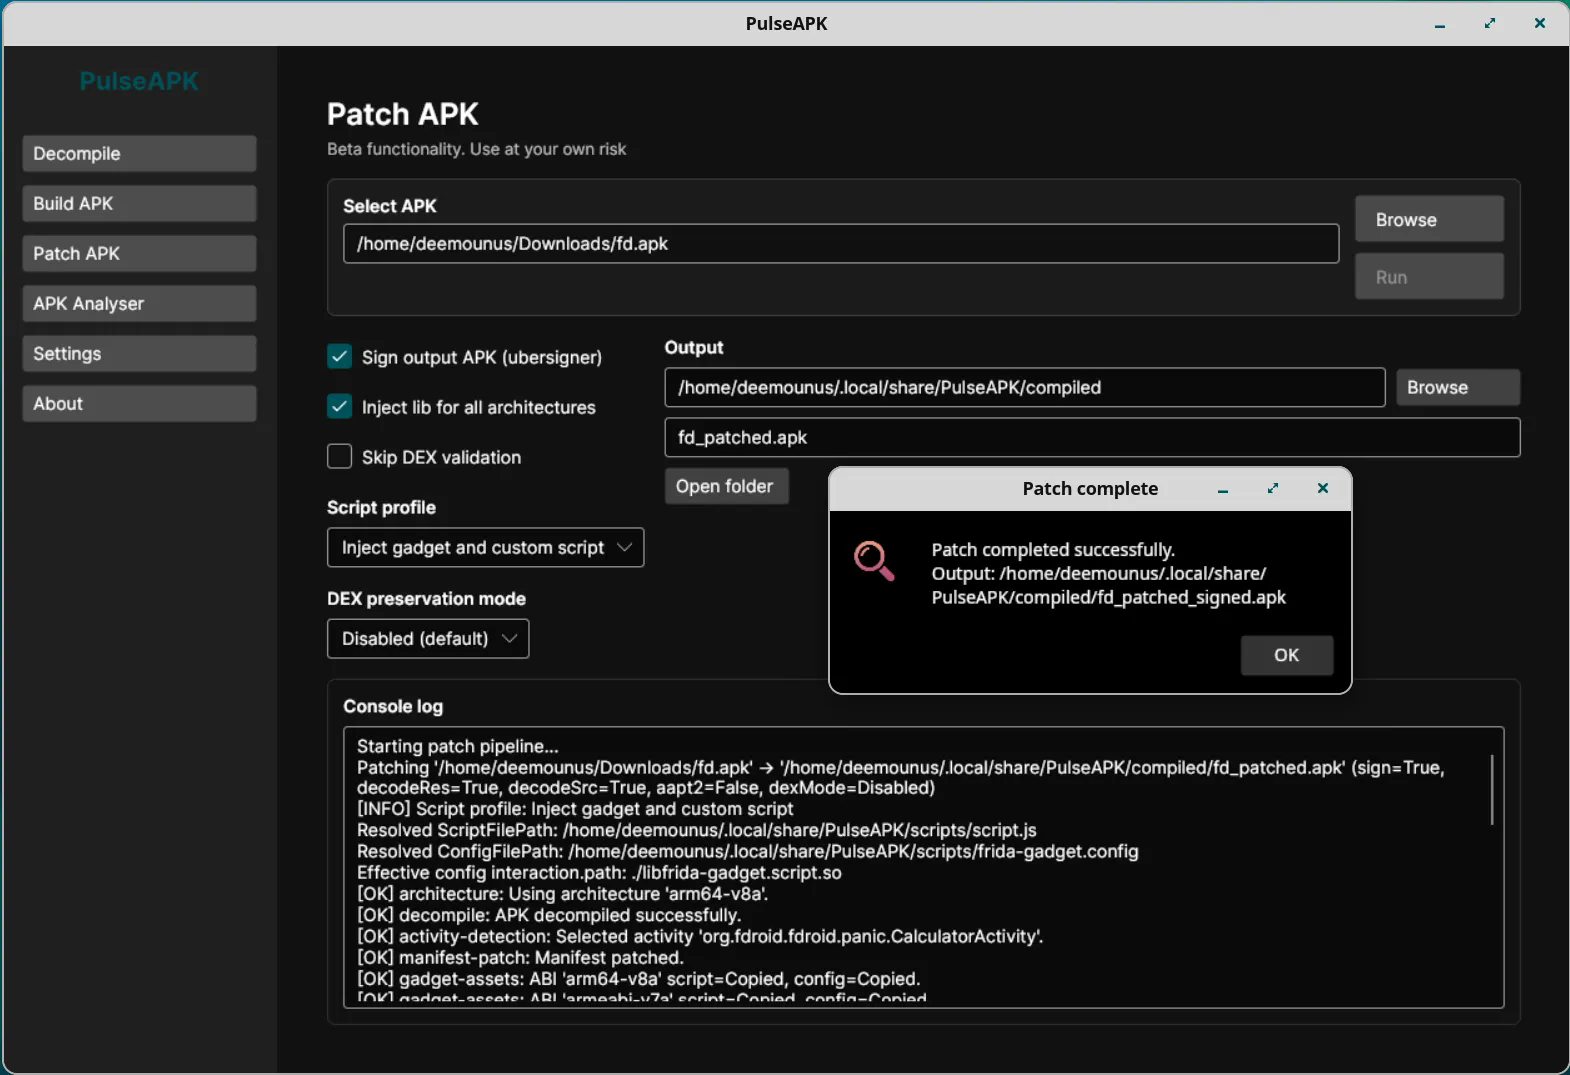 deemoun/pulseapk-core
PulseAPK Core: Cross-Platform tool for working with APK files: Decompilation, Analysis, Building
 nxenon/h2spacex
HTTP/2 Last Frame Synchronization (also known as Single Packet Attack) low Level Library / Tool based on Scapy + Exploit Timing Attacks
 aircrack-ng/mdk4
IEEE 802.11 Wi-Fi testing tool for protocol weakness exploitation, including beacon flooding, deauthentication, packet fuzzing, and IDS evasion.…
 trailofbits/polytracker
An LLVM-based instrumentation tool for universal taint tracking, dataflow analysis, and tracing.
 redcrazyghost/cve-2026-42945
Go-based exploit tool for CVE-2026-42945 (nginx HTTP/2) with detection, crash probing, command execution, and reverse shell capabilities for…
 hackmanit/tinja
TInjA is a CLI tool for testing web pages for template injection vulnerabilities and supports 44 of the most relevant template engines for eight…