
 libriscv/libloong
The fastest LoongArch sandbox


 safety-research/red-teaming-auto-mode
Research code for red-teaming AI auto-mode monitors, including simulation evals, fuzzing, and monitor implementations for Claude Code and Codex…
 kmkz/exploits
Original CVEs, exploit PoCs, and security advisories with detailed vulnerability chains, privilege escalation, and container escape techniques for…
 mda2av/http11probe
An open testing platform that probes HTTP/1.1 servers against RFC 9110/9112 requirements, smuggling vectors, and malformed input handling. Add your…
 provos/ironcurtain
A secure* runtime for autonomous AI agents. Policy from plain-English constitutions. (*https://ironcurtain.dev)
 panda-re/lava
LAVA: Large-scale Automated Vulnerability Addition
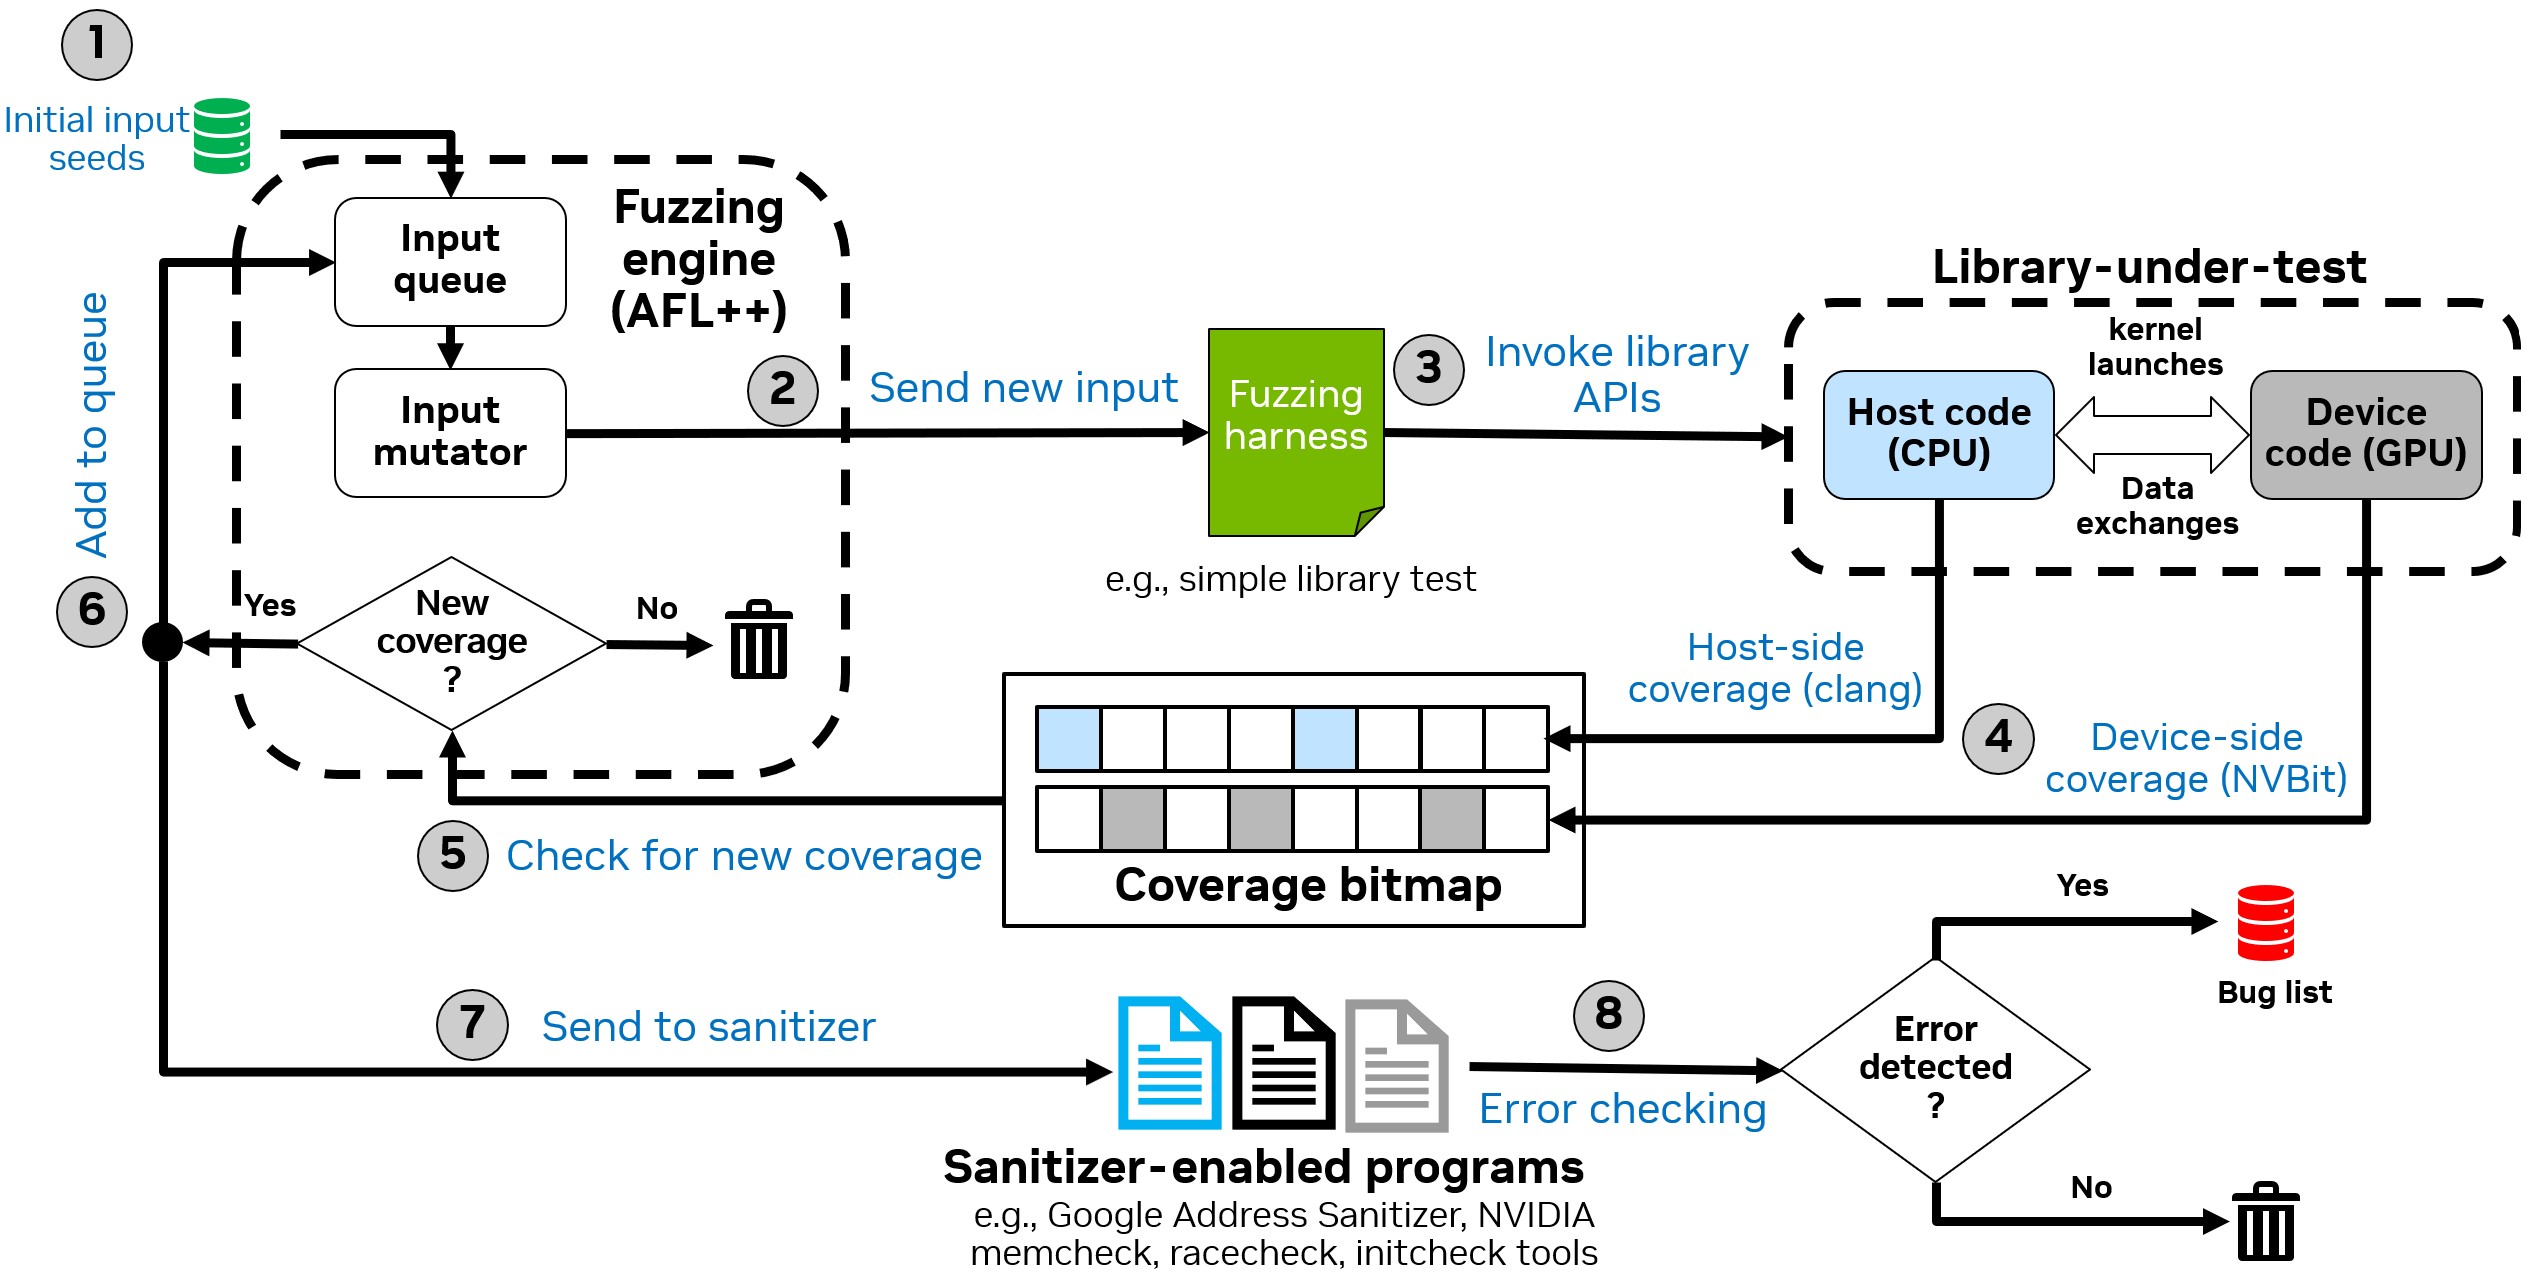 nvlabs/cufuzz
A GPU-oriented coverage-guided fuzzer for userland CUDA applications
 ivanesk315/cve-2026-42533
Docker lab reproducing CVE-2026-42533, a pre-auth nginx heap overflow and info leak via two-pass capture clobbering, with PoC scripts and patched…
 zardus/ctf-tools
Some setup scripts for security research tools.
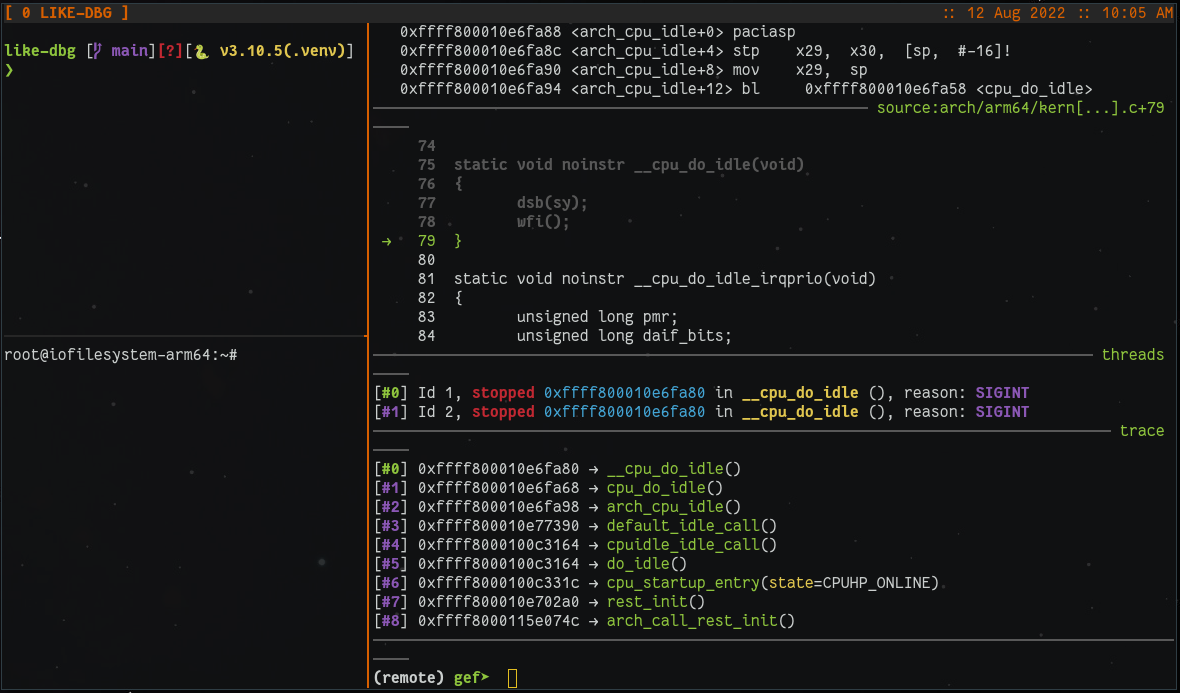 0xricksanchez/like-dbg
Fully dockerized Linux kernel debugging environment
 gokulapap/reconator
Automated reconnaissance framework with 17+ modules for subdomain enumeration, directory brute-forcing, JS/link mining, WAF fingerprinting, and…
 sunblaze-ucb/exploitgym
ExploitGym is a large-scale, realistic benchmark built from real-world vulnerabilities designed to evaluate AI agents' ability to develop exploits.
 trailofbits/trailmark
Build and query a graph database representation of source code