 provos/ironcurtain
A secure* runtime for autonomous AI agents. Policy from plain-English constitutions. (*https://ironcurtain.dev)


A secure* runtime for autonomous AI agents, where security policy is derived from a human-readable constitution.
*When someone writes "secure," you should immediately be skeptical. What do we mean by secure?
[!WARNING] Research Prototype. IronCurtain is an early-stage research project exploring how to make AI agents safe enough to be genuinely useful. APIs, configuration formats, and architecture may change. Contributions and feedback are welcome.
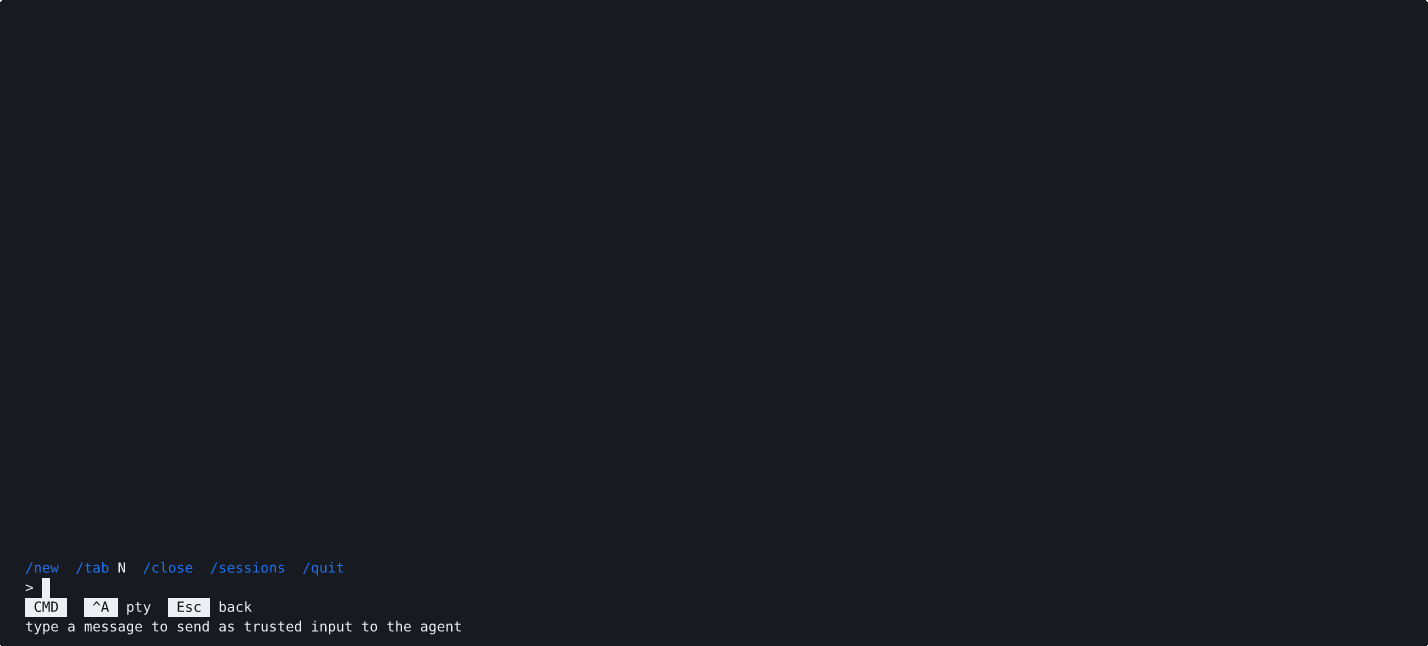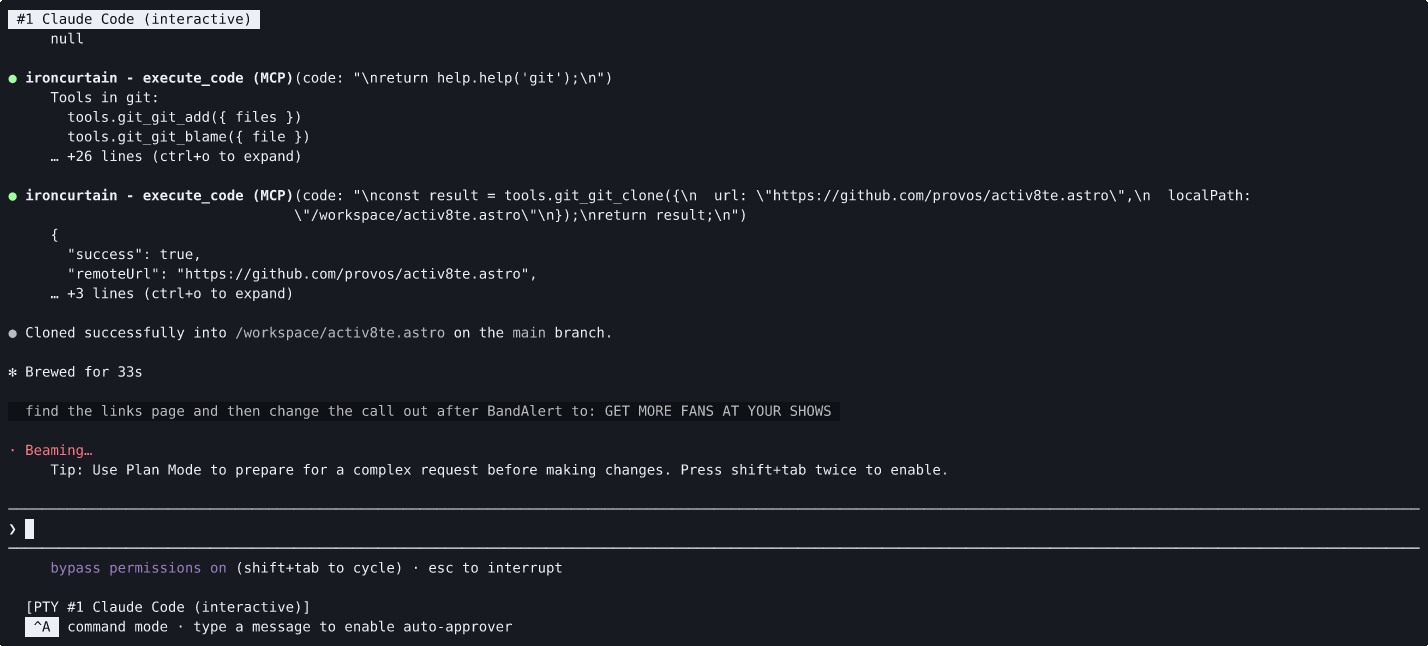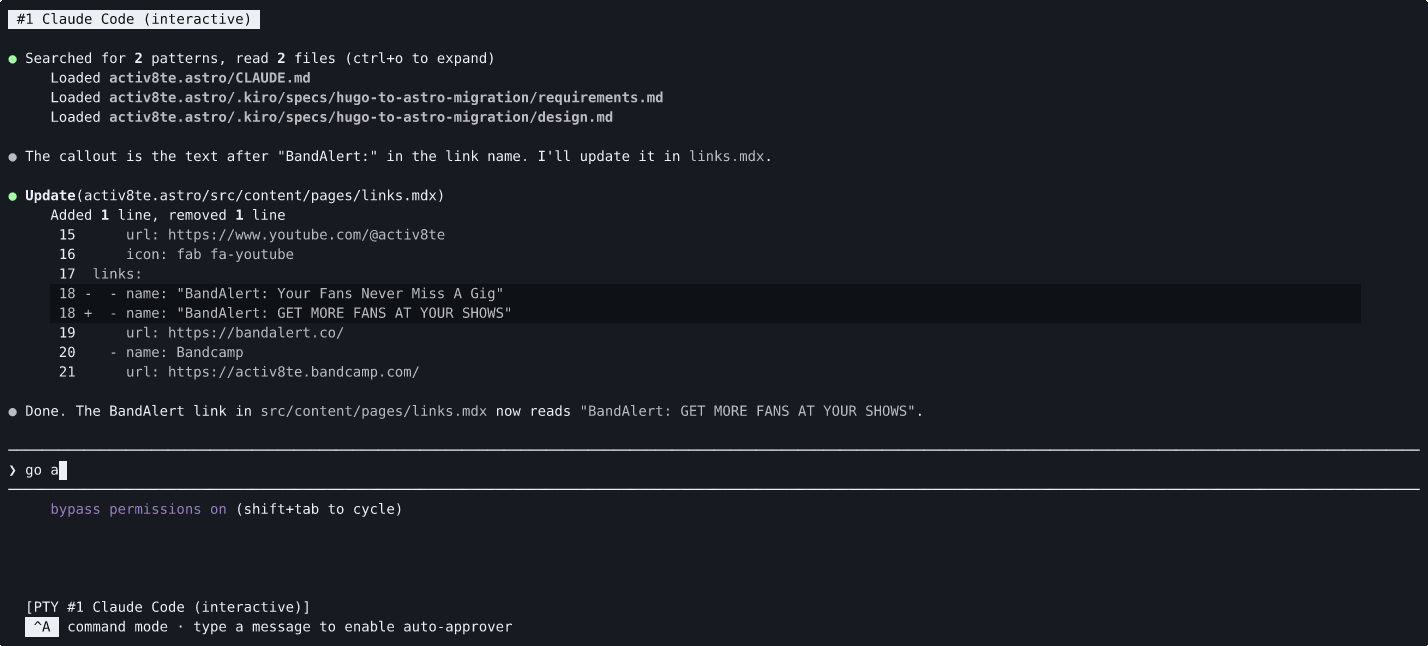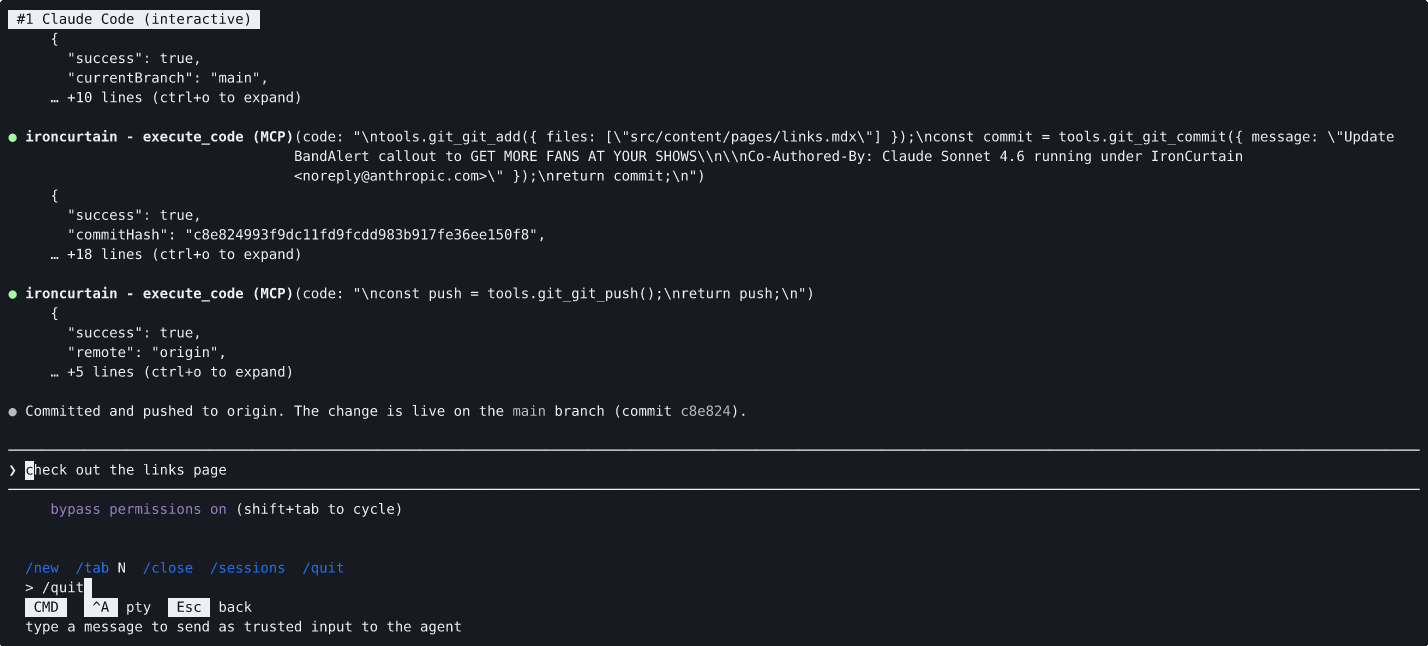
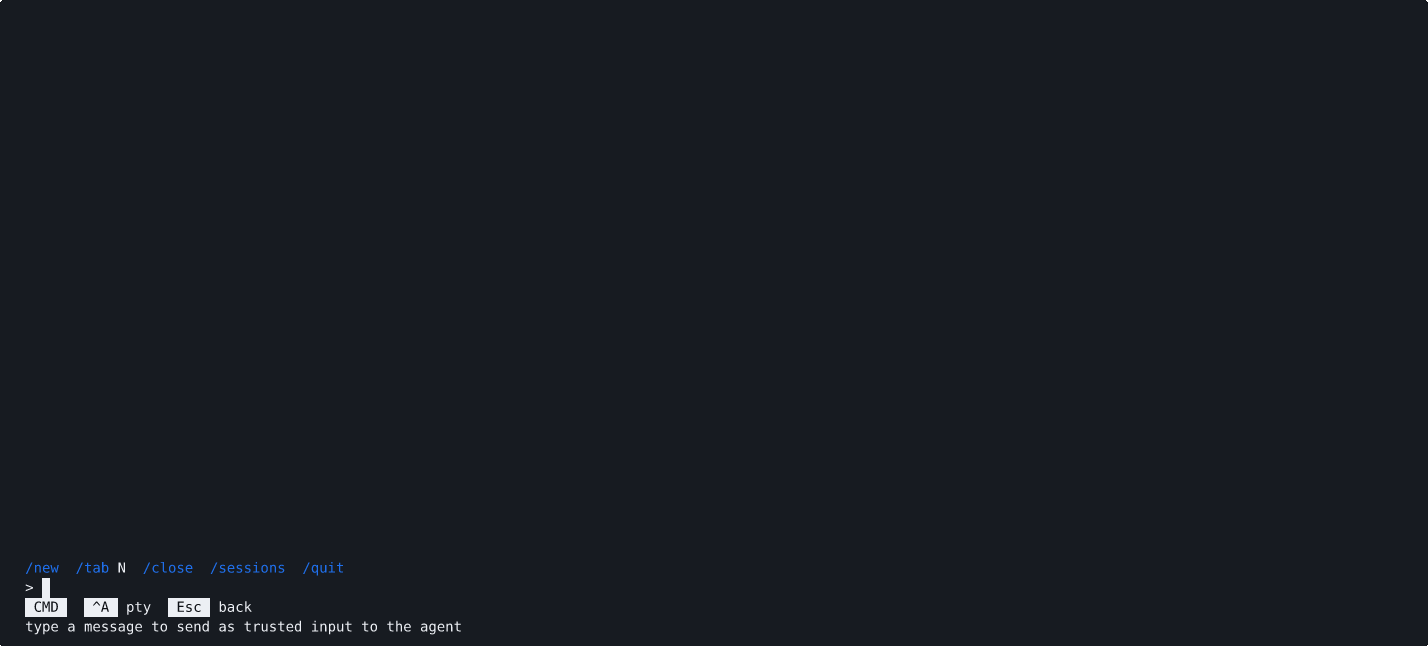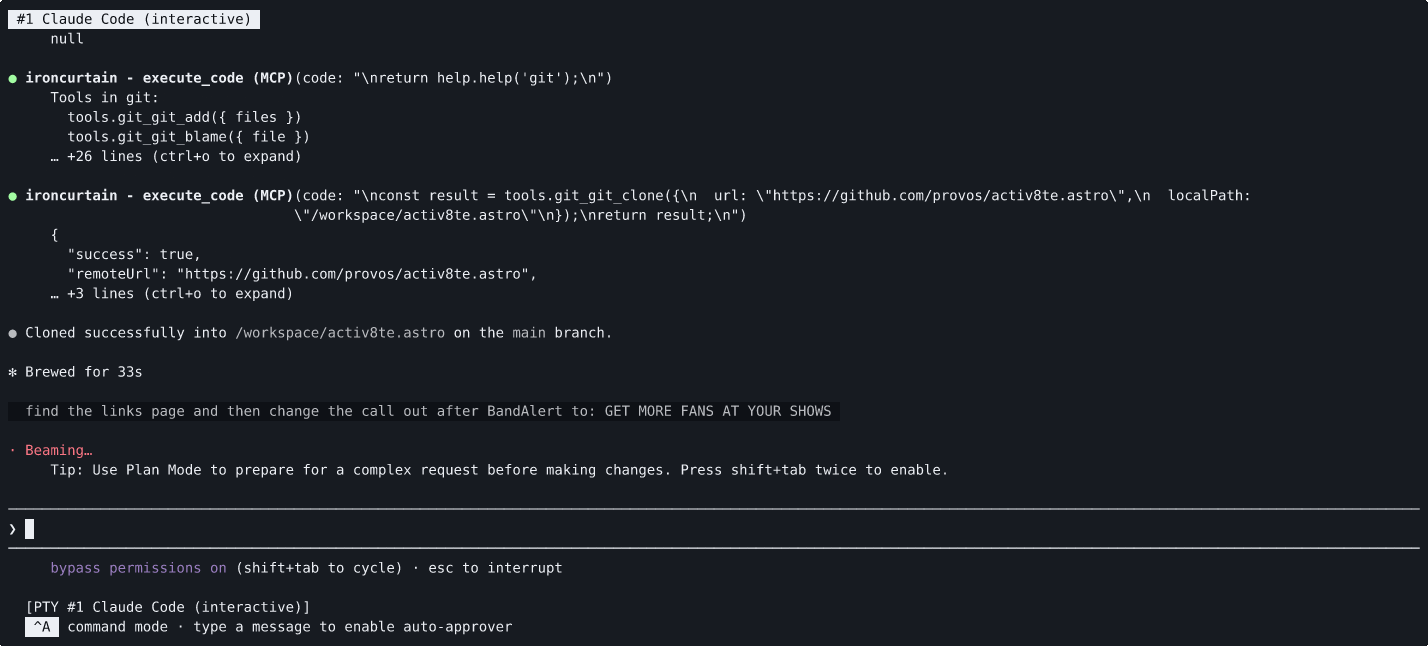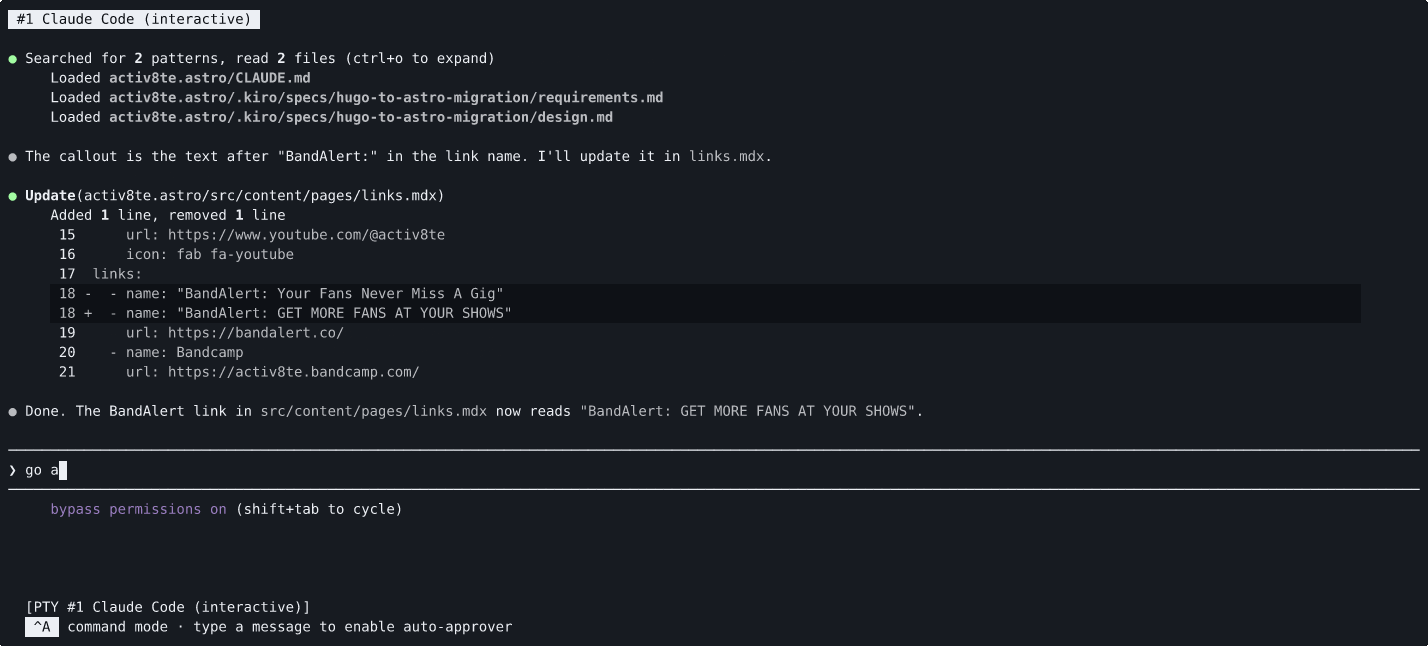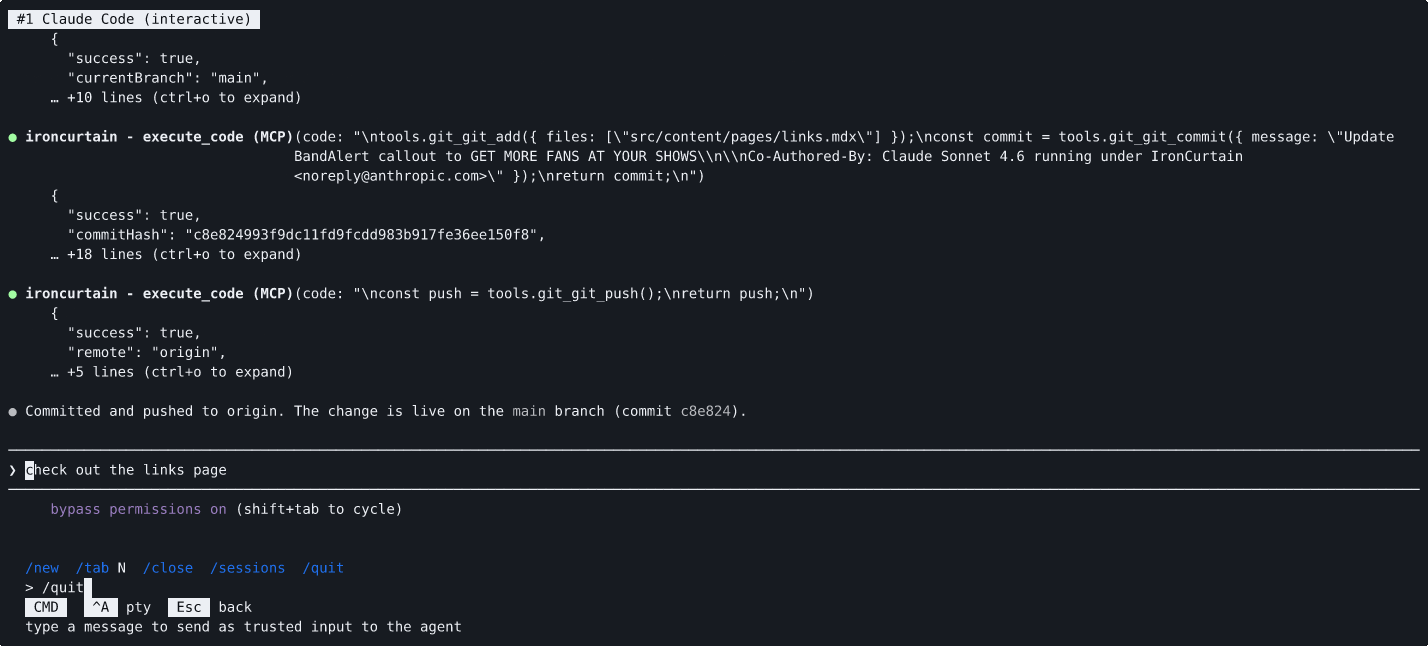
The agent is asked to clone a repository and push changes. Both git_clone and git_push are escalated by the policy engine, but the auto-approver approves them automatically — the user's trusted input from command mode (Ctrl-A) provided clear intent, so no manual /approve was needed.
Autonomous AI agents can manage files, run git commands, send messages, and interact with APIs on your behalf. But today's agent frameworks give the agent the same privileges as the user such as full access to the filesystem, credentials, and network. Security researchers call this ambient authority, and it means a single prompt injection or multi-turn drift can cause an agent to delete files, exfiltrate data, or push malicious code.
The common response is to either restrict agents to a narrow sandbox (limiting their usefulness) or to ask the user to approve every action (limiting their autonomy). Neither is satisfactory.
IronCurtain takes a different path: express your security intent in plain English, then let the system figure out enforcement.
You write a constitution which is a short document describing what your agent is and isn't allowed to do. IronCurtain compiles this into a deterministic security policy using an LLM pipeline, validates the compiled rules against generated test scenarios, and then enforces the policy at runtime on every tool call. The result is an agent that can work autonomously within boundaries you define in natural language.
The key ideas:
IronCurtain supports two session modes with different trust models:
Builtin Agent (Code Mode) — IronCurtain's own LLM agent writes TypeScript snippets that execute in a V8 sandbox. IronCurtain controls the agent, the sandbox, and the policy engine. Every tool call exits the sandbox as a structured MCP request, passes through the policy engine (allow / deny / escalate), and only then reaches the real MCP server.
Docker Agent Mode — An external agent (Claude Code, Goose, etc.) runs inside a Docker container with no network access. IronCurtain mediates the external effects: LLM API calls pass through a TLS-terminating MITM proxy (host allowlist, fake-to-real key swap), MCP tool calls pass through the same policy engine, and package installations (npm/PyPI) go through a validating registry proxy.
In both modes, the agent is untrusted. Security does not depend on the model following instructions — it is enforced at the boundary.
See SANDBOXING.md for the full architecture with diagrams, layer-by-layer trust analysis, and macOS platform notes.
isolated-vm; 24 and 26 install prebuilt binaries, Node 22 compiles from source at install and needs a C/C++ toolchain). Odd-numbered lines (23, 25) run but are untested — ironcurtain doctor warns.container works as an alternative backend (VM per container; used automatically when its services are running — see containerRuntime in ironcurtain config)As a global CLI tool (end users):
npm install -g @provos/ironcurtain
From source (development):
git clone https://github.com/provos/ironcurtain.git
cd ironcurtain
npm install
1. Set your API key:
export ANTHROPIC_API_KEY=sk-ant-...
You can also place keys in a .env file in the project root (loaded automatically via dotenv), or add them to ~/.ironcurtain/config.json via ironcurtain config. Environment variables take precedence over config file values. Supported: ANTHROPIC_API_KEY, GOOGLE_GENERATIVE_AI_API_KEY, OPENAI_API_KEY.
2. Run the first-start wizard (run this explicitly before using the recommended mux path; it also runs automatically on first non-mux ironcurtain start):
ironcurtain setup
Walks you through GitHub token setup, web search provider, model selection, and other settings. Creates ~/.ironcurtain/config.json with your choices.
IronCurtain ships with a default policy geared towards the developer experience — read-only operations are allowed, mutations (writes, pushes, PR creation) escalate for human approval. You can start using it immediately after setup.
The recommended way to use IronCurtain. It gives you the full power of your agent's interactive TUI (Claude Code or Goose) while IronCurtain mediates every tool call through its policy engine — all in a single terminal.
ironcurtain mux
Key capabilities:
/approve+ N to whitelist a domain or path for the rest of the session.git_push escalation./new), switch between them (/tab N, Alt-1..9), close them (/close). Multiple mux instances can run in parallel.