
XXStrike
 anonmoty/xxstrike
XSStrike based XSS scanner with custom features. Detects XSS vulnerabilities in web applications.
dynamic-code-analysisfuzzingpenetration-testing+5
3
anonmoty/xxstrikeXSStrike based XSS scanner with custom features. Detects XSS vulnerabilities in web applications.
 vladko312/sstimap
Automatic SSTI detection tool with interactive interface
 r00tkitsmm/pishi
Pishi is a code coverage tool like kcov for macOS.
 rust-fuzz/cargo-fuzz
Cargo subcommand for coverage-guided Rust fuzzing with libFuzzer: create and run fuzz targets, minimize failures and corpora, and report coverage.
 google/honggfuzz
Security oriented software fuzzer. Supports evolutionary, feedback-driven fuzzing based on code coverage (SW and HW based)
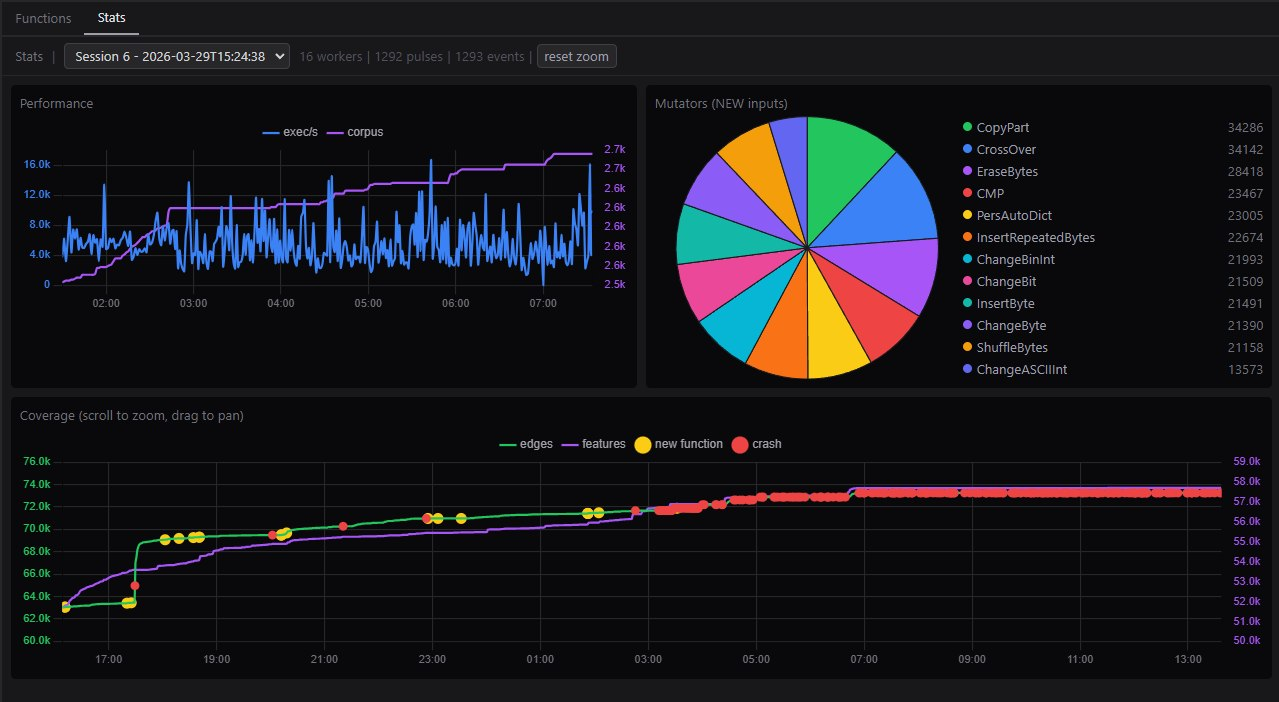 0xbigshaq/apatchy
Fuzzing Framework for Modules in Apache HTTPD Server
 trailofbits/polytracker
An LLVM-based instrumentation tool for universal taint tracking, dataflow analysis, and tracing.
 narfindustries/http-garden
Differential testing framework for HTTP implementations
 hackmanit/tinja
TInjA is a CLI tool for testing web pages for template injection vulnerabilities and supports 44 of the most relevant template engines for eight…
 google/oss-fuzz-gen
LLM powered fuzzing via OSS-Fuzz.
 google/buzzer
eBPF fuzzer toolchain for generating random eBPF programs and validating kernel verifier/runtime behavior. Supports coverage-guided fuzzing and…
 sentinel-one/peafl64
Static Binary Instrumentation tool for Windows x64 executables
 abubakar-shahid/cve-2024-36886
Academic research on N-Day Linux kernel vulnerabilities, analyzing CVE-2024-36886 in the TIPC networking subsystem, lifecycle, impact, and mitigation…
 dvyukov/centipede
Distributed coverage-guided fuzzing engine compatible with libFuzzer targets; scales to thousands of concurrent jobs, uses sanitizers and corpus…
 angorafuzzer/angora
Coverage-guided fuzzer that uses taint tracking and scalar optimization to solve path constraints without symbolic execution, improving branch…
 tca-iscas/cooper-ndss-2022
A tool for effective testing the binding layer of scripting languages
 danmcinerney/xsscrapy
XSS spider - 66/66 wavsep XSS detected