

summit
 pennacle-security/summit
Open-source web security testing platform: proxy, scanner and fuzzer in one CLI. By Pennacle Security.
api-security-testingfuzzinginformation-gathering+9
4
pennacle-security/summitOpen-source web security testing platform: proxy, scanner and fuzzer in one CLI. By Pennacle Security.
 albinowax/activescanplusplus
Burp Suite extension that extends active and passive scanning with checks for host header attacks, XXE, expression language injection, shellshock and…
 d0ge/websocketturbointruder
Burp Suite extension for fuzzing WebSocket messages with custom Python code, supporting multiple engines, HTTP middleware routing, and response…
 akha-security/akca
Evidence-oriented DAST scanner in Go that crawls web apps and APIs, then runs adaptive SQLi, XSS, RCE, SSRF, and auth checks with replayable proof.
 0xmarik/aresius
Native HTTP/HTTPS interception proxy for penetration testers and bug bounty hunters with live request tampering, request replay, high-speed fuzzing,…
 hahwul/gori
A fast, keyboard-driven HTTP intercepting proxy and pentesting toolkit for the terminal built for humans and AI agents alike.
 wapiti-scanner/wapiti
Web vulnerability scanner written in Python3
 chrislockard/api_wordlist
A wordlist of API names for web application assessments
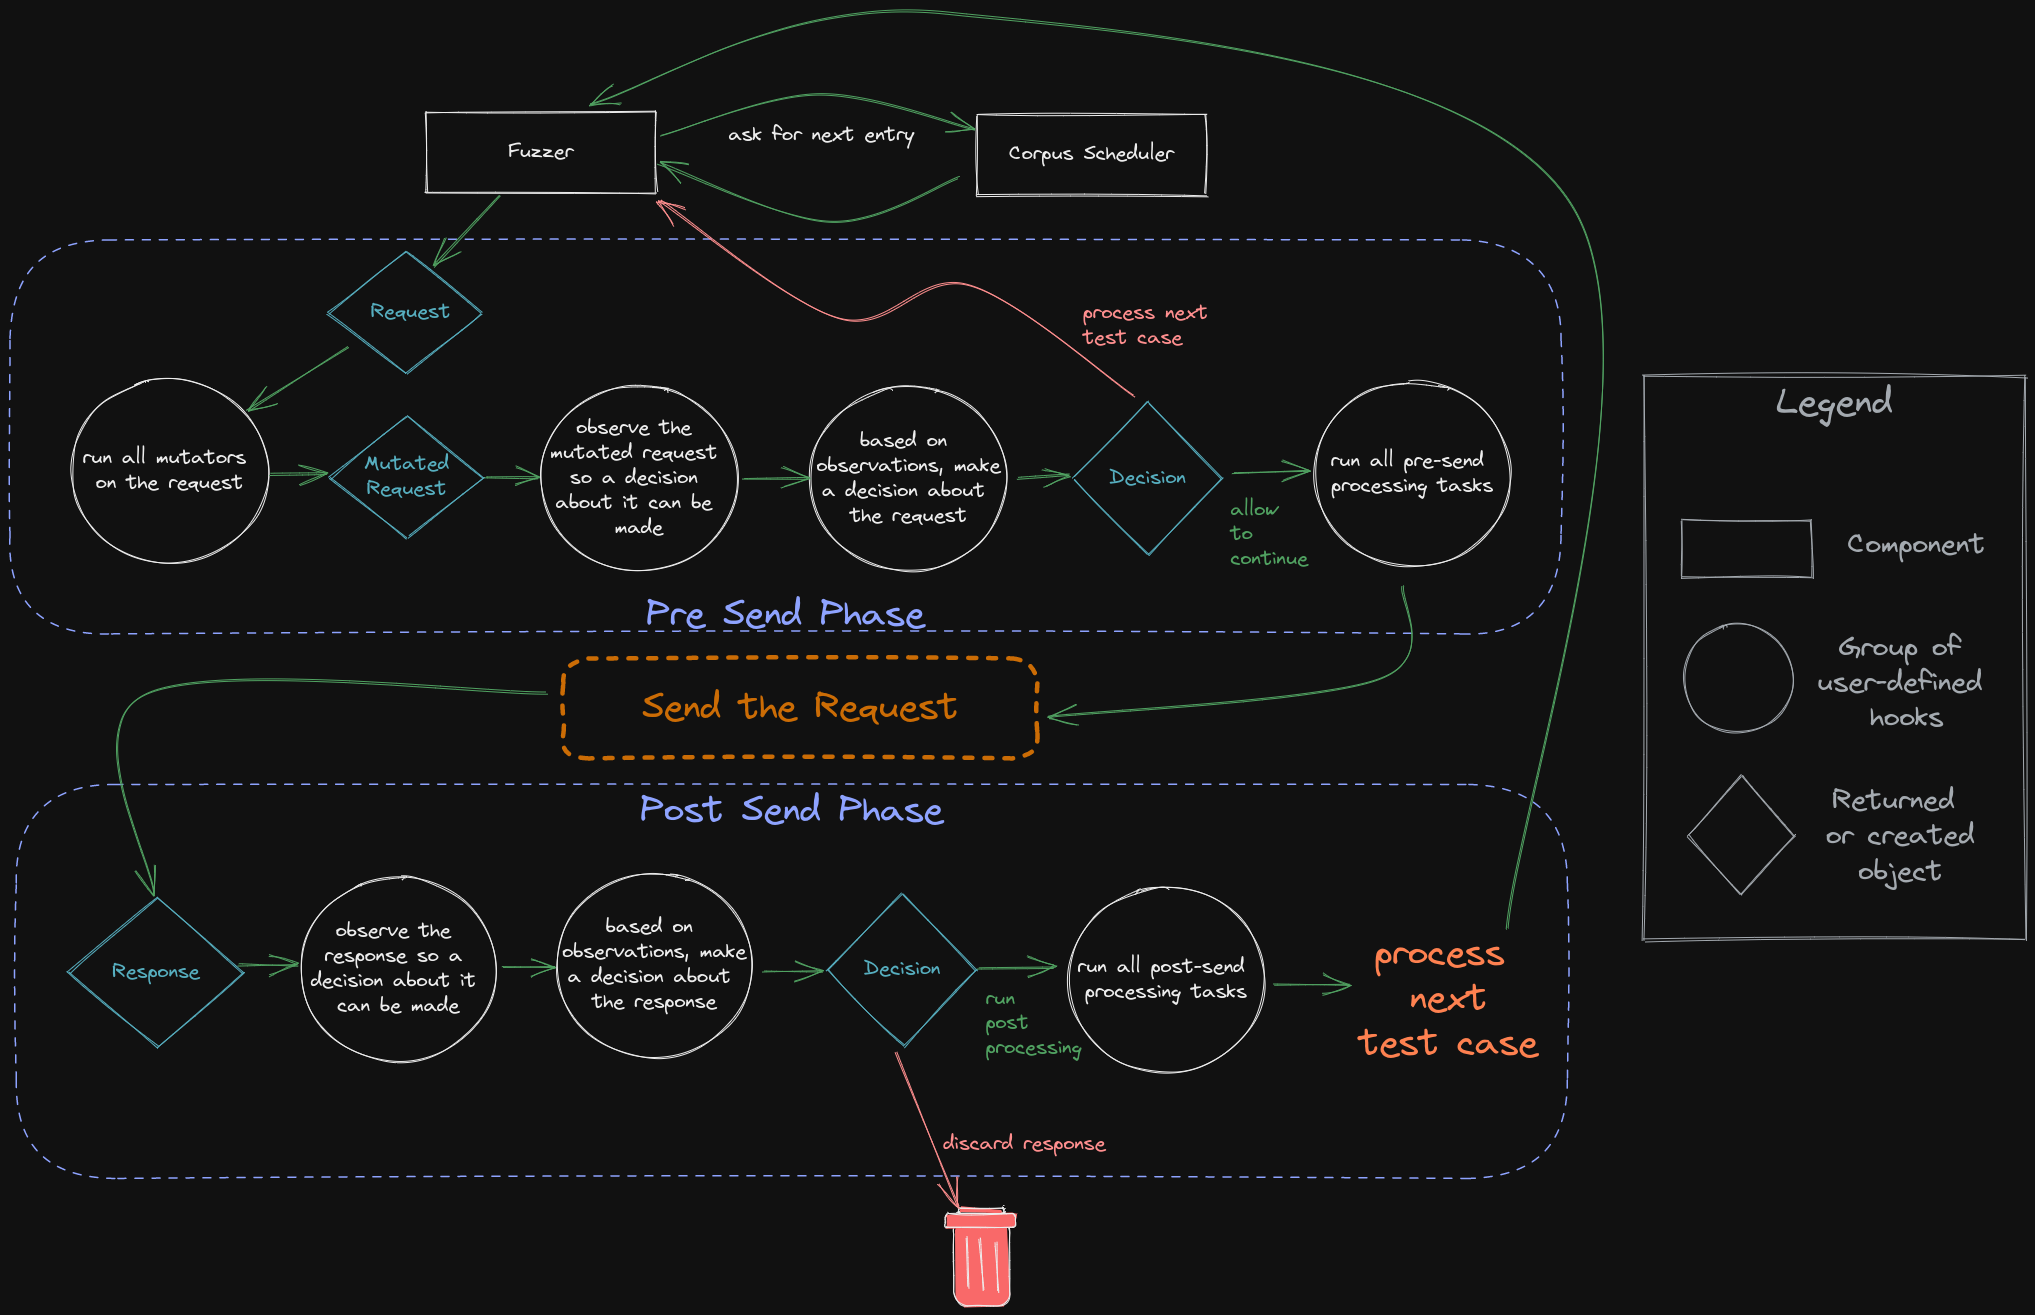 epi052/feroxfuzz
Build structure-aware black-box HTTP fuzzers in Rust with composable mutators, schedulers, observers, deciders, and processors for custom web and API…
 net-hunter121/api-wordlist
Curated wordlists of API function names, verbs, and nouns for fuzzing web application endpoints with Burp Suite Intruder.
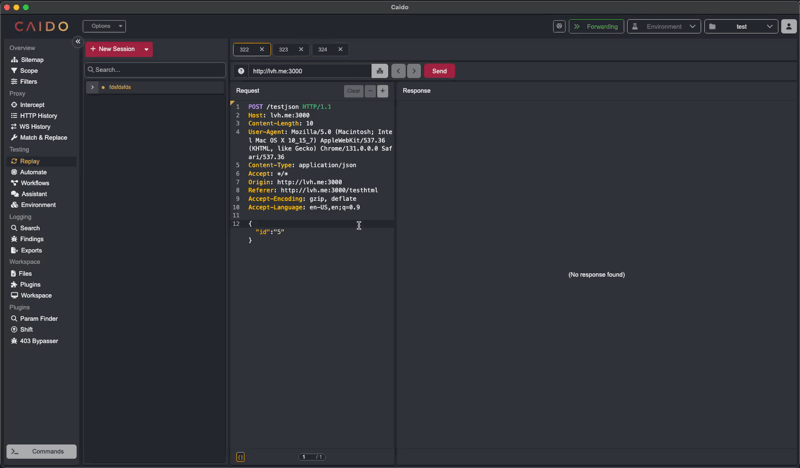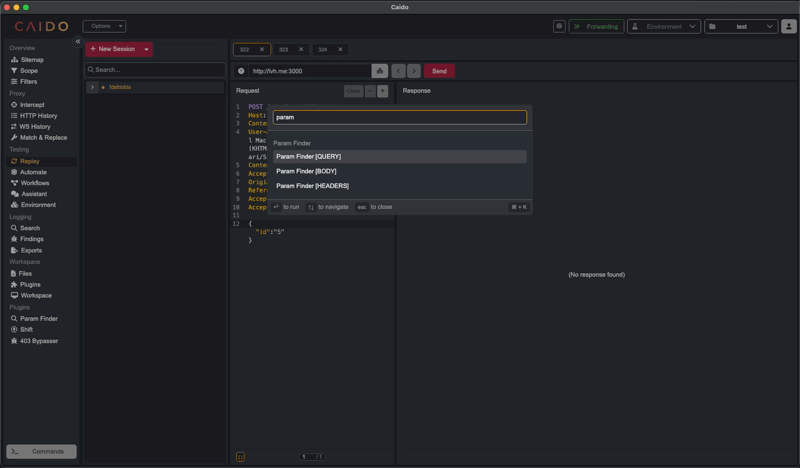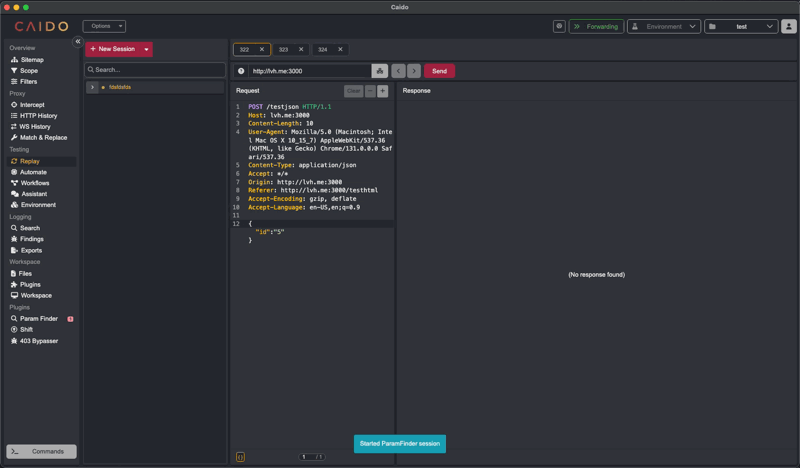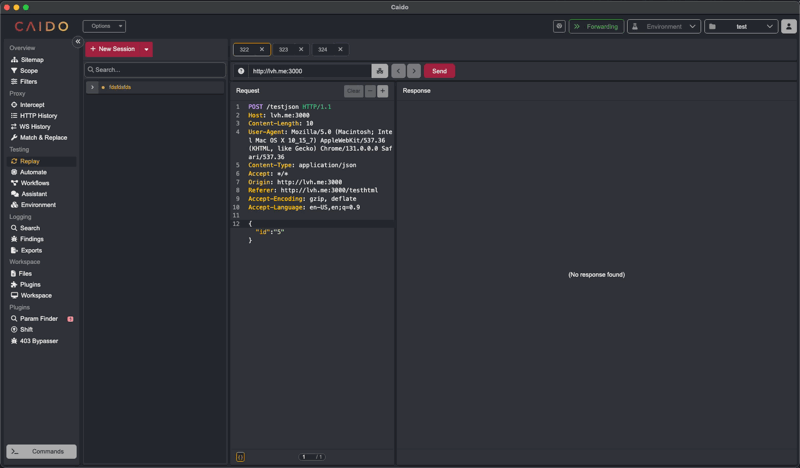 caido-community/paramfinder
Discover hidden parameters in Caido
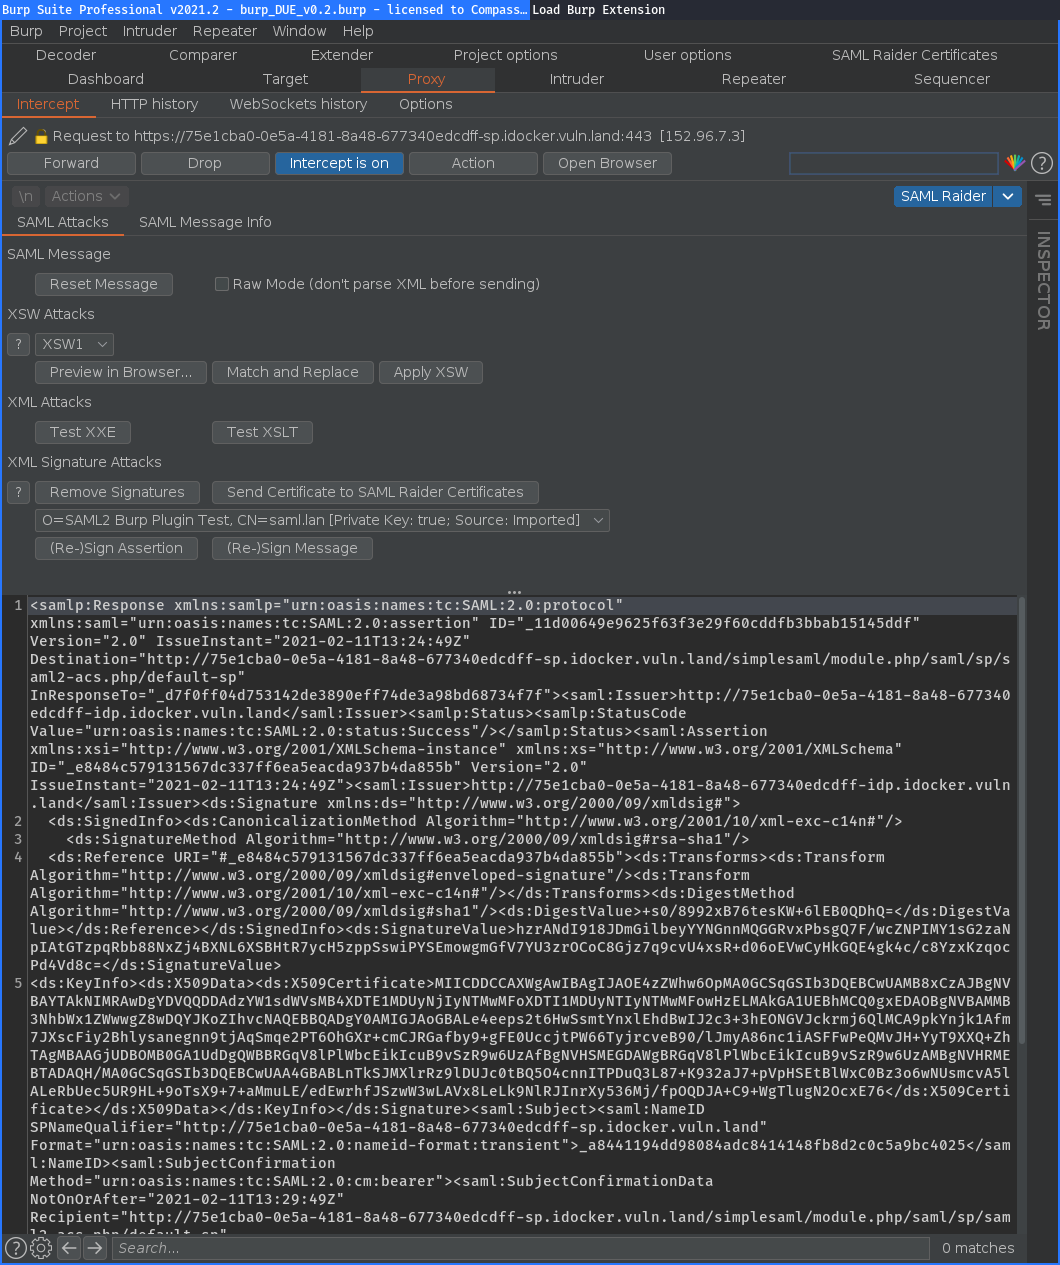 compasssecurity/samlraider
SAML2 Burp Extension
 raz0r/burp-radamsa
Radamsa fuzzer extension for Burp Suite
 hackinglz/maps_scanner
MAPS cloud scanner and response parser for Microsoft Defender research.
 bogdanticu88/ratrace
A lightweight CLI tool for systematically detecting and exploiting race conditions in web applications, APIs, and modern services.
 mda2av/http11probe
An open testing platform that probes HTTP/1.1 servers against RFC 9110/9112 requirements, smuggling vectors, and malformed input handling. Add your…
 functori/dev/gaia
Global API Integrity Assessor
 omar2535/graphqler
☸The first ever dependency-aware GraphQL API testing tool!