Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
57 results
cve-2020-5902-ioc-bigip-checker preview

cve-2020-5902-ioc-bigip-checker

GitHubf5devcentral/cve-2020-5902-ioc-bigip-checker

Local F5 BIG-IP script that scans for Indicators of Compromise (IoCs) related to CVE-2020-5902, checking logs, files, and system integrity to detect…

forensicsincident-responseioc-management+3
16
6 years ago
envocabulary preview

envocabulary

GitHubsreckoskocilic/envocabulary

Trace every shell environment variable to its exact file and line origin. Audit shell configs for dead entries, duplicates, and orphaned files across…

configuration-auditingdigital-forensicsforensics+3
38 days ago
GhostTrace preview

GhostTrace

GitHubdevzinh/ghosttrace

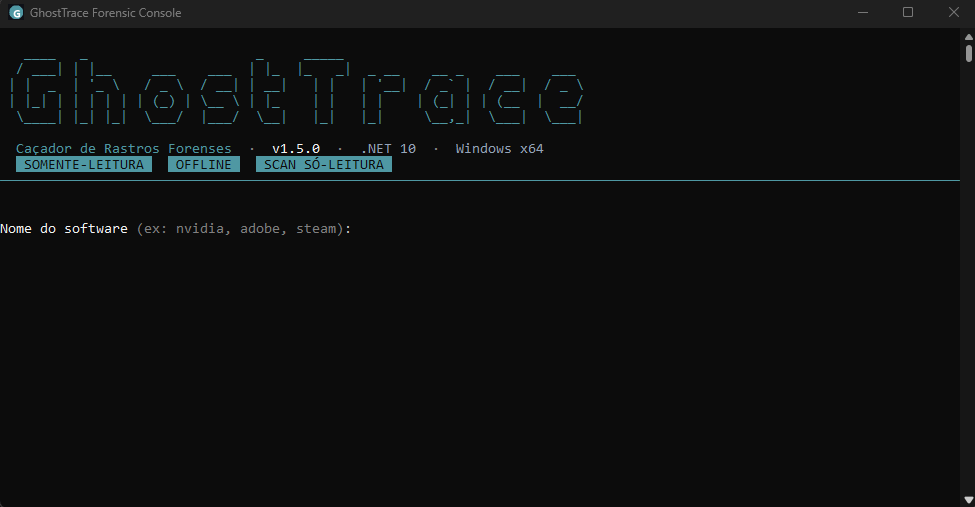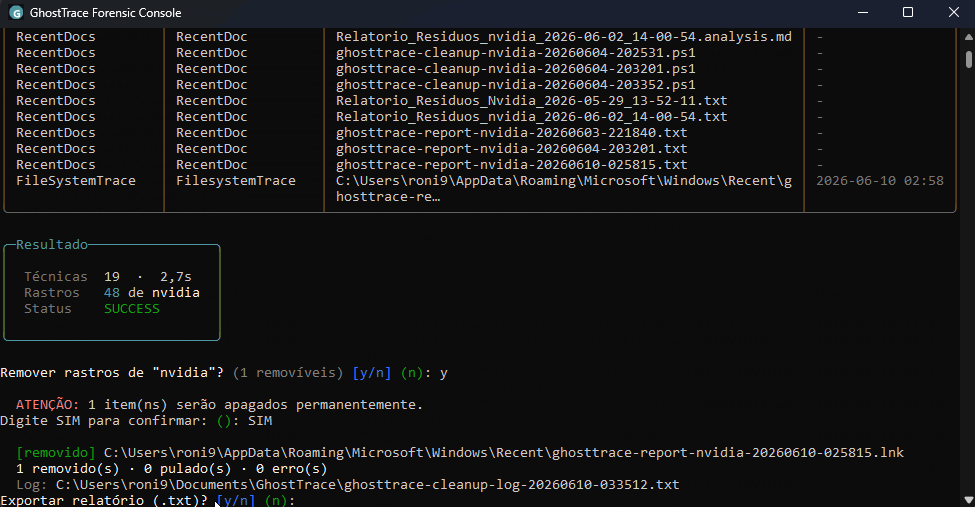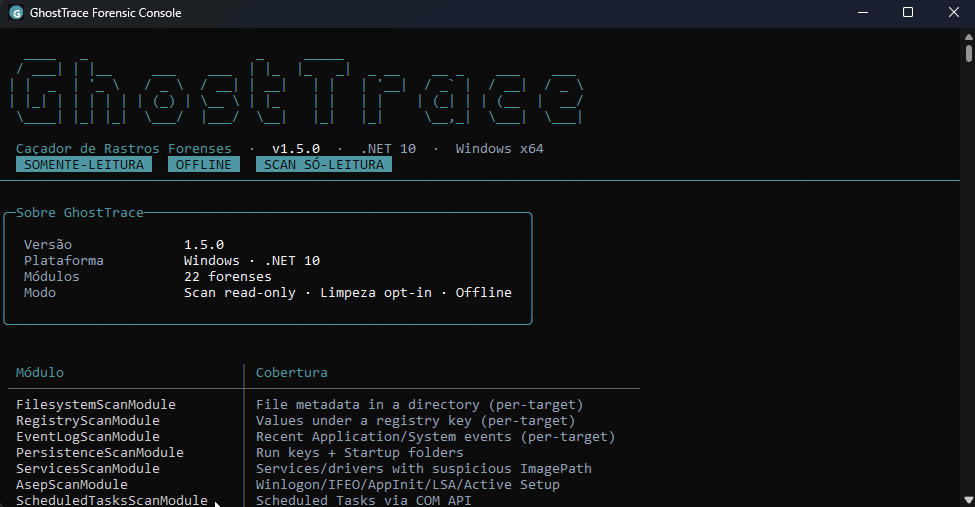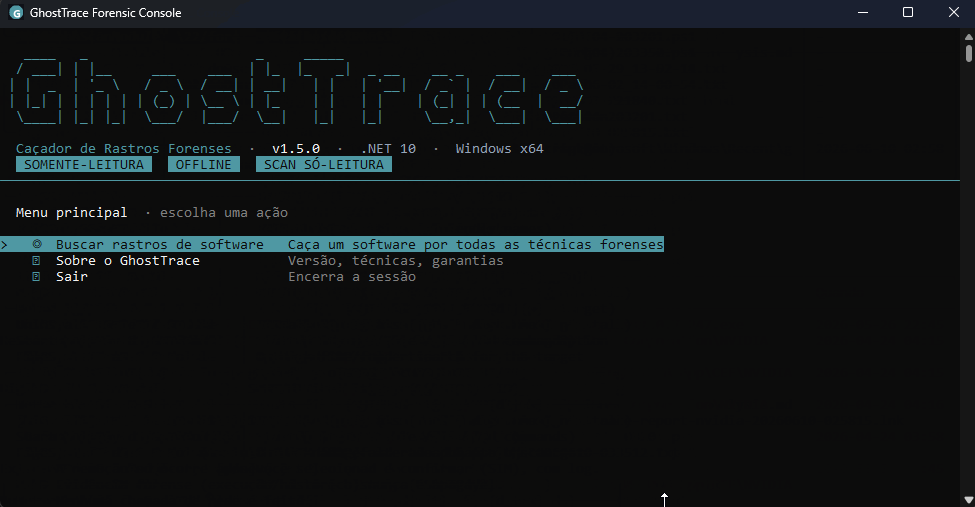
Read-only Windows forensic scanner for software traces — persistence, execution artifacts (Prefetch, Shimcache, BAM), user activity and Ghost Tasks…

digital-forensicsforensicsincident-response+3
2 months ago
mini-shai-hulud-detector preview

mini-shai-hulud-detector

GitHubprashanthnataraj/mini-shai-hulud-detector

One-command scanner for the Mini Shai-Hulud npm supply-chain worm (CVE-2026-45321). Detect before rotating tokens.

forensicsincident-responsemalware-analysis+3
4 months ago
wp2shell-compromise-scanner-plugin preview

wp2shell-compromise-scanner-plugin

GitHubeyesecurity/wp2shell-compromise-scanner-plugin

Read-only WordPress plugin that scans for artifacts of the wp2shell exploit chain (CVE-2026-63030 / CVE-2026-60137)

database-securitydigital-forensicsforensics+5
2 months ago
malware_training_vol1 preview

malware_training_vol1

GitHubhasherezade/malware_training_vol1

Materials for Windows Malware Analysis training (volume 1)

binary-analysiseducationforensics+4
2.1k2 years ago
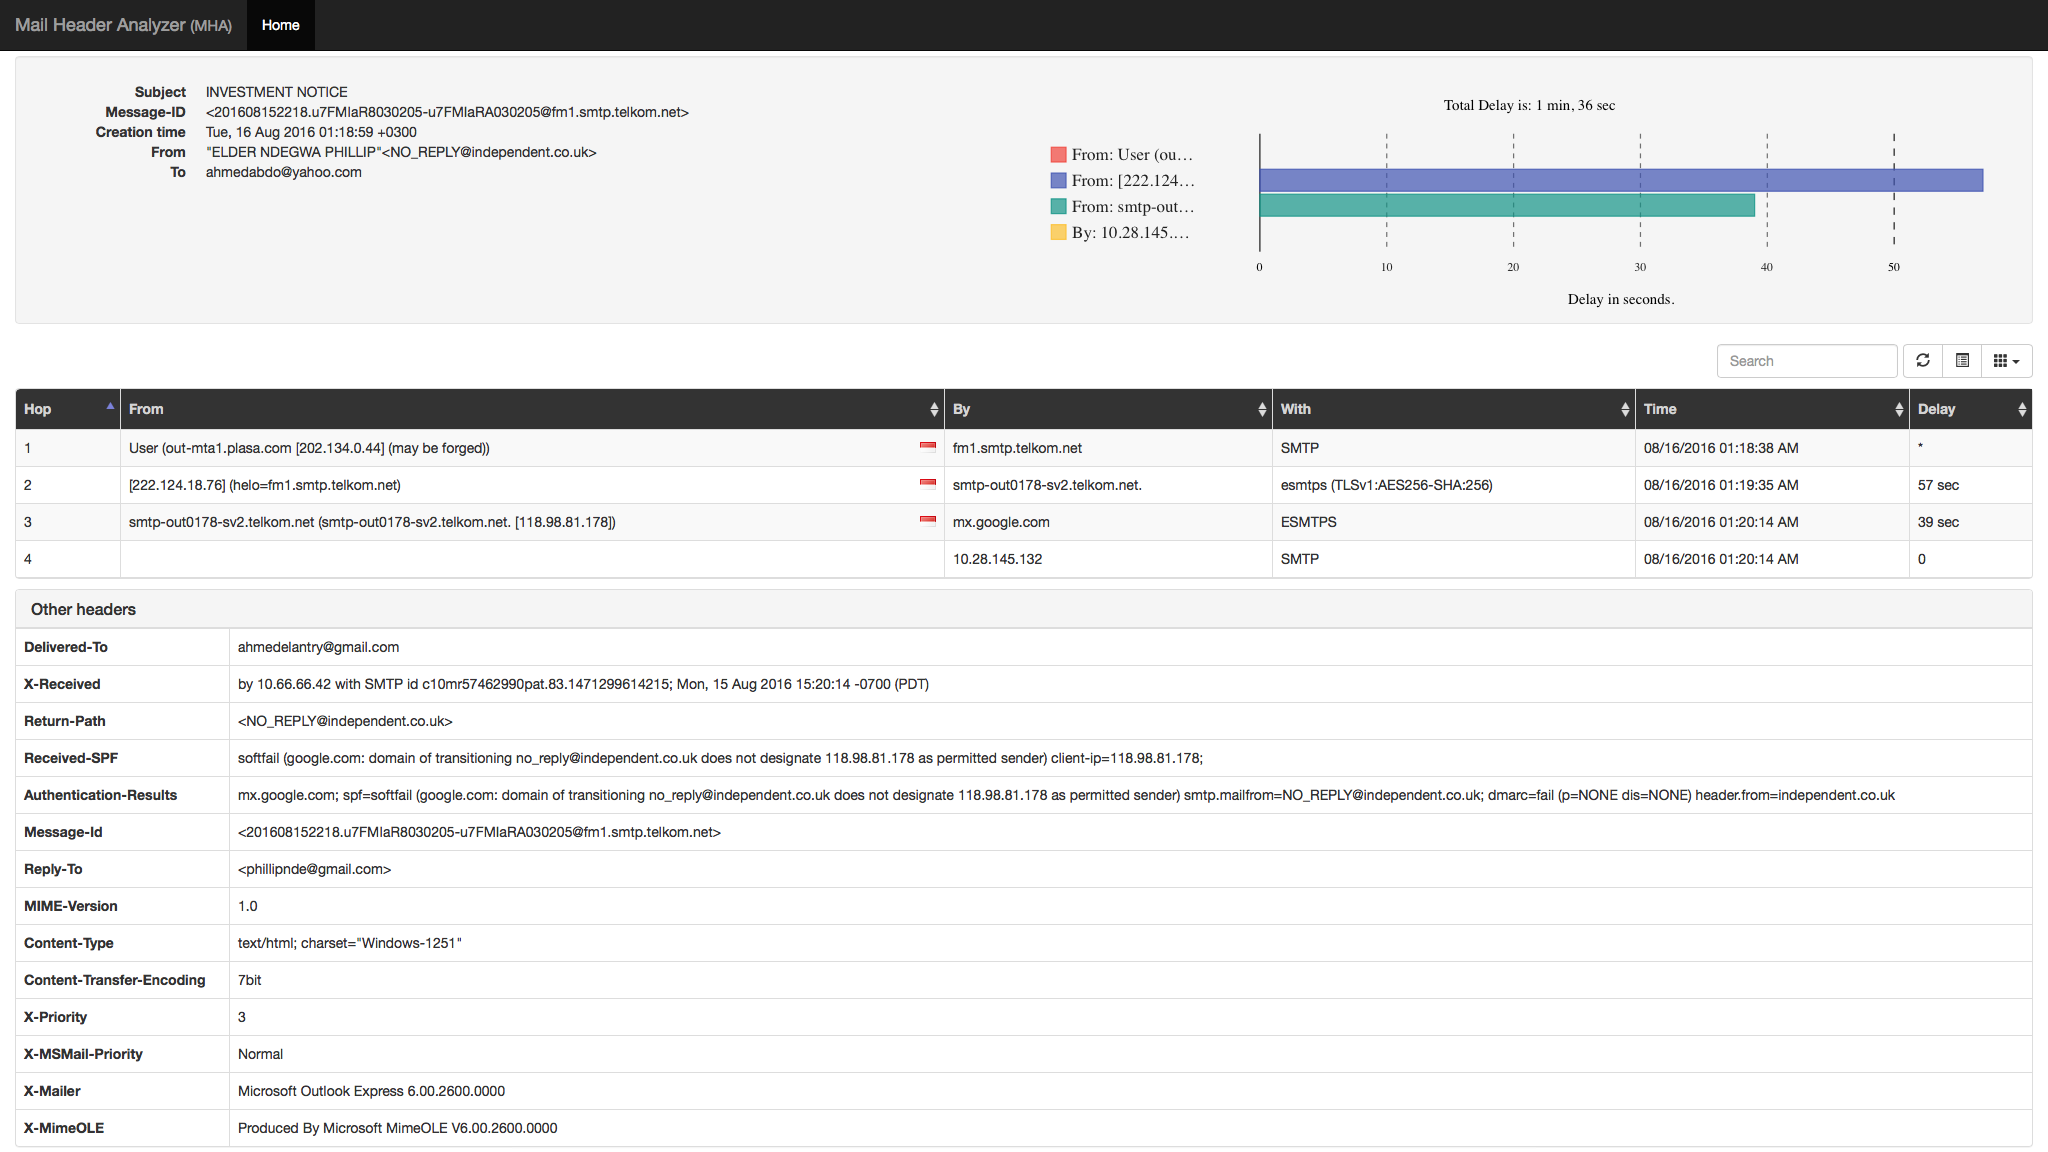
email-header-analyzer preview

email-header-analyzer

GitHubcyberdefenders/email-header-analyzer

E-Mail Header Analyzer

digital-forensicsemail-securityforensics+2
7006 years ago
modo preview

modo

GitHubmohshomis/modo

Curated collection of cybersecurity learning resources, CTF writeups, research papers, and practical labs for hands-on skill development across web…

ctfcurated-resourceseducation+9
1926 months ago
magic-extractor preview

magic-extractor

GitHubxchwarze/magic-extractor

Universal Windows extraction tool that detects unknown files and routes them to the right bundled extractor.

binary-analysisdata-recoverydigital-forensics+8
431 month ago
asclepius preview

asclepius

GitHubmatank001/asclepius

Asclepius validates backup integrity by restoring files and actively testing their recoverability. Instead of trusting metadata, it attempts to parse…

data-recoveryforensicsmalware-analysis+2
119 months ago
pyWhat preview

pyWhat

GitHubbee-san/pywhat

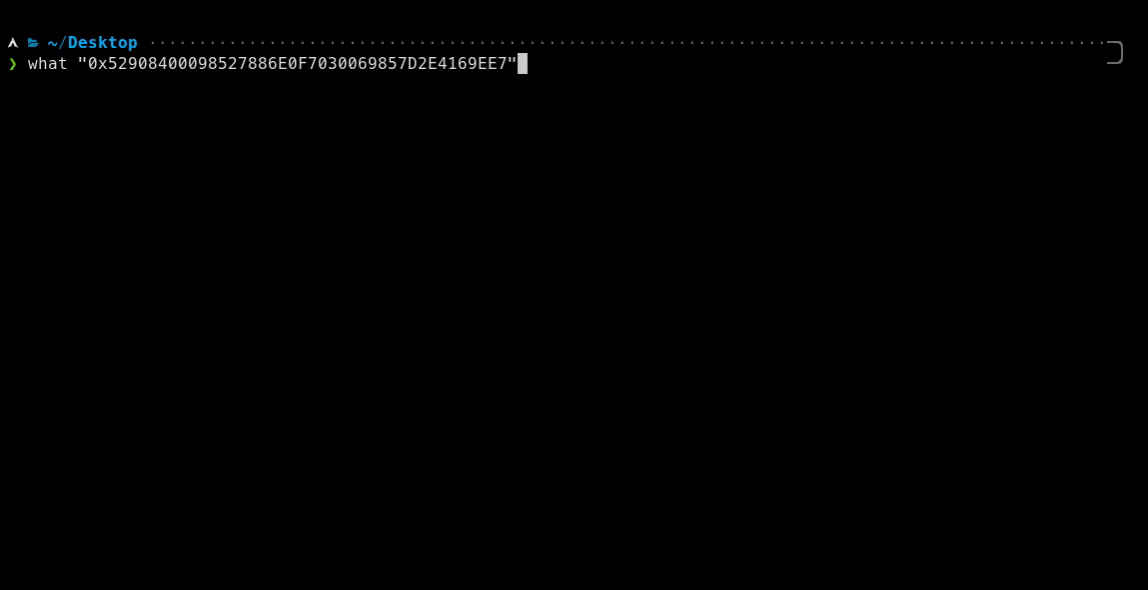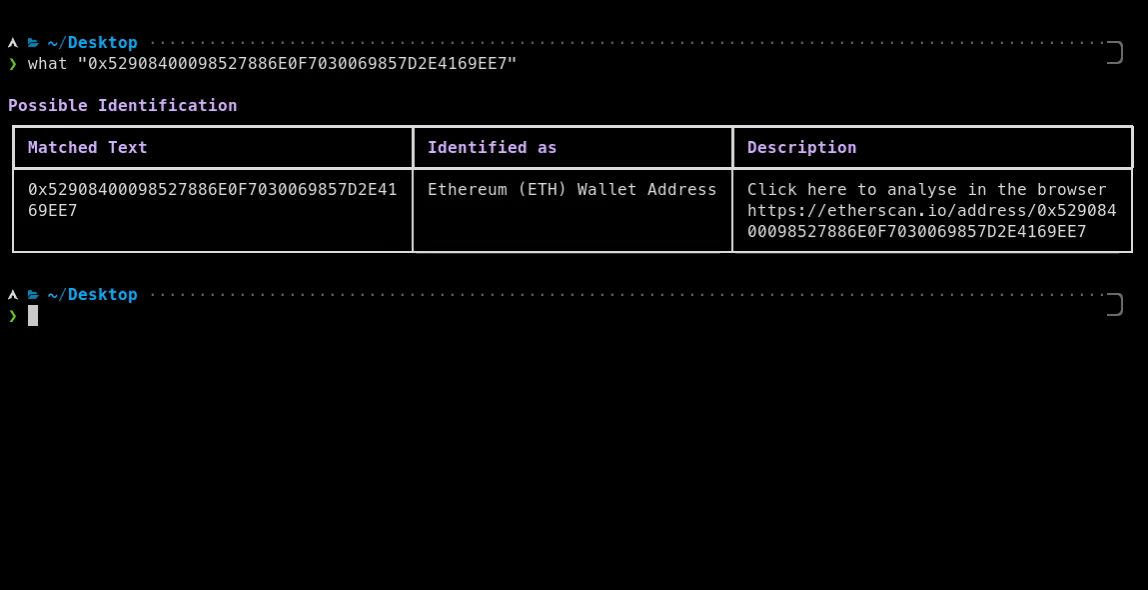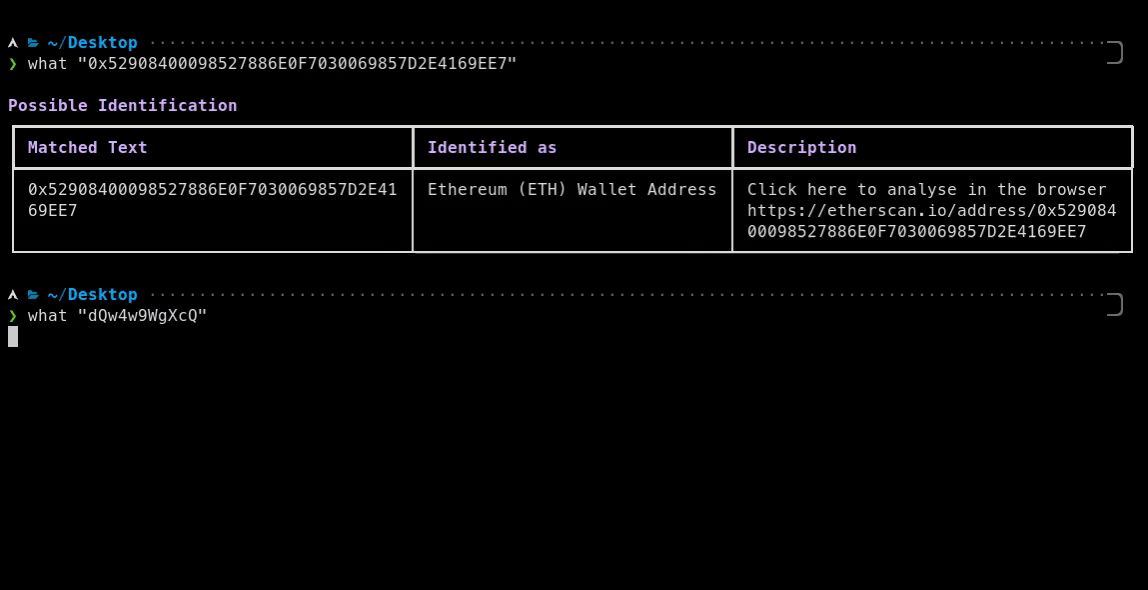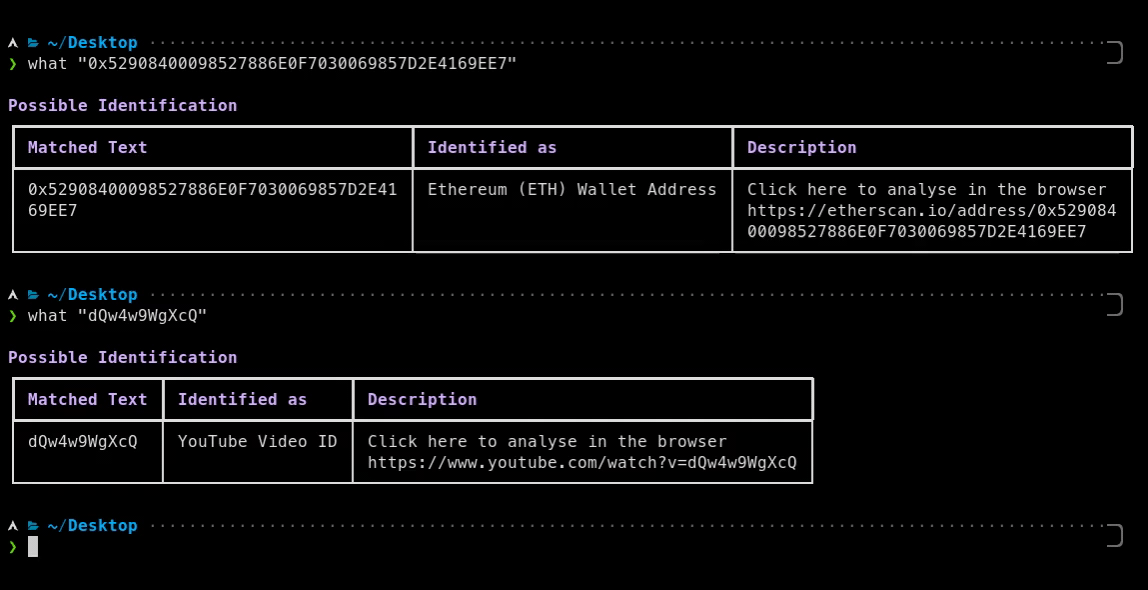
🐸 Identify anything. pyWhat easily lets you identify emails, IP addresses, and more. Feed it a .pcap file or some text and it'll tell you what it…

data-exfiltrationeducationforensics+7
7.3k5 days ago
IPED preview

IPED

GitHubsepinf-inc/iped

IPED Digital Forensic Tool. It is an open source software that can be used to process and analyze digital evidence, often seized at crime scenes by…

data-recoverydigital-forensicsdisk-forensics+9
3.0k3 days ago
autopsy preview

autopsy

GitHubsleuthkit/autopsy

Autopsy® is a digital forensics platform and graphical interface to The Sleuth Kit® and other digital forensics tools. It can be used by law…

data-recoverydigital-forensicsdisk-forensics+3
3.4k5 months ago
imaginaryC2 preview

imaginaryC2

GitHubfelixweyne/imaginaryc2

Imaginary C2 is a python tool which aims to help in the behavioral (network) analysis of malware. Imaginary C2 hosts a HTTP server which captures…

command-and-controldigital-forensicsdynamic-analysis-sandboxing+5
4463 years ago
ngrep preview

ngrep

GitHubjpr5/ngrep

ngrep is like GNU grep applied to the network layer. It's a PCAP-based tool that allows you to specify an extended regular or hexadecimal expression…

dns-analysisforensicsinformation-gathering+3
1.0k8 months ago
WDExtract preview

WDExtract

GitHubhfiref0x/wdextract

Extract Windows Defender database from vdm files and unpack it

binary-analysisencryption-decryption-toolsforensics+2
4945 months ago
windbg-mcp preview

windbg-mcp

GitHubgengstah/windbg-mcp

An MCP (Model Context Protocol) server that turns all pybag Windows debugger functions into native MCP tools. It lets MCP-compatible clients (Claude…

binary-analysisdebuggersdynamic-analysis-sandboxing+7
945 months ago
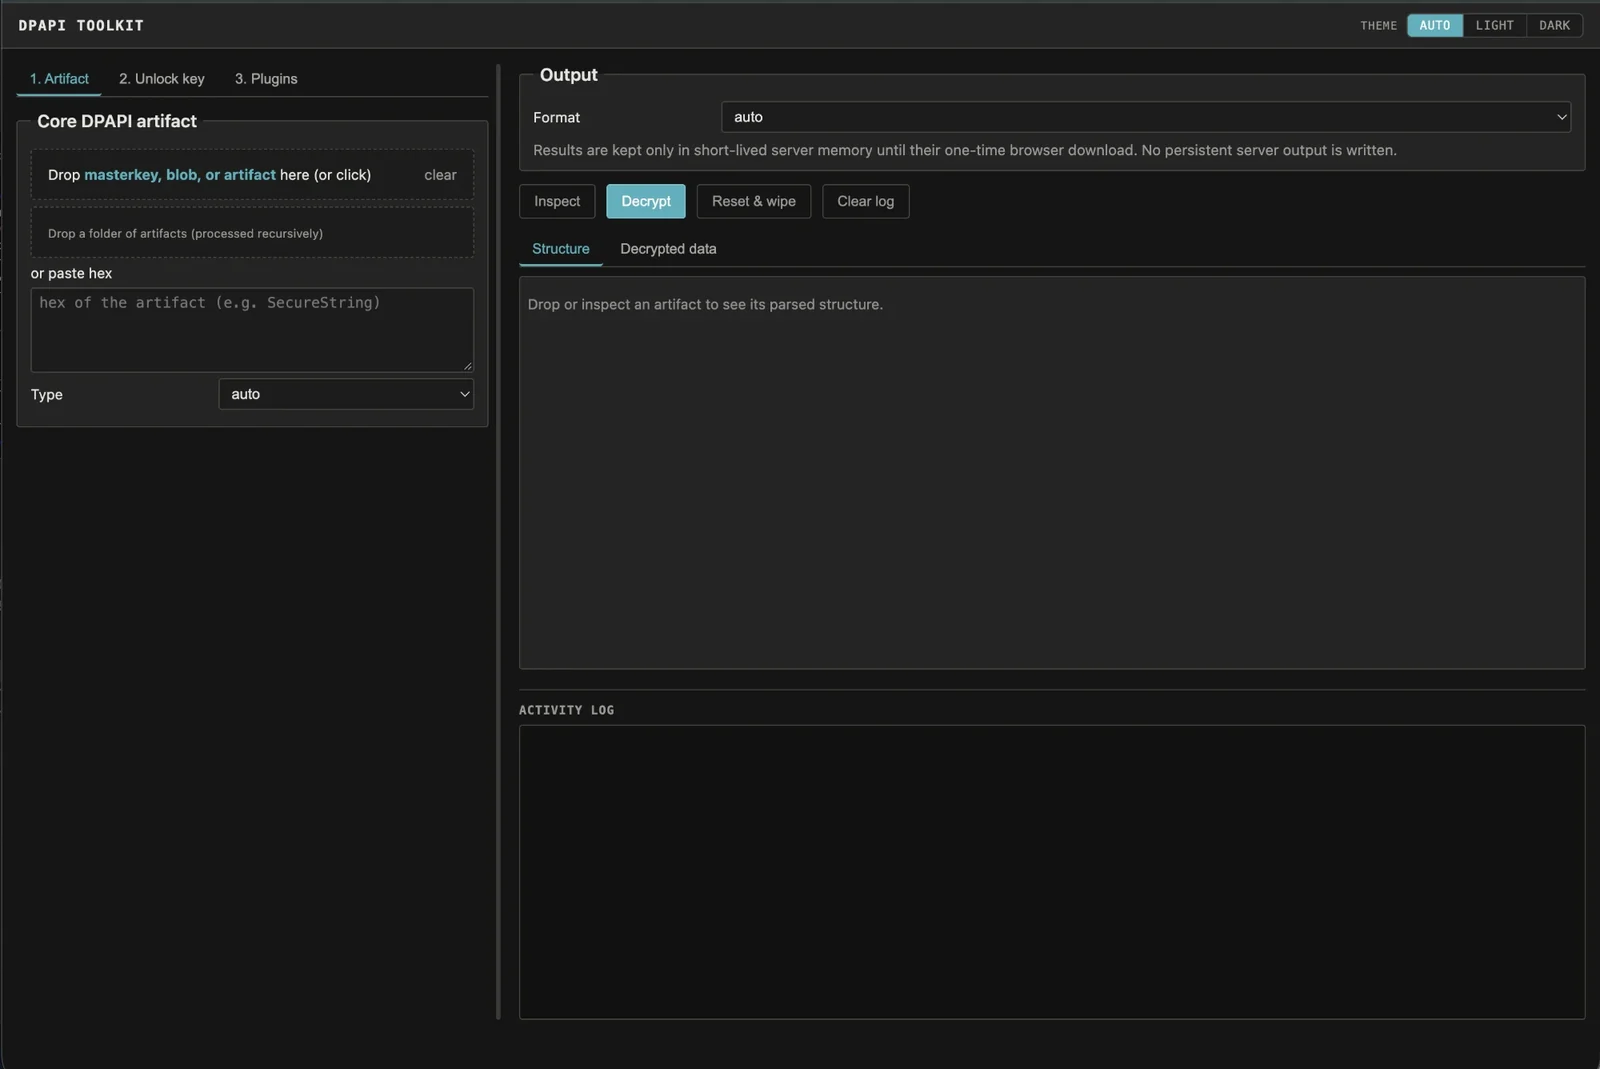
dpapi-toolkit preview

dpapi-toolkit

GitHubcrypt0p3g/dpapi-toolkit

Drop any Windows DPAPI artifact and it identifies the format and the exact master key it needs, then decrypts once you supply the key. Offline, CLI +…

digital-forensicsencryption-decryption-toolsforensics+7
2813 days ago
Previous1234Next