

iLEAPP
 abrignoni/ileapp
Parses iOS and iPadOS forensic extractions into HTML, TSV, timeline, KML, and LAVA reports with modular artifact discovery and encrypted iTunes…
digital-forensicsforensicsincident-response+3
1.3k
abrignoni/ileappParses iOS and iPadOS forensic extractions into HTML, TSV, timeline, KML, and LAVA reports with modular artifact discovery and encrypted iTunes…
 domcyrus/rustnet
Per-process network monitoring for your terminal with deep packet inspection. Cross-platform, sandboxed.

 wireshark/wireshark
Wireshark's official code repository. You can keep the releases coming by donating at https://wiresharkfoundation.org/donate/.
 wireshark/wireshark
Capture and analyze network traffic with deep packet inspection, protocol decoding across hundreds of protocols, and capture-file support for…

 yamato-security/hayabusa
Multi-threaded Windows event log forensics timeline generator and threat hunting tool with full Sigma rule support, producing CSV/JSON timelines for…
 horsicq/detect-it-easy
Program for determining types of files for Windows, Linux and MacOS.
 daffainfo/vol-rs
Volatility 3 ported to Rust. Same output, much faster.
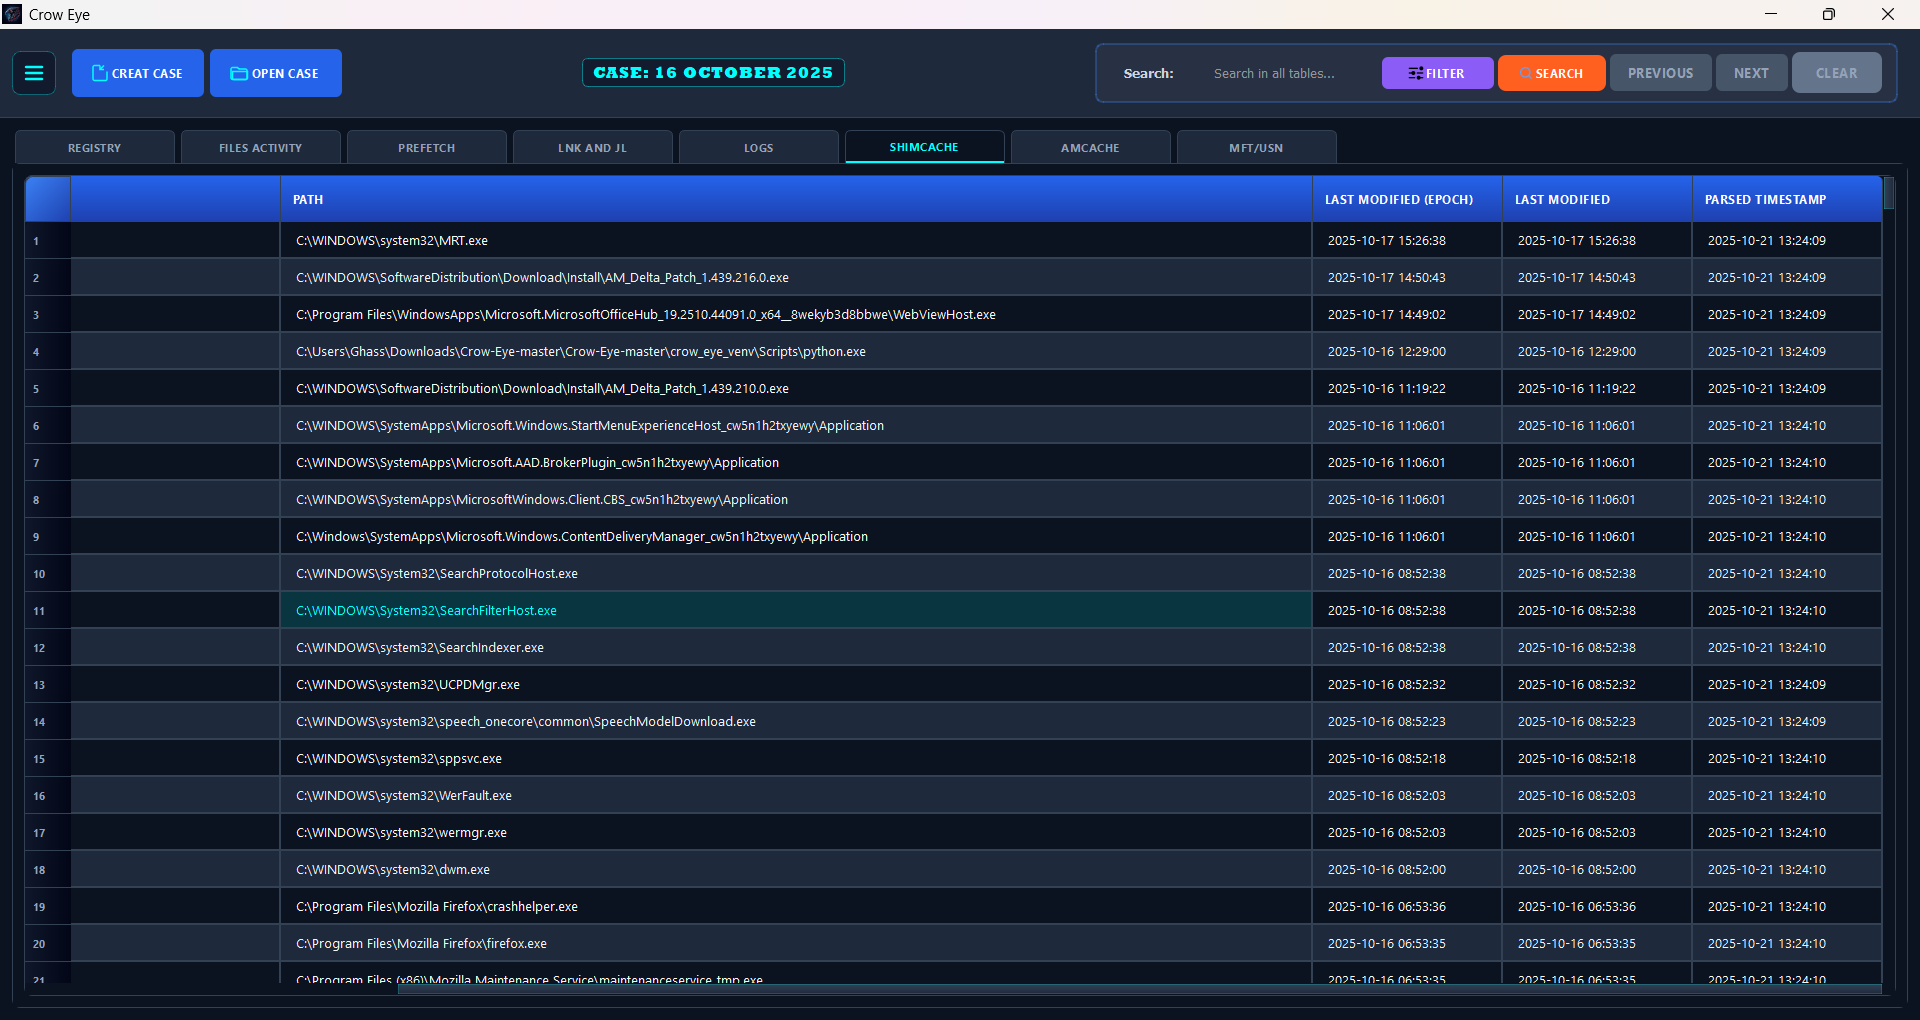 ghassan-elsman/crow-eye
Open-source Windows forensics engine that acquires, parses, and correlates artifacts (MFT, USN, Registry, etc.) to reconstruct timelines with…
 winsiderss/systeminformer
Real-time Windows system monitor with advanced process, network, and disk analysis, stack trace debugging, malware detection, and service management.…
 cgsecurity/testdisk
Recovers lost partitions and repairs boot sectors; carves 480+ file formats from damaged disks and filesystems for data recovery and forensic use.
 sepinf-inc/iped
IPED Digital Forensic Tool. It is an open source software that can be used to process and analyze digital evidence, often seized at crime scenes by…
 wagga40/zircolite
A standalone SIGMA-based detection tool for EVTX, Auditd and Sysmon for Linux logs
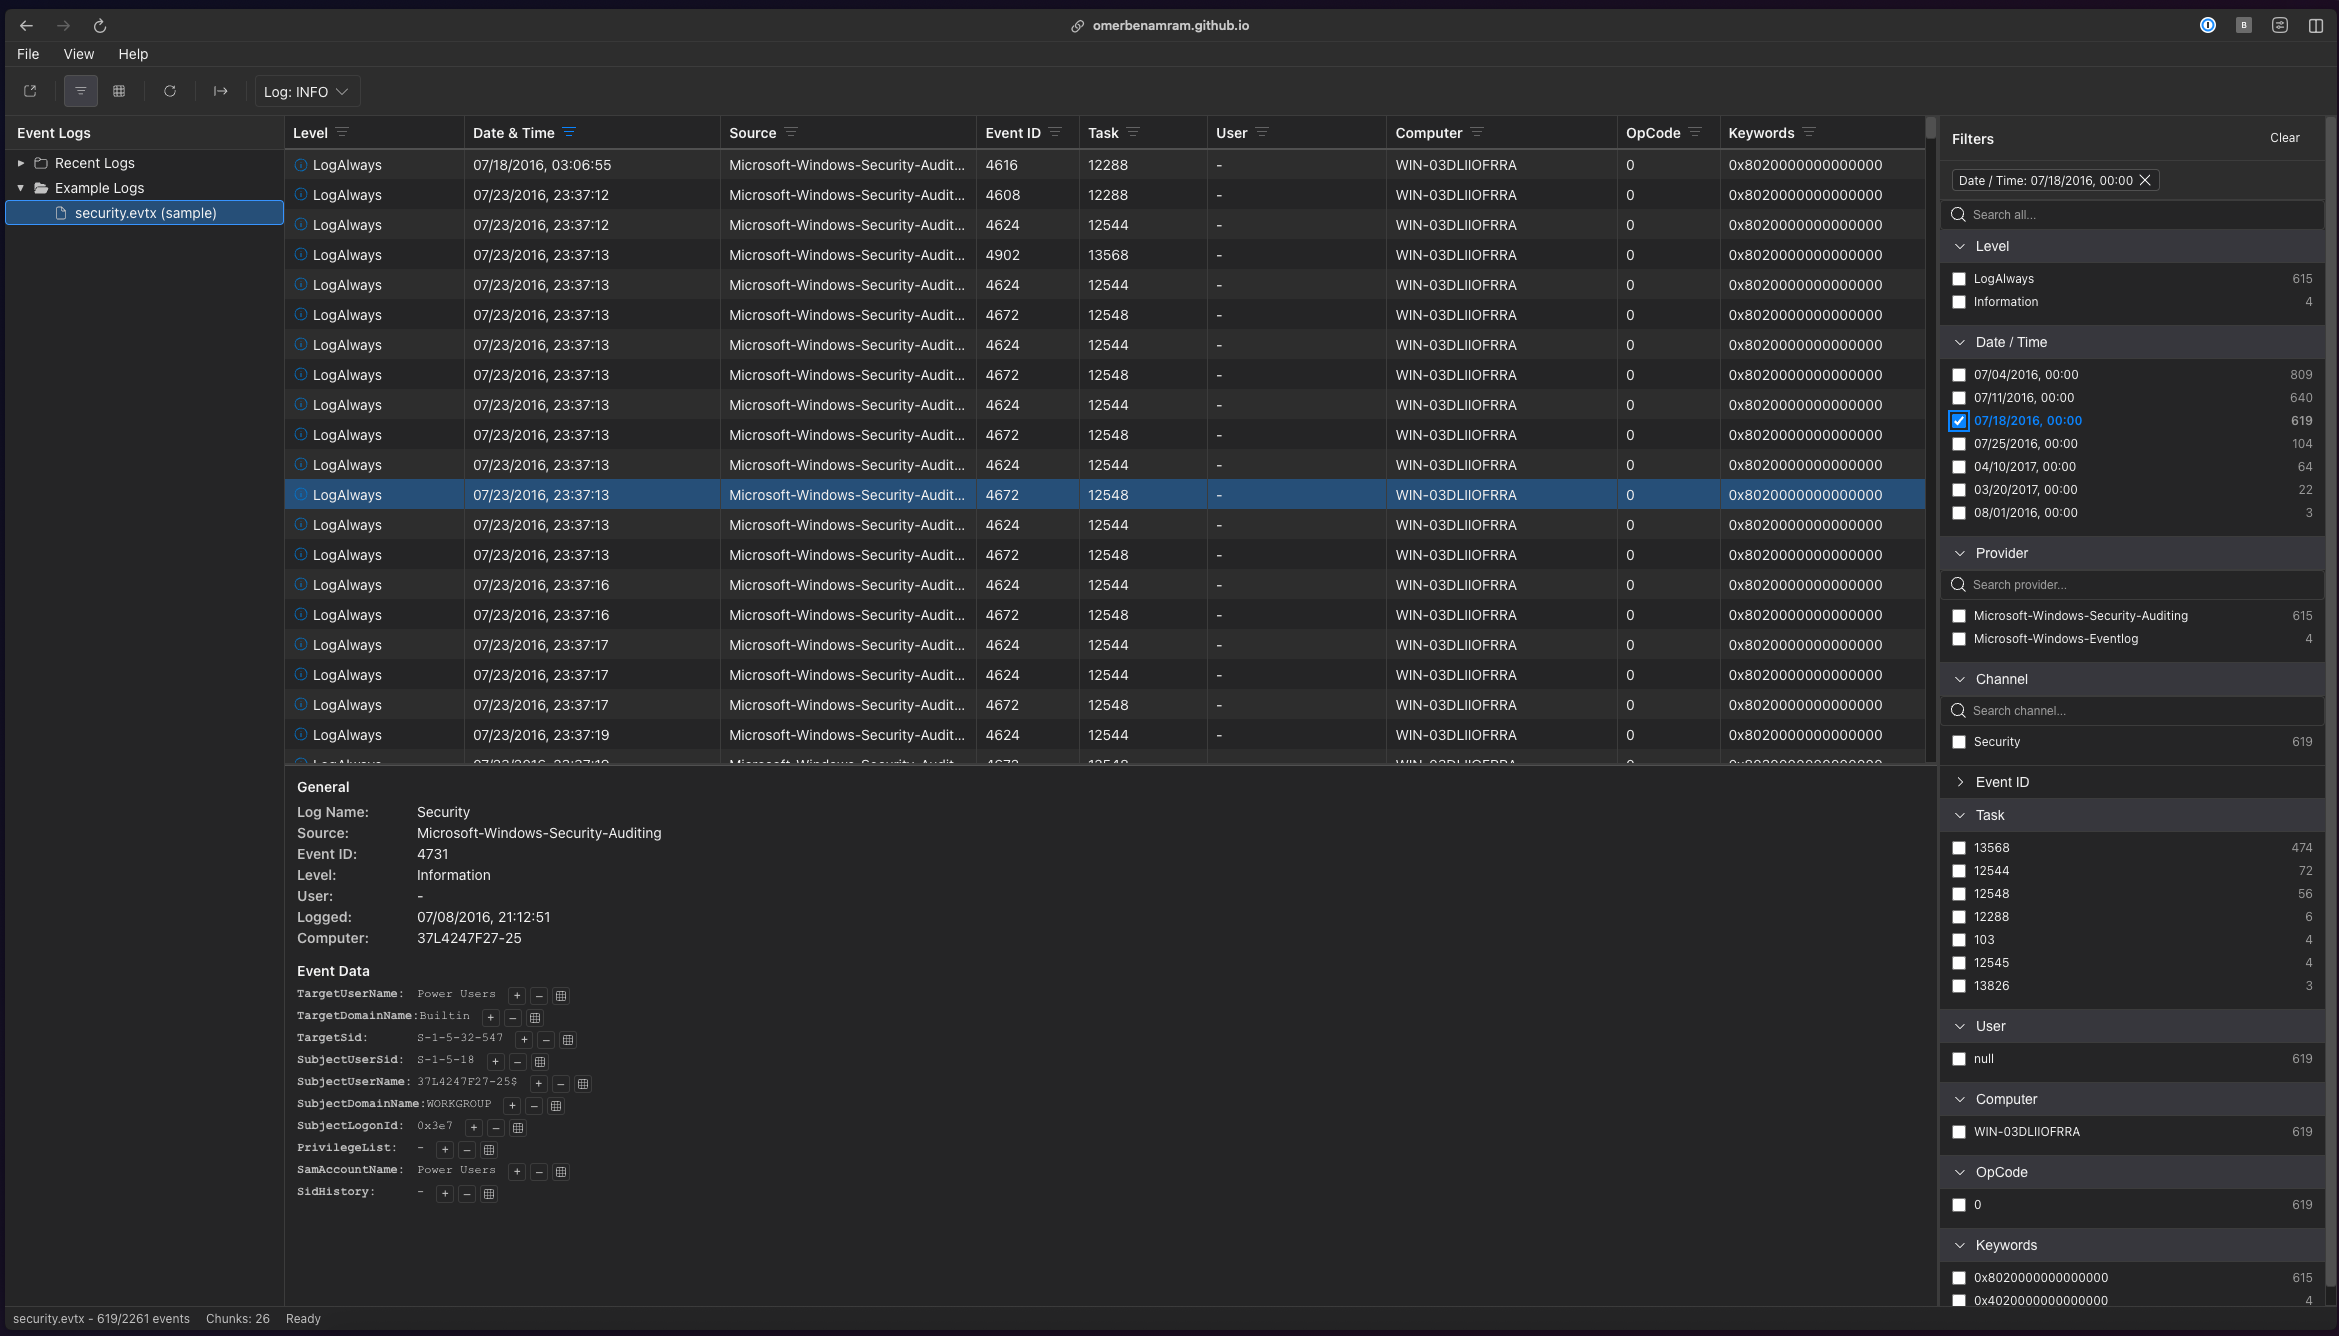 omerbenamram/evtx
A Fast (and safe) parser for the Windows XML Event Log (EVTX) format
 glmcdona/process-dump
Windows tool for dumping malware PE files from memory back to disk for analysis.
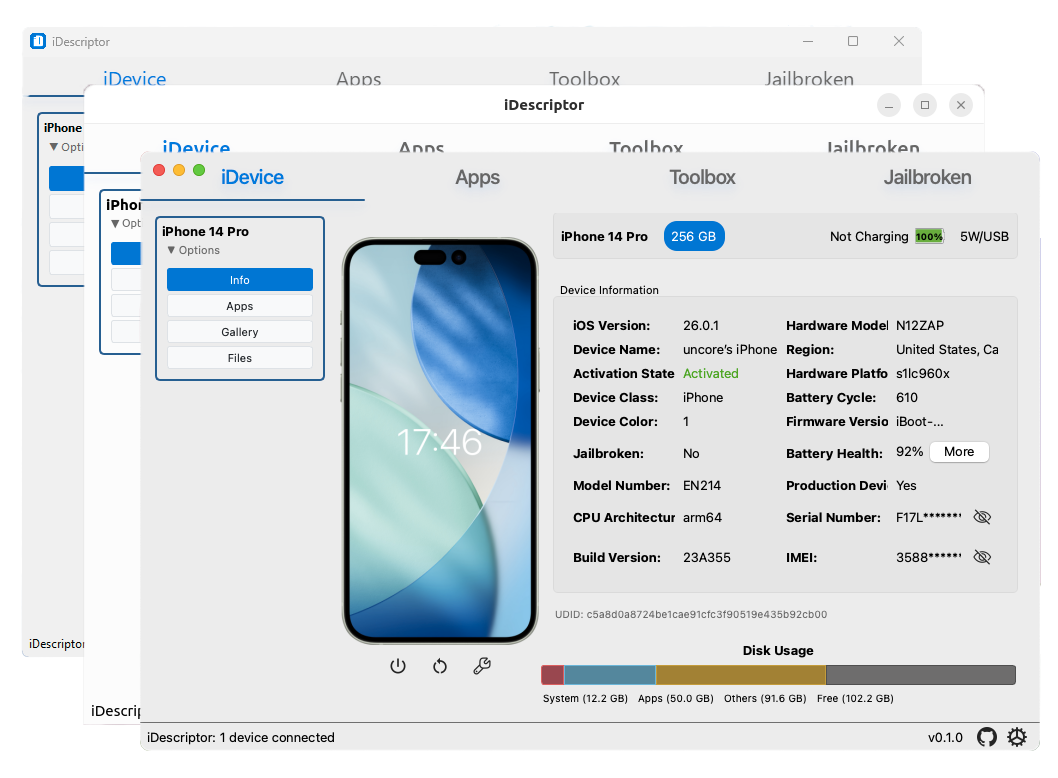 idescriptor/idescriptor
privacy-first, open-source and free idevice management tool written in Rust and Qt
 osquery/osquery
SQL powered operating system instrumentation, monitoring, and analytics.