

Detect-It-Easy
 horsicq/detect-it-easy
Program for determining types of files for Windows, Linux and MacOS.
reconnaissancestatic-analysisdynamic-analysis-sandboxing+10
11.3k
horsicq/detect-it-easyProgram for determining types of files for Windows, Linux and MacOS.

 wireshark/wireshark
Wireshark's official code repository. You can keep the releases coming by donating at https://wiresharkfoundation.org/donate/.
 secdev/scapy
Python-based interactive packet manipulation library for forging, decoding, sending, capturing, and analyzing network packets across a wide range of…
 onekey-sec/unblob
Extract files from any kind of container formats
 wiltodelta/remove-ai-watermarks
Remove visible and invisible AI watermarks from images and video, and AI provenance metadata from images, video, and audio. Python library, CLI, and…
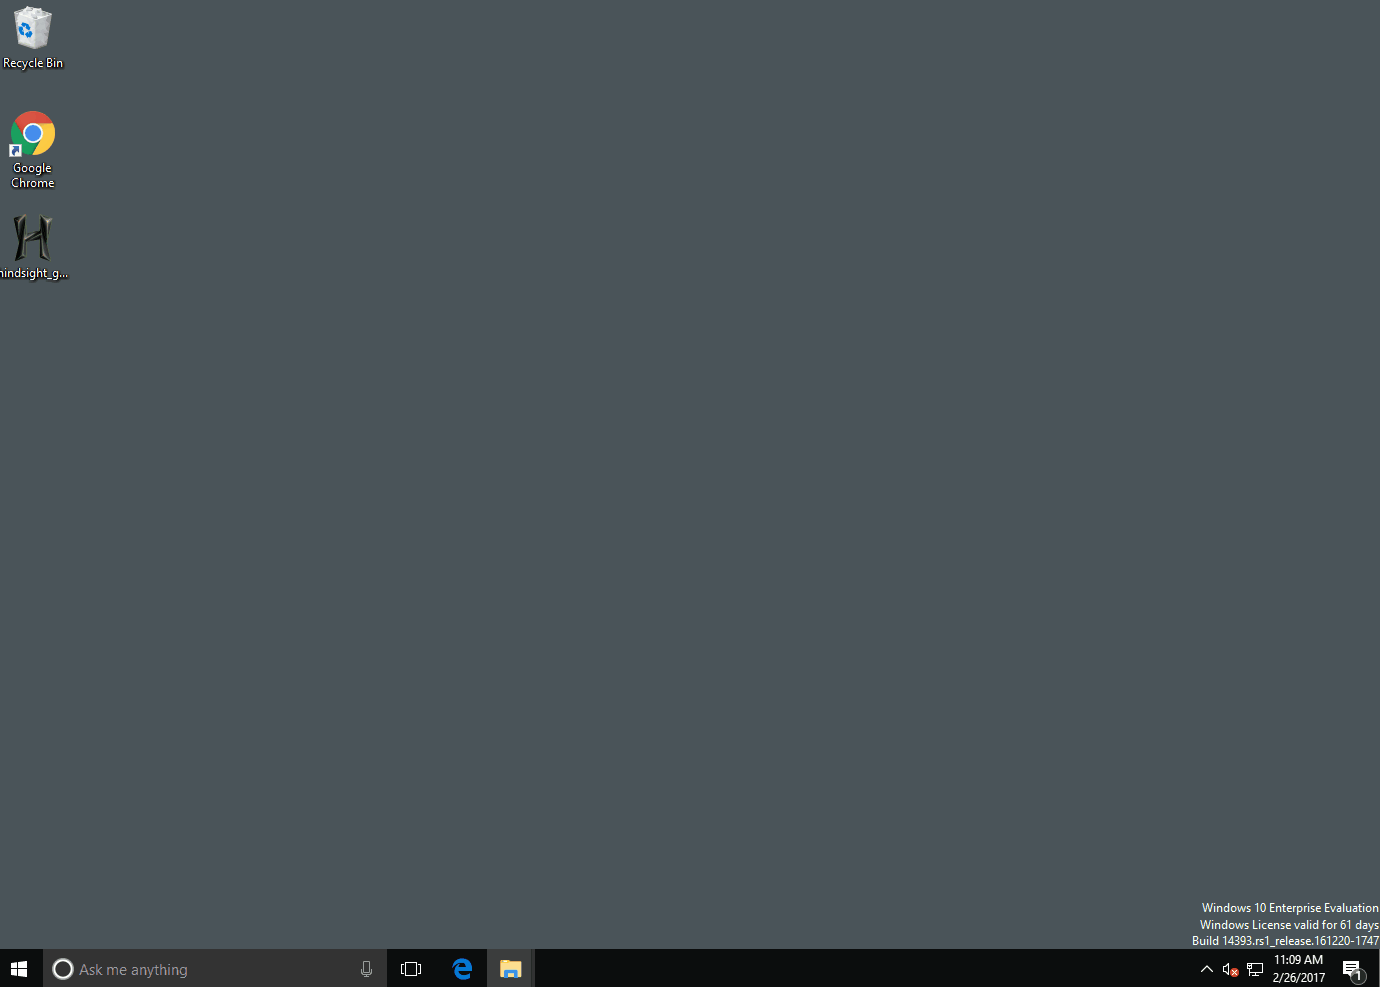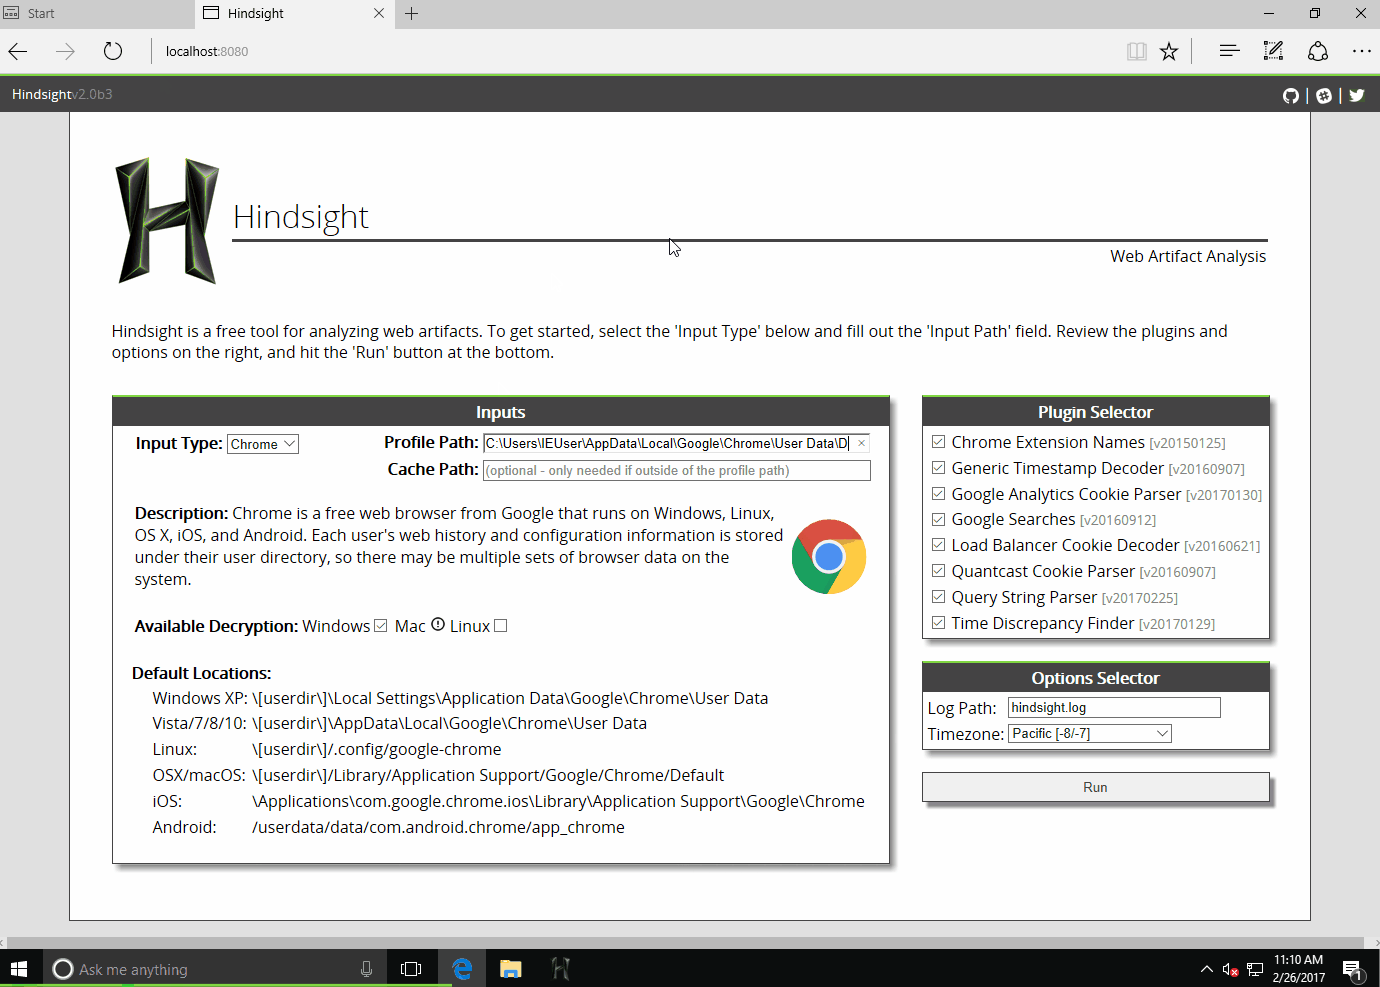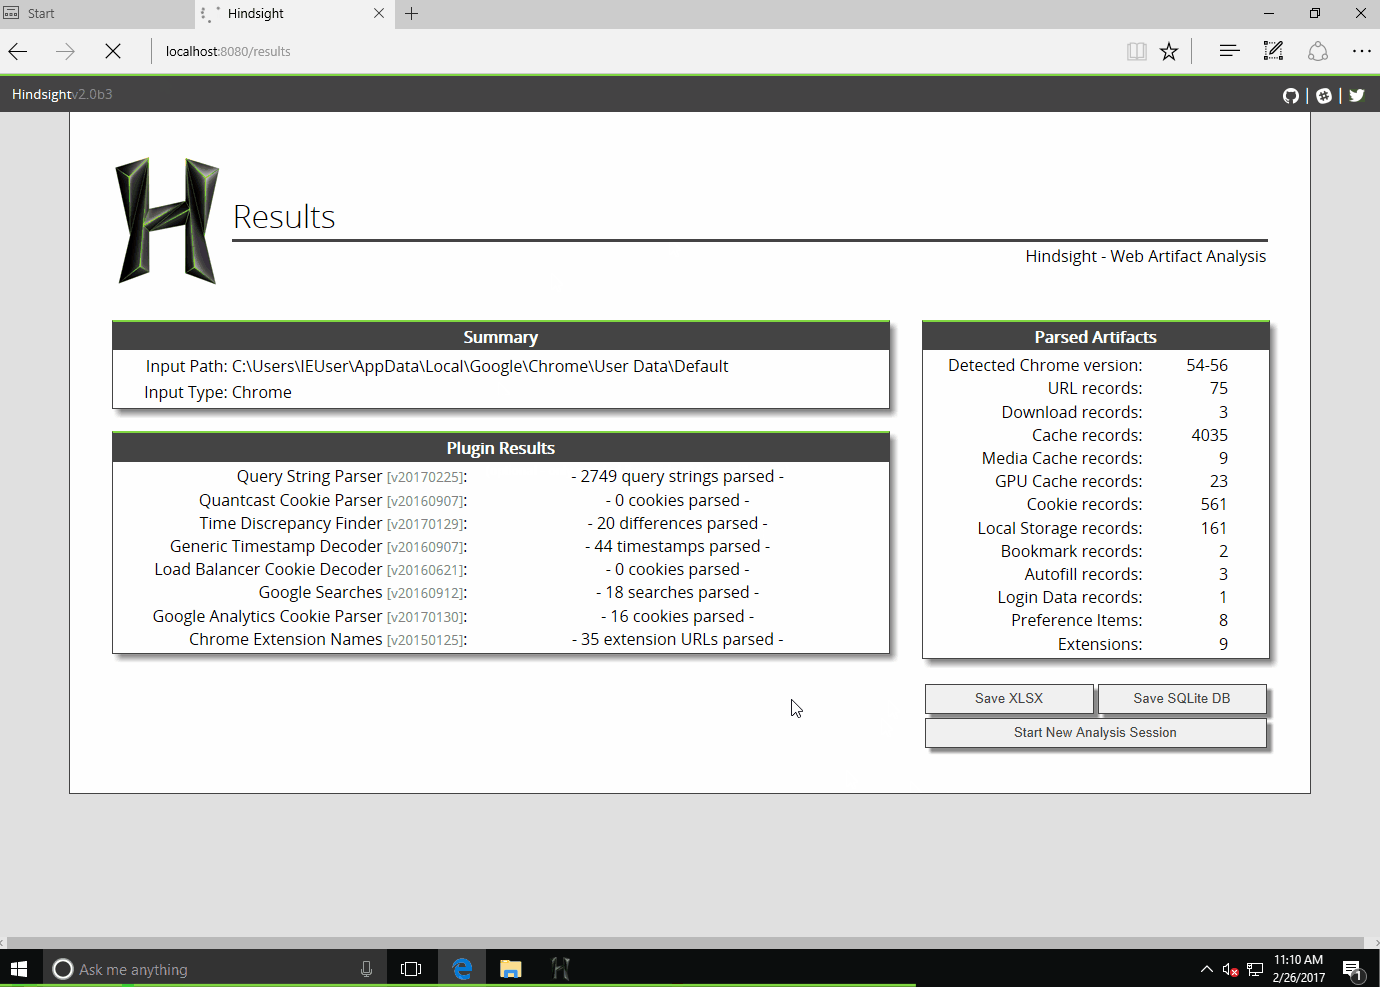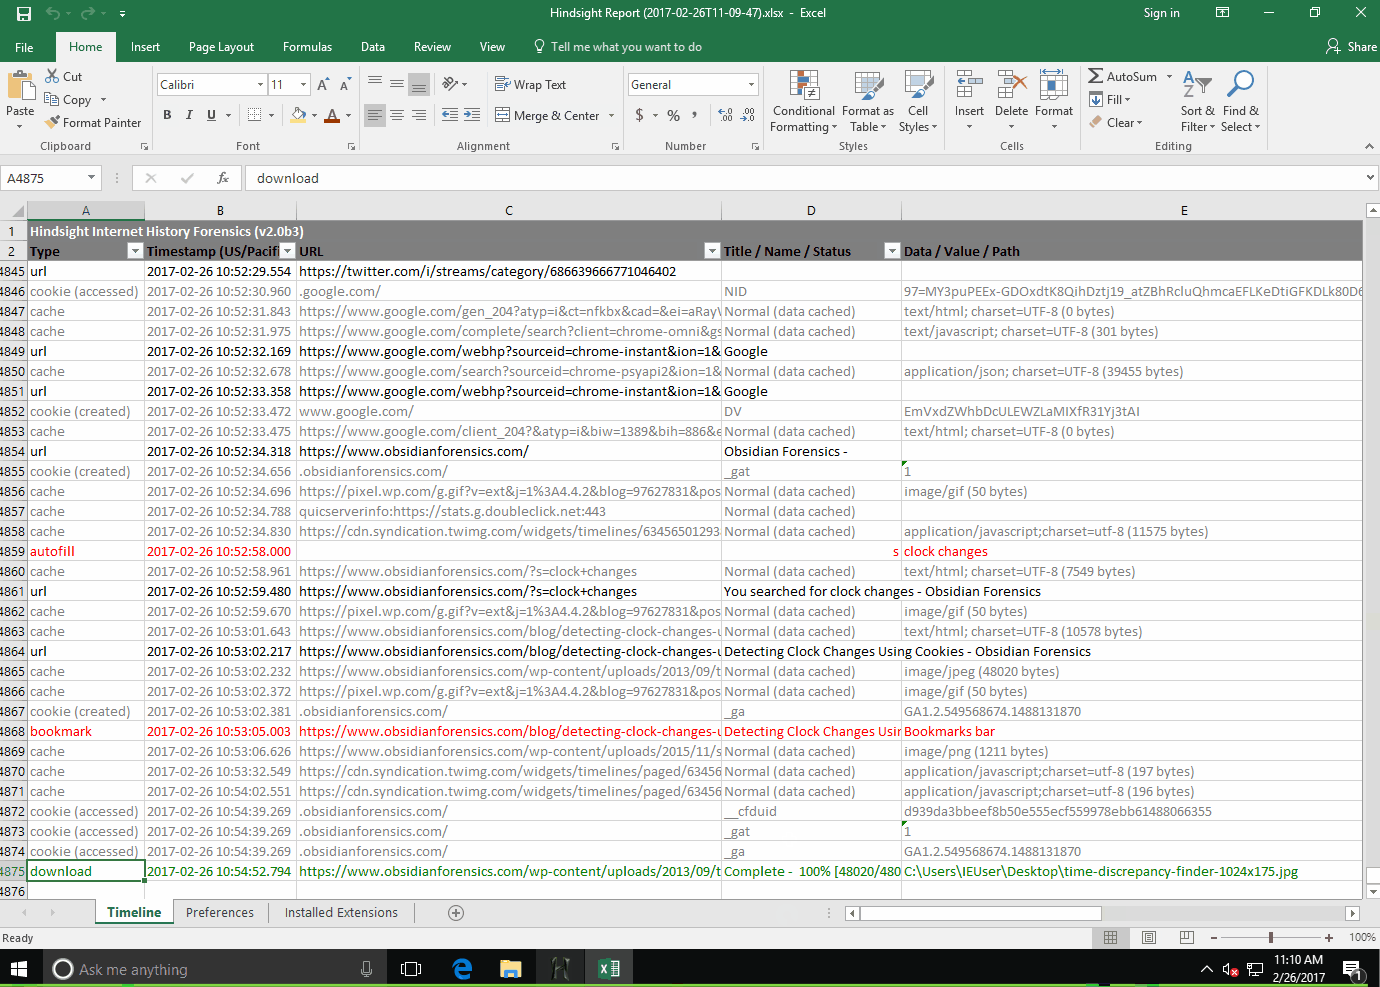 ryandfir/hindsight
Browser forensics tool for Google Chrome, other Chromium-based browsers, and Mozilla Firefox
 radareorg/radare2
UNIX-like reverse engineering framework and command-line toolset
 omerbenamram/evtx
A Fast (and safe) parser for the Windows XML Event Log (EVTX) format
 abrignoni/ileapp
Parses iOS and iPadOS forensic extractions into HTML, TSV, timeline, KML, and LAVA reports with modular artifact discovery and encrypted iTunes…
 ssrajadh/sentrysearch
Semantic search over videos using Gemini Embedding 2 or Qwen3-VL.
 the-tcpdump-group/tcpdump
the TCPdump network dissector
 gamelinux/passivedns
A network sniffer that logs all DNS server replies for use in a passive DNS setup
 wagga40/zircolite
A standalone SIGMA-based detection tool for EVTX, Auditd and Sysmon for Linux logs
 stanfrbd/cyberbro
A simple application that extracts your IoCs from garbage input and checks their reputation using multiple CTI services.
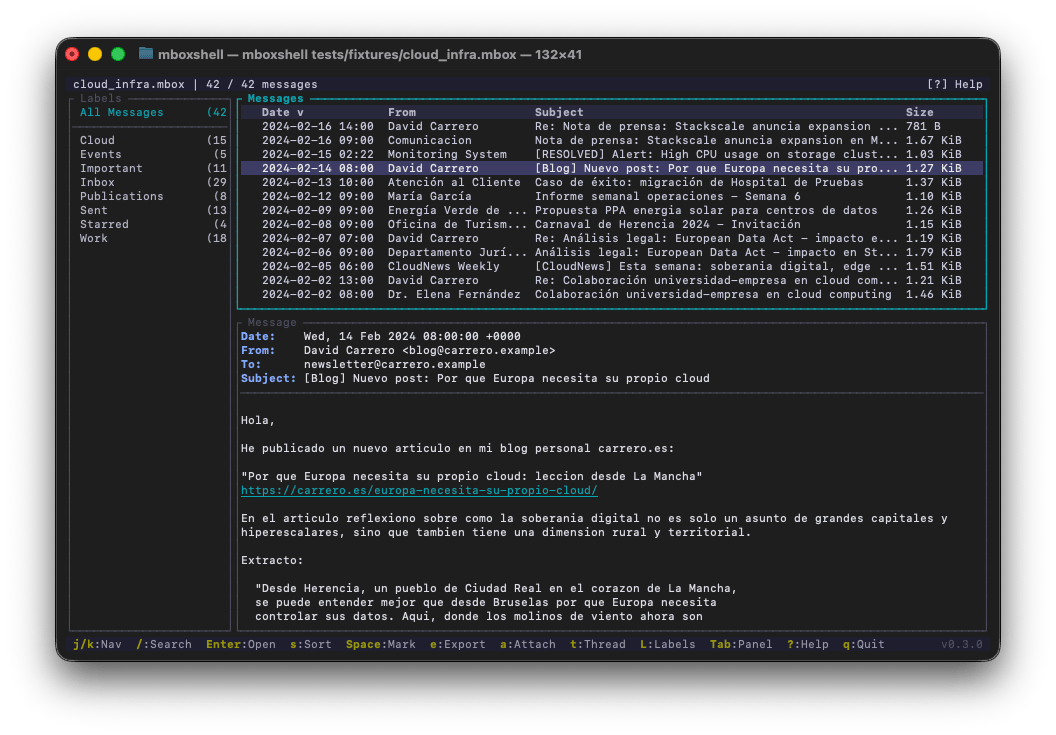 dcarrero/mboxshell
mboxShell. Fast terminal viewer for MBOX files of any size. Open, search and export emails from Gmail Takeout backups (50GB+) without loading them…
 winsiderss/systeminformer
Real-time Windows system monitor with advanced process, network, and disk analysis, stack trace debugging, malware detection, and service management.…
 arkime/arkime
Arkime is an open source, large scale, full packet capturing, indexing, and database system.
 log2timeline/plaso
Digital forensics engine that parses logs, files, and system artifacts to build super timelines, enabling chronological event correlation for…