
CVE-2024-48705
 l41kaa/cve-2024-48705
Wavlink AC1200 with firmware versions M32A3_V1410_230602 and M32A3_V1410_240222 are vulnerable to a post-authentication command injection while…
binary-analysiscommand-and-controlembedded-systems-security+7
2
l41kaa/cve-2024-48705Wavlink AC1200 with firmware versions M32A3_V1410_230602 and M32A3_V1410_240222 are vulnerable to a post-authentication command injection while…
 ivmks74/iiita-iot-security-research
IoT Security research conducted during my internship at IIIT Allahabad, leading to CVE-2026-65893, CVE-2026-65894, and the CERT-In Vulnerability Note…
 ozcanpng/cve-2026-76071
Original research and PoC for a pre-auth stack buffer overflow via unbounded sscanf scanset in the Netis NC63 ipFilterList handler
 tobss8/gigabyte-h510m-k-v2-bios-smm-reverse-engineering-cve-2025-7026-7027-7028-7029-research
Static reverse-engineering of a GIGABYTE H510M K V2 (`H510MKV2.F3`) BIOS image: full UEFI firmware-volume extraction analysis of the PI-spec SMM Core…
 micaelmaciel/cve-2024-55211
Cookie-based authentication vulnerability on Tk-Rt-Wr135G
 xernary/cve-2025-63821
Proof-of-concept of vulnerability found in Totolink A720R router
 234329a423853/cve-2021-4045
CVE-2021-4045 CVE-2021-4045 is a Command Injection vulnerability that allows Remote Code Execution in the TP-Link Tapo c200 IP camera. It affects all…
 t4e-3/cve-2025-63296
KERUI K259 5MP Wi-Fi (Tuya Smart Security Camera) contains a code execution vulnerability
 kaisersource/cve-2021-3166
Proof-of-concept exploit for CVE-2021-3166 targeting ASUS DSL-N14U routers via malicious firmware upload, triggering a denial-of-service condition.
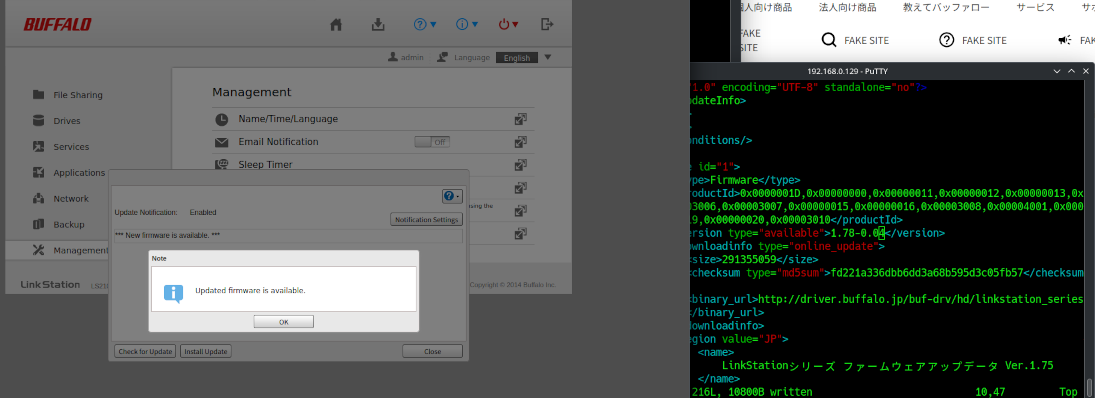 christopher-pace/cve-2023-51073
Firmware Update Server Verification Vulnerability on Buffalo LS210D Version 1.78-0.03

 hunt-benito/the-same-key-opens-every-box-cve-2026-71960-hard-coded-jwt-secret-in-cudy-wr3000-mesh-mqtt
PoC toolkit that unpacks router firmware, decrypts device secrets, forges JWT tokens, and exploits CVE-2026-71960/71961 to take over Cudy WR3000 mesh…
 platomav/mcextractor
Intel, AMD, VIA & Freescale Microcode Extraction Tool
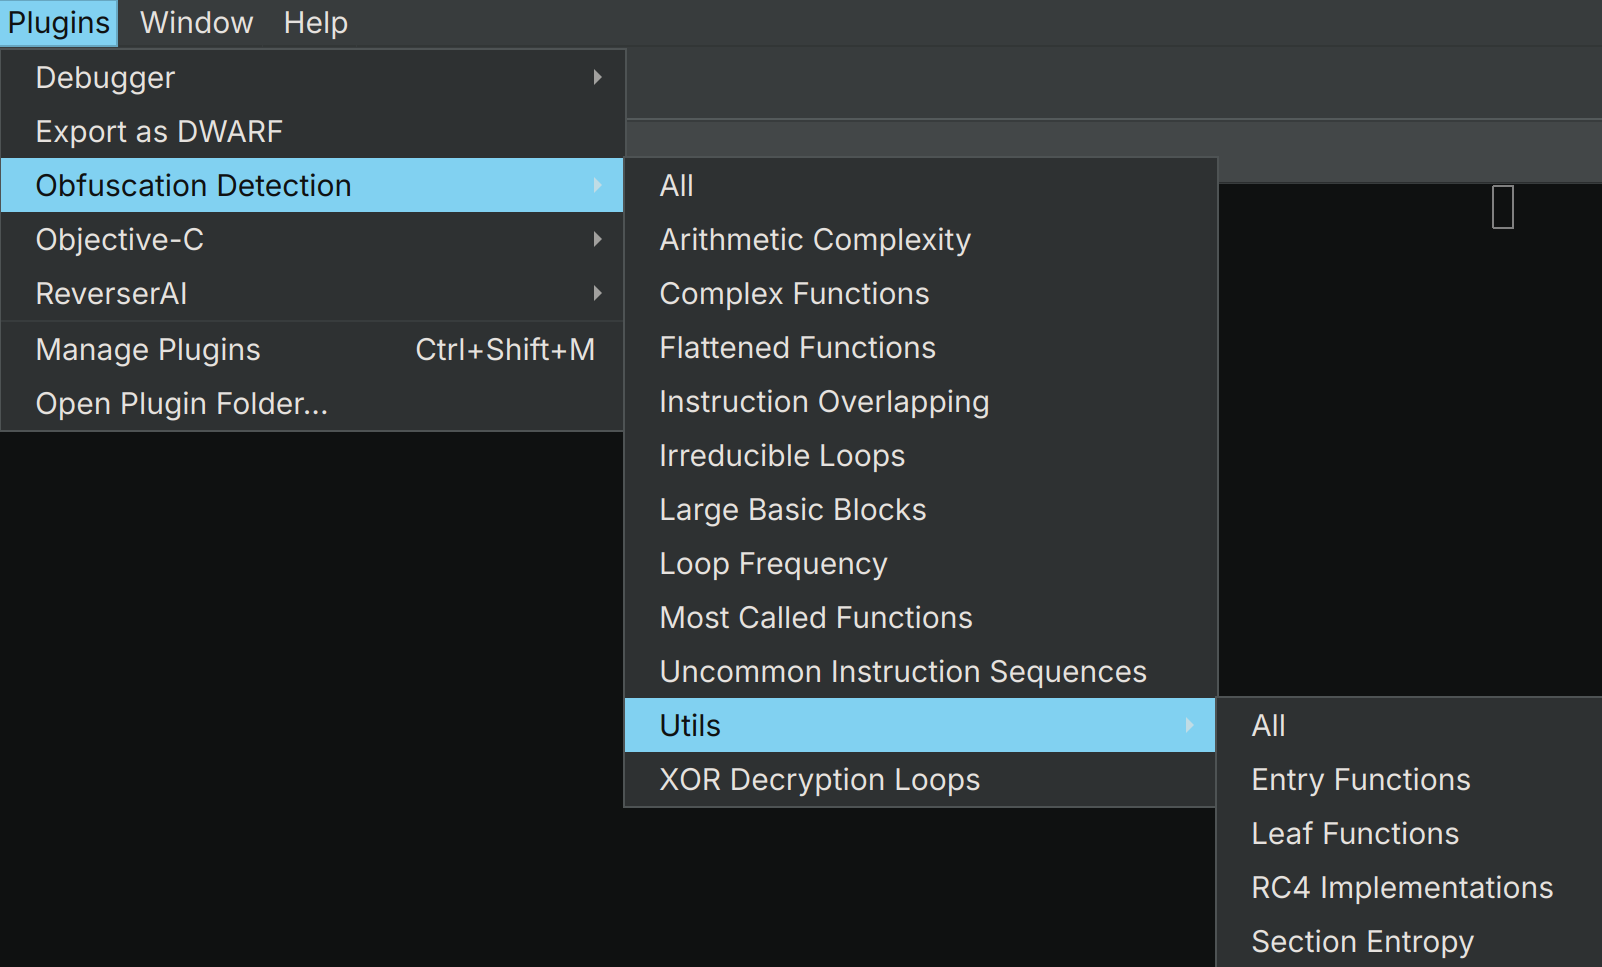 mrphrazer/obfuscation_detection
Binary Ninja plugin to identify obfuscated code and other interesting code constructs
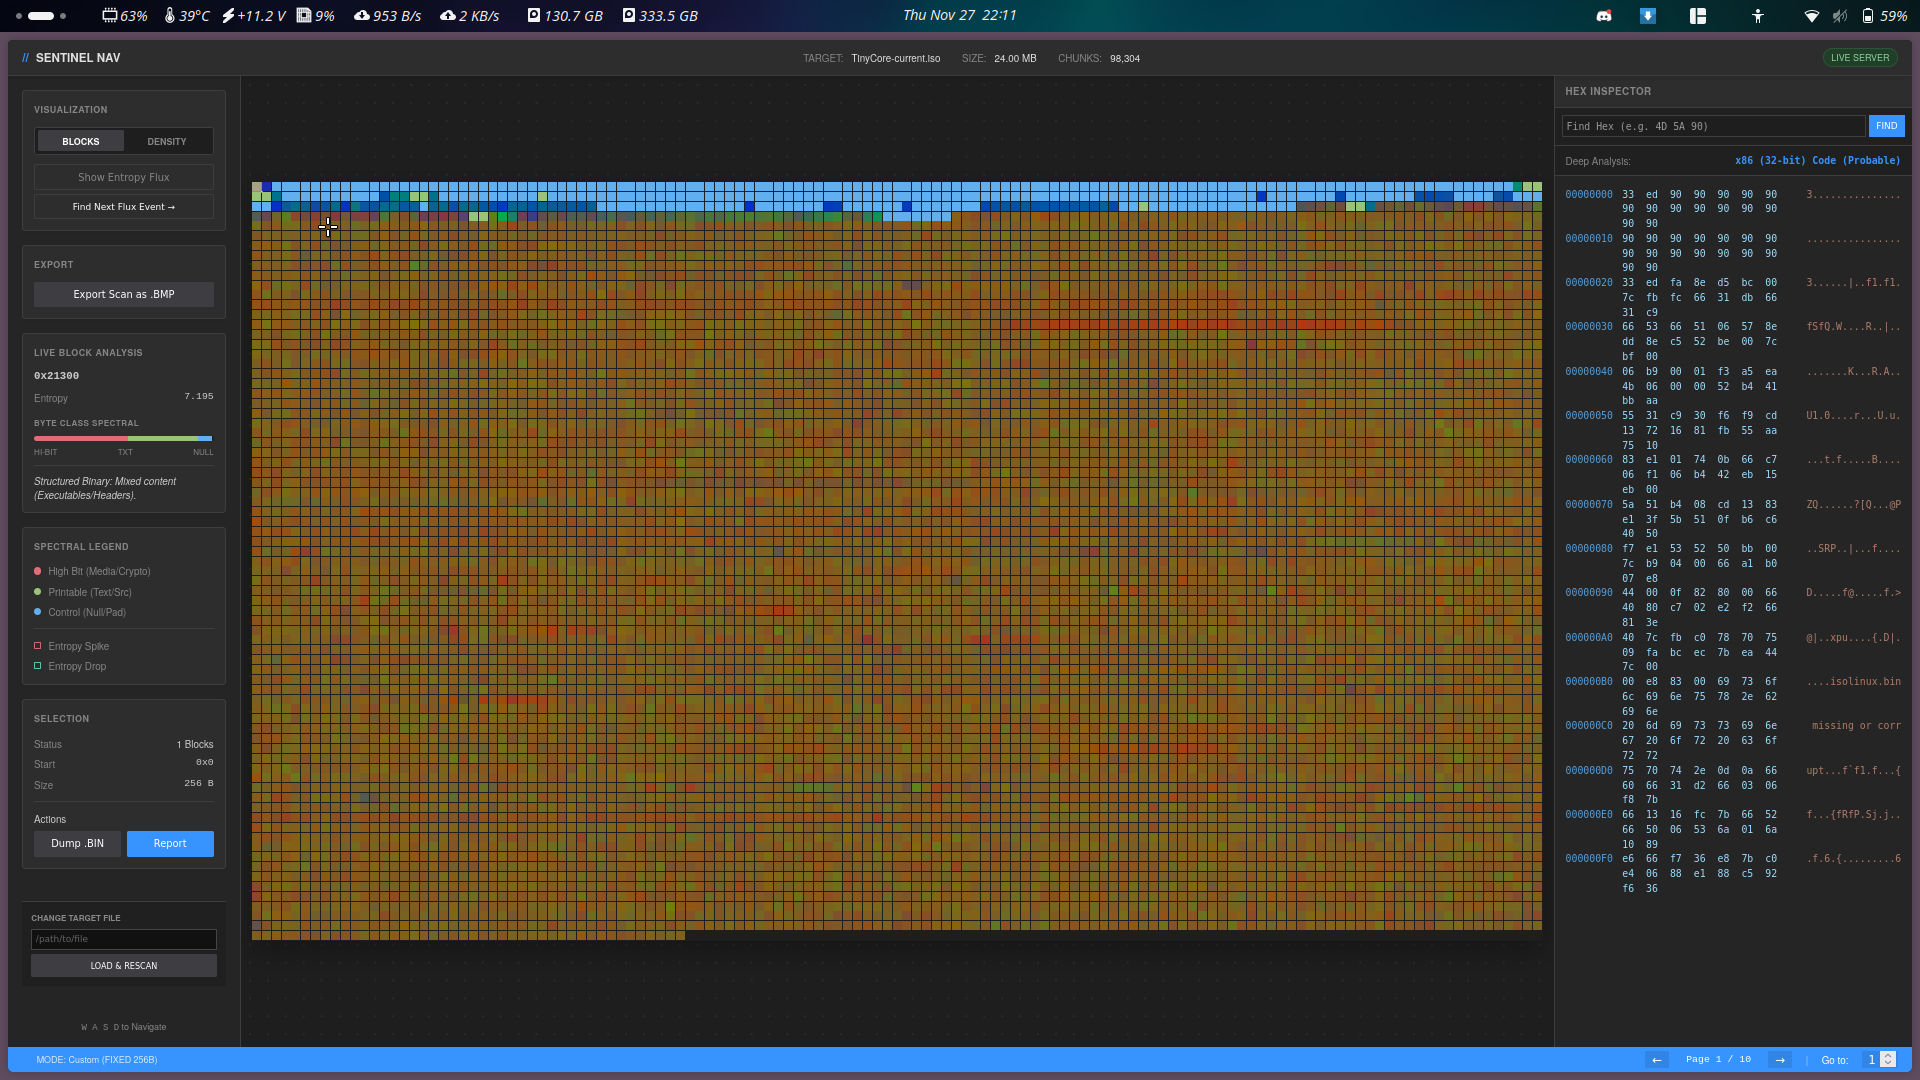 smolfiddle/sentinelnav
SentinelNav: zero-dependency, pure Python binary visualization and forensics tool.
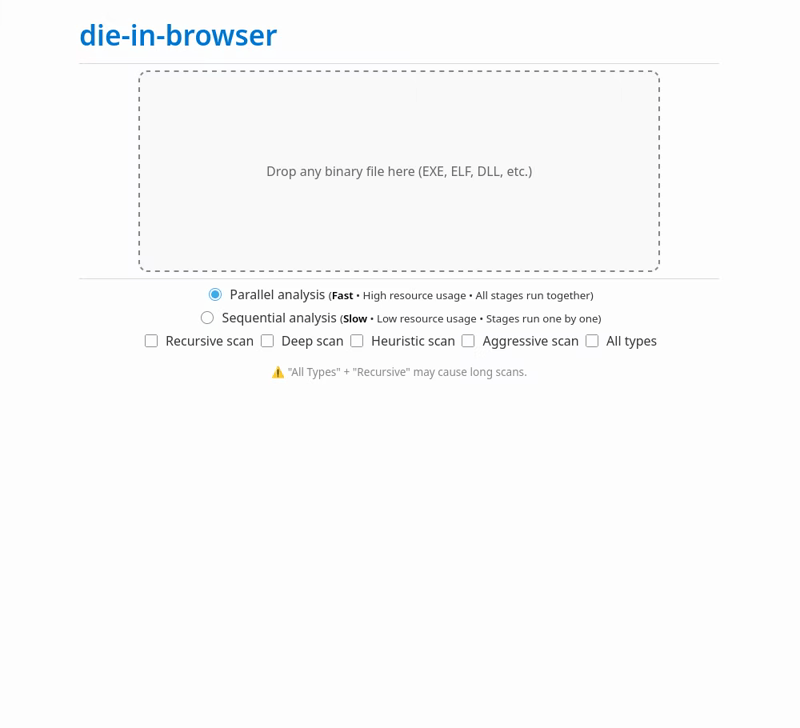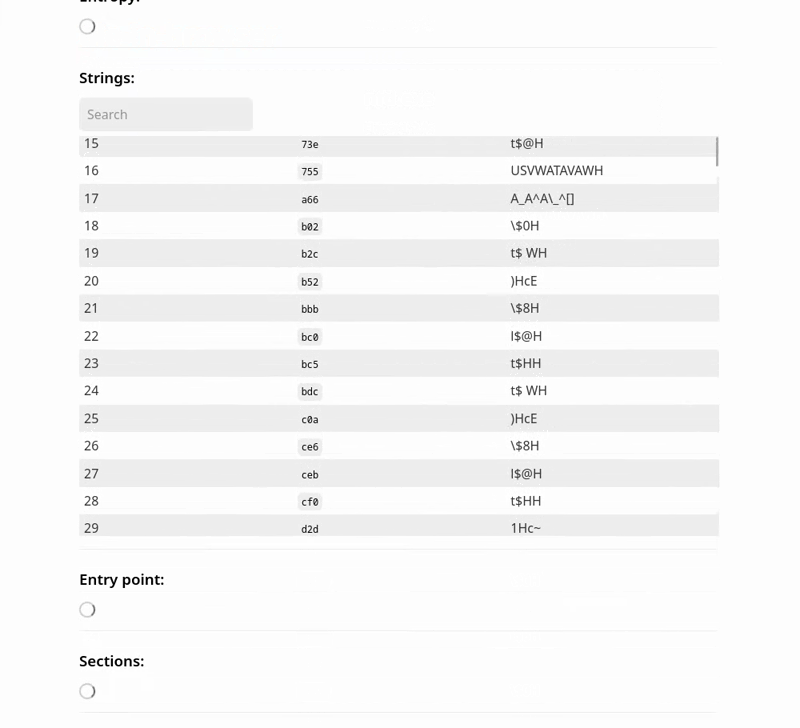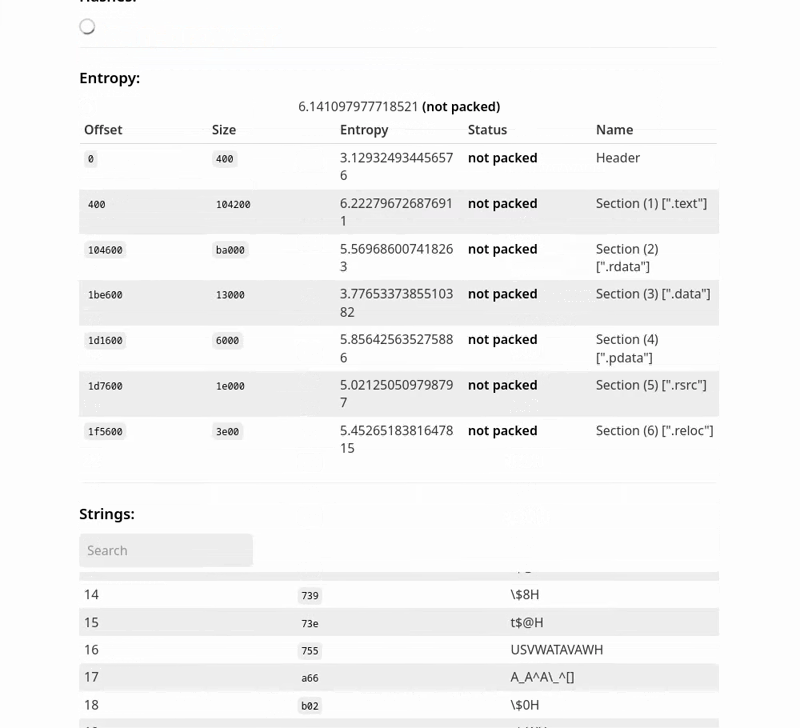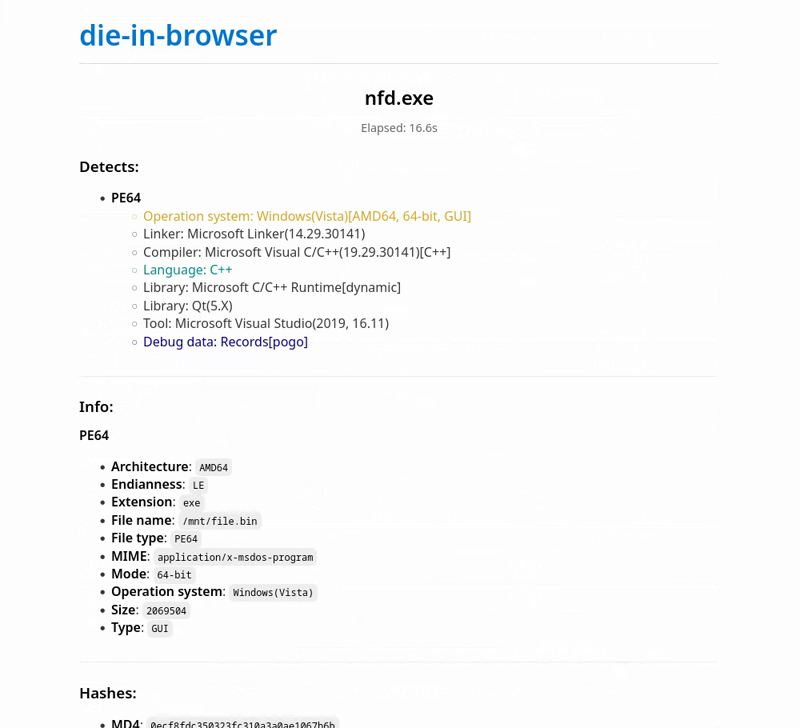 xoreaxlmbdx/die-in-browser
Static binary analysis with Detect It Easy — 100% in your browser, no uploads.
 namaek2/cve-2025-70962
CVE-2025-70962 PoC
 michaeladamgroberman/cve-2025-1242
CVE-2025-1242: Hardcoded iothubowner Connection String — Gardyn Home Kit (ICSA-26-055-03)