firmware-reverse-engineering

Agent skills for firmware extraction, static analysis, Ghidra reverse engineering, emulation, and security reporting, packaged for Claude Code and…

Agent skills for firmware extraction, static analysis, Ghidra reverse engineering, emulation, and security reporting, packaged for Claude Code and…

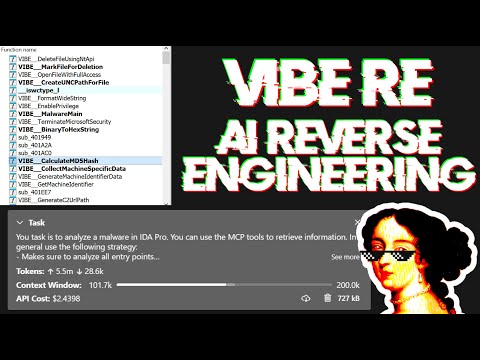
AI-powered reverse engineering assistant that bridges IDA Pro with language models through MCP.

MCP server for reverse engineering Windows executables and binary formats. Combines static triage, Ghidra-assisted function recovery, plugin-driven…

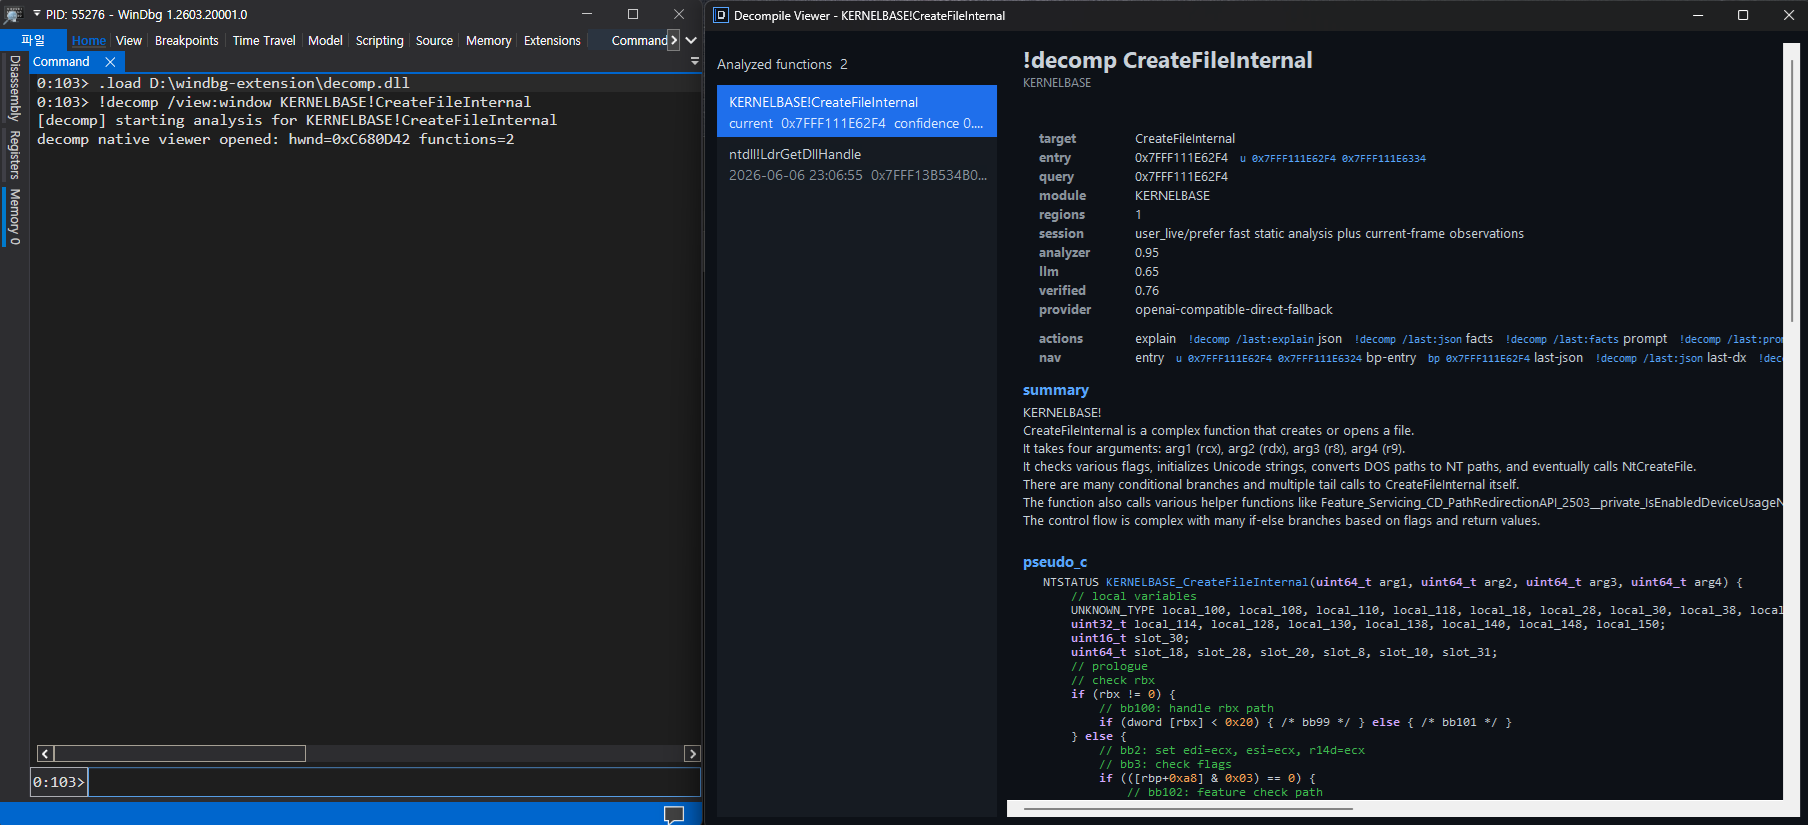
WinDbg x64 extension that disassembles live functions and uses an LLM to produce verified pseudocode.

Reverse engineering NVIDIA SASS instruction dictionary, kernel audits and pattern recognition across GPU architectures.

Static reverse-engineering of a GIGABYTE H510M K V2 (`H510MKV2.F3`) BIOS image: full UEFI firmware-volume extraction analysis of the PI-spec SMM Core…

A fast, portable, and lightweight COSE + CBOR implementation for embedded systems. Supports PQC, FIPS 140-3, DO-178, and MISRA C. Powered by wolfSSL.

Standalone MCP server plugin for IDA Pro.

Python Command-Line Ghidra MCP

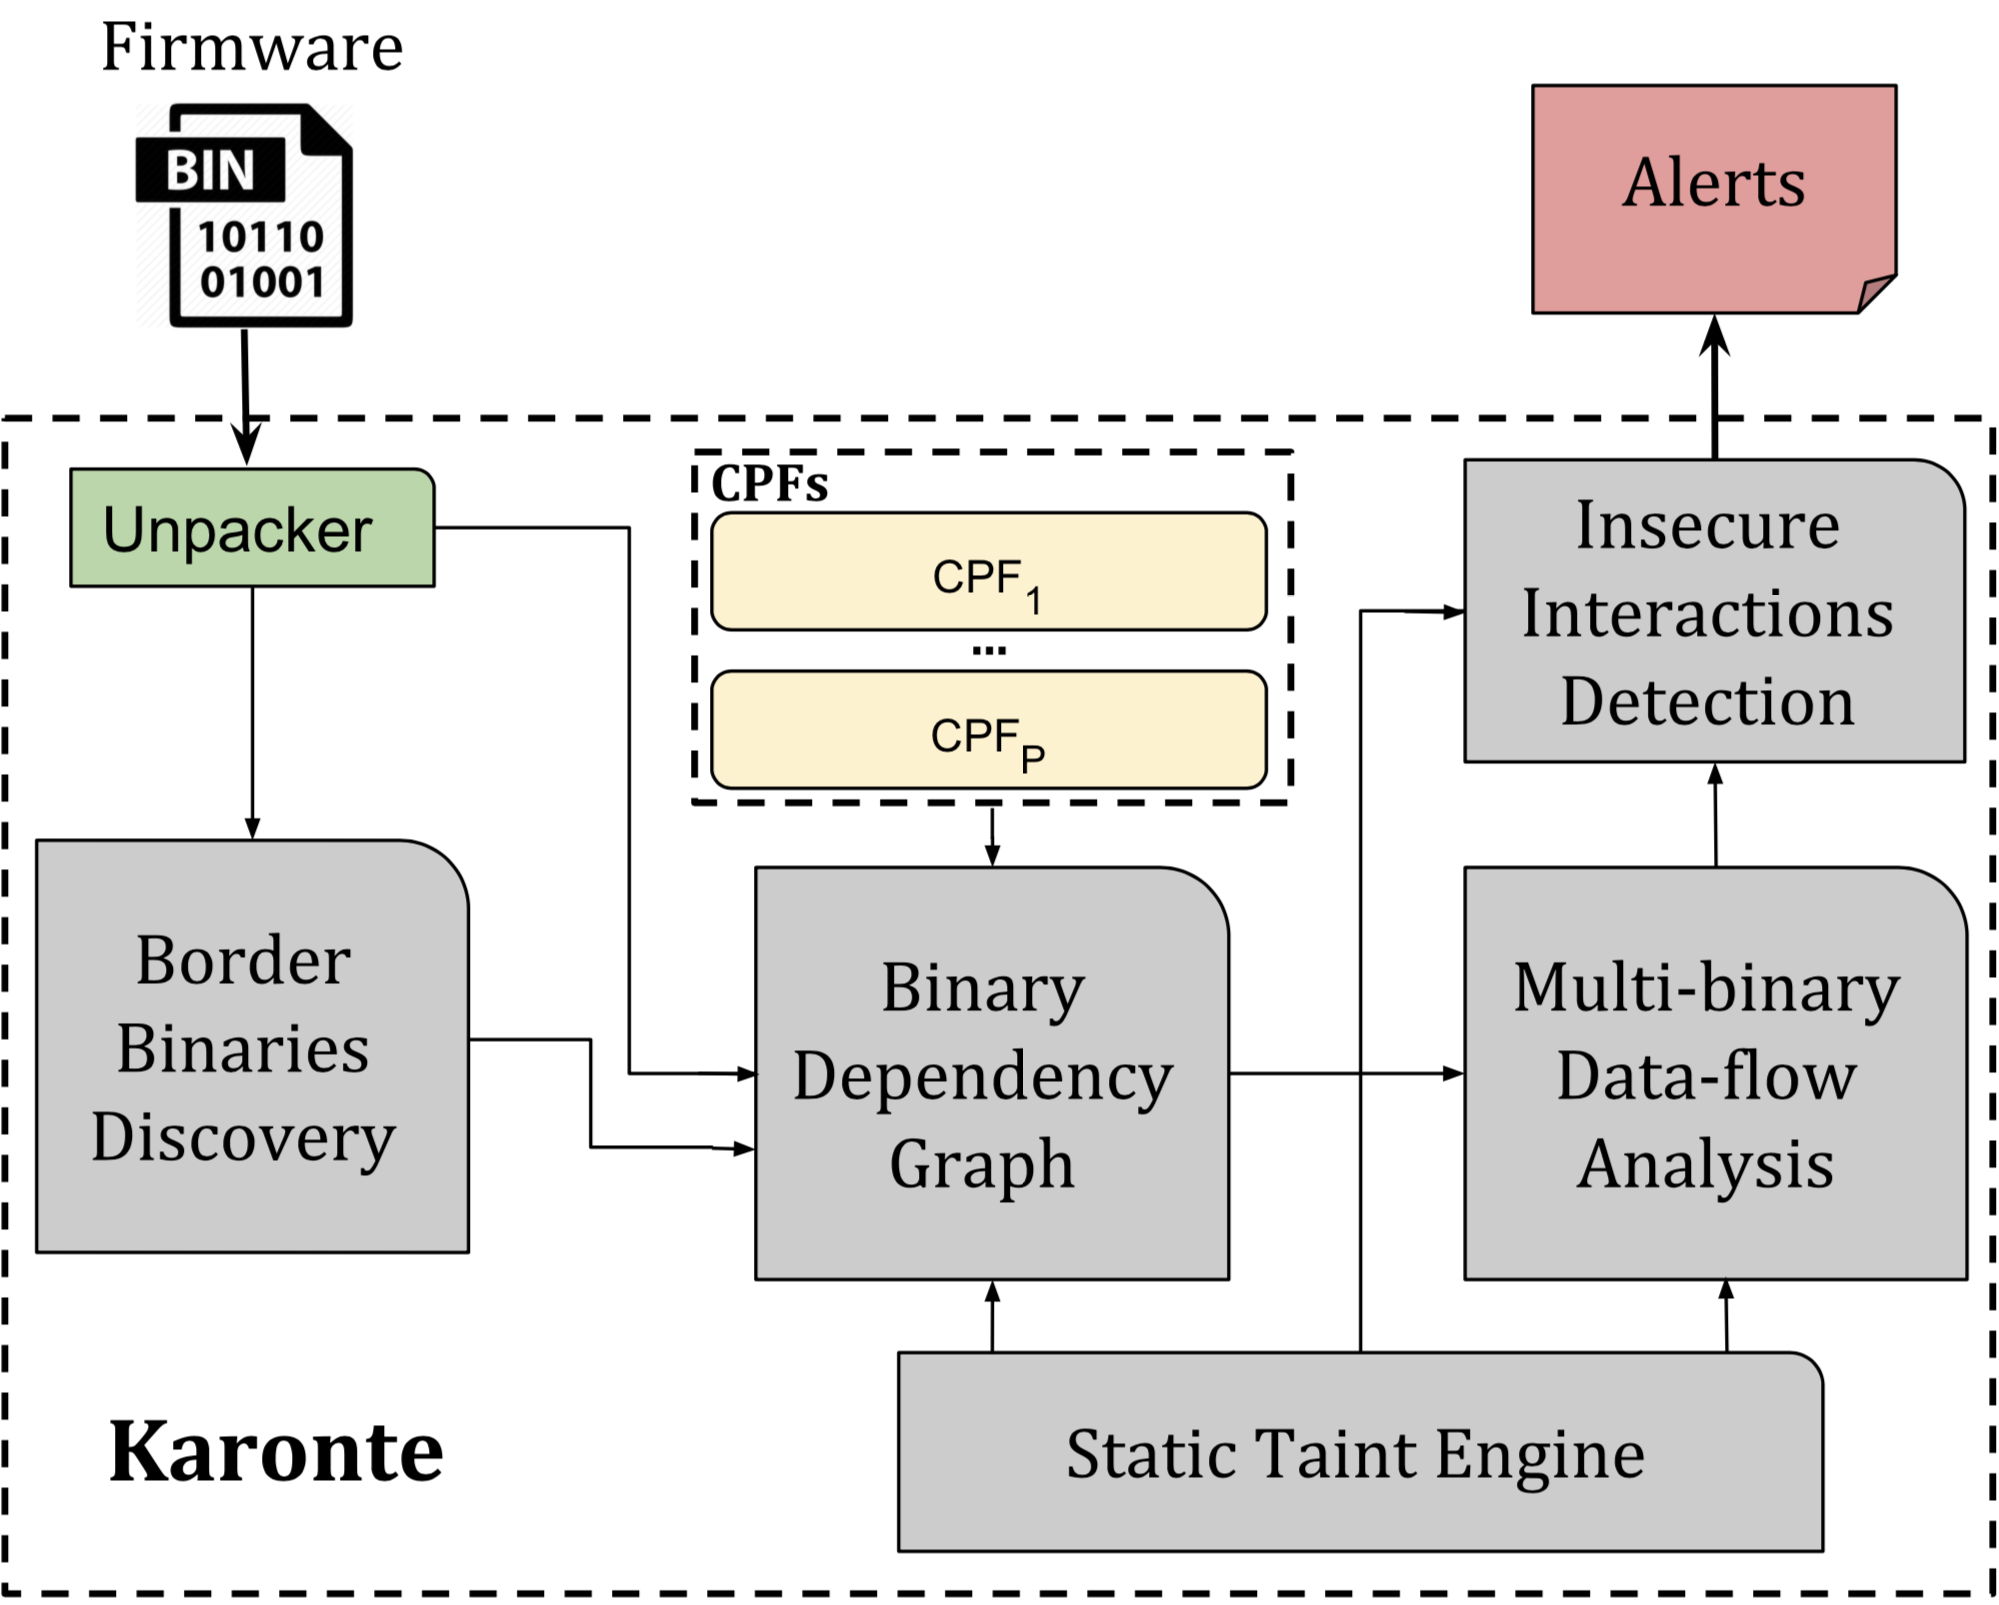
Karonte is a static analysis tool to detect multi-binary vulnerabilities in embedded firmware

Static analysis (Ghidra) and custom packet-crafting (Scapy) demonstrating a root-level DHCP command injection vulnerability (CVE-2025-14659) in…

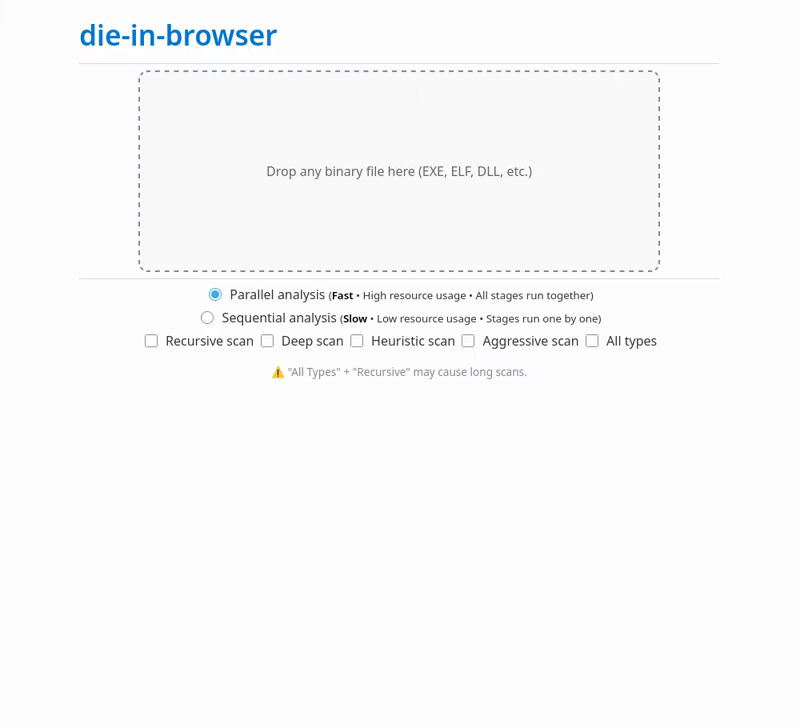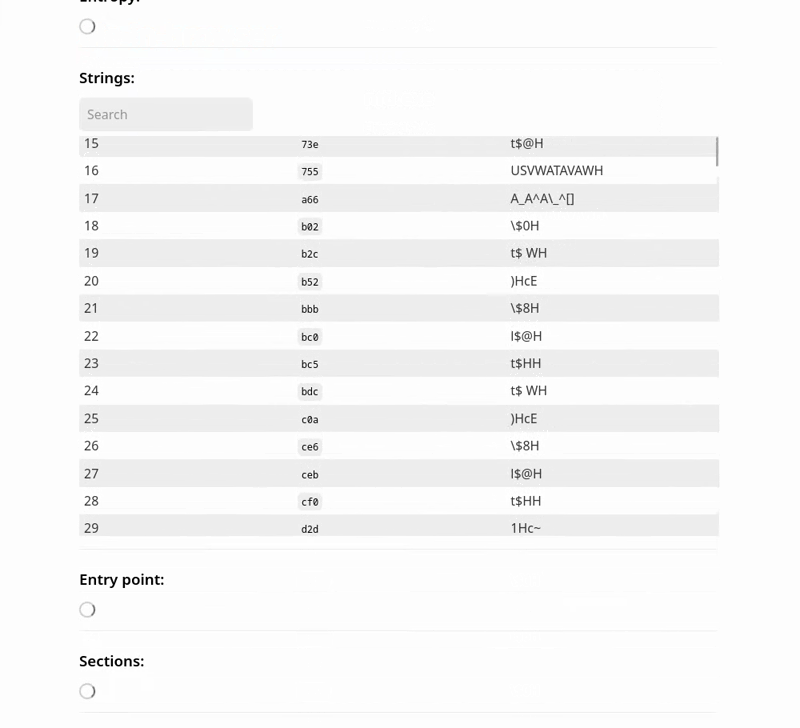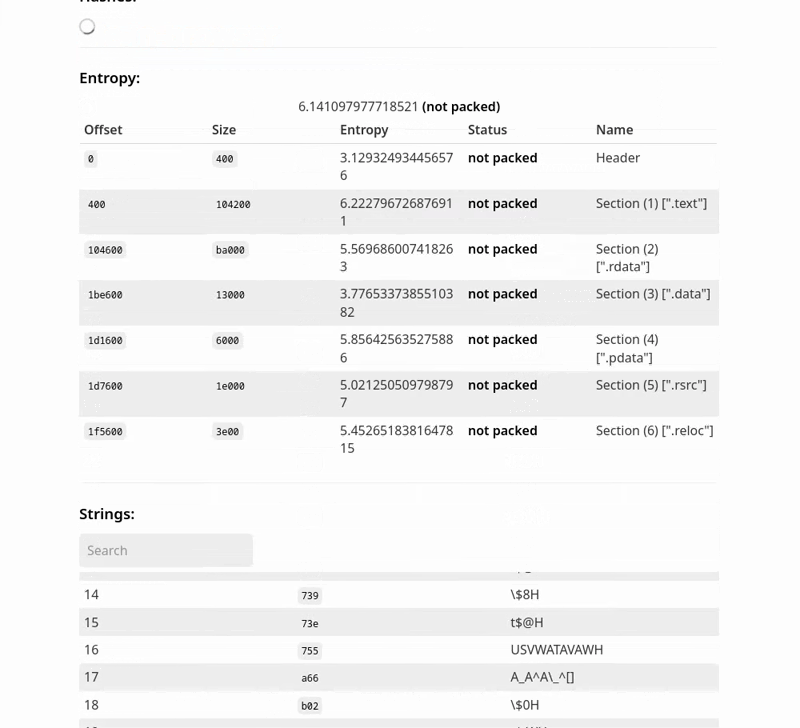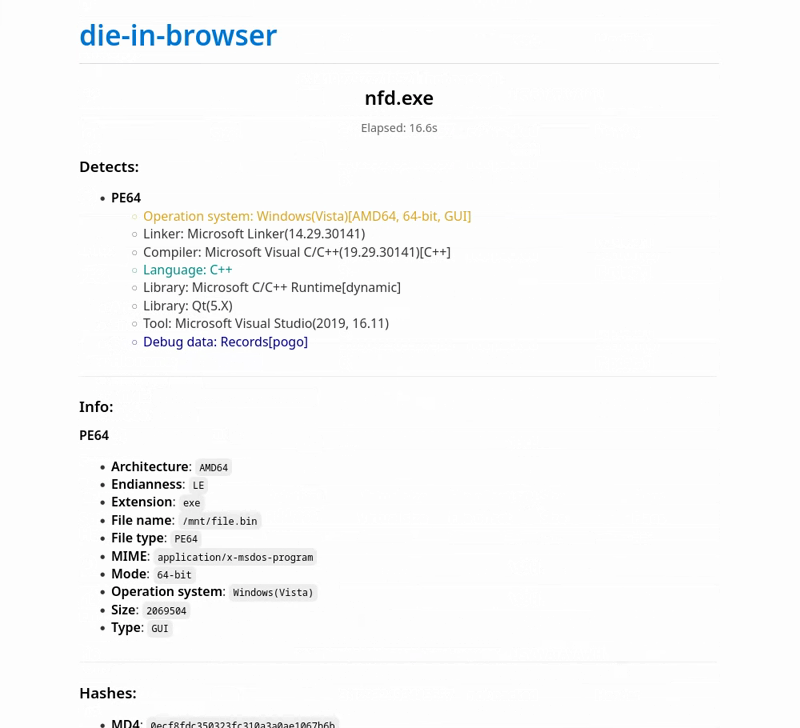
Static binary analysis with Detect It Easy — 100% in your browser, no uploads.

Deliberately insecure OpenWrt-based firmware for hands-on IoT security training. Features vulnerability challenges mapped to the OWASP IoT Top 10 for…

Exploit and firmware analysis toolkit for Canon MF644 printer vulnerabilities, including Python exploits, ARM shellcode, and IDA Pro loader scripts…

Library for lifting machine code to LLVM bitcode

LLVM based static binary analysis framework

Lightweight Protocol Buffers implementation in ANSI C for microcontrollers and memory-restricted embedded systems, enabling efficient serialization…