
CVE-2024-12849-Poc
 nxploited/cve-2024-12849-poc
Exploit for CVE-2024-12849, an arbitrary file read vulnerability in WordPress Error Log Viewer plugin. Downloads sensitive files via unauthenticated…
data-exfiltrationexploitationpenetration-testing+2
nxploited/cve-2024-12849-pocExploit for CVE-2024-12849, an arbitrary file read vulnerability in WordPress Error Log Viewer plugin. Downloads sensitive files via unauthenticated…
 horizon3ai/vcenter_saml_login
A tool to extract the IdP cert from vCenter backups and log in as Administrator
 nhh9905/cve-2026-62735
Proof-of-concept for CVE-2026-62735, an integer overflow in http.sys leading to heap overflow and SYSTEM shell. Includes crash log and stack trace…
 canyie/cve-2024-23700
PoC for CVE-2024-23700, Android slient privilege escalation allow to read/write contacts, SMS, calendar, call log and voicemail, make outgoing calls…
 eriknl/cve-2020-16152
Proof-of-concept exploit for CVE-2020-16152: LFI-to-RCE in Aerohive/Extreme Networks HiveOS via PHP string truncation and log poisoning, enabling…
 cxlfhx/ghostlock-pfem10
GhostLock (CVE-2026-43499 / IonStack) research for OPPO Find X5 Pro (PFEM10): exploit chain, progress, blocker log, and OPPO 5-series kernel notes
 nhh9905/cve-2026-34344
PoC for CVE-2026-34344, a Windows afd.sys type confusion causing a kernel crash via AfdQueryProviderInfo. Provides trigger code, crash log, and…
 jaf0rk/cve-2026-5281
Proof-of-concept exploit for CVE-2026-5281, a heap-use-after-free vulnerability in Chromium's Dawn WebGPU implementation, with ASAN log and build…
 layer-6/cve-2026-5027-langflow
Multi-CVE exploit tool for pre-auth remote code execution on Ivanti Sentry and FortiSandbox. Features interactive shell, webshell deployment,…
 vinh0212/cve-2024-23700
PoC for CVE-2024-23700, Android slient privilege escalation allow to read/write contacts, SMS, calendar, call log and voicemail, make outgoing calls…
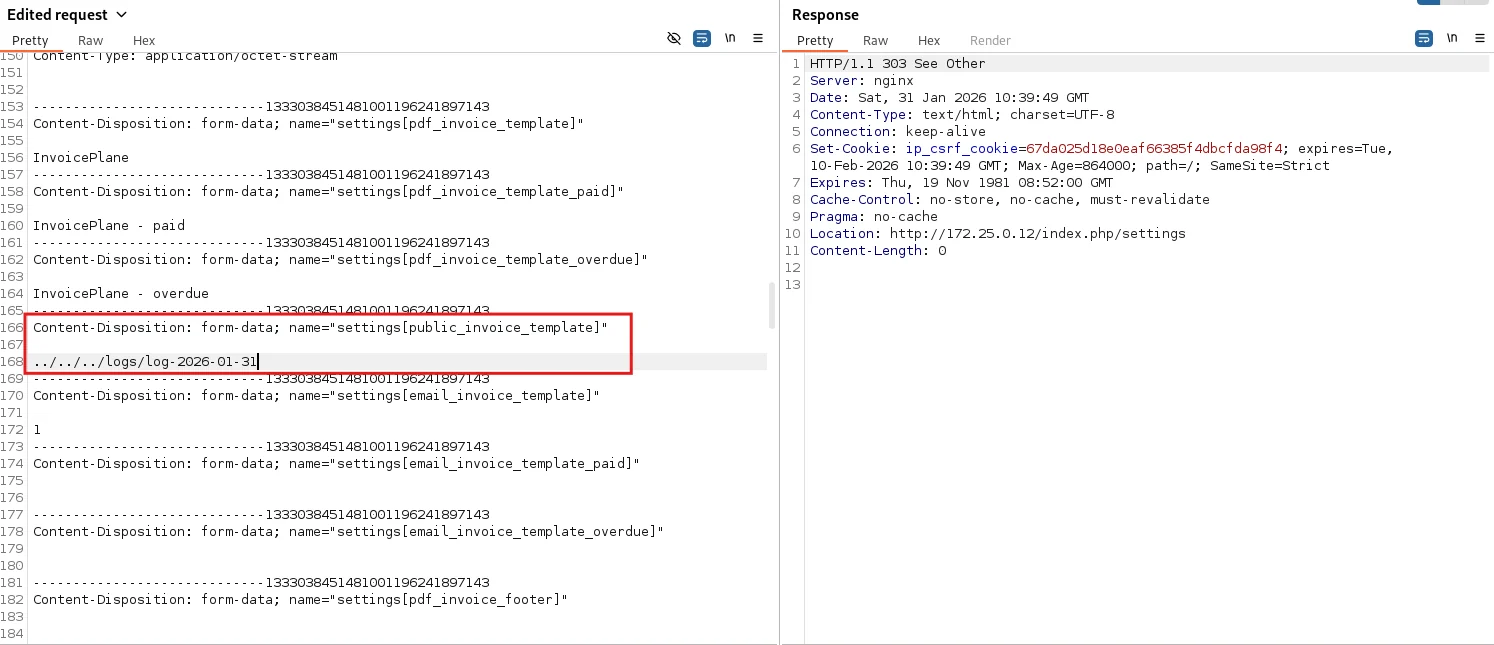 lagathos/cve-2026-25548
Detailed technical write-up and proof-of-concept for CVE-2026-25548, a critical RCE in InvoicePlane 1.7.0 via LFI and log poisoning, including attack…
 kairo-one/cve-2023-26469-jorani
Proof-of-concept exploit for CVE-2023-26469 targeting Jorani 1.0.0. Combines path traversal and log injection to achieve remote code execution with…
 mkultra6969/anysniff
AnySniff is a tool for monitoring TCP connections of processes like AnyDesk on Windows. It uses the CVE-2024-52940 vulnerability to track open…
 mdanzaruddin/cve-2021-33558.
Exploit code for CVE-2021-33558 targeting Boa/0.94.13 misconfigurations that expose sensitive information via backup, preview, log, and config files.
 giangdurian/cve-2021-3129
Python exploit script for Laravel Ignition CVE-2021-3129 RCE, using log poisoning and phar deserialization to execute commands on vulnerable web apps.
 jgoyd/ams-failopen
Zero-day in AppleMediaServices: Bag fetch failure disables Mescal/Absinthe signing. Requests to Apple services proceed unsigned, exposing downgrade,…
 miapatsune/cve-2026-43499
Kernel exploit for Redmi Pad Pro (dizi) / POCO Pad 5G with browser-based upload and execution interface, admin panel for log management, and…
 p33d/cve-2024-43363
Python exploit script to test Cacti instances for CVE-2024-43363 RCE via log poisoning. Checks version, injects PHP payload into device names, and…