

CVE-2026-54390
 shinthink/cve-2026-54390
CVE-2026-54390 — JTL Shop Smarty SSTI RCE | Pre-Auth Template Injection via fetch('string:' . ) | 5.2.0-5.7.1
exploitationpenetration-testingreconnaissance+2
shinthink/cve-2026-54390CVE-2026-54390 — JTL Shop Smarty SSTI RCE | Pre-Auth Template Injection via fetch('string:' . ) | 5.2.0-5.7.1
 cyberleelawat/cve-2025-20393
Cisco is aware of a potential vulnerability. Cisco is currently investigating and will update these details as appropriate as more…
 abc1230940/soc336-windows-ole-zero-click-rce-exploitation-detected-cve-2025-21298
SOC336 - Windows OLE Zero-Click RCE Exploitation Detected (CVE-2025-21298) Walkthrough
 randomrobbiebf/cve-2024-0368
Hustle Plugin <= 7.8.3 contains hardcoded HubSpot API credentials in inc/providers/hubspot/hustle-hubspot-api.php
 randomrobbiebf/cve-2025-8422
Propovoice <= 1.7.6.7 - Unauthenticated Arbitrary File Read
 redpack-kr/blackash-cve-2025-20393
CVE-2025-20393
 ickogz/cve-2019-13027
Details for disclosing CVE-2019-13027
 randomrobbiebf/cve-2023-41652
RSVPMarker <= 10.6.6 - Unauthenticated SQL Injection
 artemcyberlab/project-ntlm-hash-capture-and-phishing-email-exploitation-for-cve-2024-21413
Demonstrates capturing NTLM hashes via Responder and executing phishing emails exploiting CVE-2024-21413 to compromise systems.
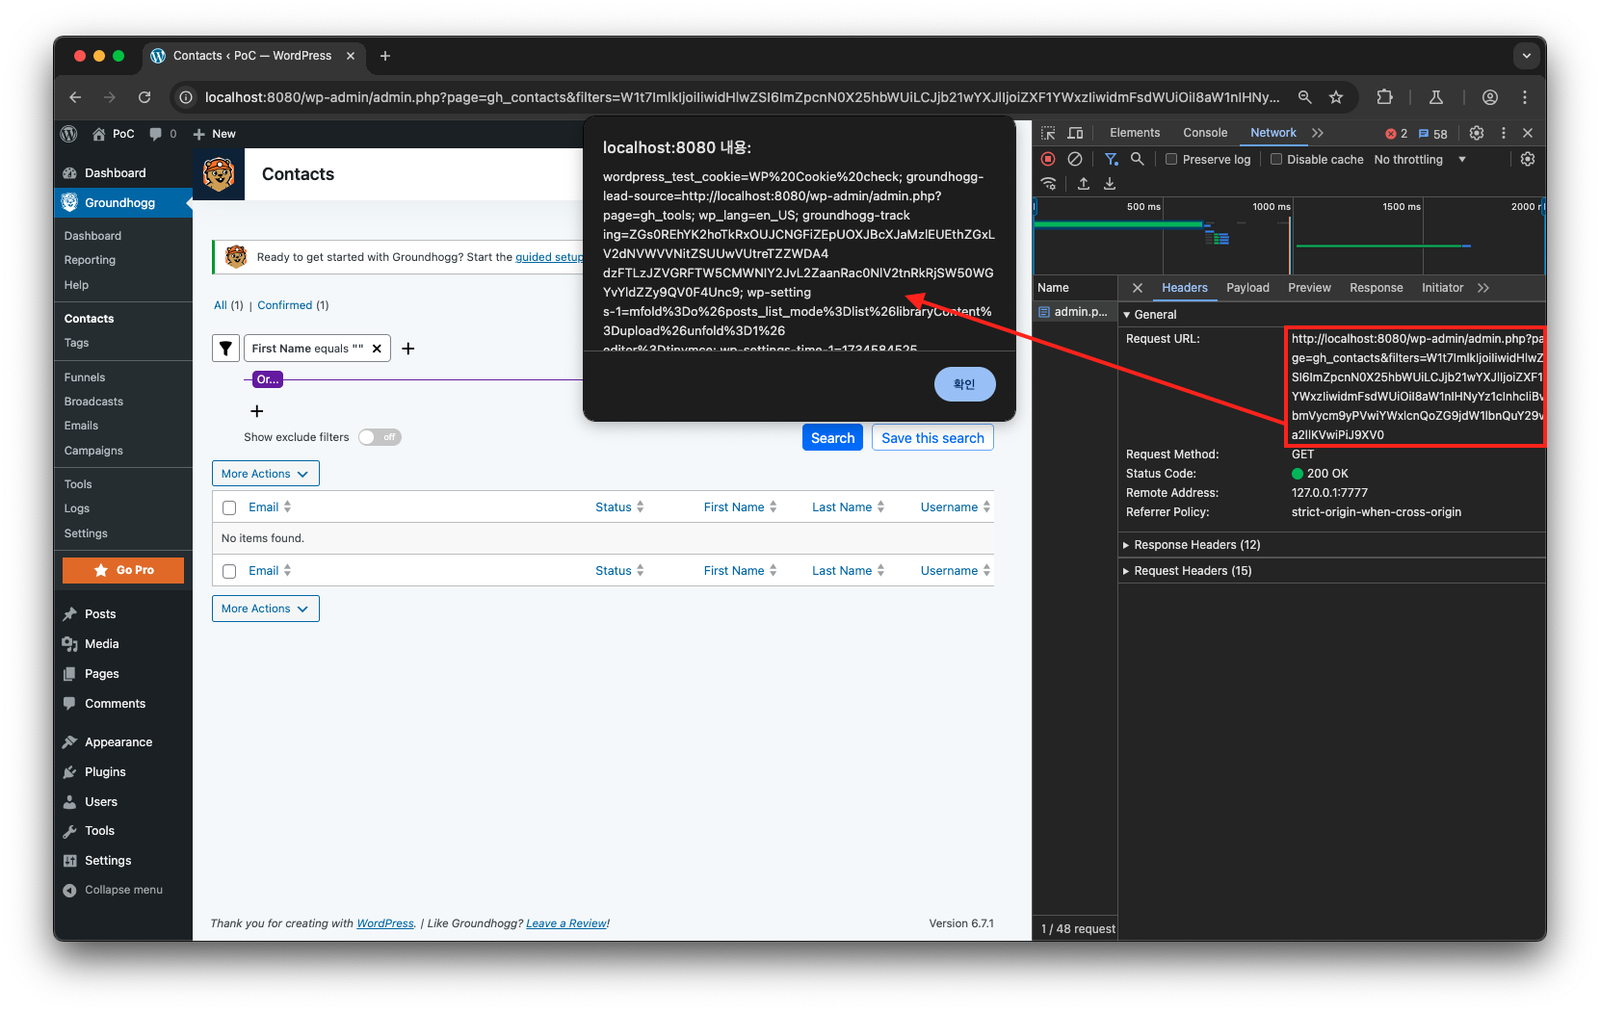 dottak/cve-2024-56289
Proof-of-concept exploit for a reflected XSS vulnerability in the Groundhogg WordPress plugin, demonstrating unauthenticated script injection via…
 dsahen/cve-2023-22515-exp
cve-2023-22515的python利用脚本
 bevennyamande/cve-2024-10557
A CSRF POC for Updating the Profile of a Hospital leading to Account Takeover
 symbolexe/cve-2023-23397
CVE-2023-23397: Remote Code Execution Vulnerability in Microsoft Outlook
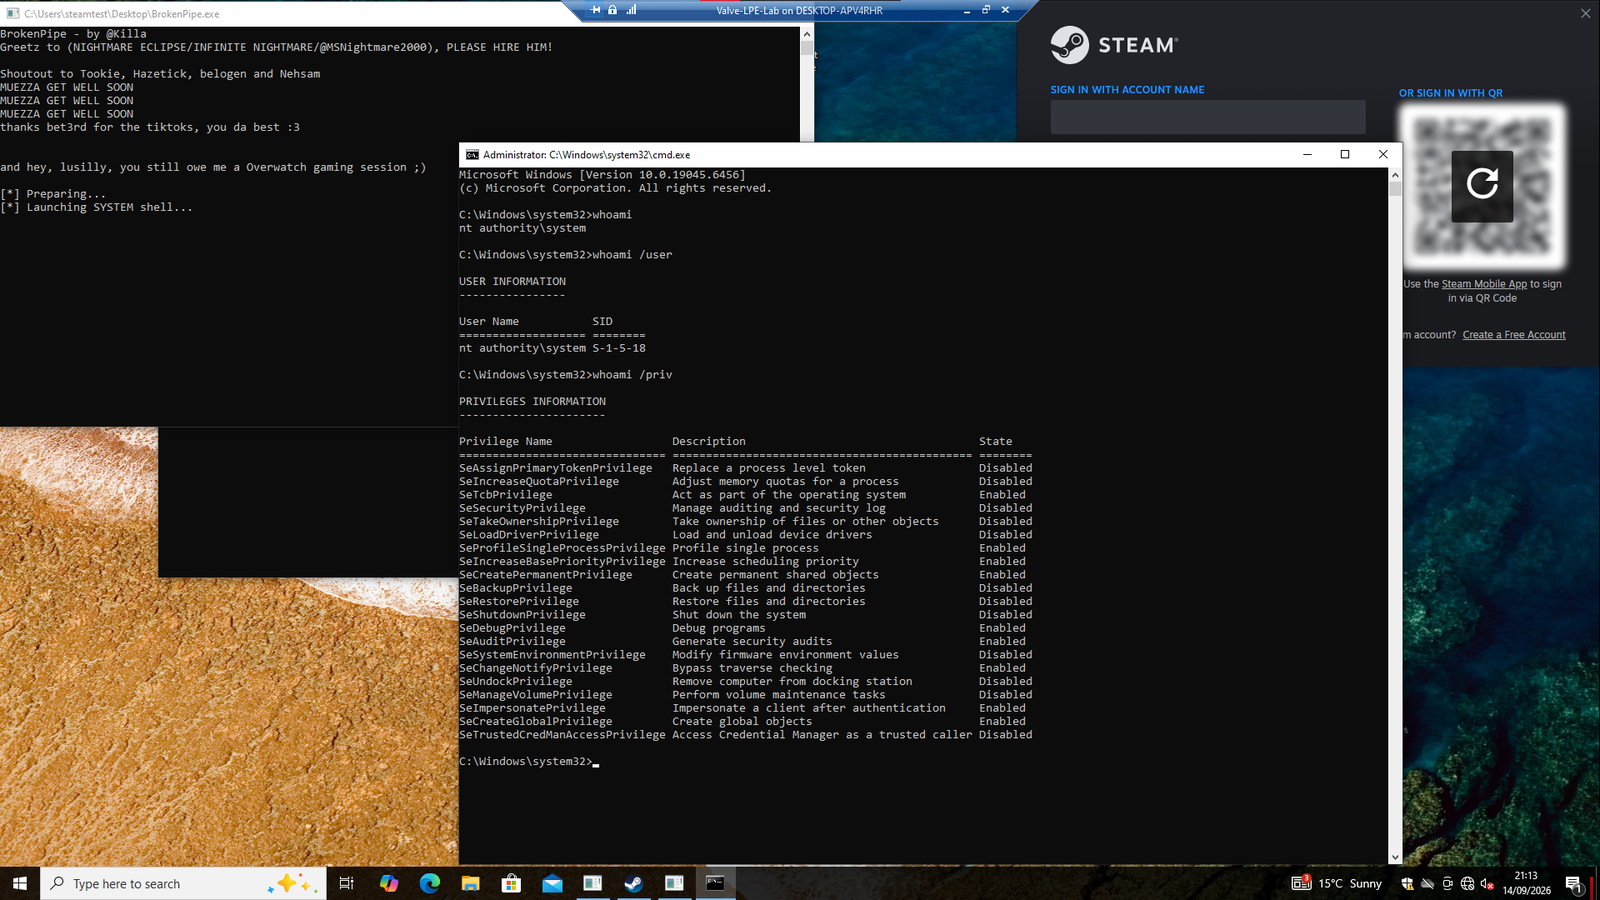 killaboi/brokenpipe
Steam Client Service Local Privilege Escalation Vulnerability
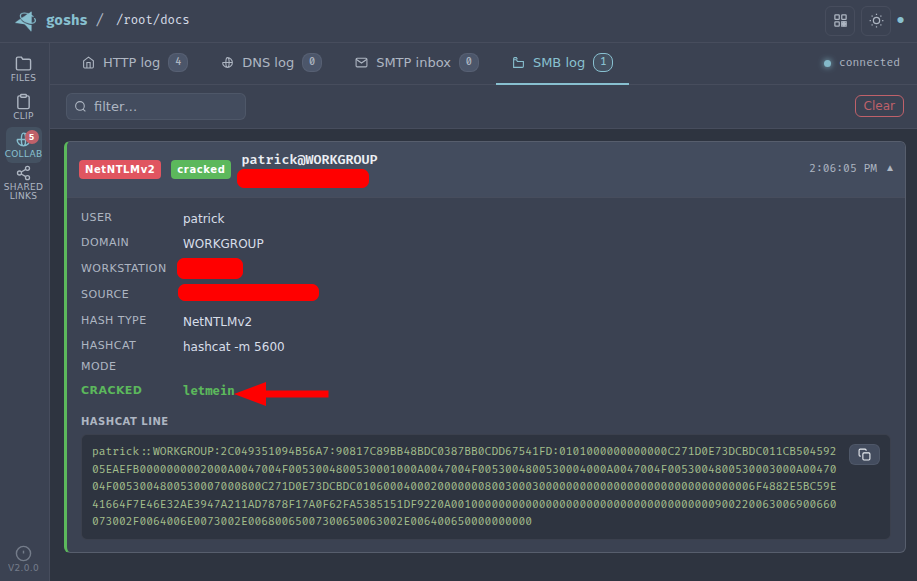 a-poc/redteam-tools
Tools and Techniques for Red Team / Penetration Testing
 ghostpack/rubeus
Trying to tame the three-headed dog.
 dirkjanm/krbrelayx
Kerberos relaying and unconstrained delegation abuse toolkit
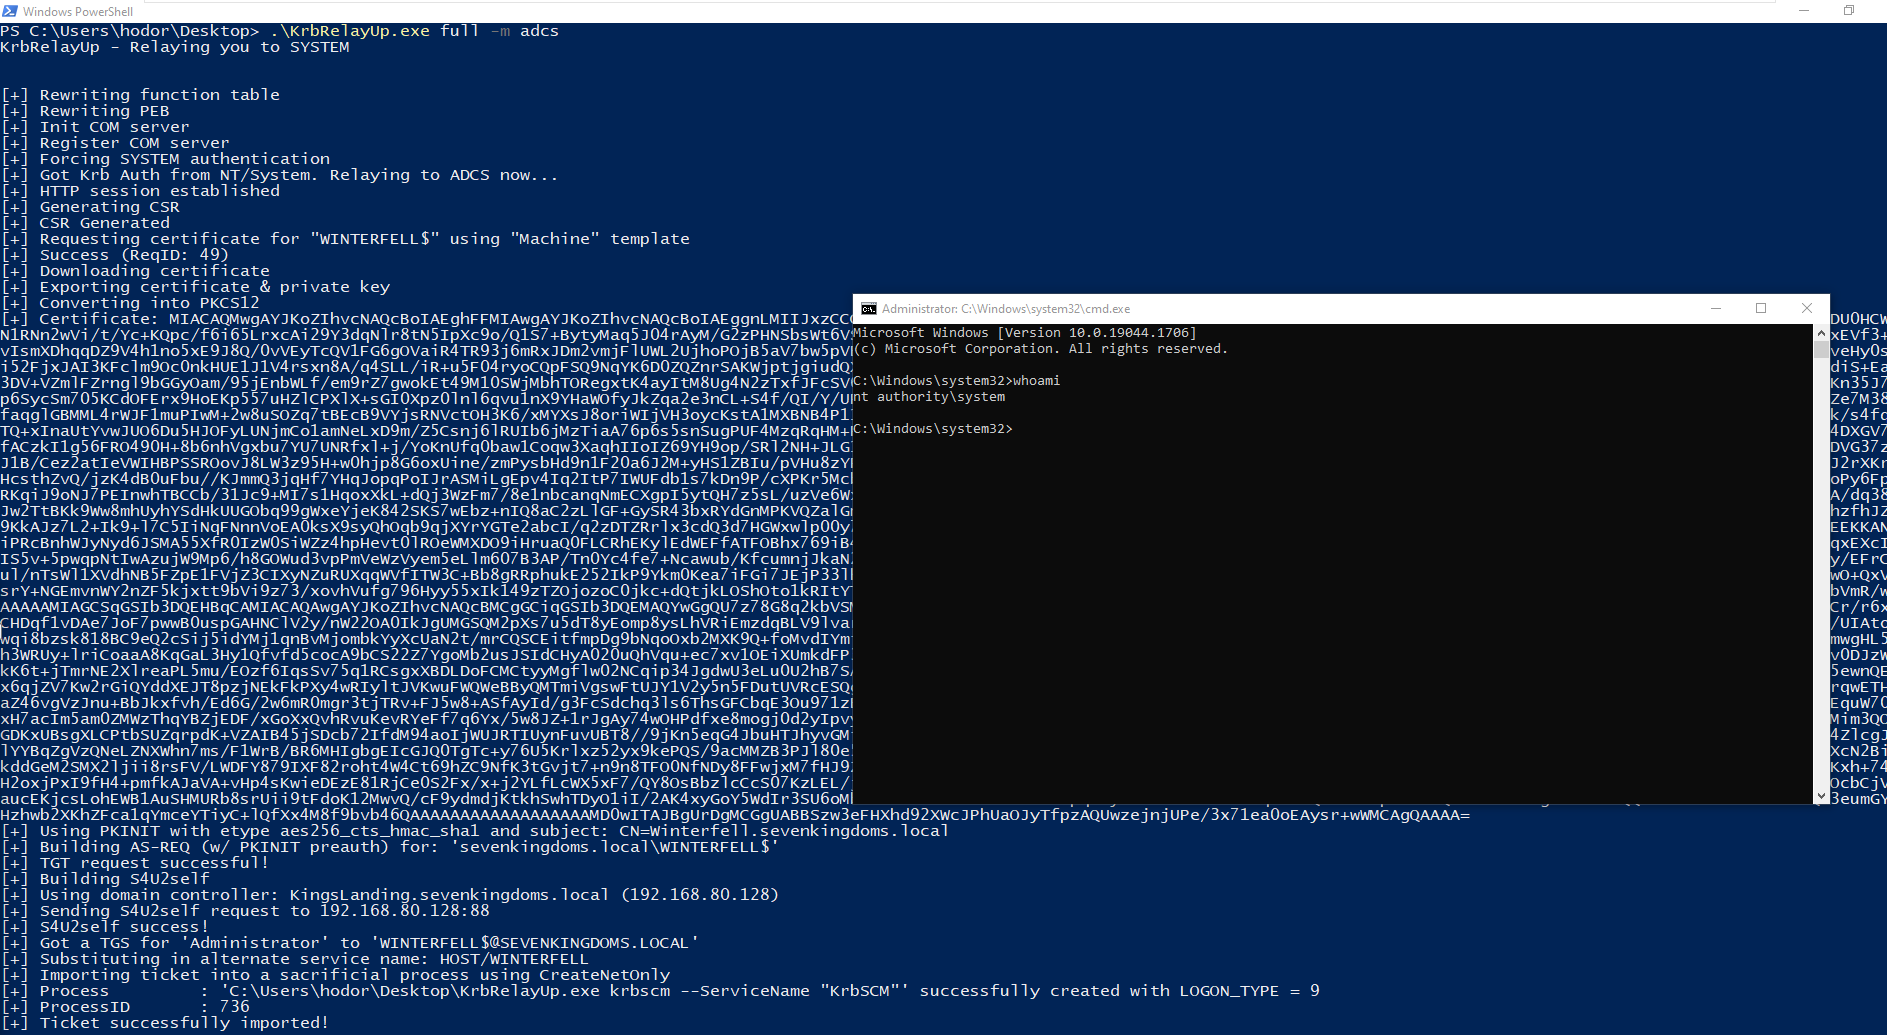 dec0ne/krbrelayup
KrbRelayUp - a universal no-fix local privilege escalation in windows domain environments where LDAP signing is not enforced (the default settings).