
preboot
 gmh5225/preboot
Experimental research code for analyzing d_olex firmware and performing preboot-stage attacks against firmware boot code.
binary-exploitationembedded-systems-securityexploitation+2
1
gmh5225/prebootExperimental research code for analyzing d_olex firmware and performing preboot-stage attacks against firmware boot code.
 vulncheck-oss/initial-access-community
Go-based exploits for unauthenticated network vulnerabilities in routers, VPNs, appliances, and IoT, bundled with PCAPs, Suricata/Snort/YARA/Sigma…
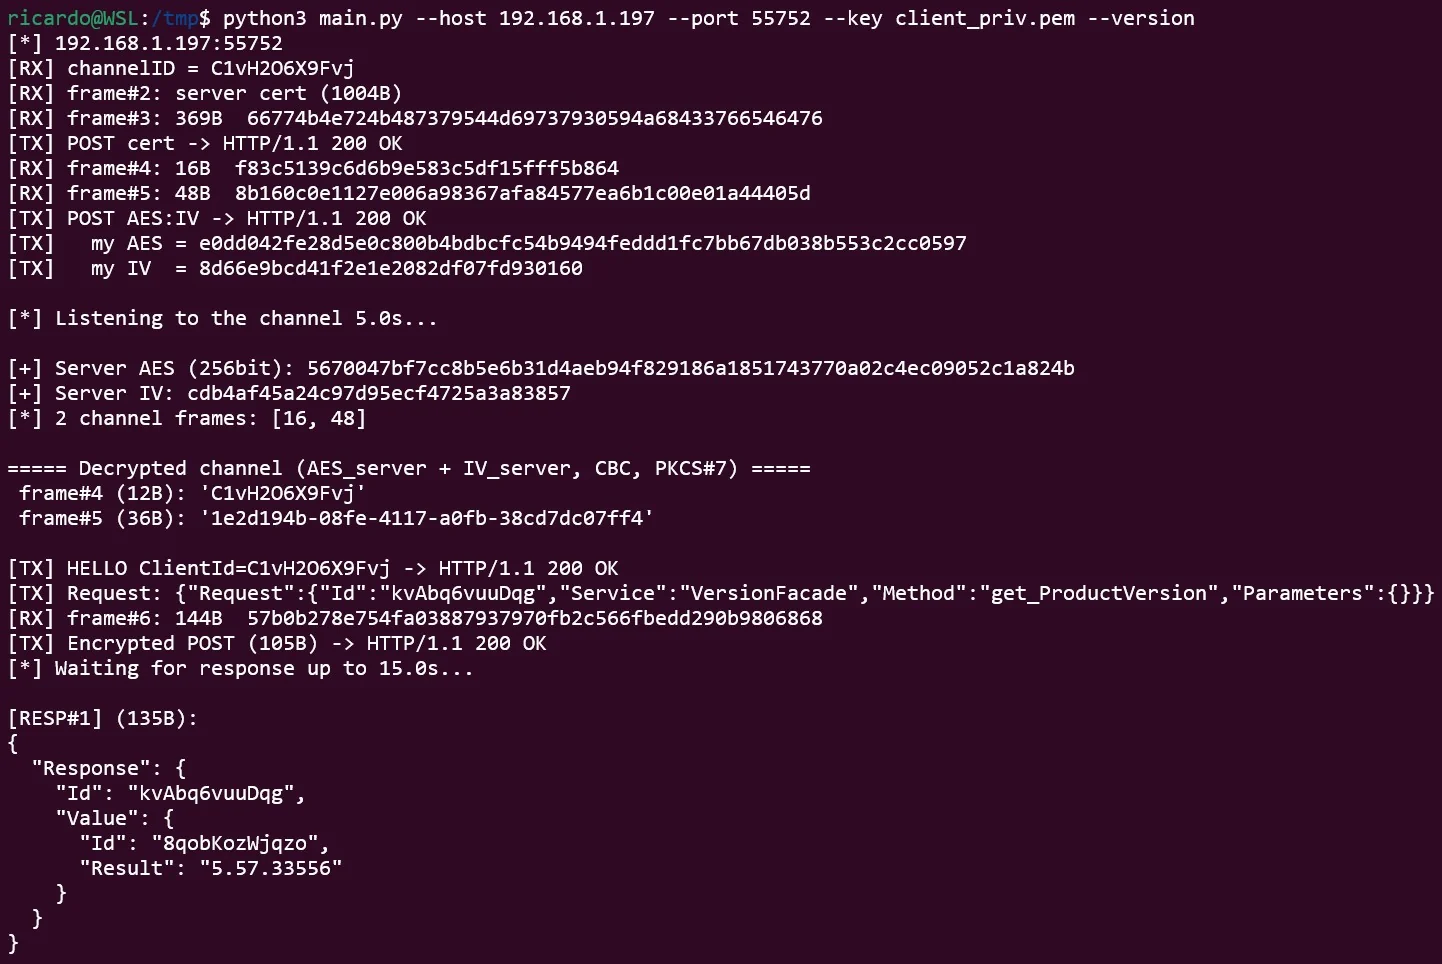 ricardojoserf/axis-rce
Unauth RCE on Axis Camera Station (ACS) chaining CVE‑2025‑30026 (Authentication bypass) + CVE‑2025‑30023 (Insecure deserialization)
 pulkin/esp8266-injection-example
Example project to demonstrate packet injection / sniffer capabilities of ESP8266 IC.
 lukr54/edk2-security
EDK2 BrotliCustomDecompressLib security findings — coordinated disclosure
 openwrt-xiaomi/xmir-patcher
Patches Xiaomi router firmware images to enable SSH access and install custom firmware, with automated Windows and Linux/macOS launcher scripts.
 commit-regrets/samsung_tizen_tv_root
Research toolkit that roots a Samsung Tizen 9 TV via a Chromium WasmGC RCE and V4L2 physmap arbitrary physical memory access, with persistent on-boot…
 blasty/wake-and-break
PSP exploit for AMD navi31 (RX 7900) GPUs that disables firmware signature checks so the card loads unsigned SMU, SDMA, MEC, IMU and RLC firmware;…
 pepsipu/ns2jb
Console jailbreak demo that executes native functions inside the Switch 2 filesystem process via SmileBASIC, verifies results, and restores original…
 cplusplus17/deco-filepush-disclosure
Disclosure and PoC for a root file read/write flaw in the TP-Link Deco XE75 Pro V3 debug channel (tmpsvr opcodes 0xC456/0xF0), with CVSS analysis and…
 newbe3e/pwn2own-automotive-2026-alpine-ilx-f511-0-click-rce-exploit-writeup
Writeup of a 0-click remote code execution exploit chain developed for the Alpine iLX-F511 automotive head unit at Pwn2Own Automotive 2026.
 abraxas/sonic-gnmi-noauth
Documents and reproduces a fail-open authentication flaw in SONiC gNMI where an empty UserAuth map allows unauthenticated gNMI Set and gNOI writes,…
 bignerd95/chimay-red
Working POC of Mikrotik exploit from Vault 7 CIA Leaks
 vulncheck-oss/cisco-ios-xe-implant-scanner
Go-based scanner that detects implanted Cisco IOS XE systems by sending crafted HTTP requests to identify compromised devices and vulnerable versions.
 j-baines/even-you-brutus
Dictionary Brute Force of the Mikrotik RouterOS 6.x Web Interface
 turretsec/u3000py
Python client for the Thinkware U3000 dashcam's local WiFi control protocol, reverse-engineered from the official Android app. PoC tooling behind…
 heapframe/seetong-ts81xxd3x-rce
CVE-2026-100886 | Unauthenticated Remote Code Execution toolkit.
 murrez/cve-2026-100740
Python PoC for CVE-2026-100740, an L2TP Host Name AVP out-of-bounds write in D-Link DIR-895L A1_102b07 tunnel_set_params. Fingerprints the device and…