

area51
 thoropass-public/area51
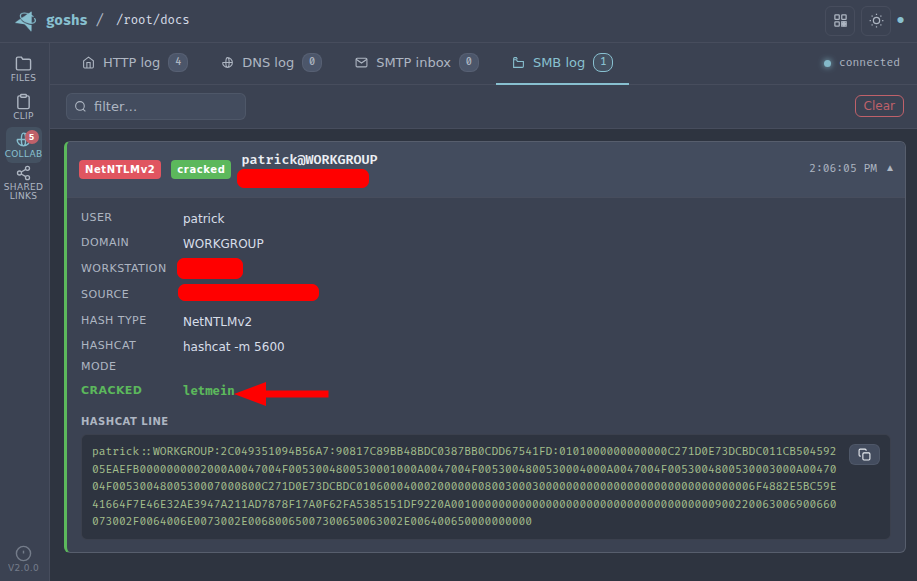
The exploit server for out-of-band findings. Point a target at a domain you own. Every HTTP request and every email it sends back lands in a…
api-security-testingcloud-securityemail-security+4
5
thoropass-public/area51The exploit server for out-of-band findings. Point a target at a domain you own. Every HTTP request and every email it sends back lands in a…
 portbuster1337/atlas
Cross-platform network execution toolkit (SMB/Kerberos/WMI/LDAP/DCSync) built on TrustedSec's Titanis - NetExec-style workflow in C#
 arno0x/ntlmrelaytoews
ntlm relay attack to Exchange Web Services
 xaitax/cve-2024-21413-microsoft-outlook-remote-code-execution-vulnerability
Microsoft-Outlook-Remote-Code-Execution-Vulnerability
 tghook/cve-2024-4295-poc
CVE-2024-4295 Email Subscribers by Icegram Express <= 5.7.20 - Unauthenticated SQL Injection via hash
 chsxthwik/cve-2024-2876
Proof-of-concept exploit for CVE-2024-2876, an unauthenticated SQL injection vulnerability in the Email Subscribers plugin for WordPress, enabling…
 randomrobbiebf/cve-2023-32117
Integrate Google Drive <= 1.1.99 - Missing Authorization via REST API Endpoints
 srvaccount/cve-2021-26855-poc
PoC exploit code for CVE-2021-26855
 sensepost/ruler
A tool to abuse Exchange services
 a-poc/redteam-tools
Tools and Techniques for Red Team / Penetration Testing
 romain-deperne/cve-2026-33715
Unauthenticated SSRF and open email relay in Chamilo LMS — CVE-2026-33715 / CVSS 7.2
 artemcyberlab/project-ntlm-hash-capture-and-phishing-email-exploitation-for-cve-2024-21413
Demonstrates capturing NTLM hashes via Responder and executing phishing emails exploiting CVE-2024-21413 to compromise systems.
 quickbreach/exchangerelayx
An NTLM relay tool to the EWS endpoint for on-premise exchange servers. Provides an OWA for hackers.
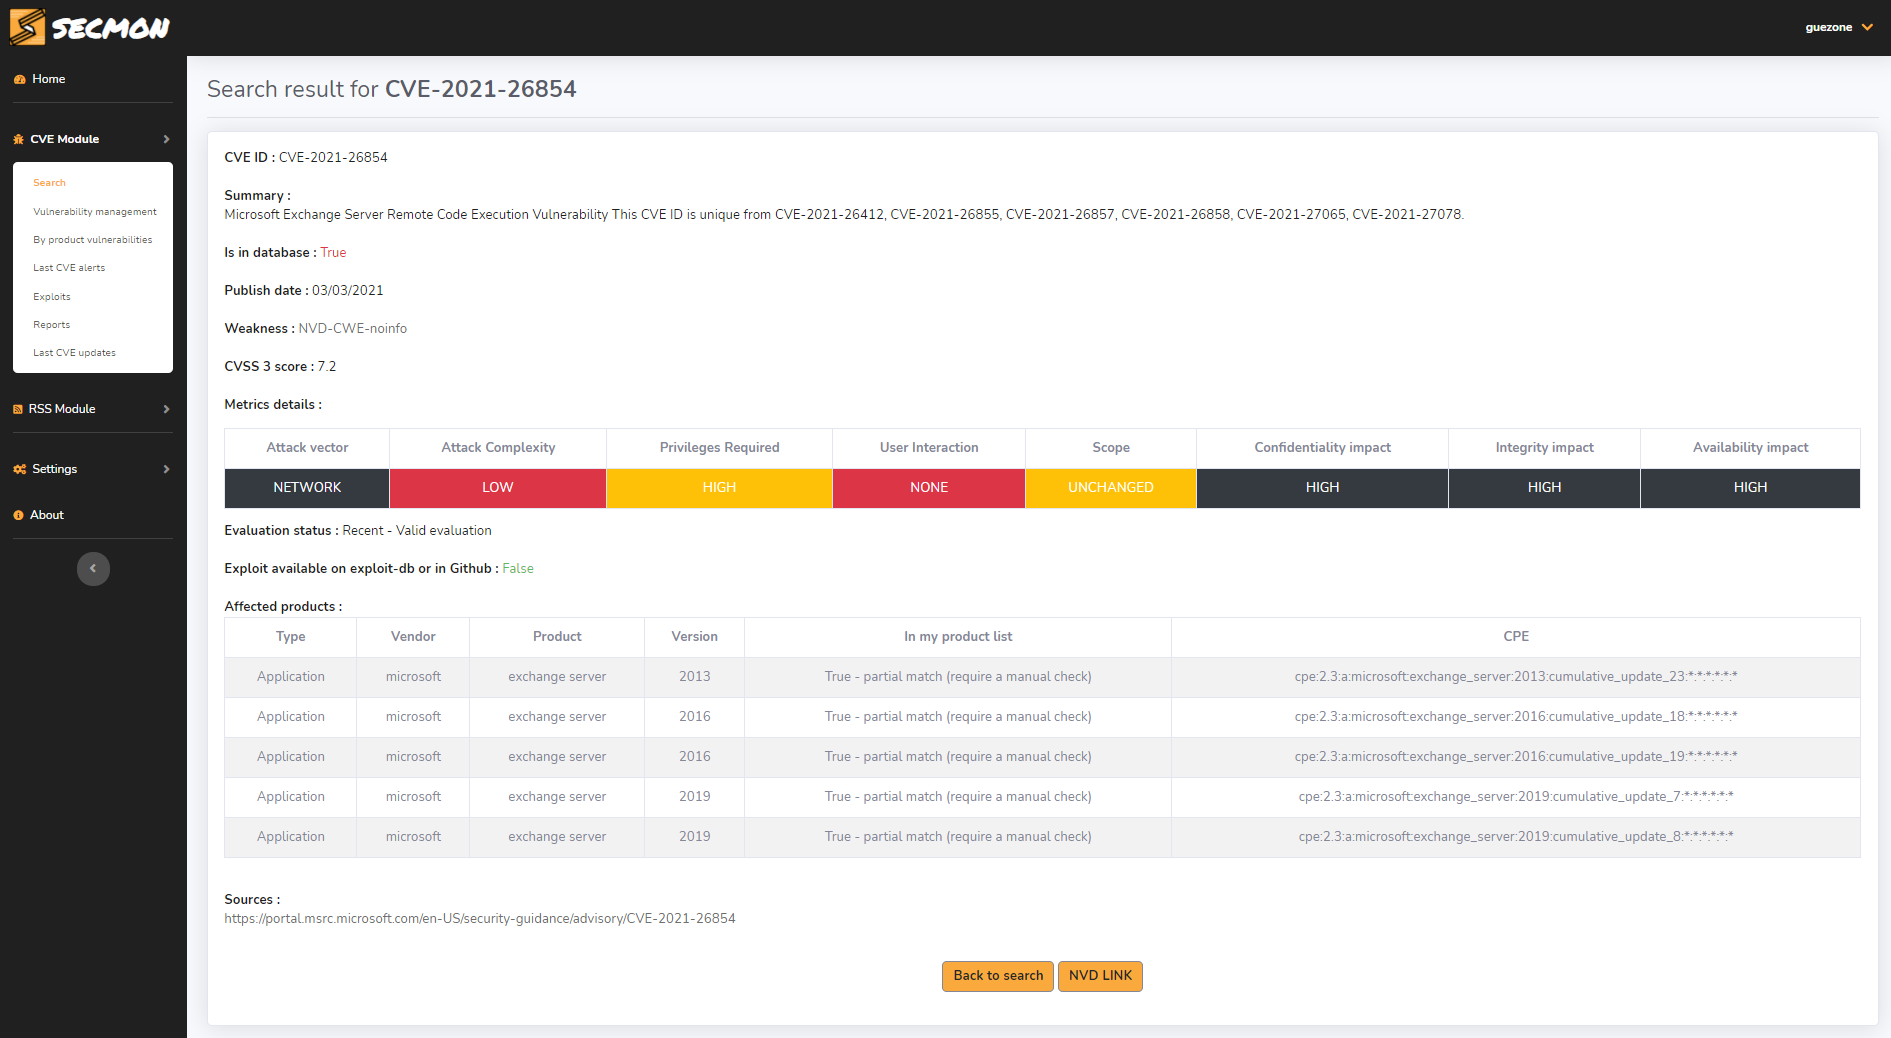 alb-uss/secmon
SECMON is a web-based tool for the automation of infosec watching and vulnerability management with a web interface.
 h4k6/cve-2023-2982-poc
WordPress社交登录和注册(Discord,Google,Twitter,LinkedIn)<=7.6.4-绕过身份验证
 sairson/yasso
强大的内网渗透辅助工具集-让Yasso像风一样 支持rdp,ssh,redis,postgres,mongodb,mssql,mysql,winrm等服务爆破,快速的端口扫描,强大的web指纹识别,各种内置服务的一键利用(包括ssh完全交互式登陆,mssql提权,redis一键利用,mysql数据库…
 bhanunamikaze/cve-2024-42009
This Proof of Concept (PoC) demonstrates an exploit for CVE-2024-42009, leveraging a cross-site scripting (XSS) vulnerability to extract emails from…