
offensive-docker
 aaaguirrep/offensive-docker
Offensive Docker is an image with the more used offensive tools to create an environment easily and quickly to launch assessment to the targets.
container-securityexploit-frameworkspassword-cracking+5
770
aaaguirrep/offensive-dockerOffensive Docker is an image with the more used offensive tools to create an environment easily and quickly to launch assessment to the targets.
 samogod/tornado
Anonymously Reverse Shell over Tor Network using Hidden services without Portforwarding.
 mwemuorg/mwemu
Pure Rust x86 hardware emulator and Windows process simulator for malware analysis, shellcode emulation, and payload unpacking. Supports 32/64-bit PE…
 chvancooten/nimpackt-v1
Nim-based assembly packer and shellcode loader for opsec & profit
 leochen-coremind/vmpacker
ARM64 ELF Virtual Machine Protection System
 0ca/boxpwnr
A modular framework for benchmarking LLMs and agentic strategies on security challenges across HackTheBox, TryHackMe, PortSwigger Labs, Cybench,…
 seanheelan/anamnesis-release
Evaluation framework for studying LLM agents that automatically generate working exploits from vulnerability reports, bypassing modern security…
 mazen160/shennina
Automating Host Exploitation with AI
 last-emo-boy/rikune
MCP server for reverse engineering Windows executables and binary formats. Combines static triage, Ghidra-assisted function recovery, plugin-driven…
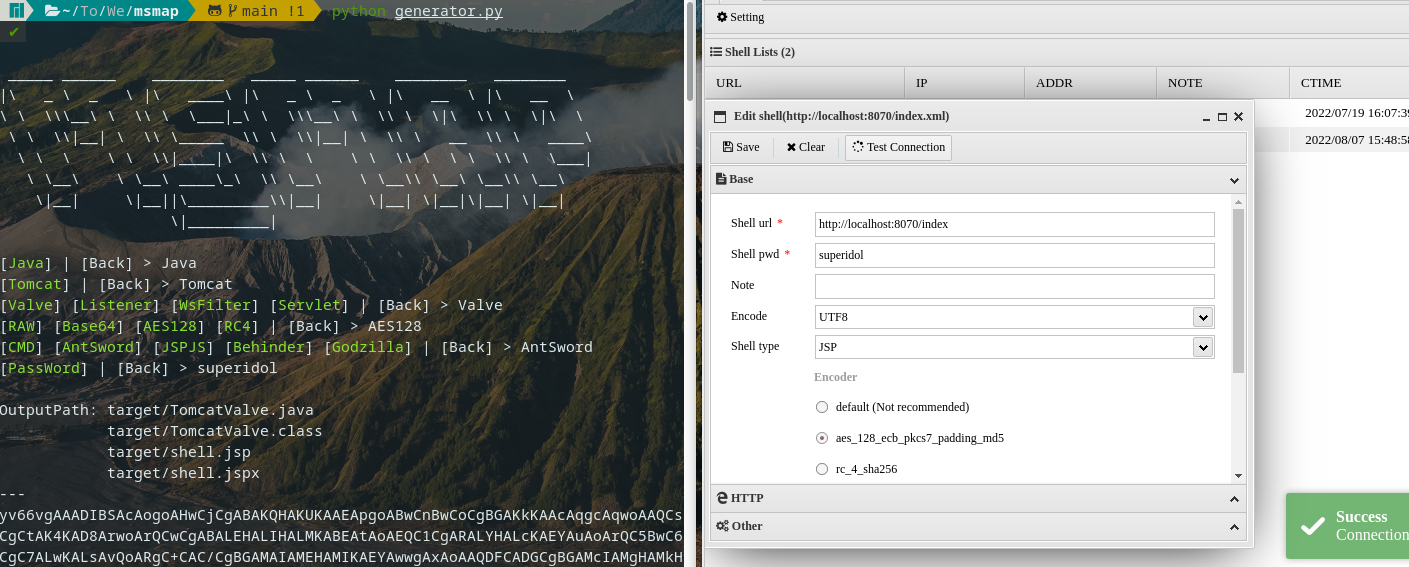 hosch3n/msmap
Modular memory webshell generator supporting Java containers (Tomcat, Spring, WebLogic) with multiple shell types, encoders, and automatic…
 abedalqaderswedan1/aswcrypter
An Bash&Python Script For Generating Payloads that Bypasses All Antivirus so far [FUD]
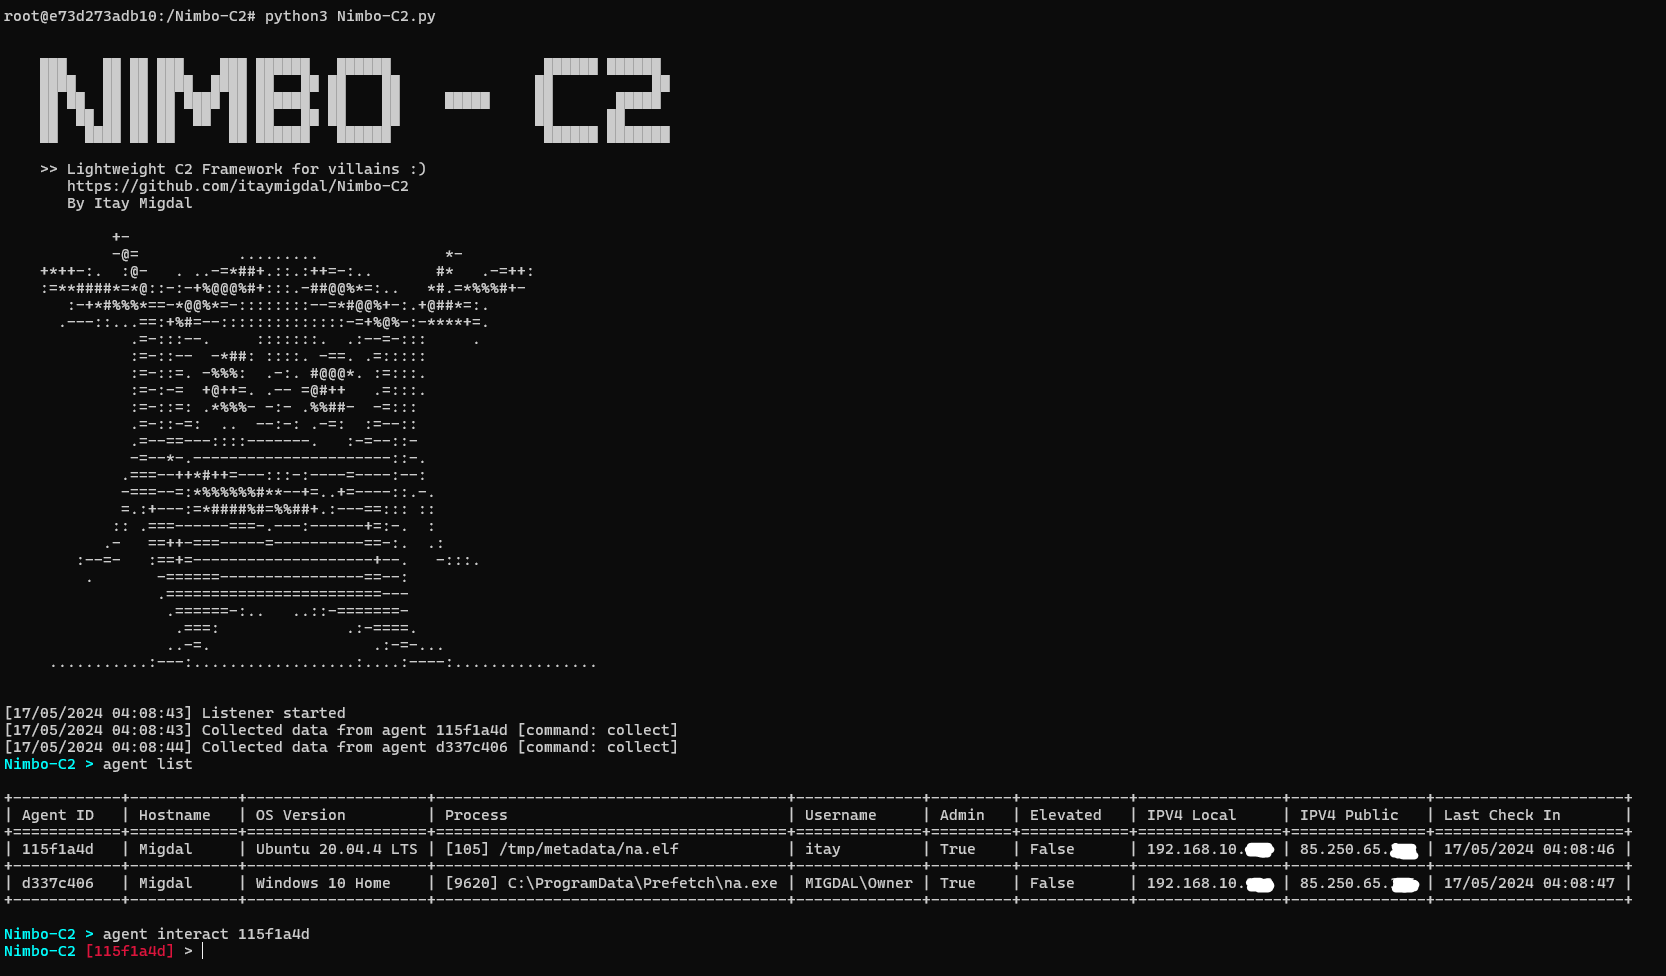 itaymigdal/nimbo-c2
Nimbo-C2 is yet another (simple and lightweight) C2 framework
 xtr4nge/fruityc2
FruityC2 is a post-exploitation (and open source) framework based on the deployment of agents on compromised machines. Agents are managed from a web…
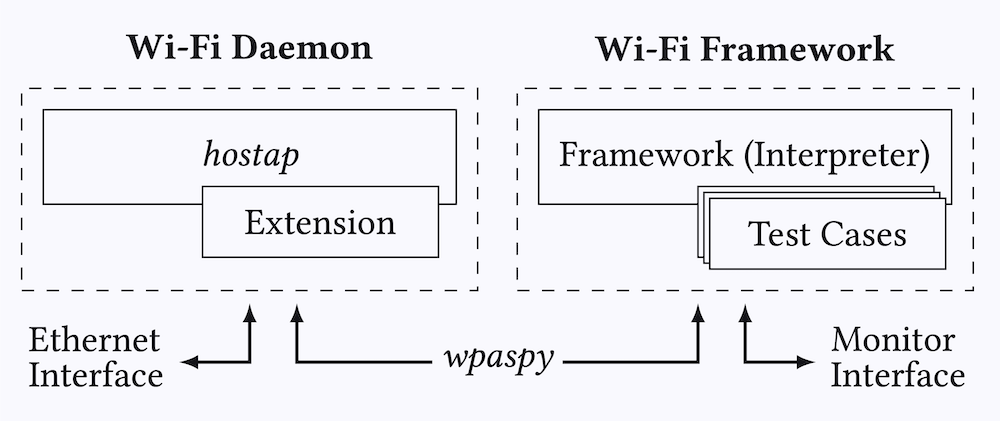 domienschepers/wifi-framework
Wi-Fi Framework for creating proof-of-concepts, automated experiments, test suites, fuzzers, and more.
 getrektboy724/betterxencrypt
A better version of Xencrypt.Xencrypt it self is a Powershell runtime crypter designed to evade AVs.
 nvisosecurity/pycobalthound
pyCobaltHound is an Aggressor script extension for Cobalt Strike which aims to provide a deep integration between Cobalt Strike and Bloodhound.
 d4em0n/exrop
Automated ROP chain generator for x86-64 binaries using symbolic execution. Supports register/memory writes, function calls, syscalls, badchar…