
bitcracker
 e-ago/bitcracker
BitCracker is the first open source password cracking tool for memory units encrypted with BitLocker
cryptographyencryption-decryption-toolspassword-cracking
e-ago/bitcrackerBitCracker is the first open source password cracking tool for memory units encrypted with BitLocker
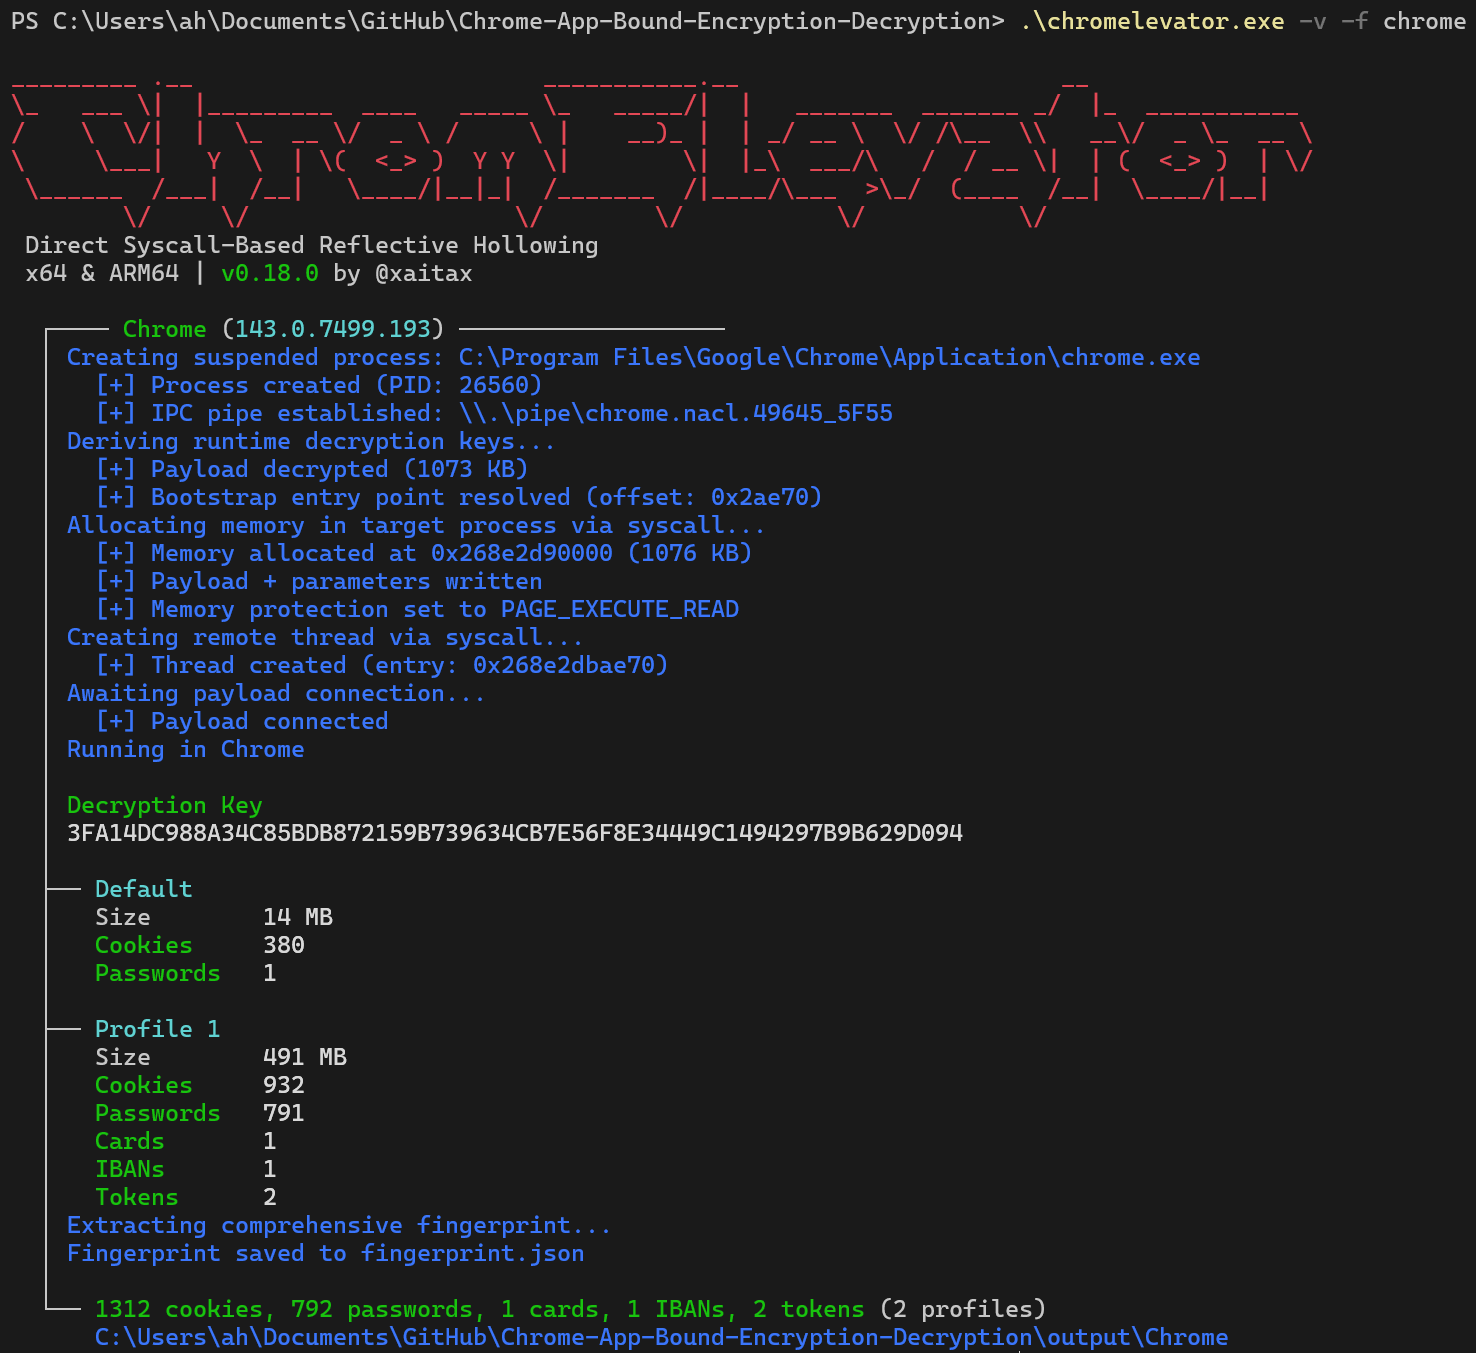 xaitax/chrome-app-bound-encryption-decryption
Bypass Chromium's App-Bound Encryption via Direct Syscall-based Reflective Process Hollowing. Extract cookies, passwords, payment methods & tokens…
 alessandroz/lazagne
Cross-platform credential recovery tool that extracts stored passwords from browsers, email clients, databases, system mechanisms, and network…
 nilsteampassnet/teampass
Collaborative Passwords Manager
 kurolabs/stegcloak
Hide secrets with invisible characters in plain text securely using passwords 🧙🏻♂️⭐
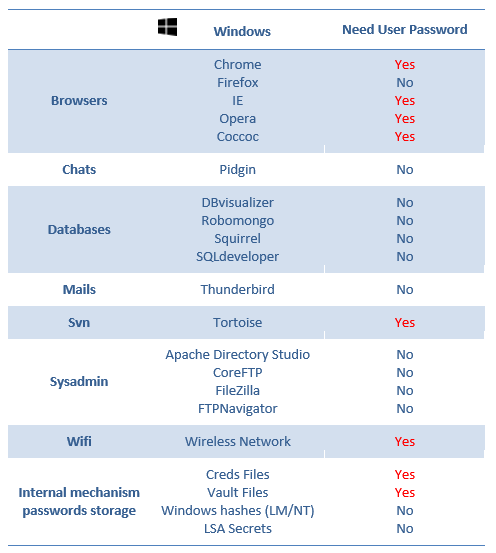 alessandroz/lazagneforensic
Windows passwords decryption from dump files
 rxwx/chlonium
Clone and import Chromium cookies and passwords across browsers with offline DPAPI state key decryption, supporting AES-256 GCM encrypted databases…
 s0md3v/locky
Locky generates "really" strong yet easy to remember passwords.
 nccgroup/untrue
Tool for checking passwords against TrueCrypt encrypted volumes and disks, and/or decrypting the data.
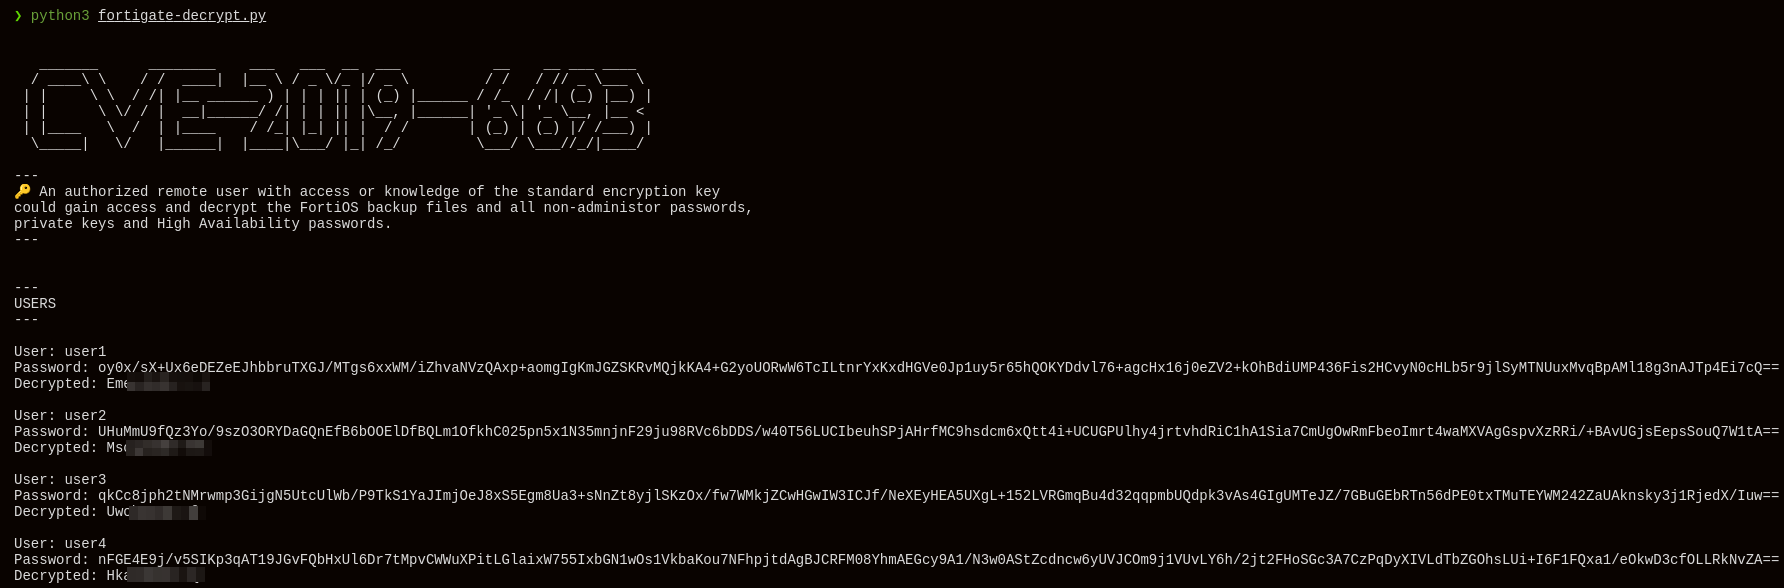 saladandonionrings/cve-2019-6693
An authorized remote user with access or knowledge of the standard encryption key can gain access and decrypt the FortiOS backup files and all…
 yukselberkay/pmanager
Store and retrieve your passwords from a secure offline database. Check if your passwords has leaked previously to prevent targeted password reuse…
 madrisan/cisco7crack
Crypt and decrypt the cisco enable 7 passwords
 gquere/cve-2019-6693
Decrypts FortiGate configuration secrets (CVE-2019-6693) for versions below 6.2.0, extracting encrypted passwords and keys from dumped configs using…
 usethisname1419/pdfcrack
PDF Crack is a GUI tool used for cracking pdf passwords. includes 3 cracking options
 sic4rio/grafana-decryptor-for-cve-2021-43798
Decrypts Grafana DataSource passwords by exploiting CVE-2021-43798 directory traversal to retrieve configuration files and derive encryption keys.
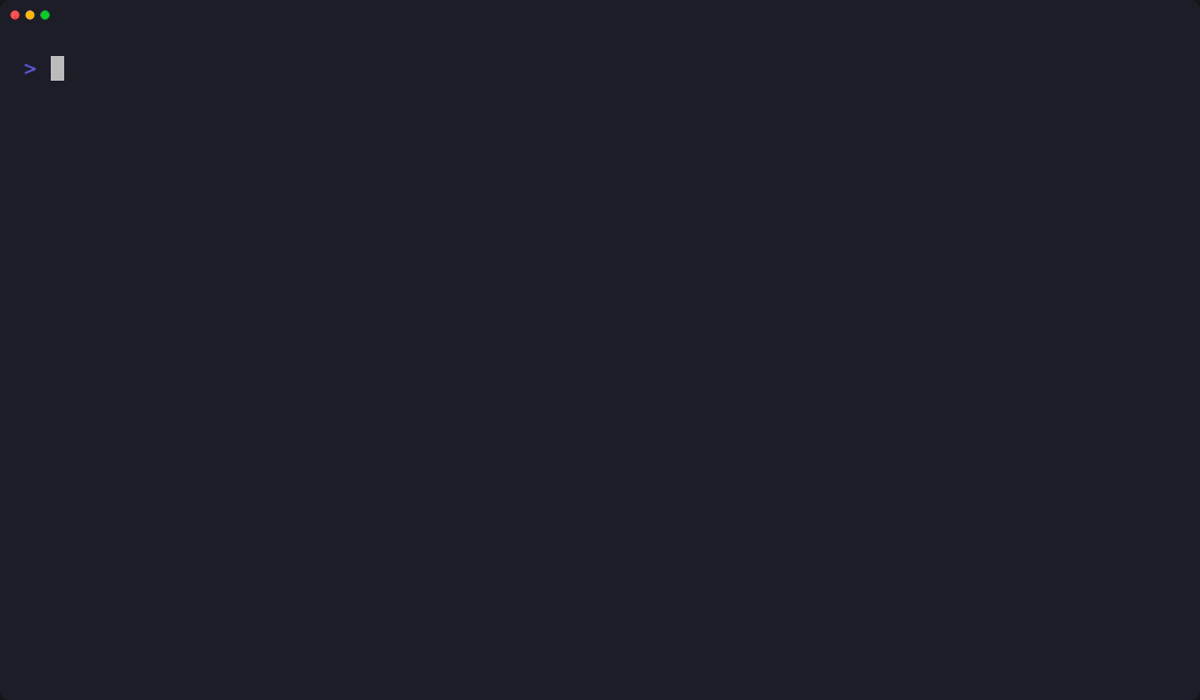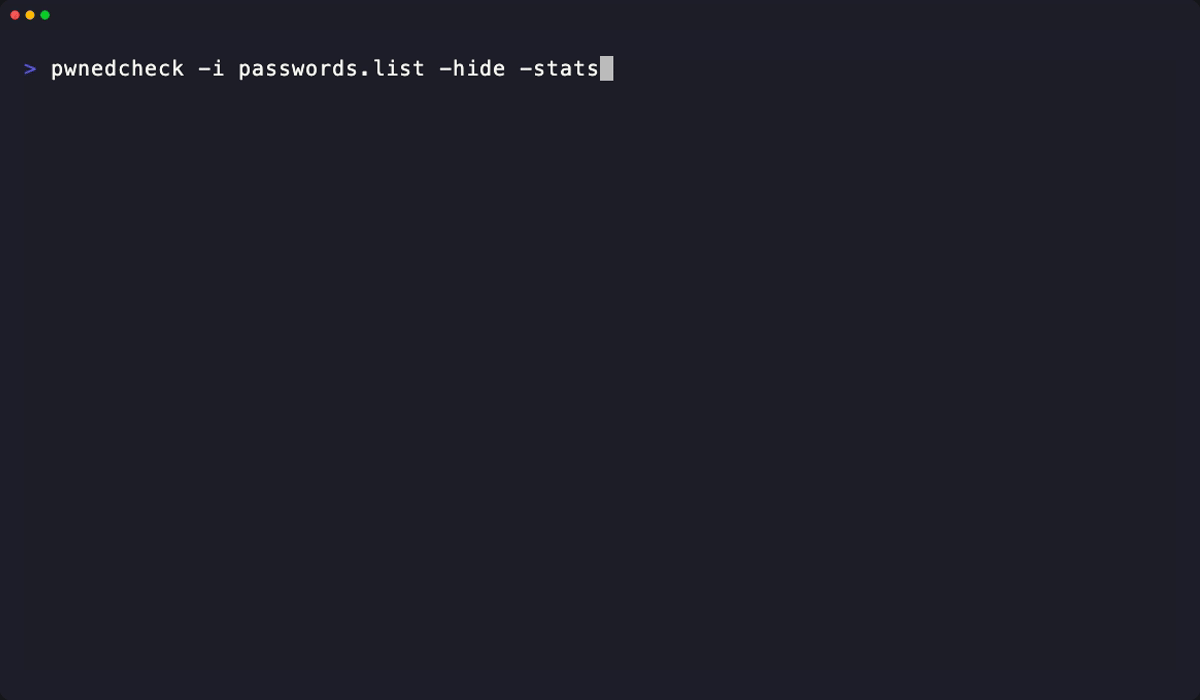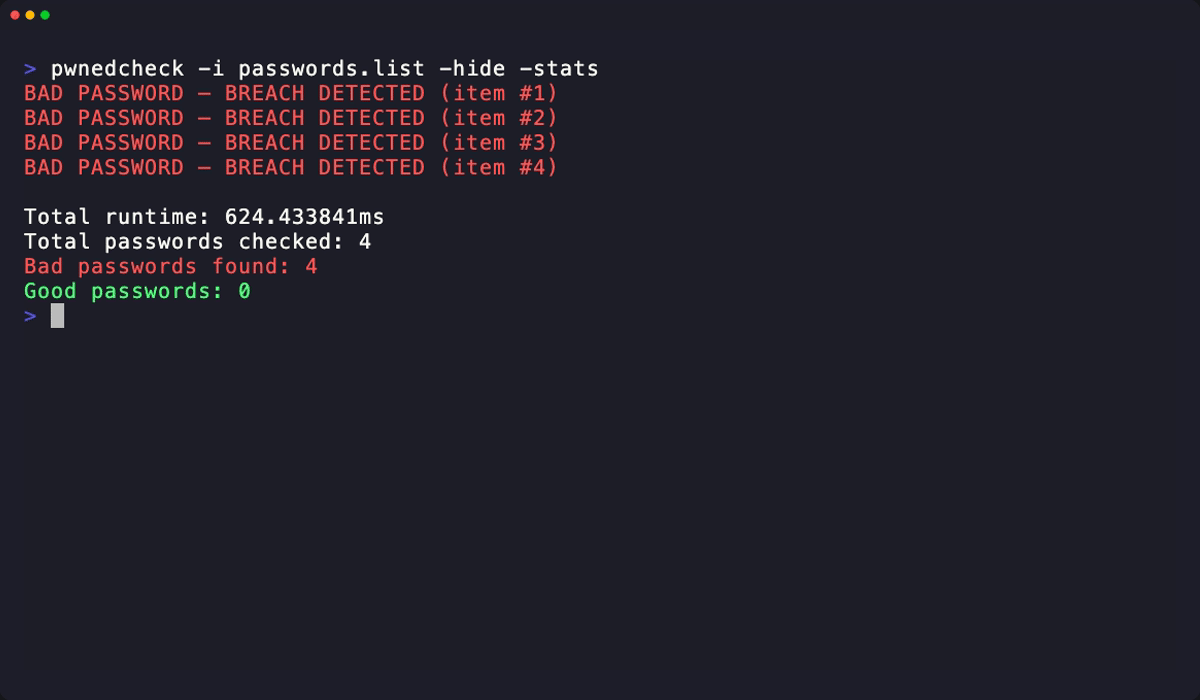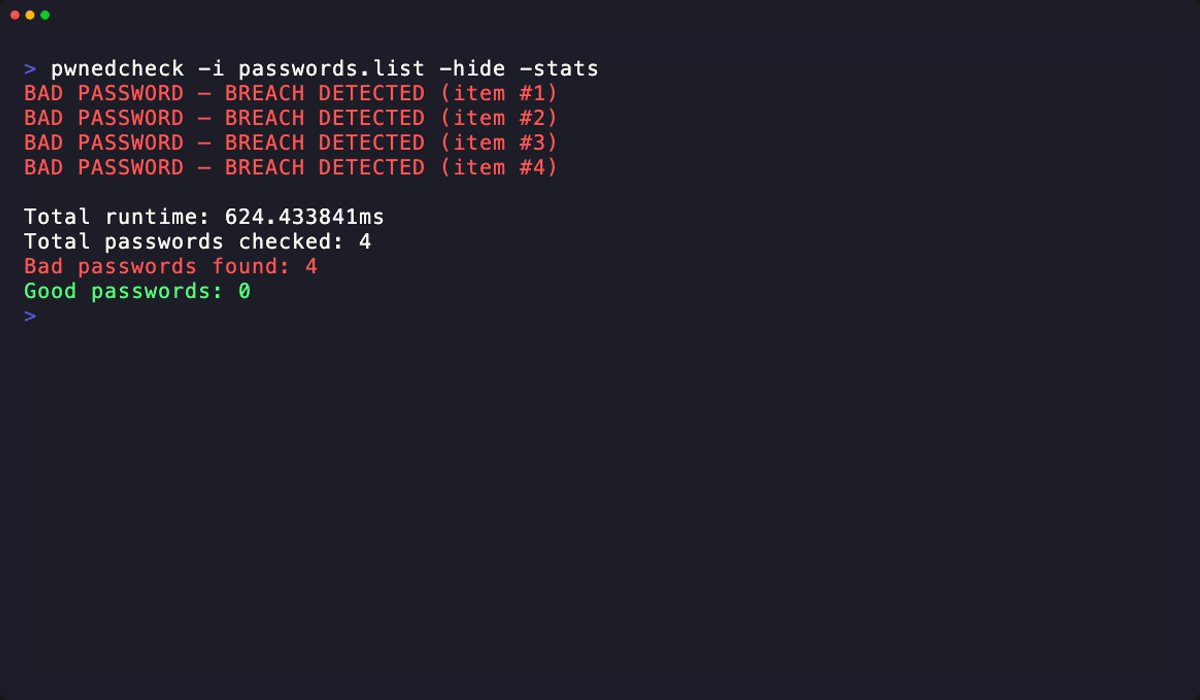 mohamedation/pwnedcheck
A command-line tool to check if passwords have been exposed in data breaches using the Have I Been Pwned (HIBP) API.
 0xsazzad/grafana-cve-2021-43798
Python implementation of a tool for decrypting and encrypting sensitive data in Grafana, specifically addressing the vulnerabilities associated with…
 m1kb0k/cve-2022-25012-dvr4-weak-password-encryption
Decrypts weak encrypted passwords from Argus Surveillance DVR systems via CVE-2022-25012, reconstructing plaintext credentials from DVRParams.ini…