
 kurolabs/stegcloak
Hide secrets with invisible characters in plain text securely using passwords 🧙🏻♂️⭐



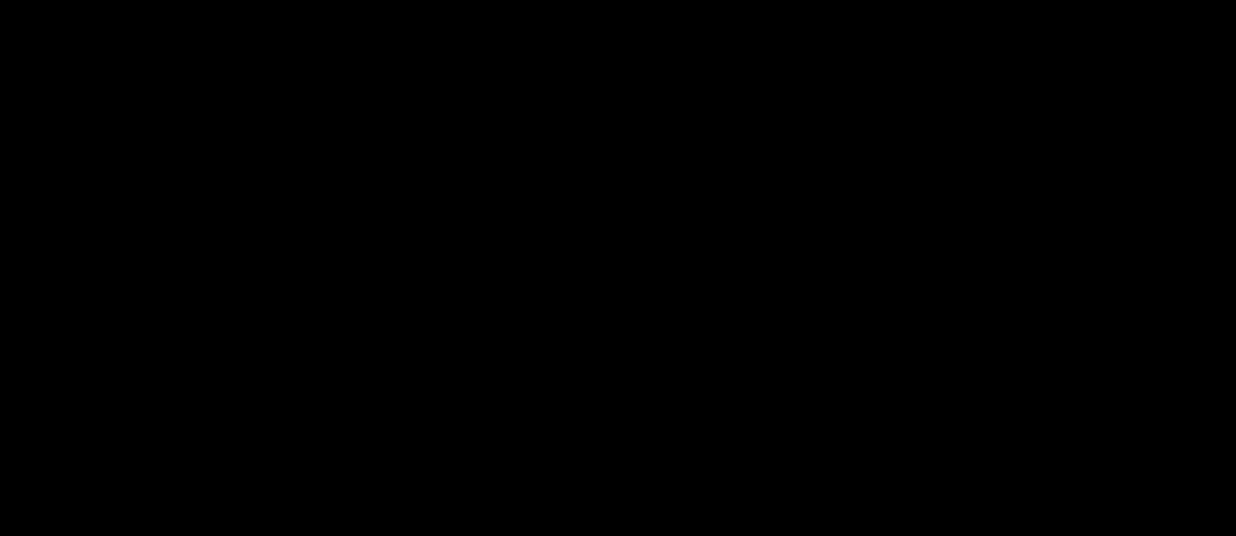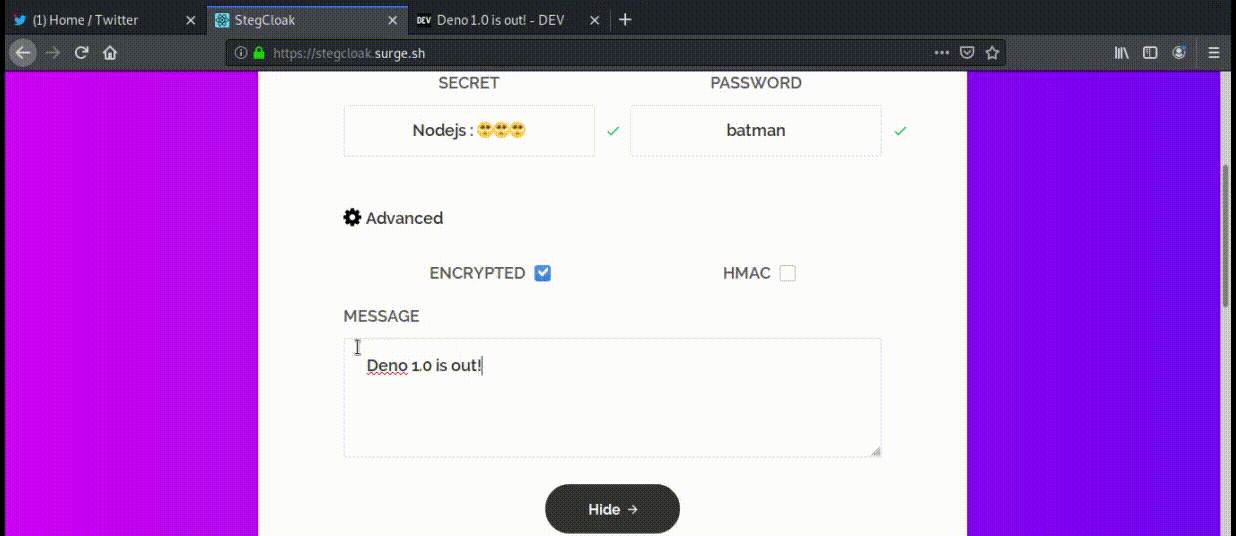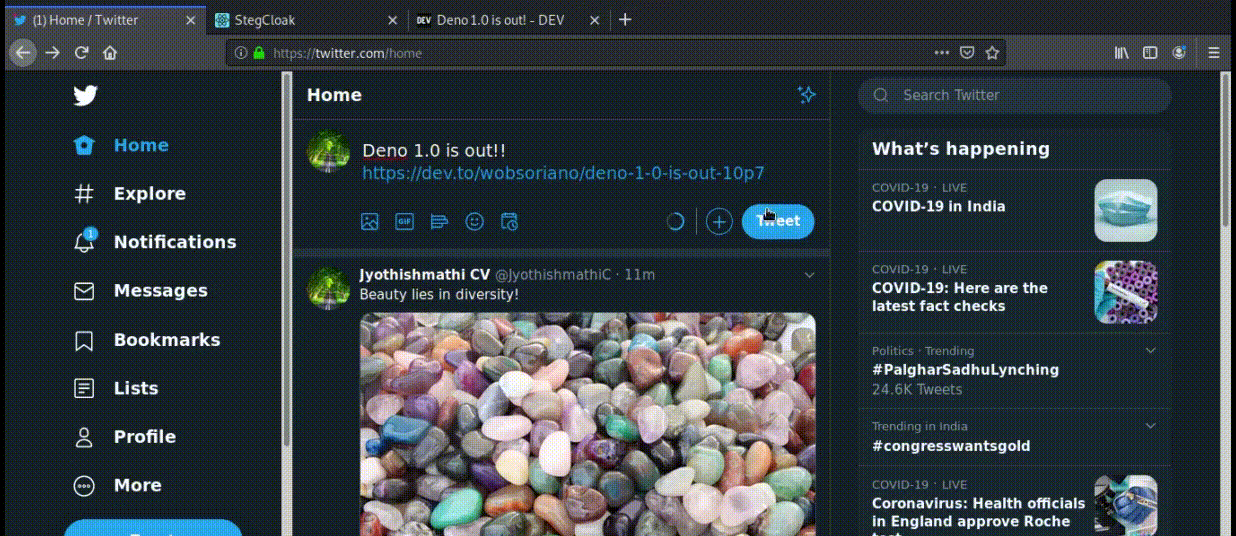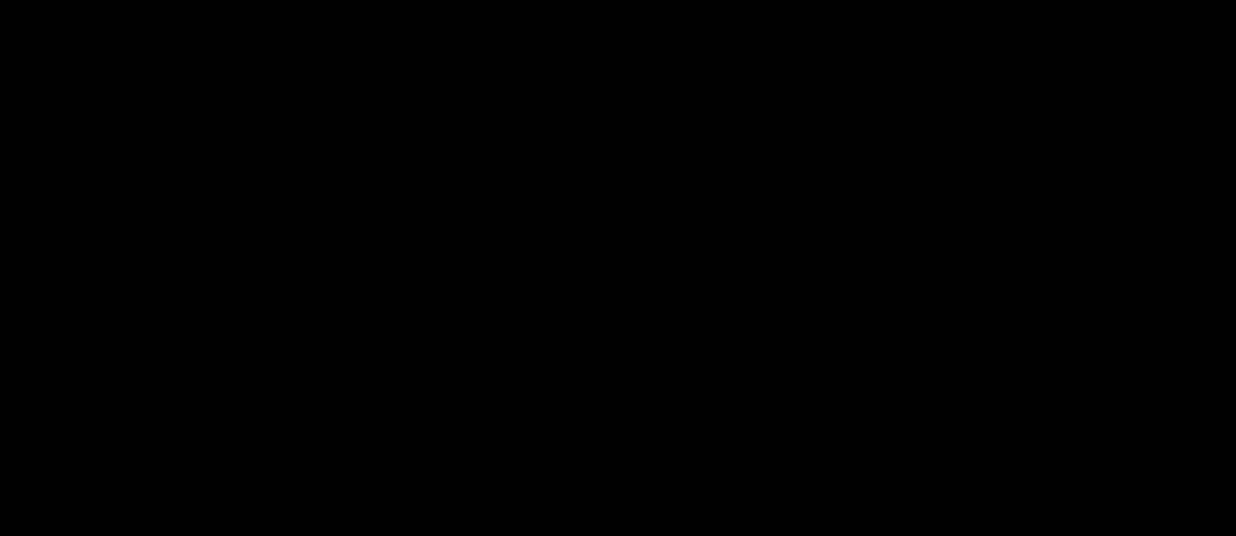
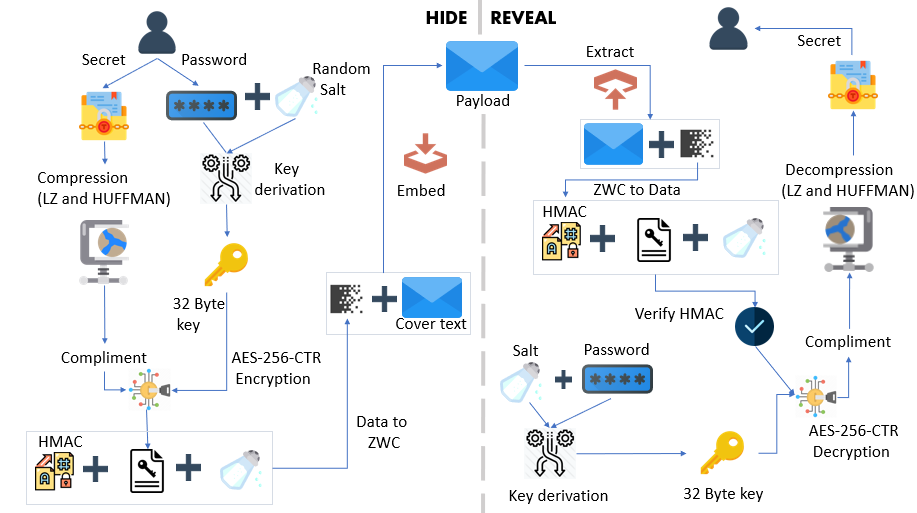
StegCloak is a pure JavaScript steganography module designed in functional programming style, to hide secrets inside text by compressing and encrypting the secret before cloaking it with special unicode invisible characters. It can be used to safely watermark strings, invisible scripts on webpages, texts on social media or for any other covert communication. Completely invisible! See how it works in-depth in this Medium article or watch our demo to know what it does.

Using npm,
$ npm install -g stegcloak
Using npm (to use it locally in your program),
$ npm install stegcloak
$ stegcloak hide
Options:
  hide [options] [secret] [cover]

  -fc, --fcover <file>      Extract cover text from file
  -fs, --fsecret <file>     Extract secret text from file
  -n, --nocrypt             If you don't need encryption (default: false)
  -i, --integrity           If additional security of preventing tampering is needed (default: false)
  -o, --output <output>     Stream the results to an output file
  -c, --config <file>       Config file
  -h, --help                display help for command
$ stegcloak reveal
Options:
  reveal [message]

  -f, --file <file>       Extract message from file
  -cp, --clip             Copy message directly from clipboard
  -o, --output <output>   Stream the secret to an output file
  -c, --config <file>     Config file
  -h, --help              display help for command
STEGCLOAK_PASSWORD environment variable, if set, will be used by default as password.
Configuration file support to configure StegCloak CLI and to avoid prompts. Read the config docs here.
const StegCloak = require('stegcloak');

const stegcloak = new StegCloak(true, false);  // Initializes with encryption true and hmac false for hiding

// These arguments are used only during hide

// Can be changed later by switching boolean flags for stegcloak.encrypt and stegcloak.integrity
HMAC is an additional fingerprint security step taken towards tampering of texts and to verify if the message received was actually sent by the intended sender. If the data is sent through WhatsApp, Messenger or any social media platform, this is already taken care of! However, if you are using StegCloak in your program to safely transmit and retrieve, this option can be enabled and StegCloak takes care of it.
stegcloak.hide(secret, password, cover) -> stringconst magic = stegcloak.hide("Voldemort is back", "mischief managed", "The WiFi's not working here!");
// Uses stegcloak.encrypt and stegcloak.integrity booleans for obfuscation
console.log(magic); // The WiFi's not working here!
stegcloak.reveal(data, password) -> stringconst secret = stegcloak.reveal(magic, "mischief managed");
// Automatically detects if encryption or integrity checks were done during hide and acts accordingly
console.log(secret); // Voldemort is back
This amazing blog by Francesco Soncina shows how you could use the StegCloak API to watermark any text on your website.
StegCloak doesn't solve the Alice-Bob-Warden problem, it's powerful only when people are not looking for it and it helps you achieve that really well, given its invisible properties around the web! It could be safely used for watermarking in forums, invisible tweets, social media etc. Please don't use it when you know there's someone who is actively sniffing your data - looking at the unicode characters through a data analysis tool. In that case, even though the secret encoded cannot be deciphered, the fact lies that the Warden (middle-man) knows some secret communication took place, because he would have noticed an unusual amount of special invisible characters.
Pull requests are welcome. For major changes, please open an issue first to discuss what you would like to change.
MIT - Copyright (c) 2020 Jyothishmathi CV, Kandavel A, Mohanasundar M
The StegCloak logo was designed by Smashicons.






