
vulnrepo
 kac89/vulnrepo
VULNRΞPO - Free vulnerability report generator and repository, end-to-end encrypted! Templates of issues, CWE,CVE,MITRE ATT&CK,PCI DSS, import…
ai-securitycurated-resourceseducation+4
584
kac89/vulnrepoVULNRΞPO - Free vulnerability report generator and repository, end-to-end encrypted! Templates of issues, CWE,CVE,MITRE ATT&CK,PCI DSS, import…
 katrielmoses/voidaccess
Self-hosted dark web OSINT platform. Automated threat intelligence from query to graph in 13 steps. Free alternative to Recorded Future, DarkOwl, and…
 torlando-tech/columba
Native Android messaging app using Bluetooth LE, TCP, or RNode (LoRa) over LXMF and Reticulum
 merces/bashacks
A set of functions to increase productivity while hacking with Bash
 foxio-llc/ja4
JA4+ is a suite of network fingerprinting standards
 captmag/maldev
Creation of multiple Malware tools consisting of evasion, enumeration and exploitation
 cbuijs/sdproxy
DNS Proxy that is simple and fast with not so simple features. Focused on routed DNS forwarding, filtering and parental control.
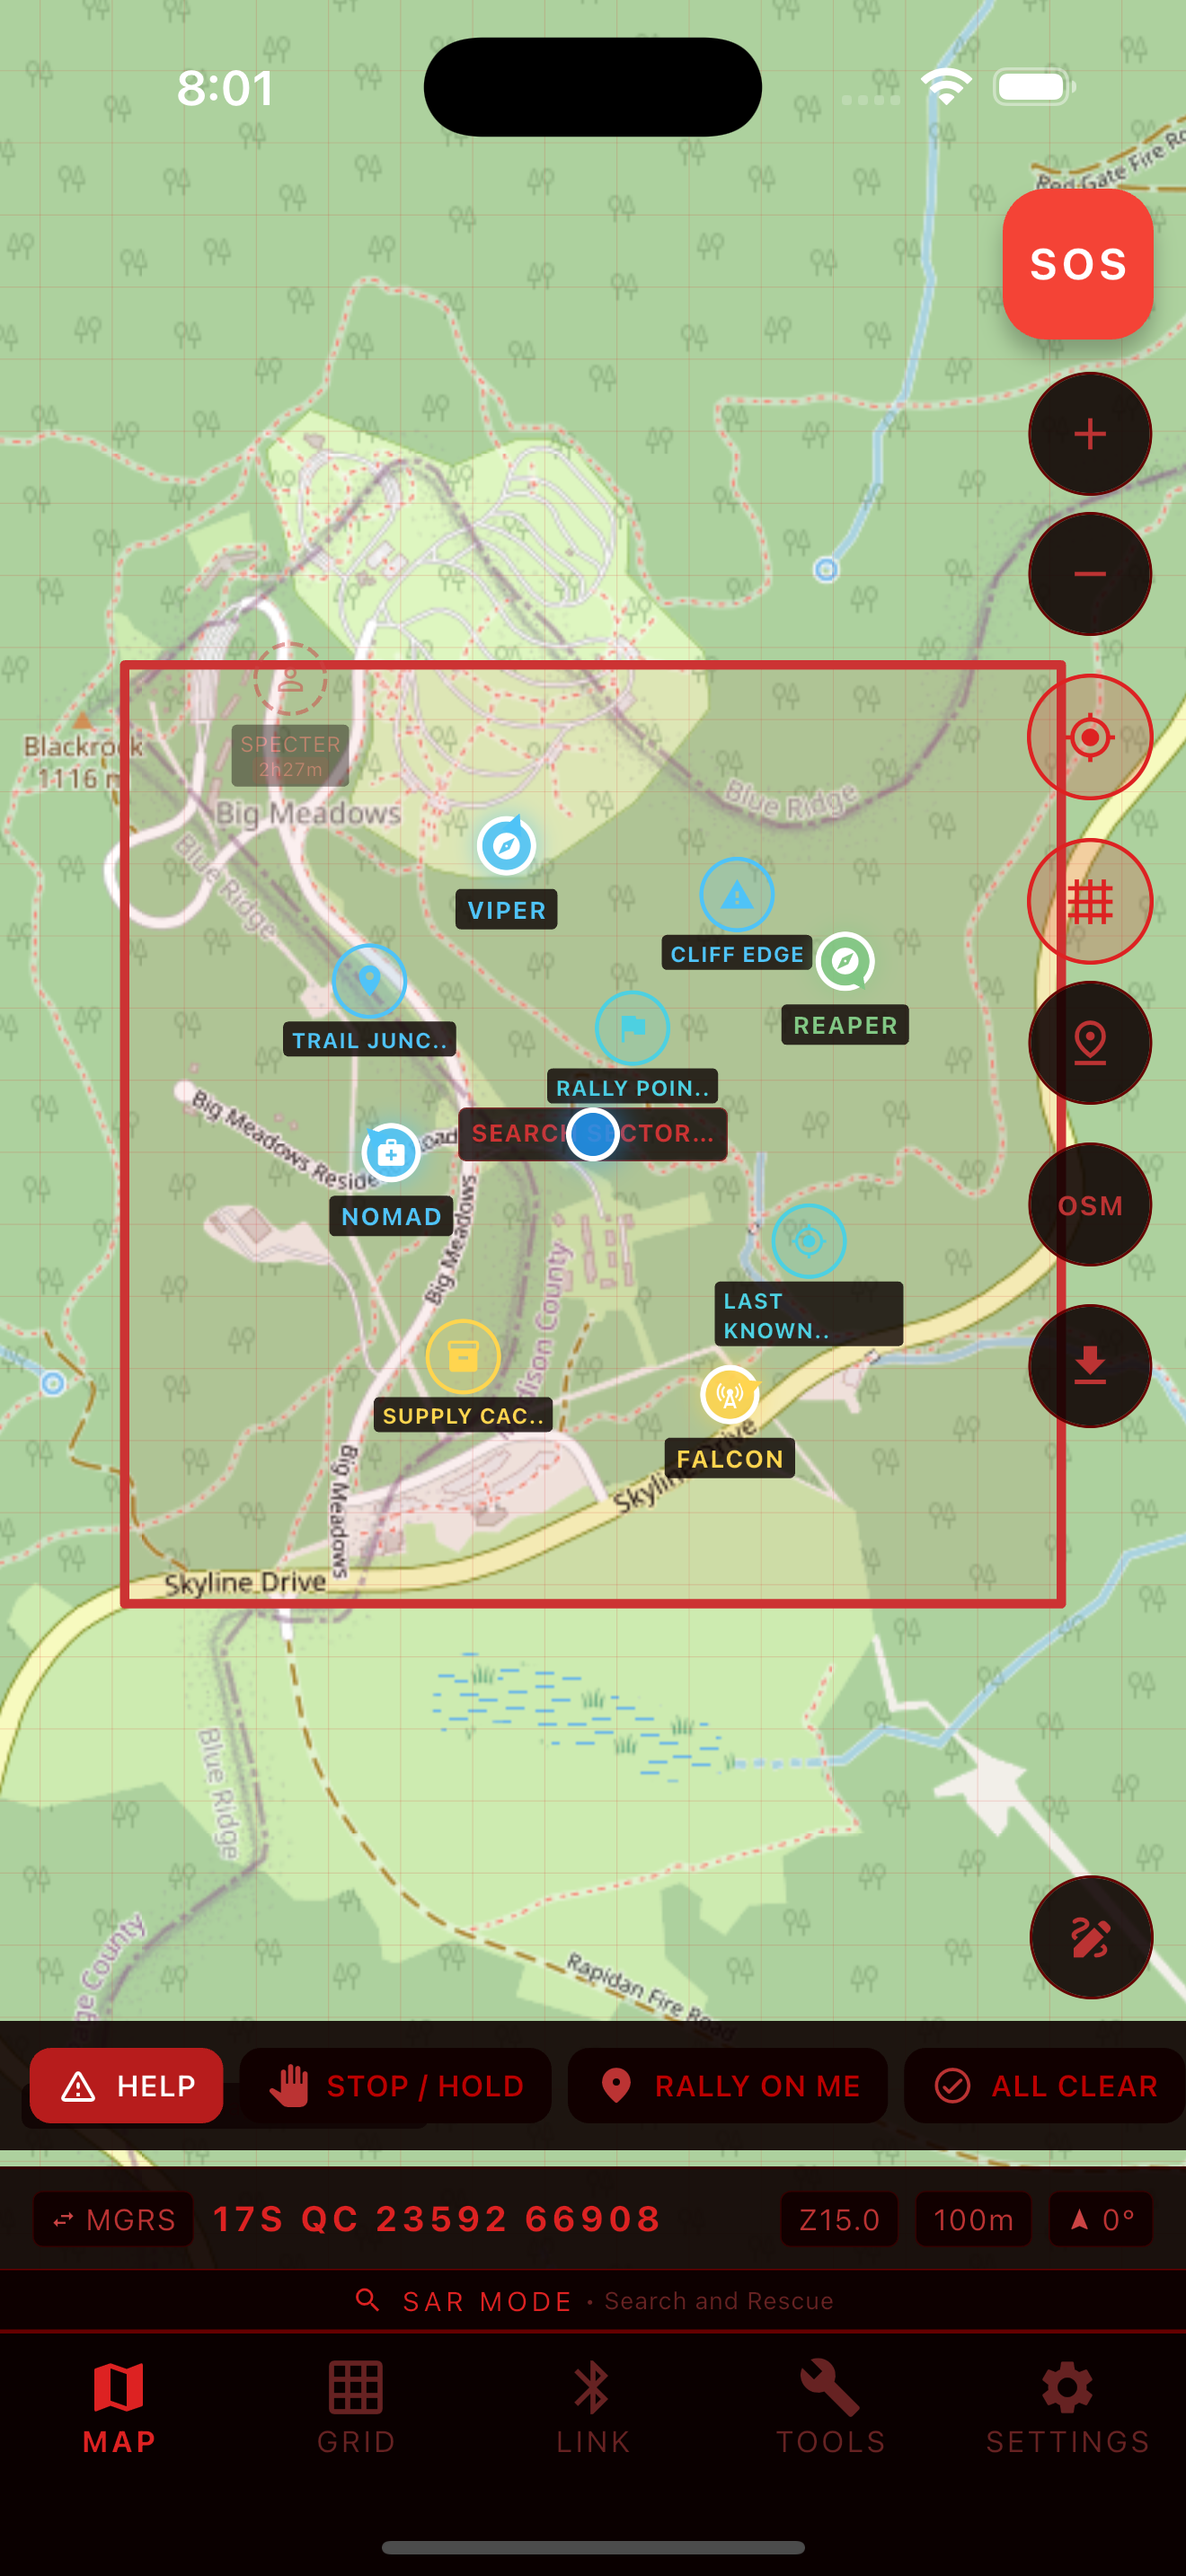 redgridtactical/redgridlink
Retired September 27, 2026. Final v1.7.0 source retained for reference; no new store downloads or purchases. Development continues in Red Grid MGRS,…
 yellowkeybitlocker-cve/yellowkey-bitlocker-cve-2026-45585
YellowKey BitLocker recovery audits CVE-2026-45585: yellowkey github, TPM, recovery key backup. Windows 10/11 CLI GUI, portable audit tool for…
 moond4rk/hackbrowserdata
Extract and decrypt browser data, supporting multiple data types, runnable on various operating systems (macOS, Windows, Linux).
 voidsecsoftwares/voidsec-proxy
Multi-module offensive security toolkit for SOCKS5 proxy chaining, port scanning, DNS enumeration, hash cracking, reverse shell generation,…
 ejfkdev/reyee_decrypt
Decrypt Ruijie ReyeeOS firmware (v1/v2) and encrypted config backups; recover plaintext passwords
 wyl-cmd/cve-2017-7921-research-toolkit
用于借助FOFA快速测试海康威视的CVE-2017-7921漏洞,并且给出登陆账号和密码,并输出json文件。
 b16f00t/whapa
Graphical forensic toolkit for parsing, decrypting, and extracting WhatsApp data from Android and iOS devices, including Google Drive and iCloud…
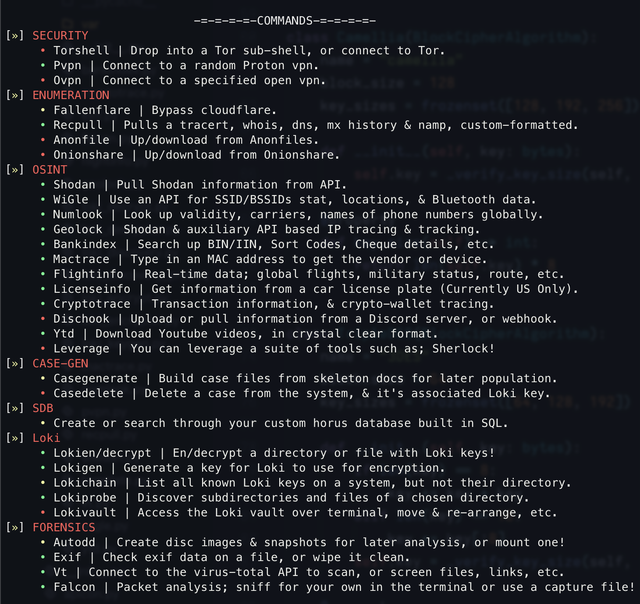 6abd/horus
An OSINT / digital forensics tool built in Python
 offsecpierogi/azure
Bash and PowerShell scripts for Azure security assessments, covering IAM privilege escalation, container registry exploitation, Key Vault exposure,…
 bimabalance/cve-2026-27944-tools-exploit
Suka suka lah
 okymi-x/cve-2021-43798
Python toolkit for authorized testing of CVE-2021-43798 Grafana path traversal, with arbitrary file read PoC, secret decryption, and user hash export…