
CVE-2026-mikrotik-poc
 gagaltotal/cve-2026-mikrotik-poc
CVE-2026-86060 - CVE-2026-67279 - CVE-2026-67276 RouterOS SSH
authenticationeducationembedded-systems-security+5
1
gagaltotal/cve-2026-mikrotik-pocCVE-2026-86060 - CVE-2026-67279 - CVE-2026-67276 RouterOS SSH
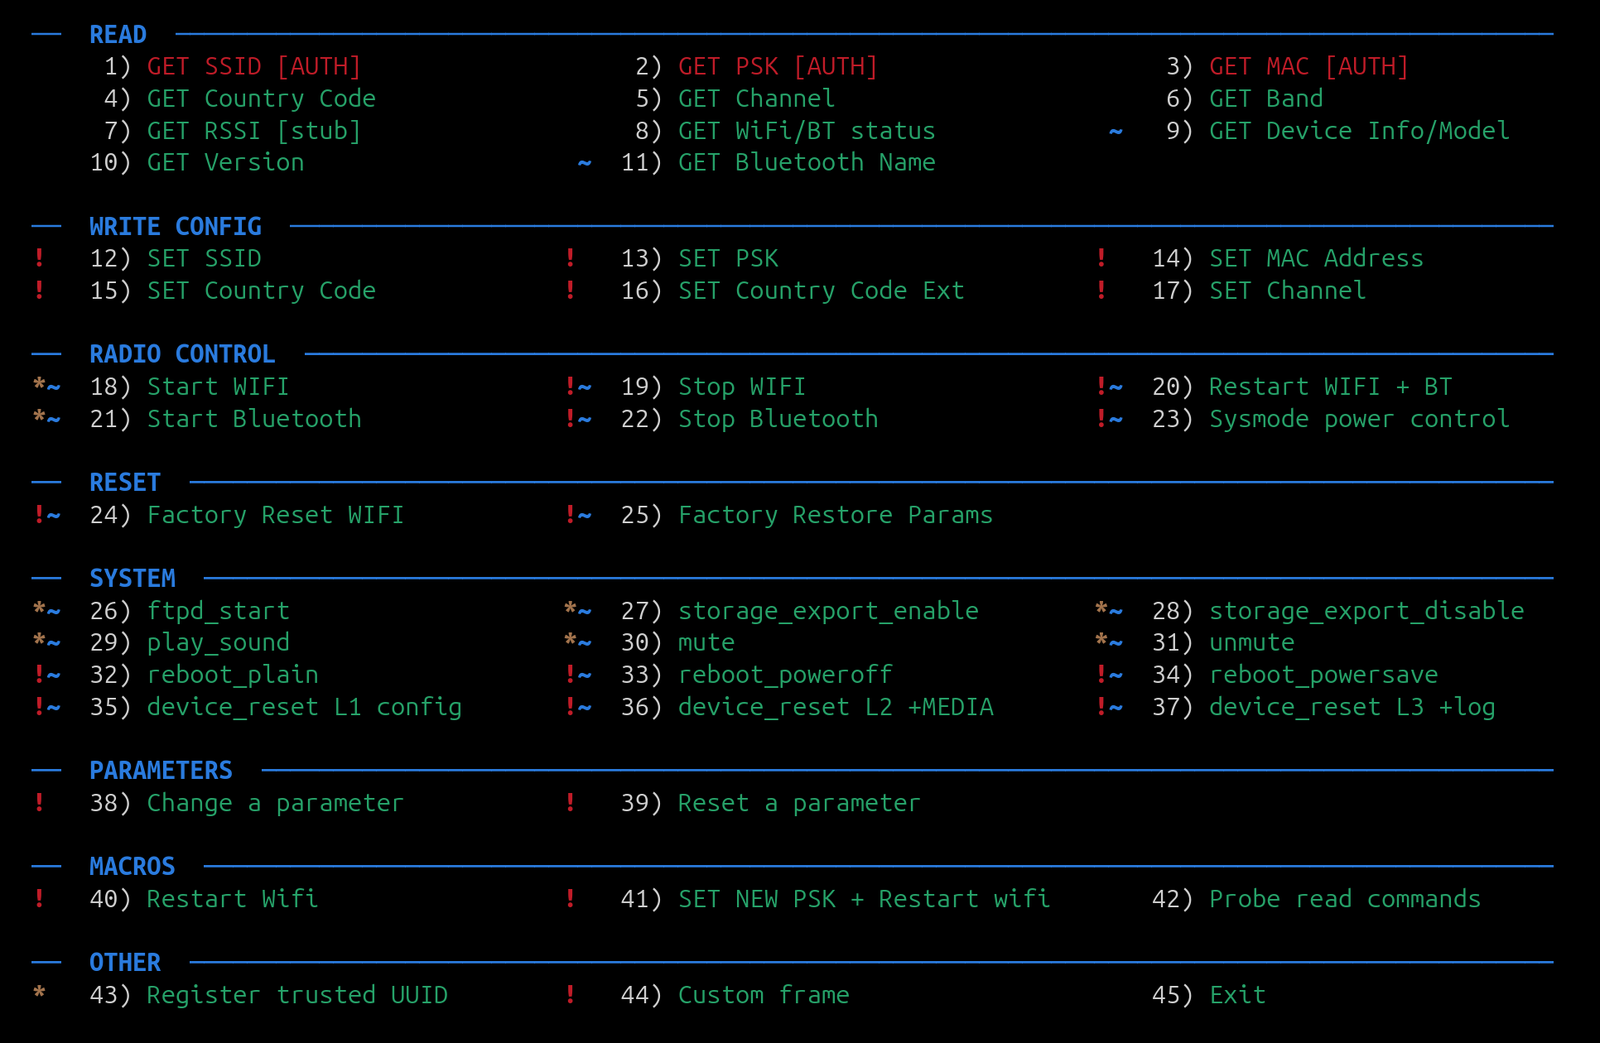 feedbeef/dji_ble_vuln
DJI Drone DUML Command Injection over Bluetooth — Proof of Concept for CVE-2026-78306
 mattgsys/cve-2026-19586
Python PoC exploiting CVE-2026-19586, an unauthenticated command injection in TP-Link Omada SSL VPN that executes arbitrary commands as root via…
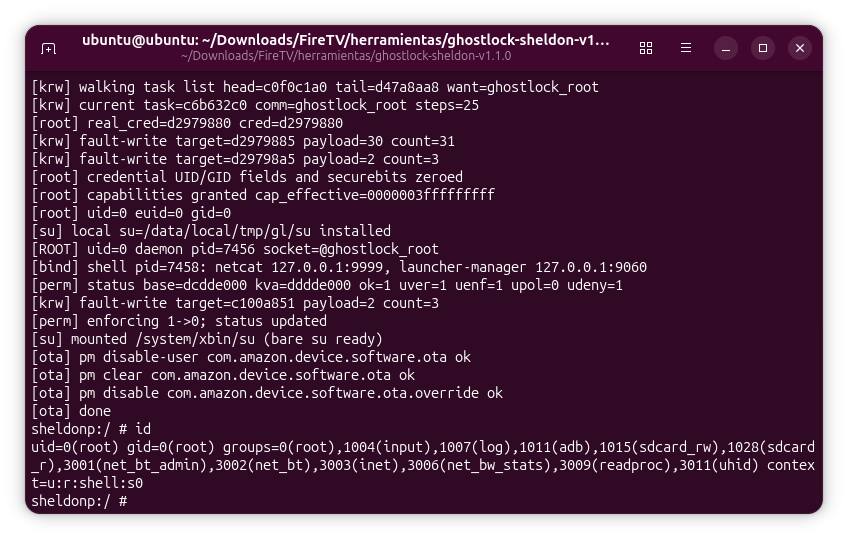 accessmodifier364/cve-2026-43499-firetv-sheldonp-writeup
Security research write-up on exploiting CVE-2026-43499 on the Amazon Fire TV Stick 3rd Gen (sheldonp), from temporary root to bootloader unlock.
 harshrajsinghania/cve-2026-86547-mrubyc-op-enter
Standalone proof of concept for CVE-2026-86547, a NULL pointer dereference in mrubyc op_enter() through 4.0.0.
 themalwareguardian/uefi-security-research-howyar-sysreturn-netcopy
Post CVE-2024-7344 analysis of Howyar SysReturn NetCopy - reverse engineering notes, vulnerable binaries, vendor correspondence, and proof-of-concept…
 doctormord/philips-pm-5139-5138a-5136-firmware-project
Firmware reverse engineering of the Philips PM5139 / PM5138A / PM5136 function generators: 8051 emulators used as measuring instruments, 35 sections…
 dsecurity/efiseek
Ghidra plugin that automates UEFI firmware analysis by identifying known GUIDs, protocols, SMI handlers, and interrupt functions, with headless…
 hellkkid/cve-2026-56718
AJCloud AJY IPC Firmware Path Traversal via jdbhttpd
 isukasanuj/cve-2026-85769
Proof-of-concept exploit for CVE-2026-85769, a heap out-of-bounds read in libtpms TPM 2.0 state deserialization, demonstrating denial of service via…
 pq-code-package/mlkem-native
Secure, fast, and portable C90 implementation of ML-KEM / FIPS 203
 jakestone594/f_hid-4.14-backports
Backports of three published f_hid fixes (incl. CVE-2026-31721, CVE-2026-31606) to an EOL Linux 4.14.190 Android vendor kernel, with on-device…
 pazhanivel07/system_bt_a10-r33_cve-2021-0474
Android Fluoride Bluetooth stack source code with a focus on CVE-2021-0474, providing a foundation for vulnerability research and security analysis…
 mbanyamer/cve-2026-32743-px4-autopilot-mavlinkloghandler-stack-buffer-overflow-dos-
A remote Denial of Service (DoS) exploit for PX4 Autopilot versions ≤1.17.0-rc2 via a stack‑based buffer overflow in the MavlinkLogHandler.
 mbanyamer/cve-2026-32707-px4-autopilot-tattu_can-stack-buffer-overflow-dos-
Proof-of-concept exploit for CVE-2026-32707, a stack buffer overflow in the PX4-Autopilot tattu_can driver, causing denial of service via crafted CAN…
 l0lsec/tapo-c260-rce
PoC exploit chain for TP-Link Tapo C260 camera — CVE-2026-0651/0652/0653. Research by @spaceraccoon.
 acen28/cve-2026-26399-disclosure
Disclosure of a stack-based use-after-return vulnerability in Arduino_Core_STM32, detailing technical root cause, affected versions, and fix, with…
 nfc-tools/libfreefare
A convenience API for NFC cards manipulations on top of libnfc.