
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
17 results
CVE-2026-73570 preview

CVE-2026-73570

GitHub0xblackash/cve-2026-73570

Advisory and detection guidance for CVE-2026-73570, an unauthenticated OS command injection in Zimbra SNMP notification processing leading to remote…
defensive-toolseducationemail-security+6
1
5 days ago
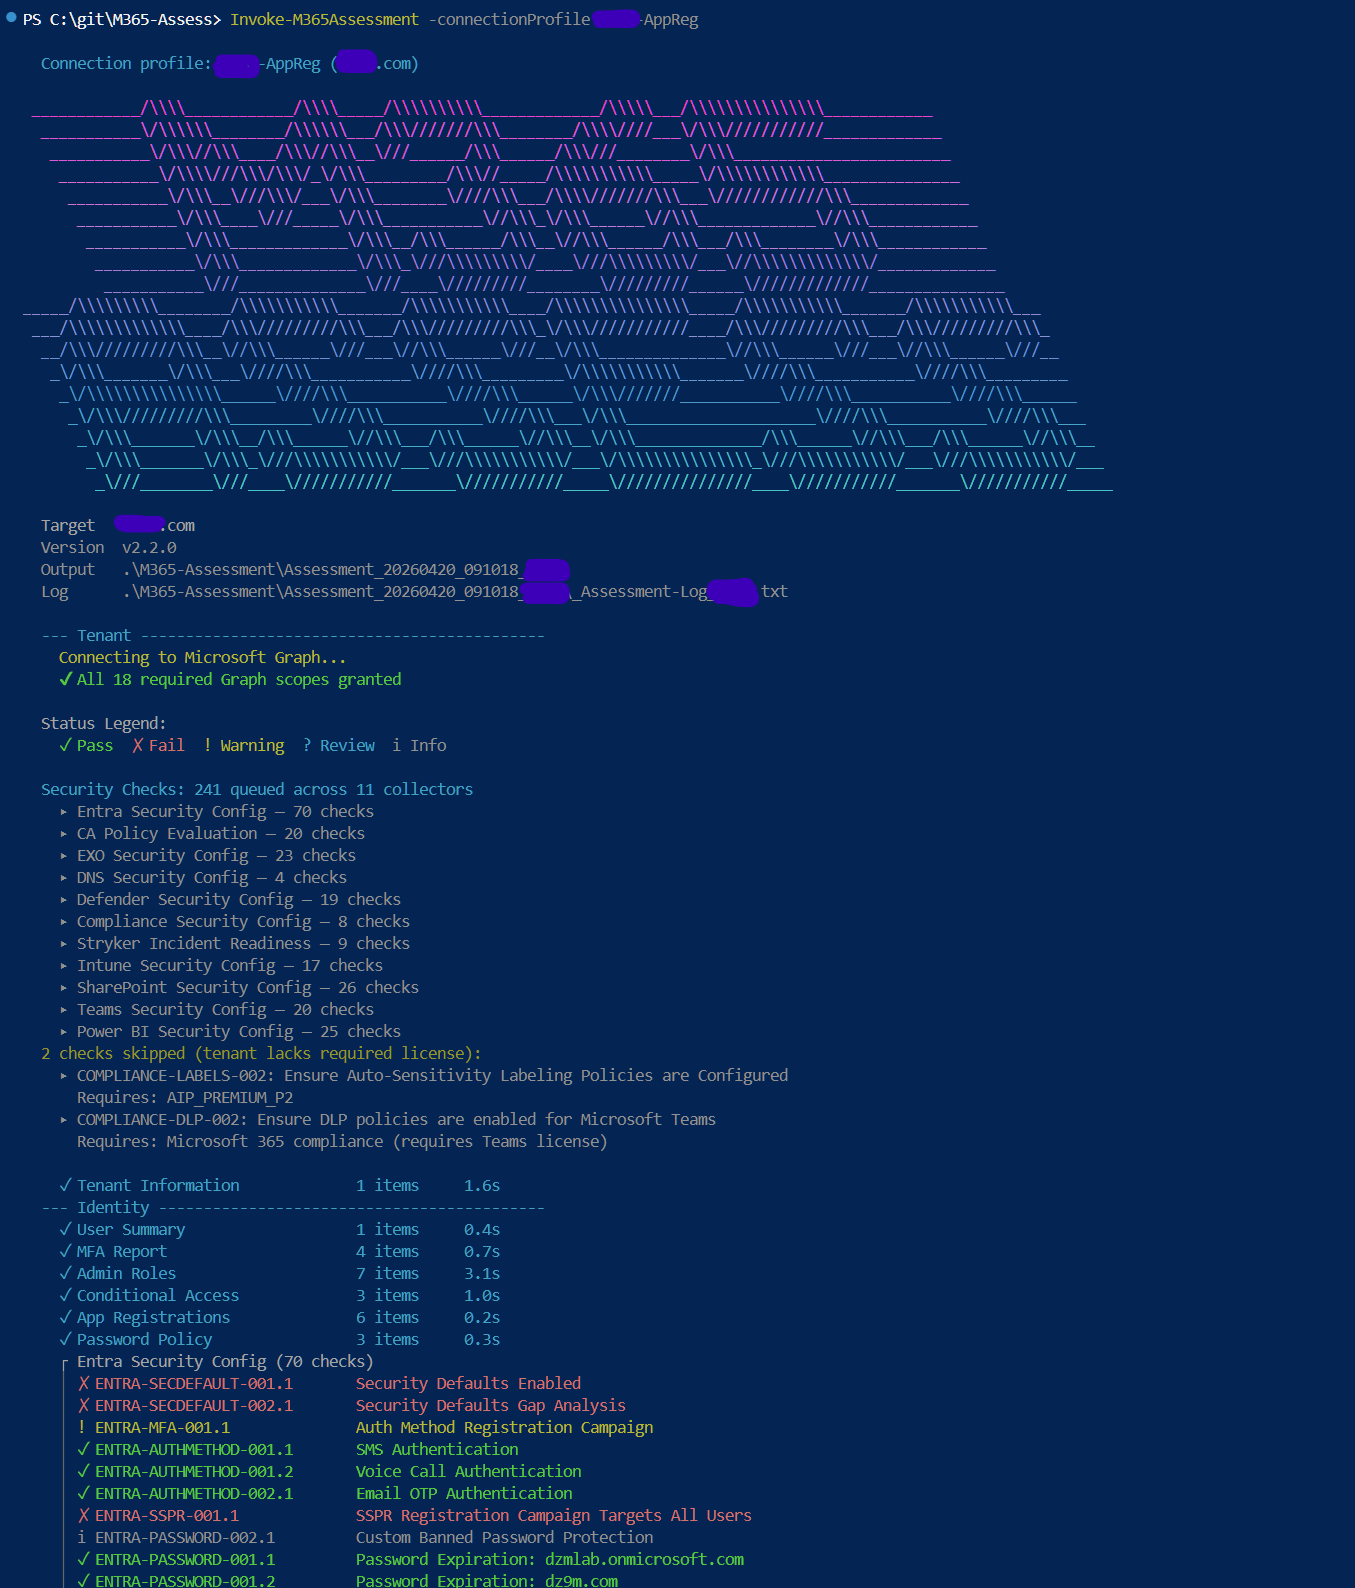
M365-Assess preview

M365-Assess

GitHubgalvnyz/m365-assess

290+ Automated checks across 14 compliance frameworks, interactive HTML report, no data leaves your machine.
cloud-securityconfiguration-auditingdevsecops+4
2046 days ago
CVE-2026-73570 preview

CVE-2026-73570

GitHubhainhc/cve-2026-73570

Proof-of-concept exploit for CVE-2026-73570, an unauthenticated OS command injection in Zimbra Collaboration Suite via zimbra-snmp log injection,…
email-securityexploitationincident-response+3
25 days ago
CVE-2026-73570 preview

CVE-2026-73570

GitHubbiutrap/cve-2026-73570

Proof-of-concept exploit for CVE-2026-73570, demonstrating SMTP command injection via crafted RCPT TO header to trigger service status changes.
email-securityexploitationvulnerability-analysis+1
1 month ago
CVE-2026-73570 preview

CVE-2026-73570

GitHubjishino567/cve-2026-73570

Python PoC for CVE-2026-73570, an SMTP command injection in Zimbra. Sends malformed RCPT TO payloads to trigger shell command execution via…
email-securityexploitationpenetration-testing+3
21 month ago
SOC336-Windows-OLE-Zero-Click-RCE-Exploitation-Detected-CVE-2025-21298 preview

SOC336-Windows-OLE-Zero-Click-RCE-Exploitation-Detected-CVE-2025-21298

GitHubabc1230940/soc336-windows-ole-zero-click-rce-exploitation-detected-cve-2025-21298

SOC336 - Windows OLE Zero-Click RCE Exploitation Detected (CVE-2025-21298) Walkthrough
command-and-controleducationemail-security+9
4 months ago
POC_CVE-2026-45185 preview

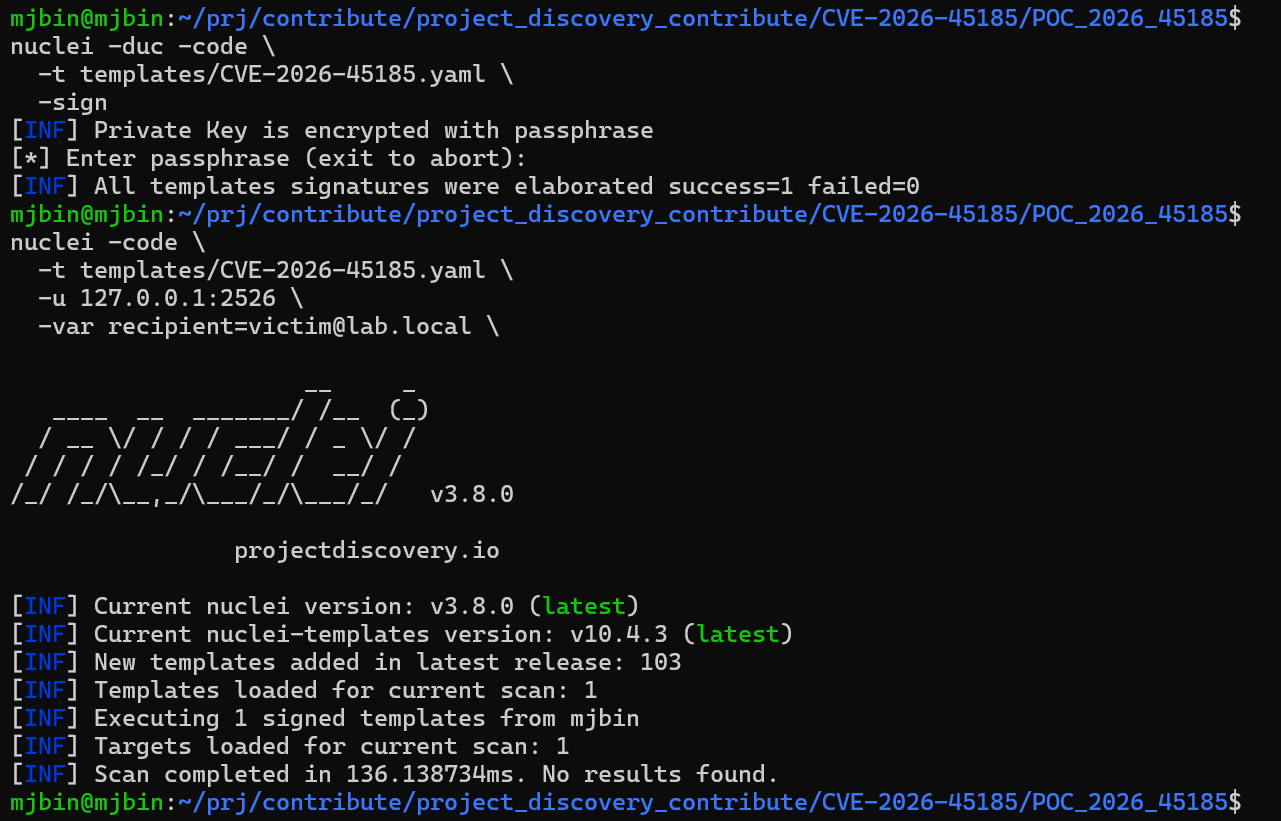
POC_CVE-2026-45185

GitHubmj-bin/poc_cve-2026-45185

POC_CVE-2026-45185 for nuclei-templates
educationemail-securityexploitation+3
44 months ago
Tangled preview

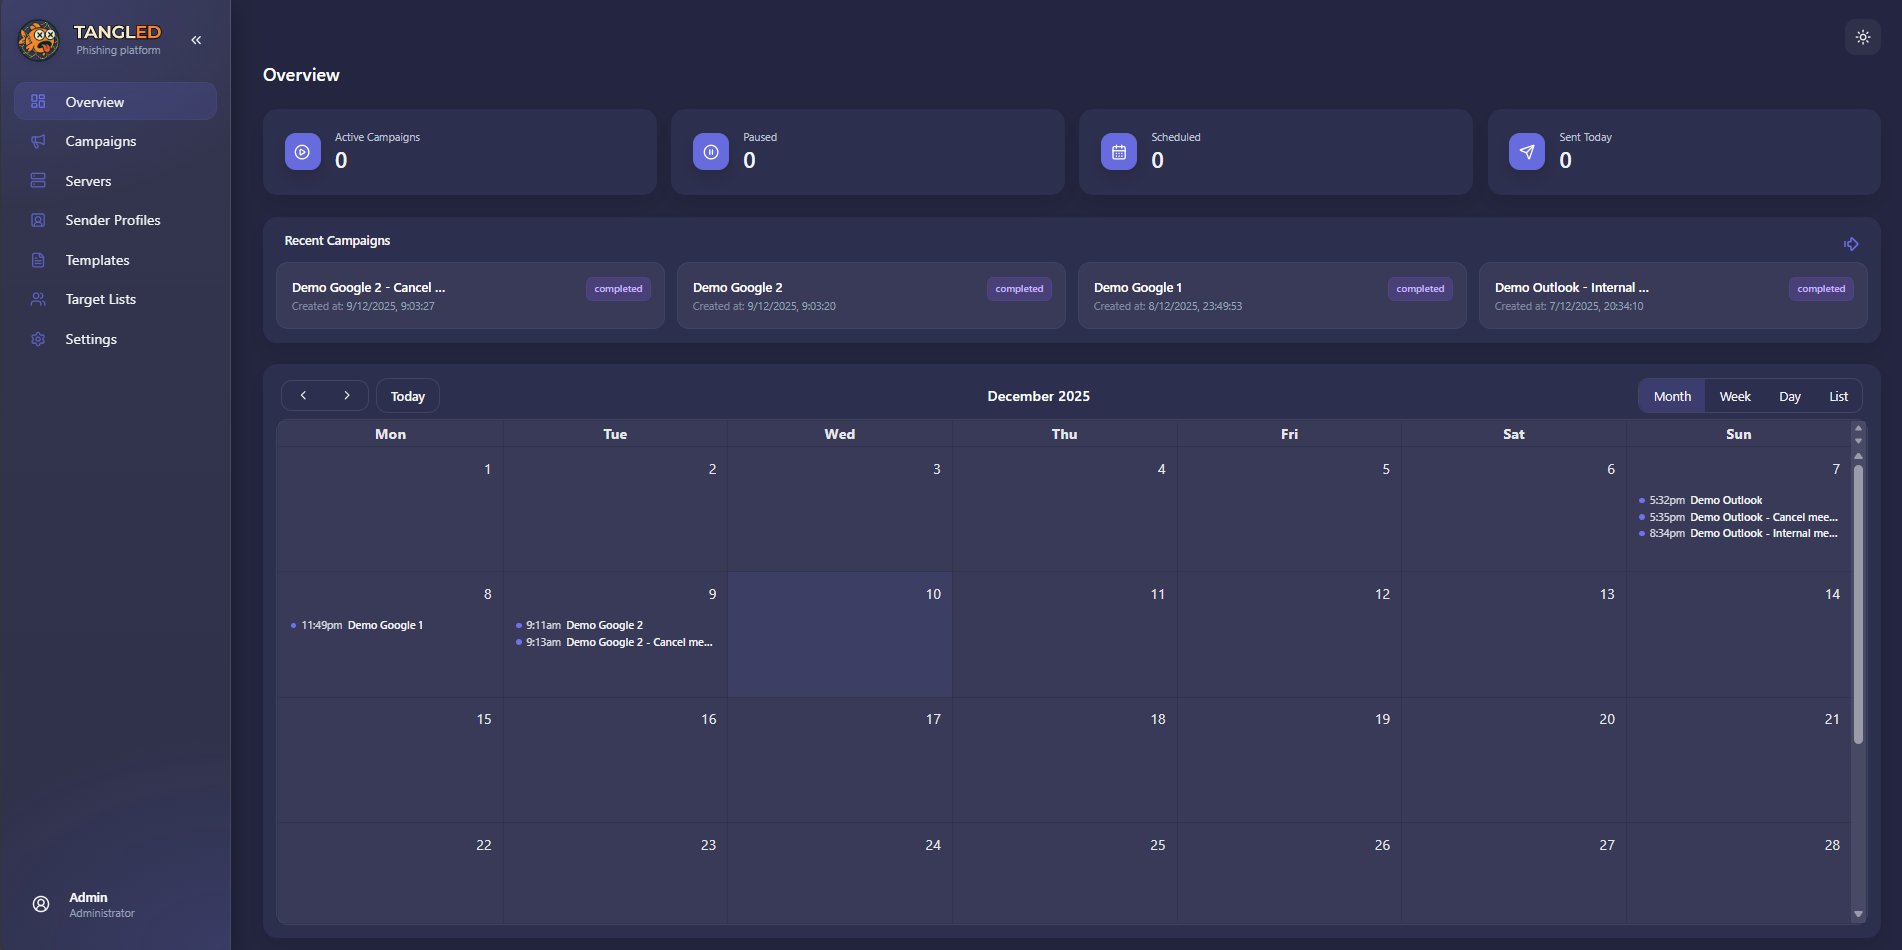
Tangled

GitHubineesdv/tangled

Open-source offensive security platform for conducting phishing campaigns that weaponizes iCalendar automatic event processing.
command-and-controlemail-securitylateral-movement+5
2759 months ago
python-inquestlabs preview

python-inquestlabs

GitHubinquest/python-inquestlabs

A Pythonic interface and command line tool for interacting with the InQuest Labs API.
email-securityhash-analysisinformation-gathering+4
3710 months ago
cve-2025-32711 preview

cve-2025-32711

GitHubdaryllundy/cve-2025-32711

PowerShell-based detection and remediation toolkit for CVE-2025-32711 (EchoLeak), a critical zero-click AI command injection vulnerability in…
ai-securitycloud-securityconfiguration-auditing+4
31 year ago
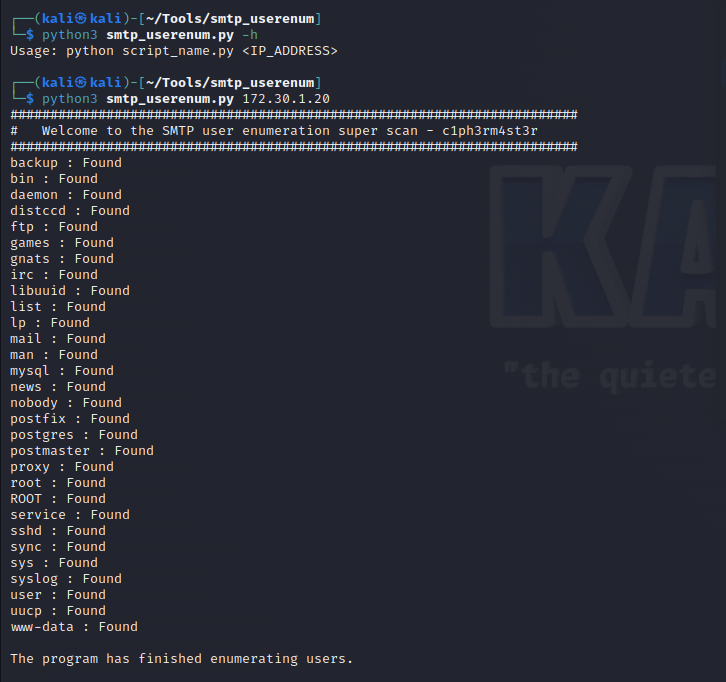
smtp_userenum preview

smtp_userenum

GitHubh3x0v3rl0rd/smtp_userenum

Python script for enumerating SMTP users by leveraging VRFY and EXPN commands to identify valid email accounts on a target mail server.
email-harvestingemail-securityinformation-gathering+4
1 year ago
Evilginx-Phishing-Infra-Setup preview

Evilginx-Phishing-Infra-Setup

GitHuban0nud4y/evilginx-phishing-infra-setup

Evilginx Phishing Infrastructure Setup Guide - Securing Evilginx and Gophish Infrastructure, Removing IOCs, Phishing TTPs
command-and-controlcurated-resourceseducation+6
6091 year ago
CVE-2025-43920 preview

CVE-2025-43920

GitHub0nyx-my7h/cve-2025-43920

PoC and technical write-up for CVE-2025-43920, a remote command injection in GNU Mailman 2.1.39's external archiver allowing unauthenticated code…

command-and-controlemail-securityexploitation+3
11 year ago
AmzWord preview

AmzWord

GitHubjump-wang-111/amzword

An automated attack chain based on CVE-2022-30190, 163 email backdoor, and image steganography.
command-and-controleducationemail-security+6
12 years ago
smtpshell preview

smtpshell

GitHubmachine1337/smtpshell

A simple Reverse Shell that can communicate through Gmail SMTP or any other SMTP to evade network restrictions
command-and-controlemail-securityred-teaming+1
82 years ago
overlord preview

overlord

GitHubqsecure-labs/overlord

Python-based CLI for automated red team infrastructure deployment on AWS and Digital Ocean, with modular support for C2, email servers, HTTP…
cloud-securitycommand-and-controlemail-security+3
6384 years ago
BadOutlook preview

BadOutlook

GitHubaahmad097/badoutlook

Proof-of-concept C# tool that reads Outlook emails via COM interface, extracts base64-encoded shellcode from trigger subject lines, and executes…

command-and-controlemail-securityexploitation+3
1375 years ago