
cakephp-smtp-crlf
 abraxas/cakephp-smtp-crlf
CakePHP 5.4.2 - High - Remote - Header injection - SmtpTransport lone LF leftover of GHSA-2qh5
email-securityexploitationpenetration-testing+4
abraxas/cakephp-smtp-crlfCakePHP 5.4.2 - High - Remote - Header injection - SmtpTransport lone LF leftover of GHSA-2qh5
 synacktiv/aadoutsider-py
Python3 rewrite of AsOutsider features of AADInternals
 thoropass-public/area51
The exploit server for out-of-band findings. Point a target at a domain you own. Every HTTP request and every email it sends back lands in a…
 hainhc/cve-2026-73570
Proof-of-concept exploit for CVE-2026-73570, an unauthenticated OS command injection in Zimbra Collaboration Suite via zimbra-snmp log injection,…
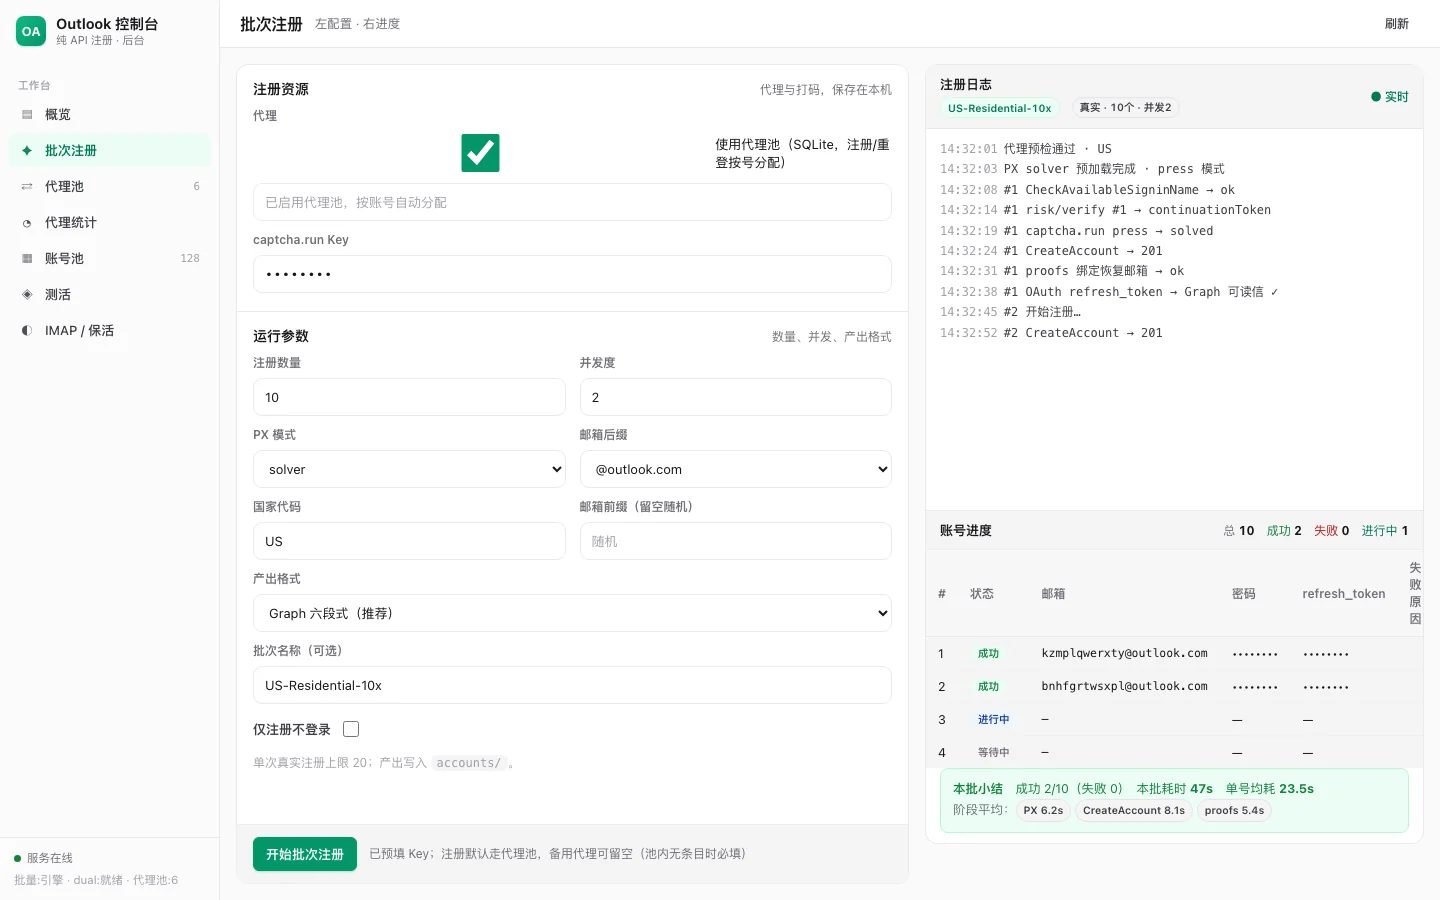 lxf746/outlook-auto-register
Automated Outlook account registration tool using pure HTTP protocol with PerimeterX captcha solving, proxy pool management, and email token…
 jishino567/cve-2026-73570
Python PoC for CVE-2026-73570, an SMTP command injection in Zimbra. Sends malformed RCPT TO payloads to trigger shell command execution via…
 biutrap/cve-2026-73570
Proof-of-concept exploit for CVE-2026-73570, demonstrating SMTP command injection via crafted RCPT TO header to trigger service status changes.
 horkimhab/cve-2026-73570
Proof-of-concept exploit for an actively exploited Zimbra Collaboration Suite vulnerability, designed for authorized penetration testing and…
 ashwesker/ashwesker-cve-2025-68645
POC BLH Magelang CSIRT 2026 by babyrootkid
 0xblackash/cve-2026-28289
CVE-2026-28289
 saykino/cve-2026-31283
Documentation of CVE-2026-31283: an email bombing vulnerability in Totara LMS's forgot password API due to missing rate limiting, allowing…
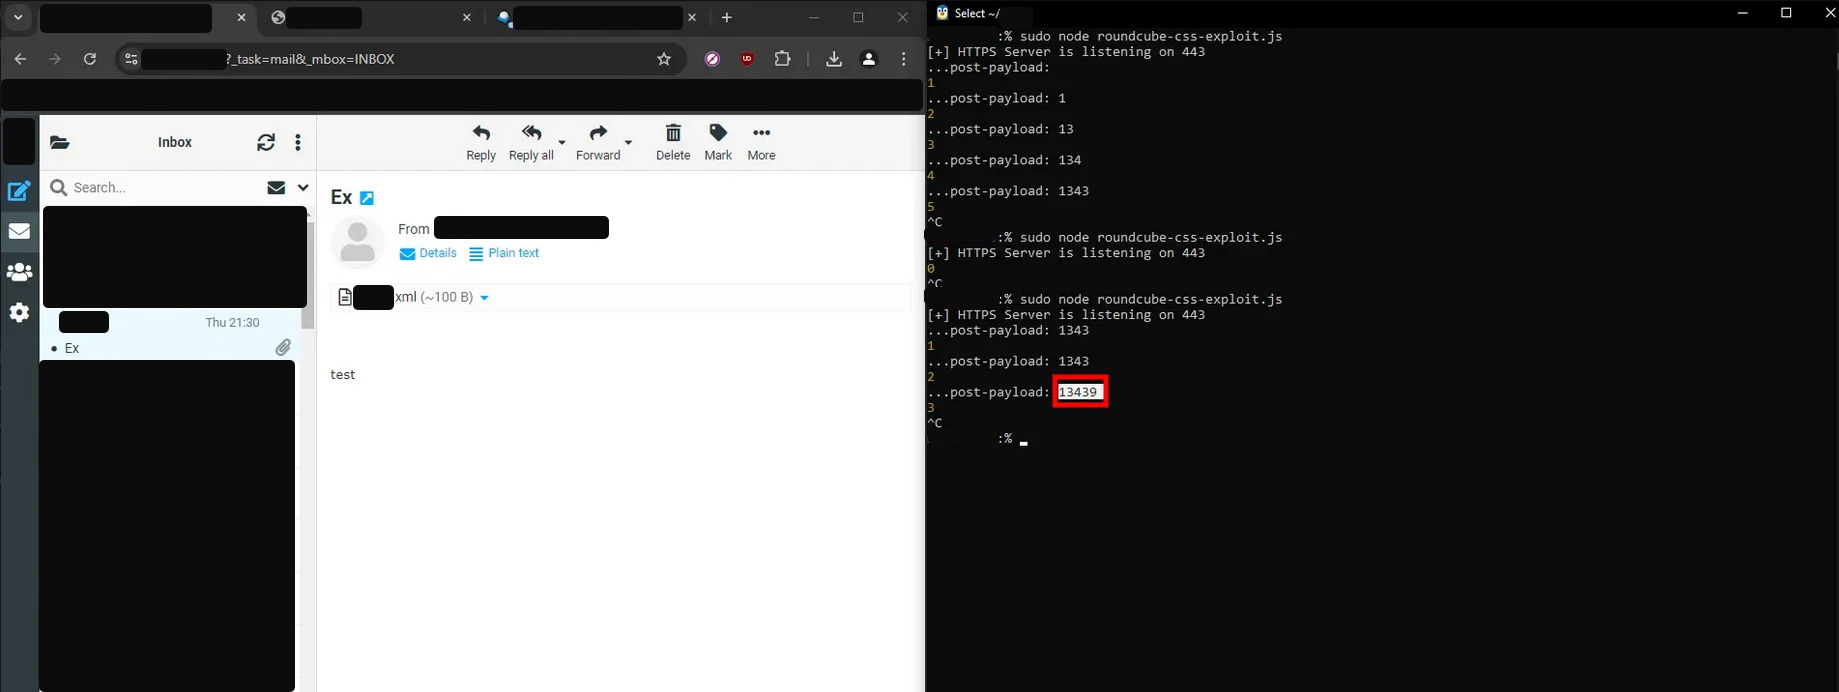 victoni/roundcube-cve-2024-42008-and-cve-2024-42010-poc
POC for Roundcube vulnerabilities CVE-2024-42008 and CVE-2024-42010
 saykino/cve-2025-54320
Proof-of-concept for CVE-2025-54320: an email bombing vulnerability in Ascertia SigningHub's Invite User API due to missing rate limiting, allowing…
 eeenvik1/cve-2023-51764
Proof-of-concept exploit for CVE-2023-51764 SMTP smuggling vulnerability in Postfix, enabling email spoofing and message injection via crafted SMTP…
 demossl/cve-2021-33766-proxytoken
Proof-of-concept exploit for CVE-2021-33766 (ProxyToken) authentication bypass in Microsoft Exchange Server. Supports single and batch target…
 derrickschoen/laravel-framework
Fork of laravel/framework 10.50.2 with CVE-2026-48019 (CRLF injection in default email rule) backported into ValidatesAttributes::validateEmail.…