CVE-2026-76461-Detection-Kit-

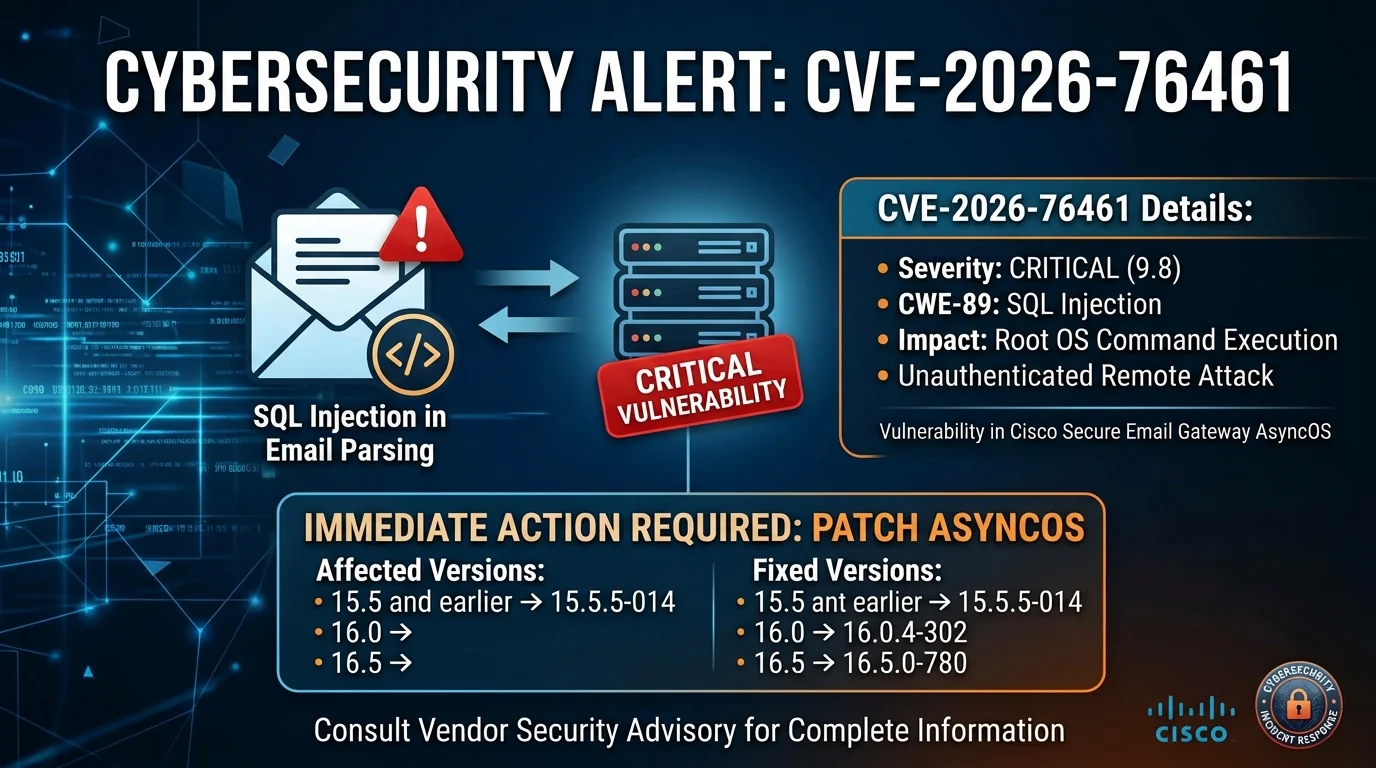
Defensive detection kit for CVE-2026-76461, a critical SQL injection in Cisco Secure Email Gateway, with Sigma and YARA rules, IOCs, and remediation…

Defensive detection kit for CVE-2026-76461, a critical SQL injection in Cisco Secure Email Gateway, with Sigma and YARA rules, IOCs, and remediation…

Research repository for CVE-2026-76461, a critical SQL injection in Cisco Secure Email Gateway leading to root RCE, with detection rules, mitigation…

The exploit server for out-of-band findings. Point a target at a domain you own. Every HTTP request and every email it sends back lands in a…

Proof-of-concept exploit for CVE-2026-73570, an unauthenticated OS command injection in Zimbra Collaboration Suite via zimbra-snmp log injection,…

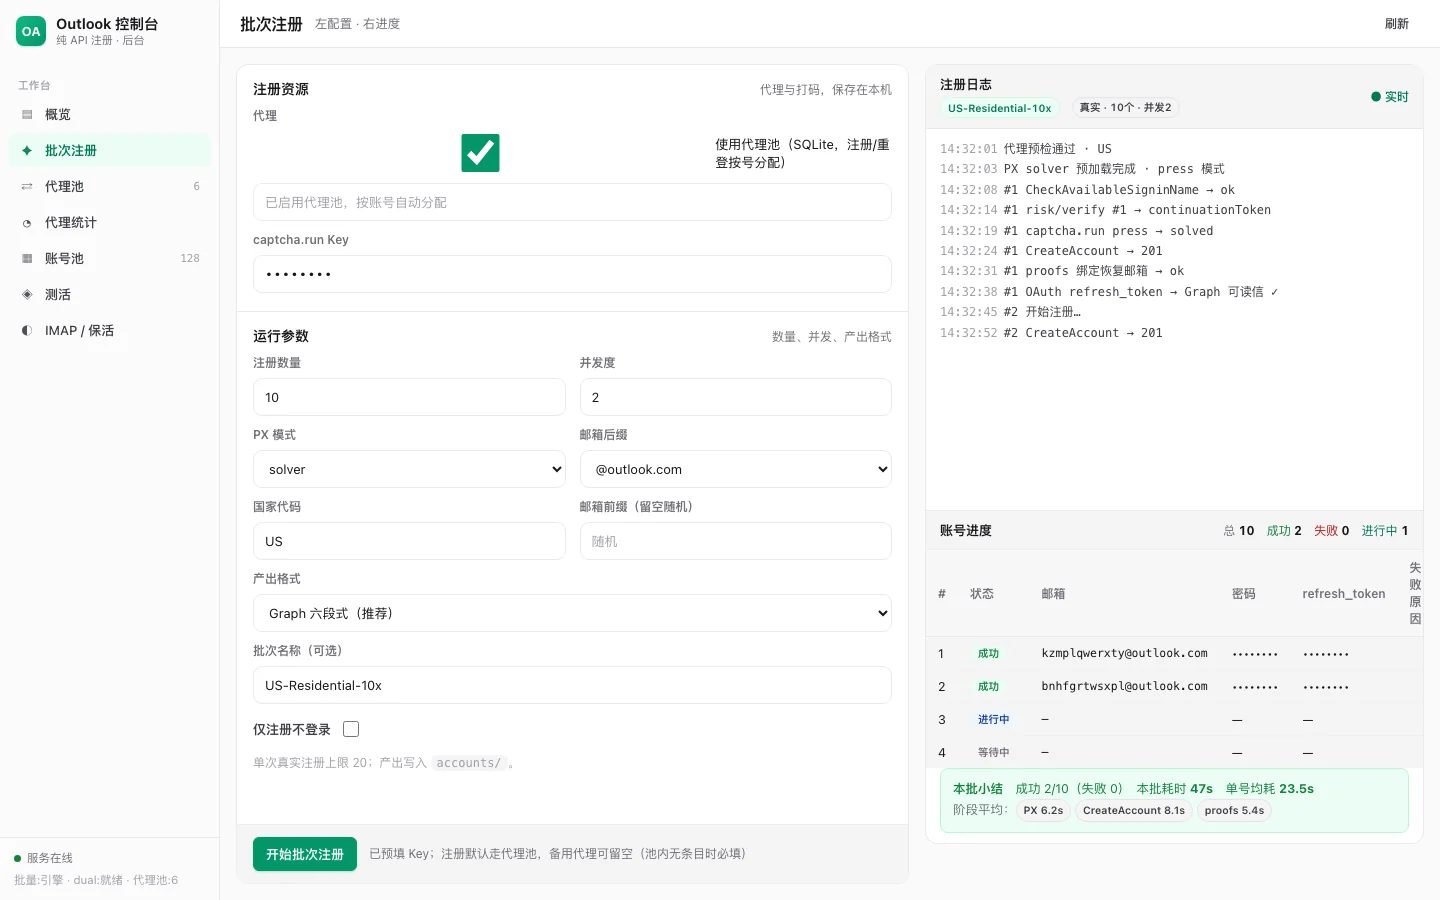
Automated Outlook account registration tool using pure HTTP protocol with PerimeterX captcha solving, proxy pool management, and email token…

Collection of offensive red team scripts including process termination, SPF bypass for phishing, password spraying, and ColdFusion password…

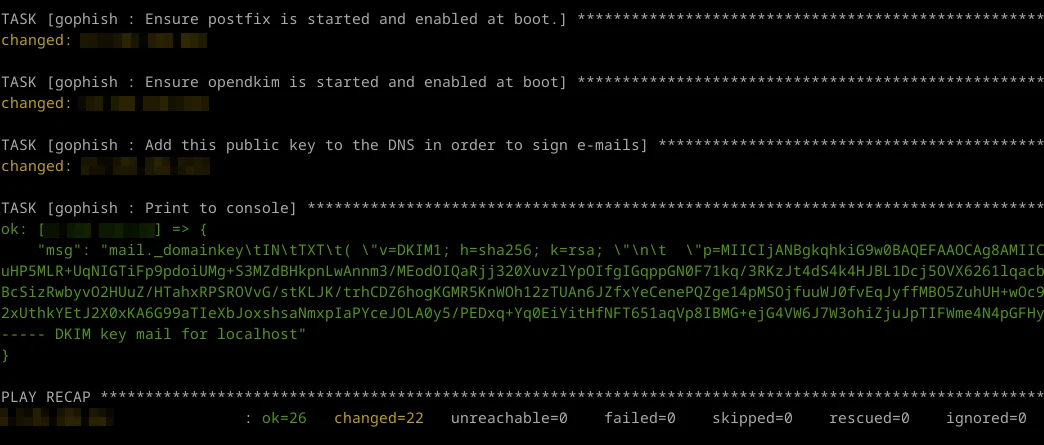
Deploy a phishing infrastructure on the fly.

Perl scripts for SSL/TLS analysis: check protocol and cipher support, verify certificates, test OCSP, and detect Heartbleed across SMTP, HTTPS, and…

Purple team project exploiting CVE-2023-23397 Outlook NTLM leak with phishing delivery, plus Sigma/Wazuh detections mapped to MITRE ATT&CK for the…

CRLF email header injection in Plunk raw MIME construction — CVE-2026-34975 / CVSS 8.5

Python exploit for Roundcube Webmail DOM-based XSS (CVE-2026-25916) via SVG href attributes, enabling session hijacking and data exfiltration through…

Python PoC for CVE-2026-73570, an SMTP command injection in Zimbra. Sends malformed RCPT TO payloads to trigger shell command execution via…

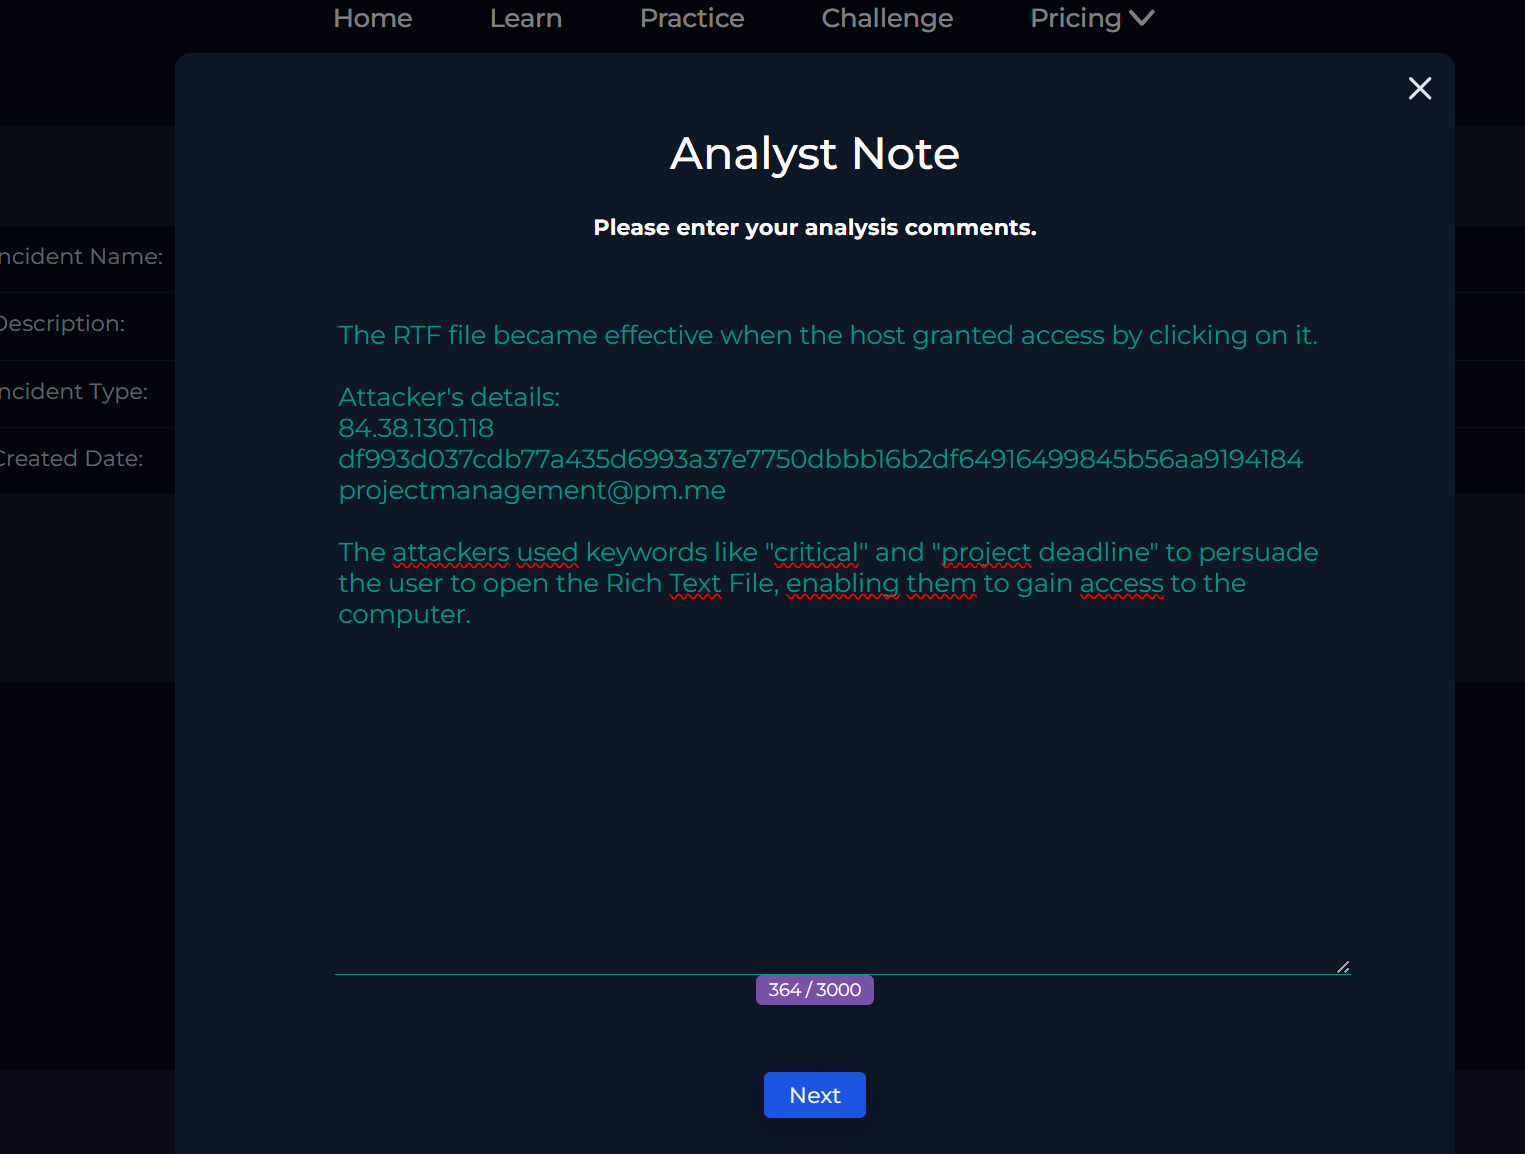
We are expected to investigate a critical alert reporting a Windows OLE zero-click RCE exploitation (CVE-2025-21298) delivered via a malicious RTF…

Proof-of-concept exploit for CVE-2026-73570, demonstrating SMTP command injection via crafted RCPT TO header to trigger service status changes.

Tuning and refactoring Google Chronicle Curated Detections to eliminate alert fatigue and fix logic gaps/bugs.

Real-time cloud-native runtime security agent for Linux that monitors syscalls and container/Kubernetes metadata to detect anomalous behavior and…

Open-source antivirus engine for detecting trojans, viruses, and malware via signature-based scanning; includes a daemon, on-demand CLI, and…

Open-source email filtering framework that detects spam and phishing using content analysis, header checks, Bayesian scoring, and DNS blocklists.