

Loki
 neo23x0/loki
IOC and YARA-based scanner for detecting indicators of compromise via file name regex, YARA signatures, hash matching, and C2 back-connect checks on…
anomaly-detectiondigital-forensicsdisk-forensics+11
neo23x0/lokiIOC and YARA-based scanner for detecting indicators of compromise via file name regex, YARA signatures, hash matching, and C2 back-connect checks on…
 thoropass-public/area51
The exploit server for out-of-band findings. Point a target at a domain you own. Every HTTP request and every email it sends back lands in a…
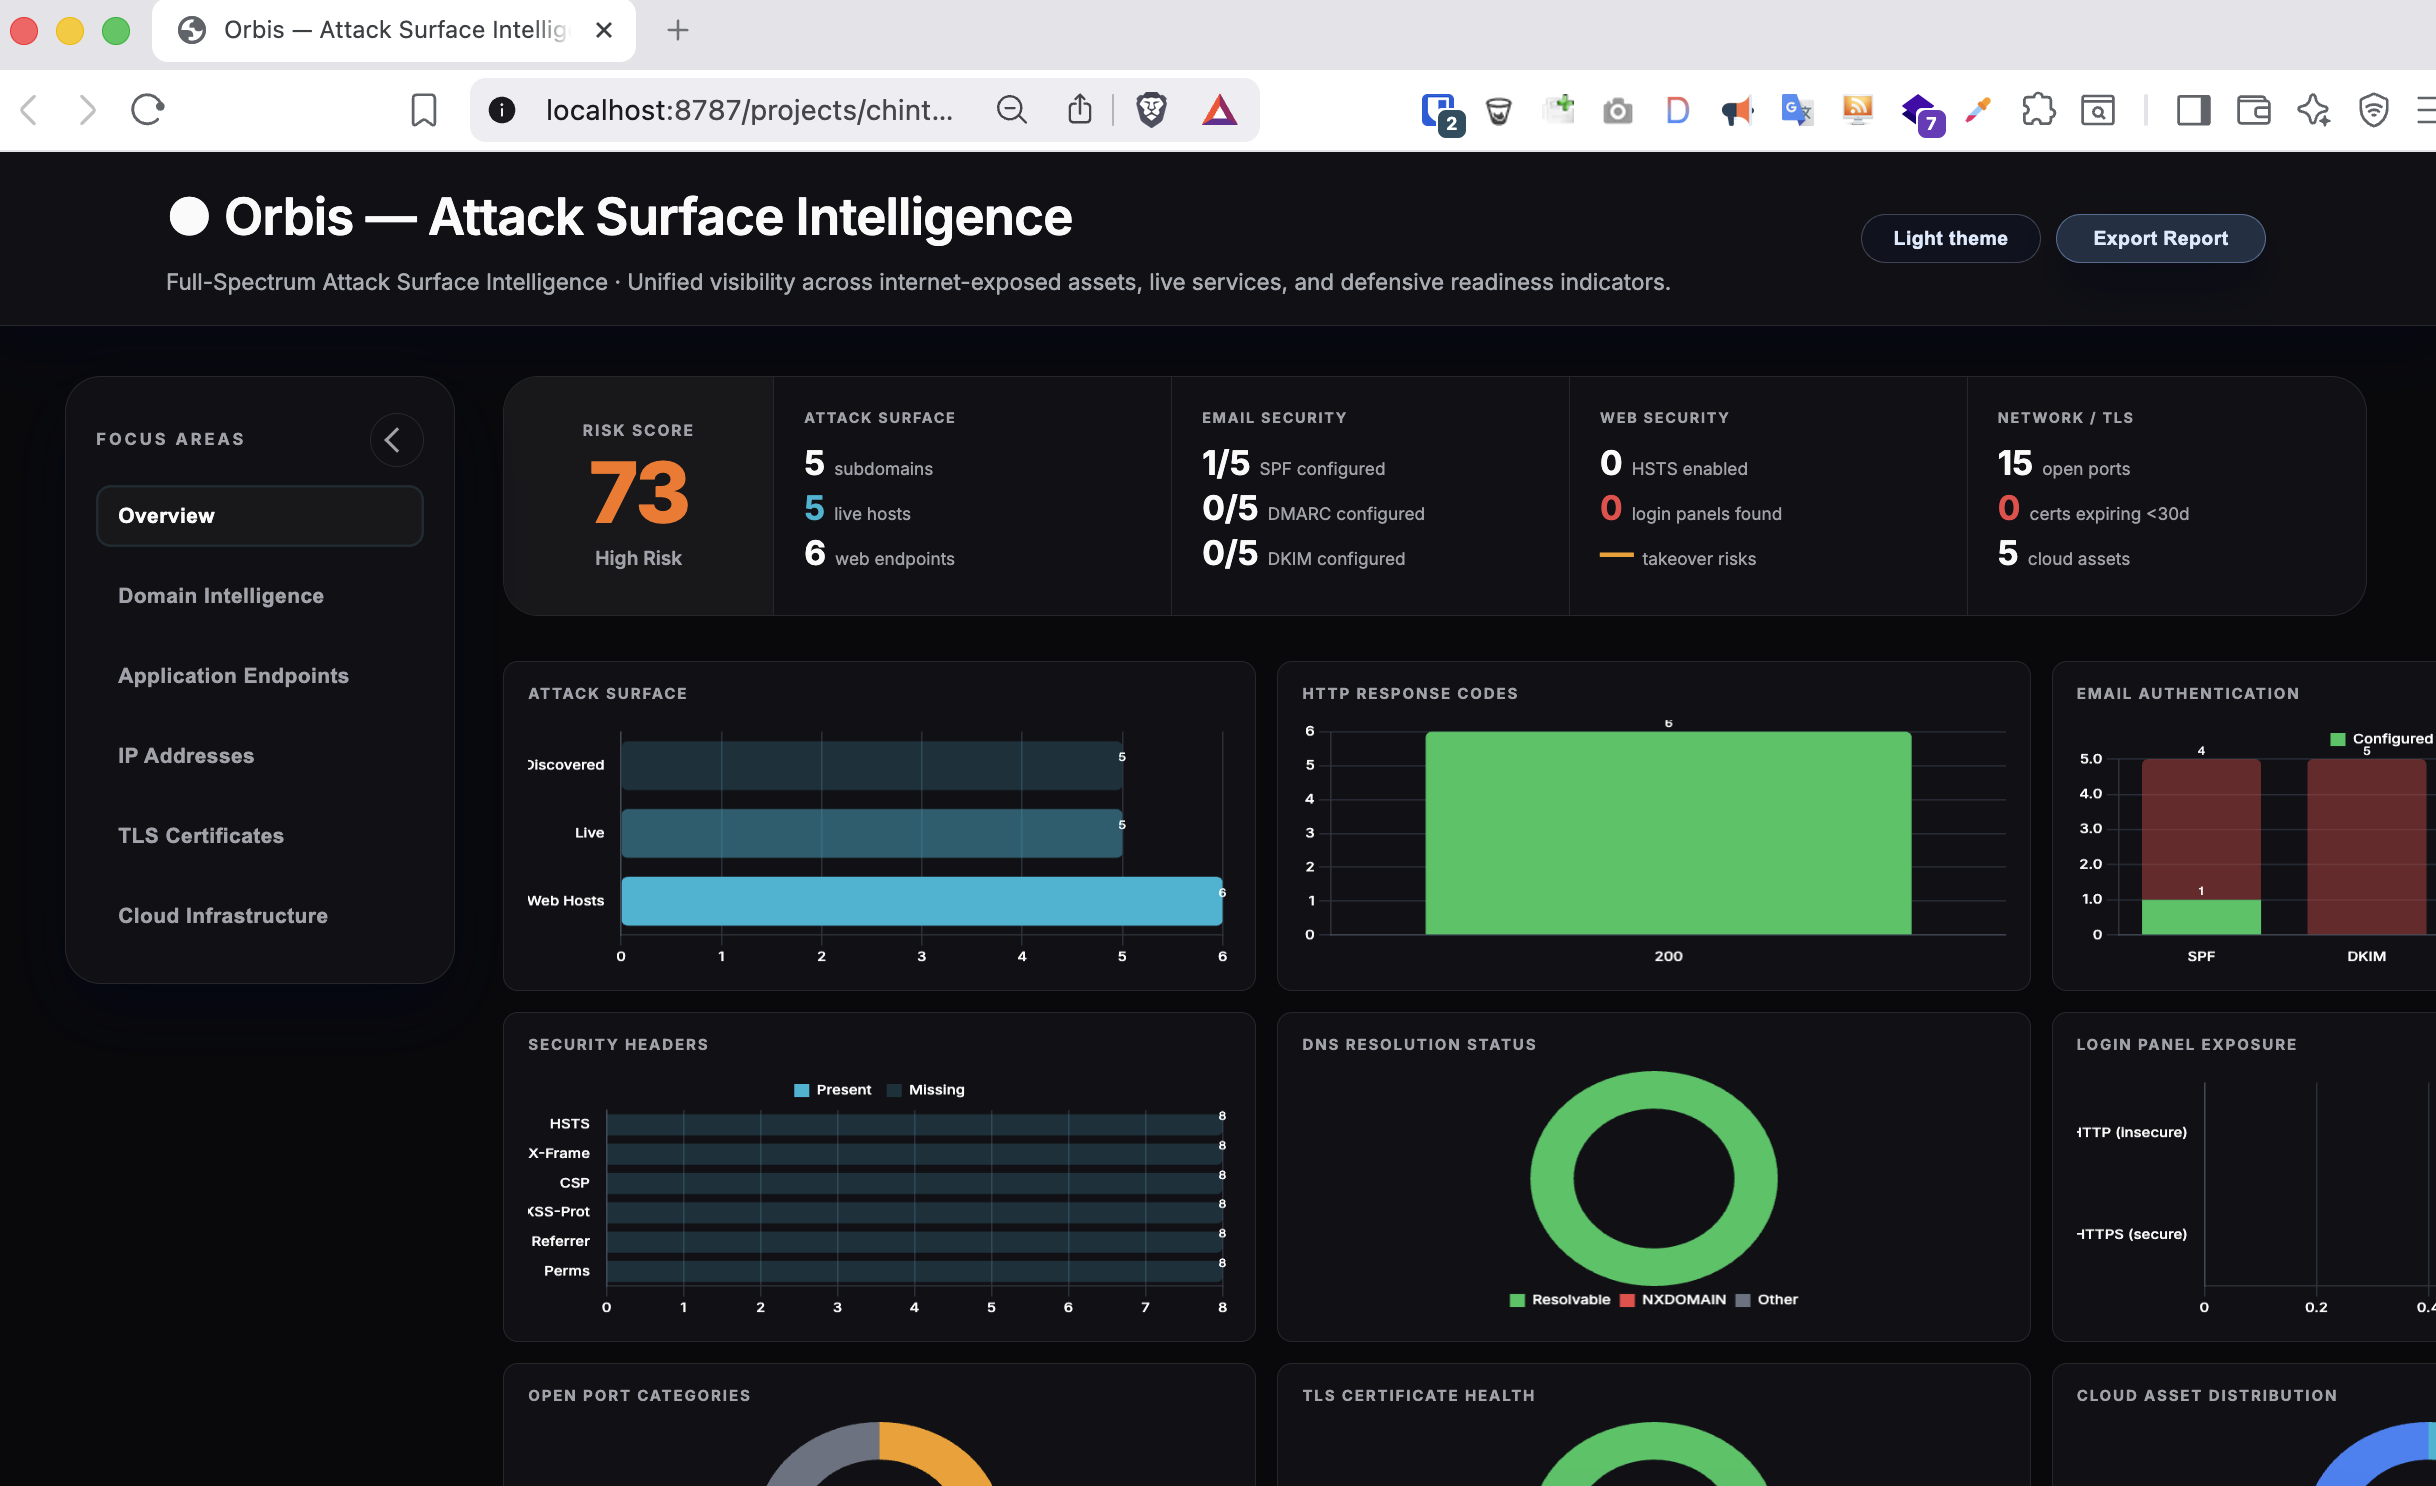 iamthefrogy/frogy2.0
Orbis is an full spectrum automated external attack surface intelligent toolkit.
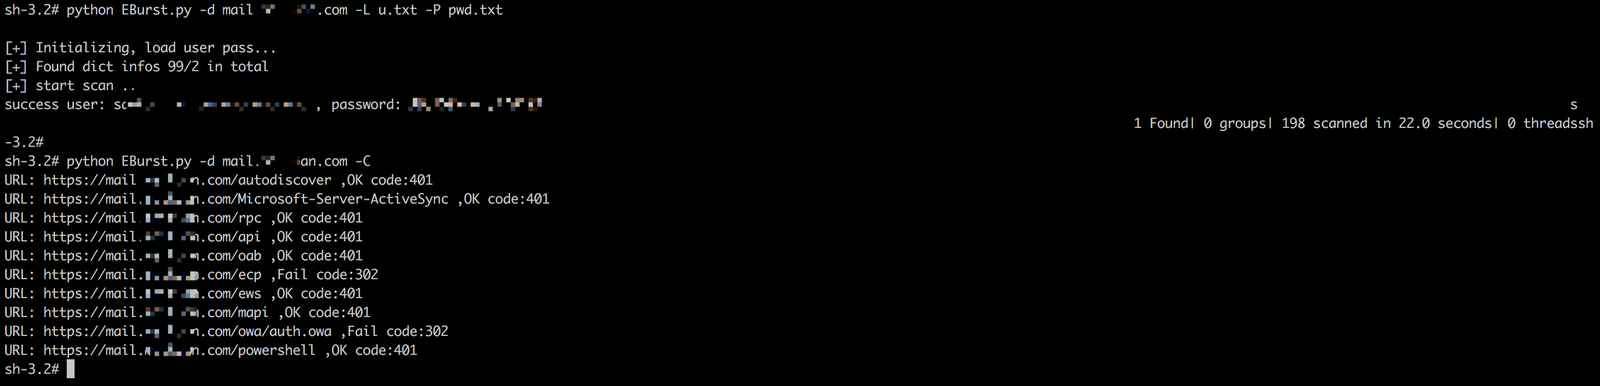 grayddq/eburst
这个脚本主要提供对Exchange邮件服务器的账户爆破功能,集成了现有主流接口的爆破方式。
 arno0x/ntlmrelaytoews
ntlm relay attack to Exchange Web Services
 lissy93/awesome-privacy
🦄 A curated list of privacy & security-focused software and services
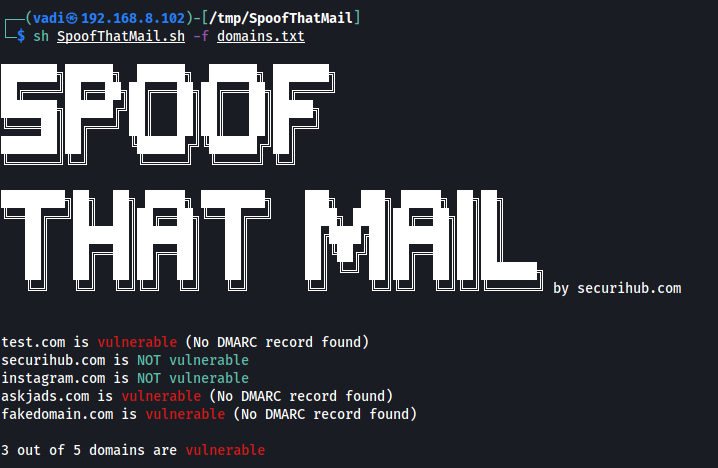 v4d1/spoofthatmail
Bash script to check if a domain or list of domains can be spoofed based in DMARC records
 synacktiv/aadoutsider-py
Python3 rewrite of AsOutsider features of AADInternals
 drpython3/mailripv2
Improved SMTP Checker / SMTP Cracker with proxy-support, inbox test and many more features.
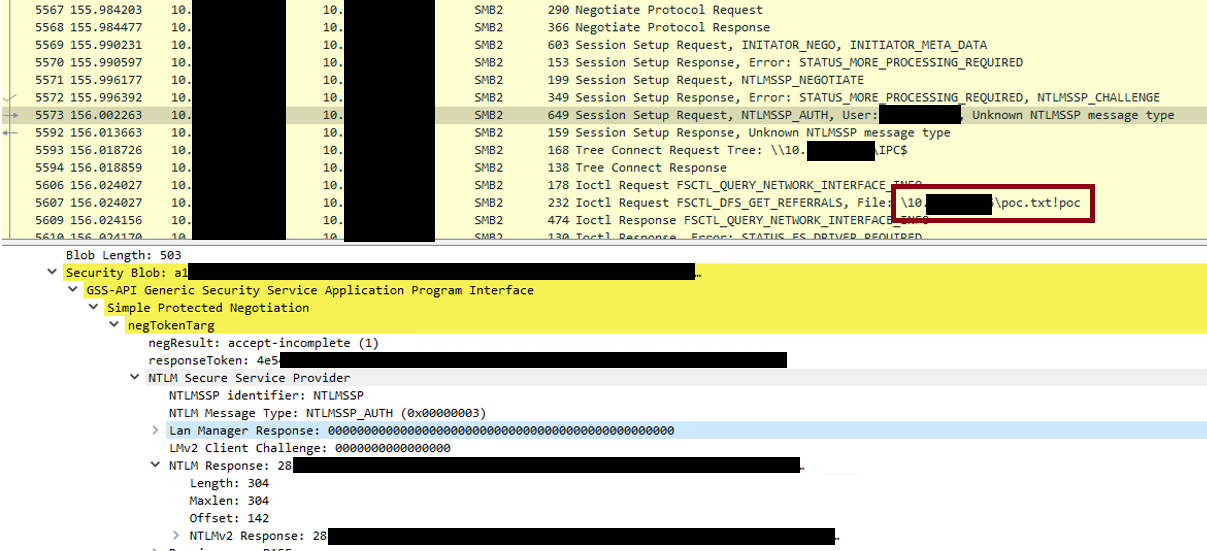 xaitax/cve-2024-21413-microsoft-outlook-remote-code-execution-vulnerability
Microsoft-Outlook-Remote-Code-Execution-Vulnerability
 yfelipecruvinel/tryhackme-moniker-link
Documentation of my hands-on lab Moniker Link (CVE-2024-21413) completed on TryHackMe.
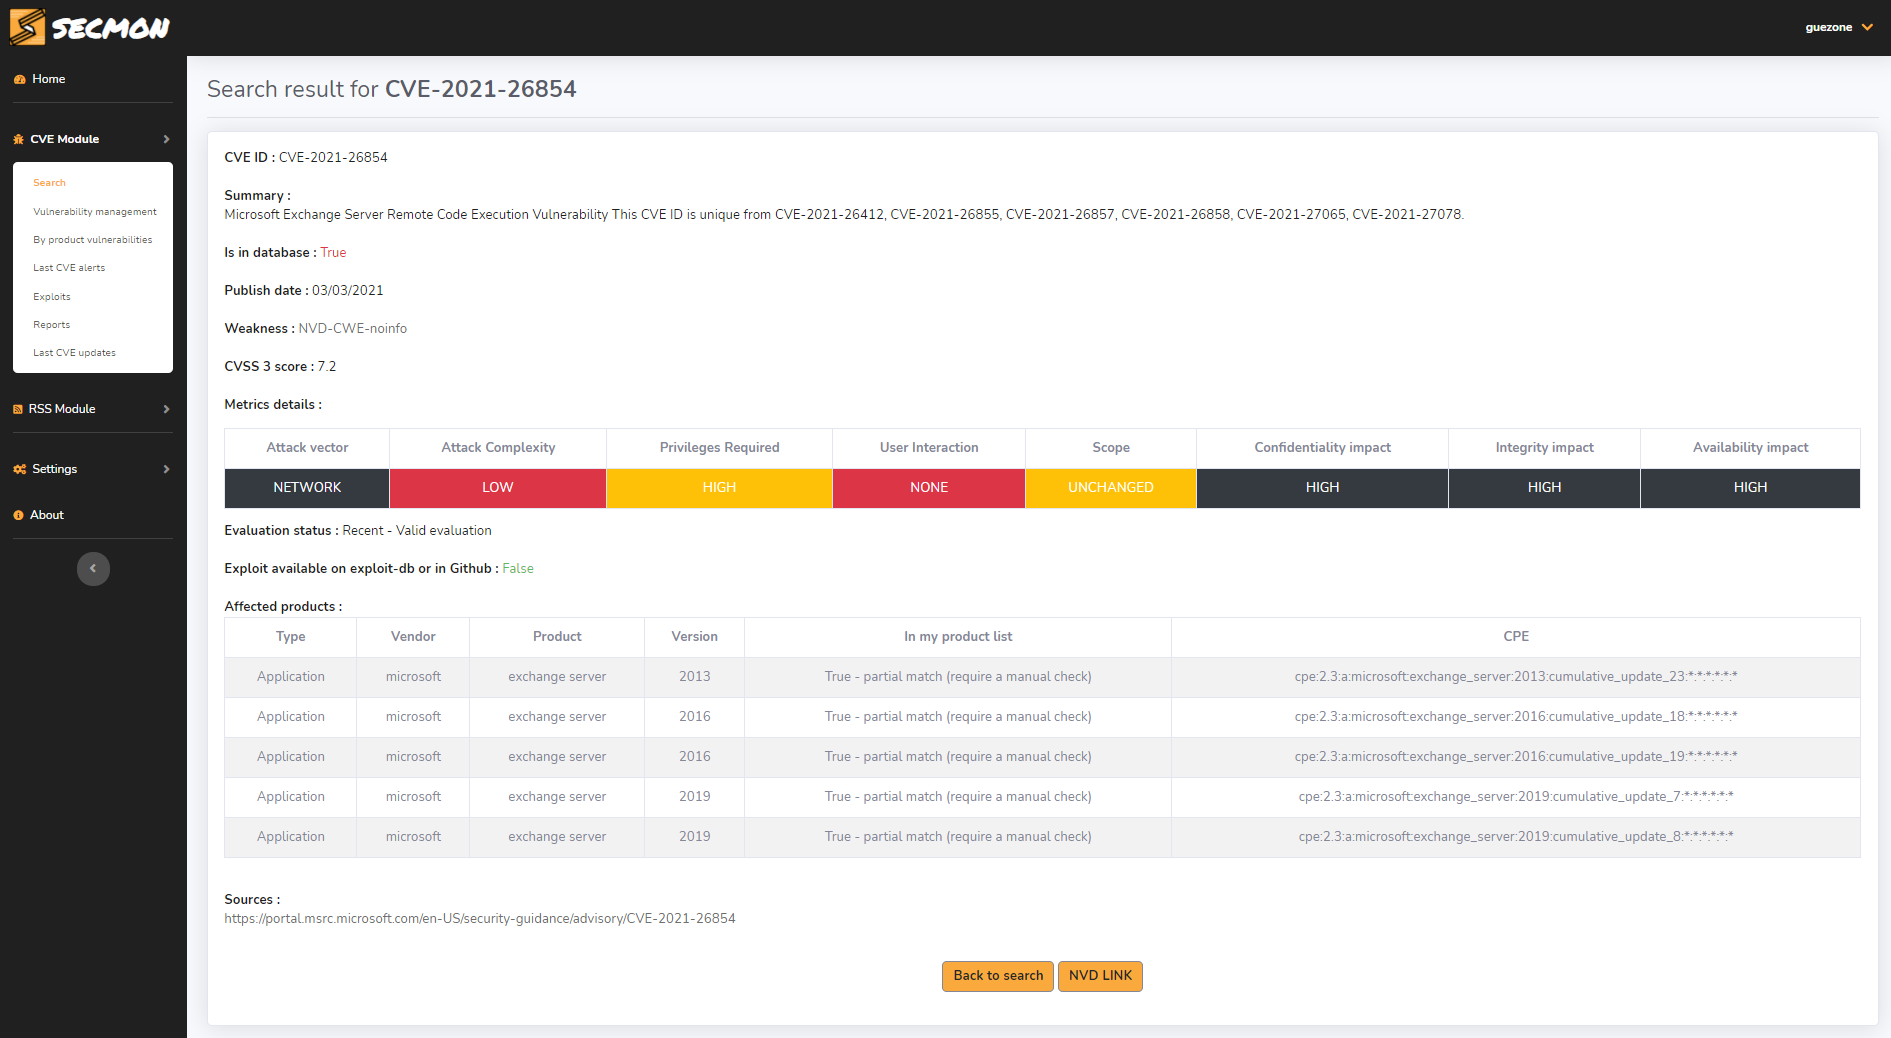 alb-uss/secmon
SECMON is a web-based tool for the automation of infosec watching and vulnerability management with a web interface.
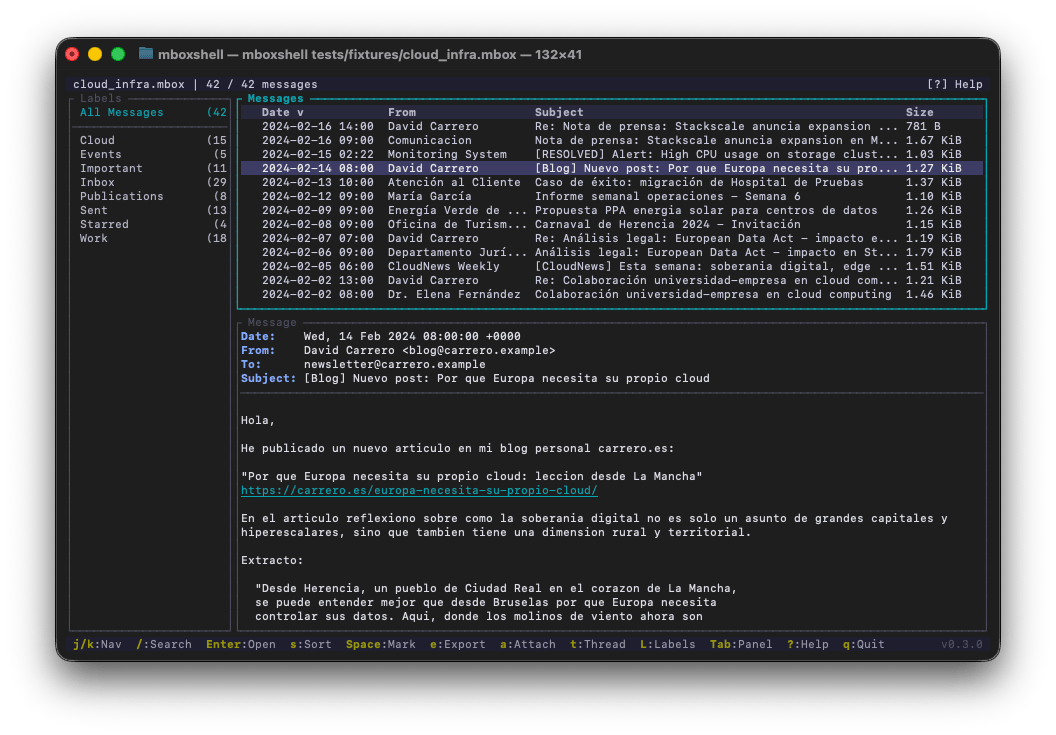 dcarrero/mboxshell
mboxShell. Fast terminal viewer for MBOX files of any size. Open, search and export emails from Gmail Takeout backups (50GB+) without loading them…
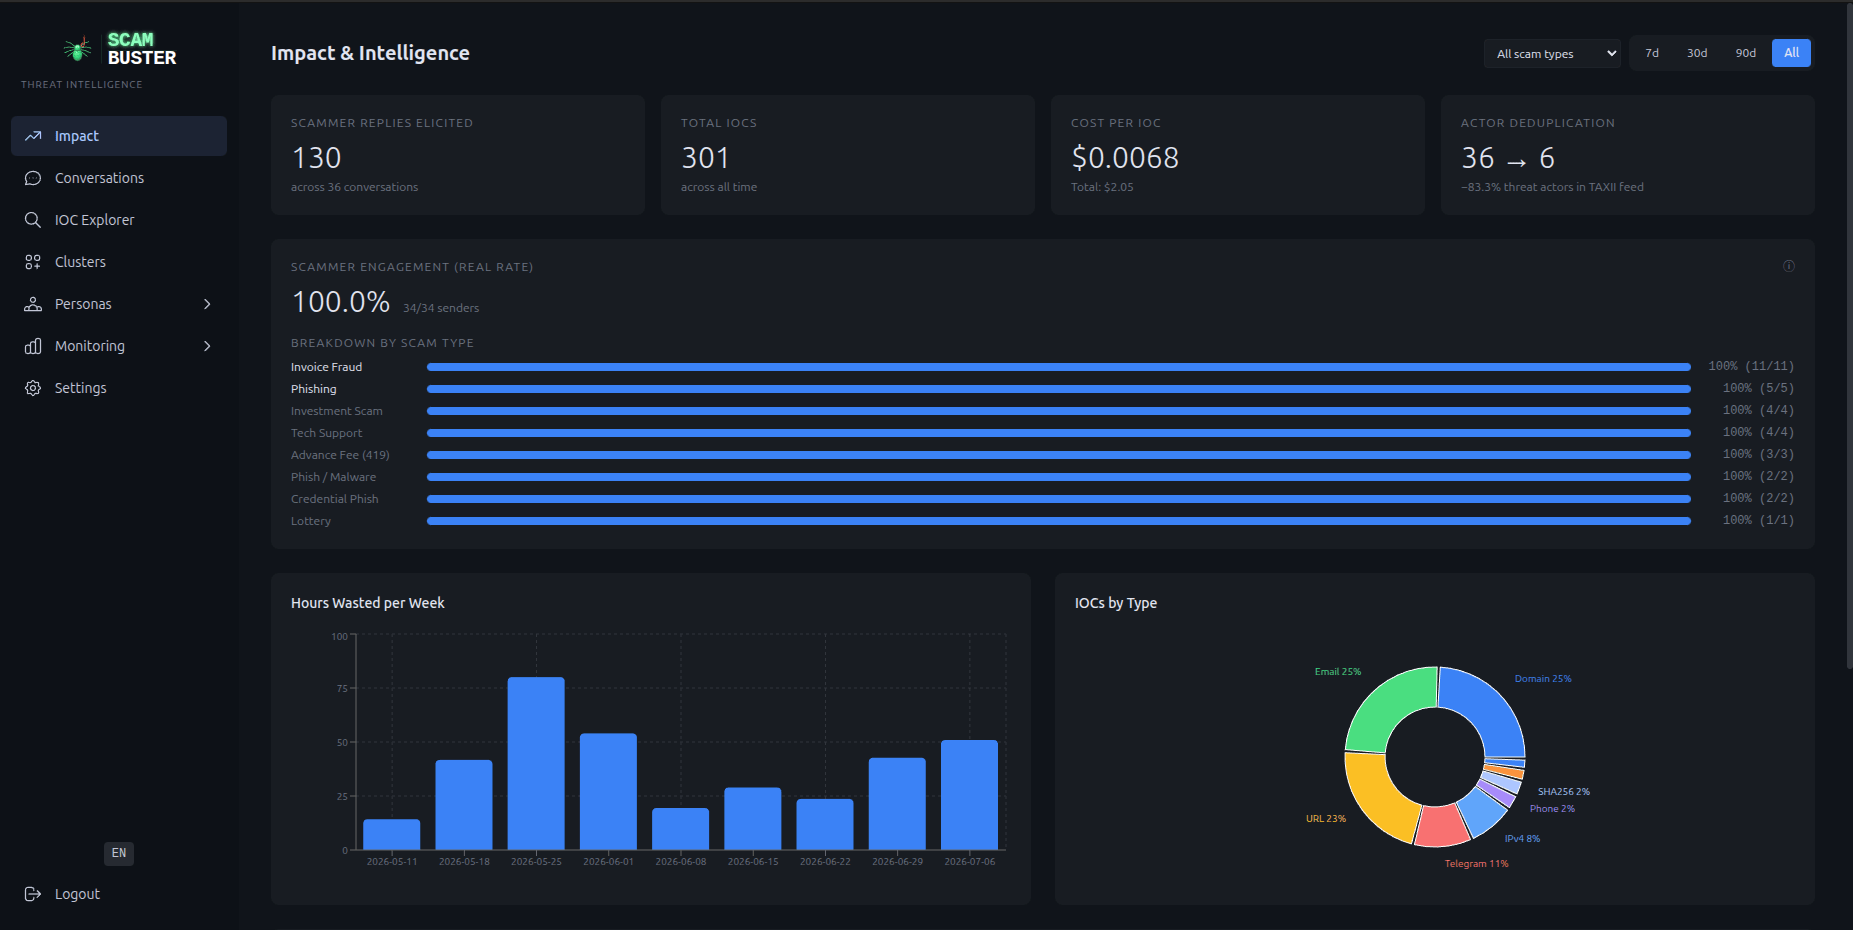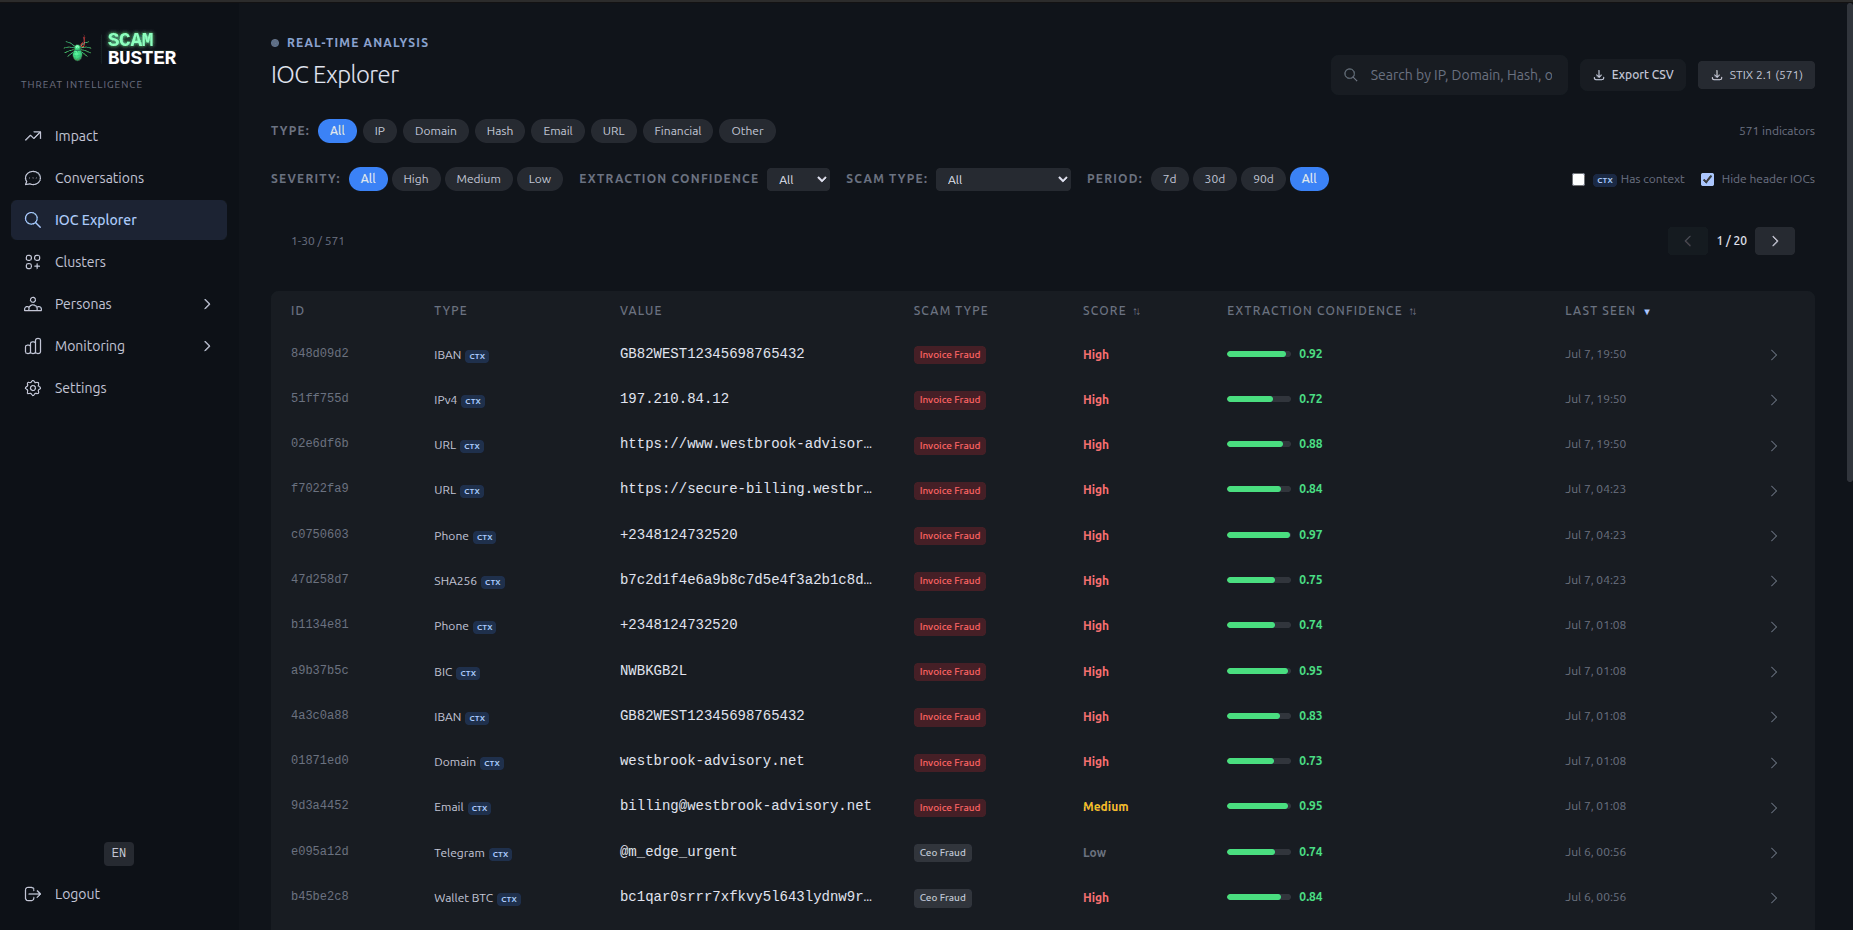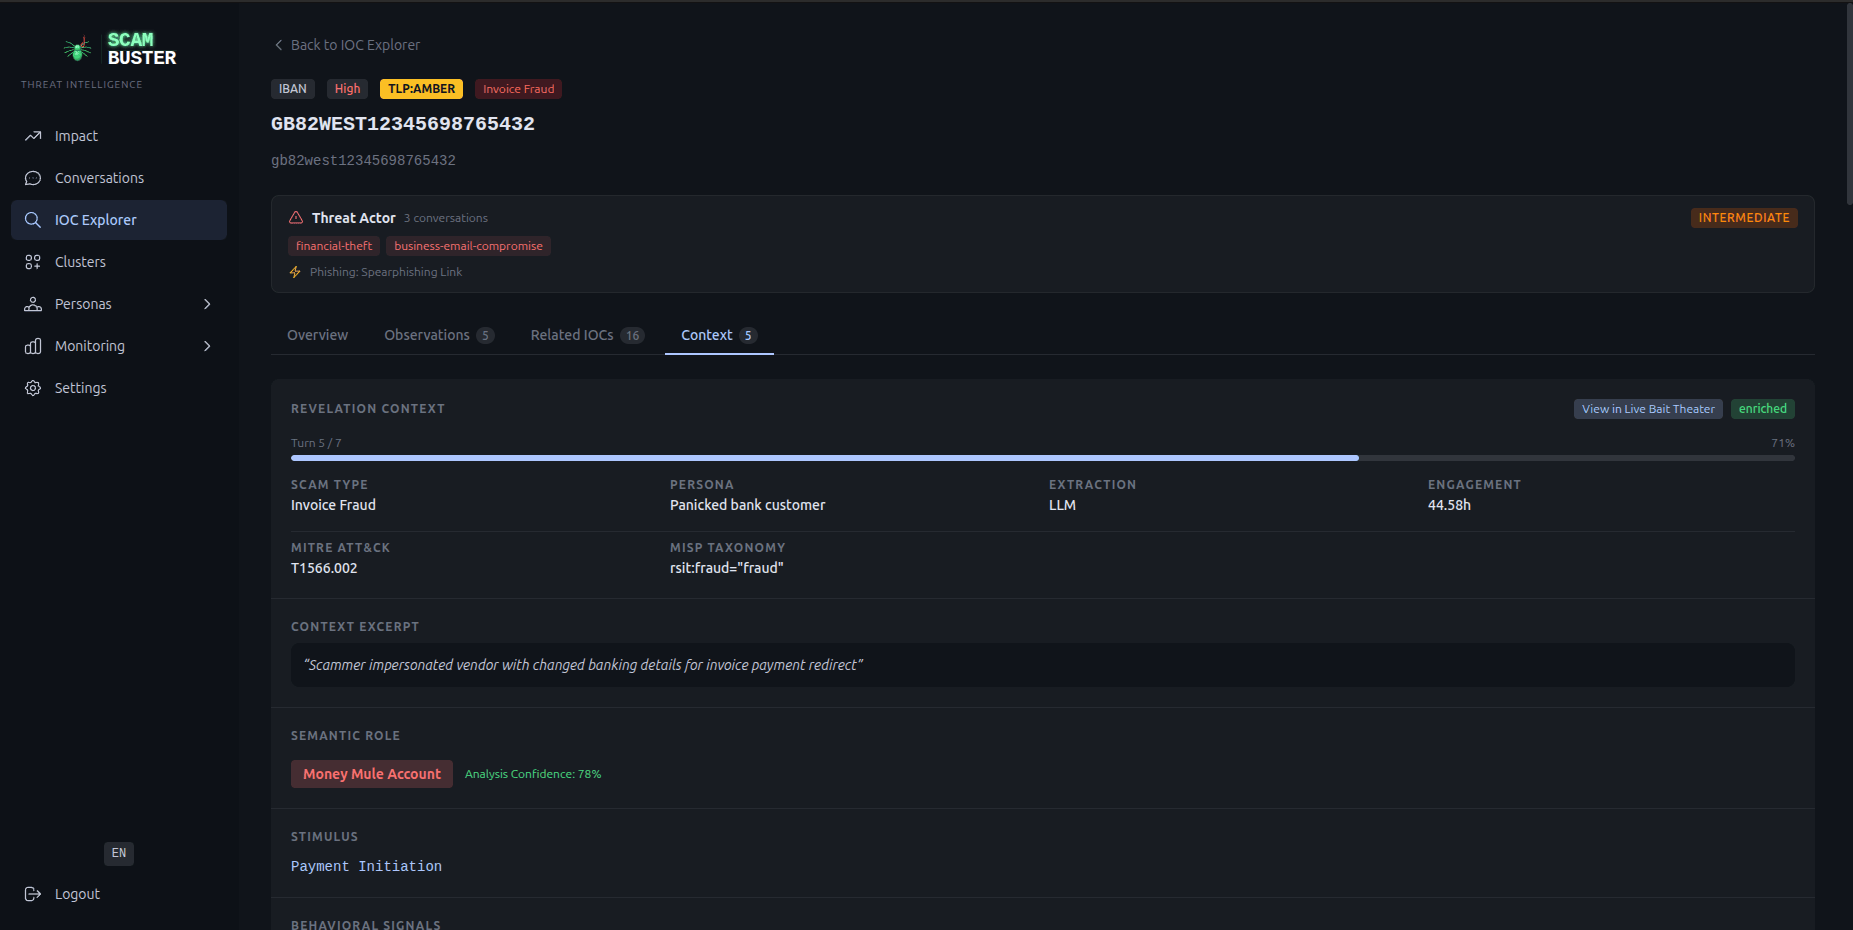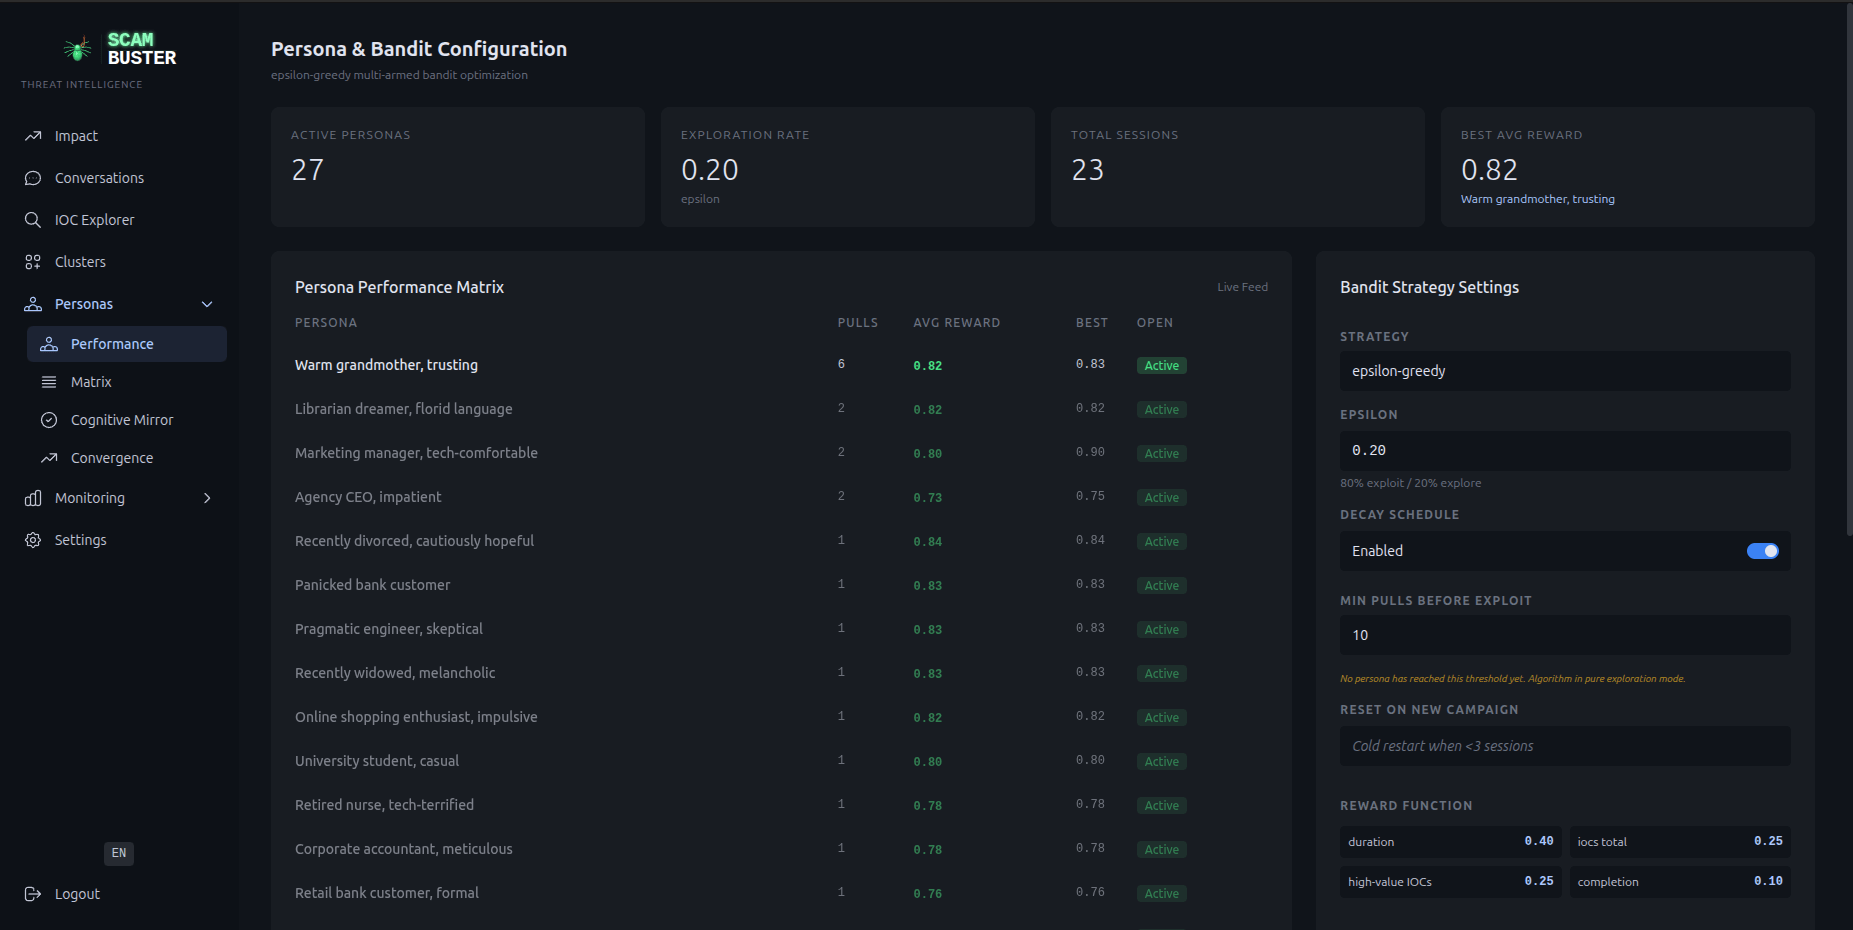 laugiov/scambuster
Defensive engagement & threat intelligence research laboratory. Converts inbound scam emails into actionable IOCs through controlled, policy-driven…

 mail-in-a-box/mailinabox
Mail-in-a-Box helps individuals take back control of their email by defining a one-click, easy-to-deploy SMTP+everything else server: a mail server…
 hevnsnt/cvengine
AI-first external attack surface assessment with continuous discovery, evidence-based vulnerability validation, and developer-agent MCP integration.
 aramosf/cve-2026-24031
Self-contained Python PoC for Dovecot SQL authentication bypass: logs in as any user without the real password and enumerates usernames on vulnerable…