
SOC-Investigation-CVE-2024-49138
 basitsajidsoc/soc-investigation-cve-2024-49138
Investigation and Incident Response report for LetsDefend Alert SOC335 (CVE-2024-49138 Exploitation)
defensive-toolsdigital-forensicseducation+5
basitsajidsoc/soc-investigation-cve-2024-49138Investigation and Incident Response report for LetsDefend Alert SOC335 (CVE-2024-49138 Exploitation)
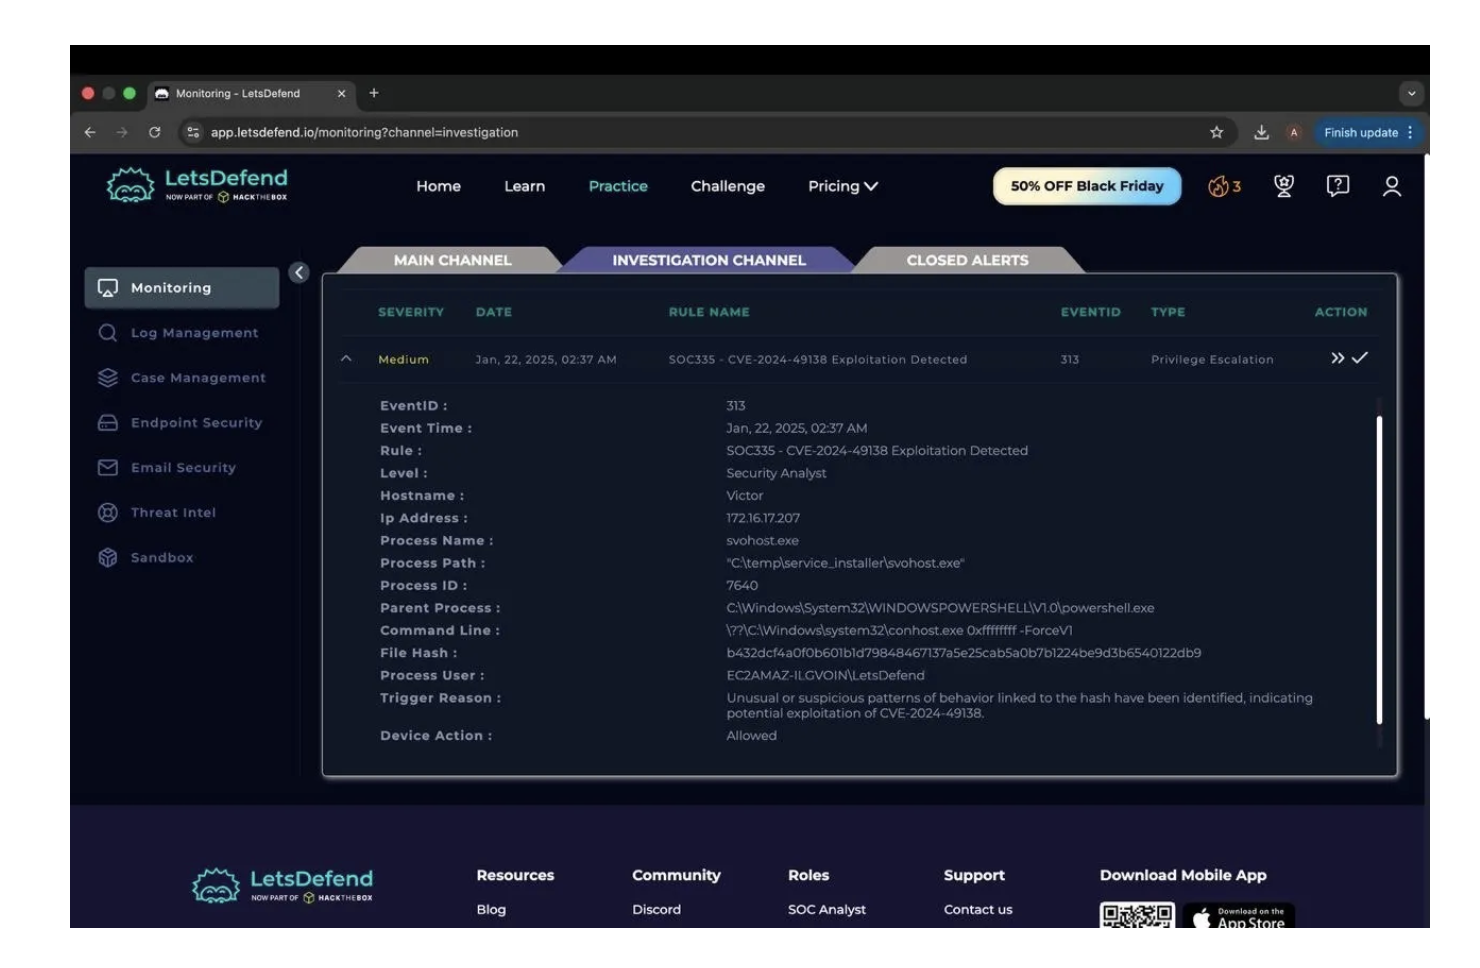 adisasoc/cve-2024-49138-soc-investigation
SOC investigation of CVE-2024-49138 exploitation involving brute-force activity, PowerShell execution, malicious payload analysis, privilege…
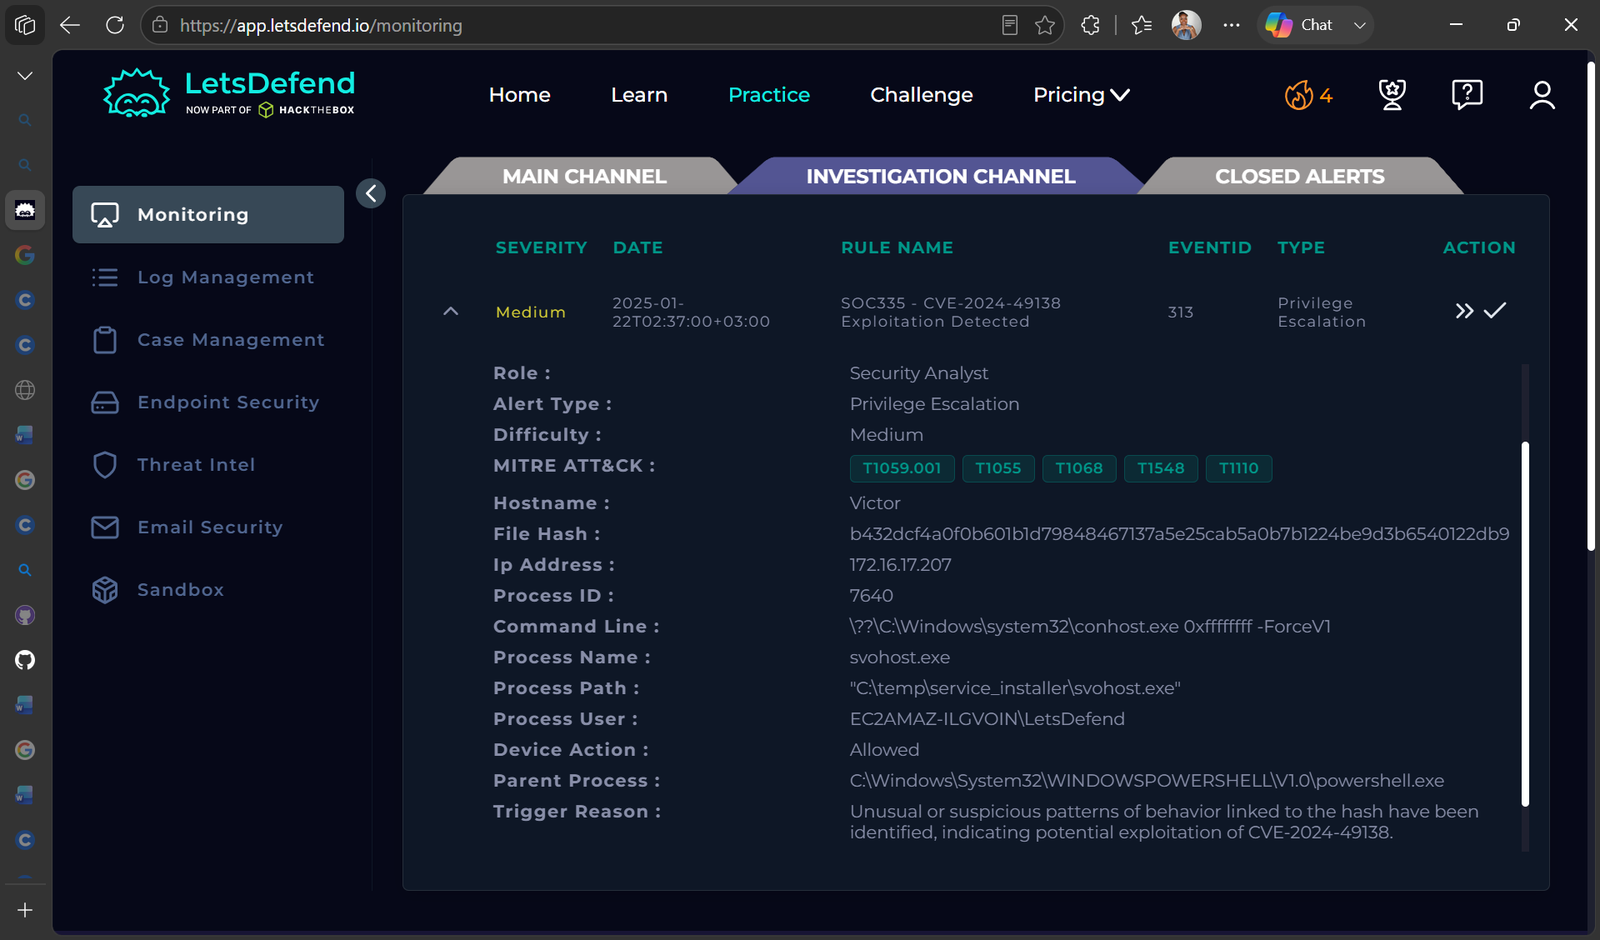 nadineelliottcyber/soc335-cve-2024-49138-investigation
SOC investigation of a CVE-2024-49138 exploitation alert using log analysis, threat intelligence, and endpoint containment.
 ledlight33/copyfail-dfir
Interactive DFIR walkthrough of CVE-2026-31431 (Copy Fail) - from SIEM alert to confirmed verdict. Real Volatility 3 commands, verified methodology.
 0x0allenace/windows-malware-behavioral-analysis
Behavioral Malware Analysis of a Simulated Multi-Stage Windows Malware Sample using FLARE-VM and REMnux. Evidence-driven DFIR investigation with IOC…
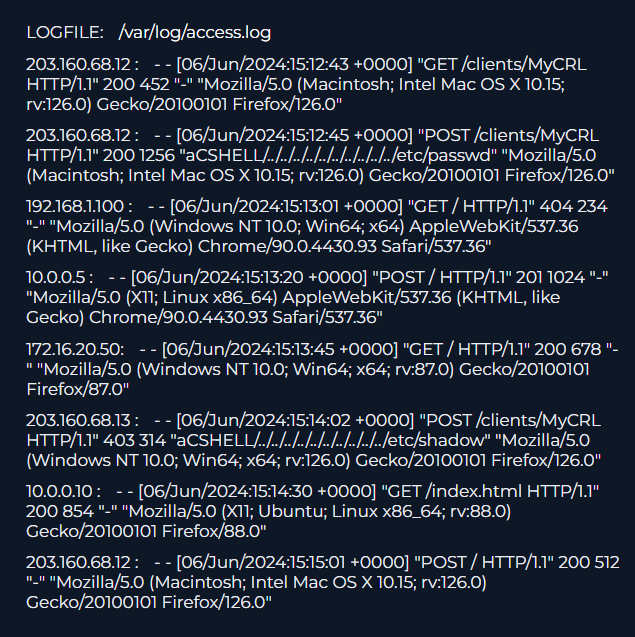 zedocun/incident-analysis-response-check-point-security-gateway-cve-2024-24919-lfi-exploitation
Incident Response (IR) case study documenting the investigation of an exploitation attempt targeting CVE-2024-24919 (Arbitrary File Read) on a Check…
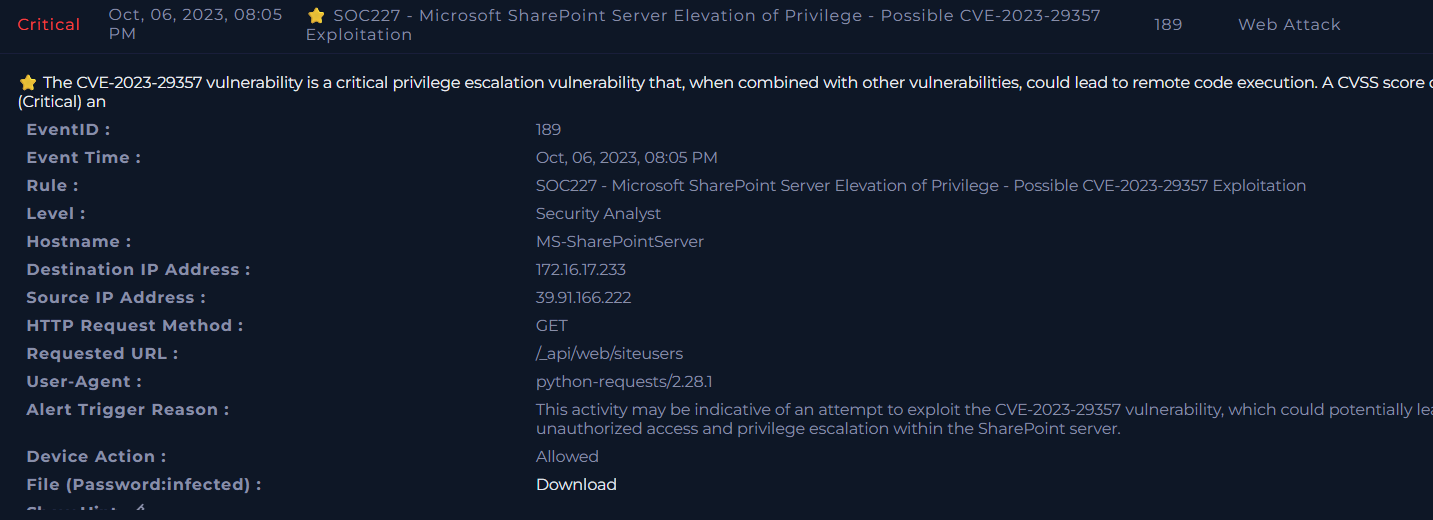 zedocun/sharepoint-cve-2023-29375-incident-response
End-to-end SOC incident analysis and threat hunting playbook targeting Microsoft SharePoint privilege escalation (CVE-2023-29357) using SIEM logs,…
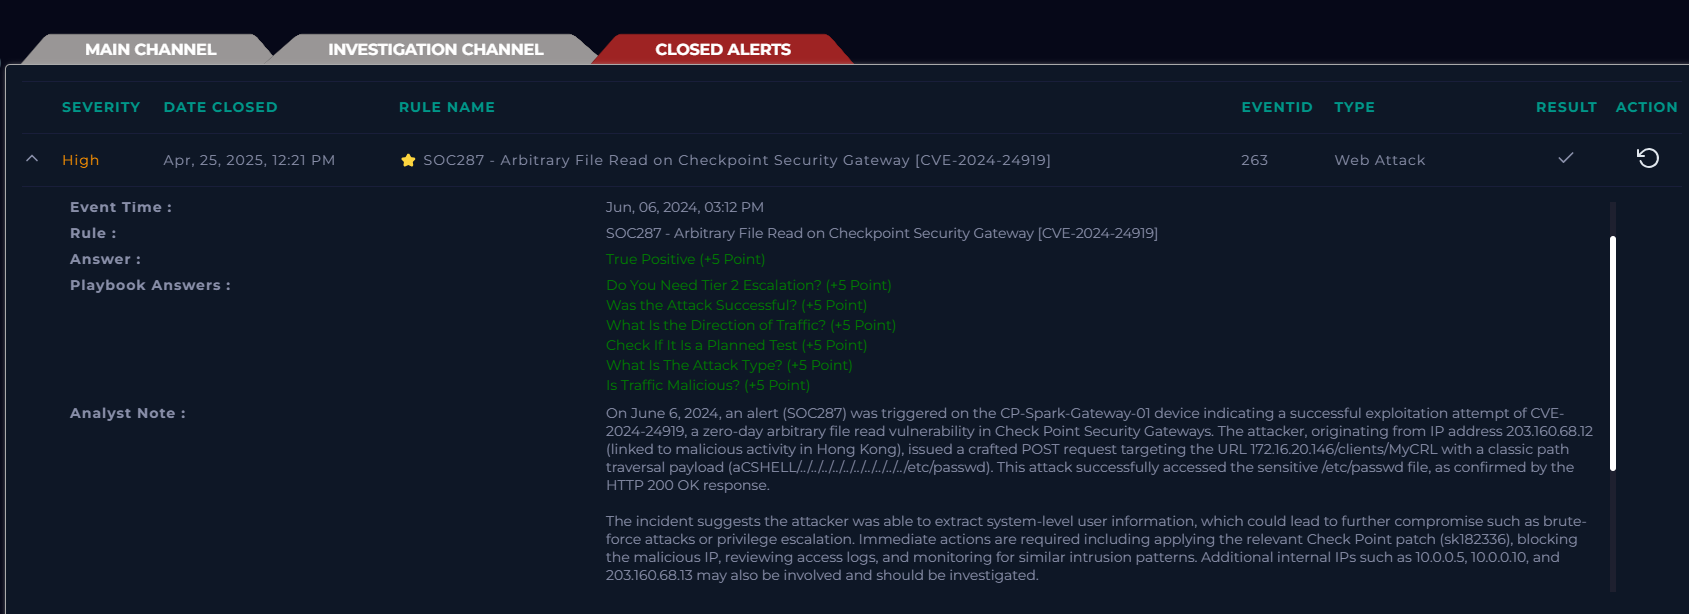 cyprianatsyor/cve-2024-24919-incident-report.md
Detailed incident report analyzing CVE-2024-24919 arbitrary file read exploit on Check Point Security Gateway, including technical analysis, response…
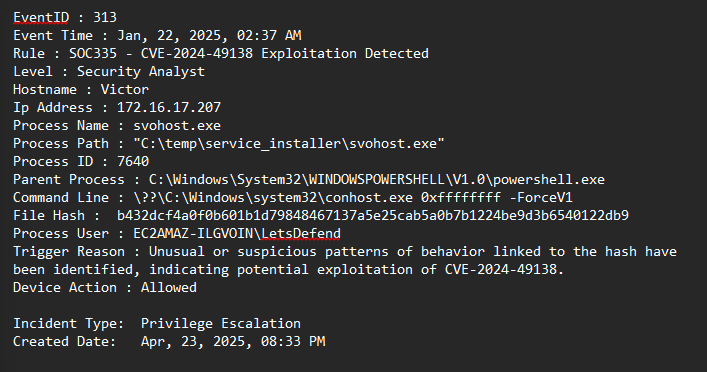 cyprianatsyor/letsdefend-cve-2024-49138-investigation
Hands-on SOC investigation of CVE-2024-49138 using LetsDefend, VirusTotal, Hybrid Analysis, TrueFort, and ChatGPT.
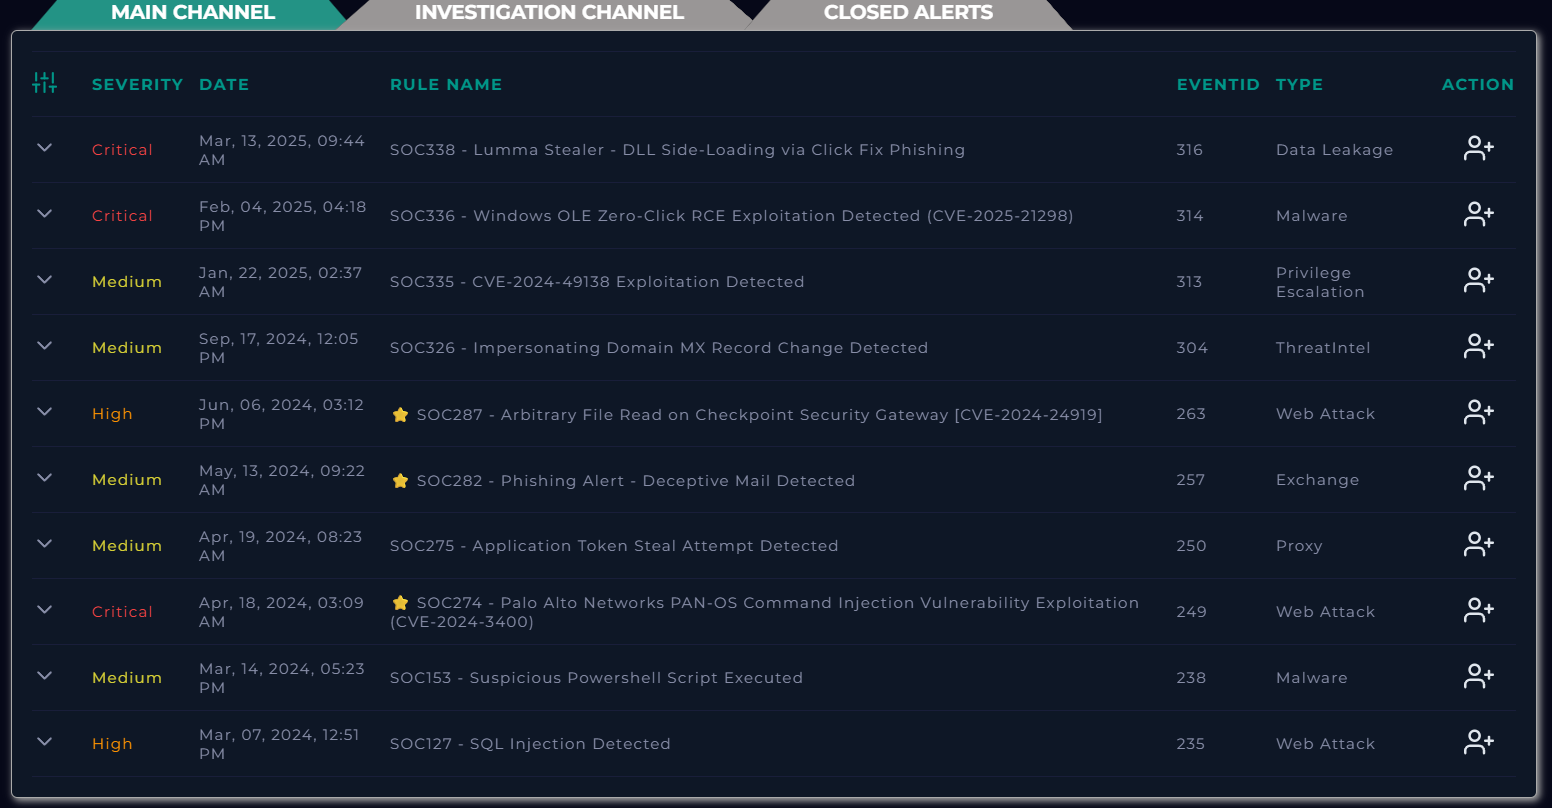 tarunbharathe/zero-click-rce-incident-response-cve-2025-21298
Technical investigation and host containment of a Critical-severity Zero-Click RCE exploit (CVE-2025-21298) using EDR telemetry and static malware…
 jhatchi/nexacorp-dfir-inc-2026-001
DFIR investigation + 7 Suricata rules on a simulated NexaCorp intrusion (vsftpd 2.3.4 CVE-2011-2523 + MITRE Caldera C2). 4-day solo engagement…
 justjeff211/conti-ransomware-writeup
Conducted a full SOC investigation into a Conti ransomware compromise of an Exchange server using Splunk 8.2.2. Analysed 28,145 events across Windows…
 zedocun/soc-investigation-powershell-edrfreeze
SOC investigation of CVE-2024-49138 exploitation alert involving PowerShell, EDRFreeze execution, and defense evasion behavior in a simulated…
 zedocun/sharepoint-toolshell-cve-2025-53770-incident-analysis
Technical analysis of a SharePoint ToolShell (CVE-2025-53770) exploitation attempt involving RCE, webshell deployment, and MachineKey extraction.
 czabatta/thm-tempest
TryHackMe SOC Level 1 — Follina CVE-2022-30190, Nim C2, Chisel, PrintSpoofer, backdoor accounts
 frankwxu/digital-forensics-lab
Free hands-on digital forensics labs for students and faculty