
recaptcha
 elyelysiox/recaptcha
Documentation and reverse engineering of reCAPTCHA
anti-botcaptcha-bypassdynamic-code-analysis+3
262
elyelysiox/recaptchaDocumentation and reverse engineering of reCAPTCHA
 dynamorio/dynamorio
Runtime instrumentation framework for building dynamic analysis tools: tracing, profiling, code coverage, memory debugging, fuzzing, and disassembly…
 0xdea/frida-scripts
A collection of my Frida instrumentation scripts to reverse engineer mobile apps and more.
 frkngksl/exporthider
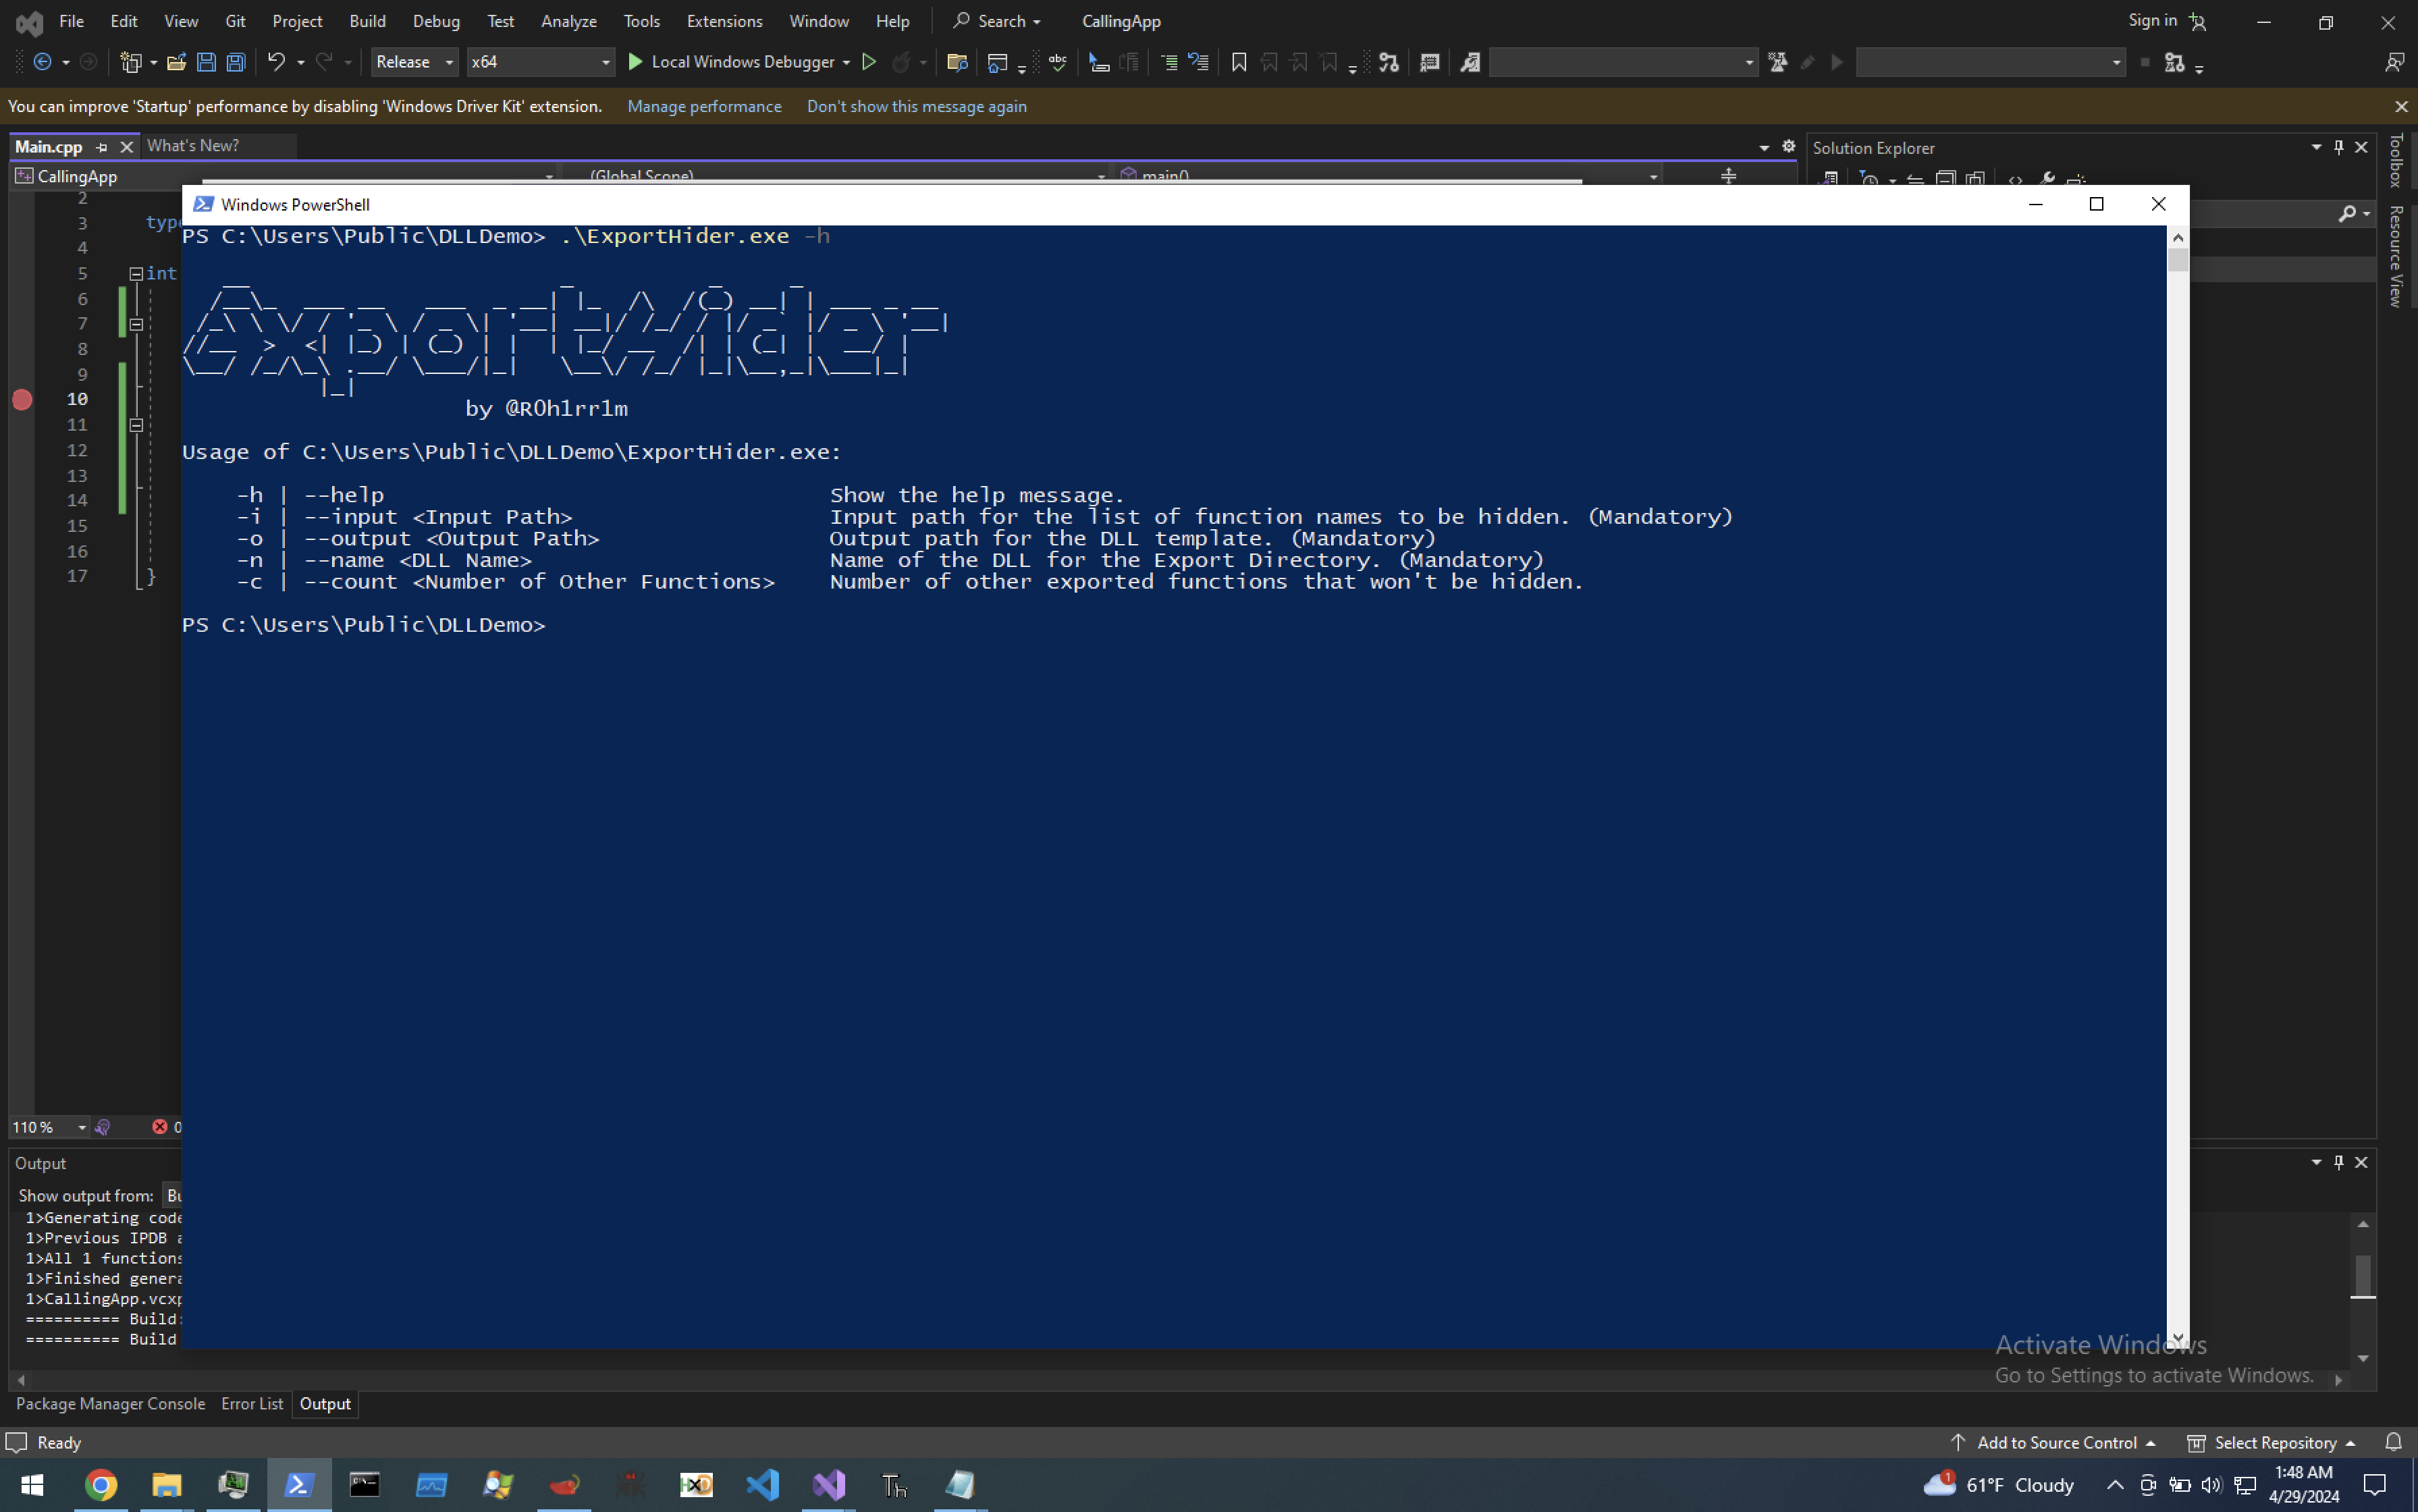
ExportHider: Generating Export Table during Runtime to Hide the Exported Functions from the DLL File.
 tanprathan/mobileapp-pentest-cheatsheet
The Mobile App Pentest cheat sheet was created to provide concise collection of high value information on specific mobile application penetration…
 mandiant/strace
A DTrace on Windows Reimplementation
 dere-ad2001/frida-labs
The repo contains a series of challenges for learning Frida for Android Exploitation.
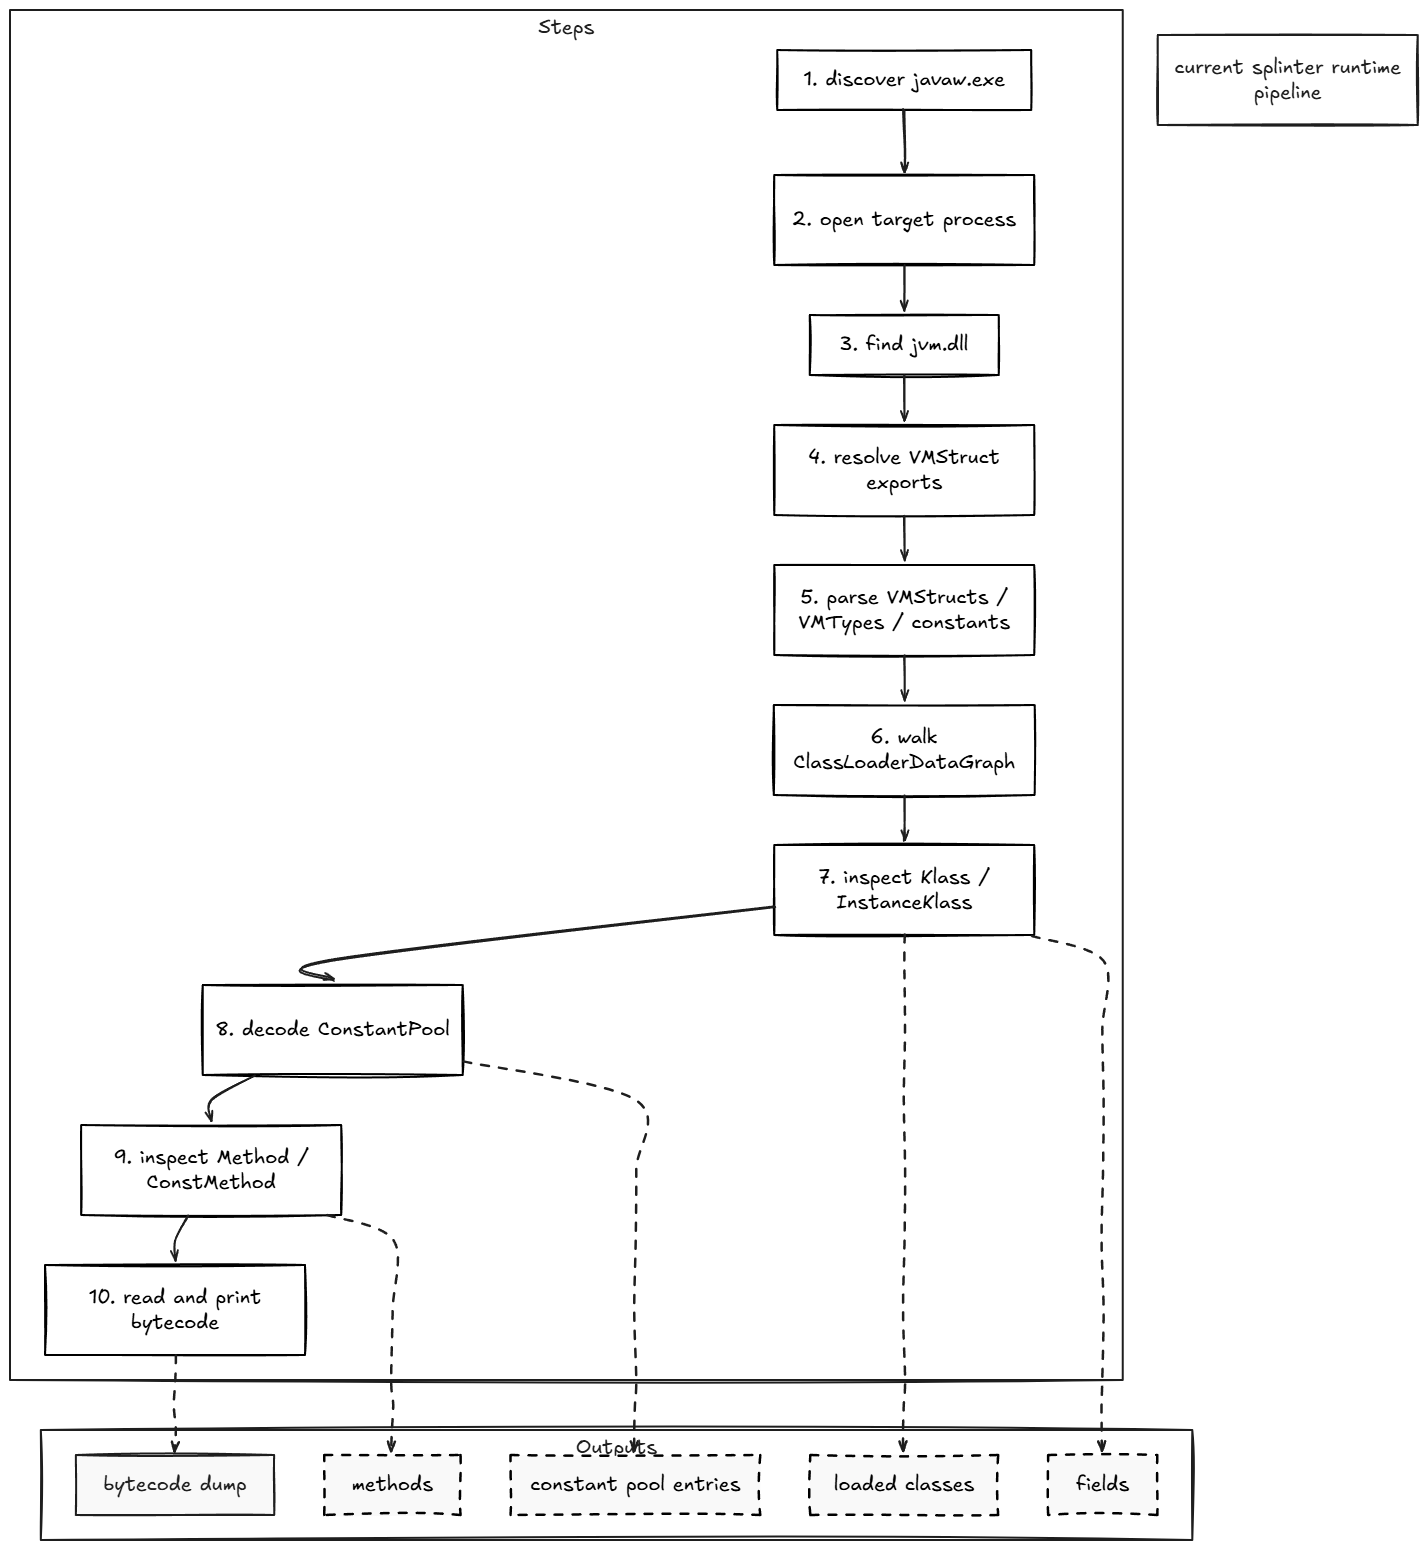 awrped/splinter
Runtime JVM analysis toolkit for inspecting classes, methods, fields, constant pool, and bytecode
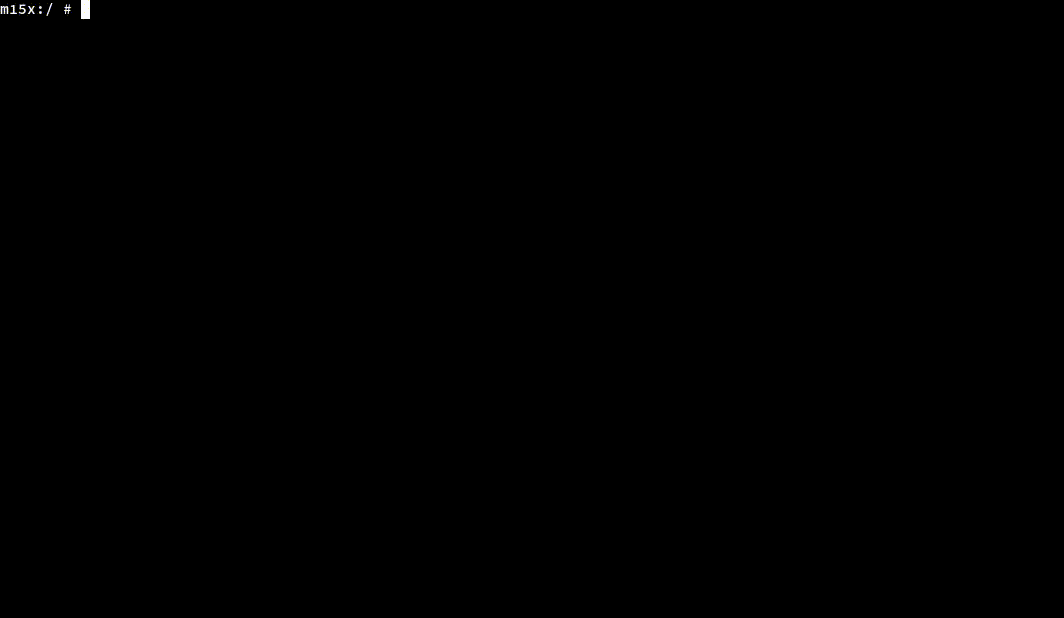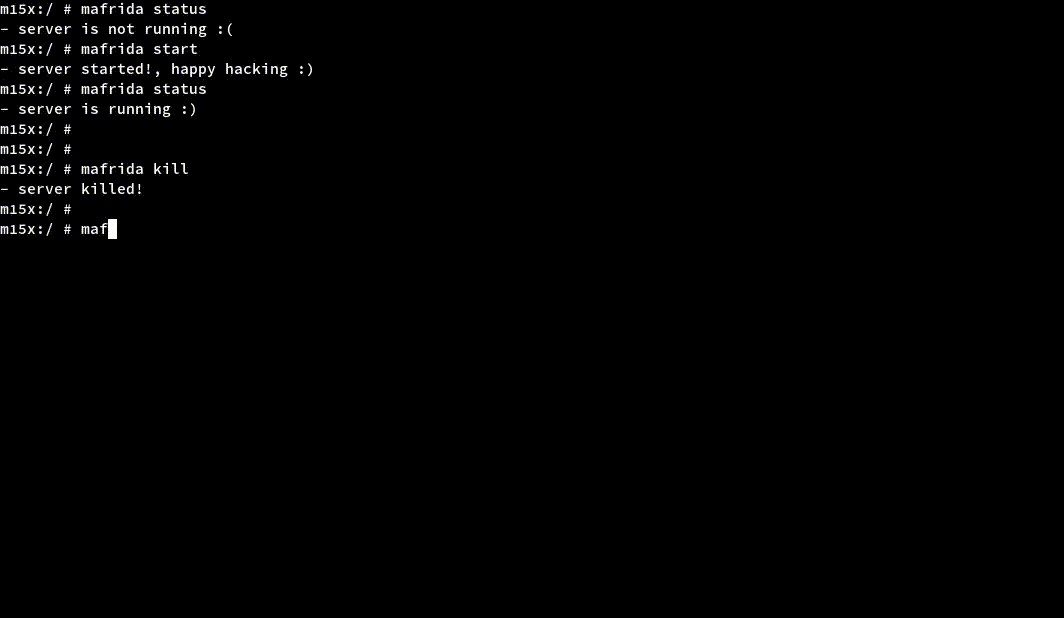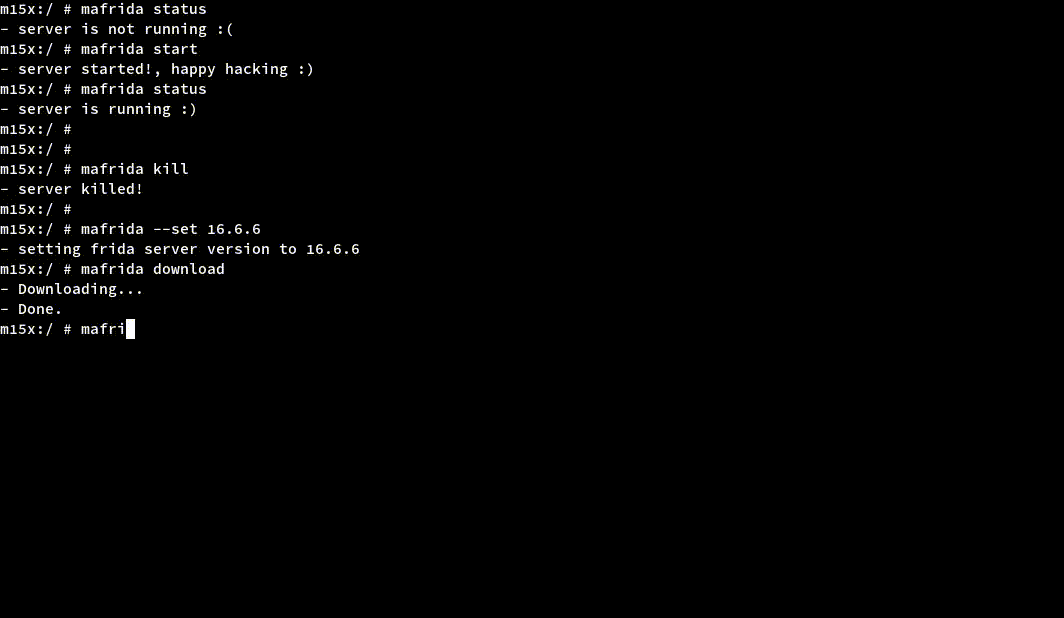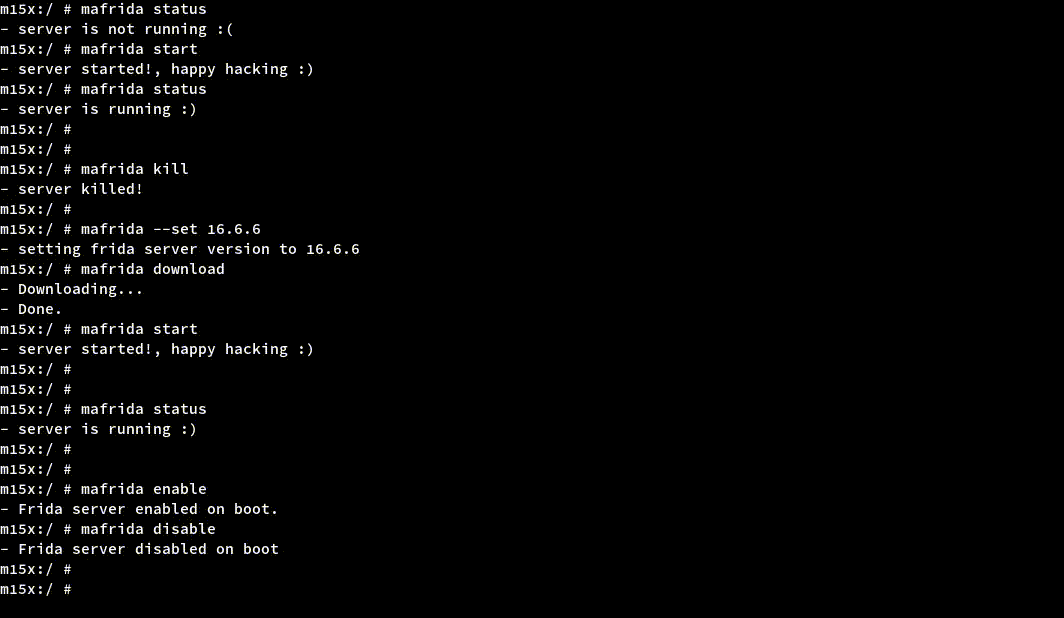 theshinigami/mafrida
A Magisk module that simplifies running the Frida server on Android, with easy management commands to download specific versions, enable or disable…
 chichou/vscode-frida
Unofficial frida extension for VSCode
 google/honggfuzz
Security oriented software fuzzer. Supports evolutionary, feedback-driven fuzzing based on code coverage (SW and HW based)
 shoucheng3/x-stream__xstream_cve-2021-21345_1-4-15
Java XML serialization library with a focus on CVE-2021-21345 exploit analysis and deserialization vulnerability testing for web applications.
 microsoft/detours
Runtime Windows API interception library for hooking, monitoring, and instrumenting function calls. Supports binary rewriting and DLL injection,…
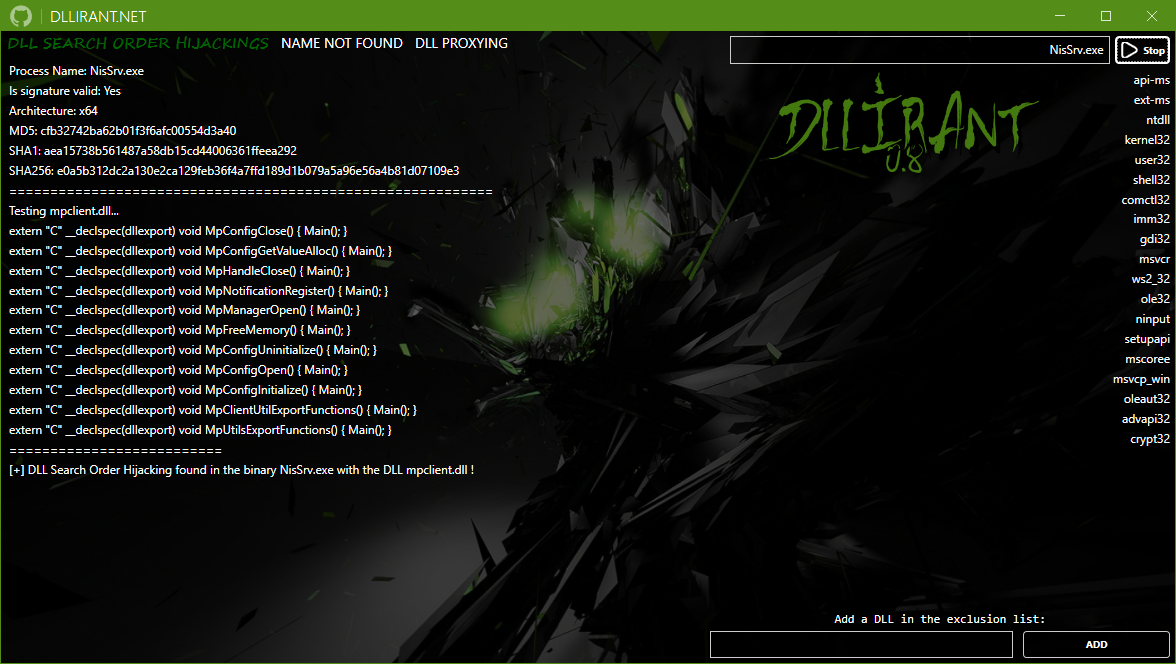 redteamsocietegenerale/dllirant
DLLirant is a tool to automatize the DLL Hijacking researches on a specified binary.
 steven-michaud/hookcase
Tool for reverse engineering macOS/OS X
 zaproxy/zaproxy
Open-source web application security scanner for automated vulnerability detection, manual penetration testing, and API security testing with a…
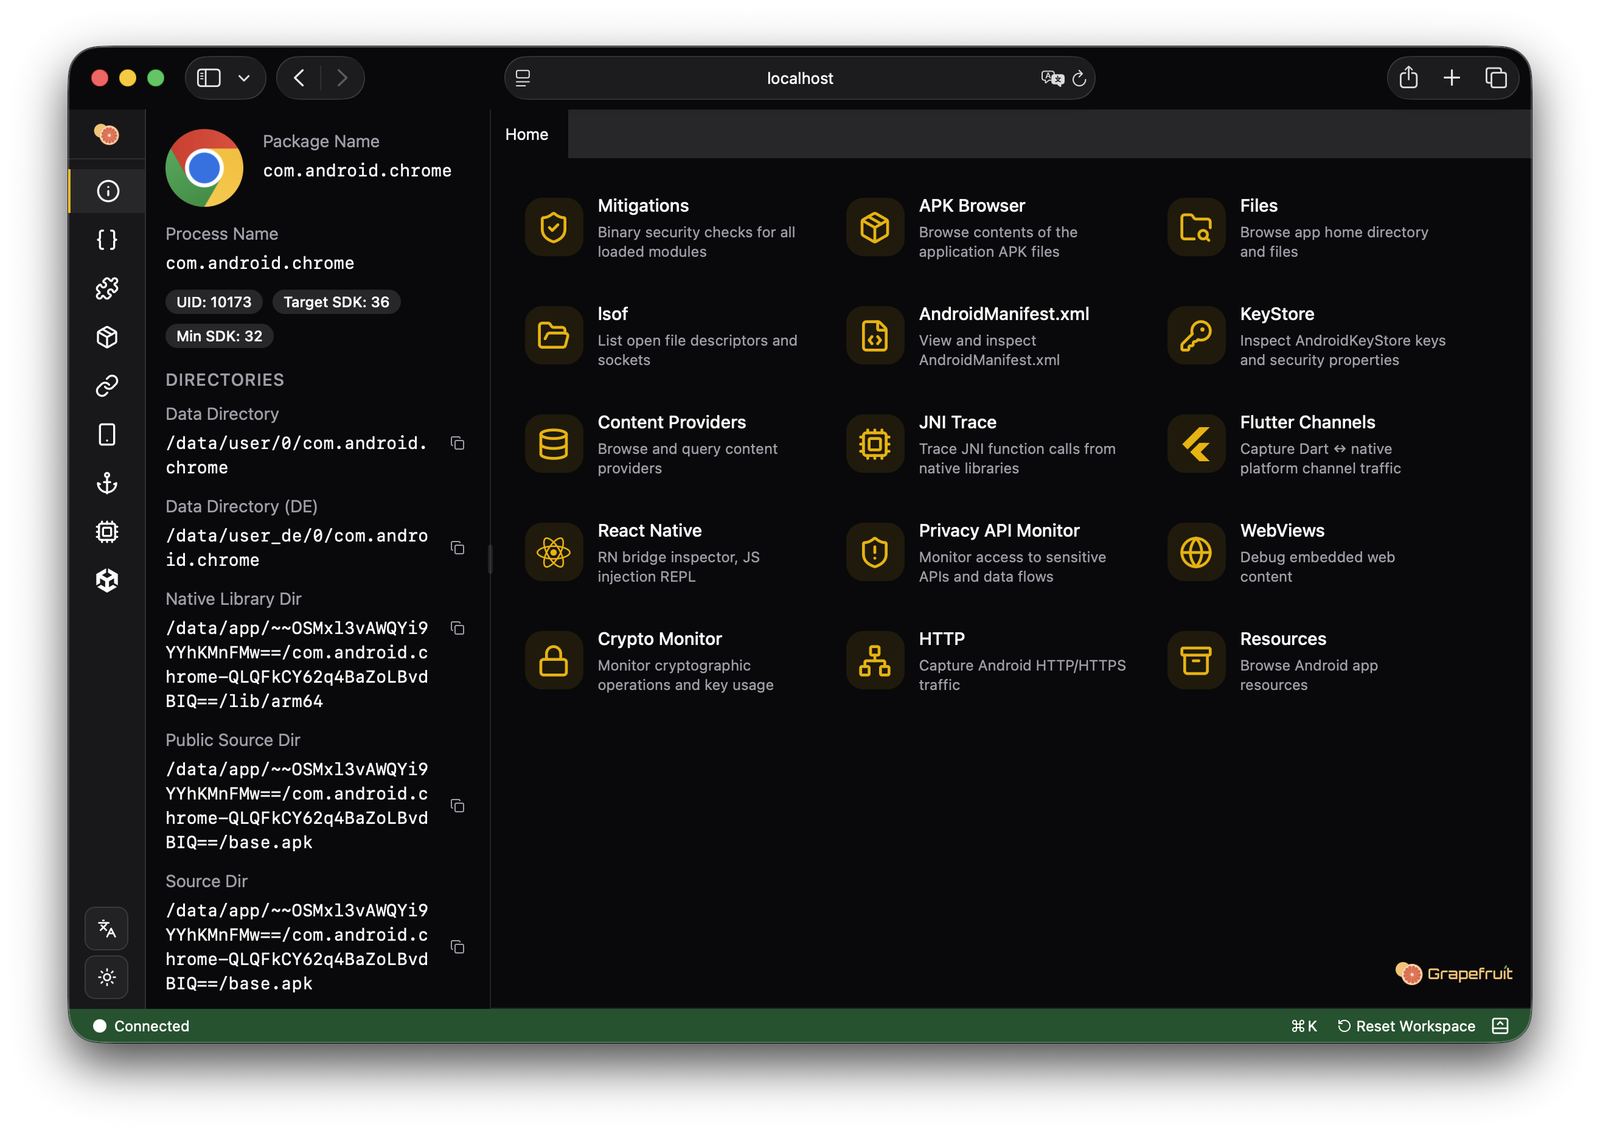 chichou/grapefruit
Open-source mobile security testing suite for iOS and Android. Previously Passionfruit