

hermit
 xv4l3x/hermit
Inspects, decompiles and structurally patches Hermes bytecode (HBC) from React Native apps, with a GDB-style REPL, CFG, decompiler and re-serializing…
android-securitybinary-analysiscode-analysis+7
6
xv4l3x/hermitInspects, decompiles and structurally patches Hermes bytecode (HBC) from React Native apps, with a GDB-style REPL, CFG, decompiler and re-serializing…
 anonmoty/xxstrike
XSStrike based XSS scanner with custom features. Detects XSS vulnerabilities in web applications.
 hunt-benito/one-multiply-too-many-cve-2026-70638-llama-cpp-android-jni-integer-overflow
Reproduces the CVE-2026-70638 integer overflow in llama.cpp Android JNI with a safe arithmetic demo, malicious GGUF generator, and Frida hook for…
 gmh5225/ida-claude-code-plugins
Plugins integrating Claude Code with IDA Pro to assist reverse engineering and binary analysis workflows through AI-driven disassembly and code…
 shoucheng3/x-stream__xstream_cve-2021-21345_1-4-15
Java XML serialization library with a focus on CVE-2021-21345 exploit analysis and deserialization vulnerability testing for web applications.
 aftermathlabs/vmp2
Unpack and deobfuscate VMProtect 2 protected binaries with an emulation-based VM explorer, handler profiler, and experimental LLVM recompiler for…
 trailofbits/umberto
Library and CLI for mutating structured data (JSON, XML, X.509) to support grammar-based fuzzing, with multiple mutation strategies and integration…
 dwisiswant0/findom-xss
A fast DOM based XSS vulnerability scanner with simplicity.


 epi052/feroxbuster
A fast, simple, recursive content discovery tool written in Rust.
 tomnomnom/gf
A wrapper around grep, to help you grep for things
 narfindustries/http-garden
Differential testing framework for HTTP implementations
 google/oss-fuzz-gen
LLM powered fuzzing via OSS-Fuzz.
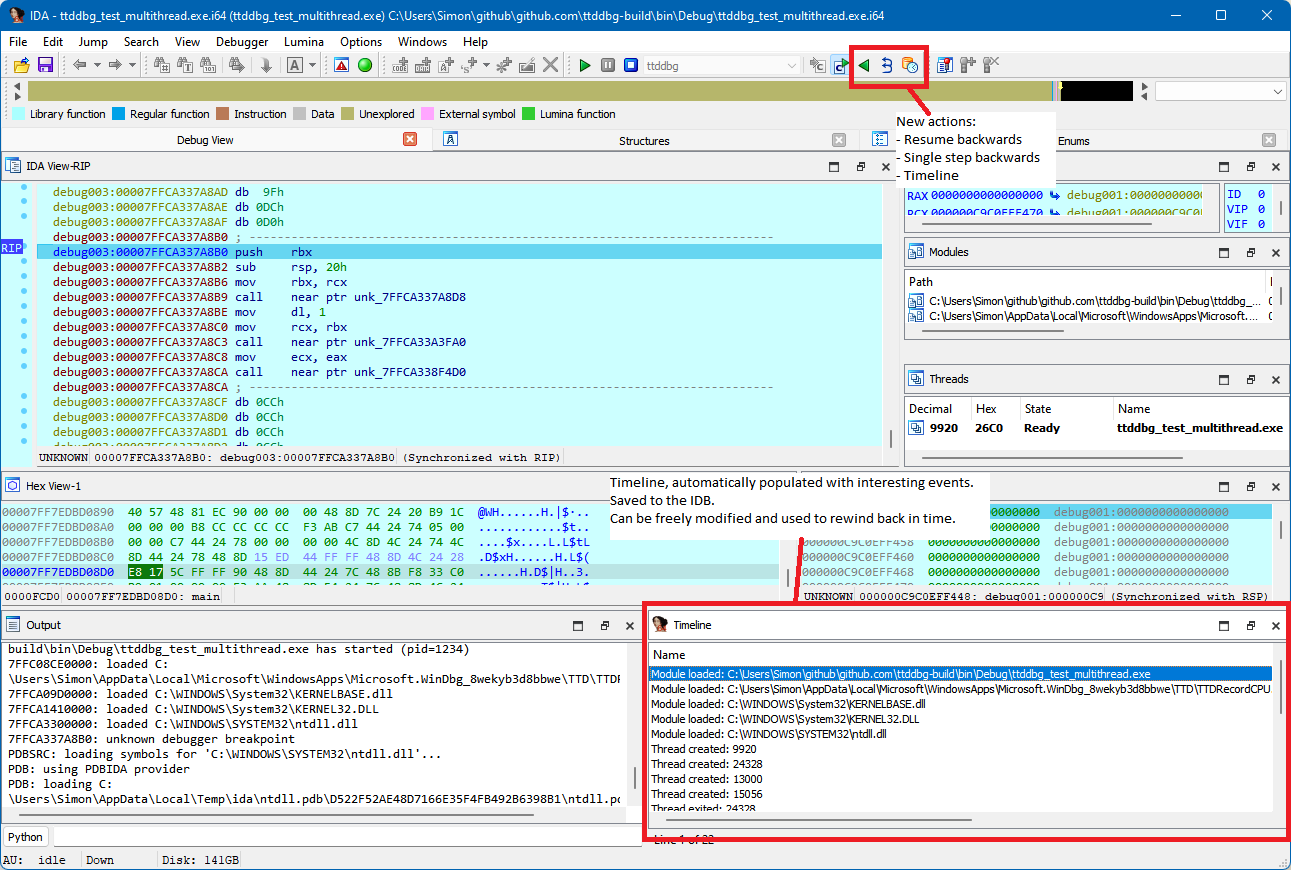 airbus-cert/ttddbg
Time Travel Debugging IDA plugin
 lifting-bits/sleigh
CMake build of Ghidra's SLEIGH processor specification library, providing standalone disassembly and p-code lifting engines for reverse engineering…
 atomdrift-project/scan
0-day malware detection for binaries, source & scripts (that doesn't suck)
 ch0pin/rdx
A native APK and DEX decompiler written in Rust