

dynamorio
 dynamorio/dynamorio
Runtime instrumentation framework for building dynamic analysis tools: tracing, profiling, code coverage, memory debugging, fuzzing, and disassembly…
binary-analysiscode-analysisdebuggers+3
3.2k
dynamorio/dynamorioRuntime instrumentation framework for building dynamic analysis tools: tracing, profiling, code coverage, memory debugging, fuzzing, and disassembly…
 giveen/decomp.anything
decomp.wtf fork: Windows PE matching, MinGW/clang-cl toolchains, and an optional REA MCP bridge
 0xdea/frida-scripts
A collection of my Frida instrumentation scripts to reverse engineer mobile apps and more.
 ejfkdev/ddc
Android DEX → Java decompiler in Rust, built for speed — full apps in seconds, queries in milliseconds. Progressive analysis, javac-verified output,…
 mg1937/asc
Fast Android APK decompiler front-end that queries compiled DEX artifacts directly, extracting classes and cross-references in milliseconds without…
 ch0pin/rdx
A native APK and DEX decompiler written in Rust
 zaproxy/zaproxy
Open-source web application security scanner for automated vulnerability detection, manual penetration testing, and API security testing with a…
 openbba0/bba
Android app-cloning sandbox with a Frida-style CLI that spawns or attaches to cloned apps and injects QuickJS scripts using Gum Interceptor and…
 xv4l3x/hermit
Inspects, decompiles and structurally patches Hermes bytecode (HBC) from React Native apps, with a GDB-style REPL, CFG, decompiler and re-serializing…
 chichou/grapefruit
Open-source mobile security testing suite for iOS and Android. Previously Passionfruit
 symbioticsec/hermes-decomp
A powerful decompiler that lets you reverse-engineer React Native mobile apps by converting their compiled Hermes bytecode (.hbc) files back into…
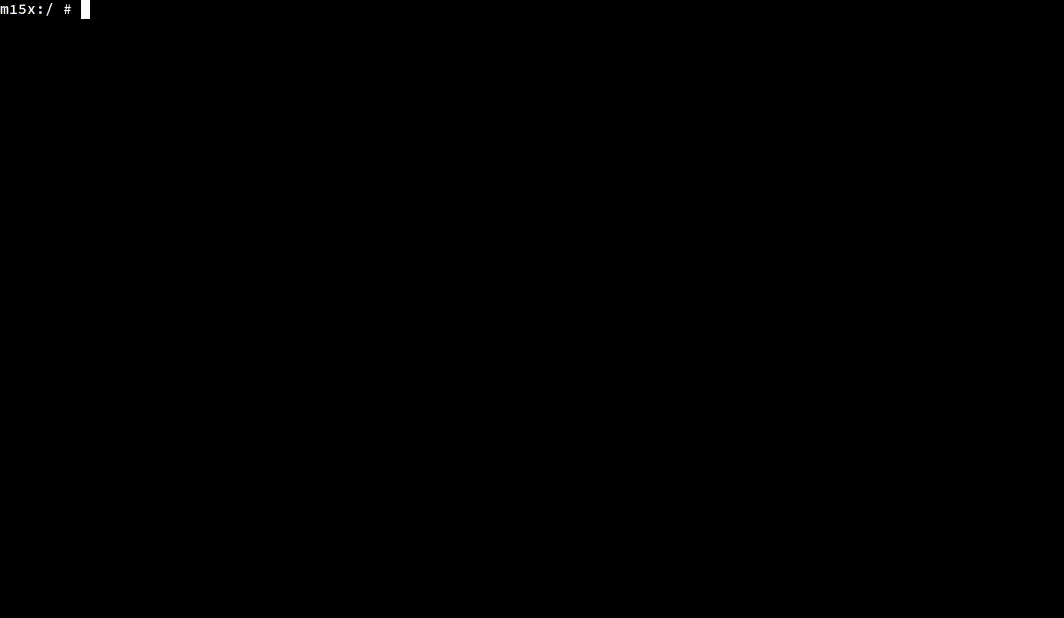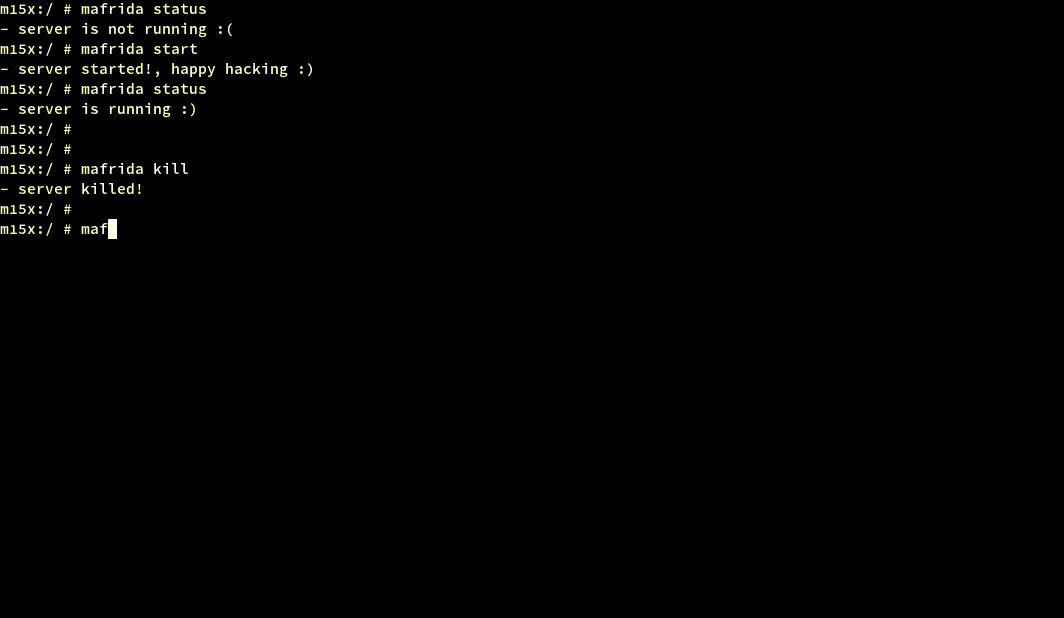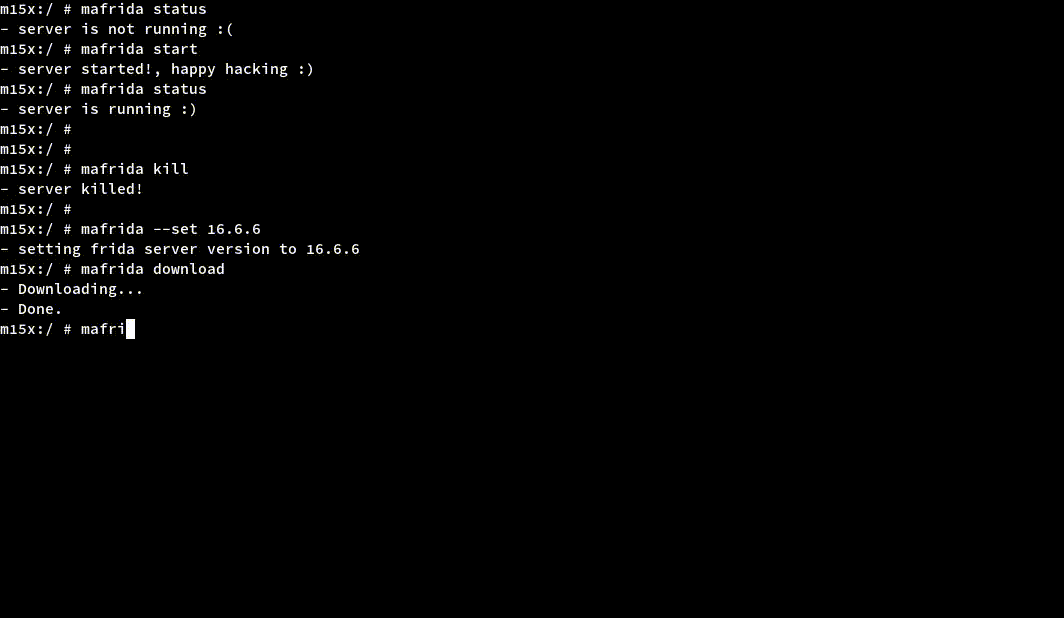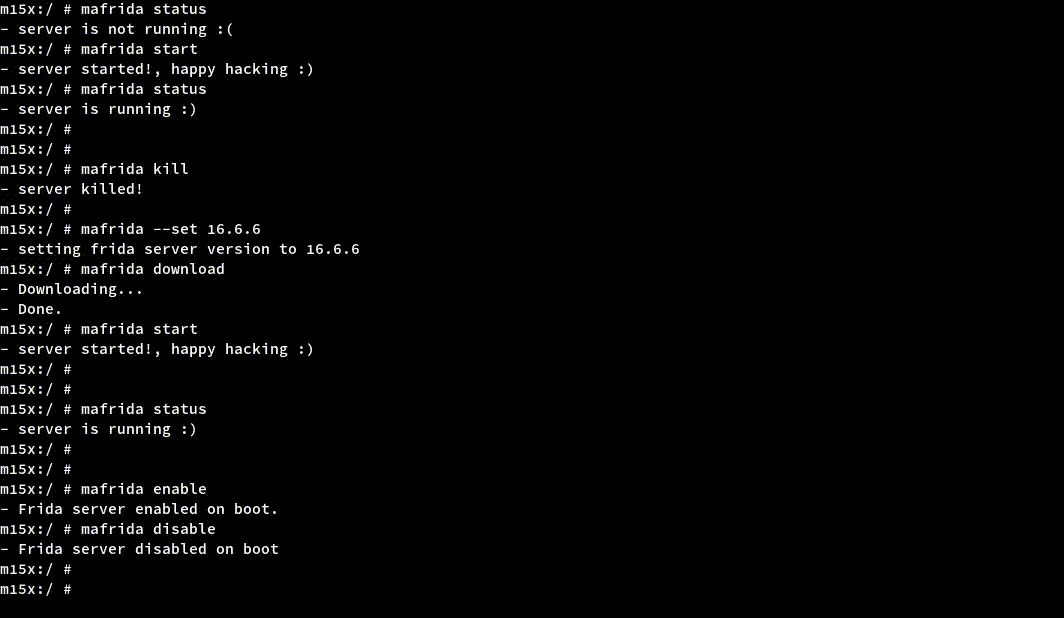 theshinigami/mafrida
A Magisk module that simplifies running the Frida server on Android, with easy management commands to download specific versions, enable or disable…
 chichou/vscode-frida
Unofficial frida extension for VSCode
 bishopfox/mauidll
Extract the managed (.NET) assemblies out of a MAUI Android assembly store.
 fkie-cad/sandroid_dexray-intercept
A Android malware analysis tool that creates comprehensive runtime profiles by hooking into application behavior across cryptography, file systems,…
 hunt-benito/one-multiply-too-many-cve-2026-70638-llama-cpp-android-jni-integer-overflow
Reproduces the CVE-2026-70638 integer overflow in llama.cpp Android JNI with a safe arithmetic demo, malicious GGUF generator, and Frida hook for…
 dere-ad2001/frida-labs
The repo contains a series of challenges for learning Frida for Android Exploitation.
 tinopreter/docviewerexploitapp
This is an Exploit App I made when solving the DocumentViewer challenge (CVE-2021-40724) from MobileHackingLab. It will download a libdocviewe_pro.so…