
Archived
purpleteam-s2-containers
 purpleteam-labs/purpleteam-s2-containers
Stage two containers
cloud-securitycontainer-securitydevsecops+5
purpleteam-labs/purpleteam-s2-containersStage two containers
 security-prince/resources-for-application-security
Some good resources for getting started with application security
 owasp/mastg
Comprehensive OWASP guide for mobile app security testing, reverse engineering, and verifying MASVS/MASWE weaknesses through static, dynamic, and…
 owasp/benchmark
The OWASP Benchmark GitHub repo has moved to: https://github.com/OWASP-Benchmark/BenchmarkJava
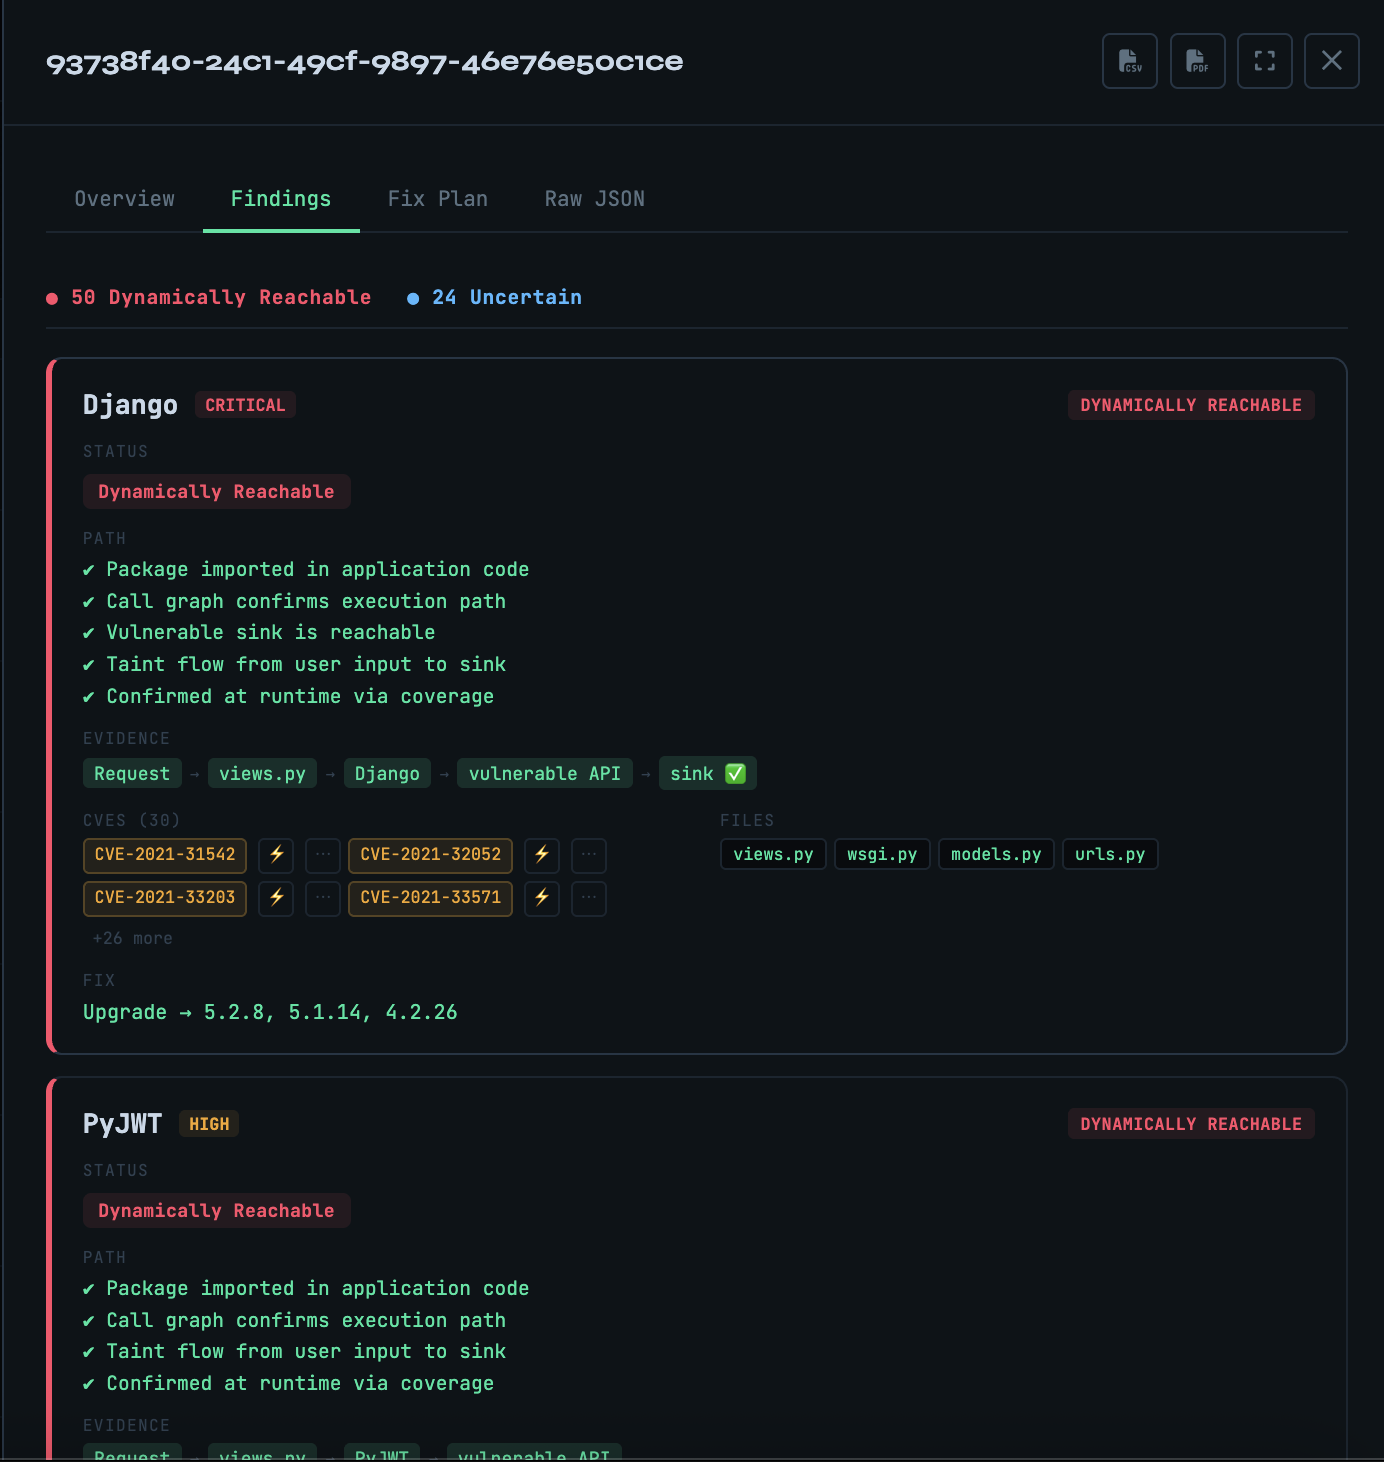 owasp/vulnreach
Runtime-aware SCA — proves which CVEs are actually reachable, not just installed.
 mobsf/mobile-security-framework-mobsf
Automated mobile application security testing framework for Android, iOS, and Windows. Performs static and dynamic analysis, malware detection, and…
 silentchainai/silentchain
AI-powered vulnerability scanner extension for Burp Suite with multi-provider support (Ollama, OpenAI, Claude, Gemini)
 nuguardai/nuguard
opensource repo for validating agentic AI applications: redteam, behavior, supply-chain, static analysis
 cspf-founder/api-scanner-docker
Automated API security testing tool that scans REST and SOAP APIs for vulnerabilities using OpenAPI/Swagger specs and WSDL files. Deploys a full …
 saffron-health/libretto
The AI toolkit for building reliable browser automations
 mseclab/pyjfuzz
PyJFuzz - Python JSON Fuzzer

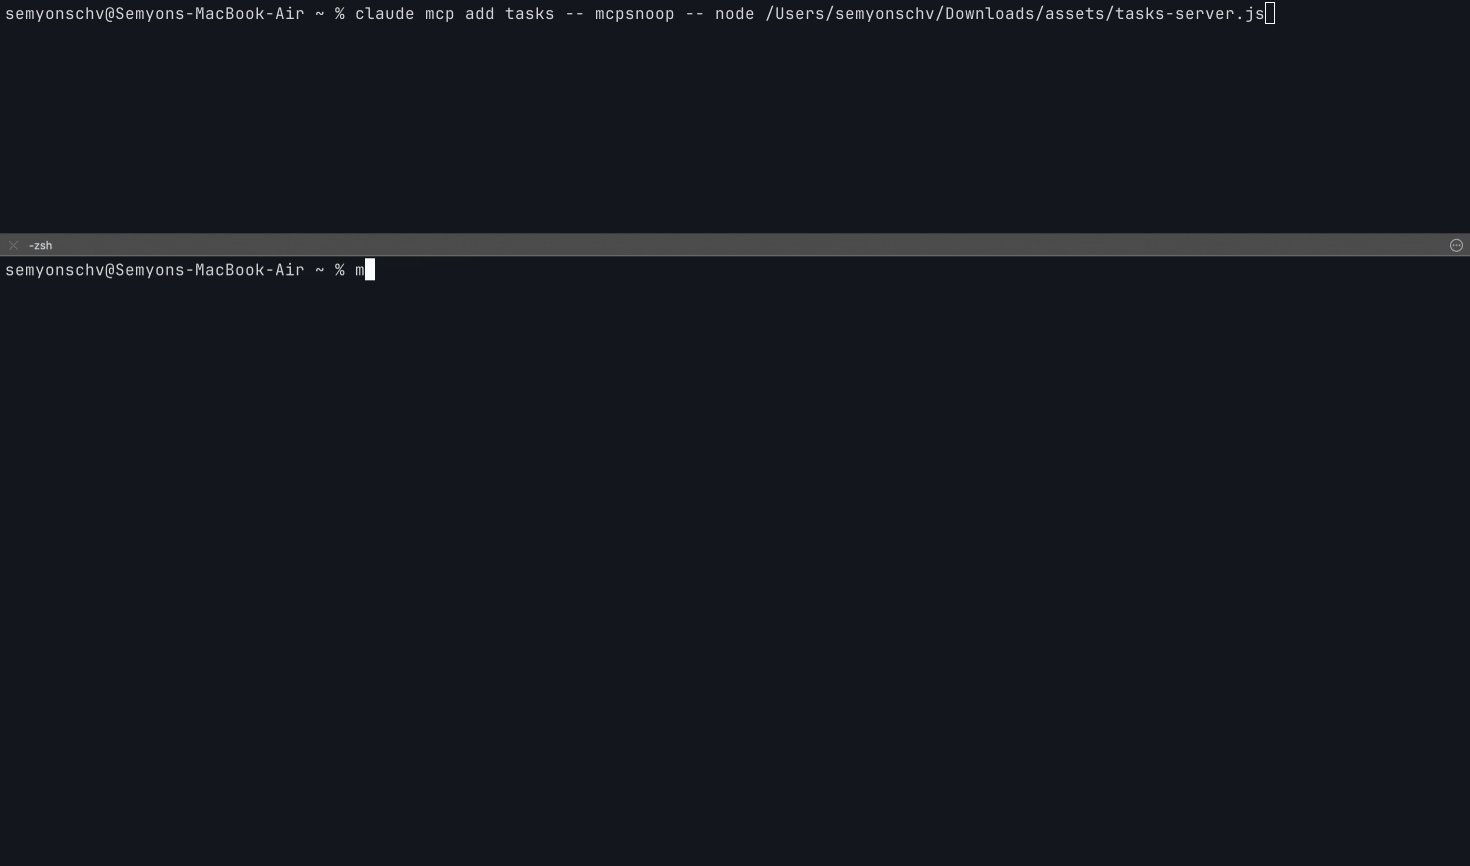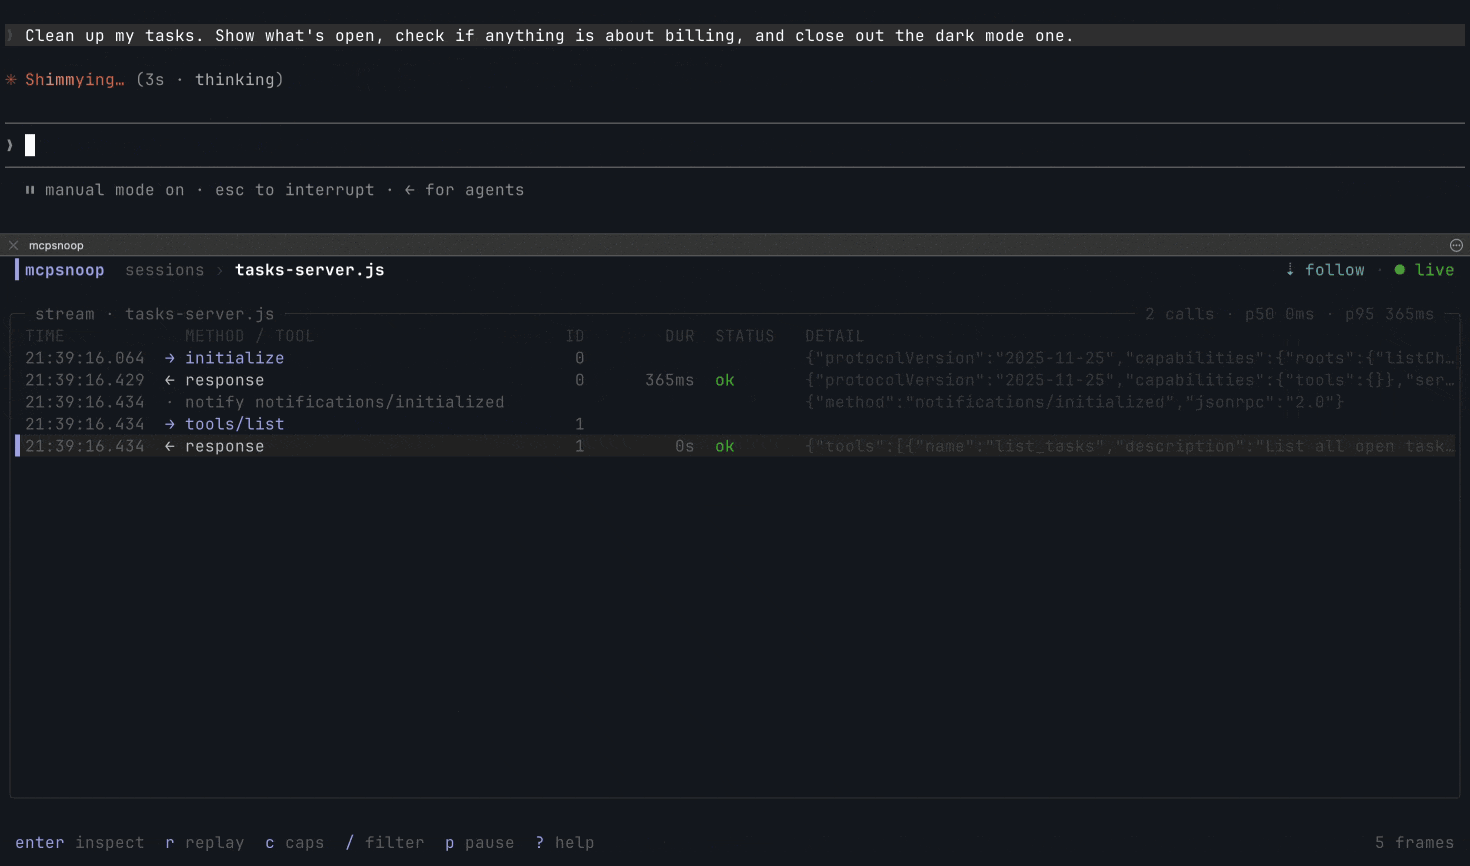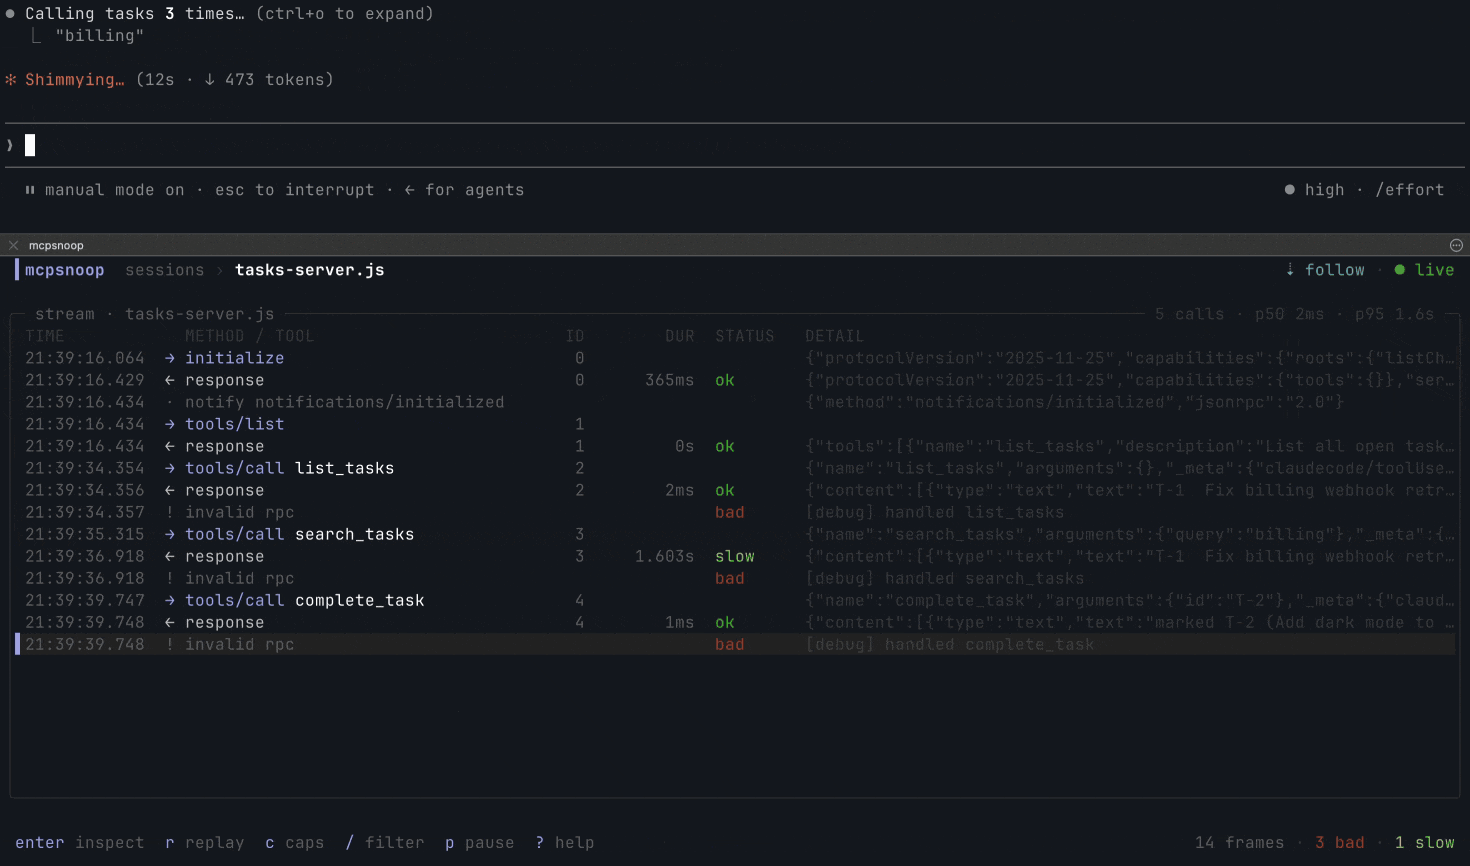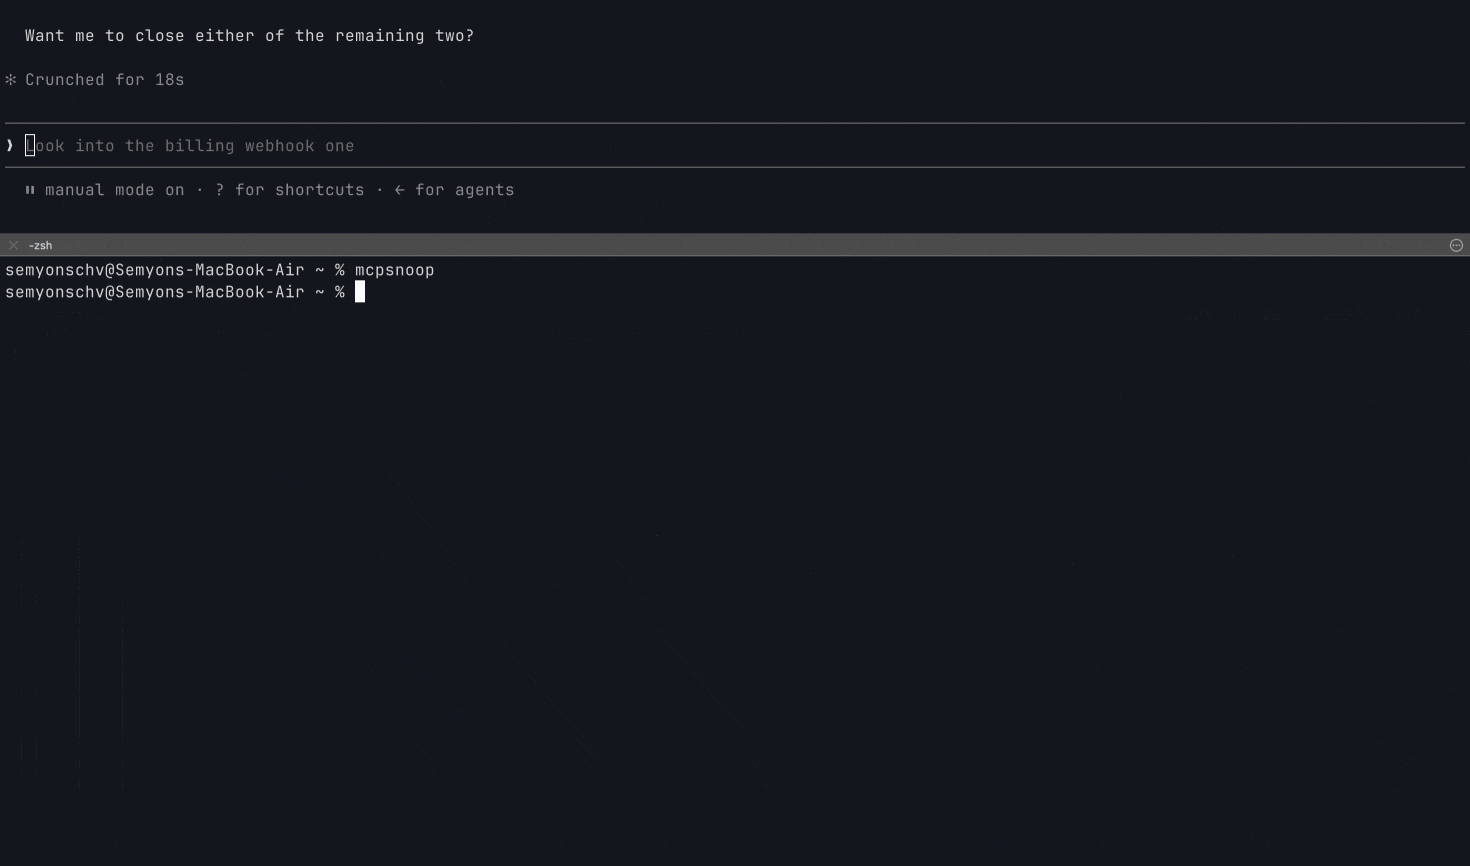 kerlenton/mcpsnoop
Wireshark for MCP. A transparent proxy that shows every real tool call between your AI client and your MCP servers, live in your terminal.
 yalcinyolalan/wssat
WEB SERVICE SECURITY ASSESSMENT TOOL
 hahwul/mzap
⚡️ Multiple target ZAP Scanning
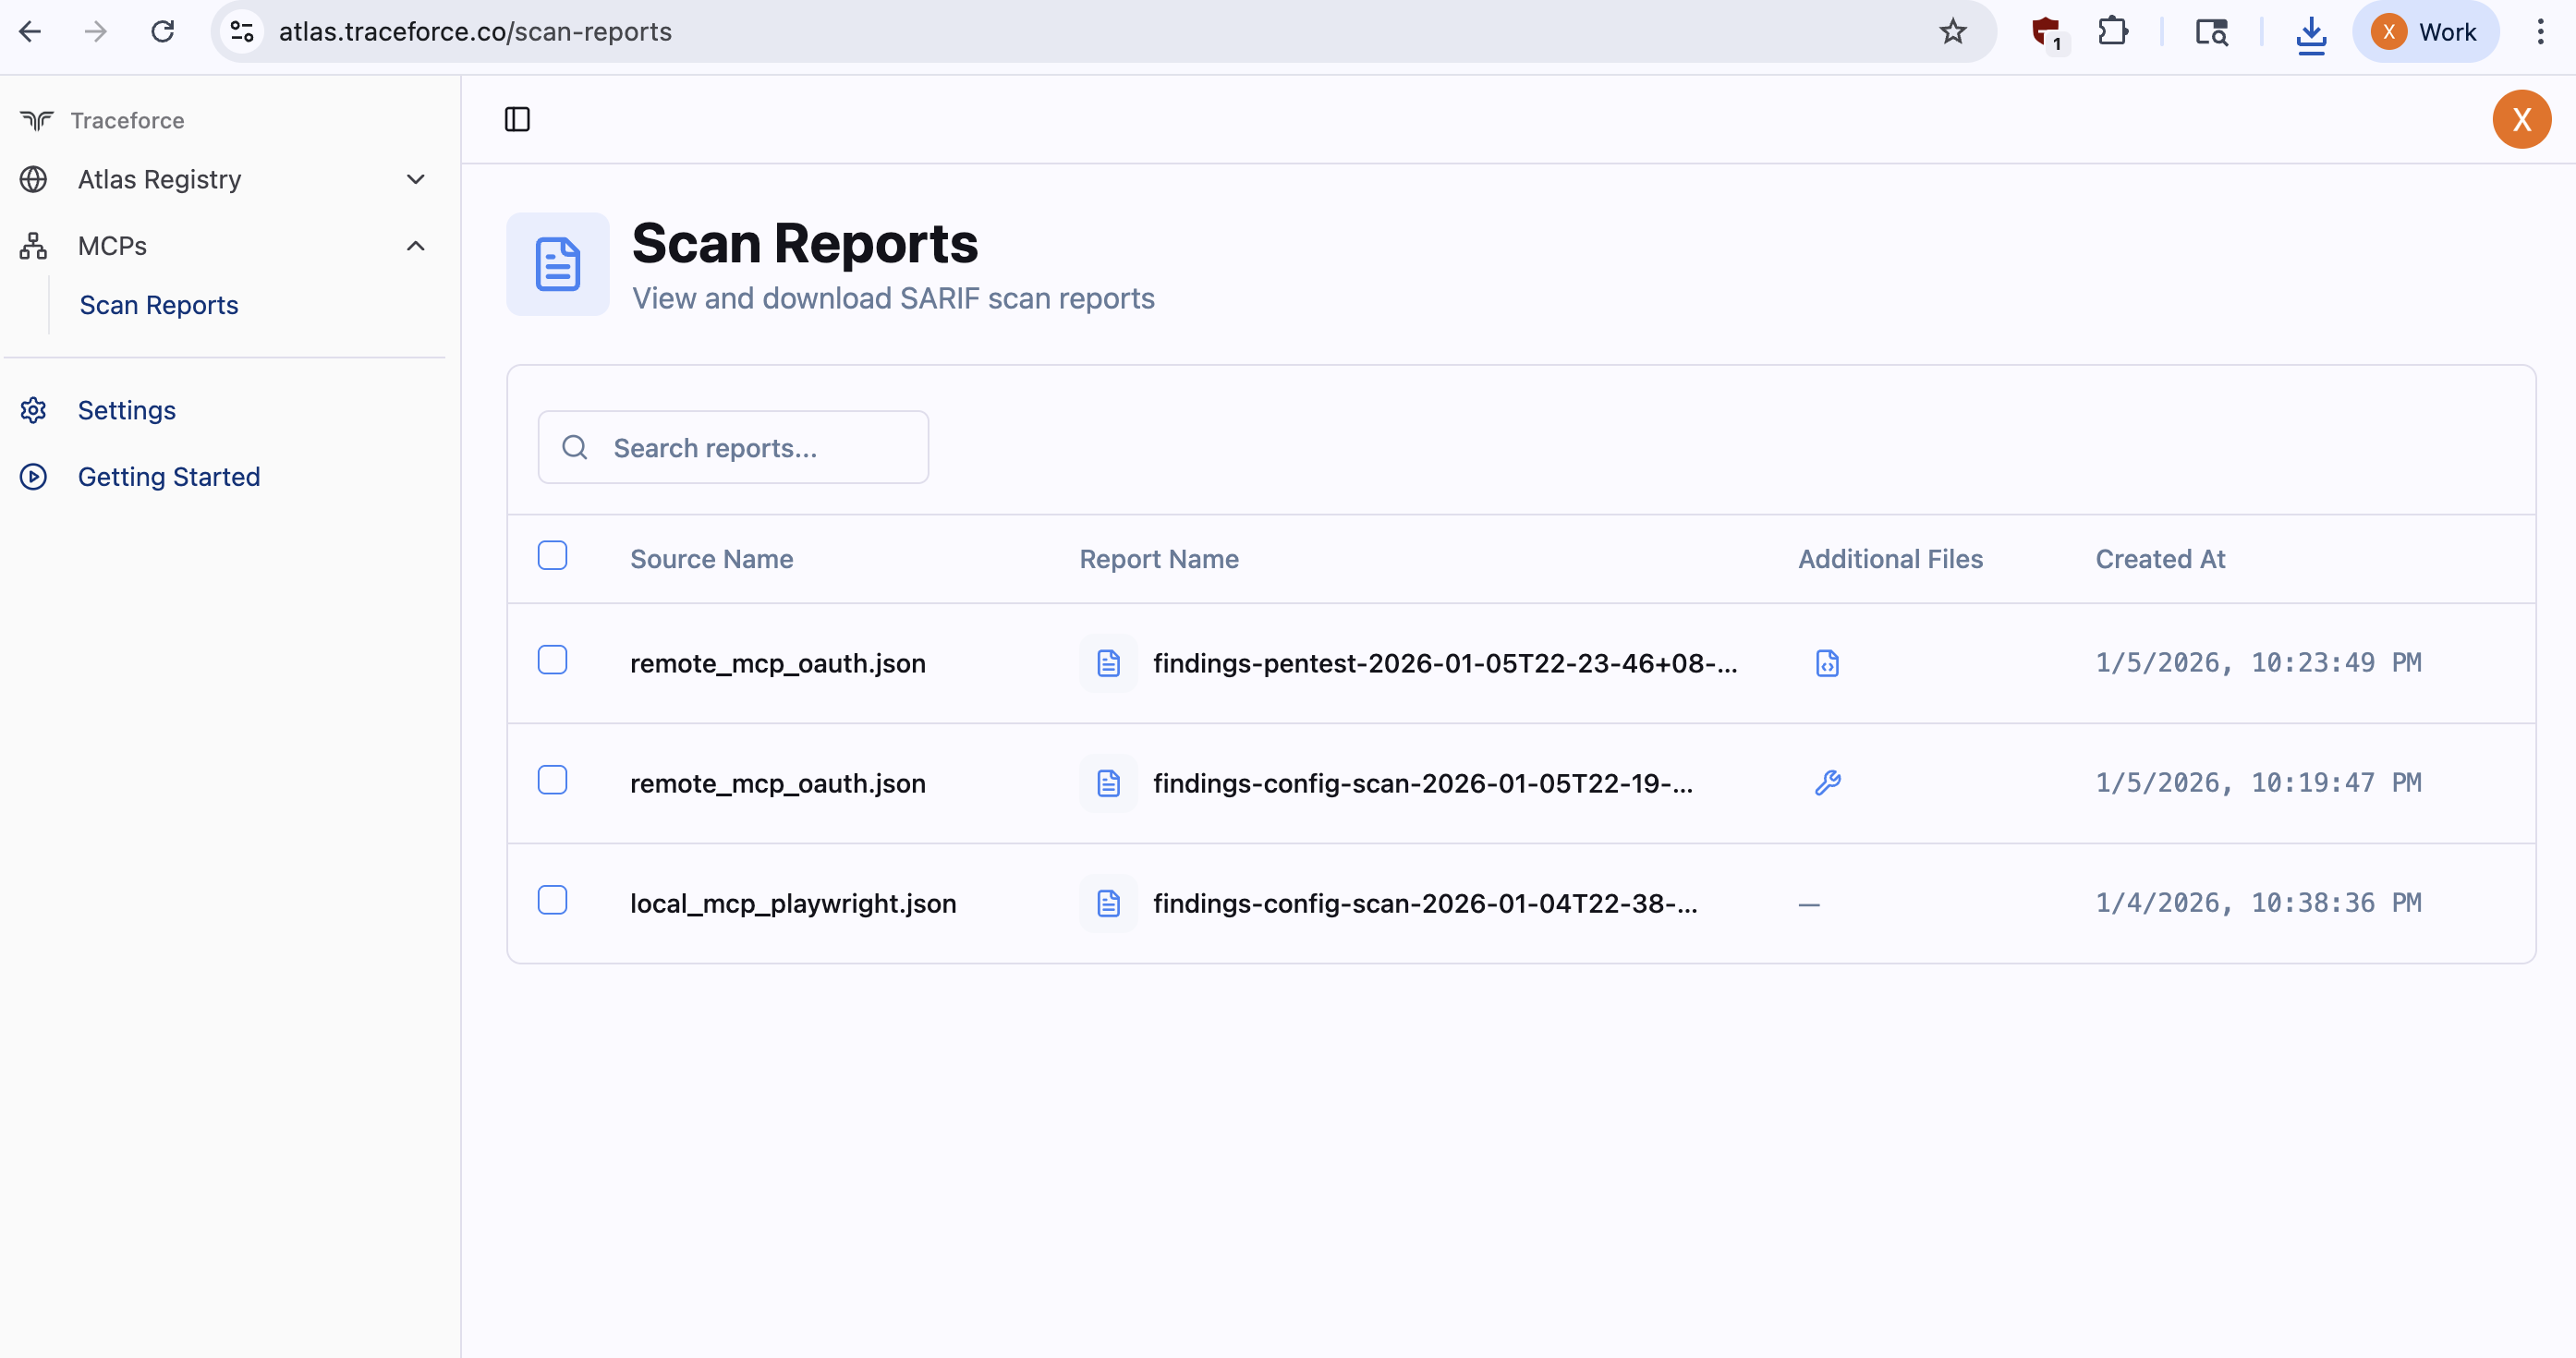 traceforce/mcp-xray
Unified security scanner for MCP servers with config, pentest, and repo-scan modes. Generates SARIF reports for CI/CD integration, detects secrets,…
 use-tusk/tusk-cli
Automated testing suite with live traffic record and replay
 go-appsec/toolbox
Collaborative application security testing between humans and agents via CLI and MCP