

mastg
 owasp/mastg
Comprehensive OWASP guide for mobile app security testing, reverse engineering, and verifying MASVS/MASWE weaknesses through static, dynamic, and…
android-securitycryptographydynamic-analysis-sandboxing+9
13.3k
owasp/mastgComprehensive OWASP guide for mobile app security testing, reverse engineering, and verifying MASVS/MASWE weaknesses through static, dynamic, and…
 mobsf/mobile-security-framework-mobsf
Automated mobile application security testing framework for Android, iOS, and Windows. Performs static and dynamic analysis, malware detection, and…
 hackinglz/maps_scanner
MAPS cloud scanner and response parser for Microsoft Defender research.
 owasp/benchmark
The OWASP Benchmark GitHub repo has moved to: https://github.com/OWASP-Benchmark/BenchmarkJava
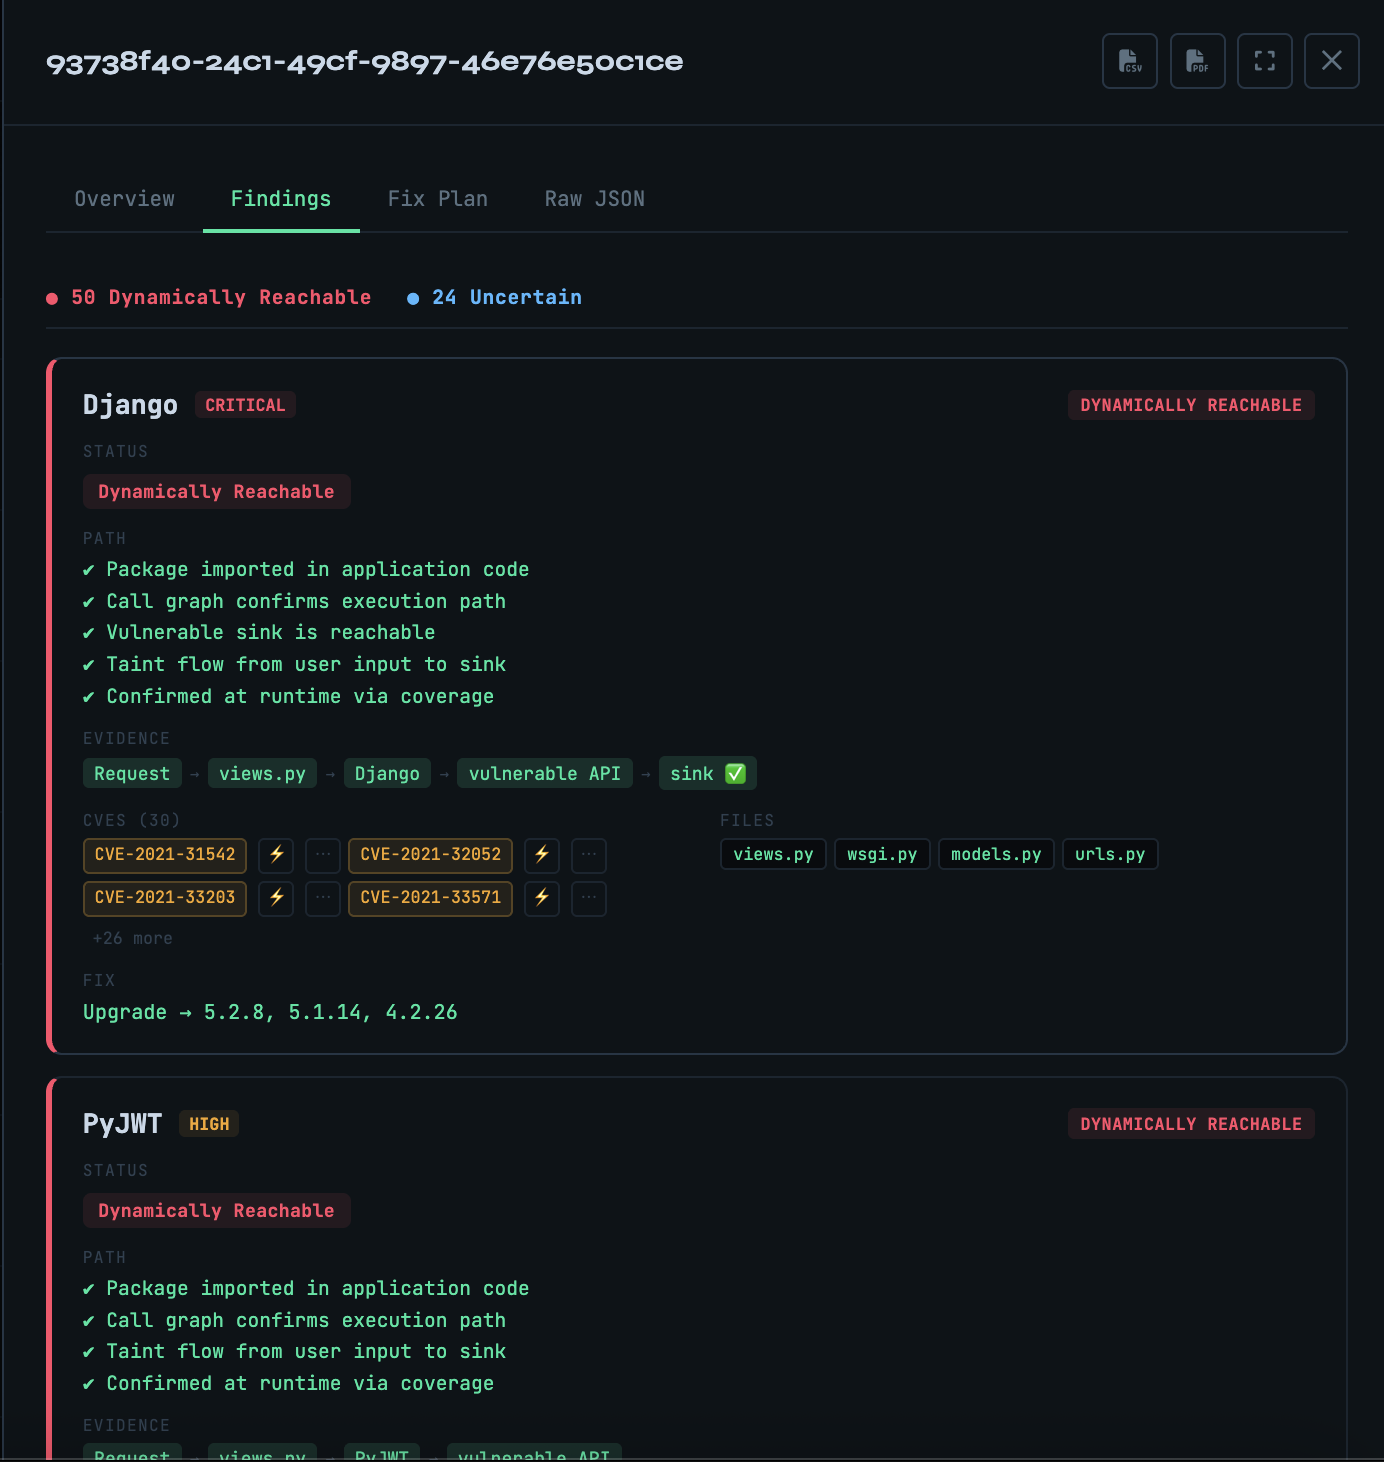 owasp/vulnreach
Runtime-aware SCA — proves which CVEs are actually reachable, not just installed.
 akha-security/akca
Evidence-oriented DAST scanner in Go that crawls web apps and APIs, then runs adaptive SQLi, XSS, RCE, SSRF, and auth checks with replayable proof.
 silentchainai/silentchain
AI-powered vulnerability scanner extension for Burp Suite with multi-provider support (Ollama, OpenAI, Claude, Gemini)
 yalcinyolalan/wssat
WEB SERVICE SECURITY ASSESSMENT TOOL
 cspf-founder/api-scanner-docker
Automated API security testing tool that scans REST and SOAP APIs for vulnerabilities using OpenAPI/Swagger specs and WSDL files. Deploys a full …
 security-prince/resources-for-application-security
Some good resources for getting started with application security
 nuguardai/nuguard
opensource repo for validating agentic AI applications: redteam, behavior, supply-chain, static analysis
 purpleteam-labs/purpleteam-s2-containers
Stage two containers
 kerlenton/mcpsnoop
Wireshark for MCP. A transparent proxy between your AI client and MCP server. Watch every call live in your terminal, fail CI on what it finds,…
 traceforce/mcp-xray
Unified security scanner for MCP servers with config, pentest, and repo-scan modes. Generates SARIF reports for CI/CD integration, detects secrets,…
 use-tusk/tusk-cli
Automated testing suite with live traffic record and replay
 go-appsec/toolbox
Collaborative application security testing between humans and agents via CLI and MCP
 nccgroup/amfdser-ngng
A Burp Extender plugin, that will take deserialized AMF objects and encode them in XML using the Xtream library
 kaisonox/apiscope
An API hooking framework for intercepting and monitoring Windows applications