
Benchmark
 owasp/benchmark
The OWASP Benchmark GitHub repo has moved to: https://github.com/OWASP-Benchmark/BenchmarkJava
code-analysisdynamic-analysis-sandboxingeducation+3
owasp/benchmarkThe OWASP Benchmark GitHub repo has moved to: https://github.com/OWASP-Benchmark/BenchmarkJava
 security-prince/resources-for-application-security
Some good resources for getting started with application security
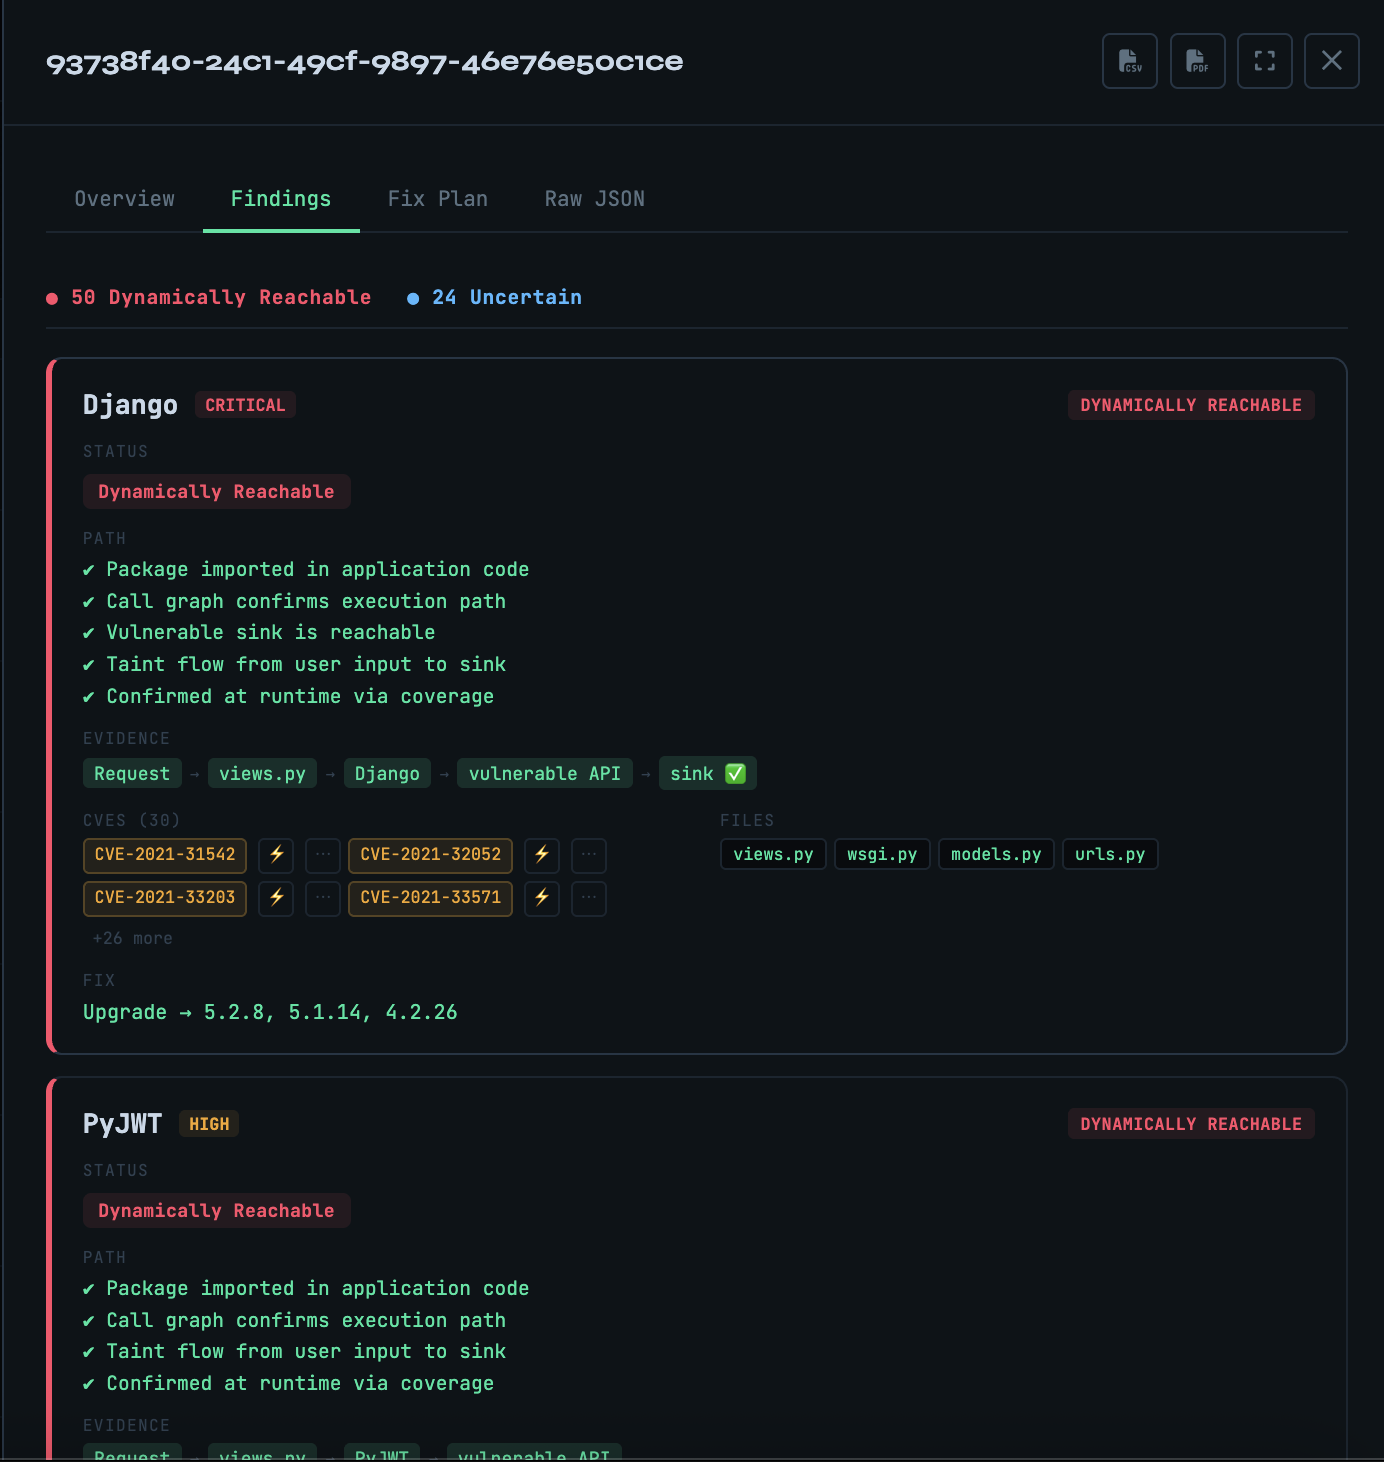 owasp/vulnreach
Runtime-aware SCA — proves which CVEs are actually reachable, not just installed.
 silentchainai/silentchain
AI-powered vulnerability scanner extension for Burp Suite with multi-provider support (Ollama, OpenAI, Claude, Gemini)
 purpleteam-labs/purpleteam-s2-containers
Stage two containers
 curtail-inc/hello-regrade-security
Find the vulnerability your tests were never written to catch. A ReGrade demo modeling CVE-2023-5968: catch a password-hash leak by comparing an app…
 andreafioraldi/frida-fuzzer
This experimetal fuzzer is meant to be used for API in-memory fuzzing.
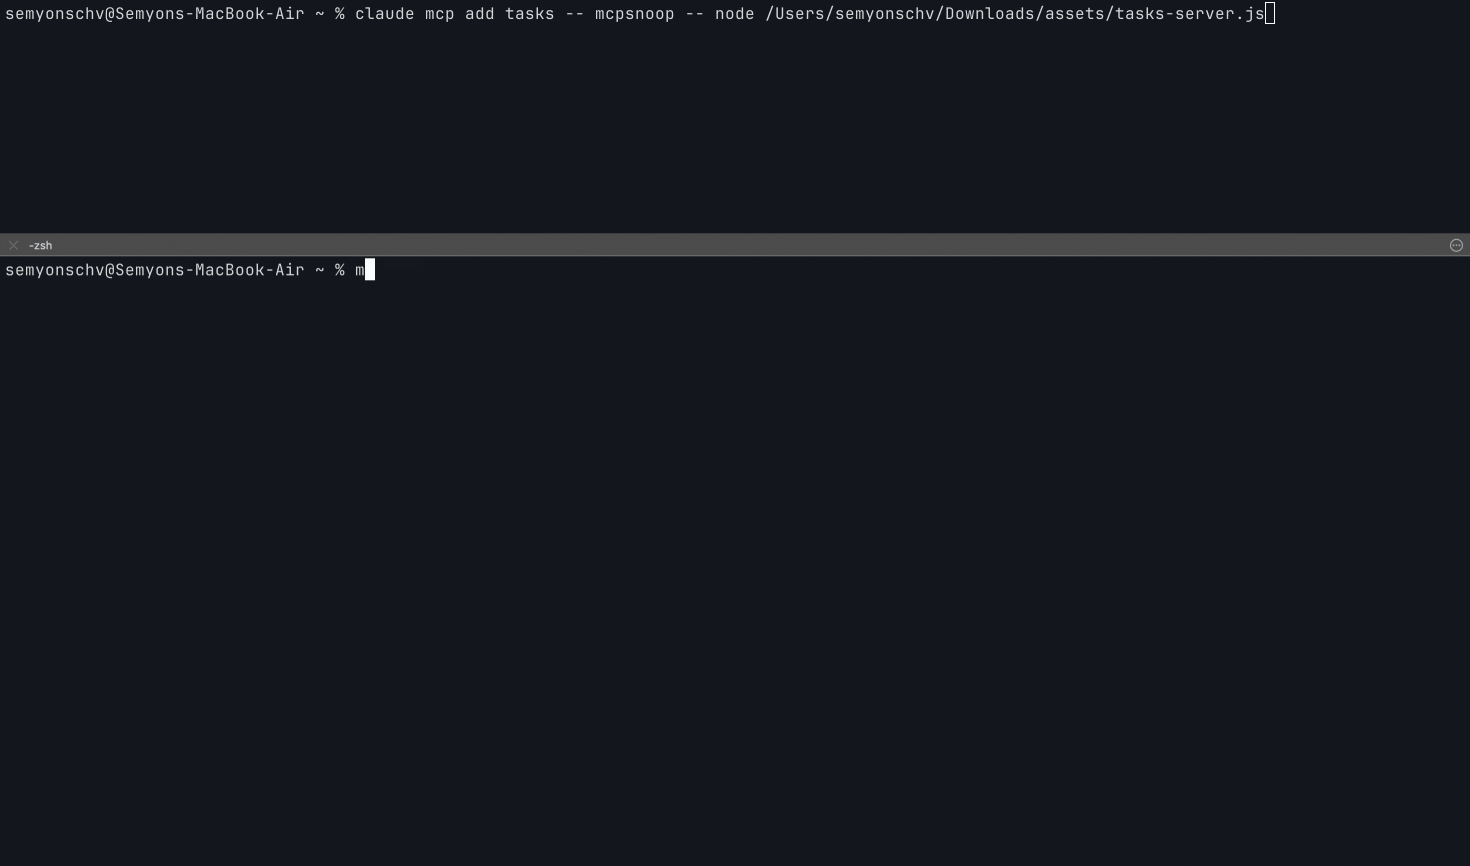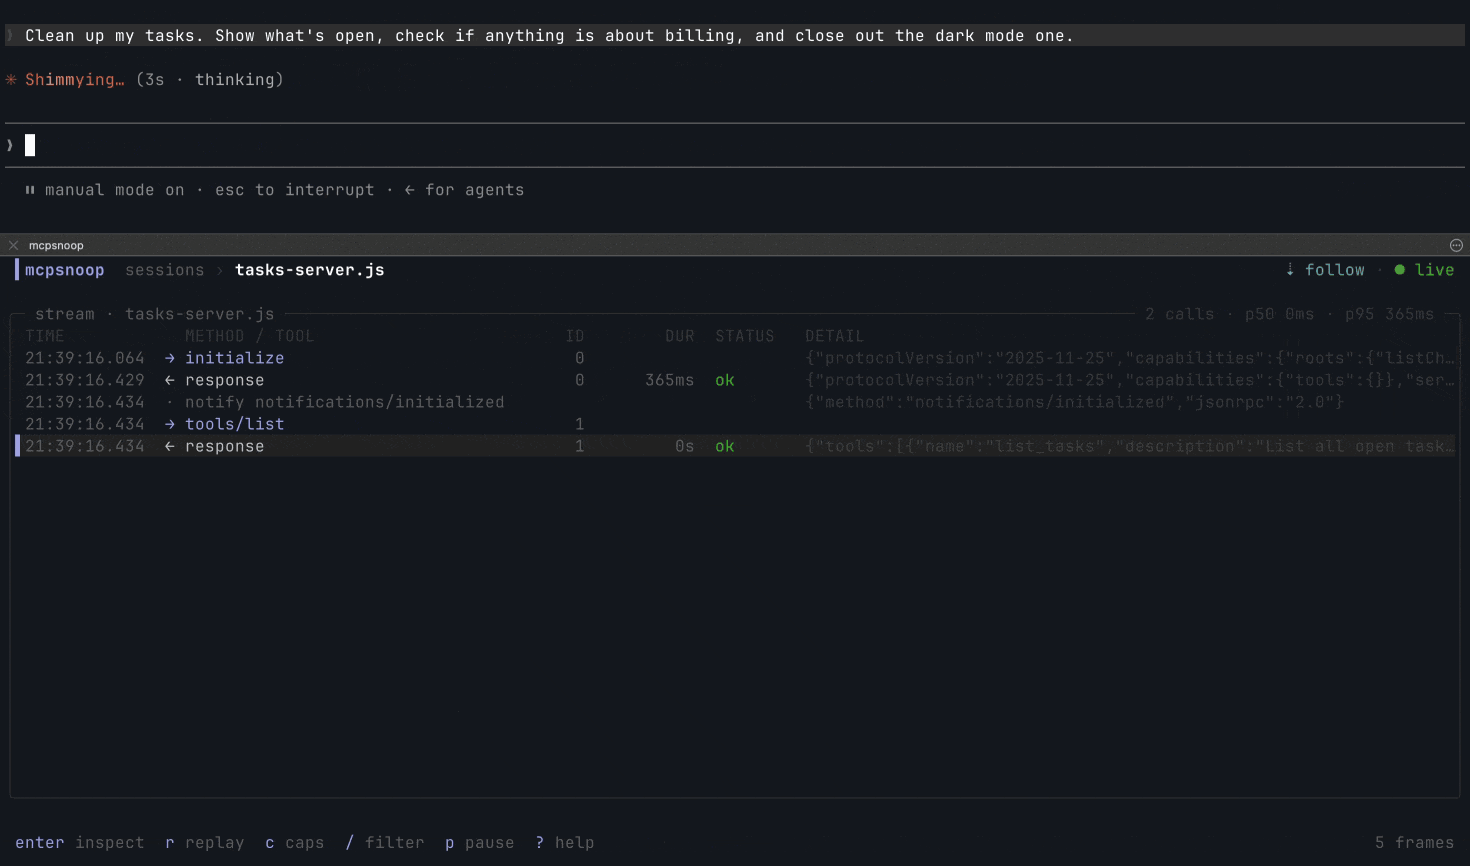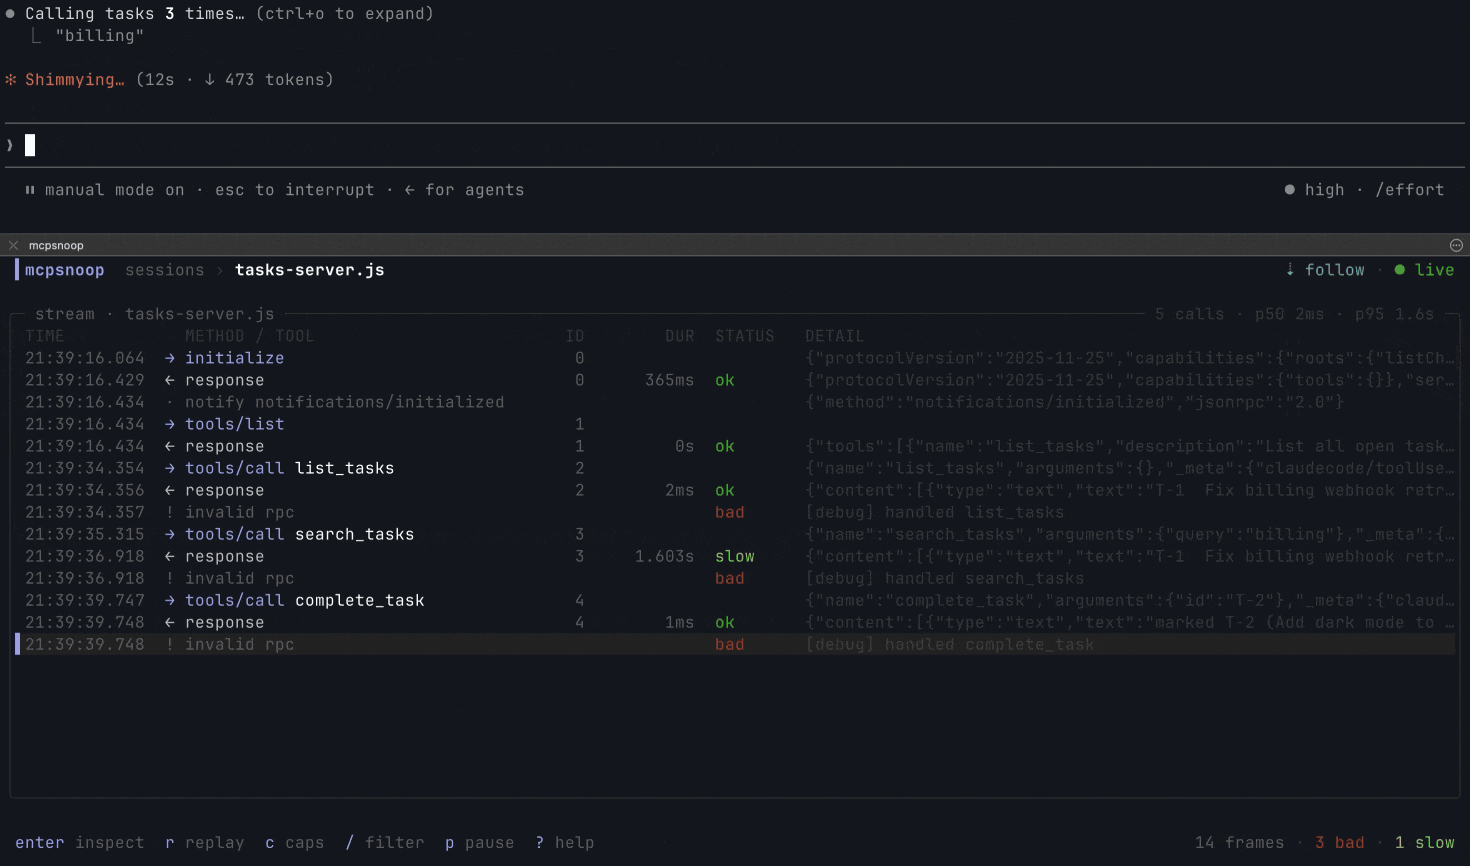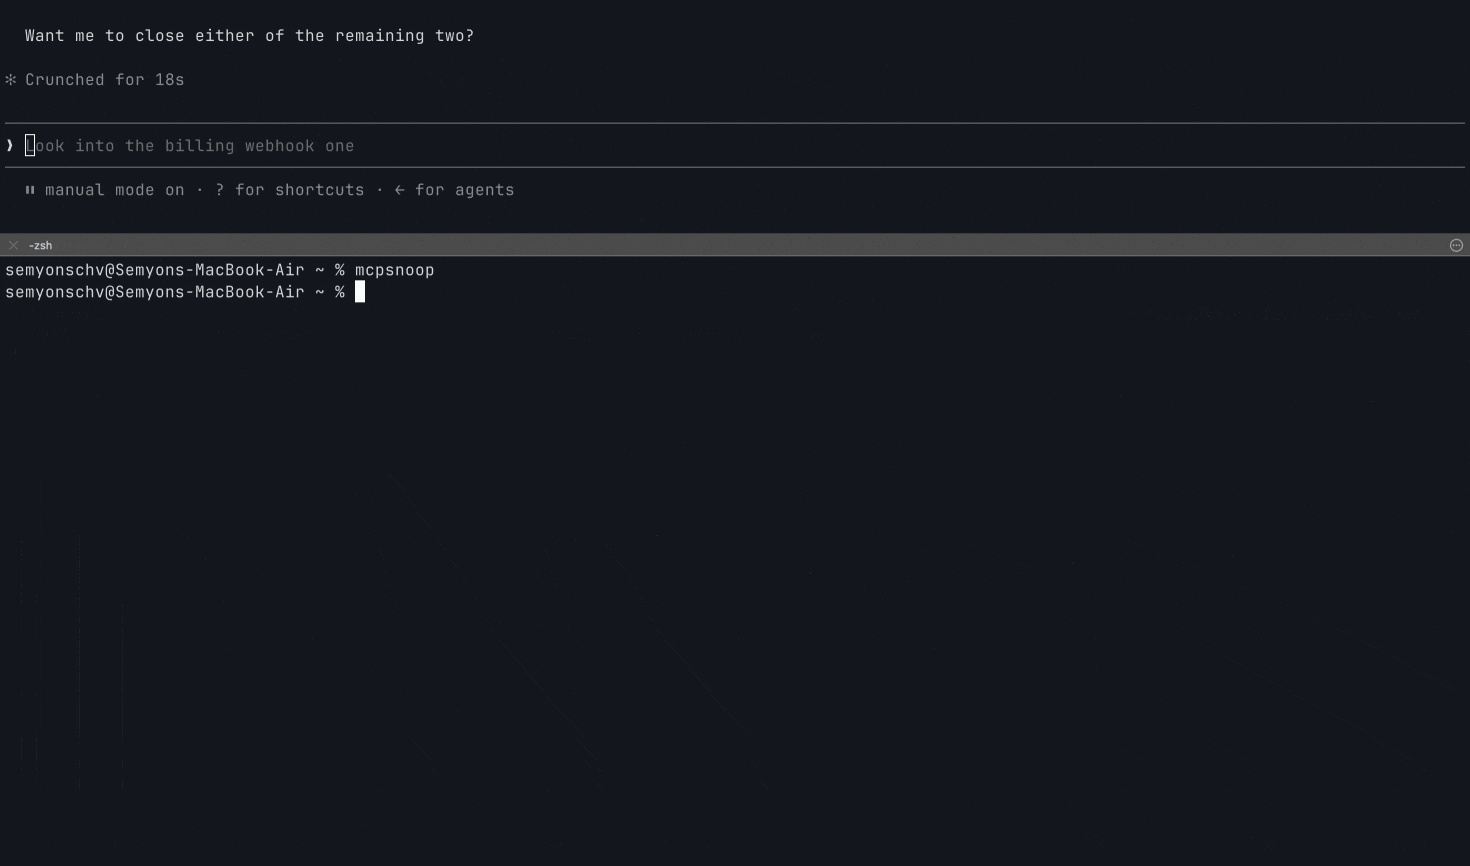 kerlenton/mcpsnoop
Wireshark for MCP. A transparent proxy between your AI client and MCP server. Watch every call live in your terminal, fail CI on what it finds,…
 yalcinyolalan/wssat
WEB SERVICE SECURITY ASSESSMENT TOOL
 use-tusk/tusk-cli
Automated testing suite with live traffic record and replay
 google/martian
Martian is a library for building custom HTTP/S proxies
 owasp/mastg
Comprehensive OWASP guide for mobile app security testing, reverse engineering, and verifying MASVS/MASWE weaknesses through static, dynamic, and…
 mobsf/mobile-security-framework-mobsf
Automated mobile application security testing framework for Android, iOS, and Windows. Performs static and dynamic analysis, malware detection, and…
 nuguardai/nuguard
opensource repo for validating agentic AI applications: redteam, behavior, supply-chain, static analysis
 cspf-founder/api-scanner-docker
Automated API security testing tool that scans REST and SOAP APIs for vulnerabilities using OpenAPI/Swagger specs and WSDL files. Deploys a full …
 mseclab/pyjfuzz
PyJFuzz - Python JSON Fuzzer
 saffron-health/libretto
The AI toolkit for building reliable browser automations
 akha-security/akca
Evidence-oriented DAST scanner in Go that crawls web apps and APIs, then runs adaptive SQLi, XSS, RCE, SSRF, and auth checks with replayable proof.