
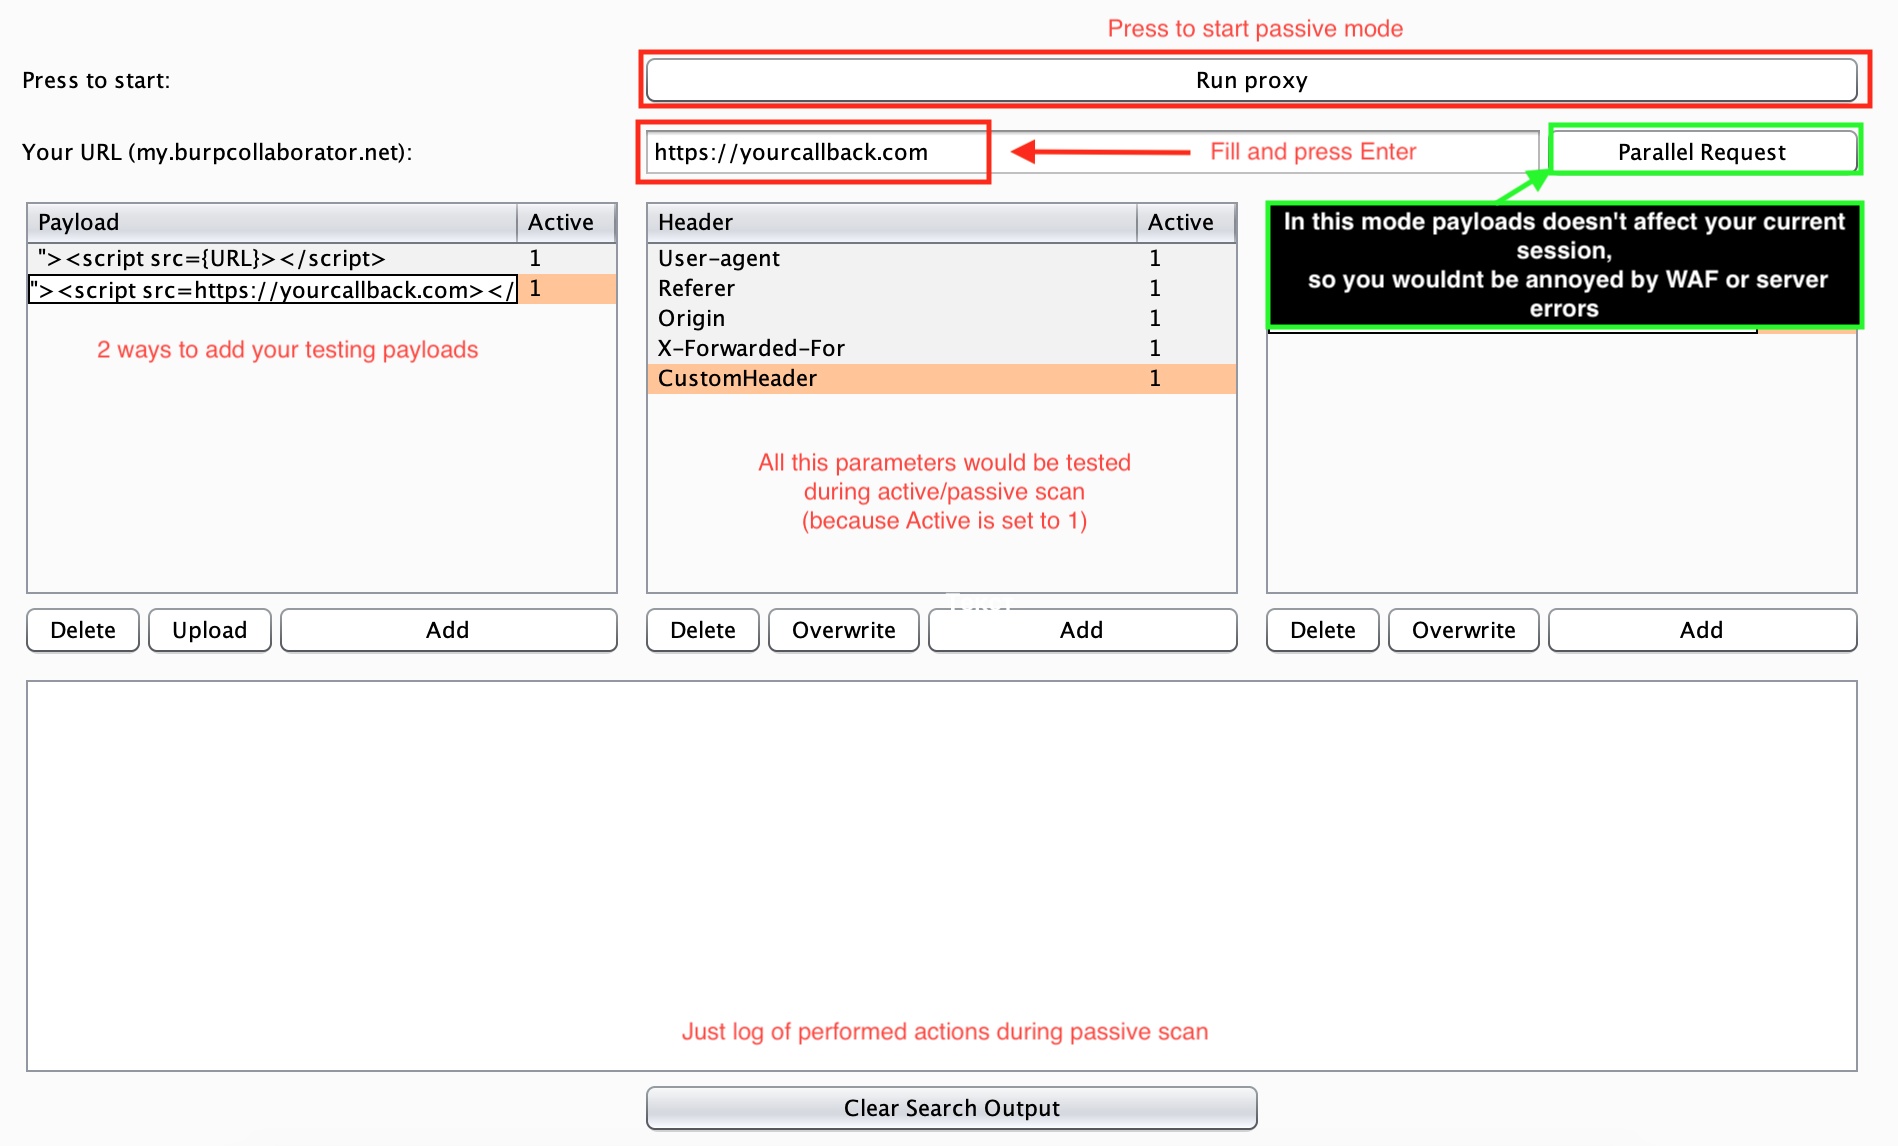
femida
 wish-i-was/femida
Automated blind-xss search for Burp Suite
dynamic-analysis-sandboxingpenetration-testingvulnerability-scanners+1
wish-i-was/femidaAutomated blind-xss search for Burp Suite
 portswigger/http-request-smuggler
Burp Suite extension for automated detection and exploitation of HTTP request smuggling vulnerabilities, supporting HTTP/1.1 and HTTP/2-downgrade…
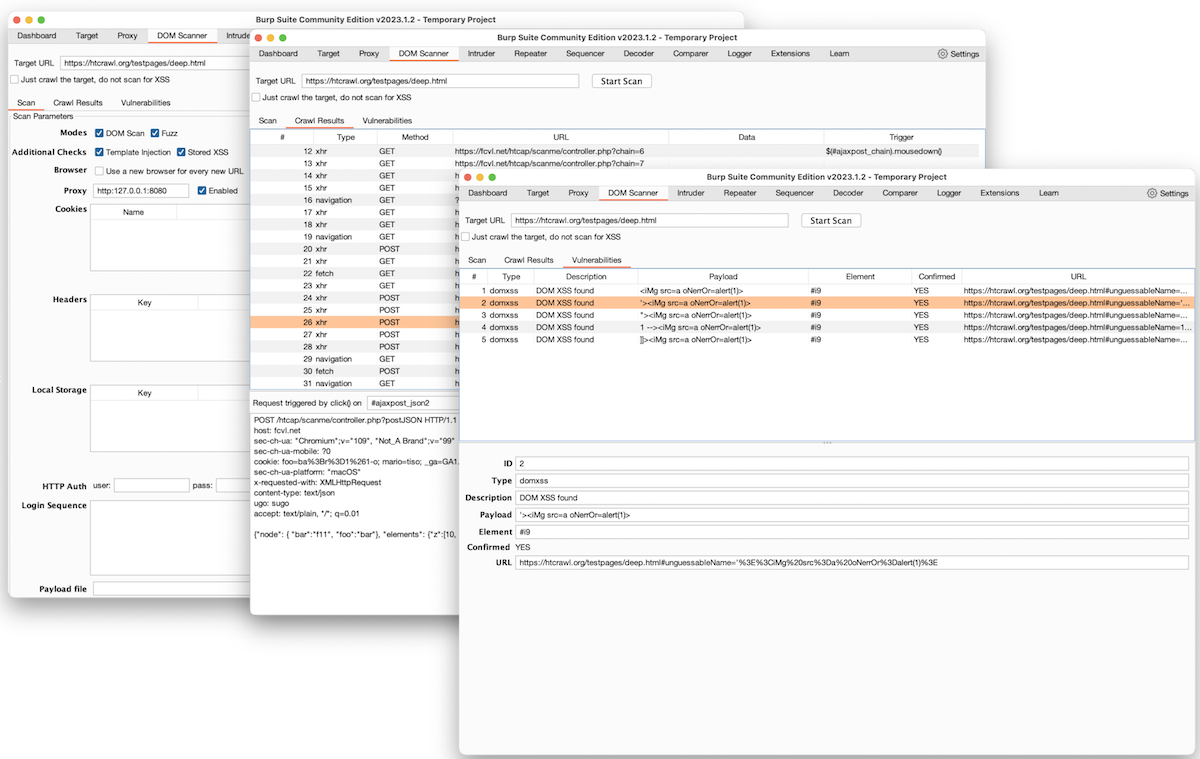 fcavallarin/burp-dom-scanner
Burp Suite's extension to scan and crawl Single Page Applications
 silentchainai/silentchain
AI-powered vulnerability scanner extension for Burp Suite with multi-provider support (Ollama, OpenAI, Claude, Gemini)
 raz0r/burp-radamsa
Radamsa fuzzer extension for Burp Suite
 aliclub0x00/cve-2025-55182-poc-nextjs
Working proof of concept for NextJS RCE to establish a reverse shell. [React2Shell]
 f2u0a0d3/cve-2026-42945-nginx-rift-poc
PoC for CVE-2026-42945 (nginx Rift) — heap buffer overflow in ngx_http_rewrite_module. Includes detect/probe/exploit modes, dual-fixture Docker lab,…
 androidhooker/hooker
Hooker is an opensource project for dynamic analyses of Android applications. This project provides various tools and applications that can be use to…
 zhixiangyao/cve-2025-66478-exploit-poc
Proof-of-concept exploit demo for CVE-2025-66478 using Node.js
 saffron-health/libretto
The AI toolkit for building reliable browser automations
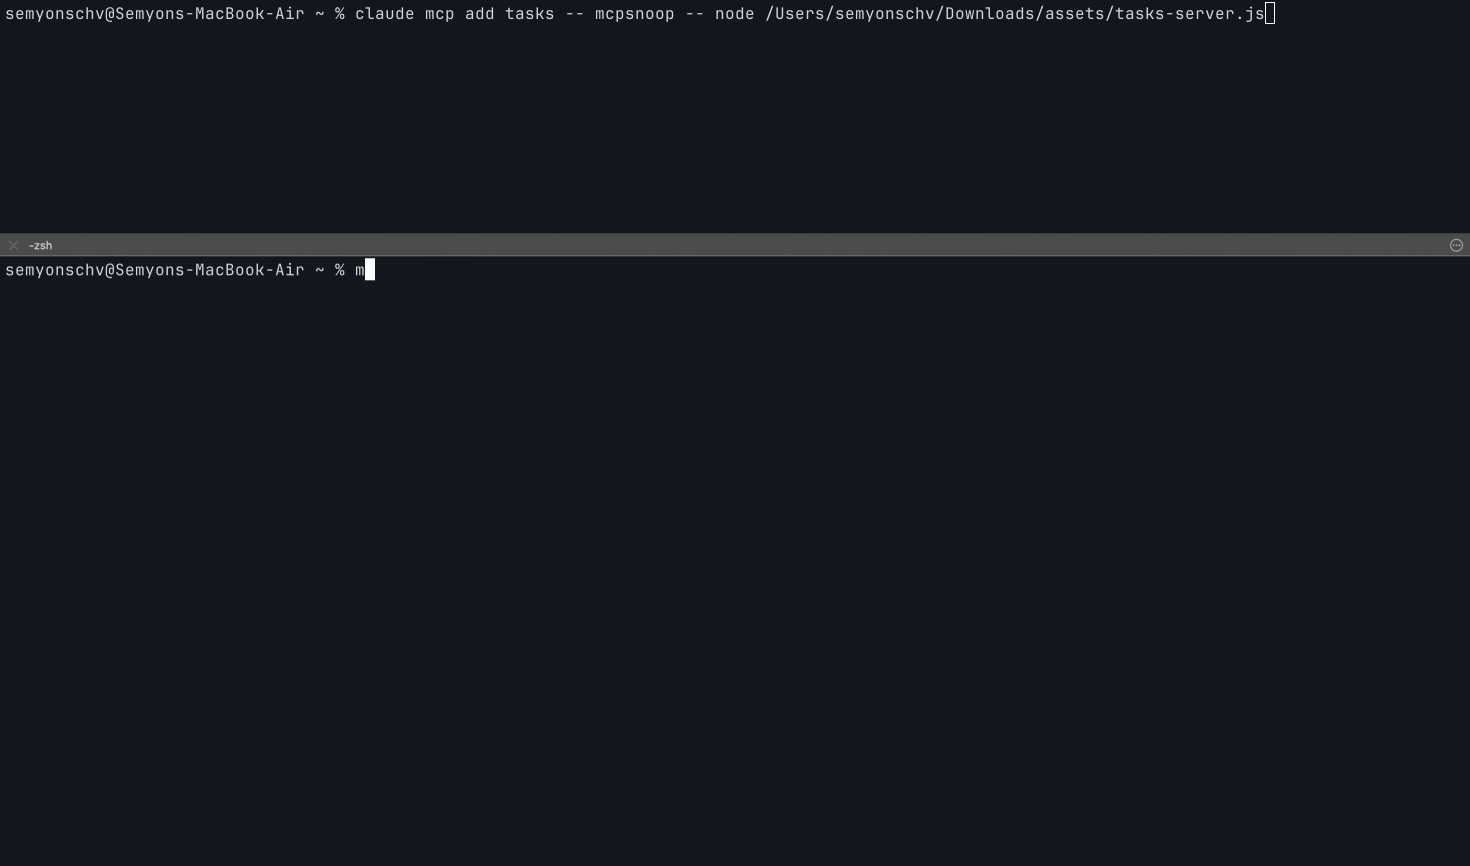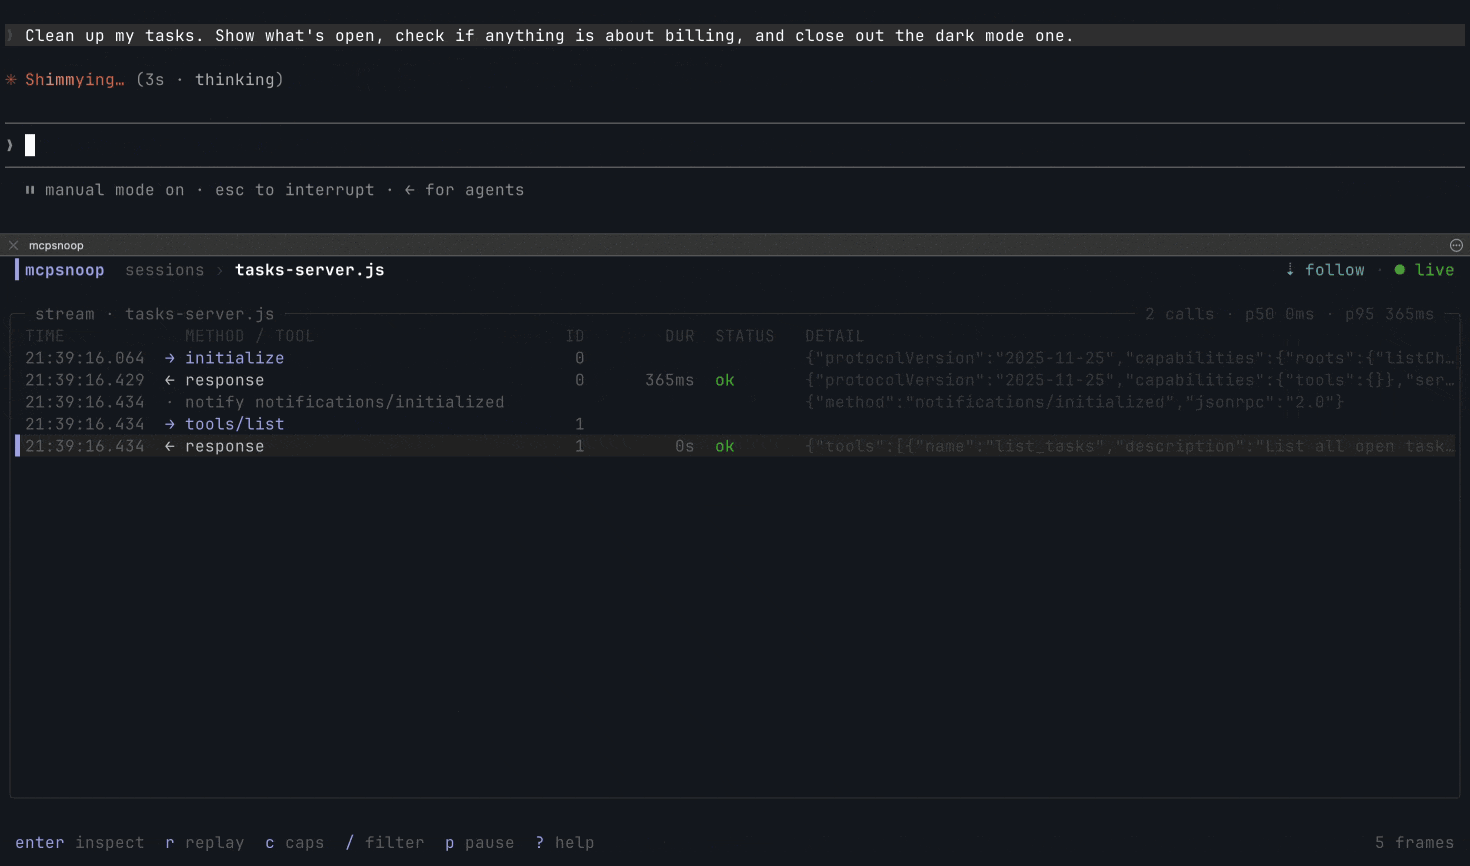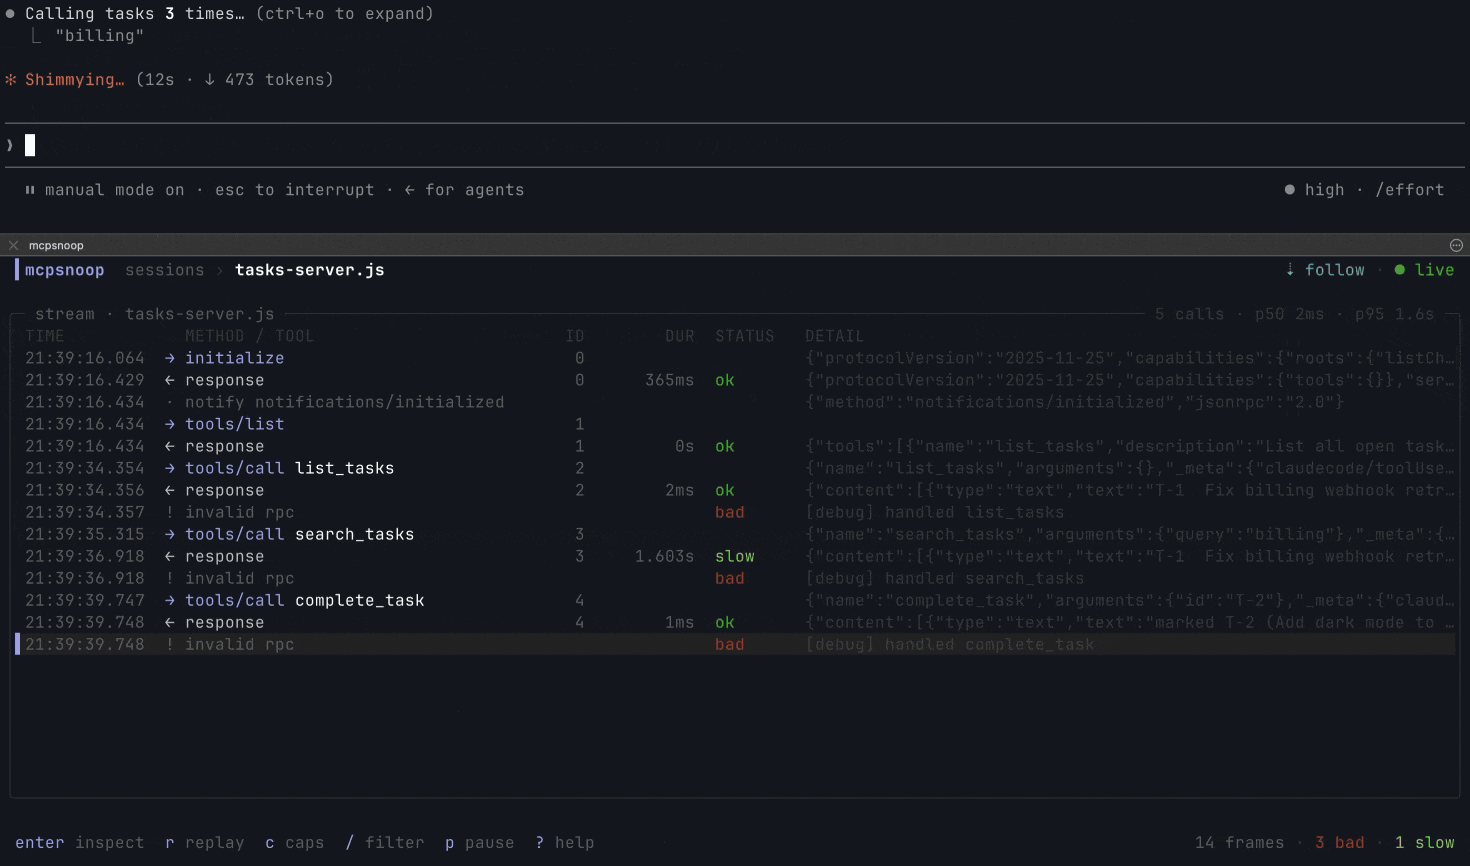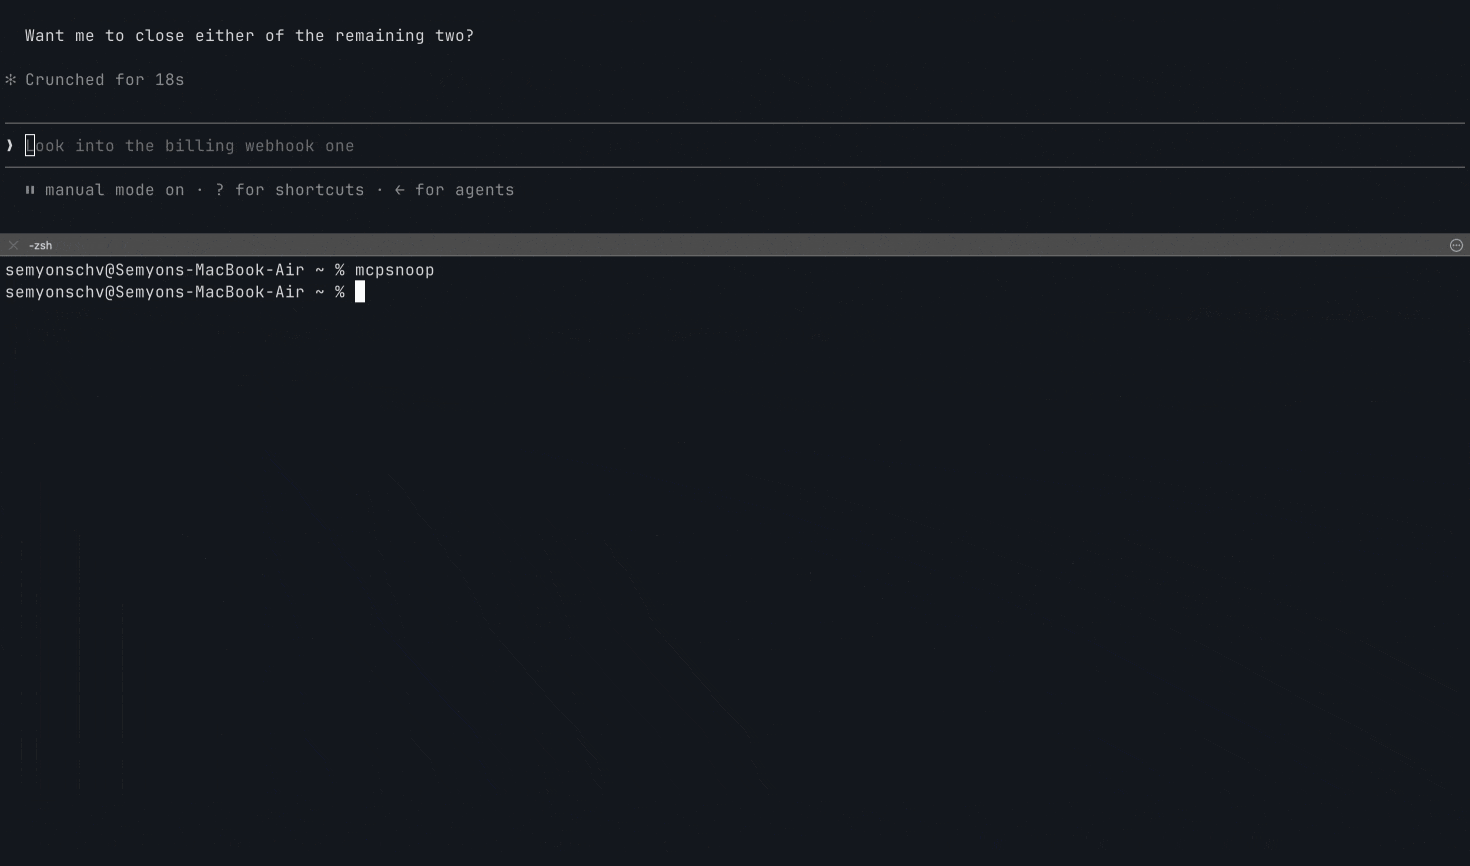 kerlenton/mcpsnoop
Wireshark for MCP. A transparent proxy between your AI client and MCP server. Watch every call live in your terminal, fail CI on what it finds,…
 hellsender01/llmmap
Automated prompt injection testing framework for LLM-integrated applications with dual-LLM architecture.
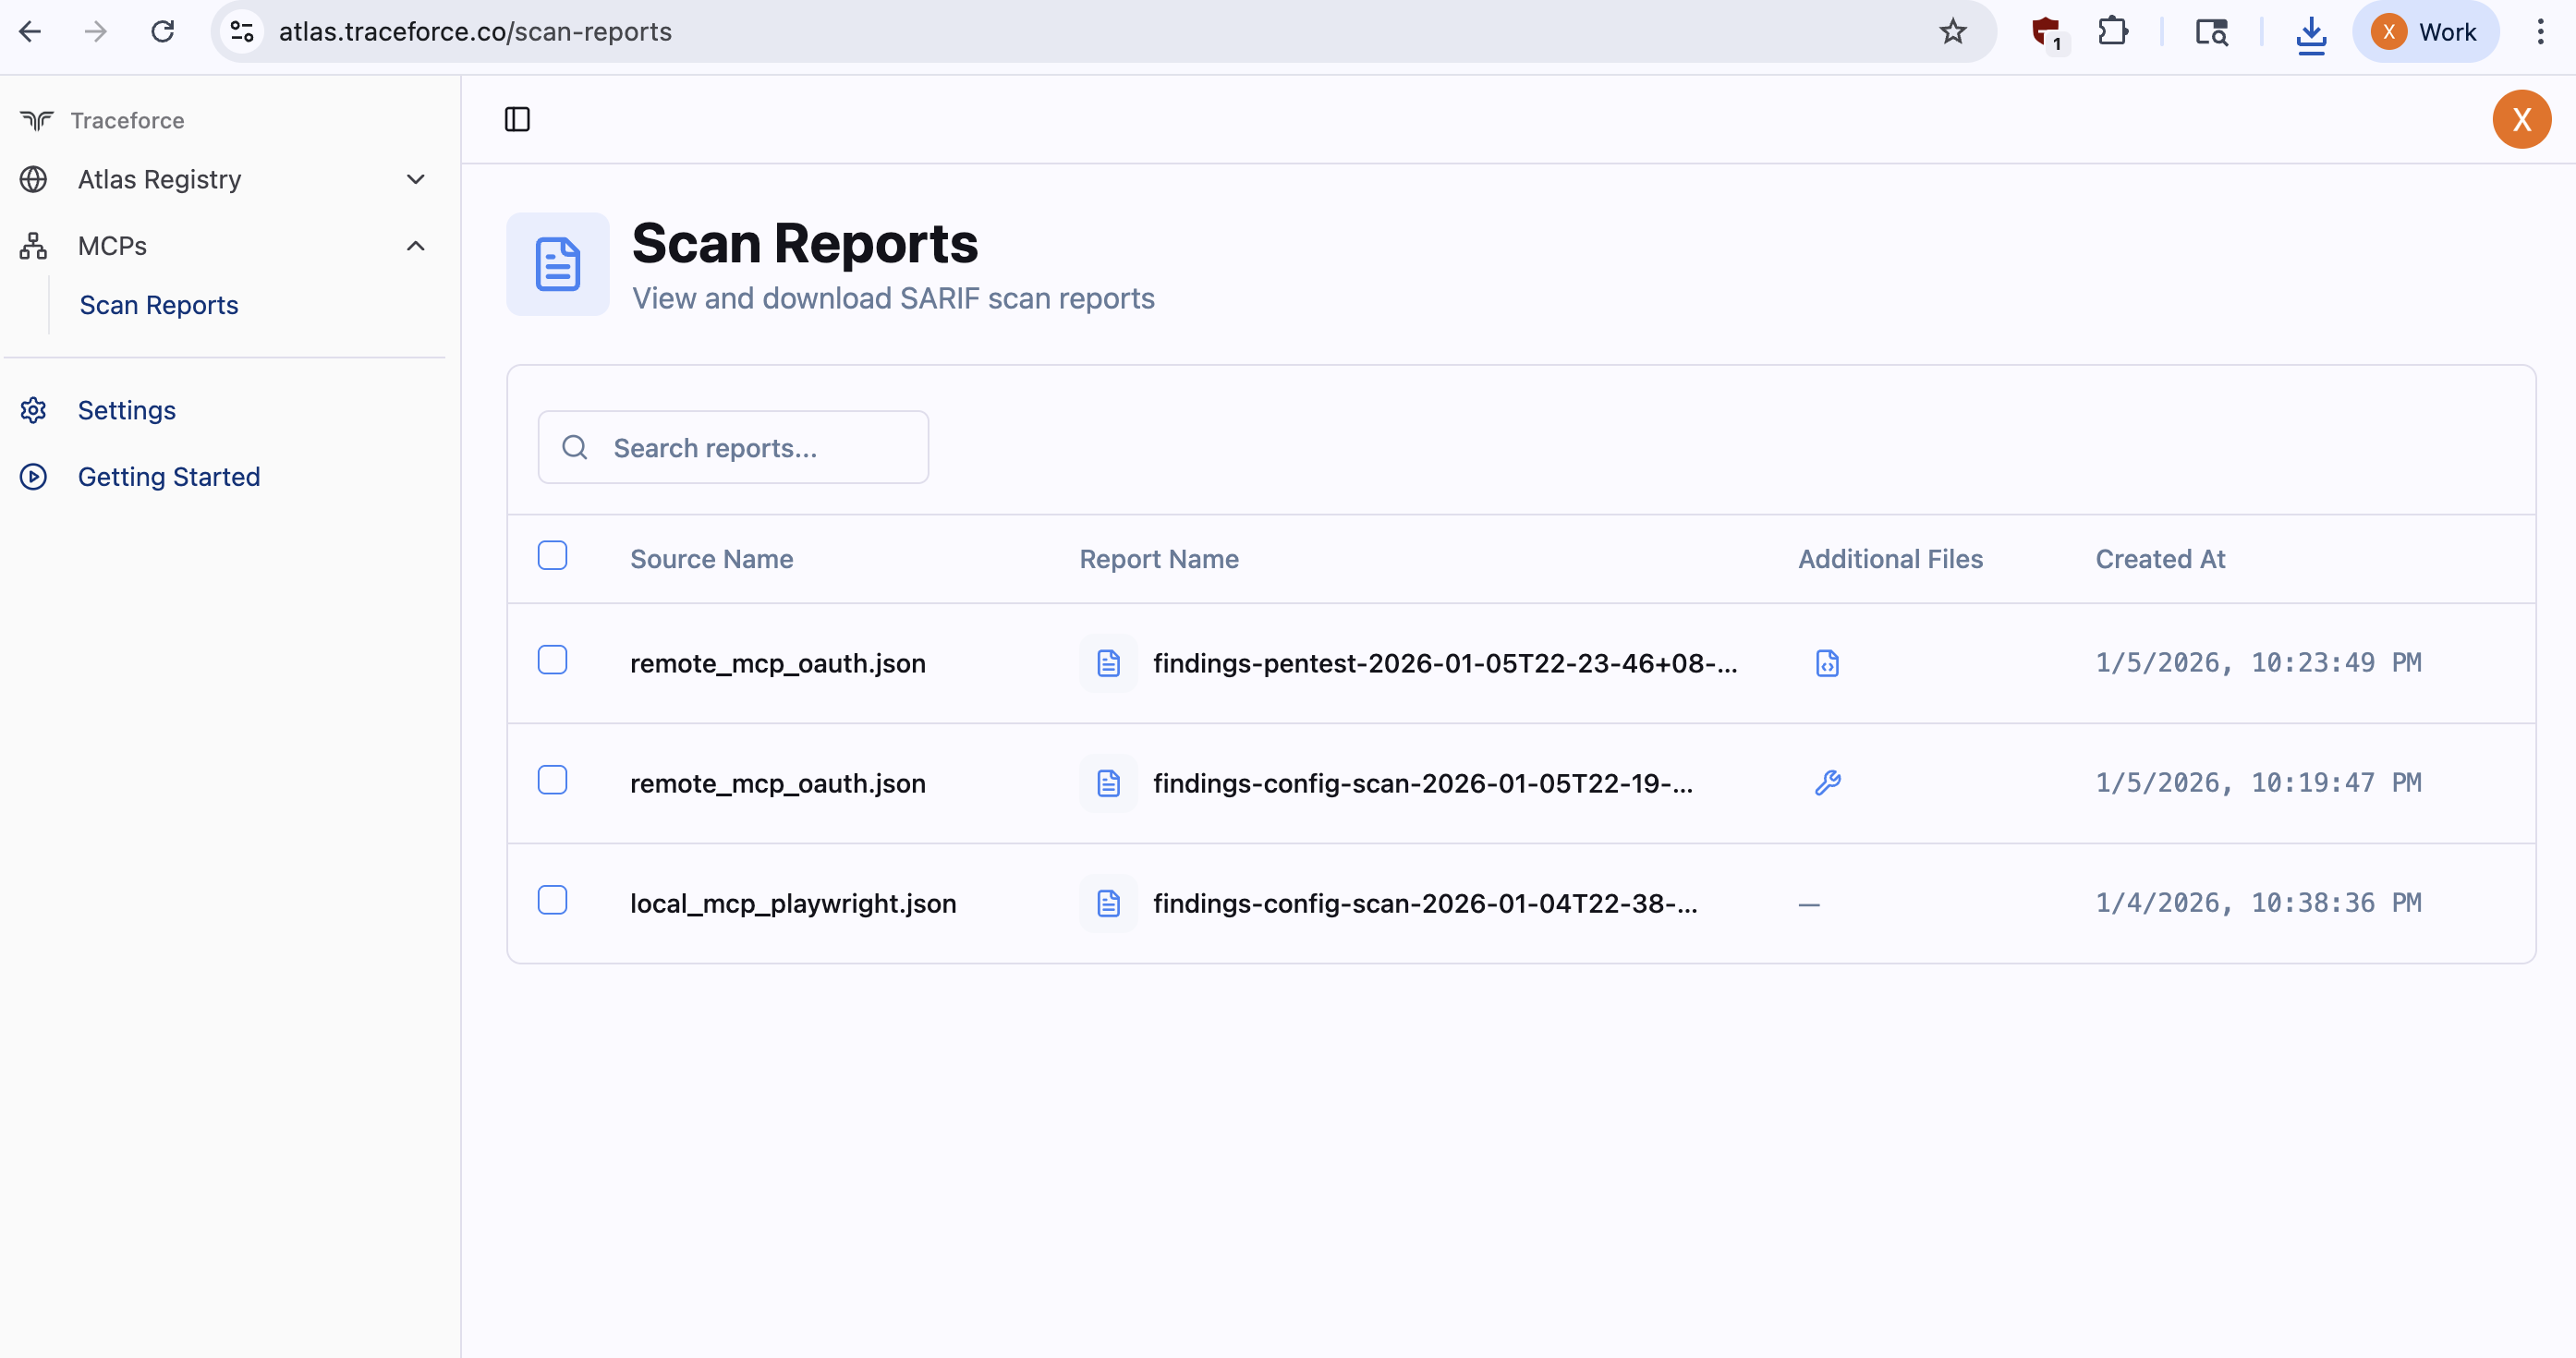 traceforce/mcp-xray
Unified security scanner for MCP servers with config, pentest, and repo-scan modes. Generates SARIF reports for CI/CD integration, detects secrets,…
 nuguardai/nuguard
opensource repo for validating agentic AI applications: redteam, behavior, supply-chain, static analysis
 s4dhulabs/vimana-framework
Vimana is a modular security framework for auditing Python APIs and Web applications. The plugin-based architecture enables security professionals to…
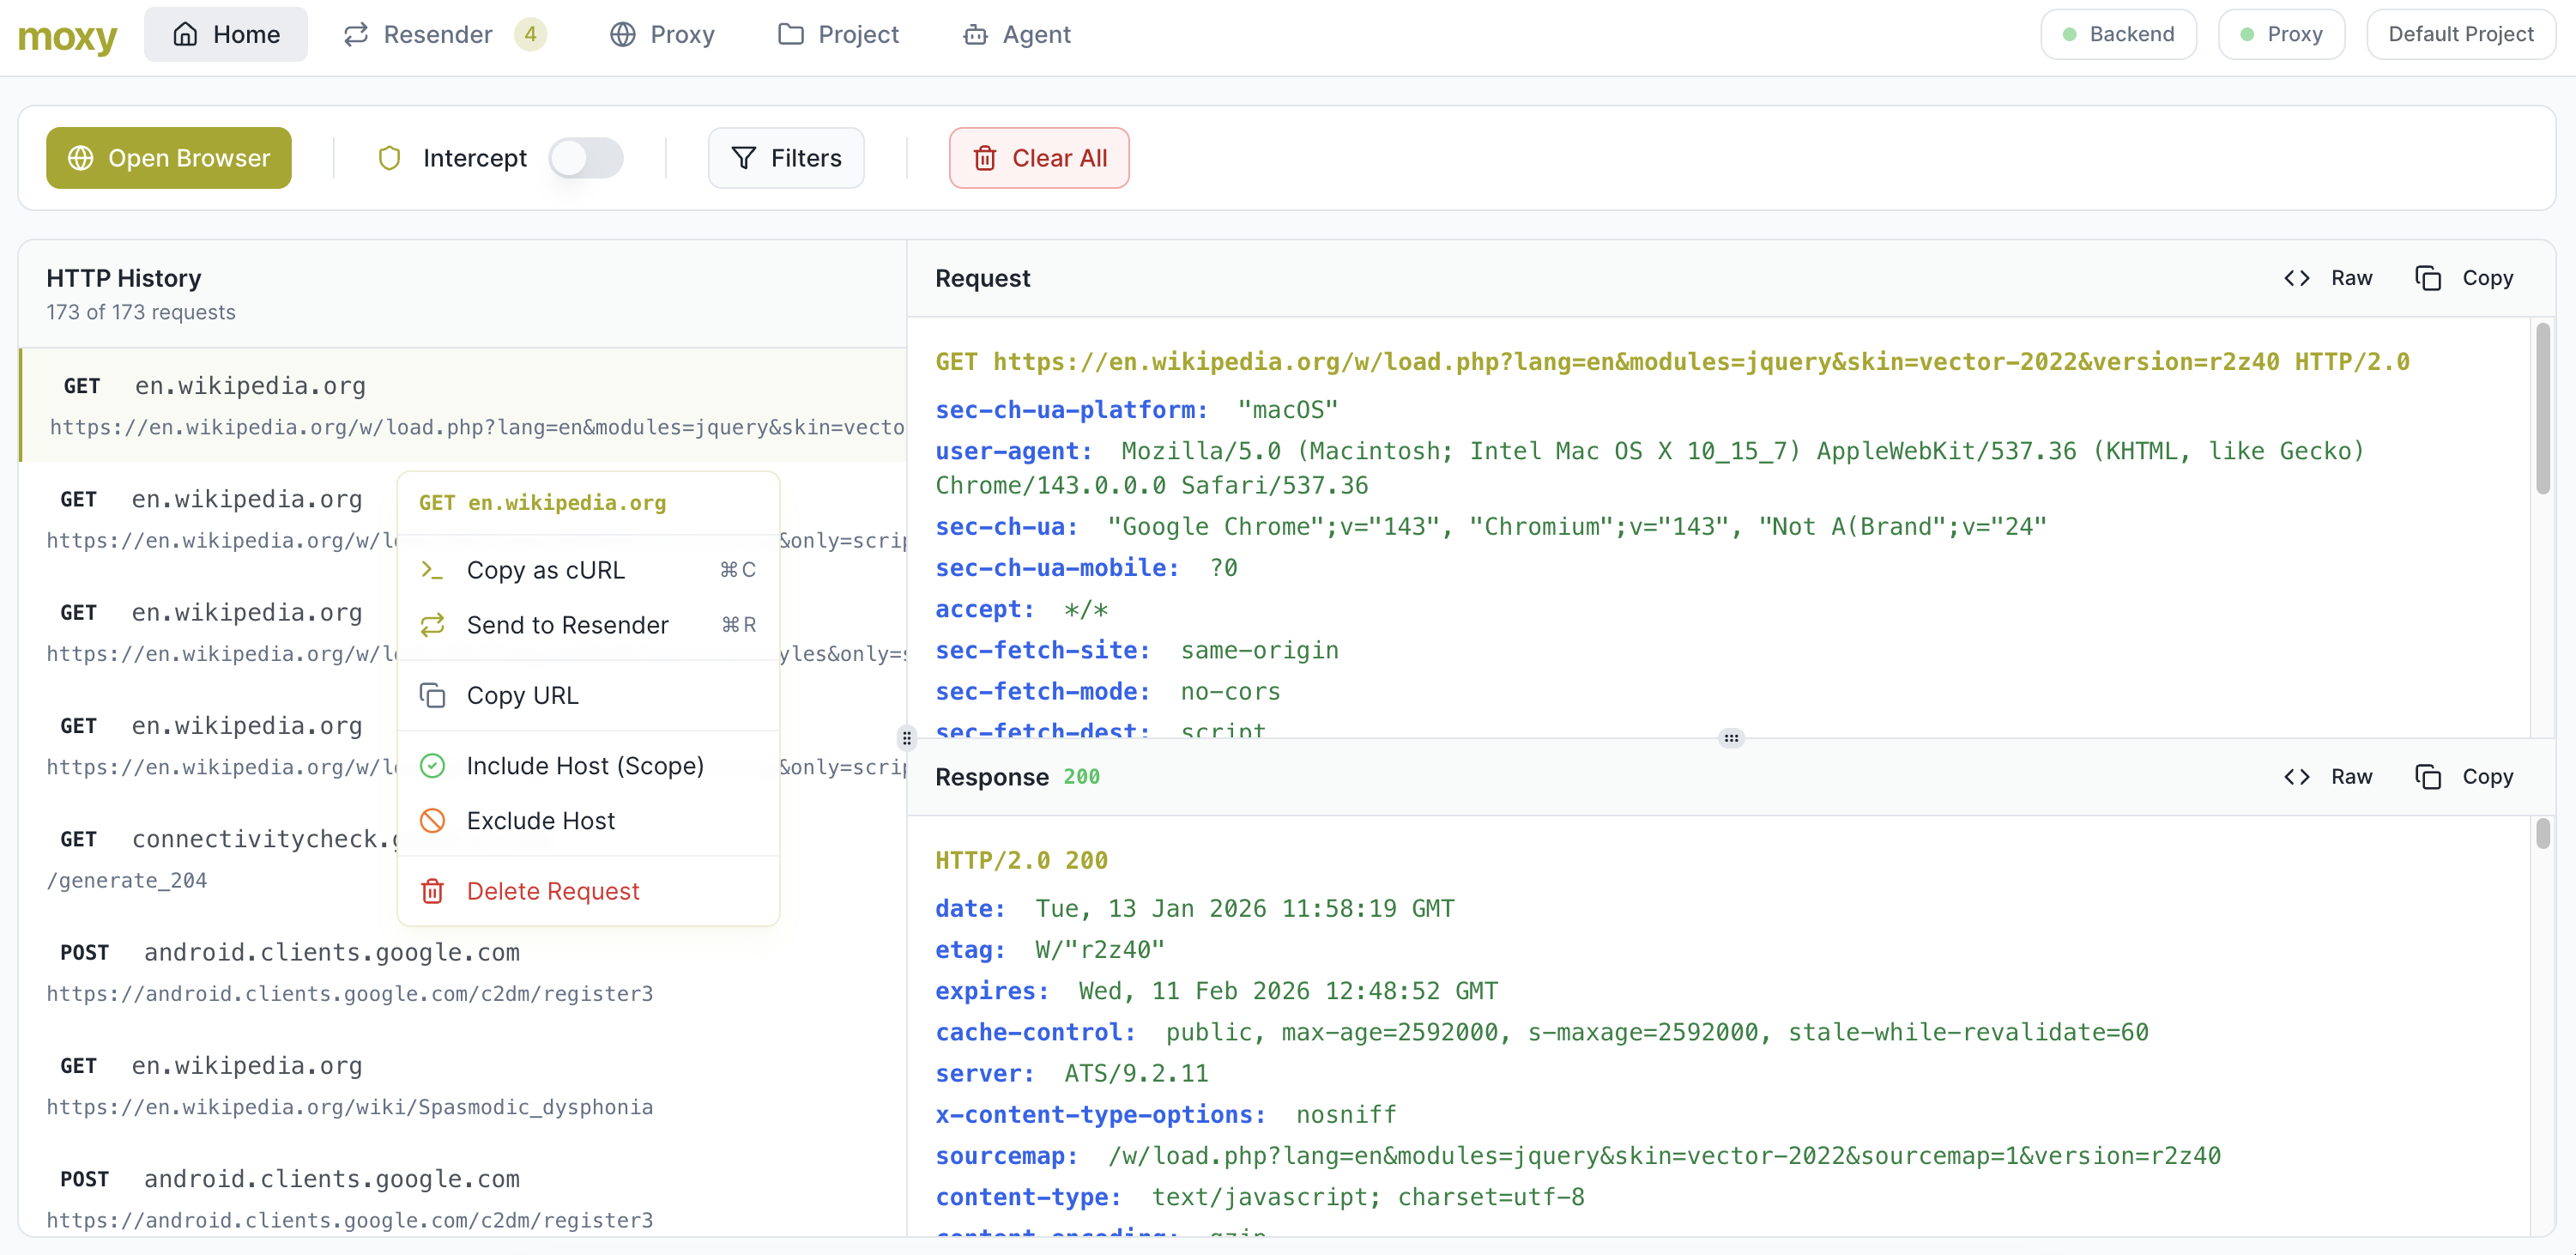 matank001/moxy
Moxy is an open-source DAST tool designed for modern web application security testing. It provides an easy-to-use interface with agentic capabilities…
 hackinglz/maps_scanner
MAPS cloud scanner and response parser for Microsoft Defender research.
 nccgroup/amfdser-ngng
A Burp Extender plugin, that will take deserialized AMF objects and encode them in XML using the Xtream library