
Archived
purpleteam-s2-containers
 purpleteam-labs/purpleteam-s2-containers
Stage two containers
cloud-securitycontainer-securitydevsecops+5
purpleteam-labs/purpleteam-s2-containersStage two containers

 zaproxy/zaproxy
Open-source web application security scanner for automated vulnerability detection, manual penetration testing, and API security testing with a…
 morpheuslord/quadrainspect
Modular Android APK security analysis framework integrating static, dynamic, and reverse engineering tools for comprehensive vulnerability assessment…
 ernw/androtickler
Penetration testing and auditing toolkit for Android apps.
 mandiant/commando-vm
Customizable Windows-based virtual machine distribution pre-packaged with offensive security tools for penetration testing and red teaming operations.
 stuxlabs/awe
adaptive agents for dynamic web penetration testing
 t0thkr1s/frida
Frida scripts for mobile application dynamic-analysis.
 horkimhab/cve-2026-39808
CVE-2026-39808 - Fortinet Sandbox - Draft
 horkimhab/cve-2026-39813
CVE-2026-39813 - Fortinet Sandbox - Draft
 use-tusk/tusk-cli
Automated testing suite with live traffic record and replay
 mitmproxy/mitmproxy
An interactive TLS-capable intercepting HTTP proxy for penetration testers and software developers.
 mobsf/mobile-security-framework-mobsf
Automated mobile application security testing framework for Android, iOS, and Windows. Performs static and dynamic analysis, malware detection, and…
 owasp/mastg
Comprehensive OWASP guide for mobile app security testing, reverse engineering, and verifying MASVS/MASWE weaknesses through static, dynamic, and…
 hellsender01/llmmap
Automated prompt injection testing framework for LLM-integrated applications with dual-LLM architecture.
 go-appsec/toolbox
Collaborative application security testing between humans and agents via CLI and MCP
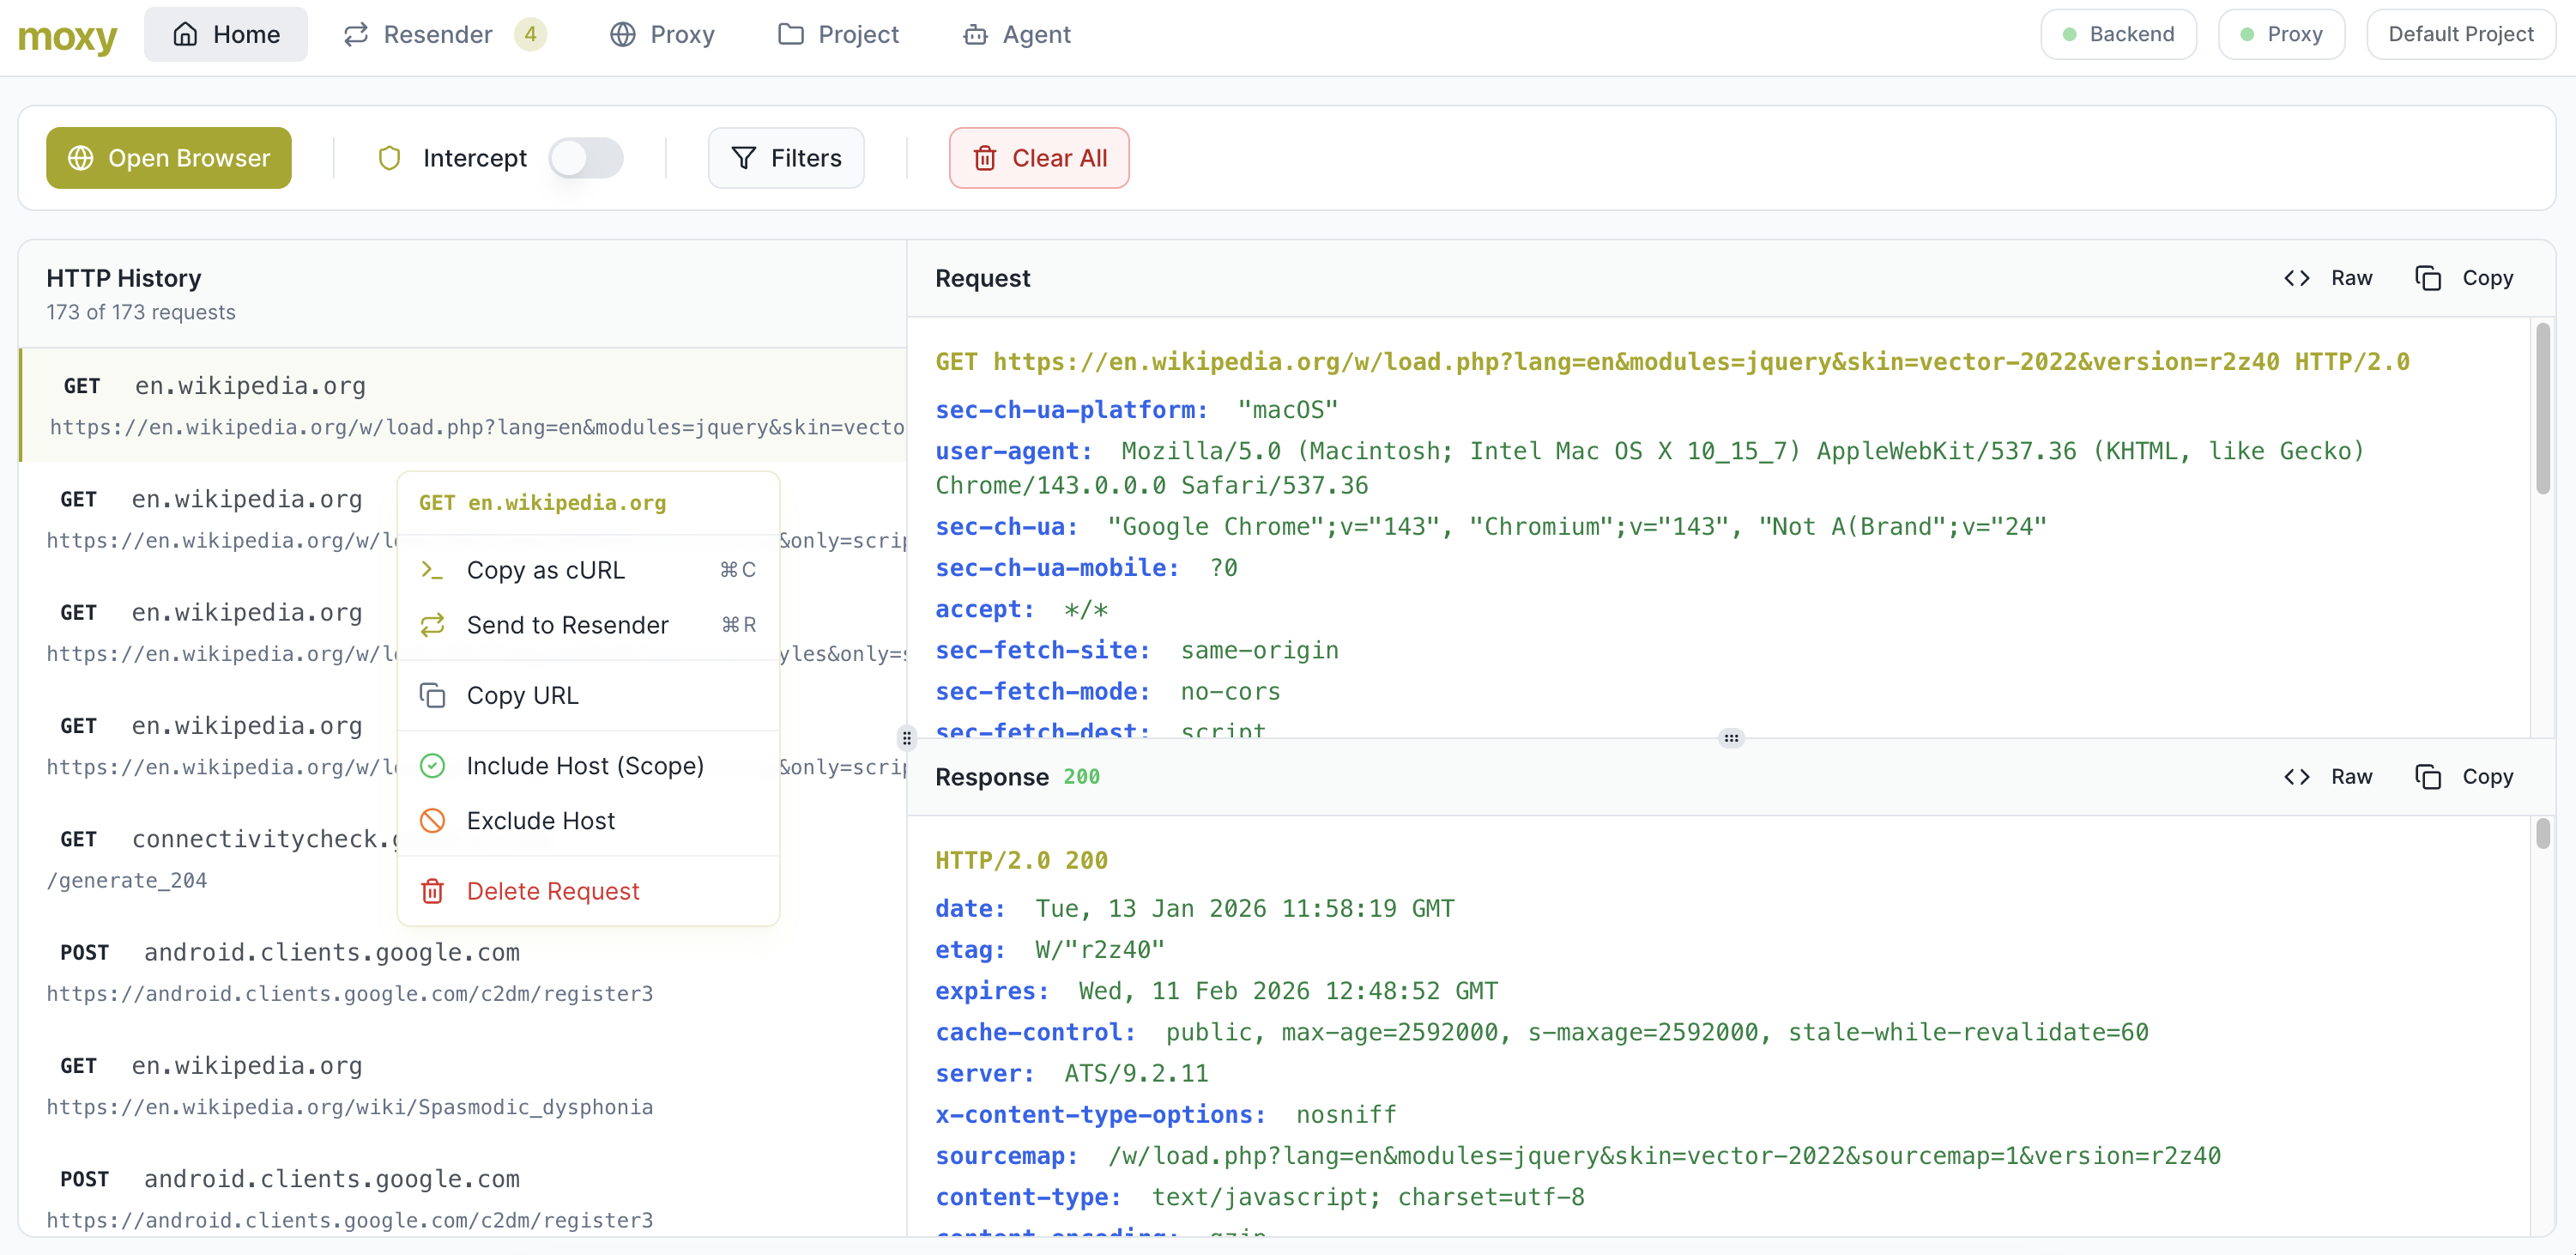 matank001/moxy
Moxy is an open-source DAST tool designed for modern web application security testing. It provides an easy-to-use interface with agentic capabilities…
 stuxctf/slythestx
Mobile app security auditing tool focused on automating SAST analysis, identifying underlying technologies (React Native, Flutter, Xamarin, native),…
 weirdmachine64/redom
A Burp Suite extension that brings full DOM rendering capabilities directly into Burp, enabling effective security testing of modern JavaScript-heavy…