DexLoader
 bend0us/dexloader
A demo Android project showcasing dynamic DEX loading using DexClassLoader, PathClassLoader, and in-memory execution. For educational purposes only.
android-securitybinary-exploitationdynamic-analysis-sandboxing+3
2
bend0us/dexloaderA demo Android project showcasing dynamic DEX loading using DexClassLoader, PathClassLoader, and in-memory execution. For educational purposes only.
 curtail-inc/hello-regrade-security
Find the vulnerability your tests were never written to catch. A ReGrade demo modeling CVE-2023-5968: catch a password-hash leak by comparing an app…
 gmh5225/frida-vmprotect-bypass
Frida script that bypasses VMProtect runtime protections on mobile platforms, enabling dynamic instrumentation and analysis of protected binaries.
 humoud/hooketh
A set of scripts that ease working with frida
 sahalll/cve-2024-54916
Frida-based proof-of-concept demonstrating authentication bypass in Telegram Android by hooking SharedConfig.checkPasscode to always return true,…
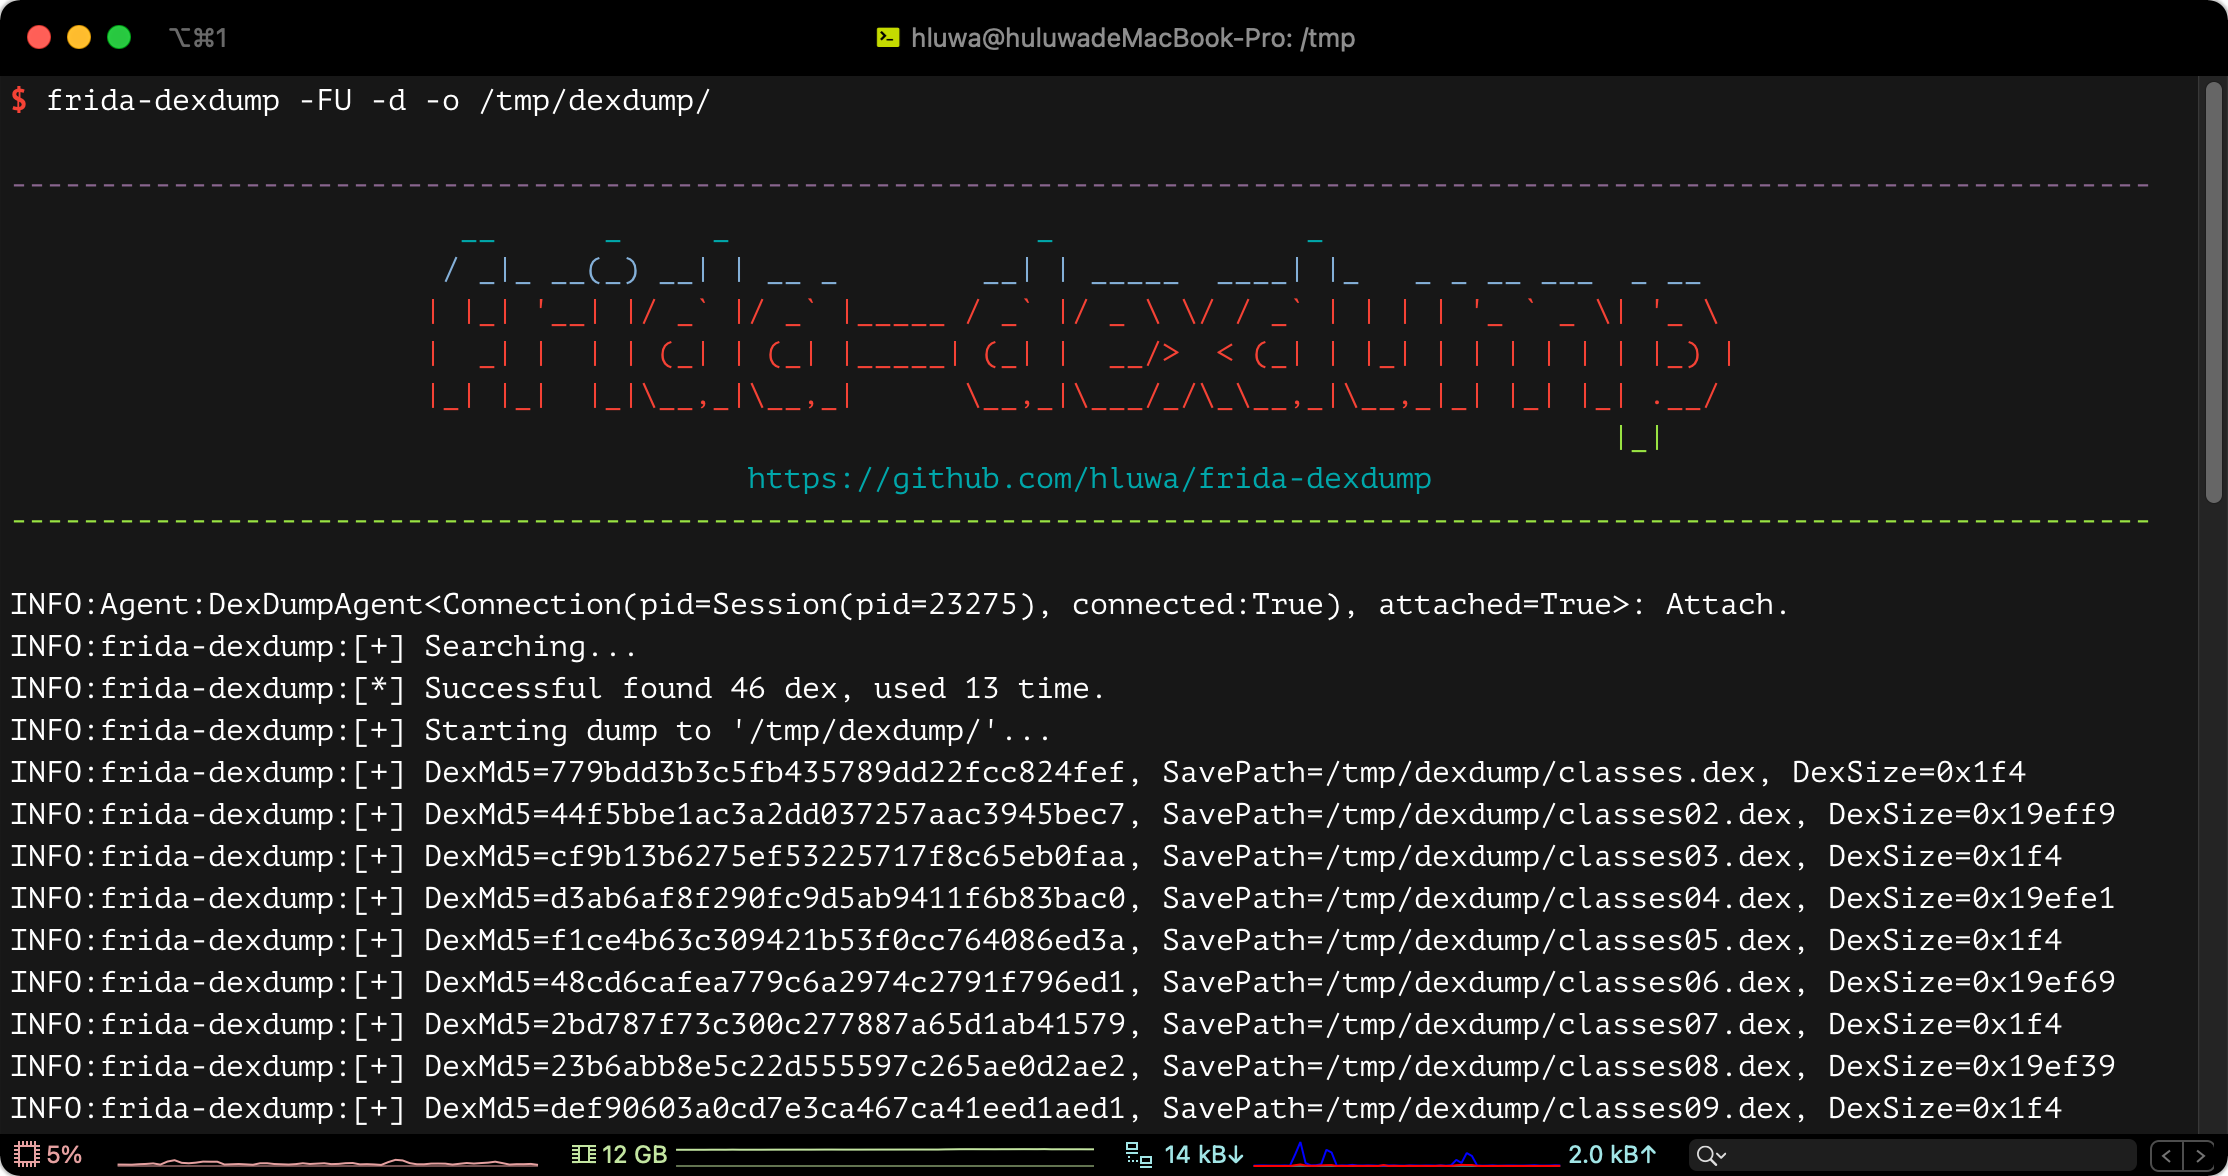 hluwa/frida-dexdump
A frida tool to dump dex in memory to support security engineers analyzing malware.
 claudiugeorgiu/obfuscapk
An automatic obfuscation tool for Android apps that works in a black-box fashion, supports advanced obfuscation features and has a modular…
 ptswarm/reflutter
Flutter Reverse Engineering Framework
 androidhooker/hooker
Hooker is an opensource project for dynamic analyses of Android applications. This project provides various tools and applications that can be use to…
 nighthawkk/jnisleuth-mcp
Automated Android JNI RegisterNatives recovery, stripped ARM64 .so type reconstruction, OLLVM BR X8 deobfuscator, and universal LLM/MCP bridge for…
 superandroidanalyzer/super
Secure, Unified, Powerful and Extensible Rust Android Analyzer
 google/martian
Martian is a library for building custom HTTP/S proxies
 1ultimat3/badintent
Intercept, modify, repeat and attack Android's Binder transactions using Burp Suite
 andreafioraldi/frida-fuzzer
This experimetal fuzzer is meant to be used for API in-memory fuzzing.
 jankammerath/bogusmips
Forensic analytics for disassembly, reassembly, reverse engineering and auditing of Android apps
 purpleteam-labs/purpleteam-s2-containers
Stage two containers