Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
141 results
hello-ReGrade-security preview

hello-ReGrade-security

GitHubcurtail-inc/hello-regrade-security

Find the vulnerability your tests were never written to catch. A ReGrade demo modeling CVE-2023-5968: catch a password-hash leak by comparing an app…

api-security-testingcryptographydynamic-analysis-sandboxing+6
2 months ago
rendering-code-outside-the-sandbox-cve-2026-76036-dawn-webgpu-buffer-overflow-in-chrome-on-android preview

rendering-code-outside-the-sandbox-cve-2026-76036-dawn-webgpu-buffer-overflow-in-chrome-on-android

GitHubhunt-benito/rendering-code-outside-the-sandbox-cve-2026-76036-dawn-webgpu-buffer-overflow-in-chrome-on-android

Differential detection harness for CVE-2026-76036, a Dawn WebGPU heap buffer overflow in Chrome on Android. Probes vulnerable depth/stencil texture…

android-securitybinary-analysisdefensive-tools+3
12 months ago
Frida-VMProtect-Bypass preview

Frida-VMProtect-Bypass

GitHubgmh5225/frida-vmprotect-bypass

Frida script that bypasses VMProtect runtime protections on mobile platforms, enabling dynamic instrumentation and analysis of protected binaries.

android-securitybinary-exploitationdynamic-analysis-sandboxing+3
23 years ago
Hooketh preview

Hooketh

GitHubhumoud/hooketh

A set of scripts that ease working with frida

android-securitydebuggersdynamic-analysis-sandboxing+2
26 years ago
CVE-2024-54916 preview

CVE-2024-54916

GitHubsahalll/cve-2024-54916

Frida-based proof-of-concept demonstrating authentication bypass in Telegram Android by hooking SharedConfig.checkPasscode to always return true,…

android-securityauthenticationbinary-analysis+4
1 year ago
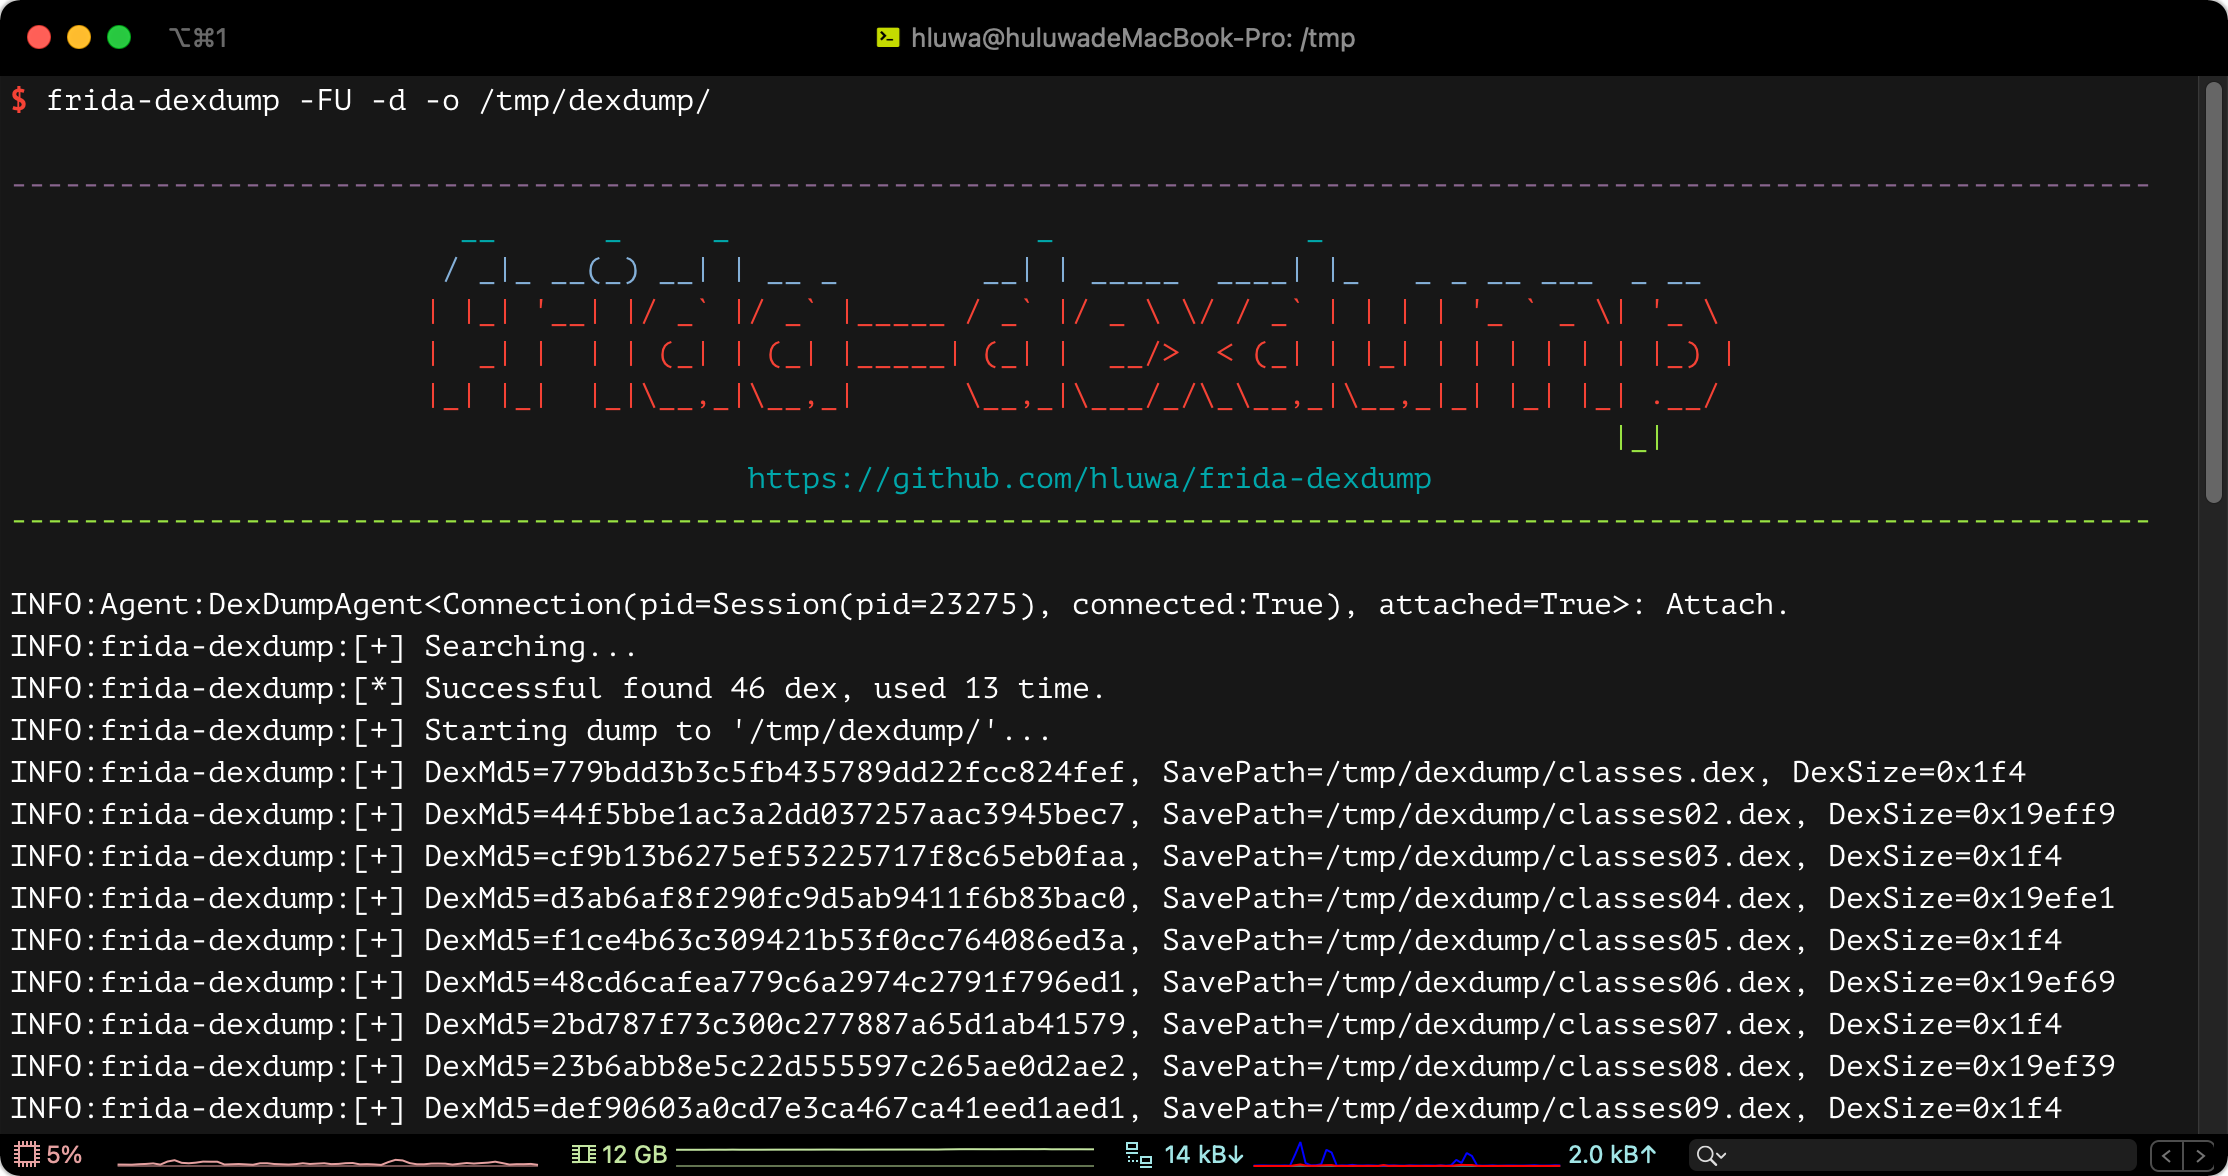
frida-dexdump preview
Archived

frida-dexdump

GitHubhluwa/frida-dexdump

A frida tool to dump dex in memory to support security engineers analyzing malware.

android-securitybinary-analysisdynamic-analysis-sandboxing+5
4.6k3 years ago
Obfuscapk preview
Archived

Obfuscapk

GitHubclaudiugeorgiu/obfuscapk

An automatic obfuscation tool for Android apps that works in a black-box fashion, supports advanced obfuscation features and has a modular…

android-securitydynamic-analysis-sandboxingeducation+4
1.3k2 years ago
reFlutter preview
Archived

reFlutter

GitHubptswarm/reflutter

Flutter Reverse Engineering Framework

android-securitybinary-analysisdynamic-analysis-sandboxing+4
1.5k4 years ago
hooker preview
Archived

hooker

GitHubandroidhooker/hooker

Hooker is an opensource project for dynamic analyses of Android applications. This project provides various tools and applications that can be use to…

android-securityapi-security-testingdynamic-analysis-sandboxing+3
41510 years ago
JNISleuth-MCP preview

JNISleuth-MCP

GitHubnighthawkk/jnisleuth-mcp

Automated Android JNI RegisterNatives recovery, stripped ARM64 .so type reconstruction, OLLVM BR X8 deobfuscator, and universal LLM/MCP bridge for…

ai-assisted-reversingandroid-securitybinary-analysis+5
26 days ago
appmon preview
Archived

appmon

GitHubdpnishant/appmon

Documentation:

android-securitybinary-analysisdebuggers+6
1.6k3 years ago
super preview
Archived

super

GitHubsuperandroidanalyzer/super

Secure, Unified, Powerful and Extensible Rust Android Analyzer

android-securitycode-analysisdynamic-analysis-sandboxing+4
4286 years ago
BadIntent preview
Archived

BadIntent

GitHub1ultimat3/badintent

Intercept, modify, repeat and attack Android's Binder transactions using Burp Suite

android-securitydynamic-analysis-sandboxingexploitation+4
3229 years ago
frida-fuzzer preview
Archived

frida-fuzzer

GitHubandreafioraldi/frida-fuzzer

This experimetal fuzzer is meant to be used for API in-memory fuzzing.

api-security-testingbinary-analysisdynamic-analysis-sandboxing+3
5776 years ago
BogusMips preview

BogusMips

GitHubjankammerath/bogusmips

Forensic analytics for disassembly, reassembly, reverse engineering and auditing of Android apps

ai-assisted-reversingandroid-securitybinary-analysis+8
43 days ago
Previous1…78Next