Archived
Obfuscapk
 claudiugeorgiu/obfuscapk
An automatic obfuscation tool for Android apps that works in a black-box fashion, supports advanced obfuscation features and has a modular…
android-securitydynamic-analysis-sandboxingeducation+4
 angr/angr
A powerful and user-friendly binary analysis platform!
 stefan2200/aparoid
Static and dynamic Android application security analysis
 kishorbal/deep-c
Android deeplink misconfiguration detector and exploitation tool
 charles2gan/gda-android-reversing-tool
the fastest and most powerful android decompiler(native tool working without Java VM) for the APK, DEX, ODEX, OAT, JAR, AAR, and CLASS file. which…
 federicodotta/brida
The new bridge between Burp Suite and Frida!
 honeynet/apkinspector
APKinspector is a powerful GUI tool for analysts to analyze the Android applications.
 maoabc/nmmp
dex-vm used to protect the android classes.dex file
 saffron-health/libretto
The AI toolkit for building reliable browser automations
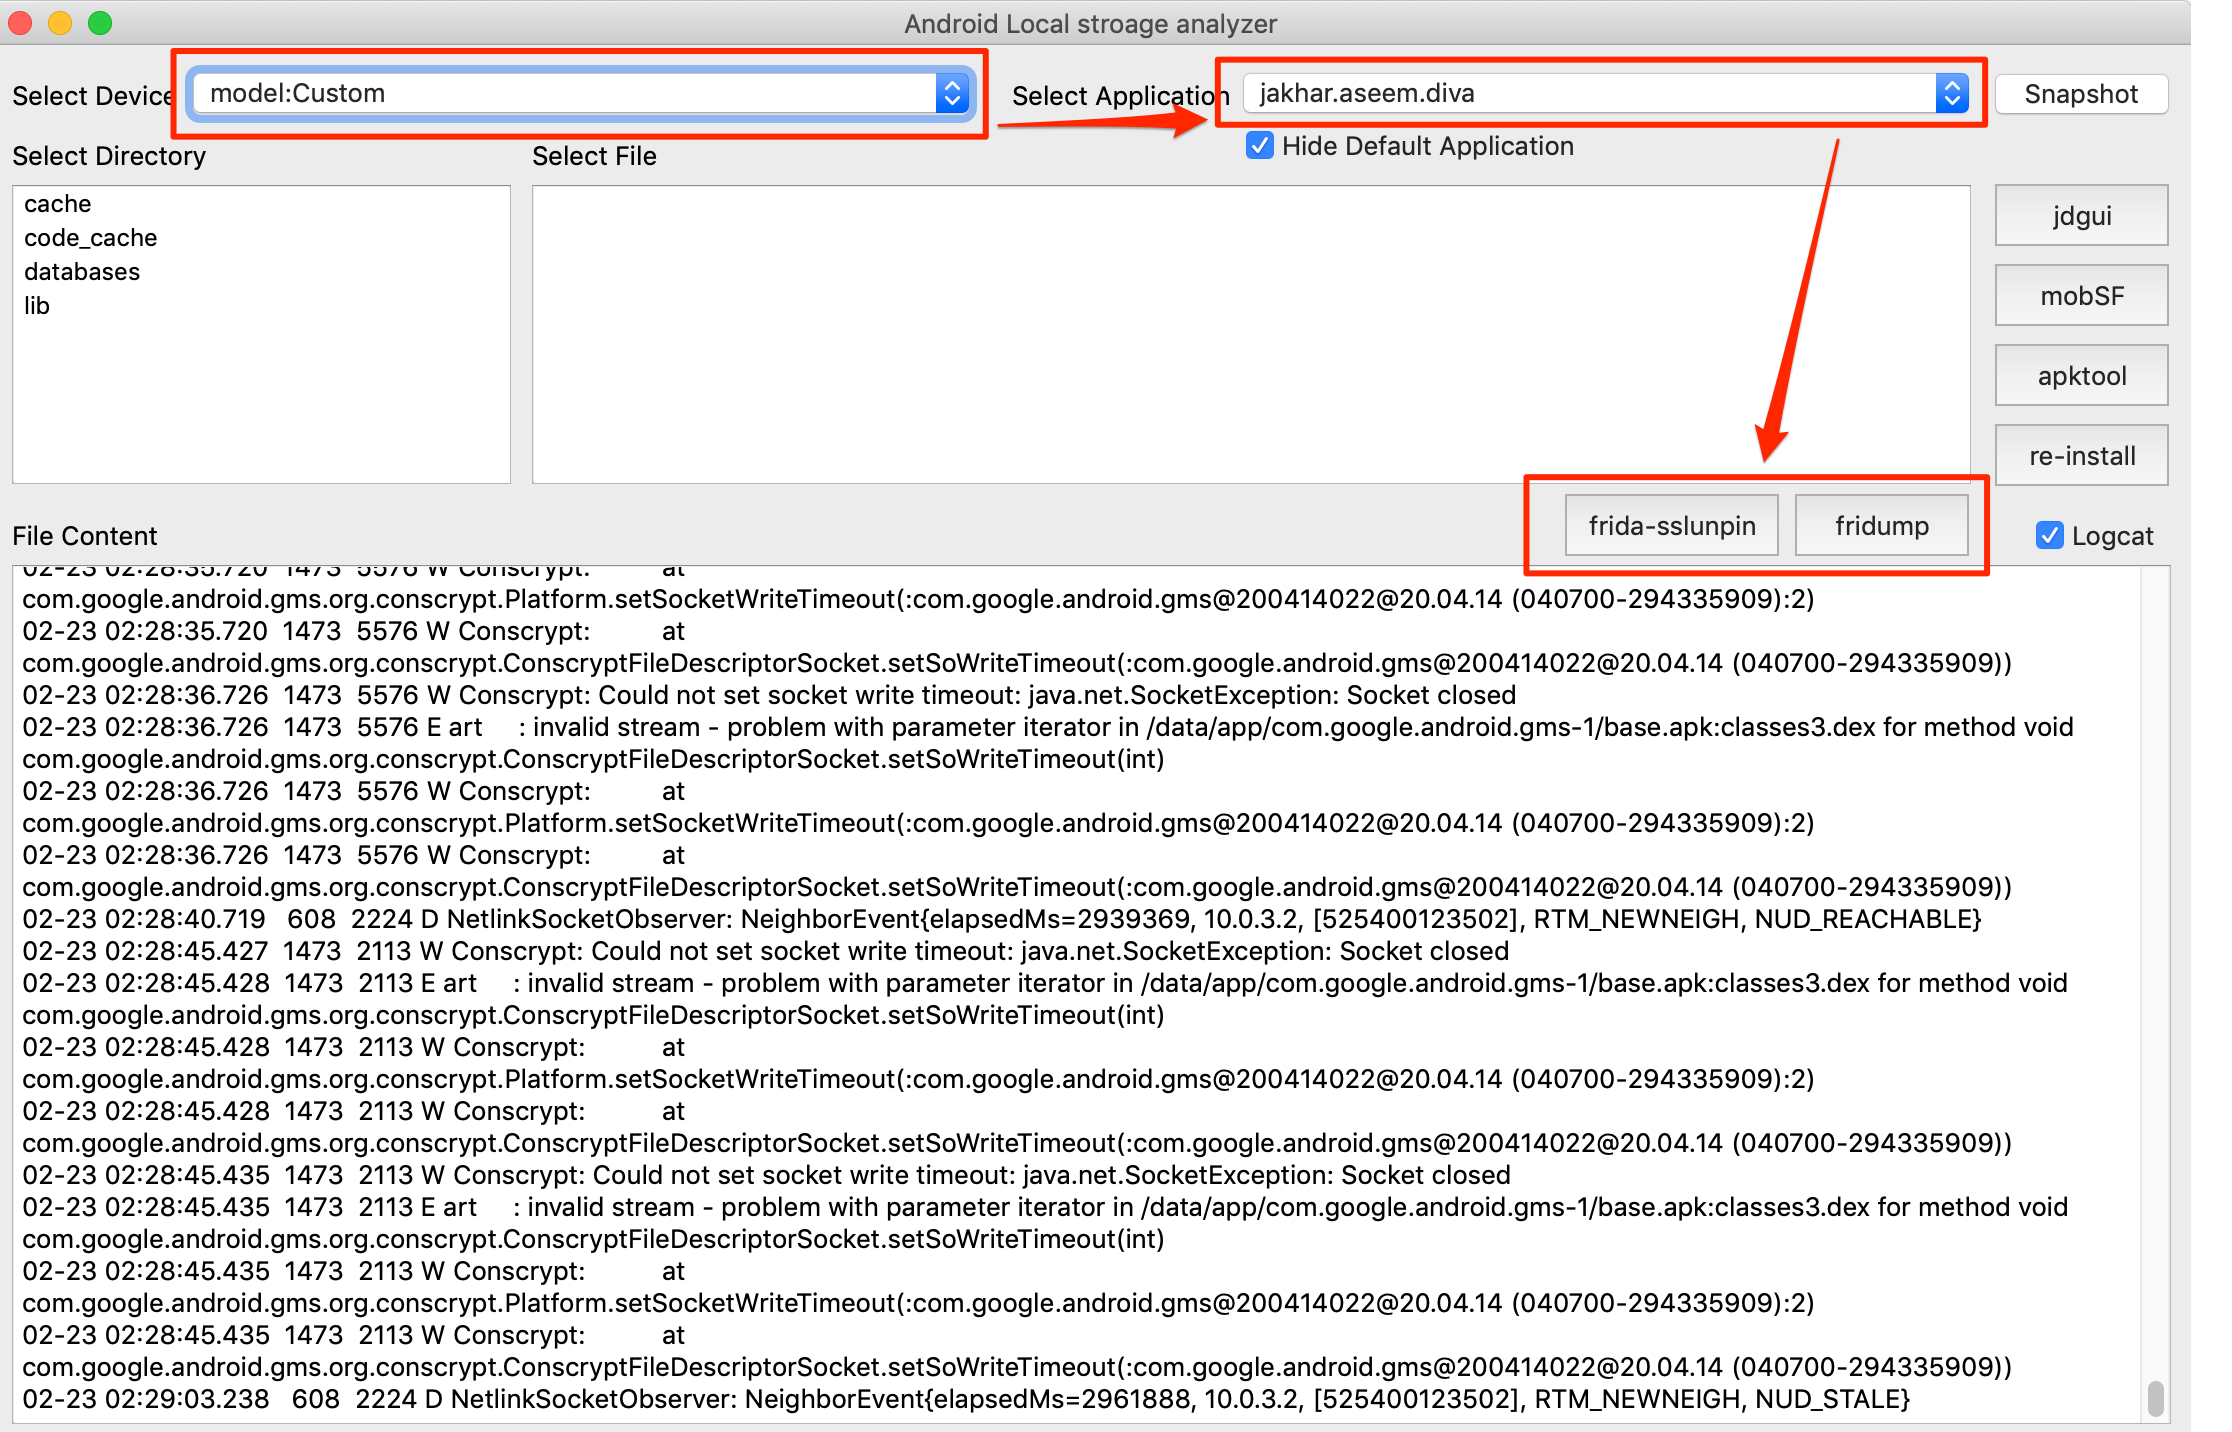 notsosecure/android_application_analyzer
The tool is used to analyze the content of the android application in local storage.
 amd2g2zz/kunglao-agent
The reverse-engineering expert agent: plans its own analysis path, derives every fact from raw evidence, and converges under mechanical verification…
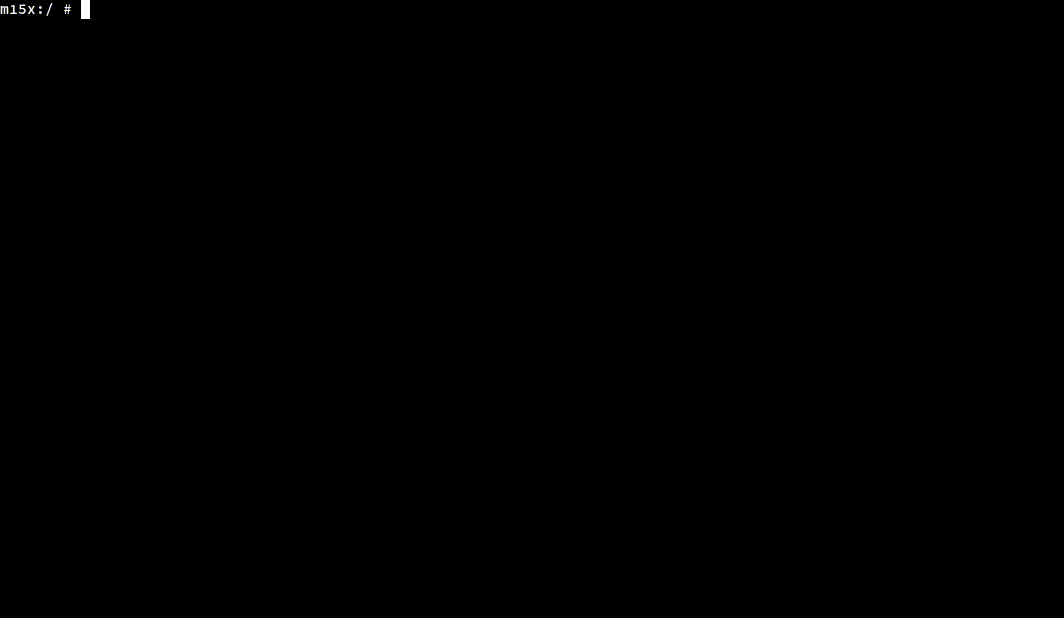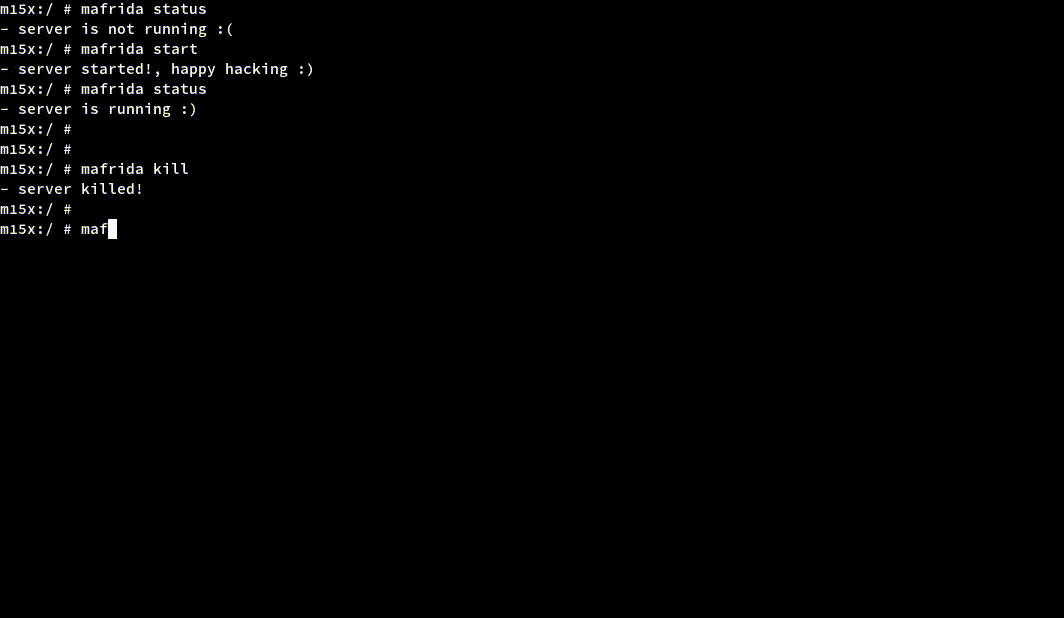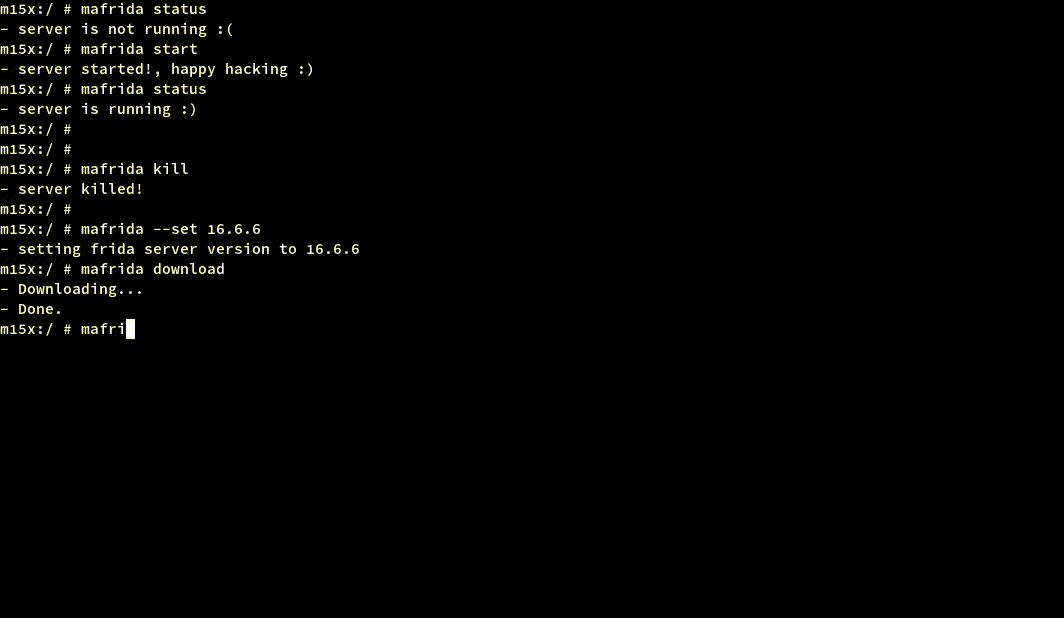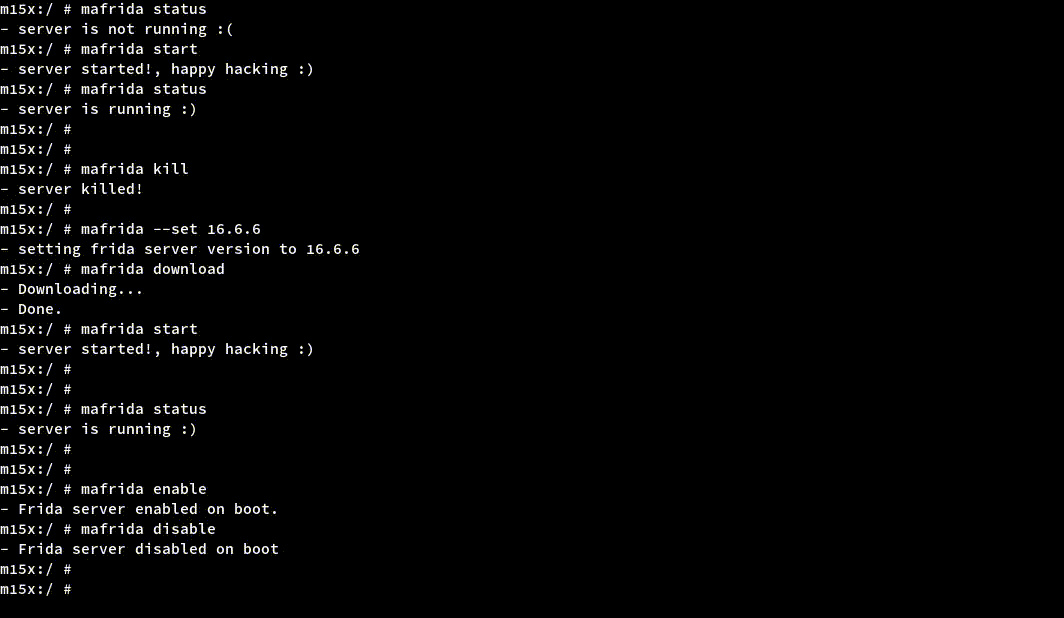 theshinigami/mafrida
A Magisk module that simplifies running the Frida server on Android, with easy management commands to download specific versions, enable or disable…
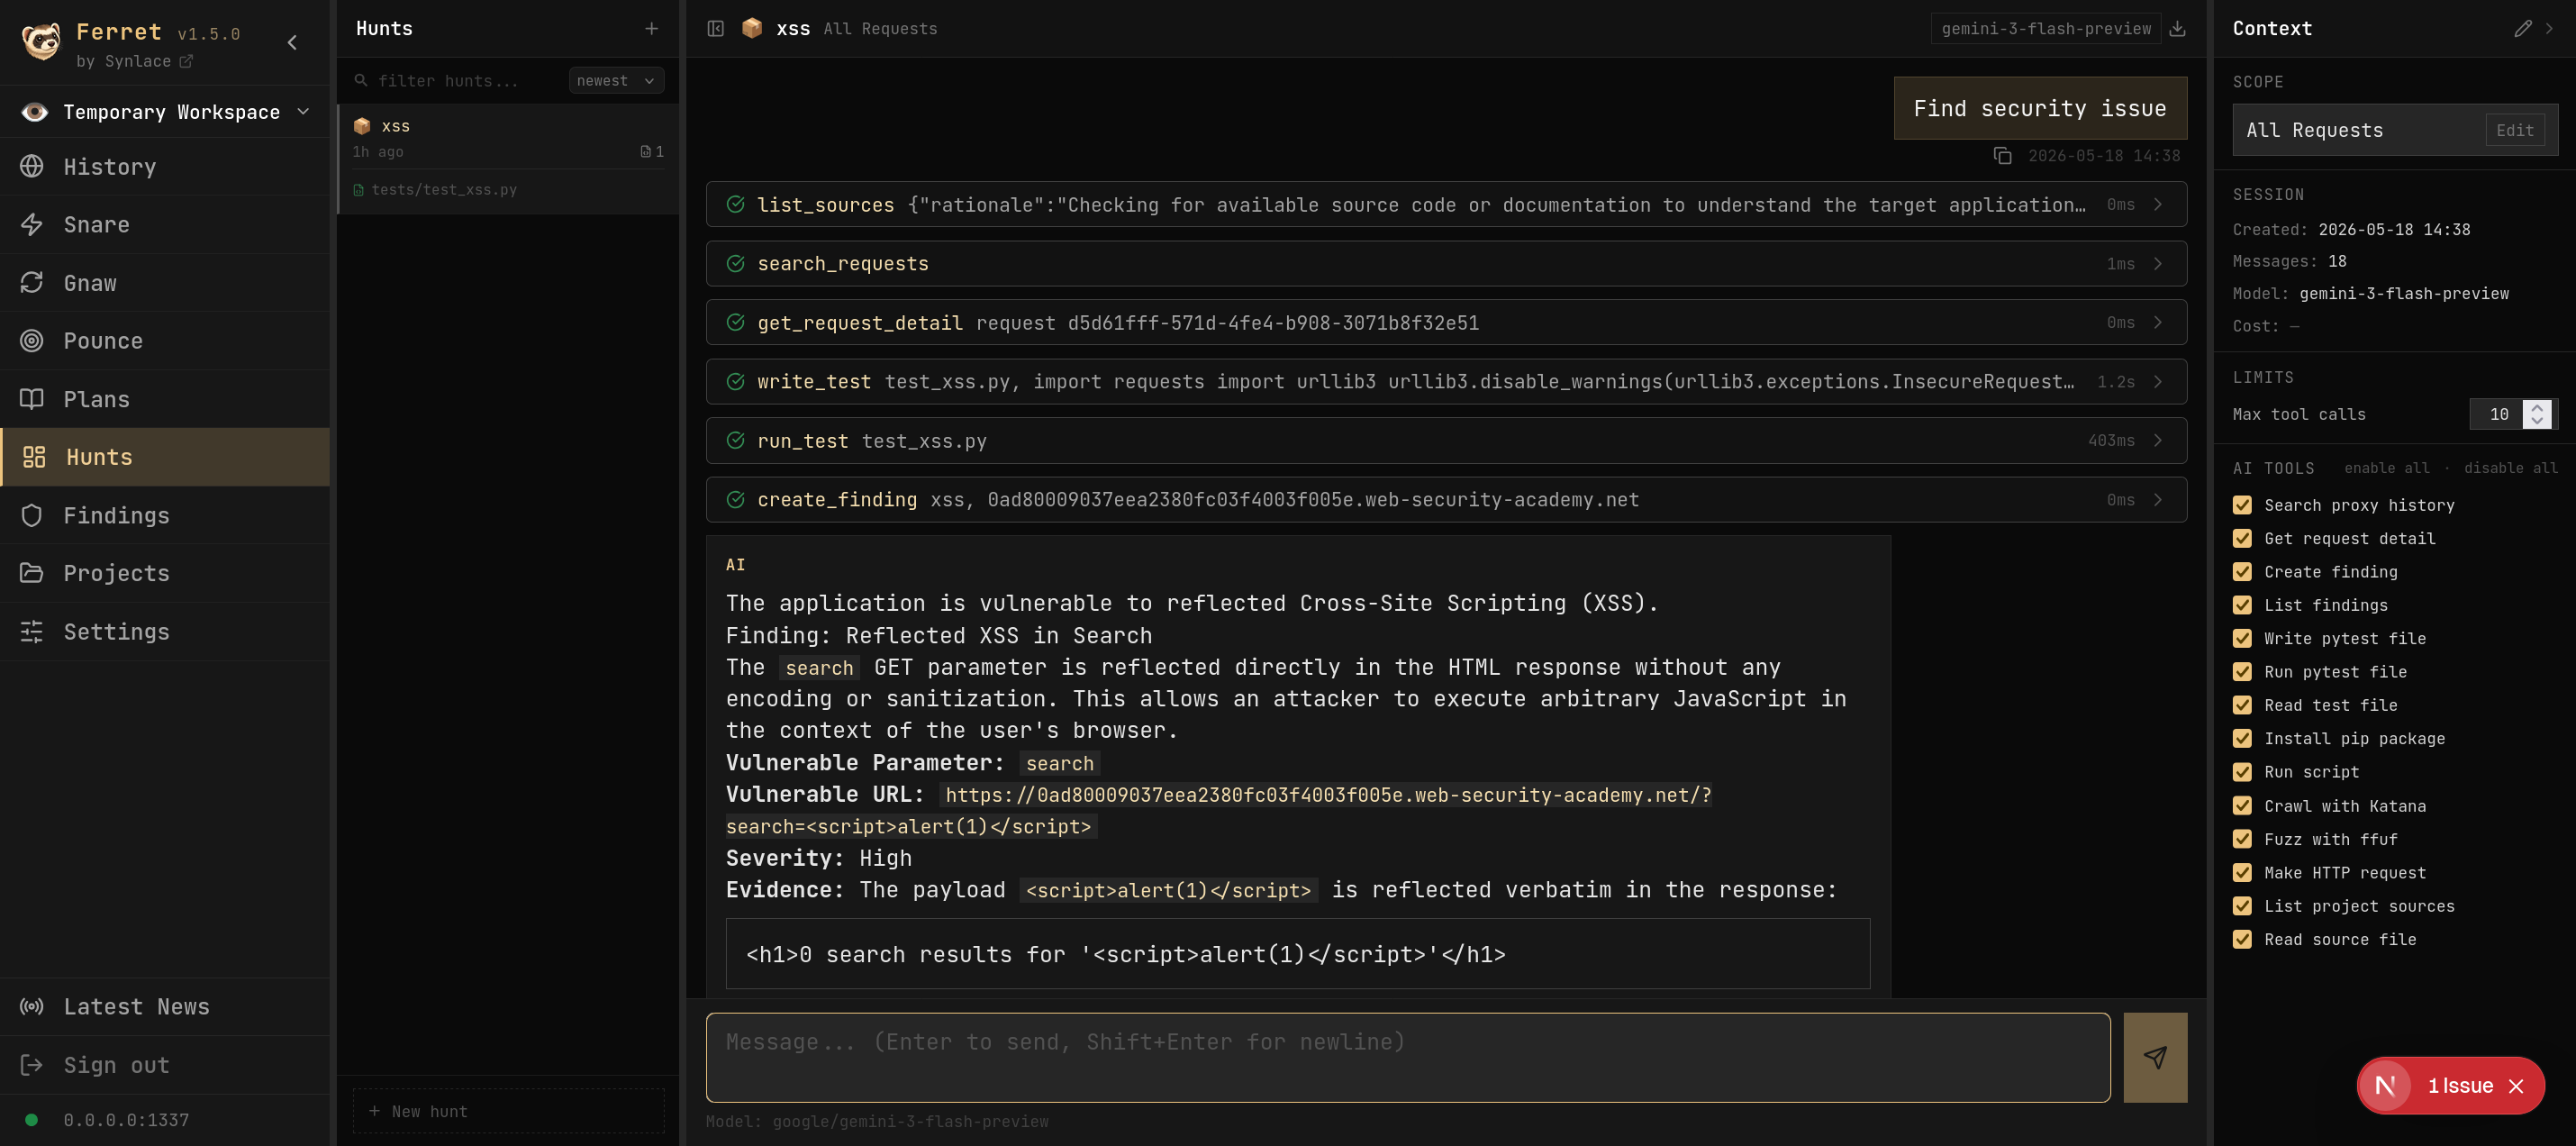 synlace/ferret
The collaborative web app pentest suite
 nccgroup/amfdser-ngng
A Burp Extender plugin, that will take deserialized AMF objects and encode them in XML using the Xtream library
 veridiff/veridiff
Dynamic branch-divergence finder for native code -- traces two Frida executions and finds the exact instruction where they diverge.
 hunt-benito/the-callback-that-outlived-the-page-cve-2026-78997-uc-browser-android-universal-xss
PoC for CVE-2026-78997, a Universal XSS in UC Browser for Android. Includes a crafted URL builder, a callback-dispatch oracle, and Frida hooks to…
 curtail-inc/hello-regrade-security
Find the vulnerability your tests were never written to catch. A ReGrade demo modeling CVE-2023-5968: catch a password-hash leak by comparing an app…