
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
75 results
r2web preview

r2web

GitHubradareorg/r2web

Access radare2 from anywhere, anytime.

binary-analysisdebuggersdynamic-analysis-sandboxing+2
5128 days ago
kunglao-agent preview

kunglao-agent

GitHubamd2g2zz/kunglao-agent

The reverse-engineering expert agent: plans its own analysis path, derives every fact from raw evidence, and converges under mechanical verification…
ai-assisted-reversingandroid-securitybinary-analysis+8
5615 days ago
firmware-workshop preview

firmware-workshop

GitHubonekey-sec/firmware-workshop

In this workshop session, we will extract firmware from an EV charger, dig into the firmware, and eventually emulate it so we can interact with the…
binary-analysisdynamic-analysis-sandboxingeducation+5
594 months ago
usbsnoop preview

usbsnoop

GitHubyeet-src/usbsnoop

Live, system-wide USB transfer sniffer in eBPF — decodes USB traffic inline (control SETUP, SCSI, HID) from two universal URB hooks. No usbmon, no…
debuggersdynamic-analysis-sandboxingembedded-systems-security+7
852 months ago
Nemesis preview

Nemesis

GitHubzypherion-technologies/nemesis

.NET process monitor that hooks CLR at the native layer, dumps reflective assemblies from memory, and checks AMSI/ETW integrity vs on disk binaries.
defensive-toolsdynamic-analysis-sandboxingmalware-analysis+2
4123 days ago
vmsan preview

vmsan

GitHubangelorc/vmsan

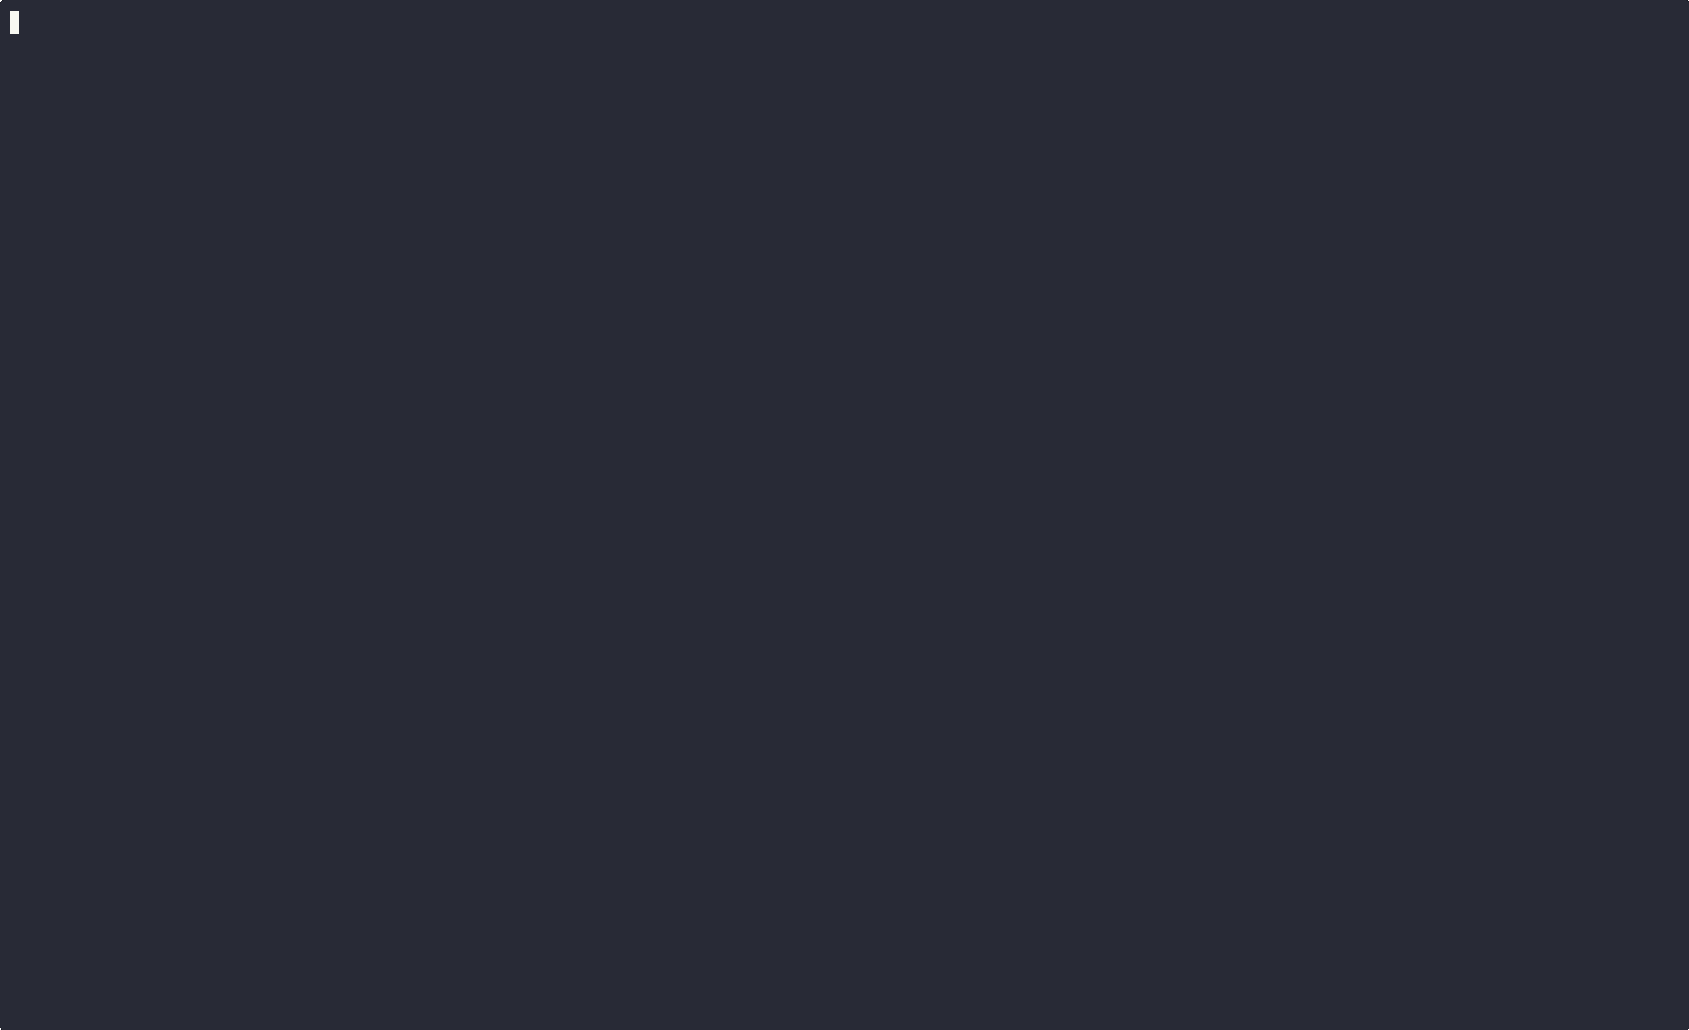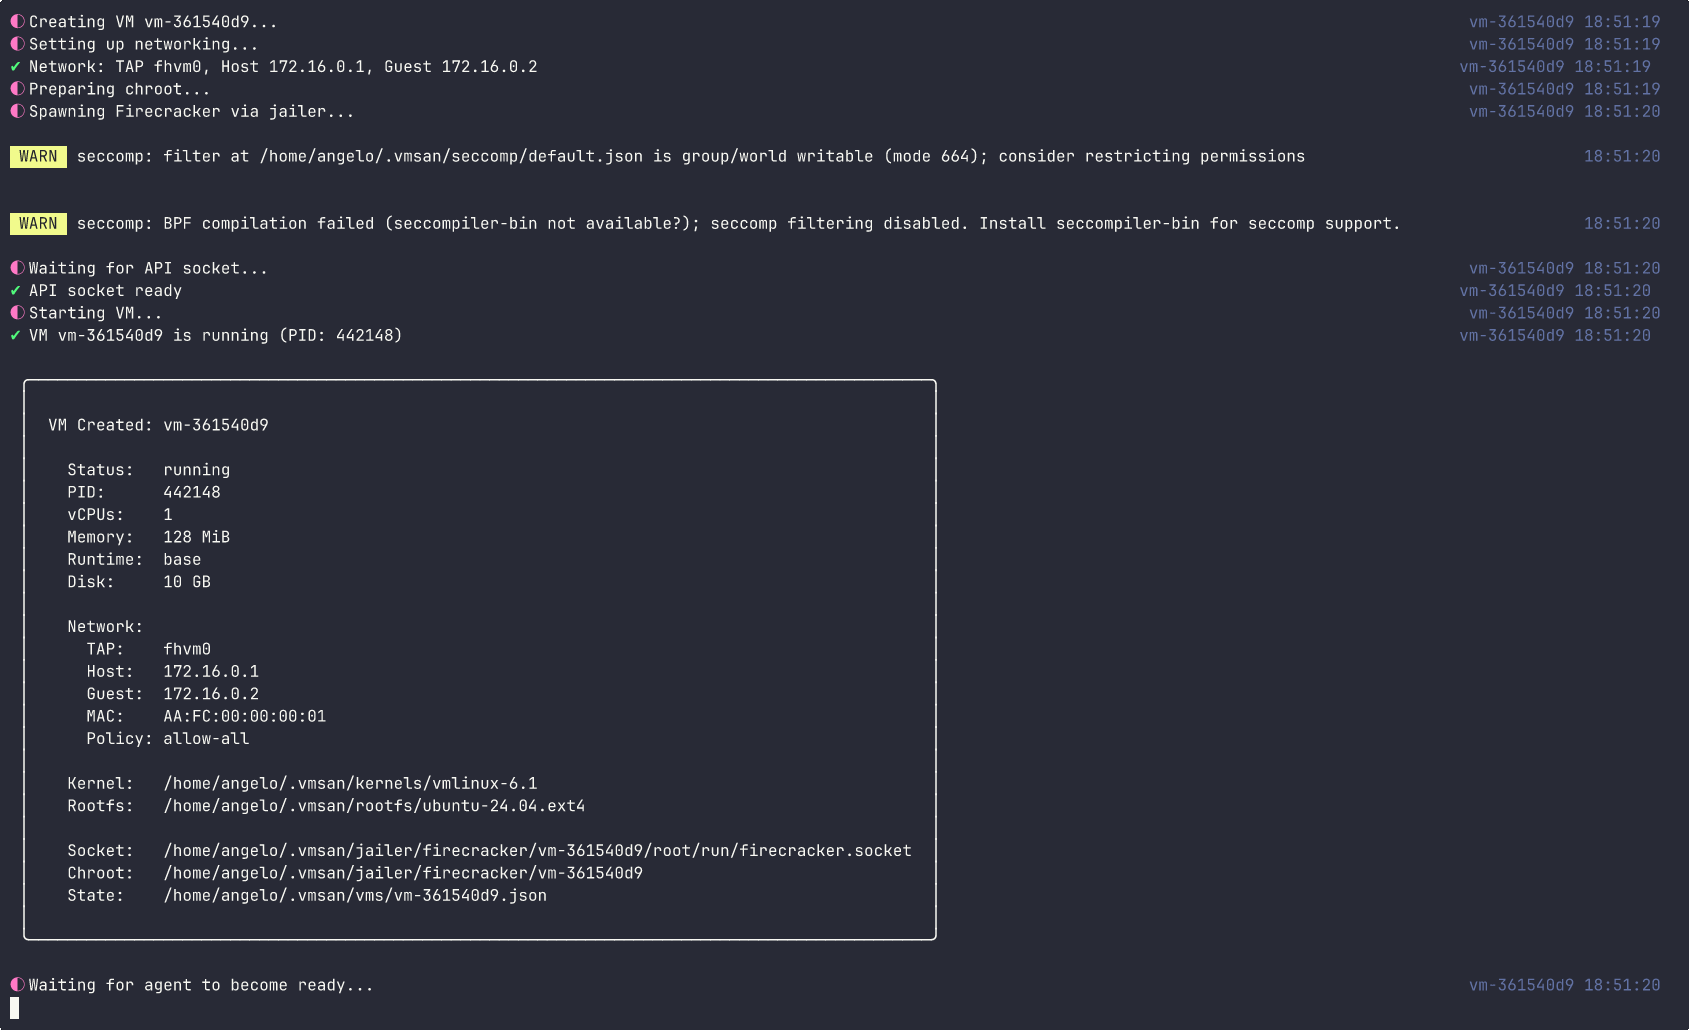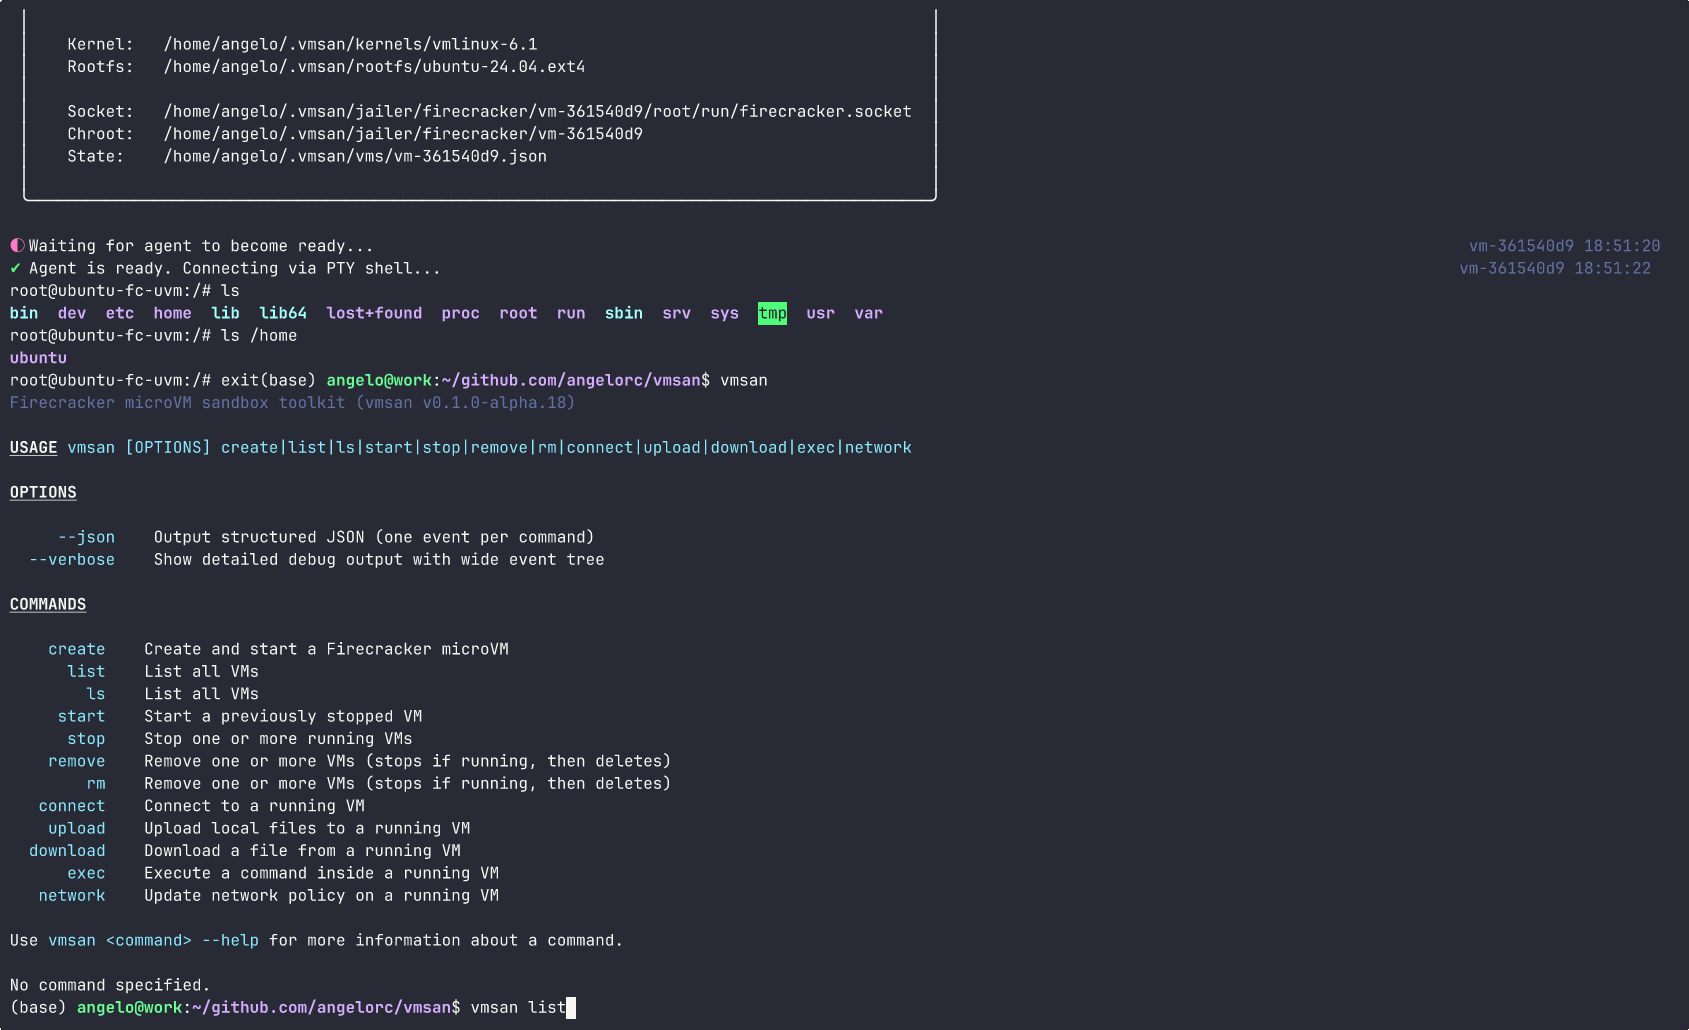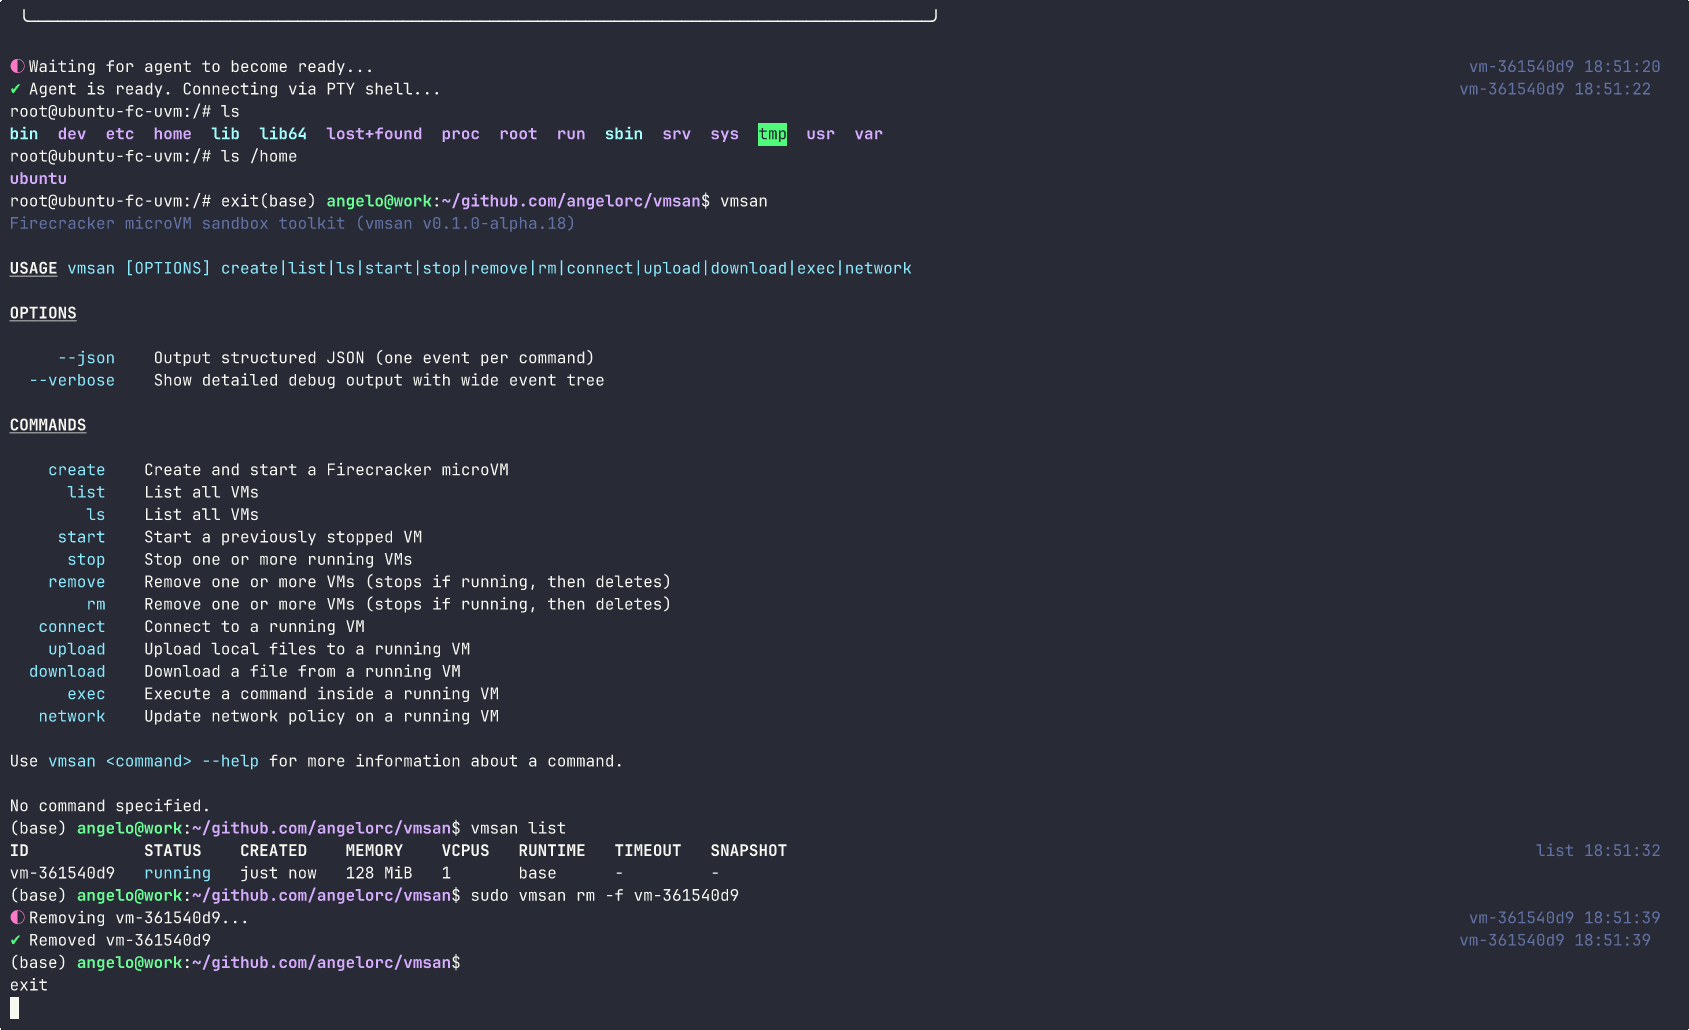
Firecracker made simple. Spin up secure microVMs in milliseconds, from install to interactive shell in one command.
cloud-infrastructure-securitycontainer-securitydevsecops+3
827 months ago
Cheshire preview

Cheshire

GitHubblacksnufkin/cheshire

Adaptix C2 service plugin that drives LitterBox payload analysis from the operator UI.

command-and-controldynamic-analysis-sandboxingexploit-frameworks+4
666 months ago
oversight preview

oversight

GitHubrakosn1cek/oversight

A lightweight security auditor and sandbox for shell scripts. Oversight combines a Static Analysis engine (Rust) with Dynamic Enforcement (Linux…
code-analysisdevsecopsdynamic-analysis-sandboxing+7
3912 days ago
readme2demo preview

readme2demo

GitHubalphacrack/readme2demo

Verified tutorials and demo videos from your README. An AI agent runs it in a hardened Docker sandbox and replays it in a fresh container before…

devsecopsdynamic-analysis-sandboxingeducation+2
812 days ago
Vidar-Stealer-Chrome-Injection-Malicious-JS-Targeting-Google-Reddit-Sessions-Analysis preview

Vidar-Stealer-Chrome-Injection-Malicious-JS-Targeting-Google-Reddit-Sessions-Analysis

GitHubkaandemir993/vidar-stealer-chrome-injection-malicious-js-targeting-google-reddit-sessions-analysis

Reverse engineering Vidar Stealer: From obfuscated memory strings to Chrome process injection, malicious JS execution, and active session hijacking…

binary-analysisdigital-forensicsdynamic-analysis-sandboxing+6
510 days ago
raccoon_config preview

raccoon_config

GitHubnexusfuzzy/raccoon_config

Scans a list of raccoon servers from Tria.ge and extracts the config
dynamic-analysis-sandboxingmalware-analysisthreat-intelligence
153 years ago
nanocore_extractor preview

nanocore_extractor

GitHubjacobpimental/nanocore_extractor

Extracts nanocore sample from compile AutoIT script

binary-analysisdynamic-analysis-sandboxingforensics+2
67 years ago
SecLog preview

SecLog

GitHubseclog-open/seclog

Collects multi-source security logs from reproducible Docker attack scenarios, builds attack chains, and provides the SecLog-Bench-216 benchmark for…

anomaly-detectiondynamic-analysis-sandboxingeducation+6
211 days ago
Driver-PiDqSerializationWrite-Example preview

Driver-PiDqSerializationWrite-Example

GitHubgmh5225/driver-pidqserializationwrite-example

How to use PiDqSerializationWrite. Introduces how to safely read and write from mapped driver

binary-analysisdebuggersdynamic-analysis-sandboxing+5
23 years ago
flare-ida preview
Archived

flare-ida

GitHubmandiant/flare-ida

IDA Pro utilities from FLARE team
binary-analysisdebuggersdynamic-analysis-sandboxing+3
2.5k2 years ago
CrowdFMS preview
Archived

CrowdFMS

GitHubcrowdstrike/crowdfms

CrowdStrike Feed Management System. CrowdFMS is a framework for automating collection and processing of samples from VirusTotal, by leveraging the…
api-securitydynamic-analysis-sandboxingmalware-analysis+1
1337 years ago
Transformers-Forged-To-Fight-Offline-Version preview

Transformers-Forged-To-Fight-Offline-Version

GitHubgeamztheangrybirds727/transformers-forged-to-fight-offline-version

TRANSFORMERS: Forged to Fight is a 3D combat game where you take over some of the most charismatic troopers straight out of the Transformers…

binary-analysisbinary-exploitationcurated-resources+5
24 months ago
defending-code-reference-harness preview

defending-code-reference-harness

GitHubanthropics/defending-code-reference-harness

Skills for threat modeling, scanning, triage, patching, plus an autonomous scanning harness you can /customize

ai-securitycode-analysisdevsecops+6
7.0k2 months ago
Previous12345Next
