CollaboratorPlusPlus

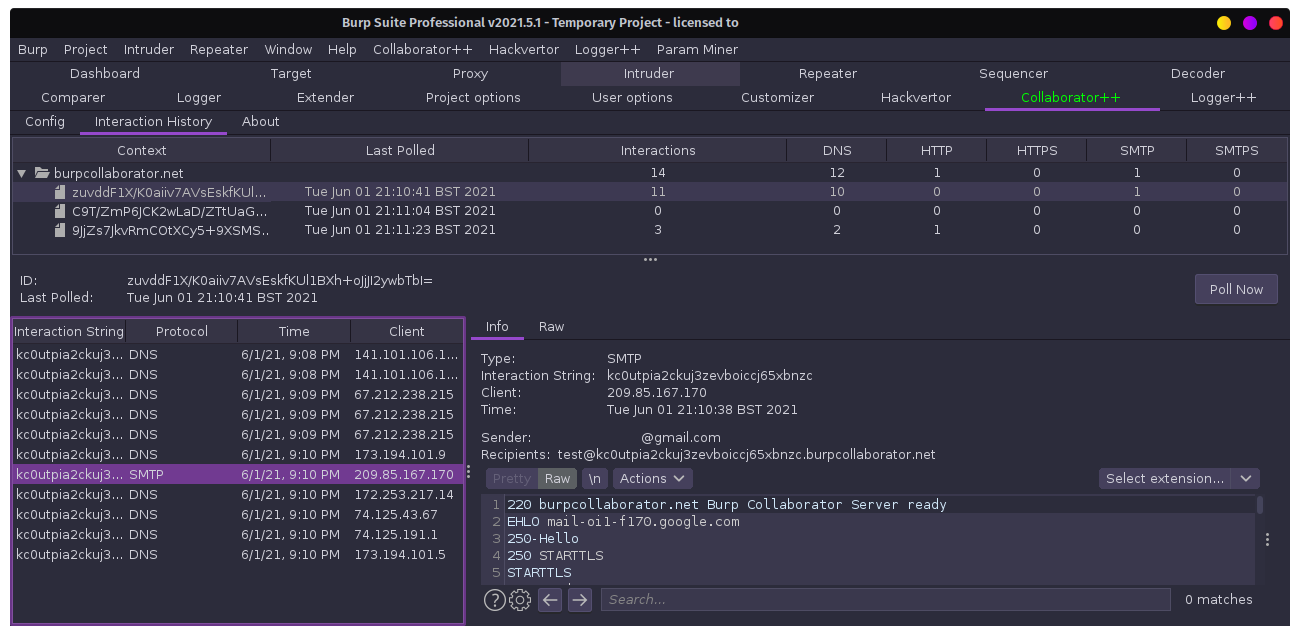
Burp Suite extension enhancing Collaborator with context capture, polling history, and optional AES-encrypted authentication for private server…

Burp Suite extension enhancing Collaborator with context capture, polling history, and optional AES-encrypted authentication for private server…

Burp Suite extension to generate Intruder payloads using Radamsa

Radamsa fuzzer extension for Burp Suite

AI-powered vulnerability scanner extension for Burp Suite with multi-provider support (Ollama, OpenAI, Claude, Gemini)

Burp Suite extension to detect the Next.js / React Server Components (RSC) Remote Code Execution vulnerability (CVE-2025-55182 & CVE-2025-66478).

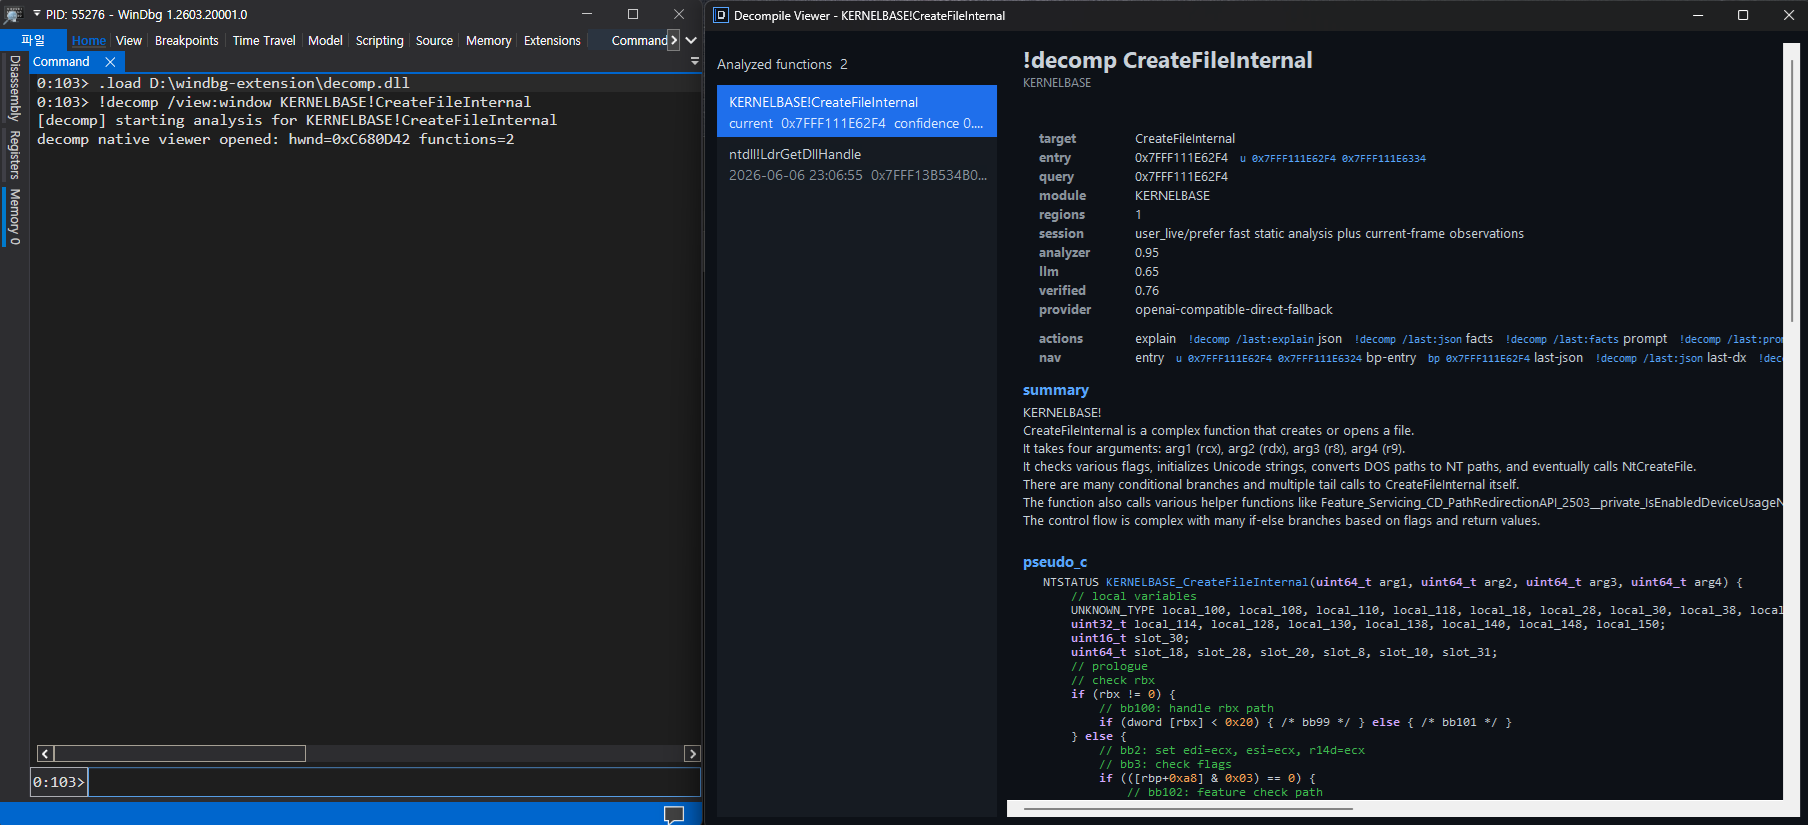
WinDbg x64 extension that disassembles live functions and uses an LLM to produce verified pseudocode.

Burp Active Scan extension to identify Log4j vulnerabilities CVE-2021-44228 and CVE-2021-45046

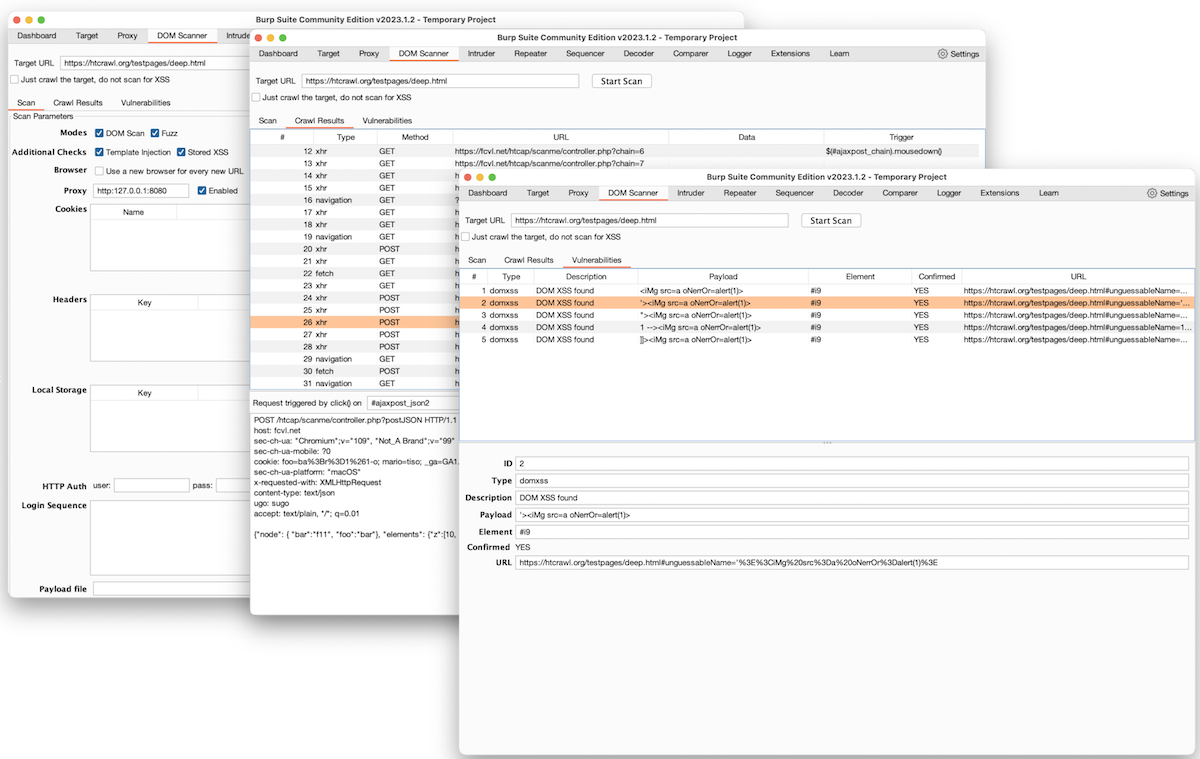
A Burp Suite extension that brings full DOM rendering capabilities directly into Burp, enabling effective security testing of modern JavaScript-heavy…

Rex is a safe and usable kernel extension framework that allows loading and executing Rust kernel extension programs in the place of eBPF.

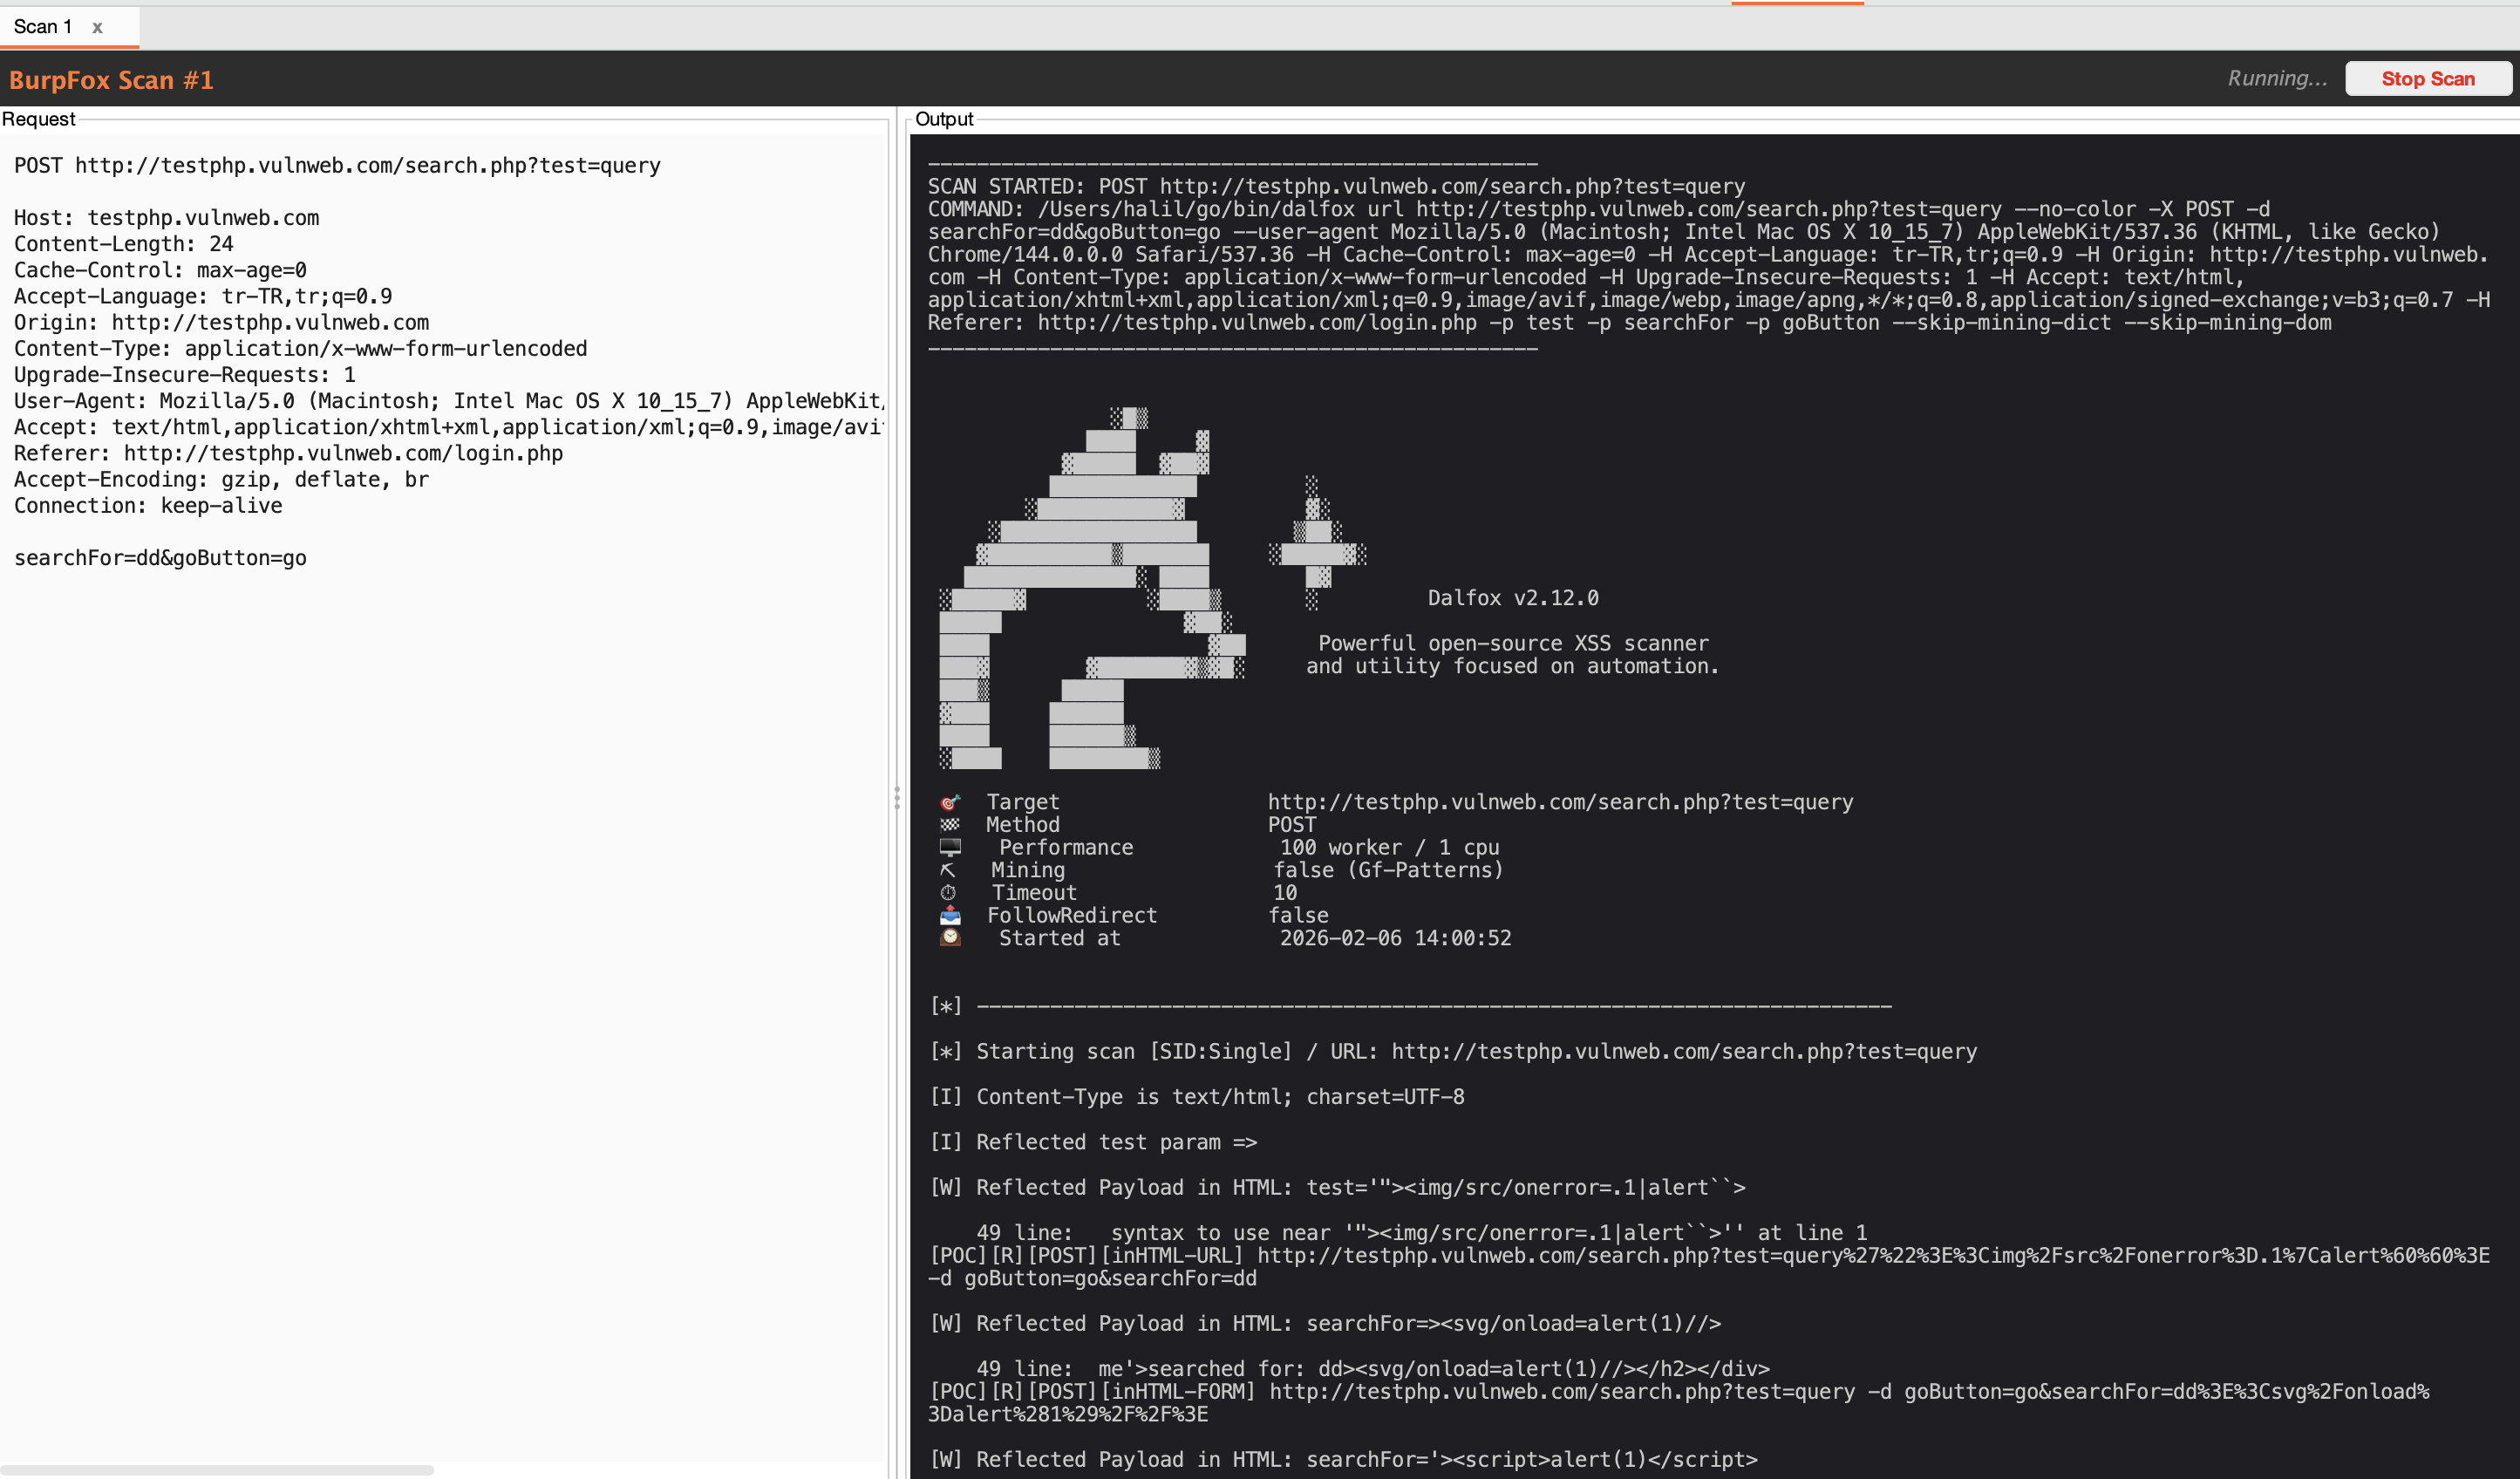
A Burp Suite extension that integrates Dalfox XSS scanner directly into your workflow.

Runtime process analysis and memory hacking MCP server for AI agents. Supports dynamic extension loading, read-only mode, audit logging, and…

CuckooDroid - Automated Android Malware Analysis with Cuckoo Sandbox.

Burp Suite extension for automated detection and exploitation of HTTP request smuggling vulnerabilities, supporting HTTP/1.1 and HTTP/2-downgrade…

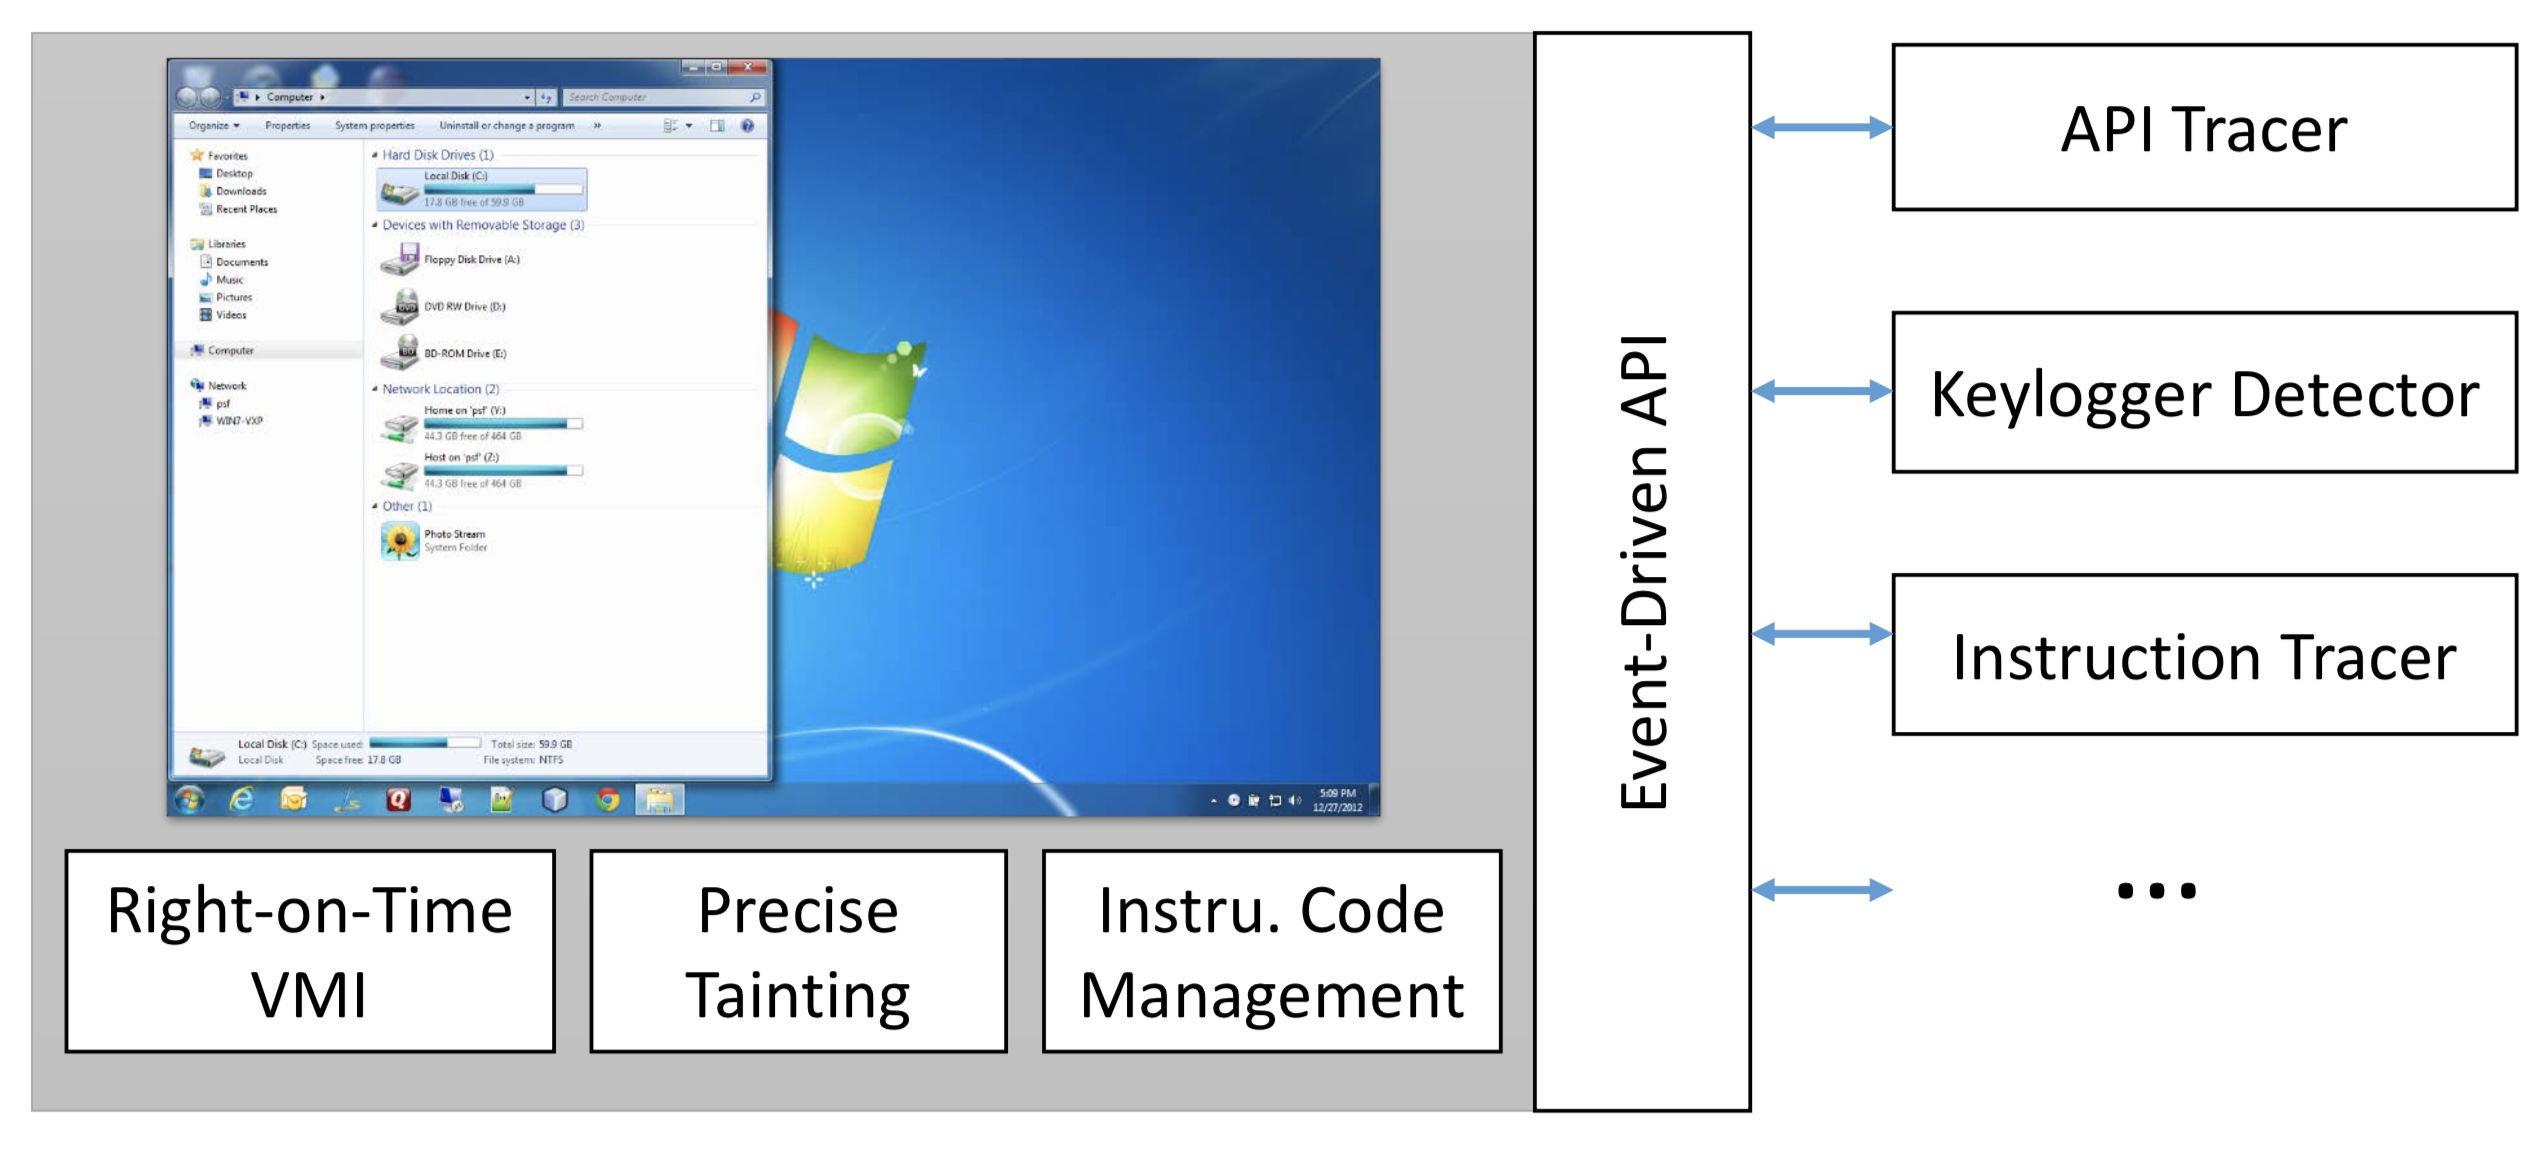
DECAF (short for Dynamic Executable Code Analysis Framework) is a binary analysis platform based on QEMU. This is also the home of the DroidScope…

Ghidra extension bridging static and dynamic analysis via Frida, enabling scriptable runtime instrumentation for reverse engineering binaries on…

The new bridge between Burp Suite and Frida!

Burp Suite's extension to scan and crawl Single Page Applications