Android-Forensics-References

Curated reference for Android forensic artifacts and log paths, with links to CTF writeups, research papers, and mobile device analysis tooling.

Curated reference for Android forensic artifacts and log paths, with links to CTF writeups, research papers, and mobile device analysis tooling.

Audit Preference Pane and Log Reader for OS X

Security Onion 16.04 - Linux distro for threat hunting, enterprise security monitoring, and log management

PowerShell module for Office 365 and Azure log collection

Download and View Skype History Without Skype

Rust-based Windows forensic toolkit for real-time MFT monitoring, event log streaming, and channel enumeration, enabling live system analysis and…

Read-only IOC scanner and mitigation toolkit for cPanel & WHM EmailTrack SQL injection (CVE-2026-67401). Performs version fingerprinting, file…

IOC feed and analysis toolkit for EITest campaigns, featuring C2 data decryption, victim payload decoding, and sinkhole log processing for threat…

Conducted a full SOC investigation into a Conti ransomware compromise of an Exchange server using Splunk 8.2.2. Analysed 28,145 events across Windows…

SO-CRATES: Security Onion Containerized Rapid Analysis of Threats, Evil, and Sus!

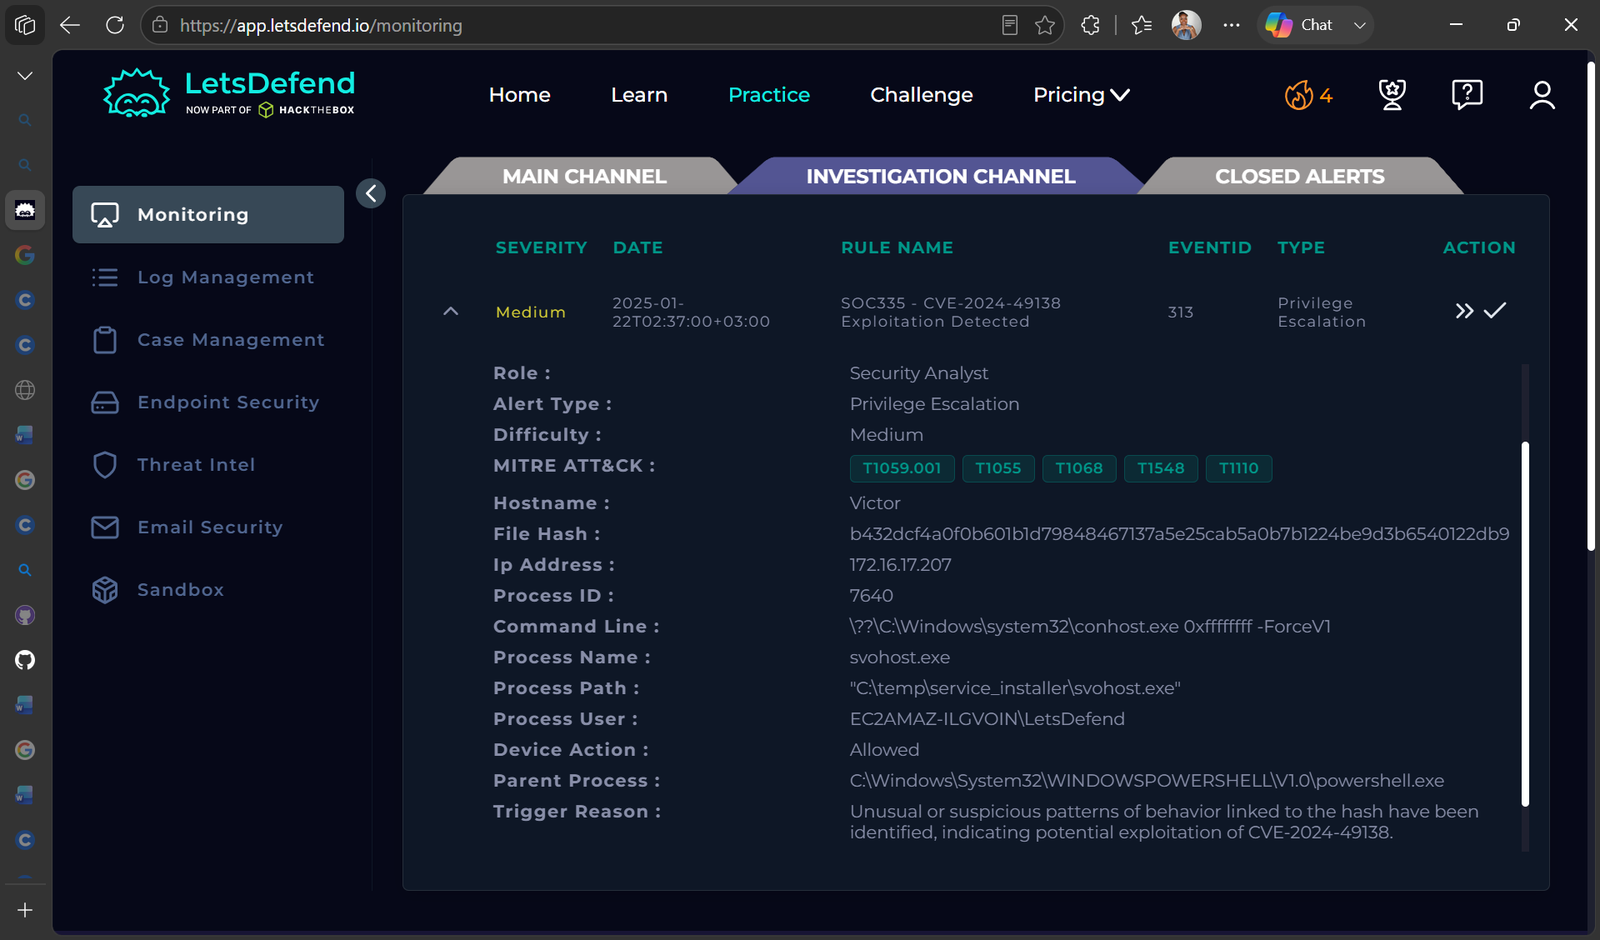
Documented incident response case for CVE-2024-49138 exploitation, featuring log analysis, hash validation, C2 detection, and containment procedures…

The best-in-class macOS app to See every packet clearly on your Mac. Alternative to Wireshark

Curated index of incident response and DFIR tools, including memory and disk forensics, evidence collection, log analysis, playbooks, and educational…

Multi-threaded Windows event log forensics timeline generator and threat hunting tool with full Sigma rule support, producing CSV/JSON timelines for…

Investigate malicious Windows logon by visualizing and analyzing Windows event log

SOC investigation of a CVE-2024-49138 exploitation alert using log analysis, threat intelligence, and endpoint containment.

Audits Windows event log settings against best-practice guidelines and Sigma-rule detectability, with automated configuration for DFIR readiness.

Investigation of a PAN-OS CVE-2024-3400 command injection attempt, analyzing payload delivery, internal processing, and execution validation based on…